
modo
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
ctfcurated-resourceseducation+9
1926 months ago
mohshomis/modoCurated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 projectdiscovery/nuclei-templates-labs
Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀
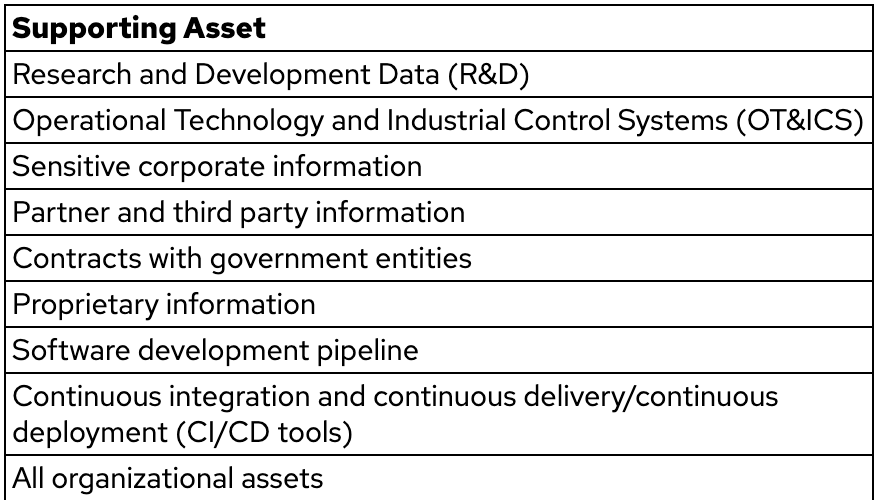 redhat-infosec/priority-intelligence-requirements-dev
This guide describes a process for developing Cyber Threat Intelligence Priority Intelligence Requirements
 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.
 arpeetrathii/50-days-of-sqli
Learning and hunting SQL injection bugs for 50 continuous days
 gmh5225/awesome-web3-security
A curated list of Web3 Security materials and resources for Pentesters and Bug Hunters.
 paulveillard/cybersecurity-interview-questions
A collection of awesome framework, libraries, learning tutorials, videos, webcasts, technical resources and cool stuff about Interview for Security &…
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
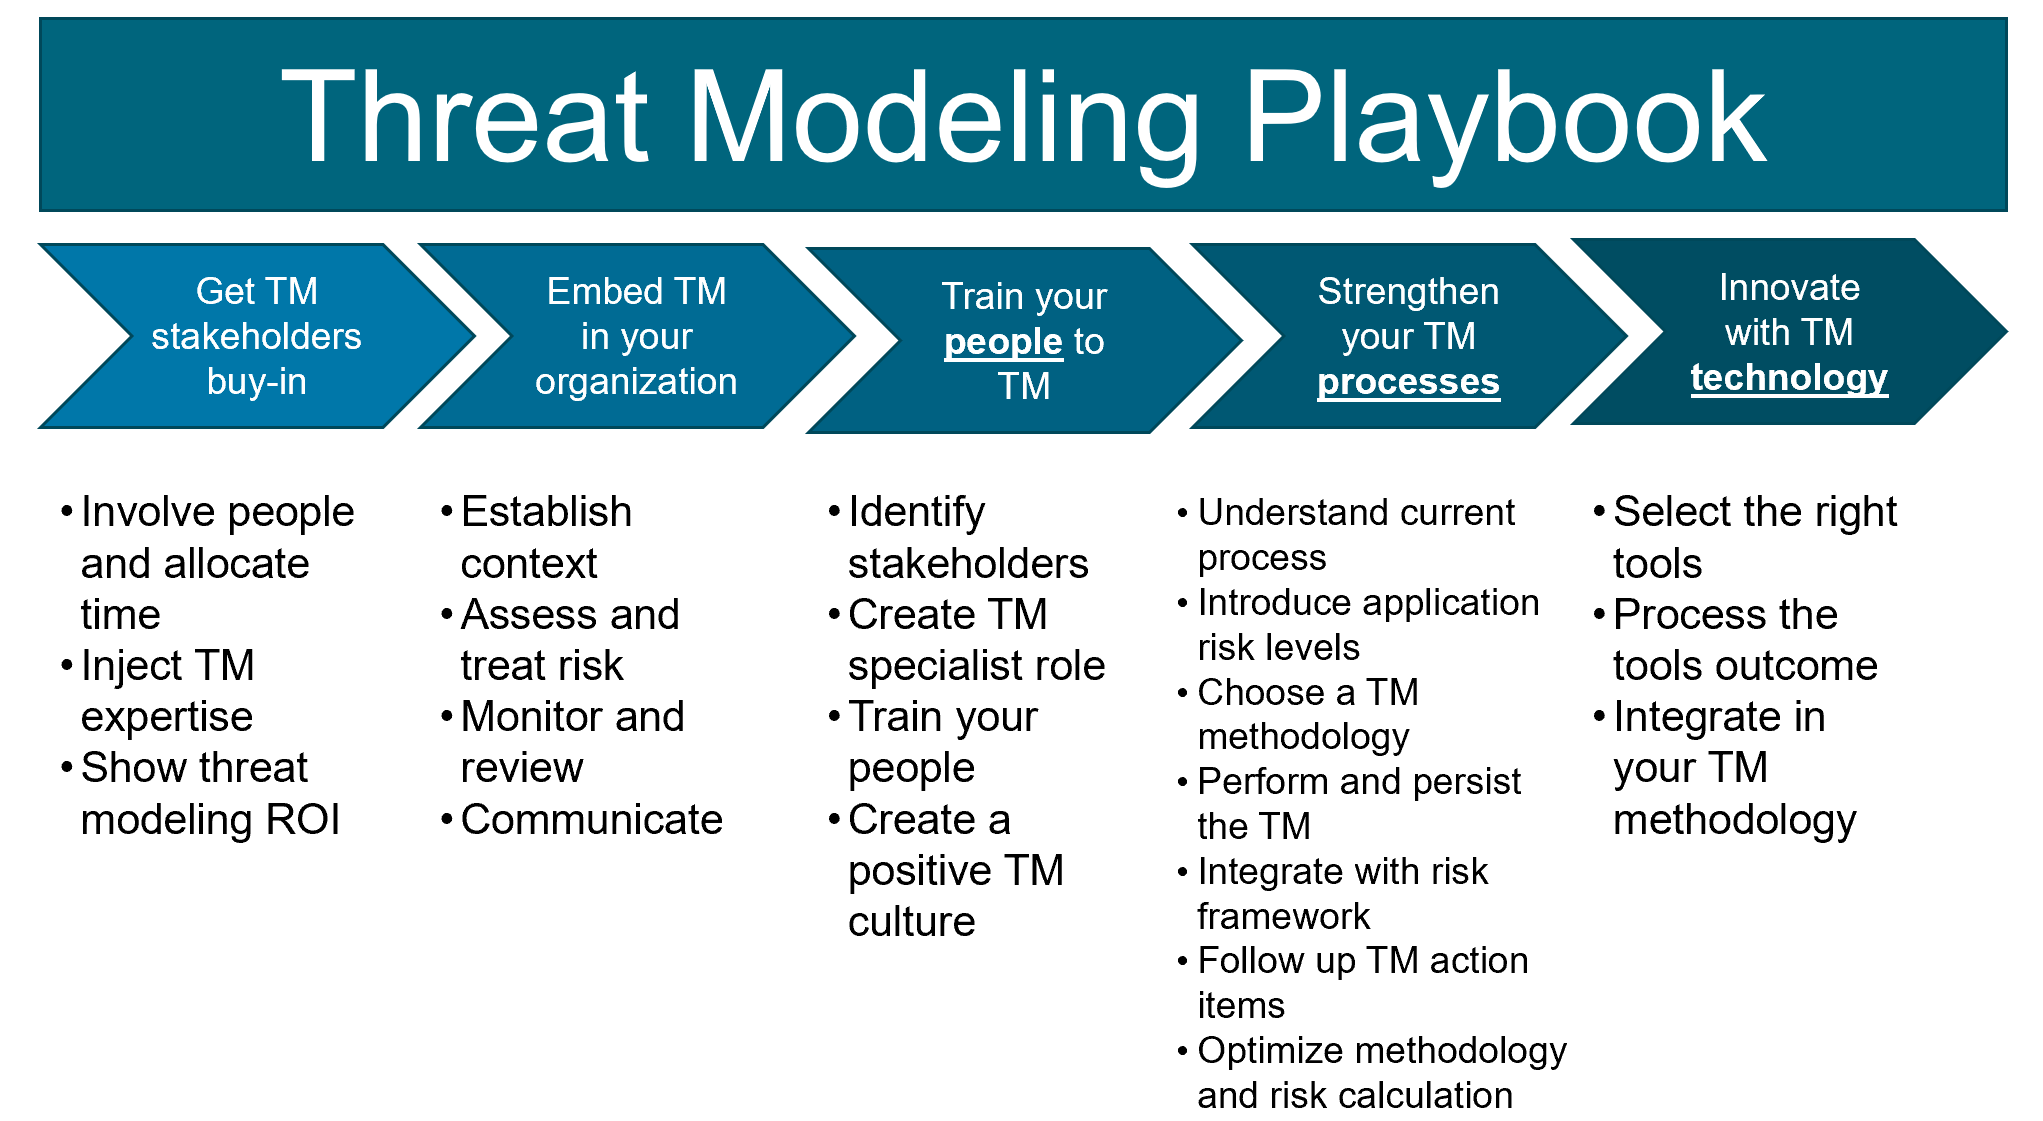 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 sylwia-budzynska/codeql-workshop
Take first steps in CodeQL for Python by writing a query to find CVE-2024-32022
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…