
oss-oopssec-store
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
ai-securityctfeducation+7
koadt/oss-oopssec-storeSecurity training for the apps you actually ship. Open your browser and start hacking.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 lylemi/learn-web-hacking
Structured study notes covering web hacking fundamentals, common vulnerabilities, penetration testing techniques, and defensive security, with…
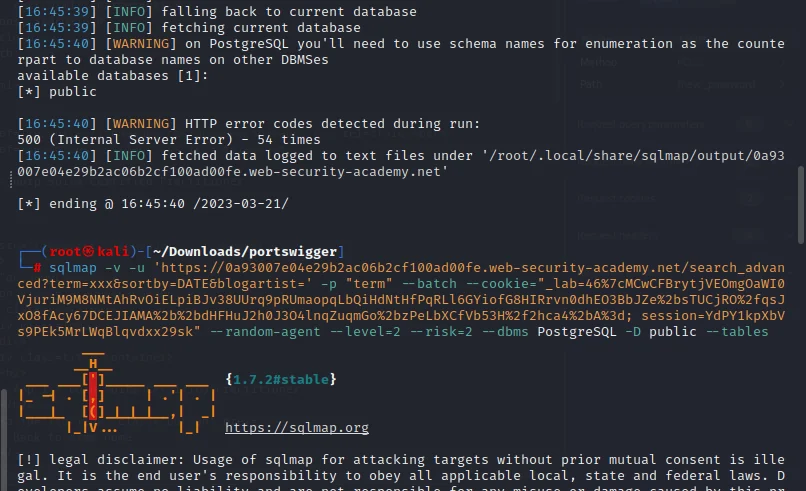 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 n3oari/bscp-exam-guide-by-n3oari-2026
Burp Suite Certified Practitioner - Portswigger - My notes - Guide
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 enaqx/awesome-pentest
A collection of awesome penetration testing resources and tools
 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…