
Vulnvault
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
code-analysiscurated-resourcesdevsecops+5
4
viralmaniar/vulnvaultDeveloper-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
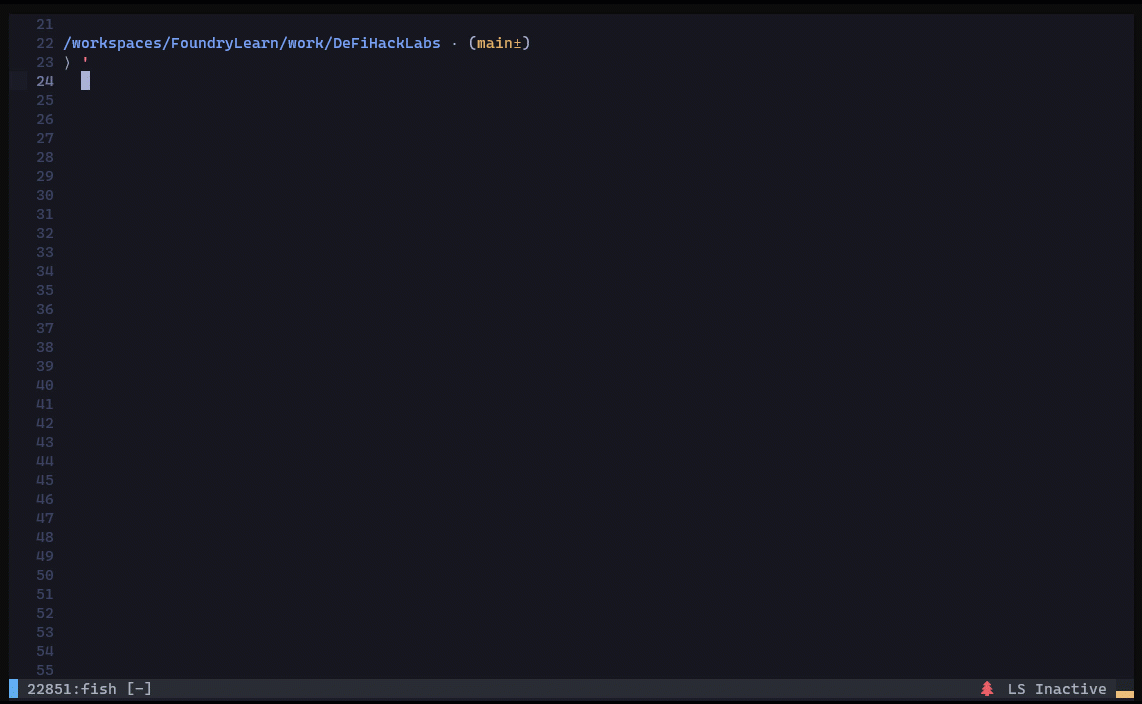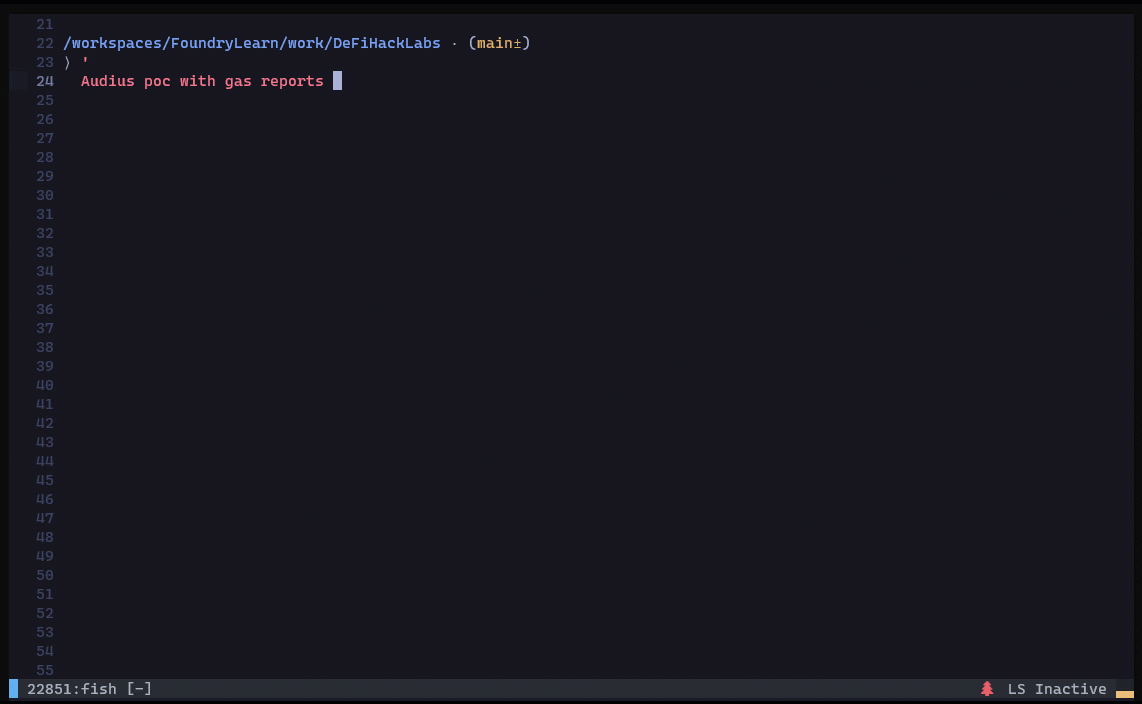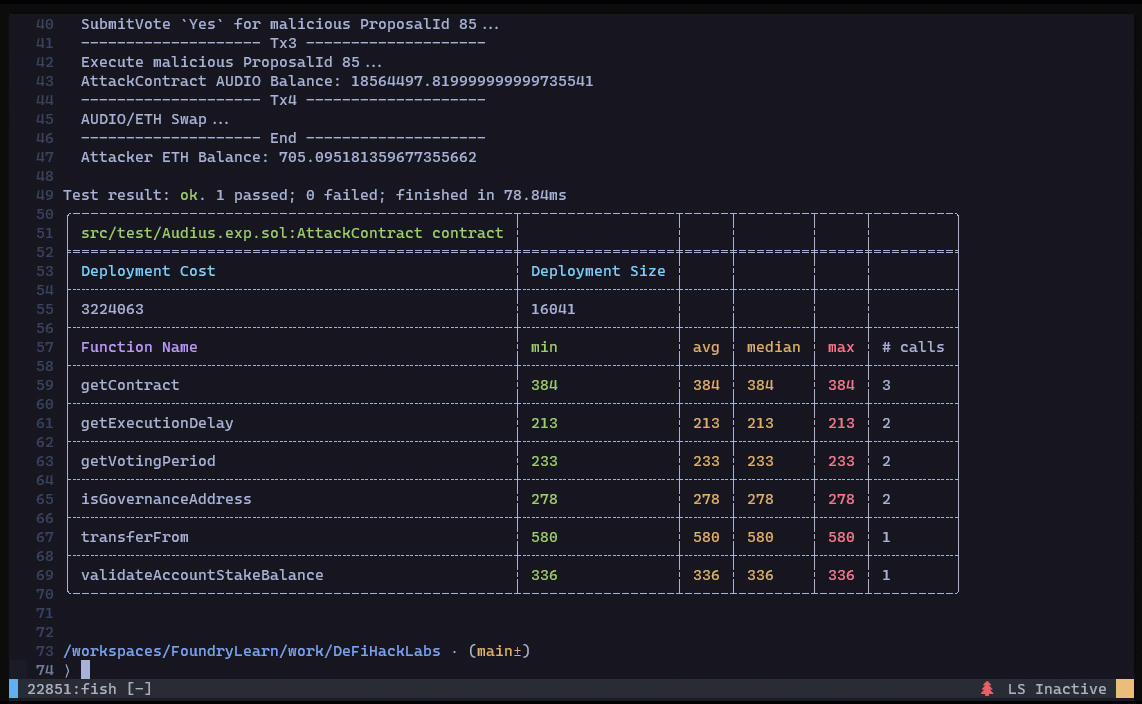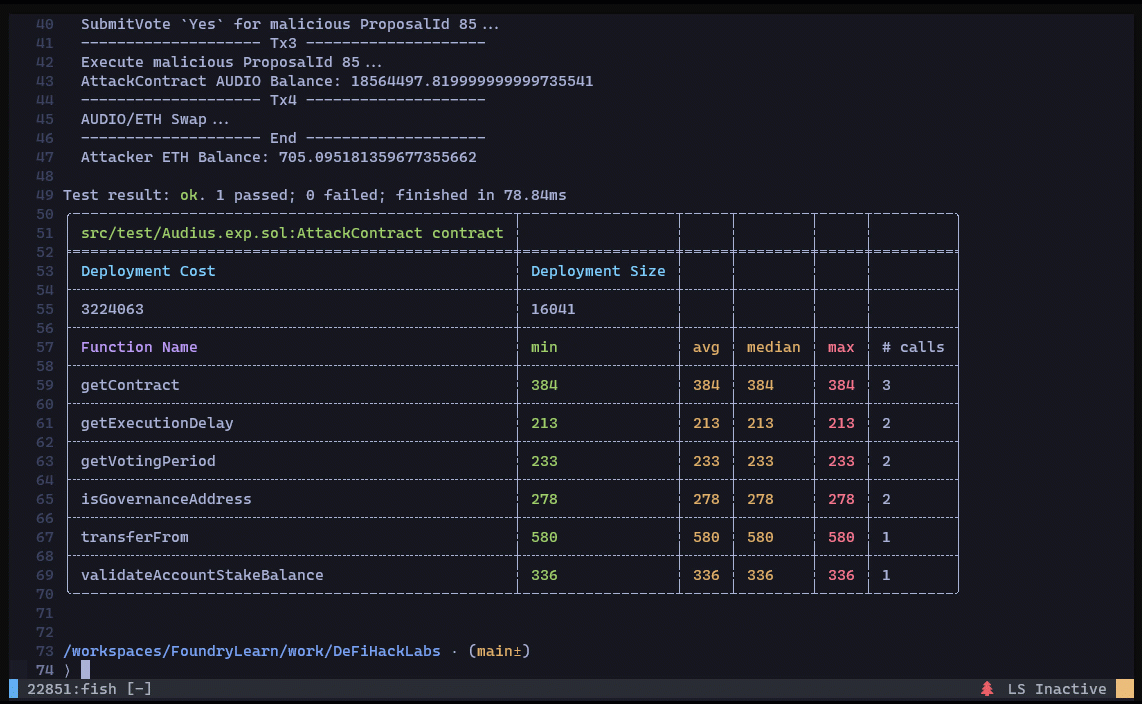 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 syslifters/offsec-reporting
Offensive Security OSCP+, OSEP, OSWP, OSWA, OSWE, OSED, OSMR, OSEE, OSDA, OSIR, OSTH Exam and Lab Reporting / Note-Taking Tool
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 owasp/ocsd
OWASP Certified Secure-Software Developer
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 github/securitylab
Resources related to GitHub Security Lab
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 sylwia-budzynska/codeql-workshop
Take first steps in CodeQL for Python by writing a query to find CVE-2024-32022
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 parasimpaticki/awesome-appsec-interview
A curated list of resources, practice questions, and study materials to help you prepare for Application Security (AppSec) interviews