Burp-Suite-Certified-Practitioner-Exam-Study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.

The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…

Building 70 Projects ranging from beginner to advanced so anyone can — learn from, build upon, use as a reference, or even copy directly. Owned by my…

This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.

Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…

Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…

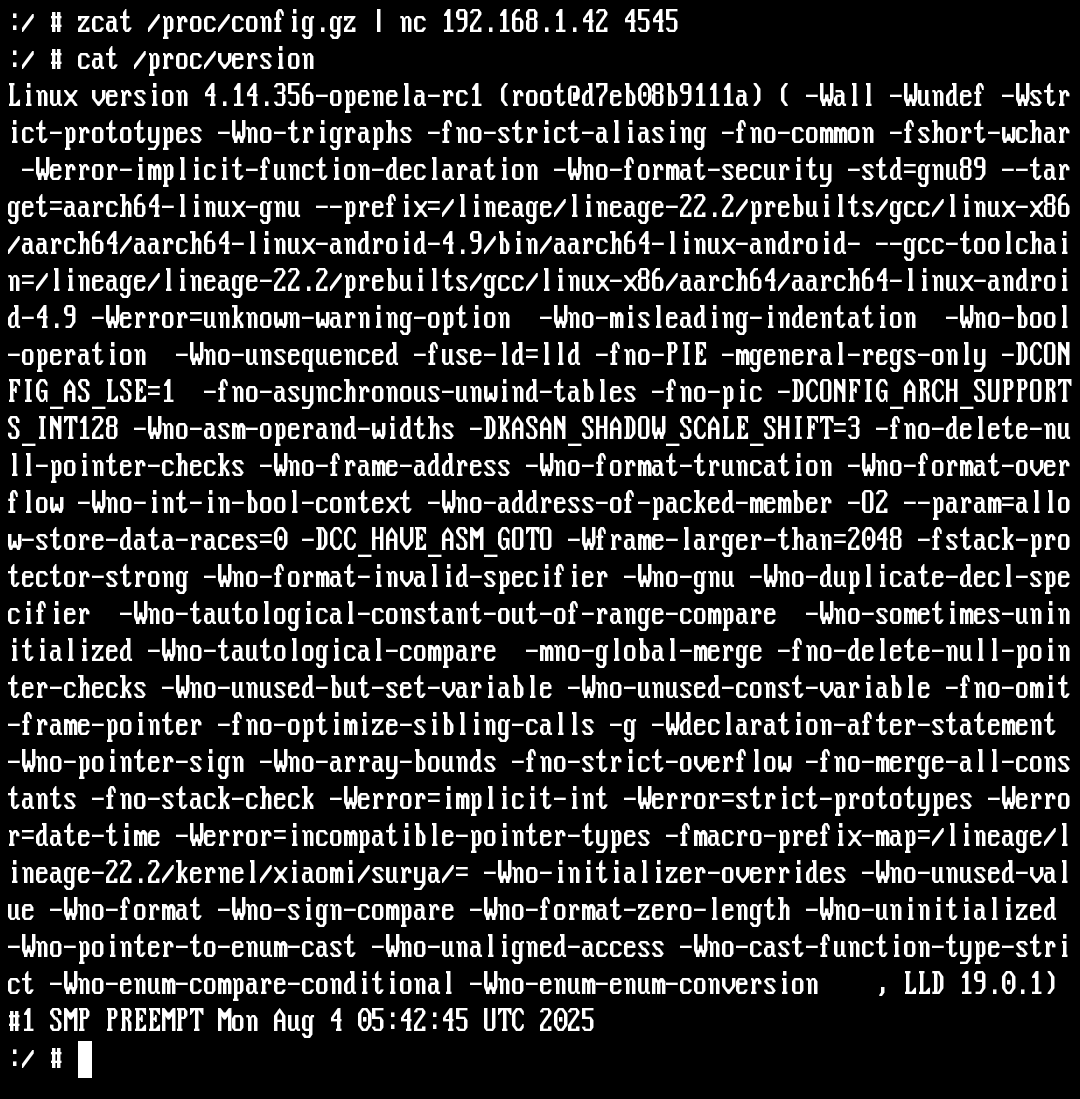
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.

My documentation and tools for learn ethical hacking.

2024年信息安全工程师、2024InformationSecurityEngineer

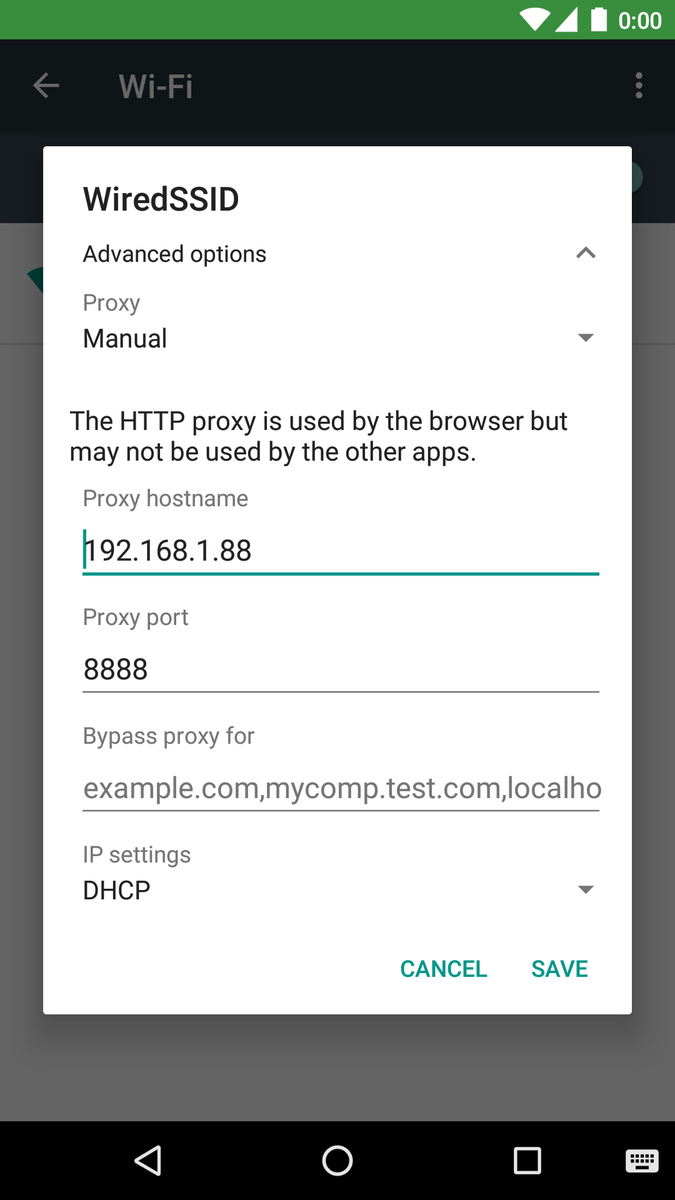
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…

Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.