

Resources-for-Application-Security
 security-prince/resources-for-application-security
Some good resources for getting started with application security
ctfcurated-resourcesdynamic-analysis-sandboxing+6
150
security-prince/resources-for-application-securitySome good resources for getting started with application security
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
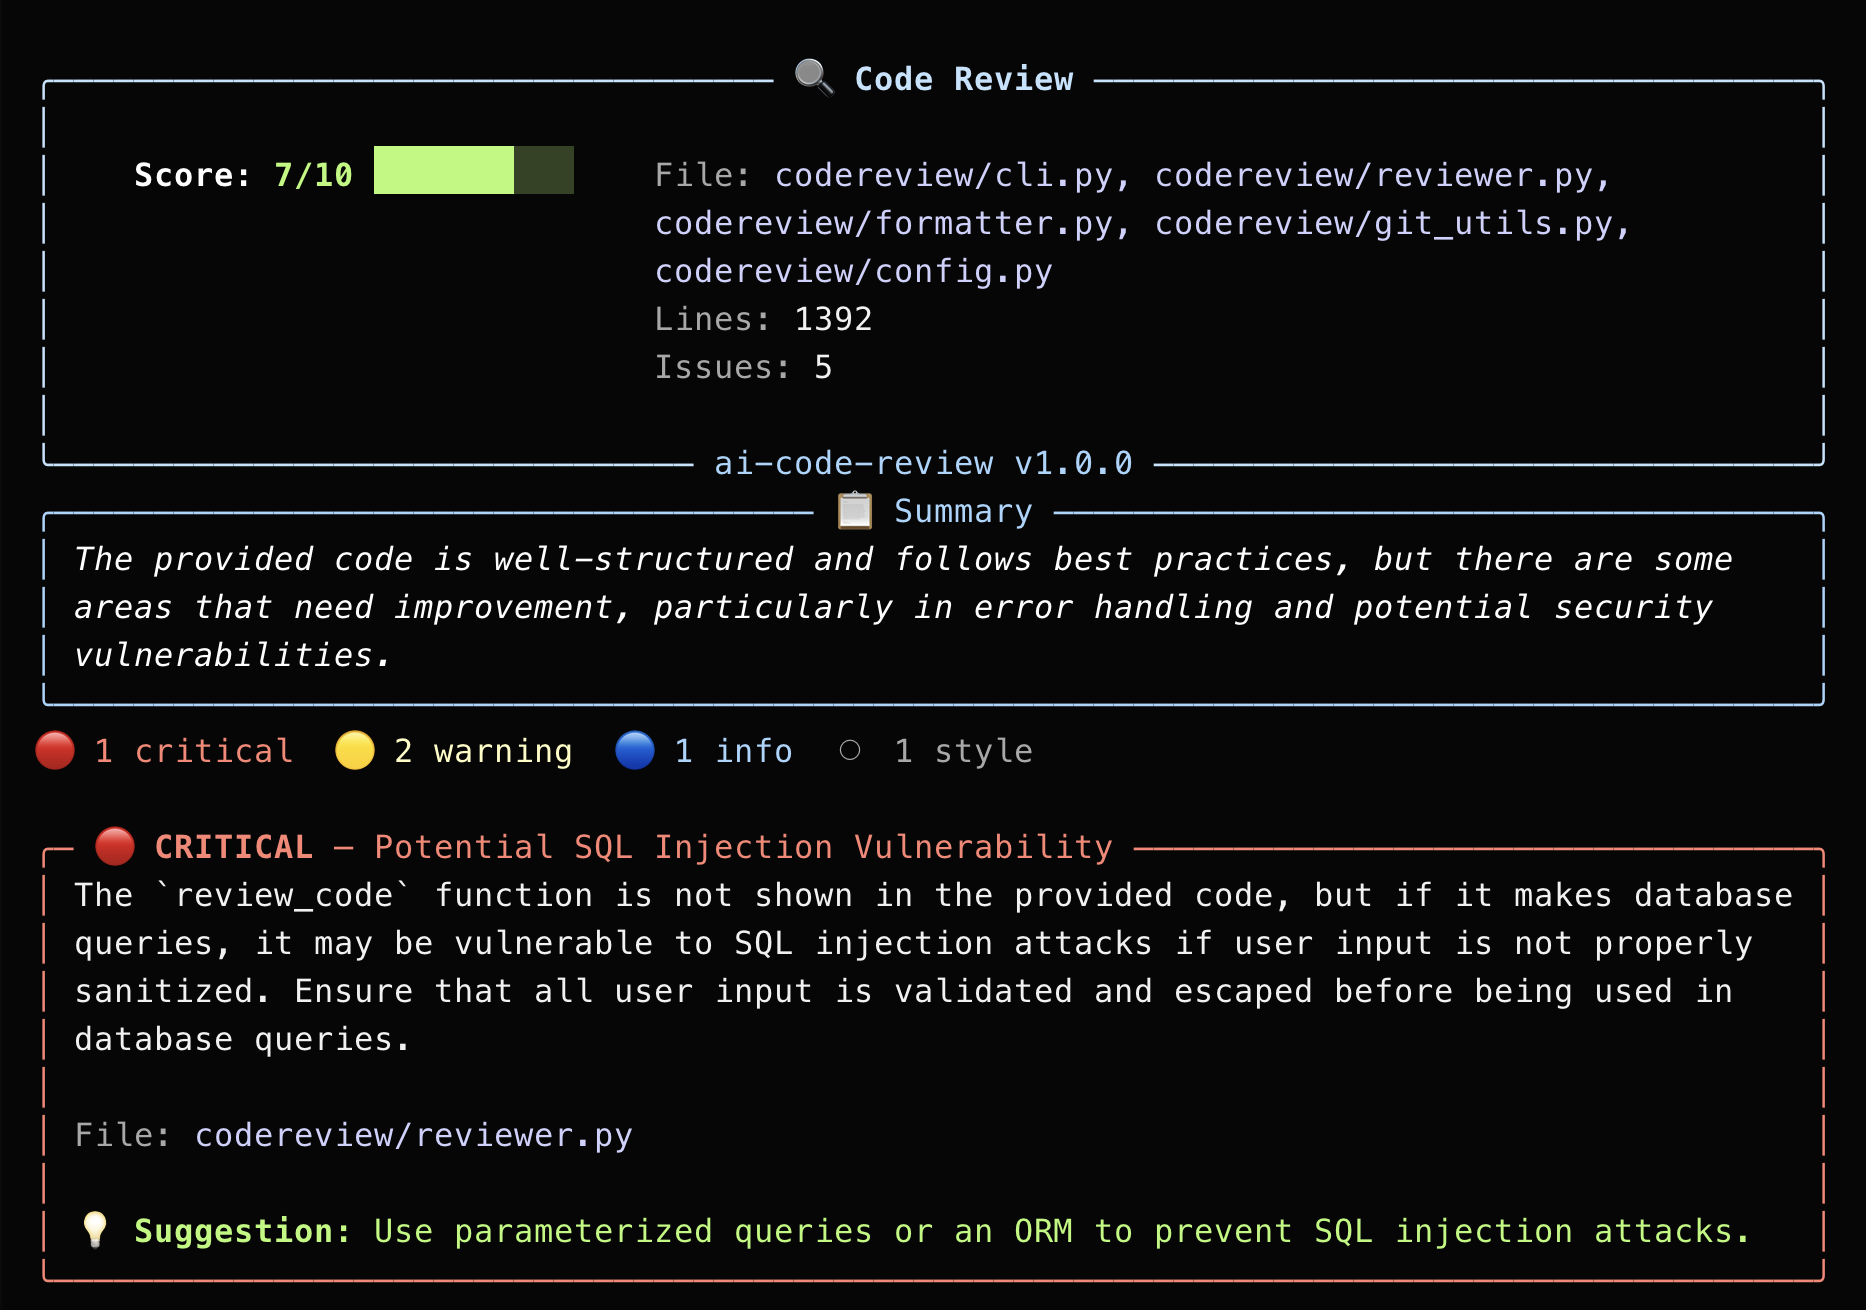 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
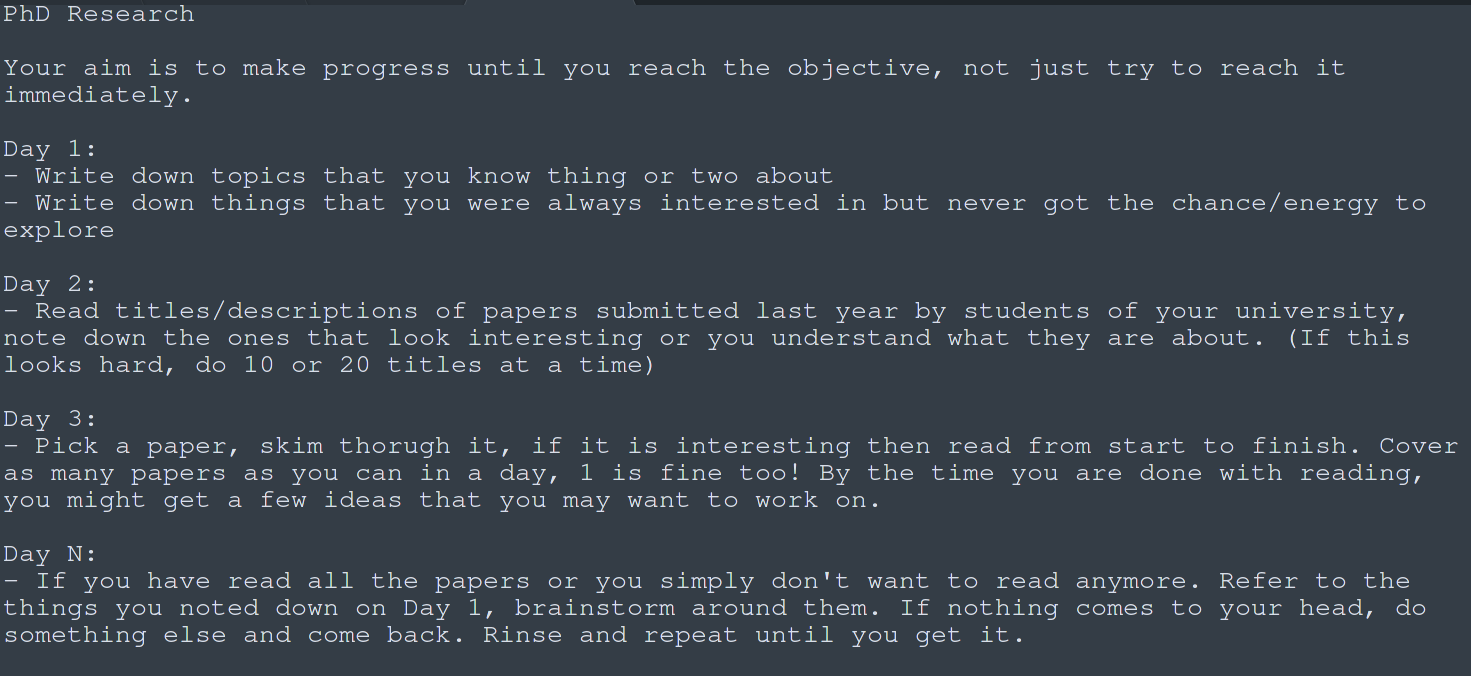 s0md3v/be-a-hacker
roadmap for a self-taught hacker
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.