

smbtakeover
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
authentication-authorizationlateral-movementpenetration-testing+2
361
zyn3rgy/smbtakeoverBOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
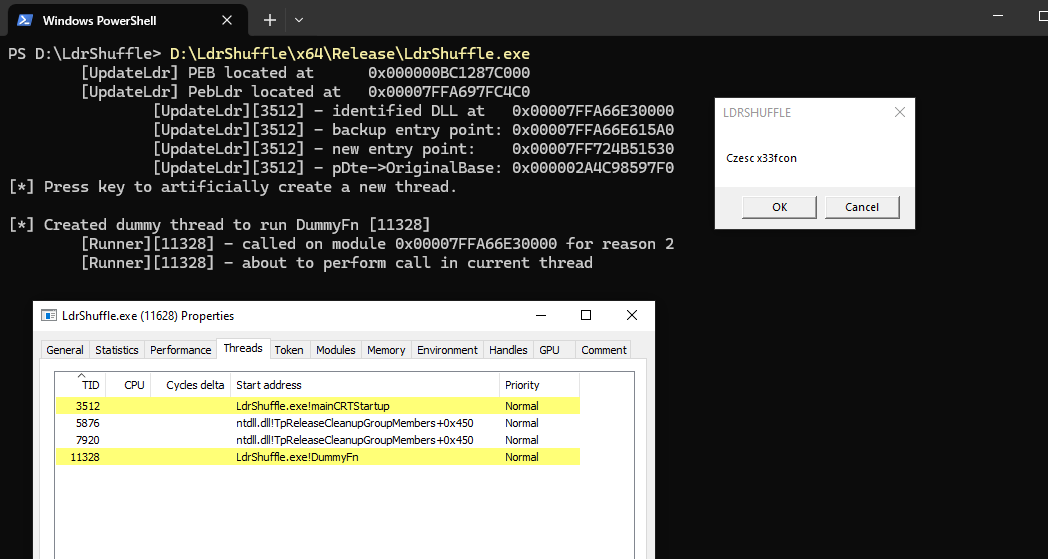 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
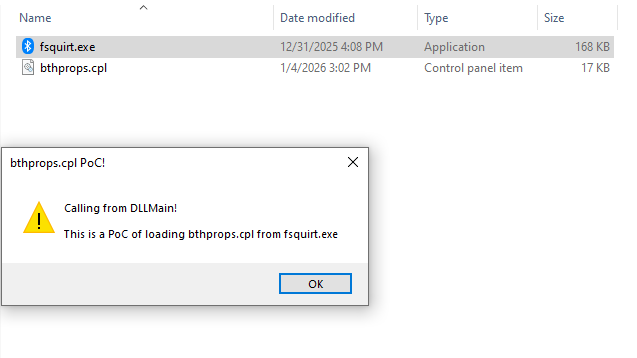 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration