
DCOMrade
 sud0woodo/dcomrade
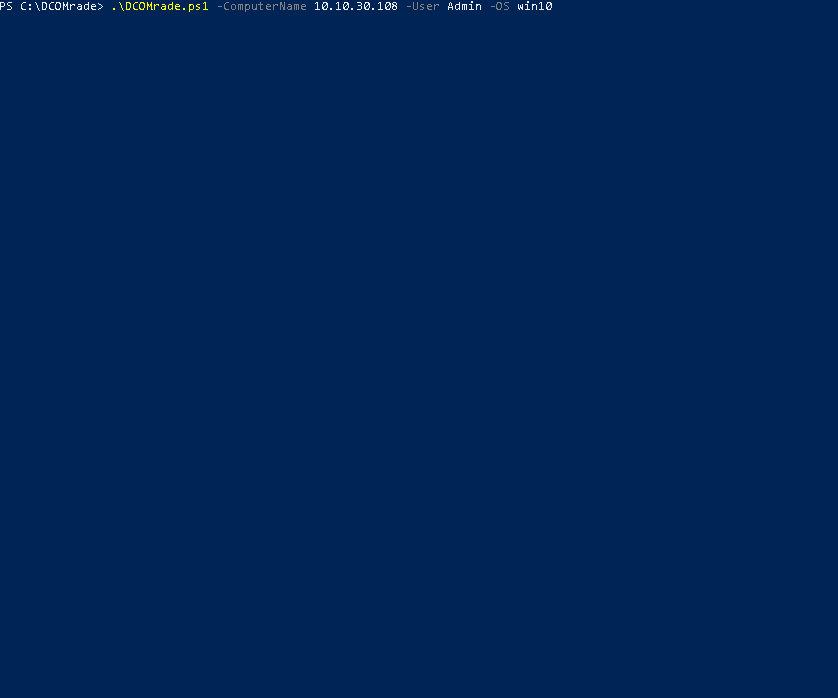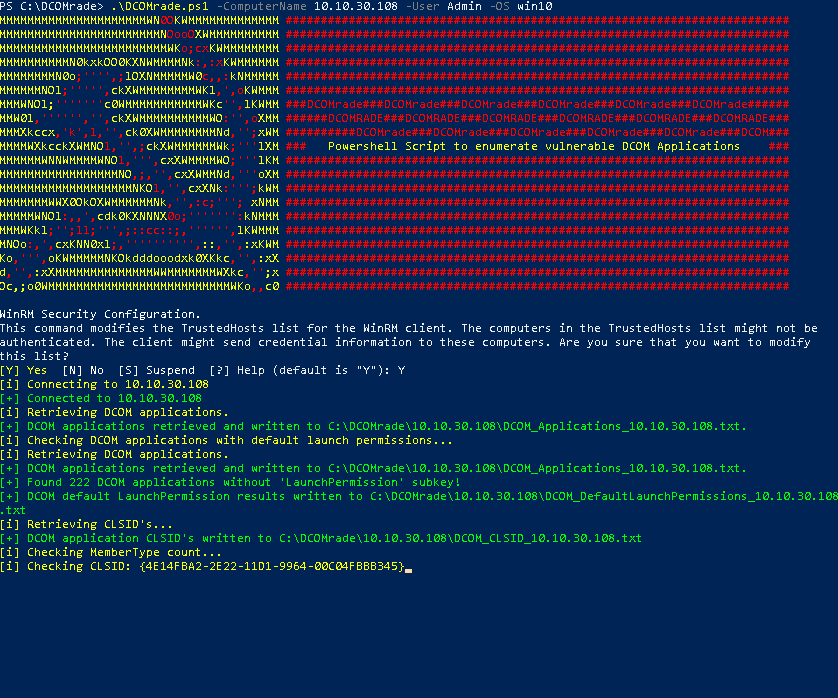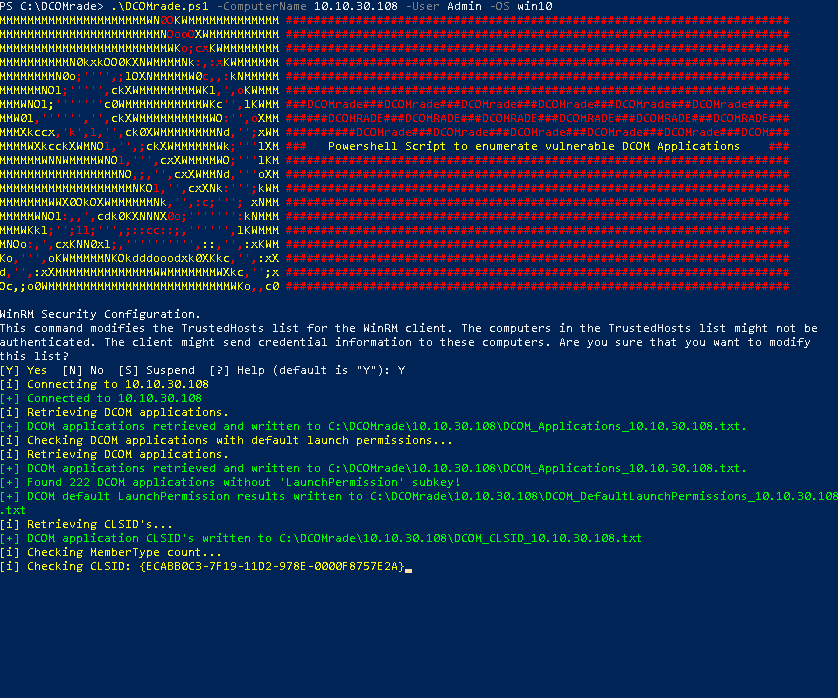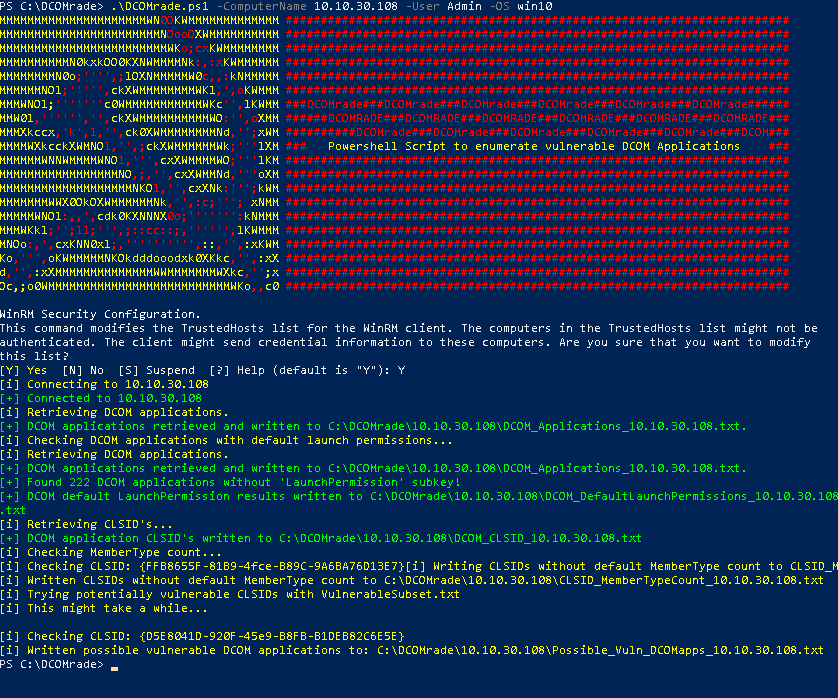
Powershell script for enumerating vulnerable DCOM Applications
lateral-movementpenetration-testingpost-exploitation+2
sud0woodo/dcomradePowershell script for enumerating vulnerable DCOM Applications
 synacktiv/dlhell
Local & remote Windows DLL Proxying
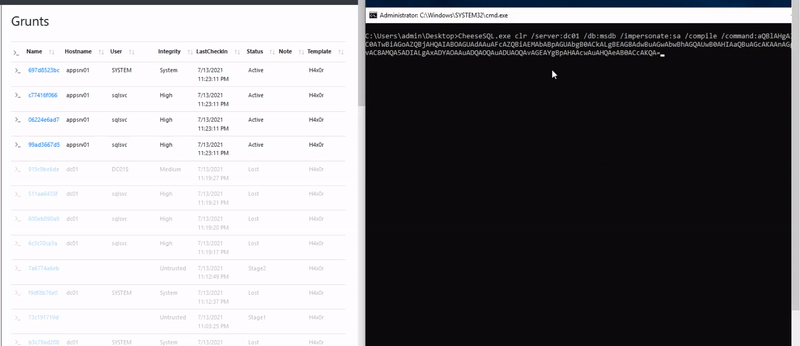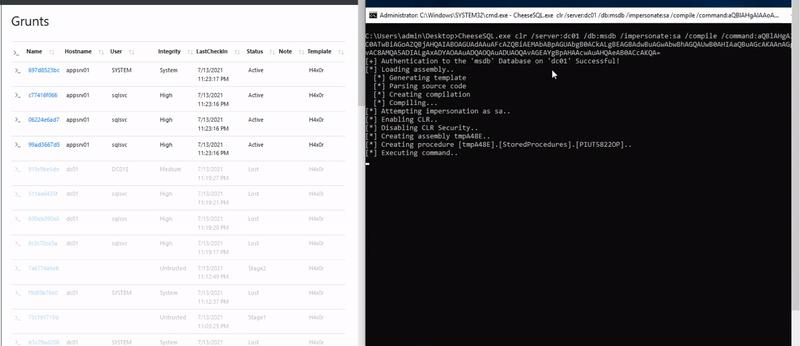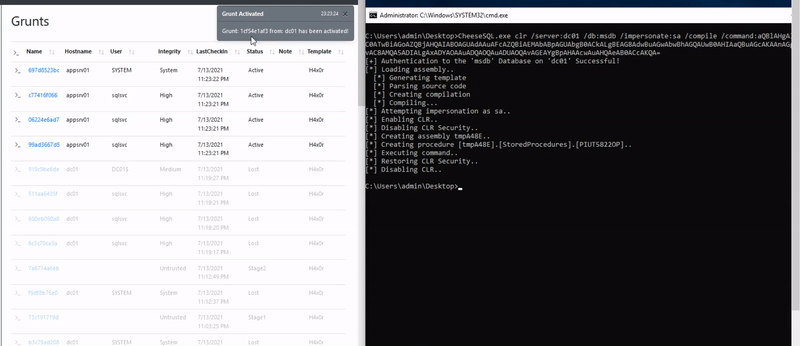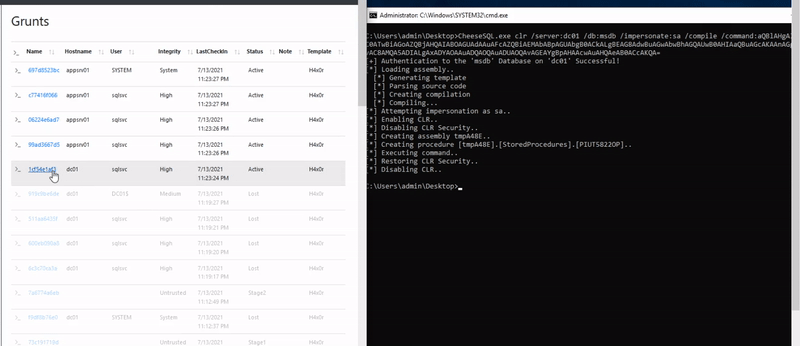 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.