Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
PowerSploit preview
Archived

PowerSploit

GitHubpowershellmafia/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k
6 years ago
ThievingFox preview

ThievingFox

GitHubslowerzs/thievingfox

Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
lateral-movementpenetration-testingpost-exploitation+1
5702 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubdll00p/cve-2021-1675

Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
exploitationlateral-movementpayload-generation+4
11 year ago
PrintSpoofer-ReflectiveDLL preview

PrintSpoofer-ReflectiveDLL

GitHubjonyfilc/printspoofer-reflectivedll

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

exploitationlateral-movementpayload-development+4
22 months ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
nosferatu preview

nosferatu

GitHubkindtime/nosferatu

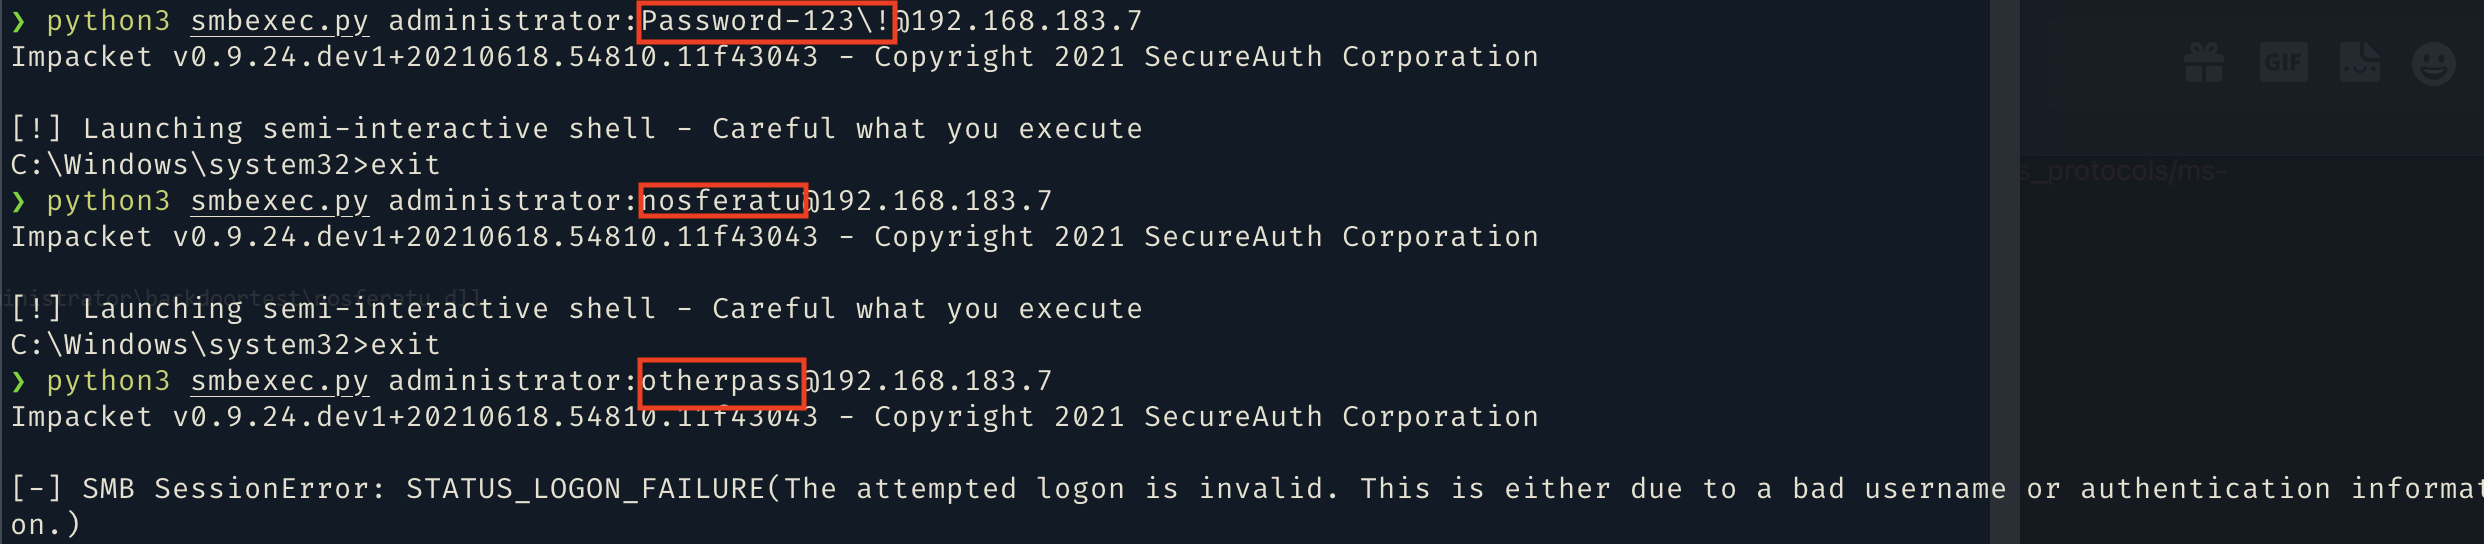
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
authenticationlateral-movementpenetration-testing+2
2421 year ago
dcomhijack preview

dcomhijack

GitHubwkl-sec/dcomhijack

Lateral Movement Using DCOM and DLL Hijacking
exploitationlateral-movementpayload-development+3
3273 years ago
clrinject preview

clrinject

GitHubjonatan1024/clrinject

Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
exploitationlateral-movementpenetration-testing+3
2377 years ago
DLHell preview

DLHell

GitHubsynacktiv/dlhell

Local & remote Windows DLL Proxying
exploitationlateral-movementpayload-development+3
1722 years ago
CVE-2022-26809 preview

CVE-2022-26809

GitHubauduongxuan/cve-2022-26809

Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
exploitationlateral-movementpenetration-testing+3
74 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubpuckiestyle/cve-2021-1675

Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
exploitationlateral-movementpayload-generation+3
15 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubedsonjt81/cve-2021-1675

Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
exploitationlateral-movementpayload-generation+3
3 years ago
CVE-2024-57394 preview

CVE-2024-57394

GitHubcwjchoi01/cve-2024-57394

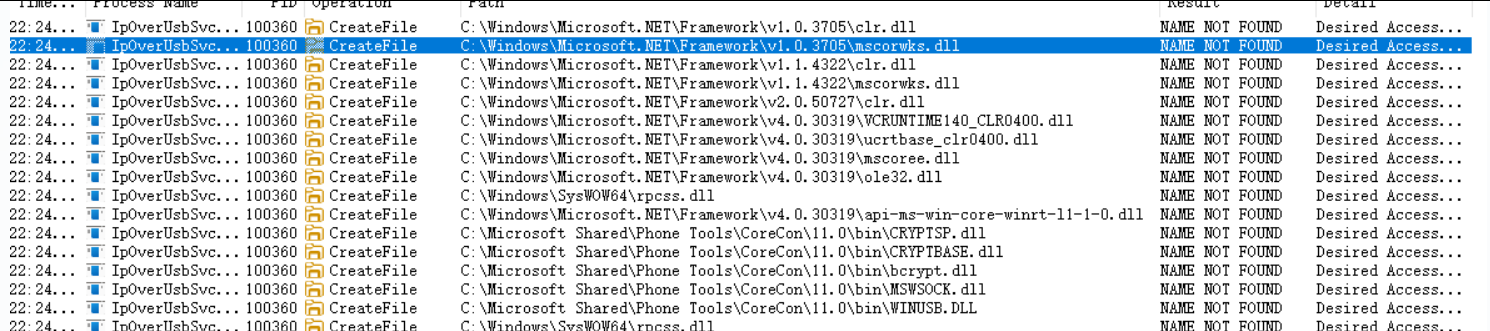
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
binary-exploitationexploitationlateral-movement+4
1 year ago
CVE-2025-47962-POC preview

CVE-2025-47962-POC

GitHubq1uf3ng/cve-2025-47962-poc

Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
binary-exploitationexploitationlateral-movement+2
410 months ago
LocalPotato_CVE-2023-21746 preview

LocalPotato_CVE-2023-21746

GitHubmuhammad-ali007/localpotato_cve-2023-21746

Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
binary-exploitationexploitationlateral-movement+5
33 years ago
TeamViewer_Permissions_Hook_V1 preview

TeamViewer_Permissions_Hook_V1

GitHubgellin/teamviewer_permissions_hook_v1

A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
educationexploitationlateral-movement+5
3108 years ago
CVE-2024-34329 preview

CVE-2024-34329

GitHubpamoutaf/cve-2024-34329

Proof-of-concept exploit for a local privilege escalation vulnerability in Datacard XPS Card Printer Driver via insecure file permissions and DLL…
binary-exploitationexploitationlateral-movement+2
2 years ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

A C2 post-exploitation framework

command-and-controlencryption-decryption-toolslateral-movement+7
4862 years ago
Previous12Next