
CVE-2024-38472
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
command-and-controlexploit-frameworkslateral-movement+6
4
abdurahmon3236/cve-2024-38472Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 sarpantkeltiek/cve-2024-37010
Exploit for the CVE-2024-37010: access other user's external storage & lateral movement
 charlesgargasson/cve-2024-32002
Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
 0xbinder/cve-2024-0044
CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13
 rayngnpc/cve-2024-49019-rayng
Exploitation for CVE-2024-49019
 cybersecplayground/cve-2024-48887-fortiswitch-exploit
a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 0nin0hanz0/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated file read in Check Point Security Gateways; scans single or multiple IP targets and…
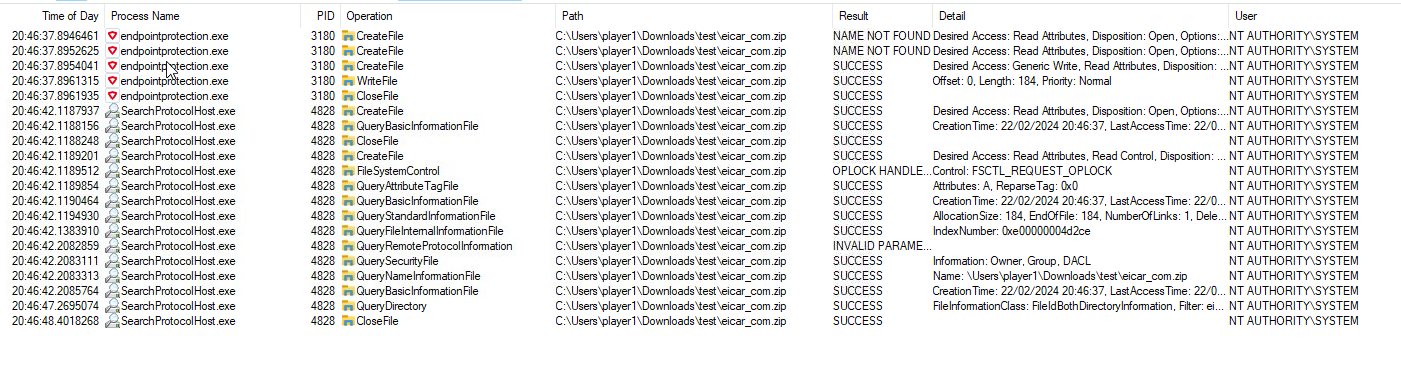 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…