
redsnarf
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
command-and-controlexploitationhash-analysis+9
nccgroup/redsnarfRedSnarf is a pen-testing / red-teaming tool for Windows environments
 redcode-labs/neurax
A framework for constructing self-spreading binaries
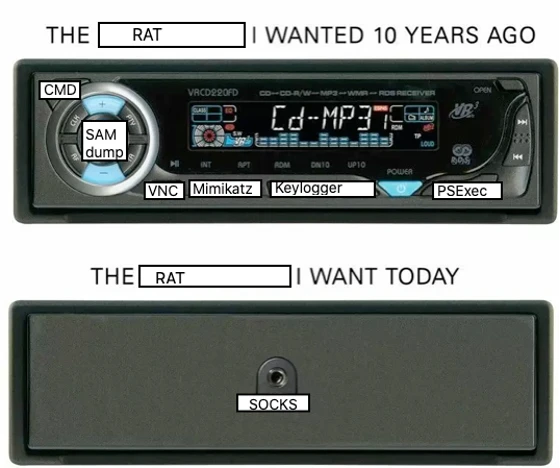 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
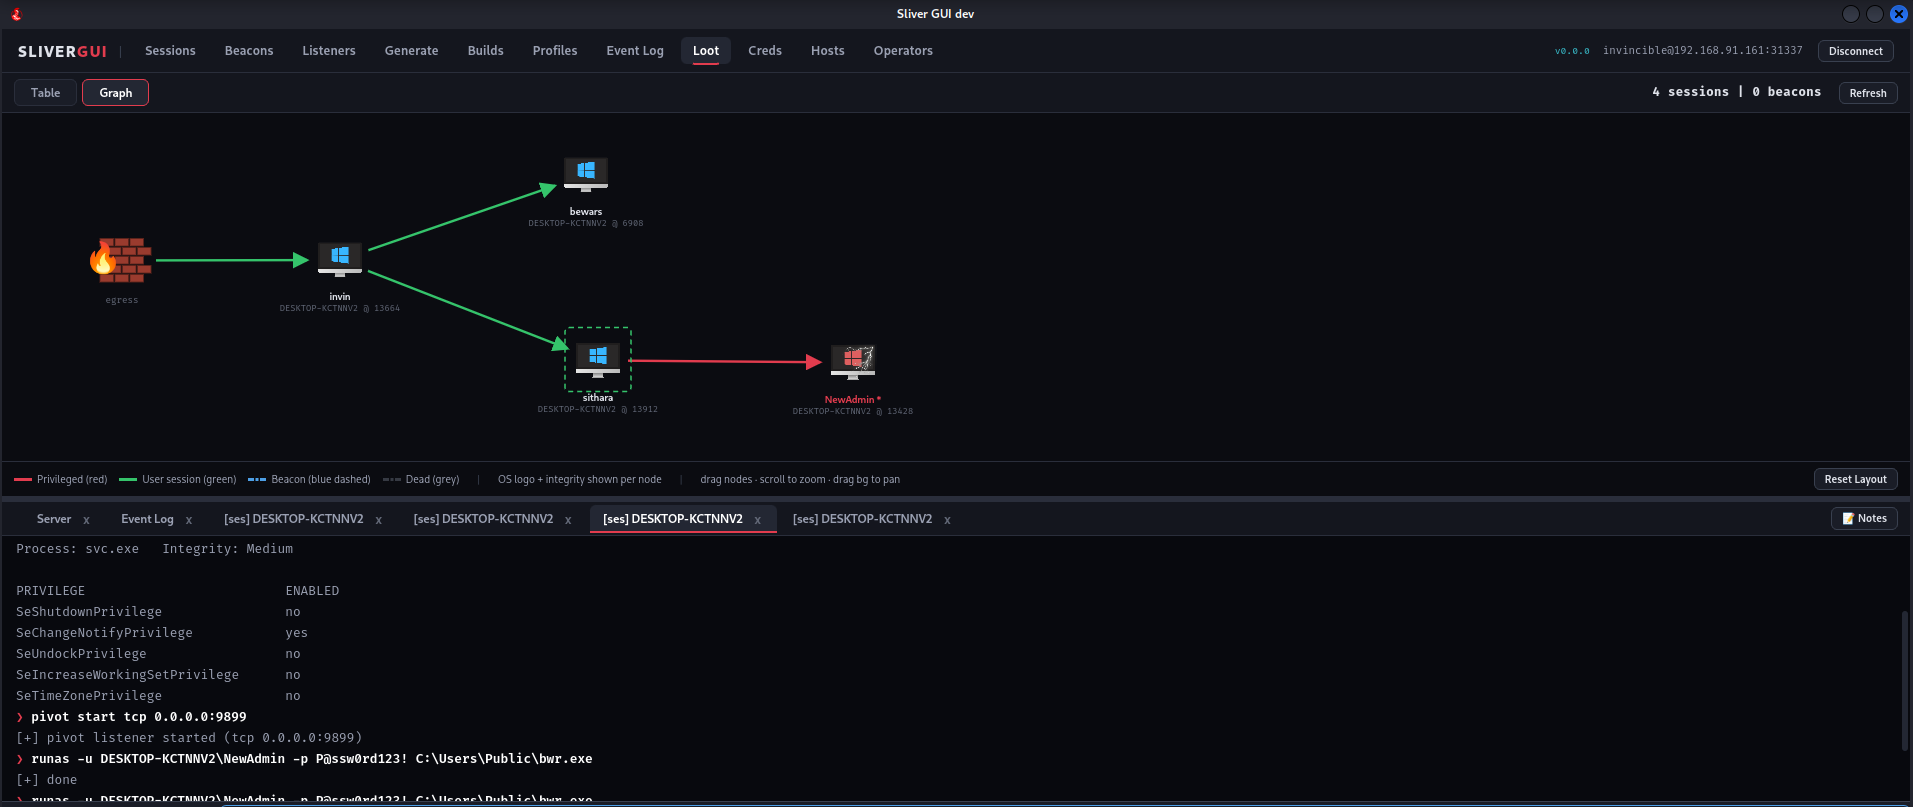 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 0xbbuddha/hermes
A Python agent targeting Linux for Mythic C2
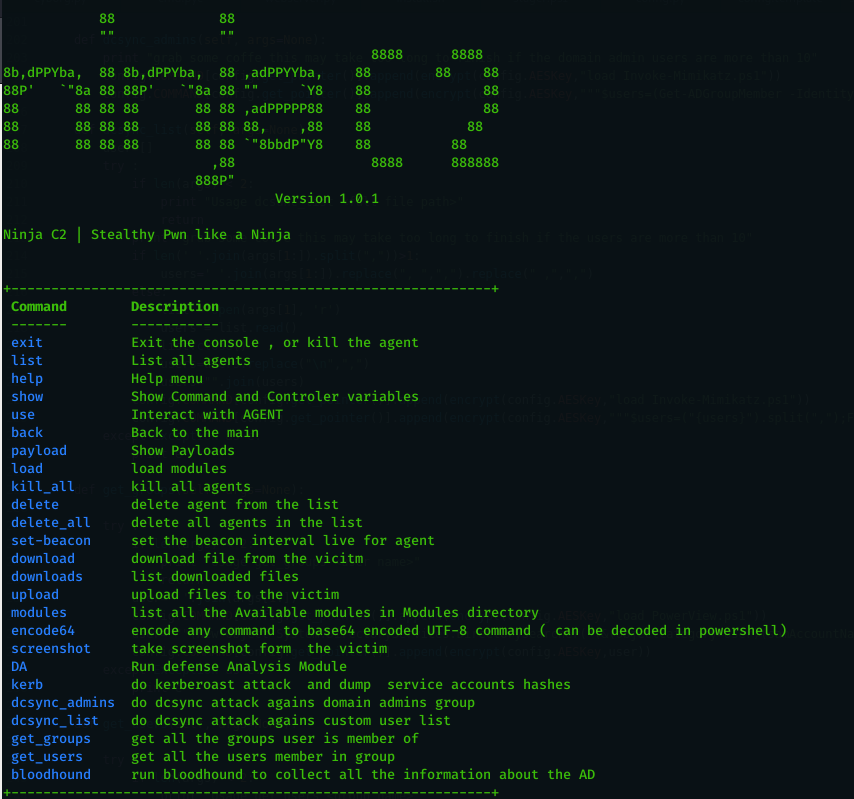 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
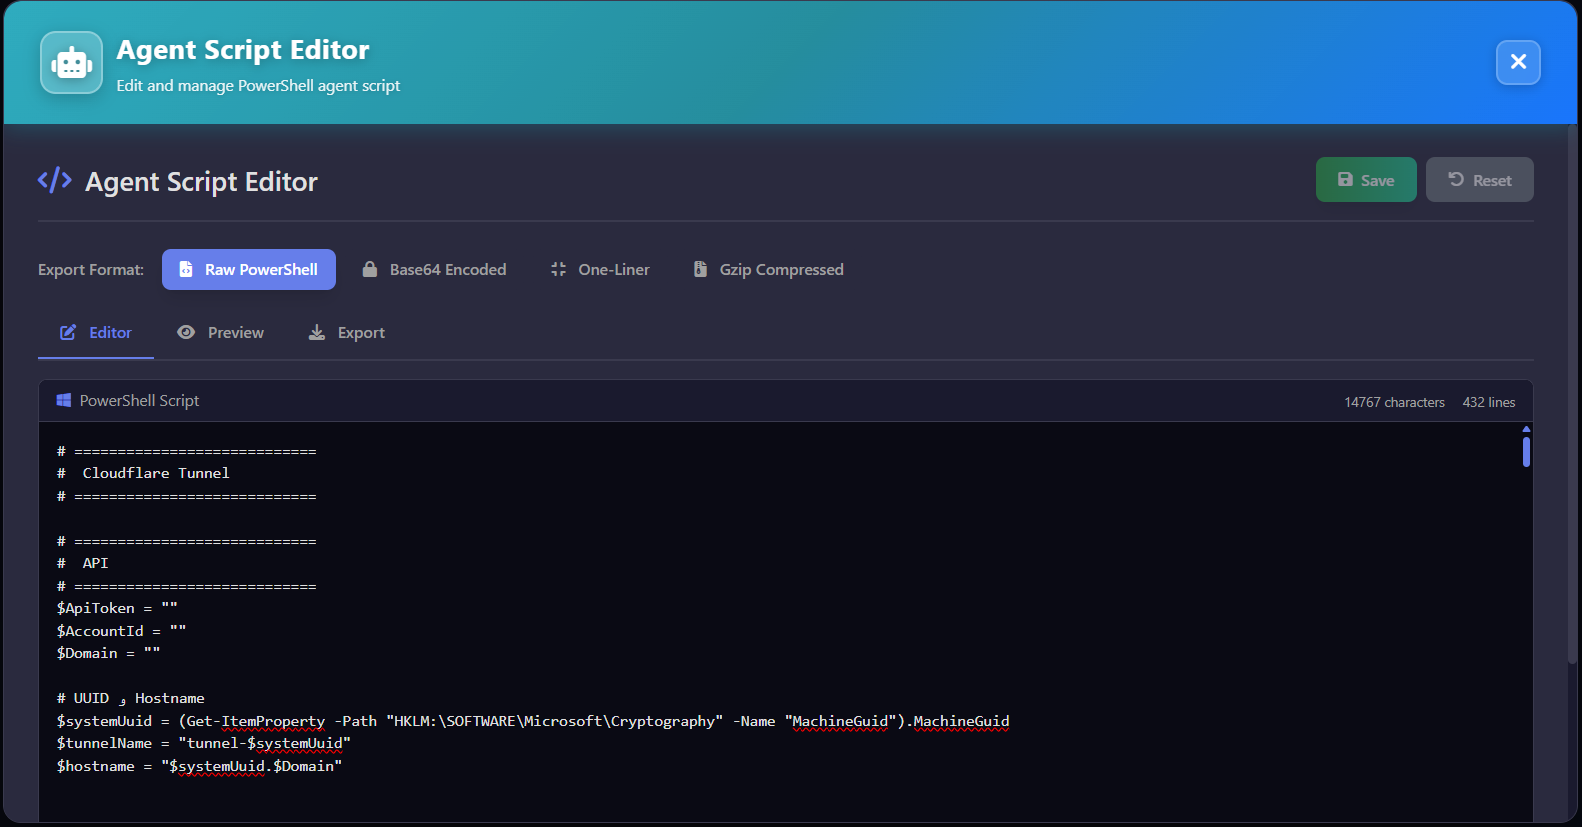 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
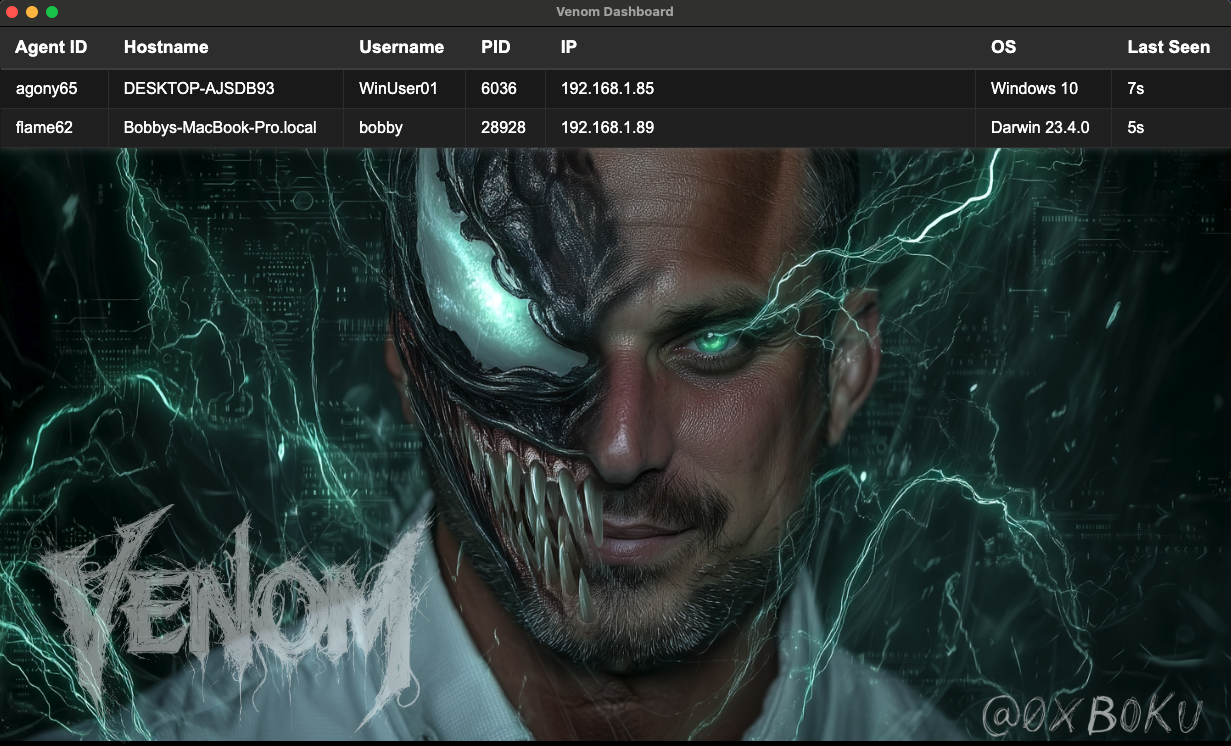 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence