Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
125 results
azure-pentesting-suite preview

azure-pentesting-suite

GitHubhac01/azure-pentesting-suite

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

cloud-securitydata-exfiltrationinformation-gathering+9
921 month ago
Wormy preview

Wormy

GitHubd4vinci/wormy

some python3 functions to add spreading features to any python backdoor

command-and-controldata-exfiltrationlateral-movement+3
559 years ago
pentestkoala preview

pentestkoala

GitHubmrschyte/pentestkoala

Modified dropbear server which acts as a client and allows authless login

data-exfiltrationlateral-movementpenetration-testing+3
1258 years ago
BetterRAT preview

BetterRAT

GitHubmwsrc/betterrat

Better Remote Access Trojan

command-and-controldata-exfiltrationlateral-movement+5
539 years ago
ZeroRAT preview

ZeroRAT

GitHub5alt/zerorat

ZeroRAT是一款windows上的一句话远控

command-and-controldata-exfiltrationexploitation+9
6310 years ago
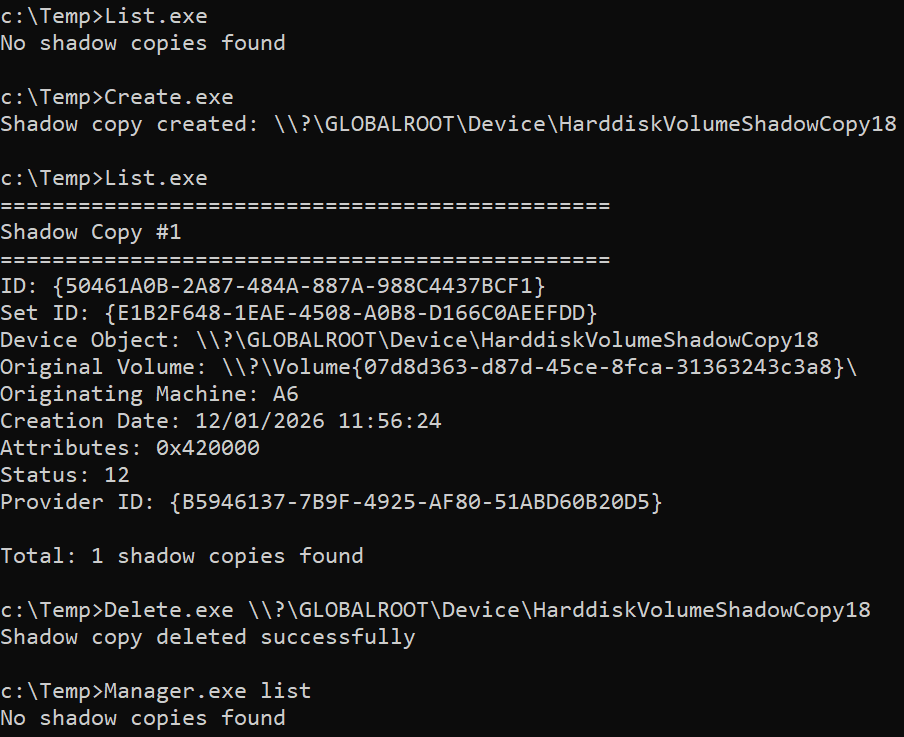
w11_shadow_copies preview

w11_shadow_copies

GitHubricardojoserf/w11_shadow_copies

Manage Shadows Copies via the VSS API using C#, C++, Crystal or Python. Working on Windows 11

data-exfiltrationexploitationlateral-movement+5
849 months ago
loki preview

loki

GitHubnccgroup/loki

LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses

data-exfiltrationlateral-movementpenetration-testing+3
6310 years ago
phantom-keylogger preview

phantom-keylogger

GitHubmattiaalessi/phantom-keylogger

Phantom Keylogger is an advanced, stealth-enabled keystroke and visual intelligence gathering system.

command-and-controldata-exfiltrationids-ips-evasion+6
7710 months ago
reave preview

reave

GitHubpsmths/reave

WIP Post-exploitation framework tailored for hypervisors.

command-and-controldata-exfiltrationexploit-frameworks+8
503 years ago
SkyRAT preview

SkyRAT

GitHubyschgroup/skyrat

SkyRAT - Powershell Remote Administration Tool

command-and-controldata-exfiltrationlateral-movement+5
348 years ago
ConfluenceC2 preview

ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

command-and-controldata-exfiltrationlateral-movement+9
2314 days ago
Schwarze-Sonne-RAT preview

Schwarze-Sonne-RAT

GitHubmwsrc/schwarze-sonne-rat

SS-RAT (Schwarze-Sonne-Remote-Access-Trojan)

command-and-controldata-exfiltrationlateral-movement+6
299 years ago
bat preview

bat

GitHubrhzv0/bat

Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

command-and-controldata-exfiltrationlateral-movement+5
366 months ago
teletunnel preview

teletunnel

GitHubmhdgning131/teletunnel

Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !

command-and-controldata-exfiltrationids-ips-evasion+7
437 months ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API

command-and-controldata-exfiltrationexploitation+8
207 years ago
TospoVirus preview

TospoVirus

GitHubcatatonicprime/tospovirus

A WiFi Pineapple infecting worm.

command-and-controldata-exfiltrationexploitation+5
1711 years ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
26 days ago
CVE-2026-65660-Poc preview

CVE-2026-65660-Poc

GitHubshadowforge-cyber/cve-2026-65660-poc

Malicious Register Directive Code Injection Exploit

command-and-controldata-exfiltrationexploitation+8
11 month ago
Previous1234567Next