
EDD
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
information-gatheringlateral-movementpenetration-testing+2
334
redsiege/edd.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 n00py/outpacket
This cheatsheet maps common impacket workflows to their modern alternatives
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
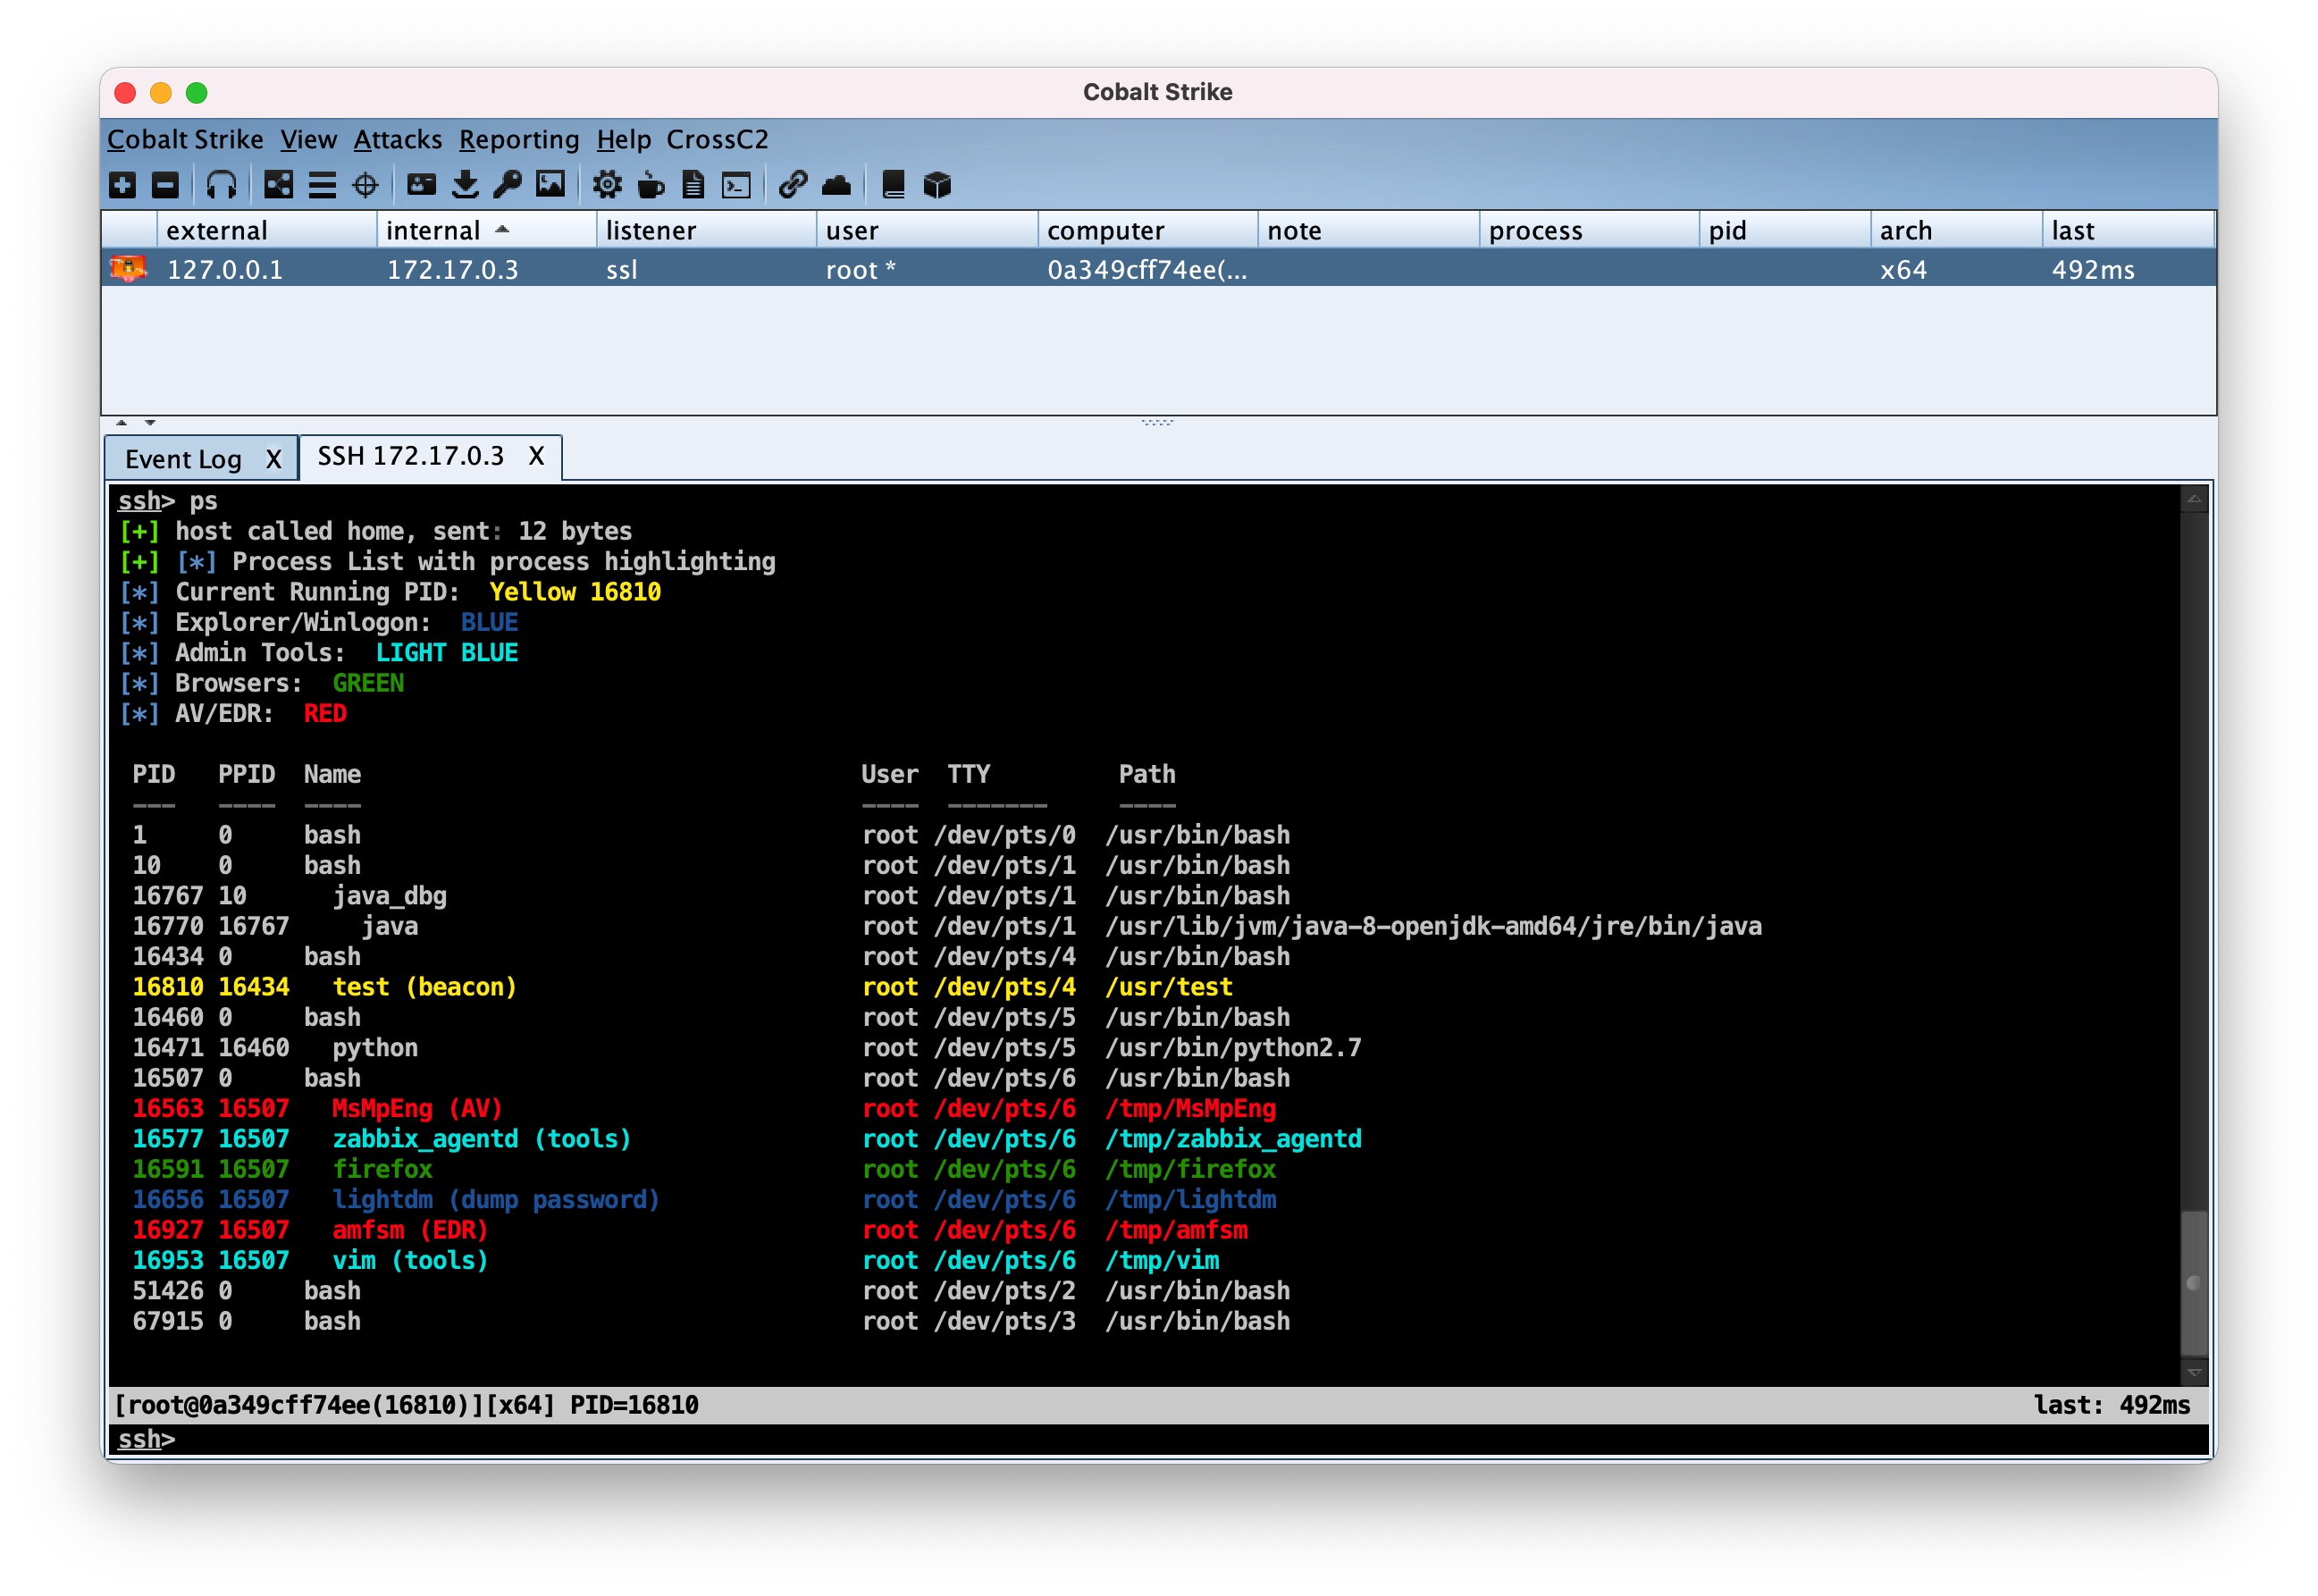 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
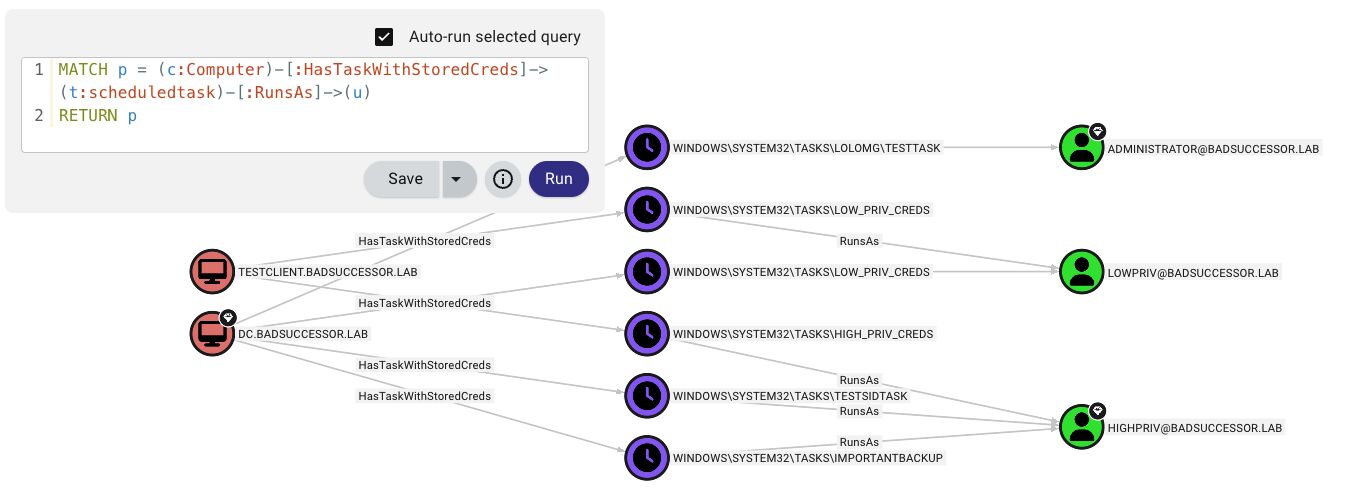 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 mayyhem/maestro
Abusing Azure services over C2
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 malwaretech/trickbot-toolkit
A collection of tools for dealing with TrickBot
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 maaaaz/crackmapexecwin
The great CrackMapExec tool compiled for Windows