
CobaltStrike-Toolset
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
command-and-controlexploit-frameworkslateral-movement+8
qax-a-team/cobaltstrike-toolsetAggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
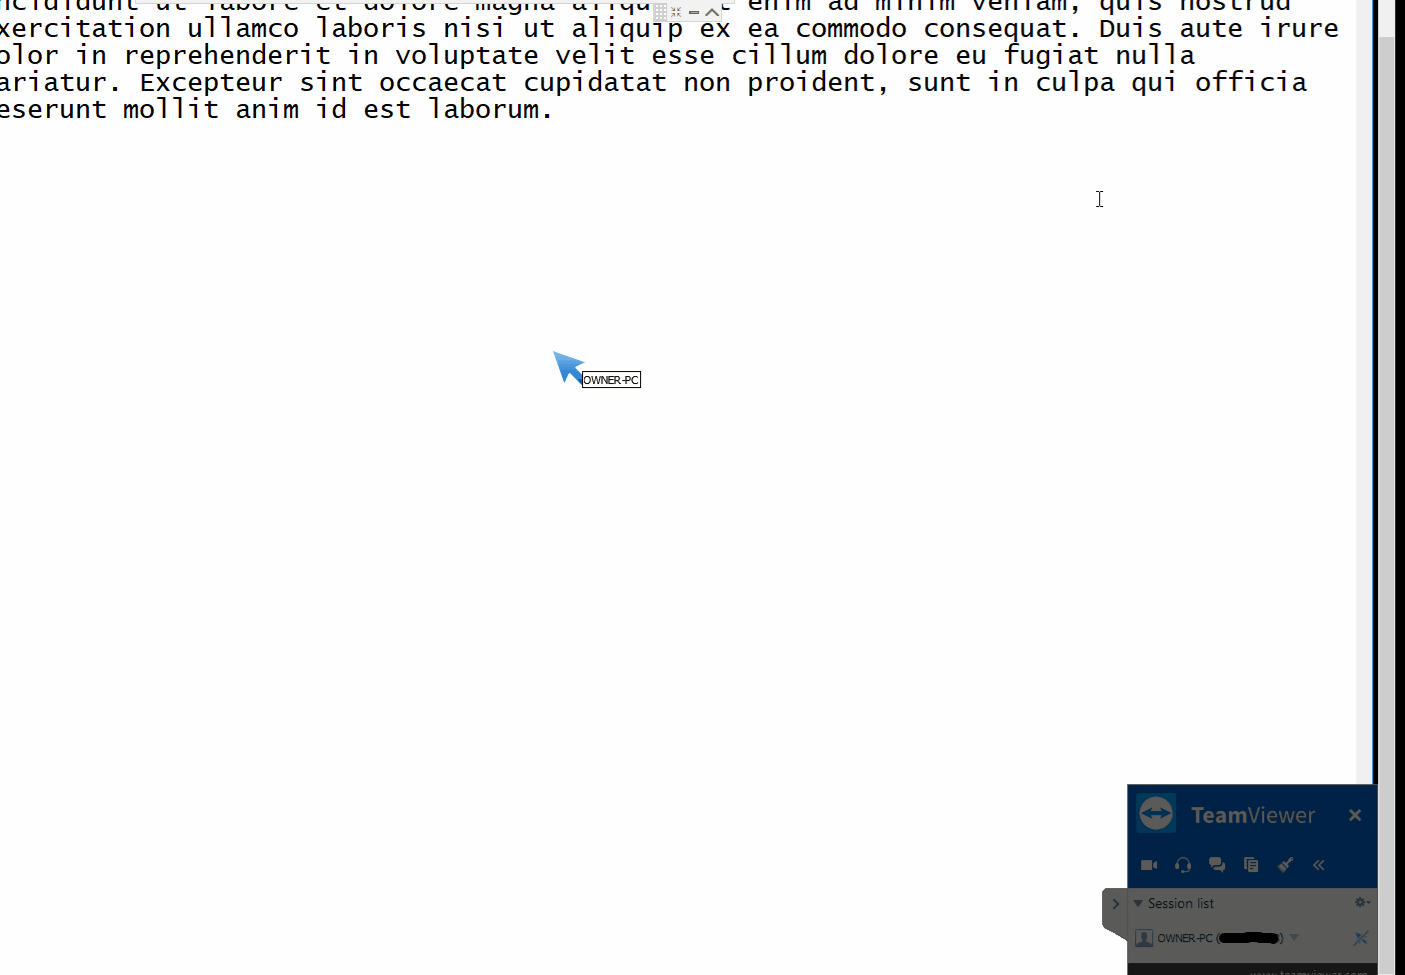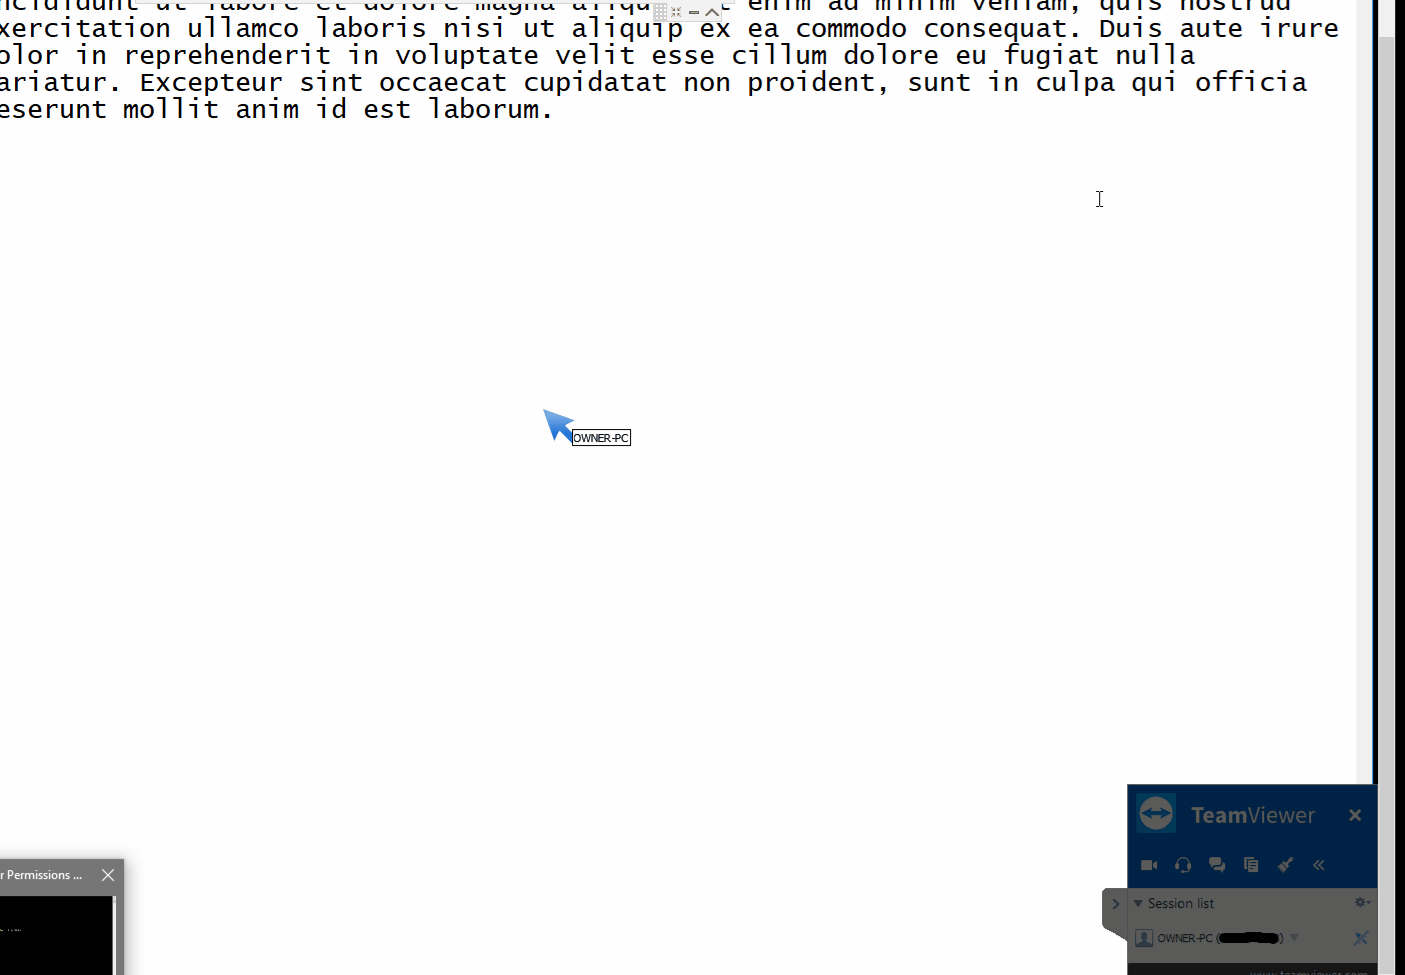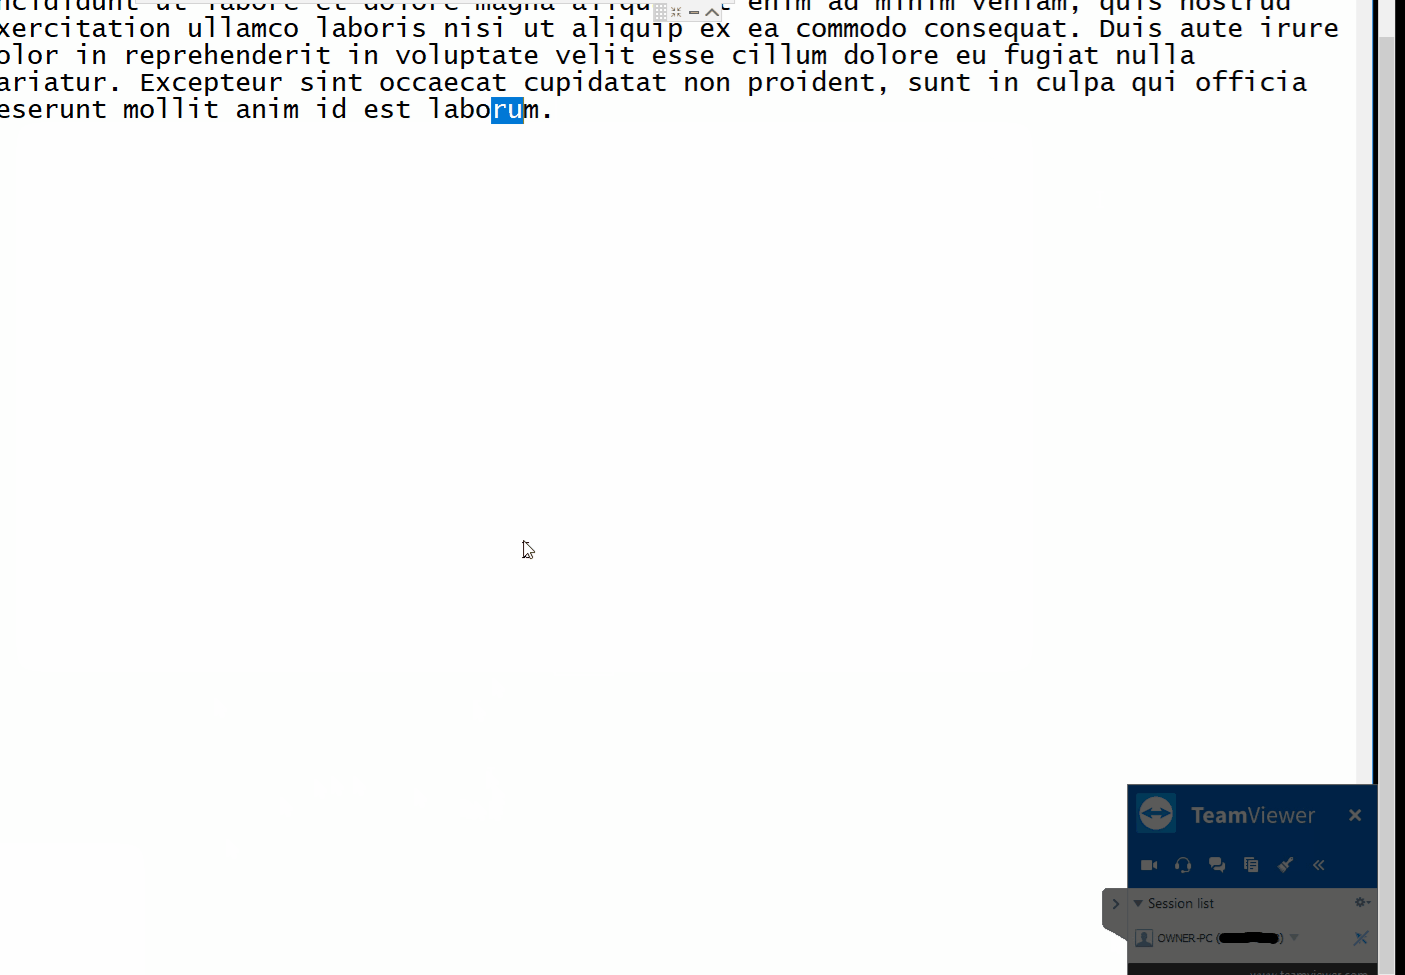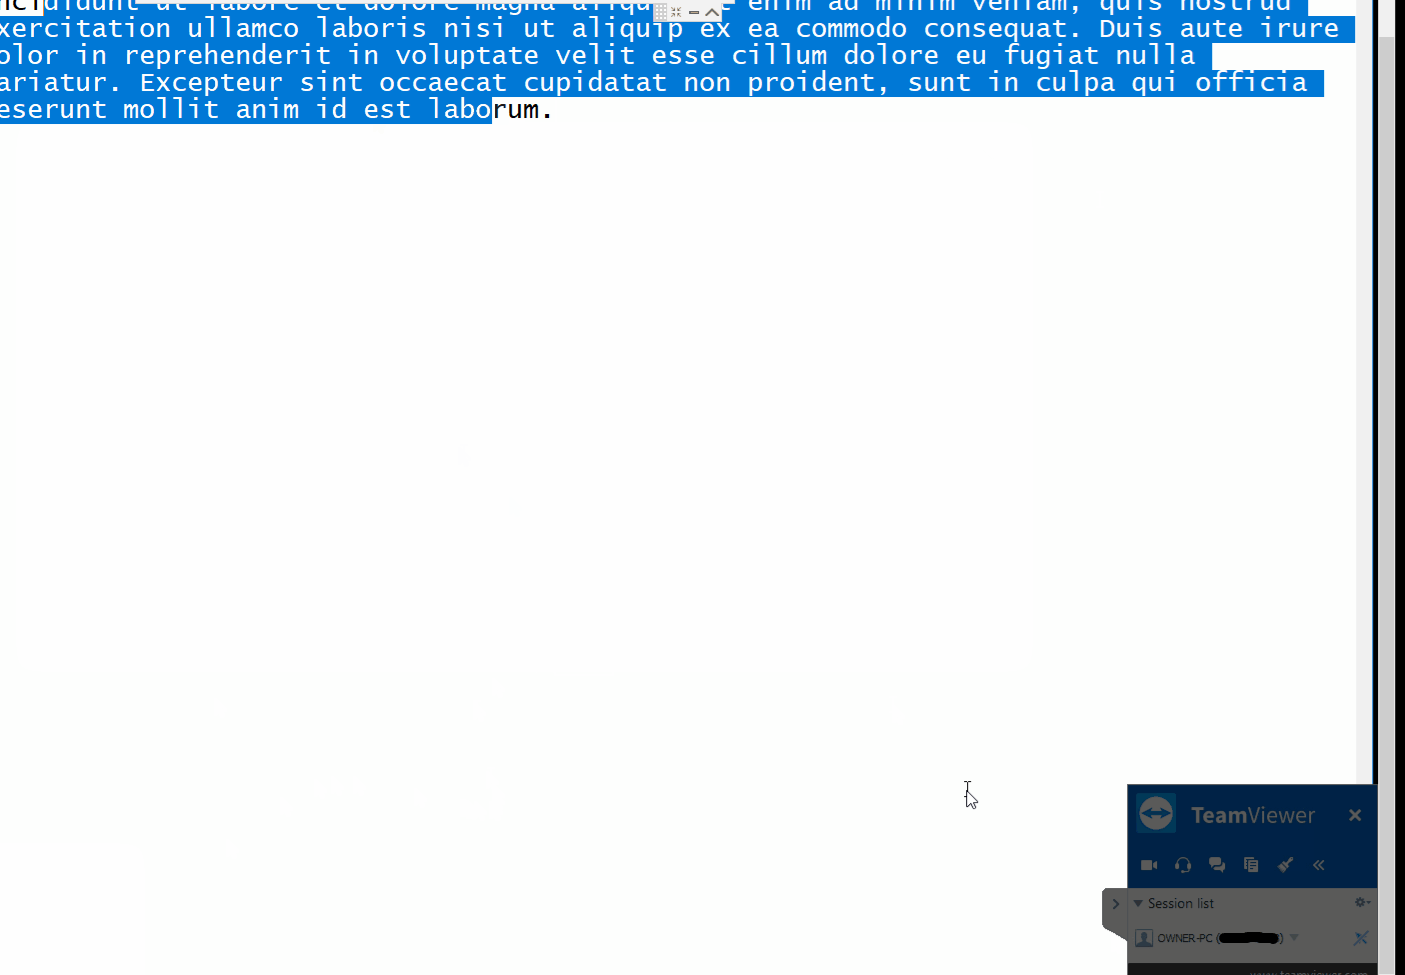 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
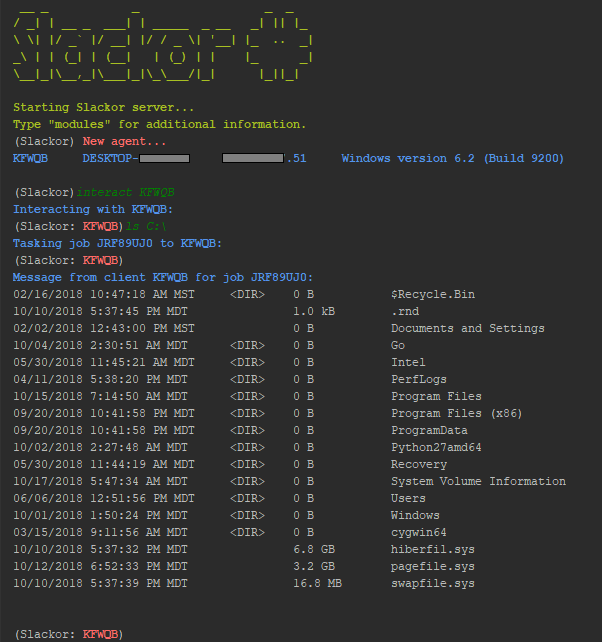 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 nettitude/poshc2_old
Powershell C2 Server and Implants
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
 d4rk007/redghost
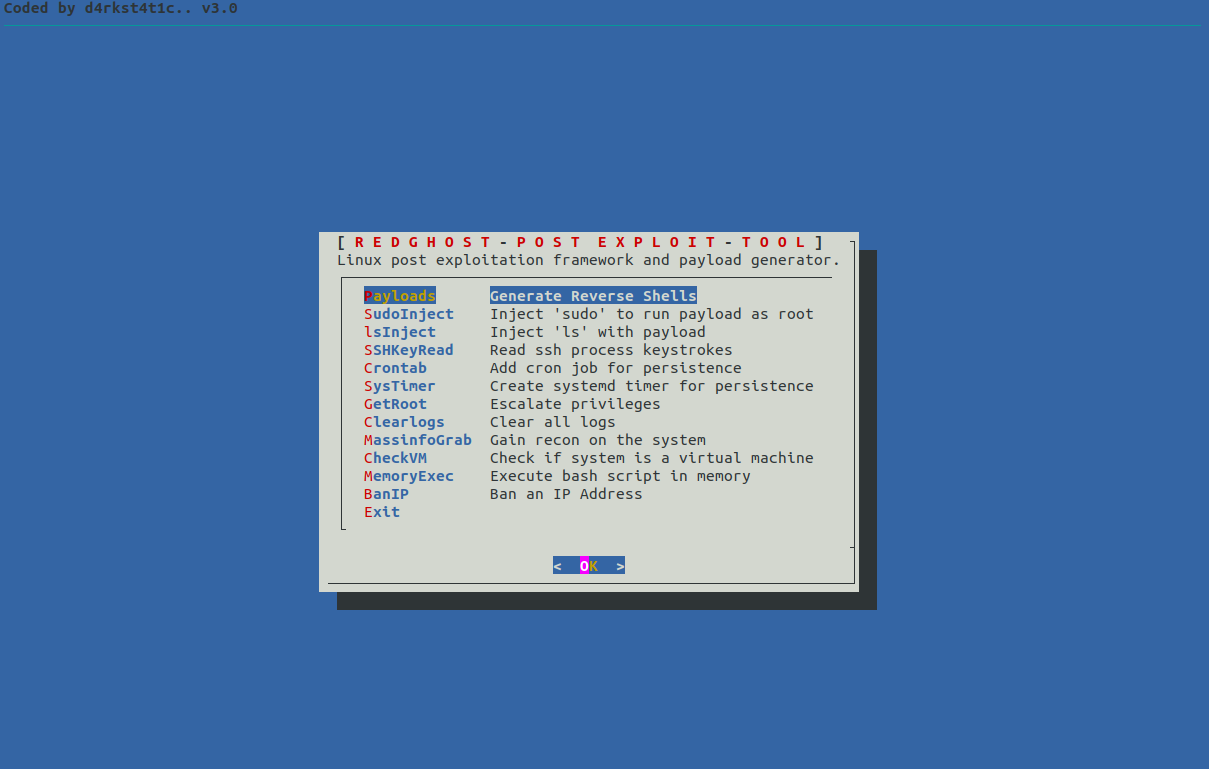
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 kudaes/lolbits
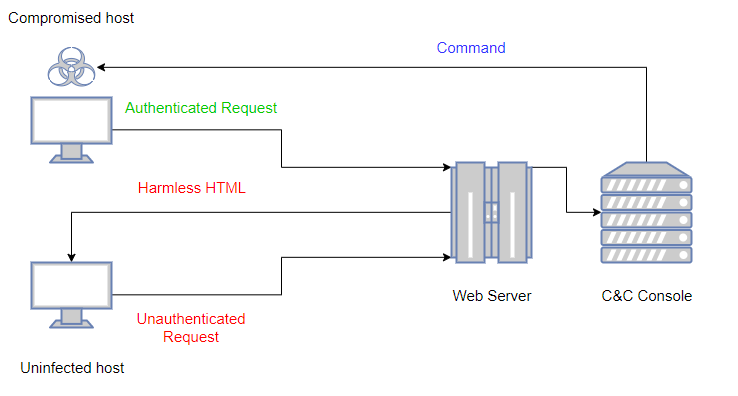
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
 yaxser/cobaltstrike-bof
Collection of beacon BOF written to learn windows and cobaltstrike