
AD-PathFinder
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
exploitationinformation-gatheringlateral-movement+7
95
netspi/ad-pathfinderAttack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 maaaaz/crackmapexecwin
The great CrackMapExec tool compiled for Windows
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
 xforcered/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 crowdstrike/sccmhound
A BloodHound collector for Microsoft Configuration Manager
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…
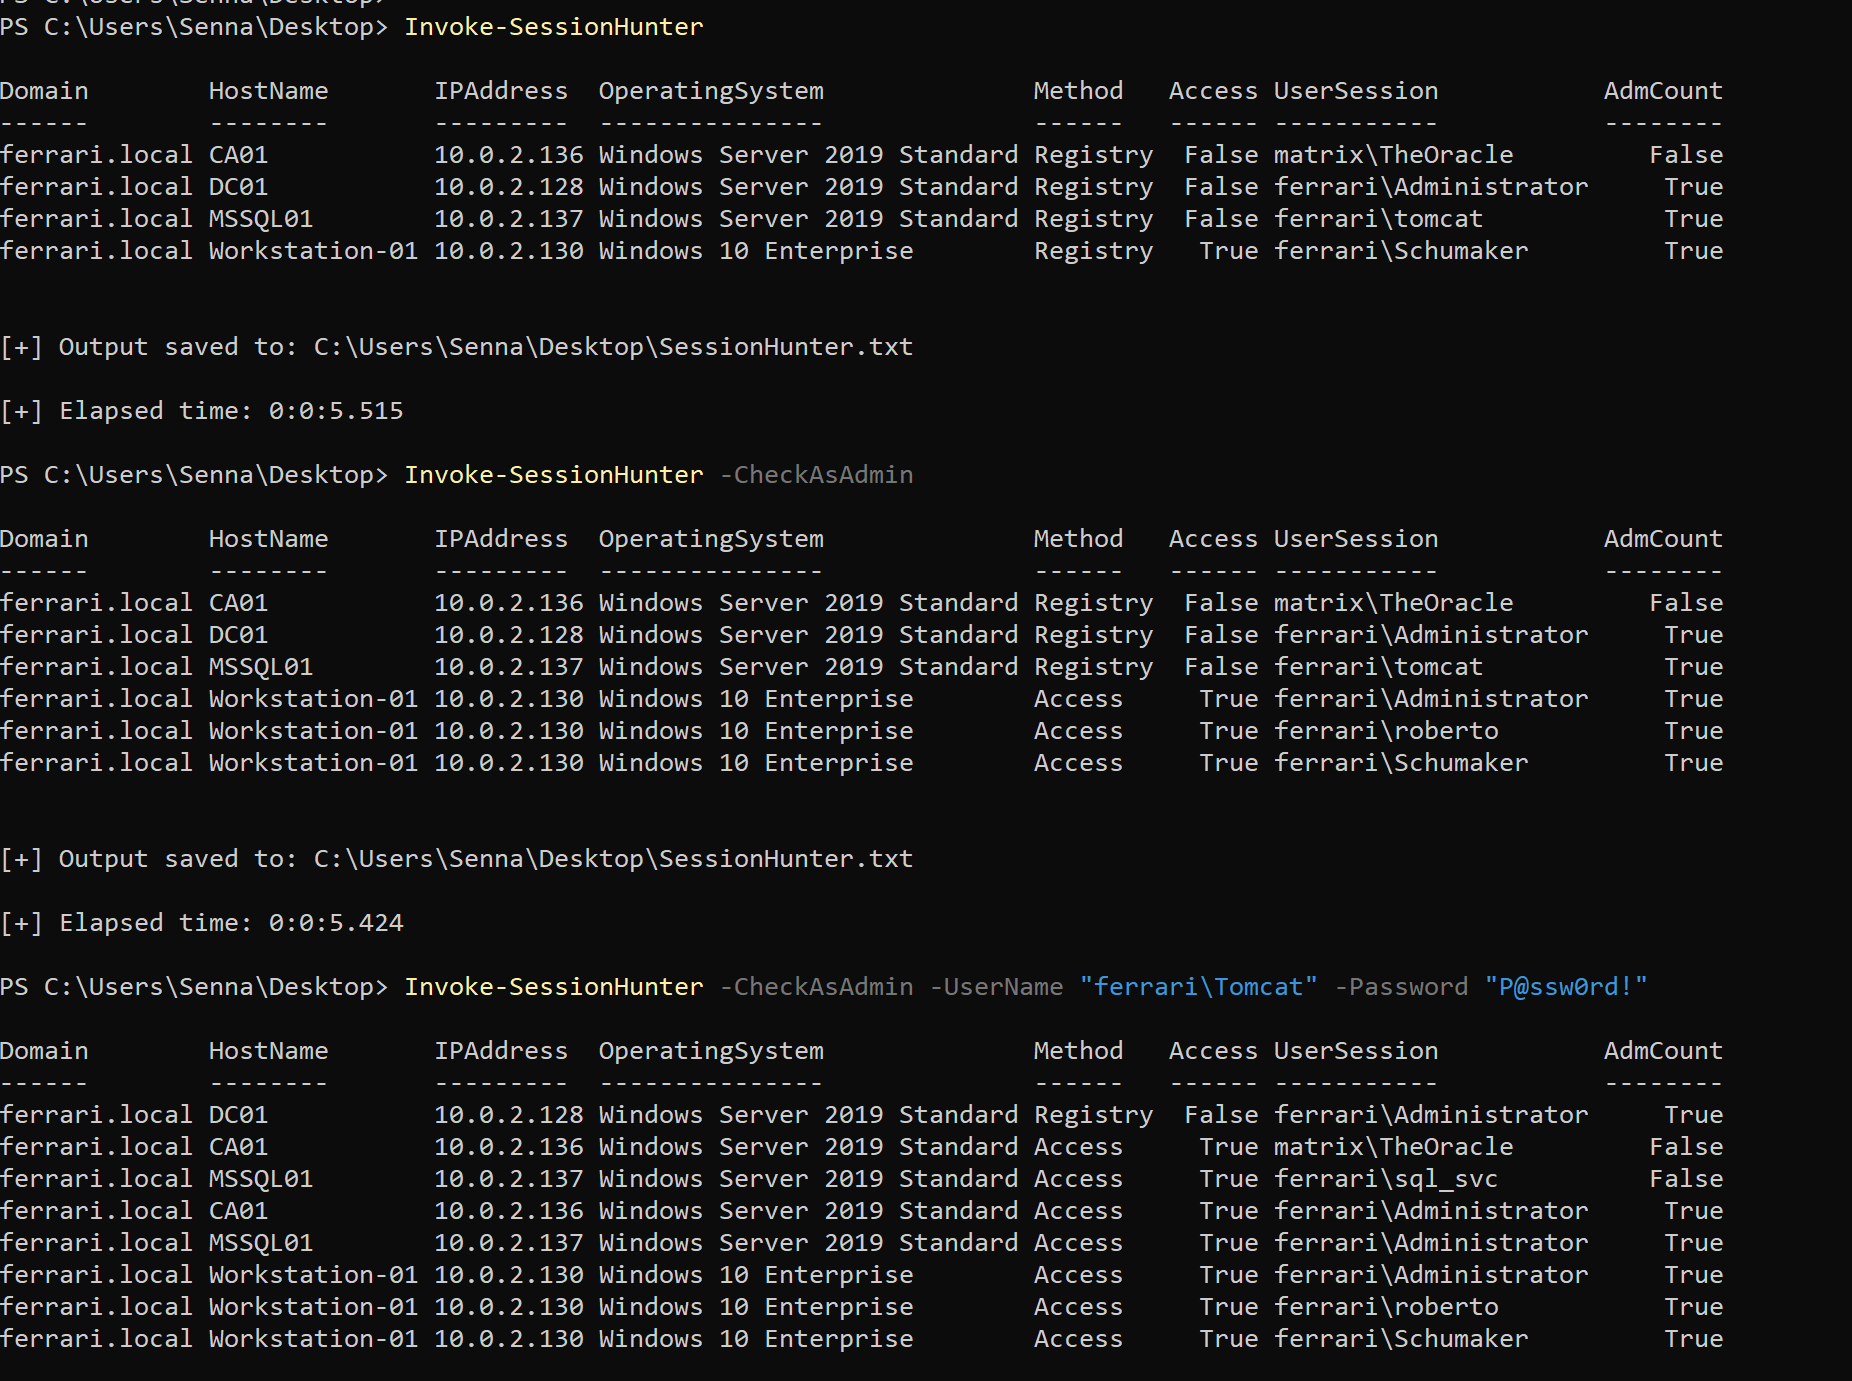 leo4j/invoke-sessionhunter
Retrieve and display information about active user sessions on remote computers. No admin privileges required.
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
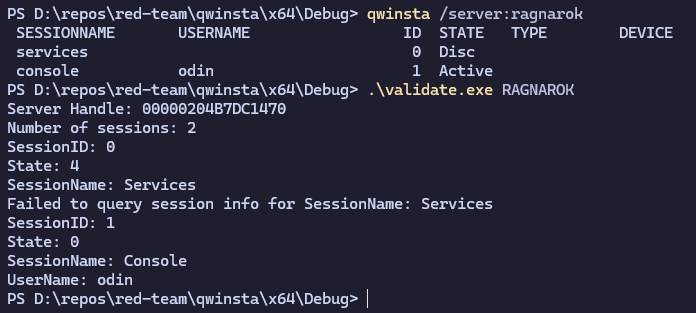 0xv1n/remotesessionenum
Remotely Enumerate sessions using undocumented Windows Station APIs
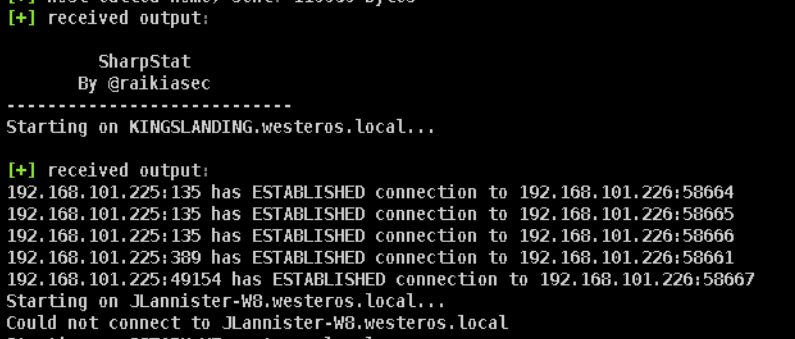 raikia/sharpstat
C# utility that uses WMI to run "cmd.exe /c netstat -n", save the output to a file, then use SMB to read and delete the file remotely
 syss-research/ldap-swak
LDAP Swiss Army Knife
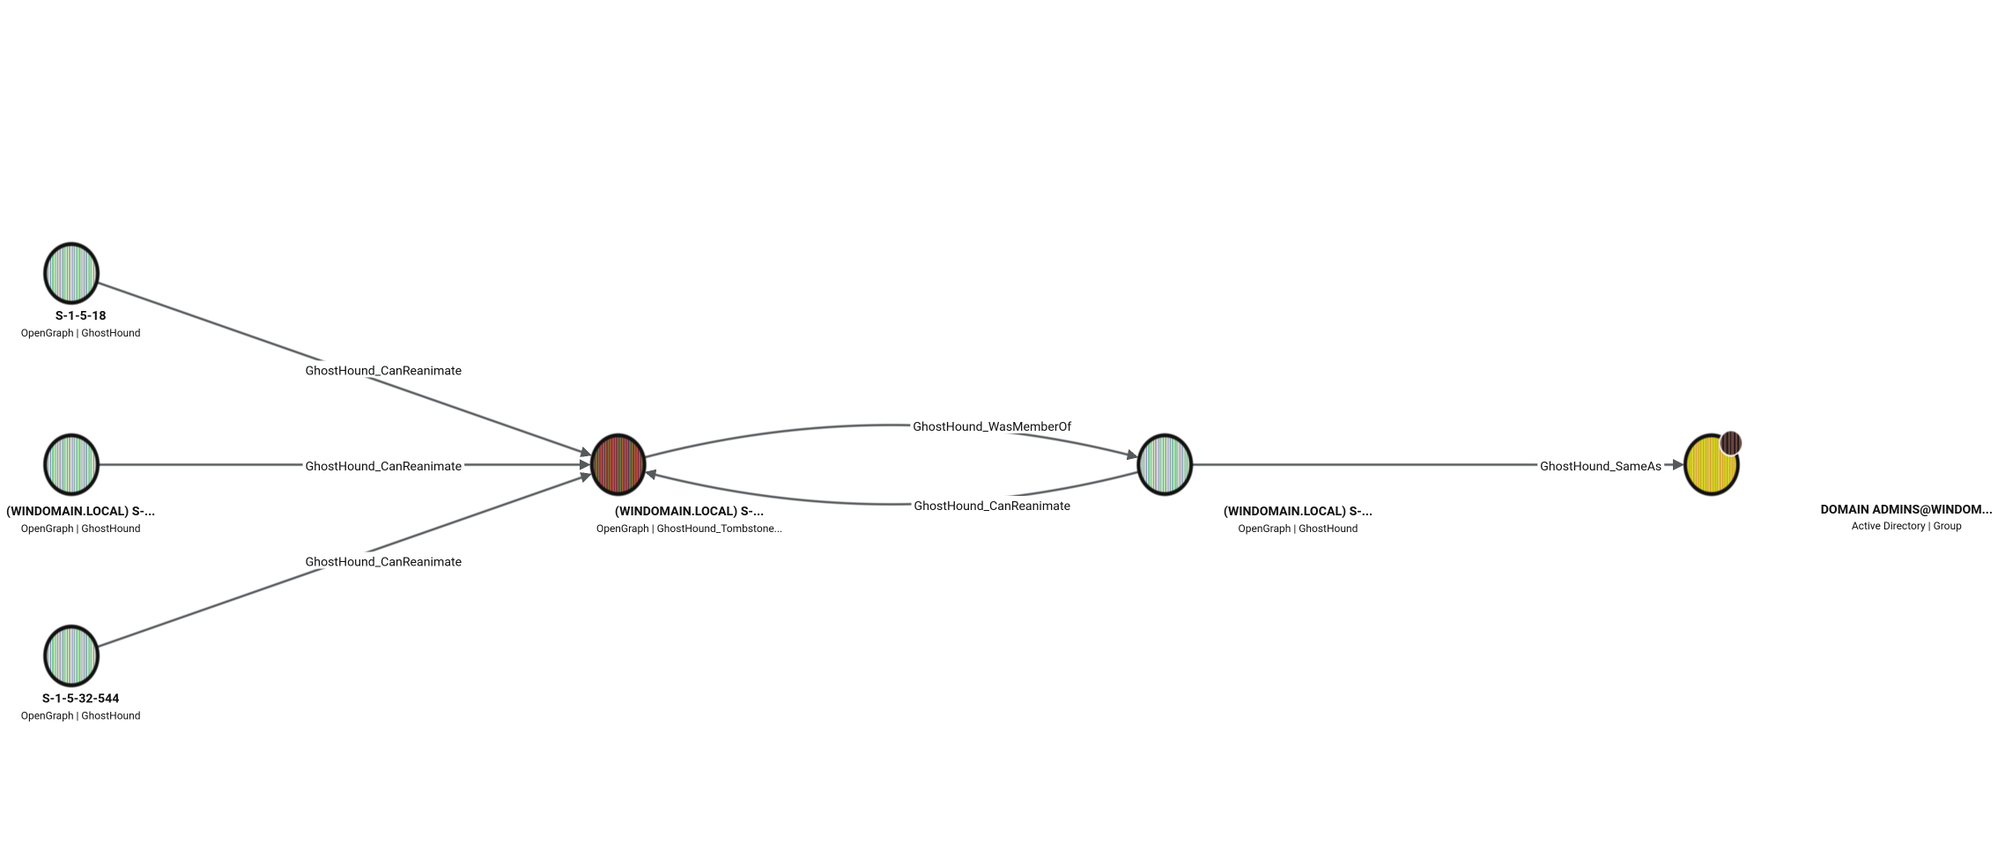 jvbotelho/ghosthound
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE