

CLSIDFinder
 0xqn/clsidfinder
PowerShell enumeration script for discovering service-backed COM objects via CLSID/AppID correlation and activation testing.
information-gatheringlateral-movementpenetration-testing+3
3
0xqn/clsidfinderPowerShell enumeration script for discovering service-backed COM objects via CLSID/AppID correlation and activation testing.
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
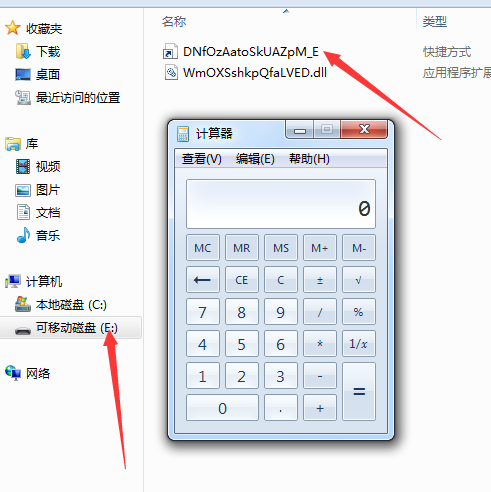 xssfile/cve-2017-8464-exp
Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and…
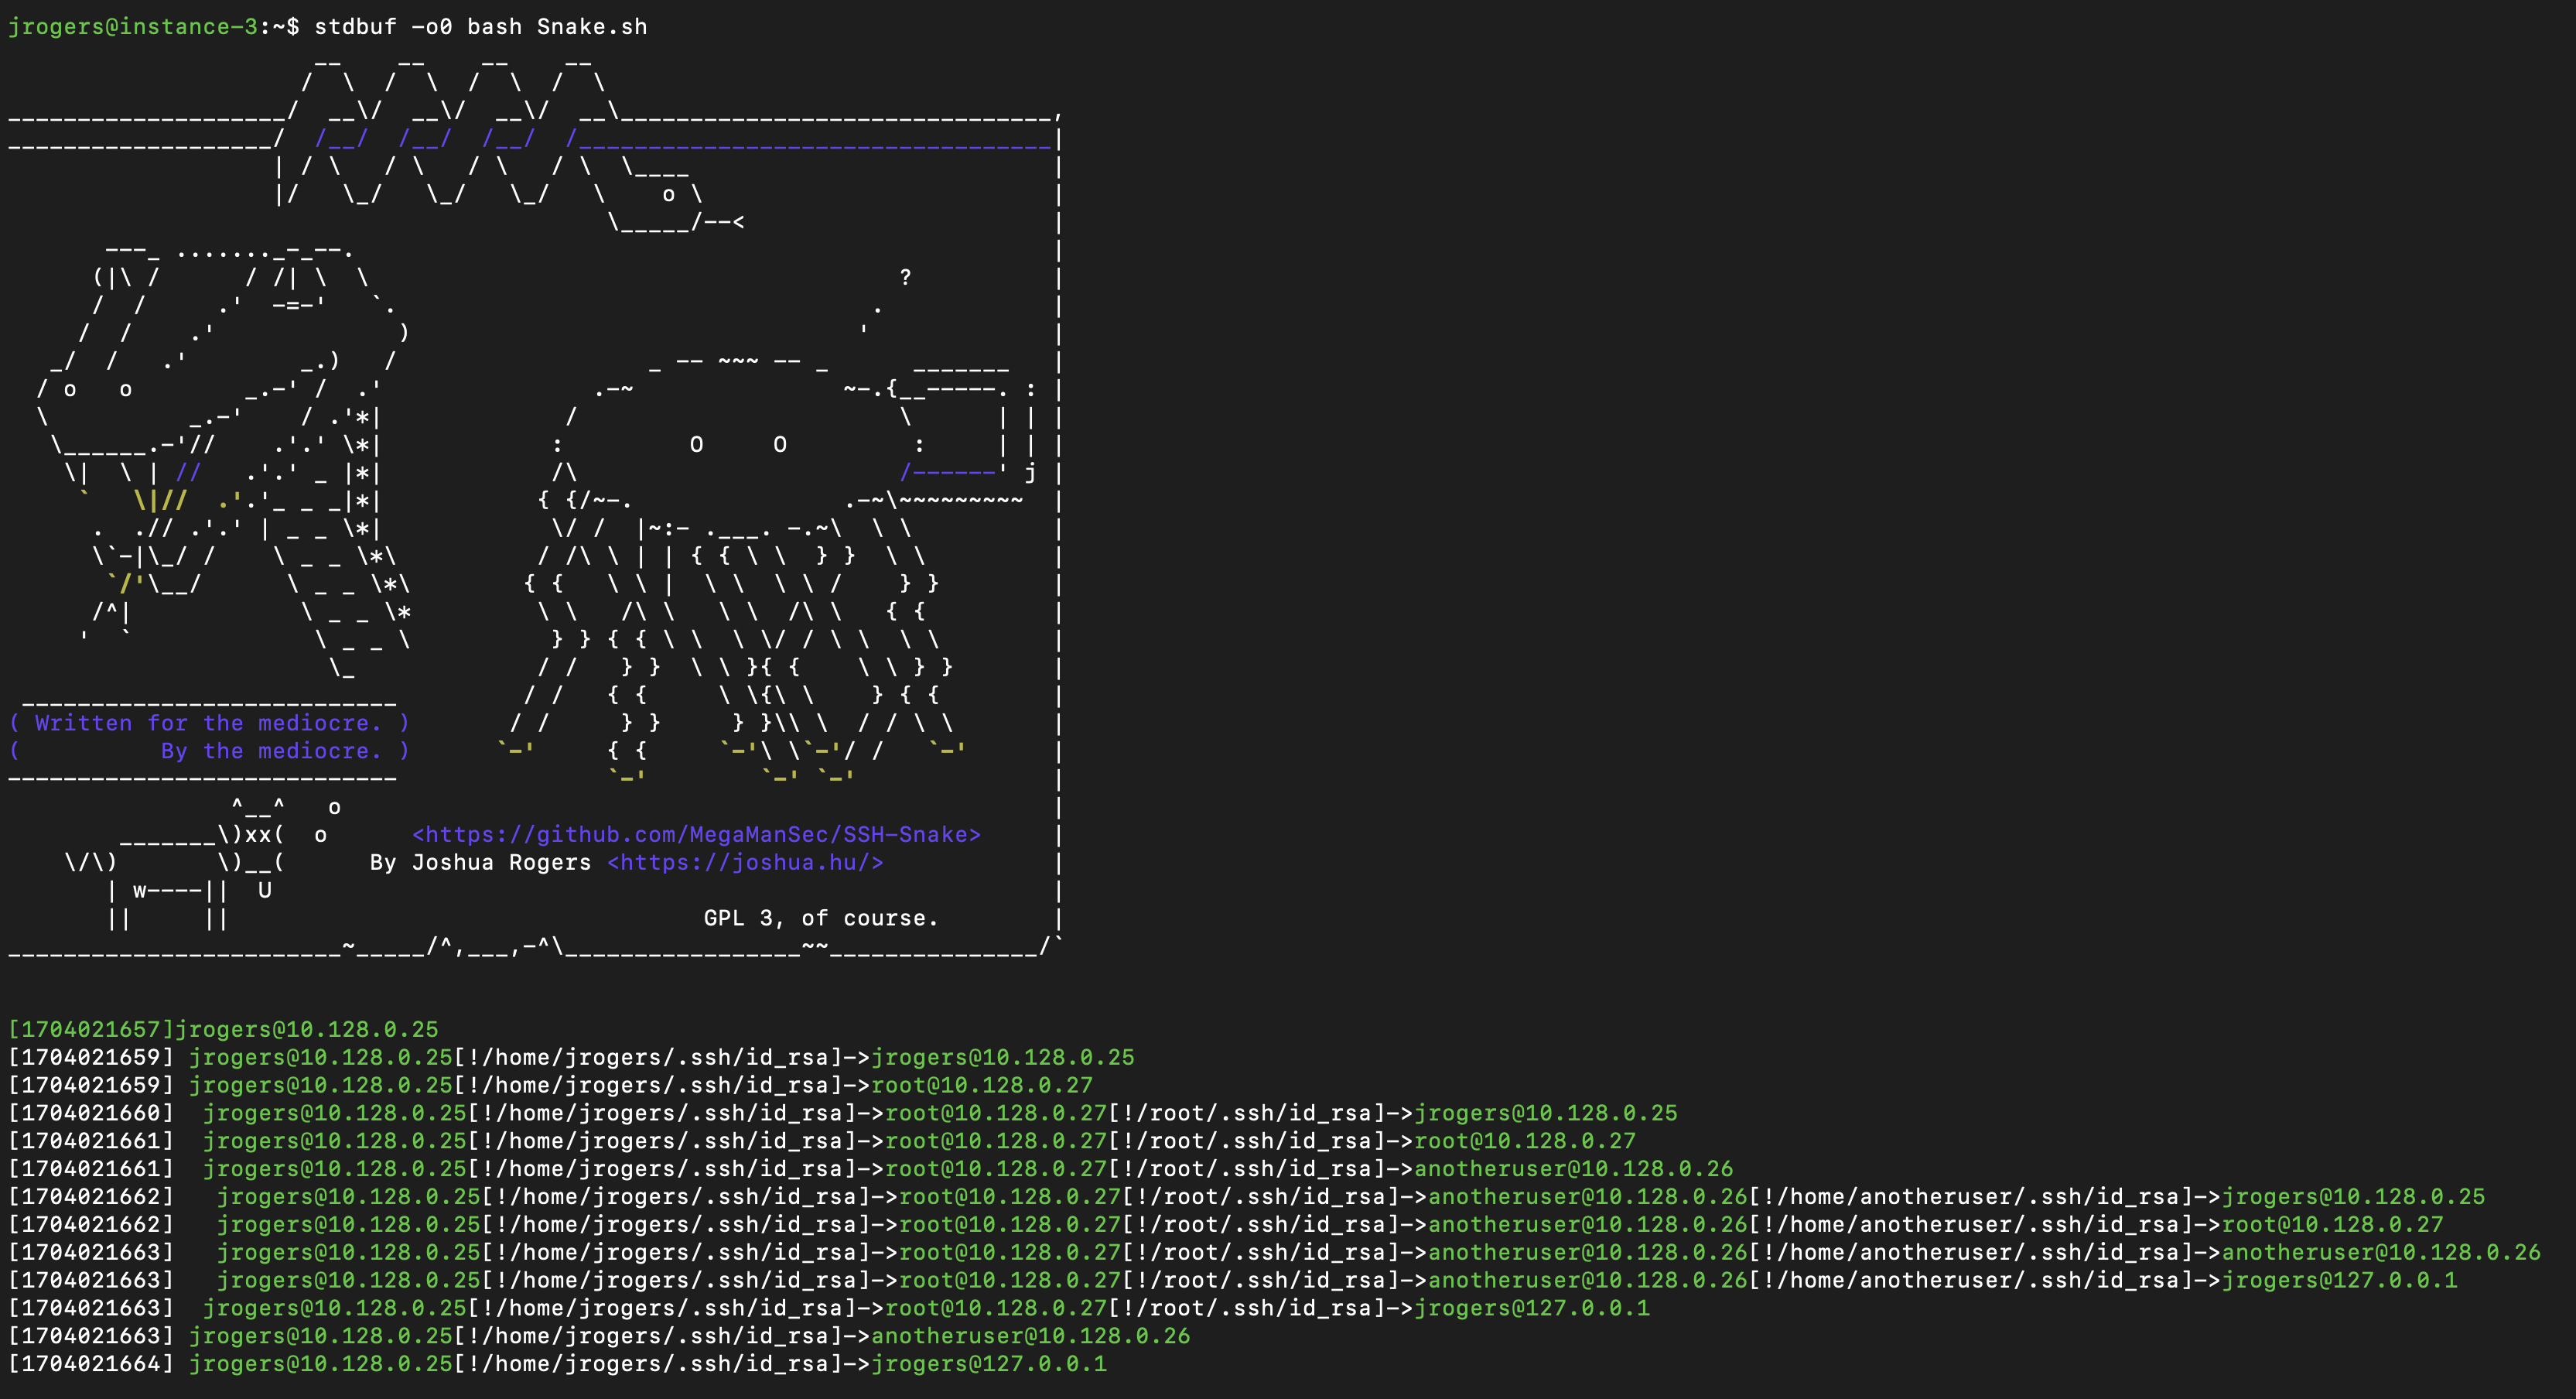 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 bishopfox/sliver
Adversary Emulation Framework
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 b23r0/heroinn
A cross platform C2/post-exploitation framework.