
Archived
ssh-mitm
 jtesta/ssh-mitm
SSH man-in-the-middle tool
authenticationids-ips-evasioninformation-gathering+6
1.7k
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
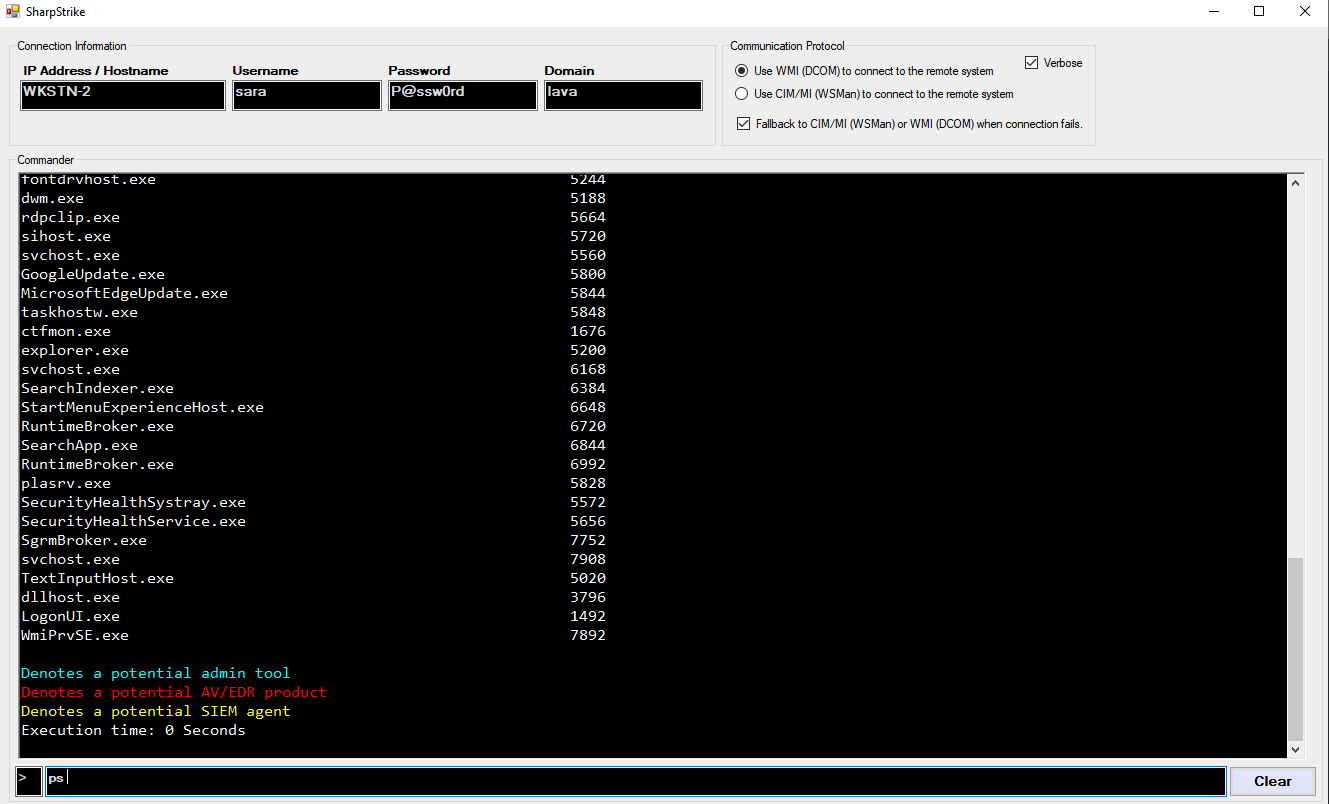 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…