
BloodHound.py
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
information-gatheringlateral-movementpenetration-testing+3
2.4k1 year ago
dirkjanm/bloodhound.pyA Python based ingestor for BloodHound
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
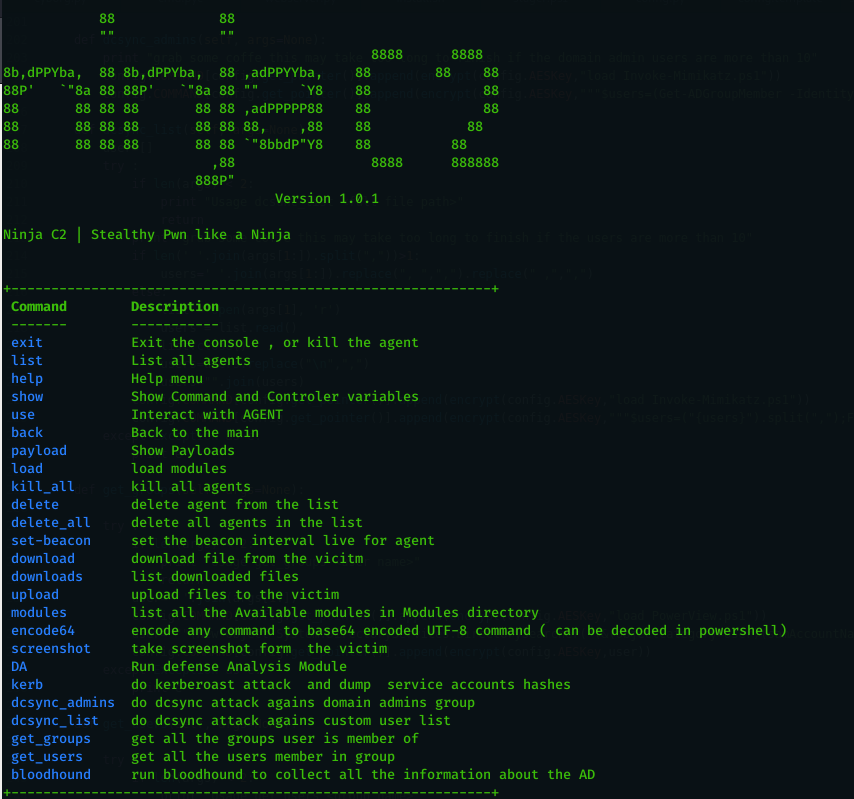 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
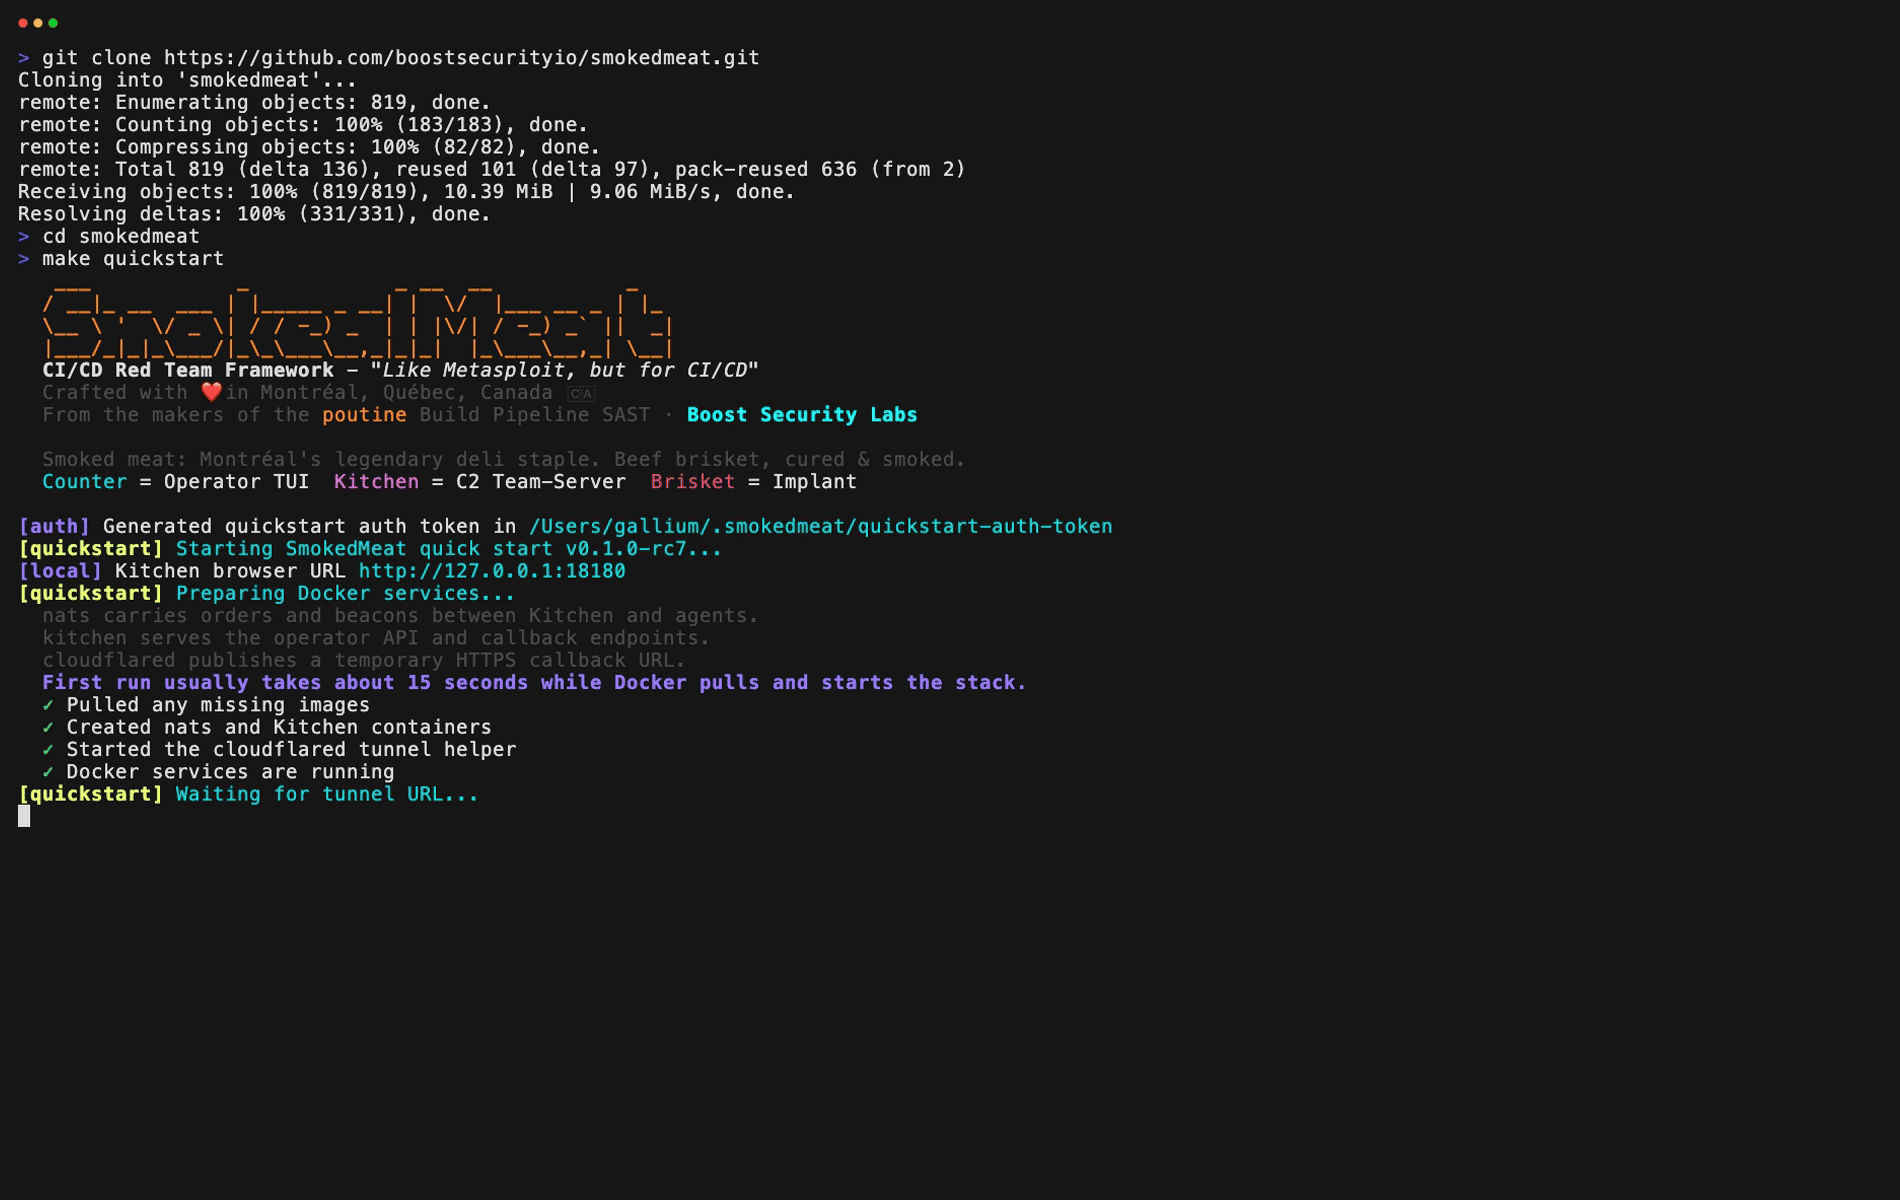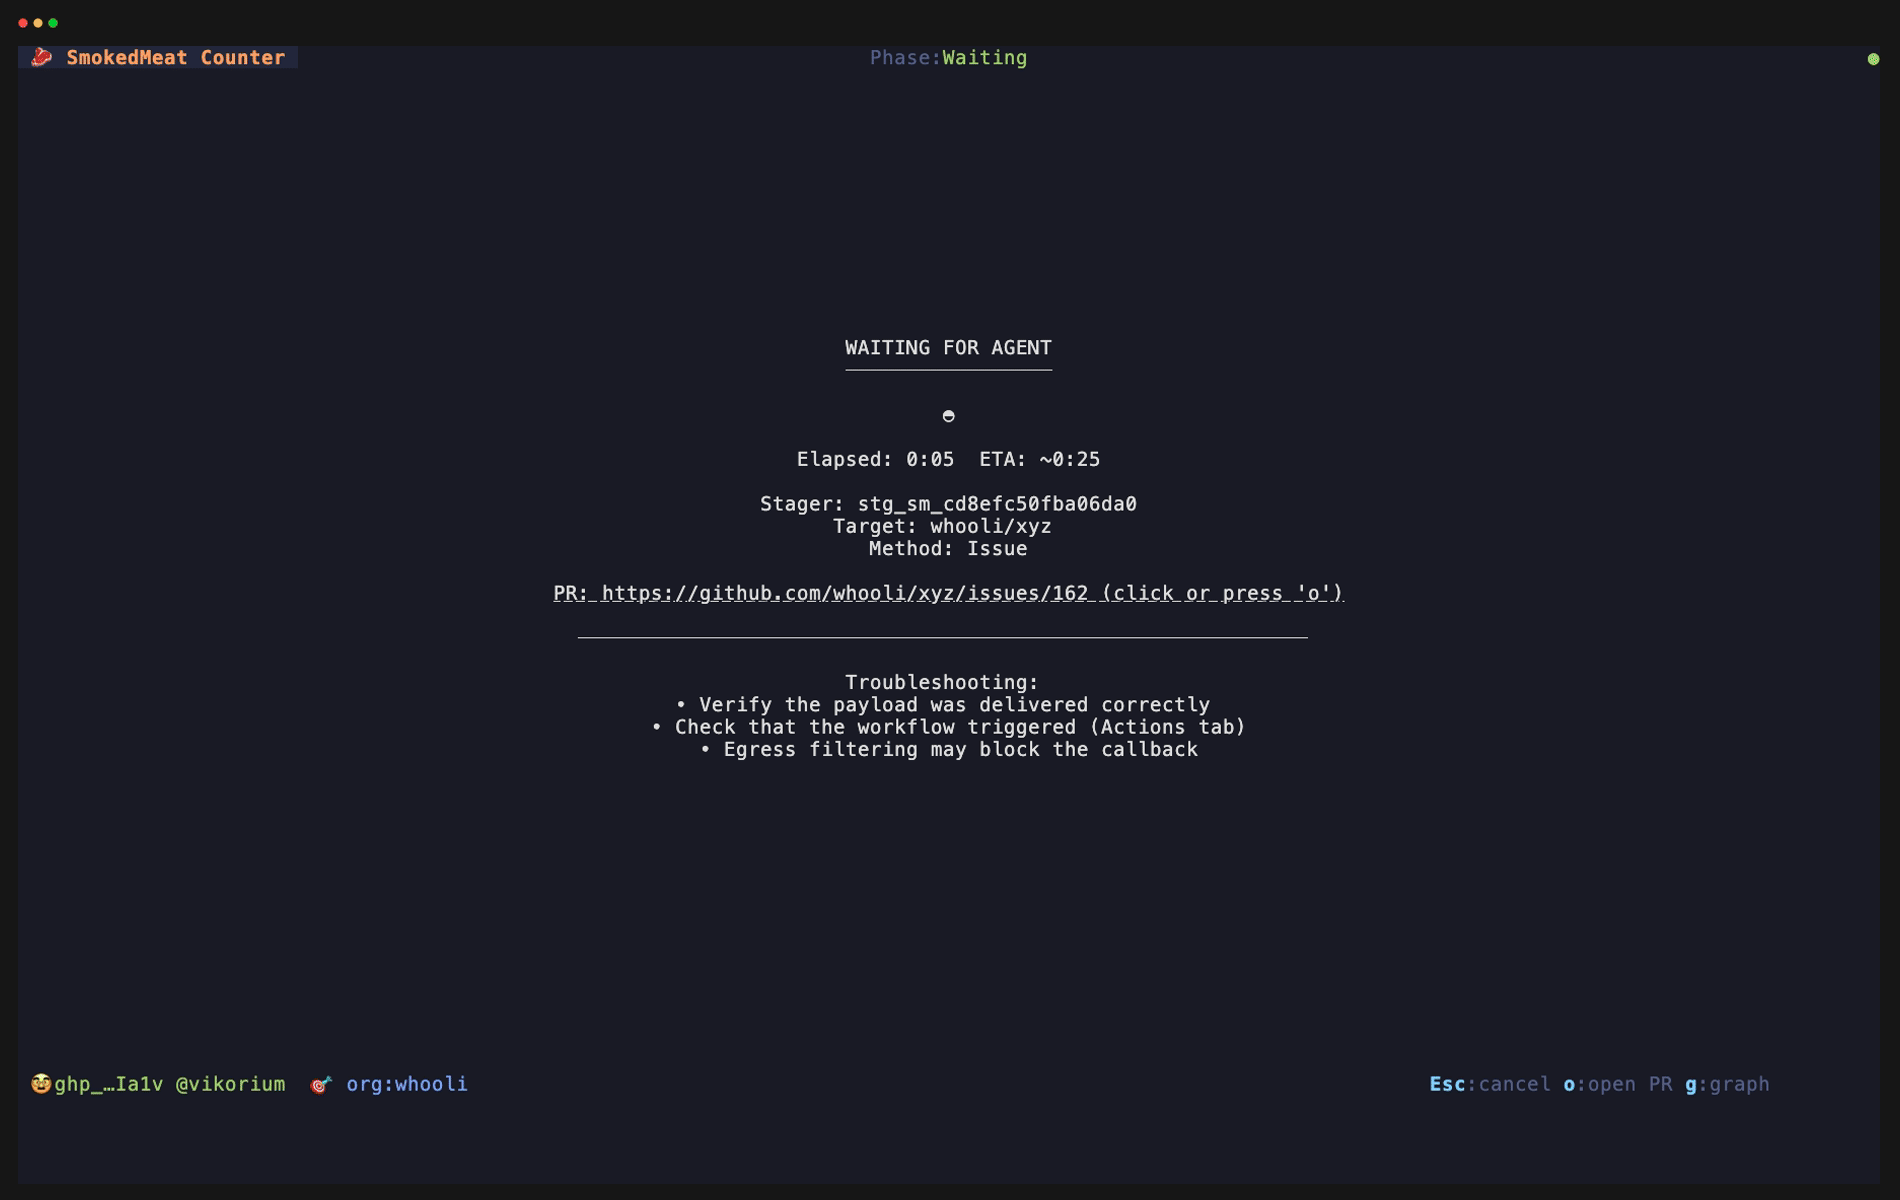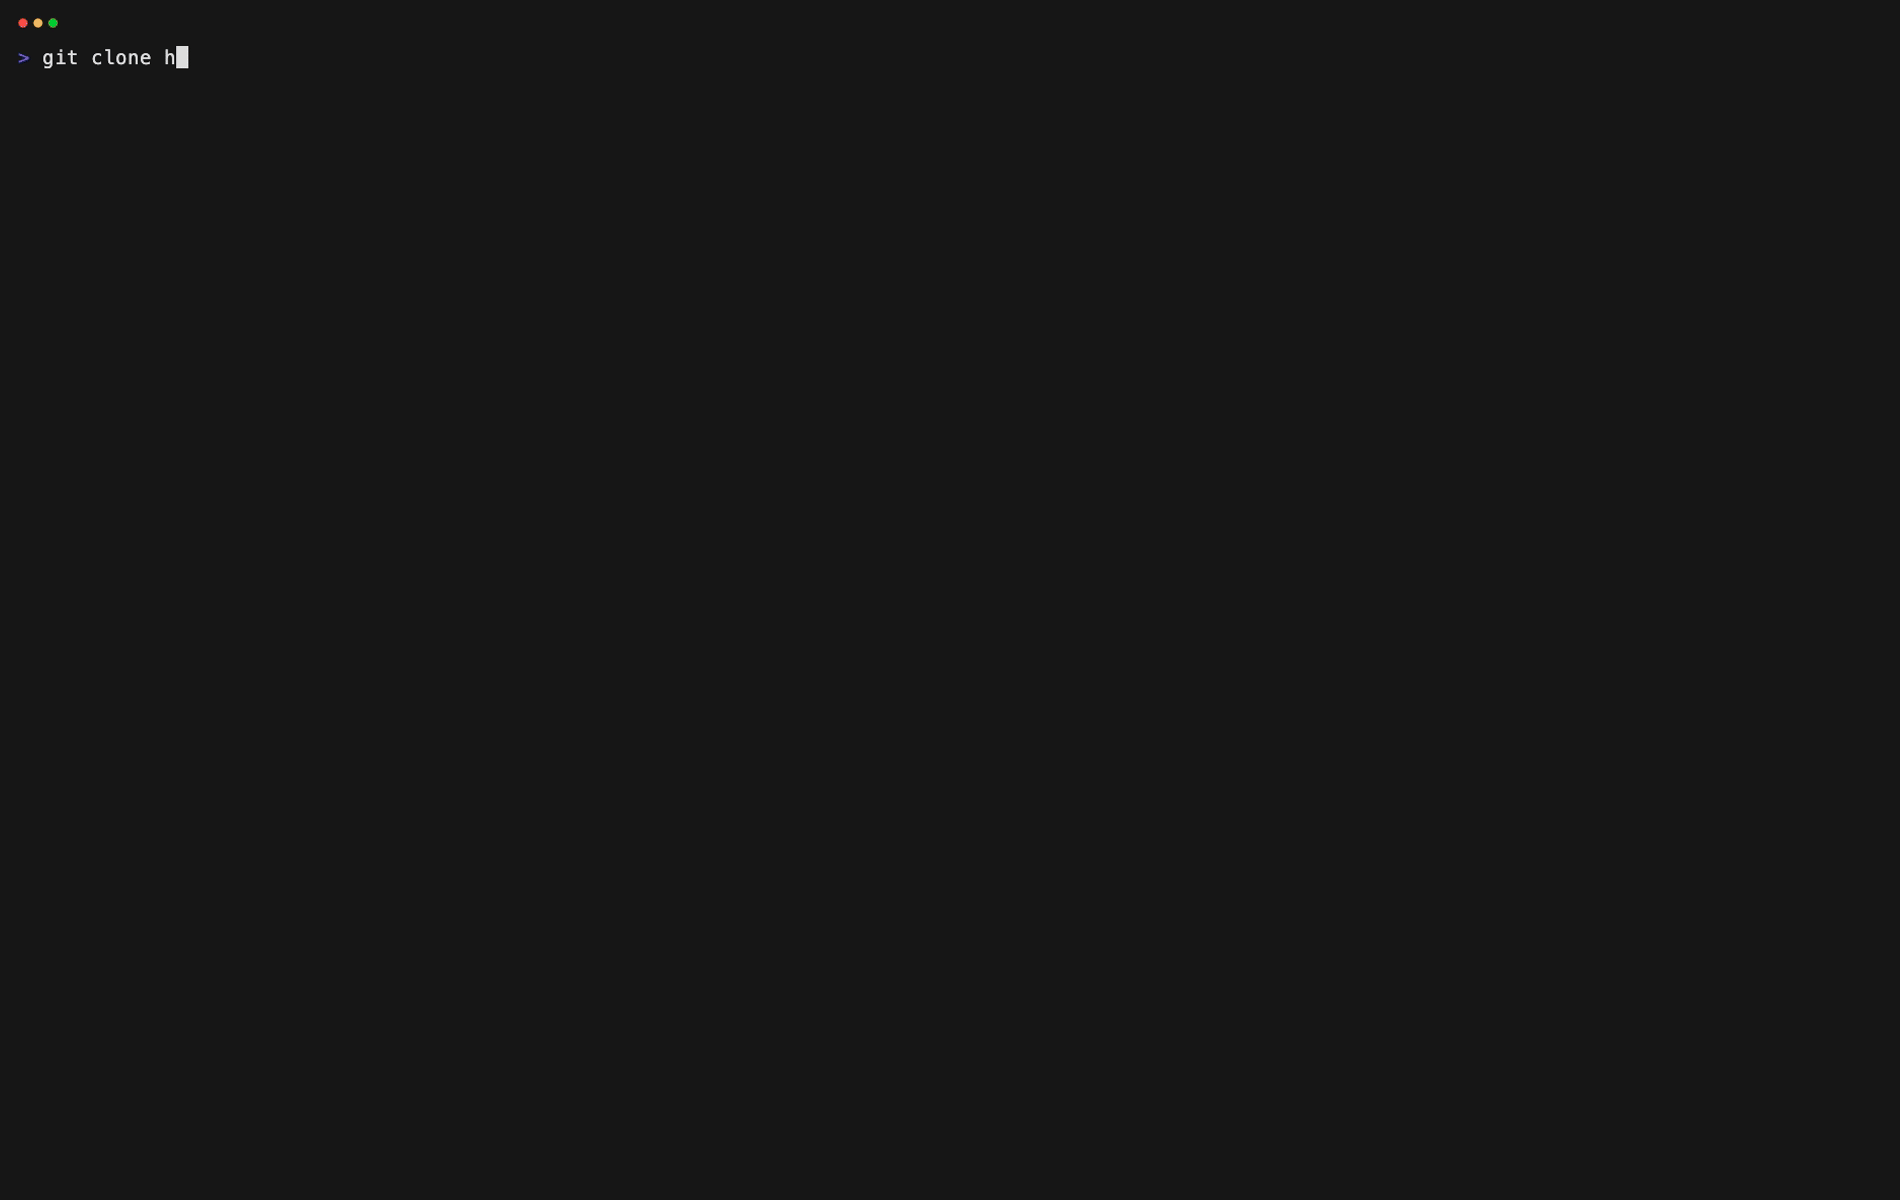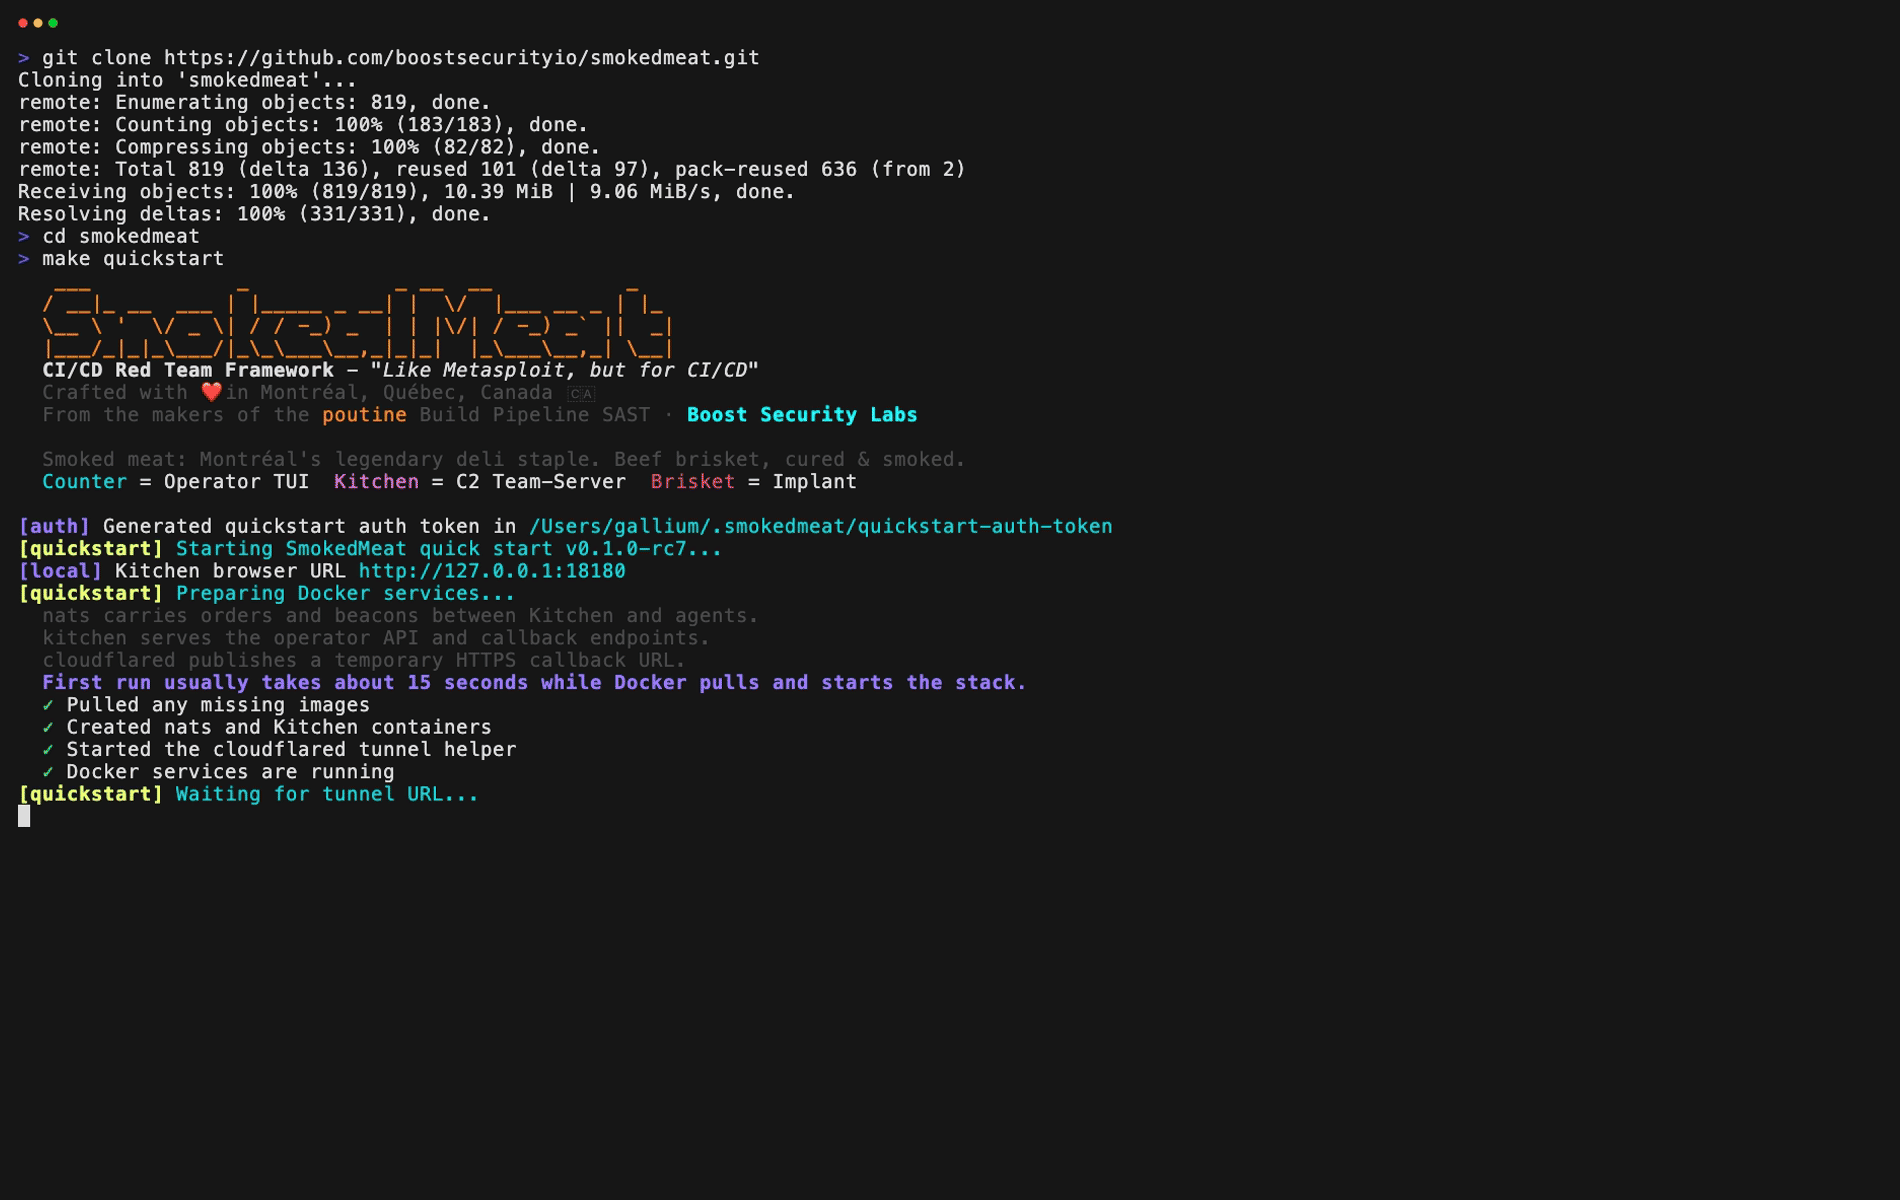 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.