honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…


PowerSploit - A PowerShell Post-Exploitation Framework

Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…

SSH man-in-the-middle tool

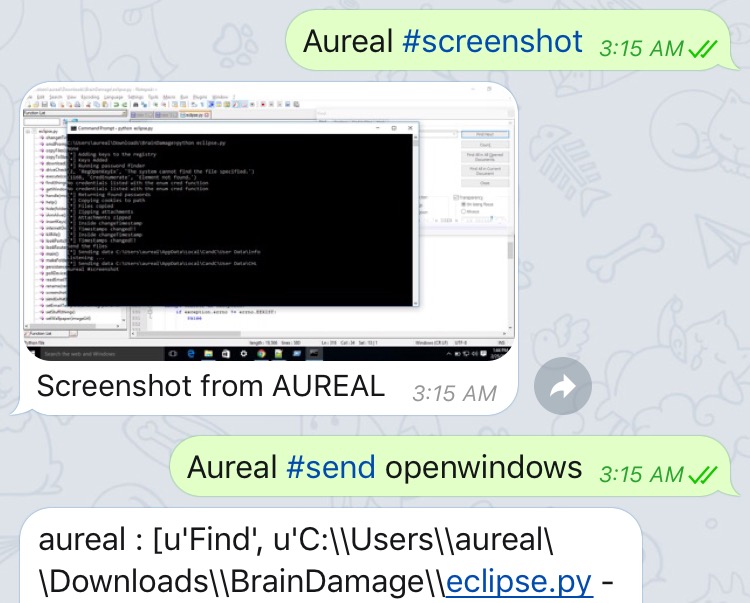
Remote administration service which uses twitter as a command and control server

Feature-rich Post Exploitation Framework with Network Pivoting capabilities.

This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

Autonomous Hacking Agent for Red Team

Course repository for PowerShell for Pentesters Course

D(COM) V(ulnerability) S(canner) AKA Devious swiss army knife - Lateral movement using DCOM Objects

Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.

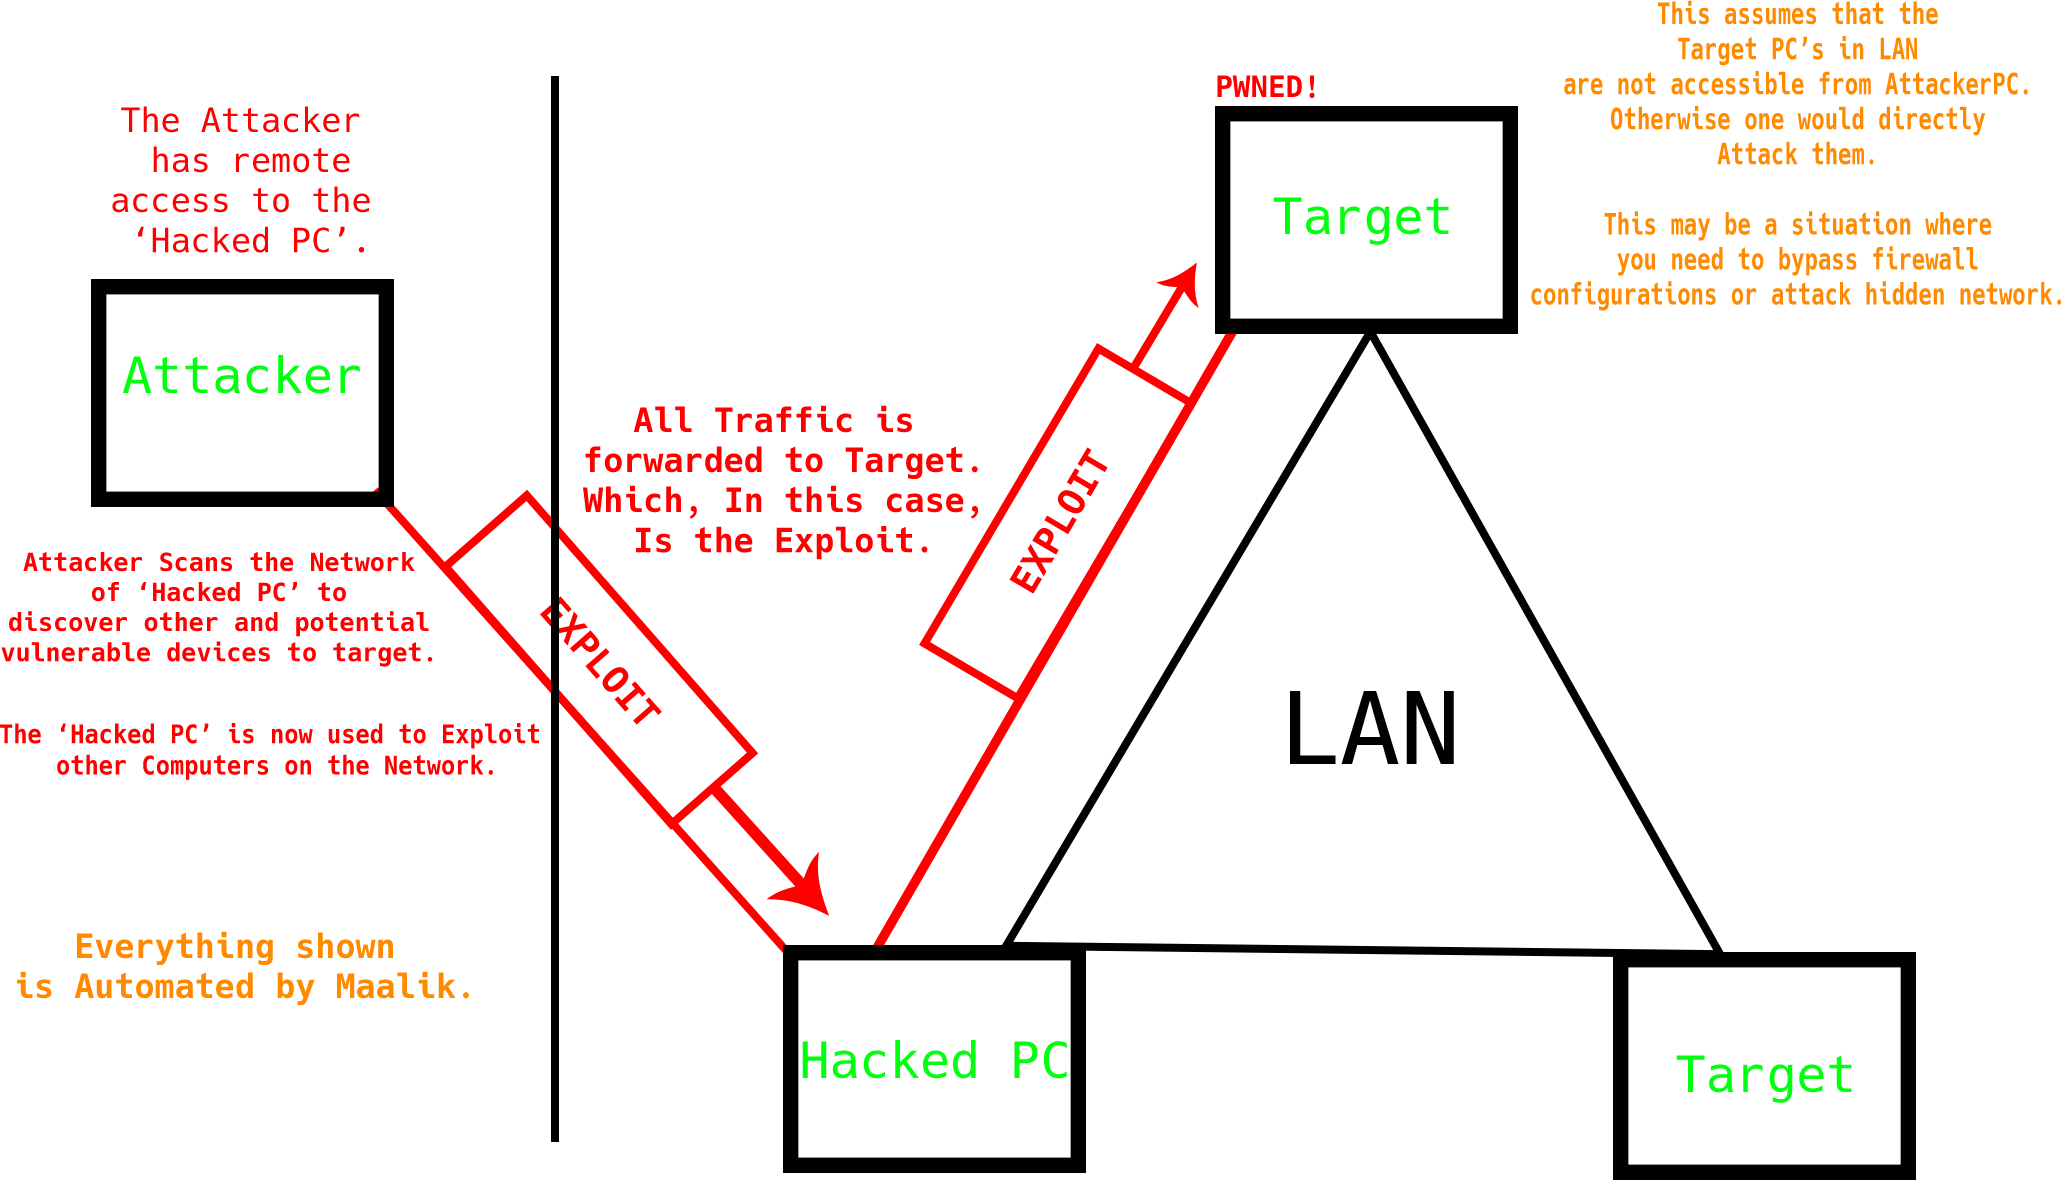
A compact guide to network pivoting for penetration testings / CTF challenges.

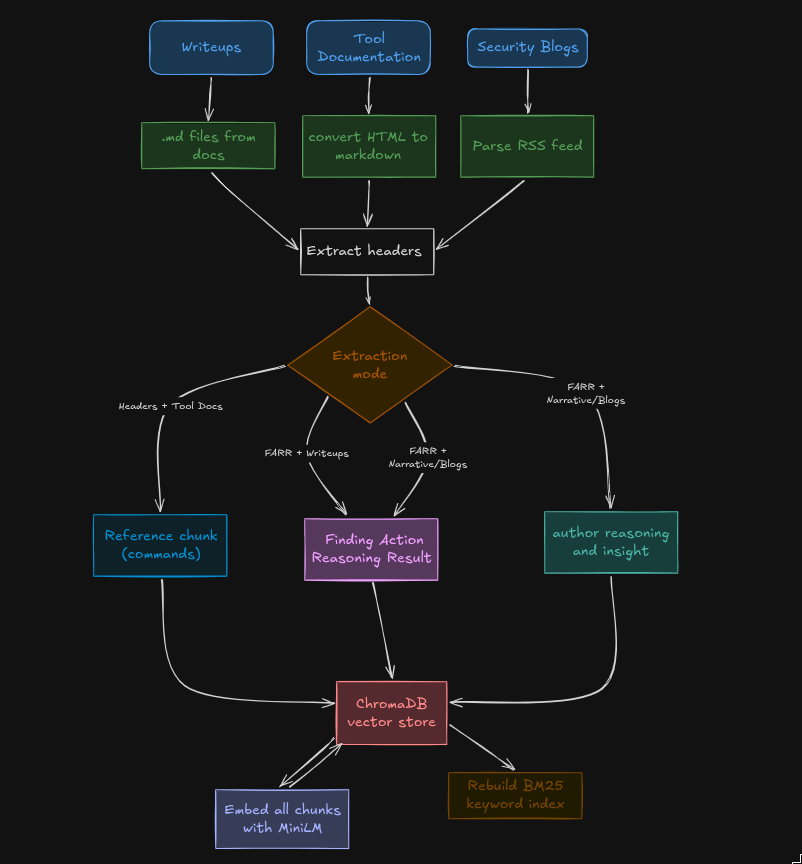
A personal RAG system for offensive security knowledge

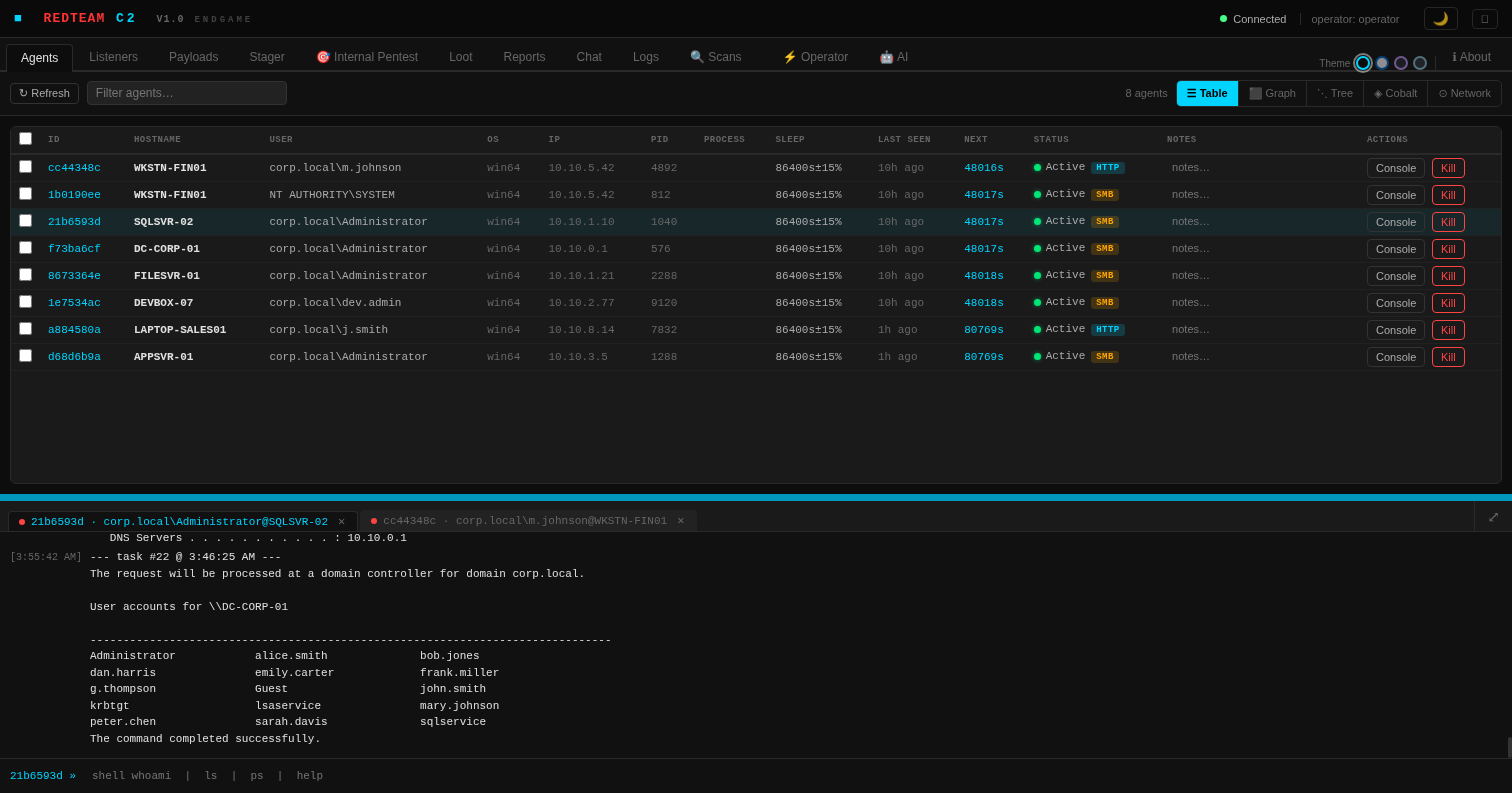
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations

Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…

Proof-of-concept exploit for CVE-2024-24919, an unauthenticated file read in Check Point Security Gateways; scans single or multiple IP targets and…