

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
78 results
HorusEye preview

HorusEye

GitHubomar-tamerr/horuseye

AI-Powered Active Directory Attack Platform
defensive-toolsinformation-gatheringlateral-movement+6
303 days ago
SSH-Snake preview
Archived

SSH-Snake

GitHubmegamansec/ssh-snake

SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
information-gatheringlateral-movementnetwork-mapping+5
2.3k5 days ago
brutus preview

brutus

GitHubpraetorian-inc/brutus

Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…

authenticationexploitationinformation-gathering+7
3077 days ago
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
3111 days ago
nimux preview

nimux

GitHubblue0x1/nimux

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

authenticationcommand-and-controlexploitation+6
412 days ago
aardwolf preview

aardwolf

GitHubskelsec/aardwolf

Asynchronous RDP client for Python (headless)

authenticationinformation-gatheringlateral-movement+5
23817 days ago
AdStrike preview

AdStrike

GitHubcapture0x/adstrike

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
40517 days ago
SharpHound preview

SharpHound

GitHubspecterops/sharphound

Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…

information-gatheringlateral-movementpenetration-testing+4
1.4k18 days ago
bloodhound-shell preview

bloodhound-shell

GitHubkr0no/bloodhound-shell

An interactive command-line shell for BloodHound API.

command-and-controlinformation-gatheringlateral-movement+7
118 days ago
TornadoRevC2 preview

TornadoRevC2

GitHubkamalx06/tornadorevc2

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
3927 days ago
ad-autopwn preview

ad-autopwn

GitHubjonaslejon/ad-autopwn

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
371 month ago
CVE-2025-24071 preview

CVE-2025-24071

GitHubbardlaudian/cve-2025-24071

Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
exploitationinformation-gatheringlateral-movement+5
1 month ago
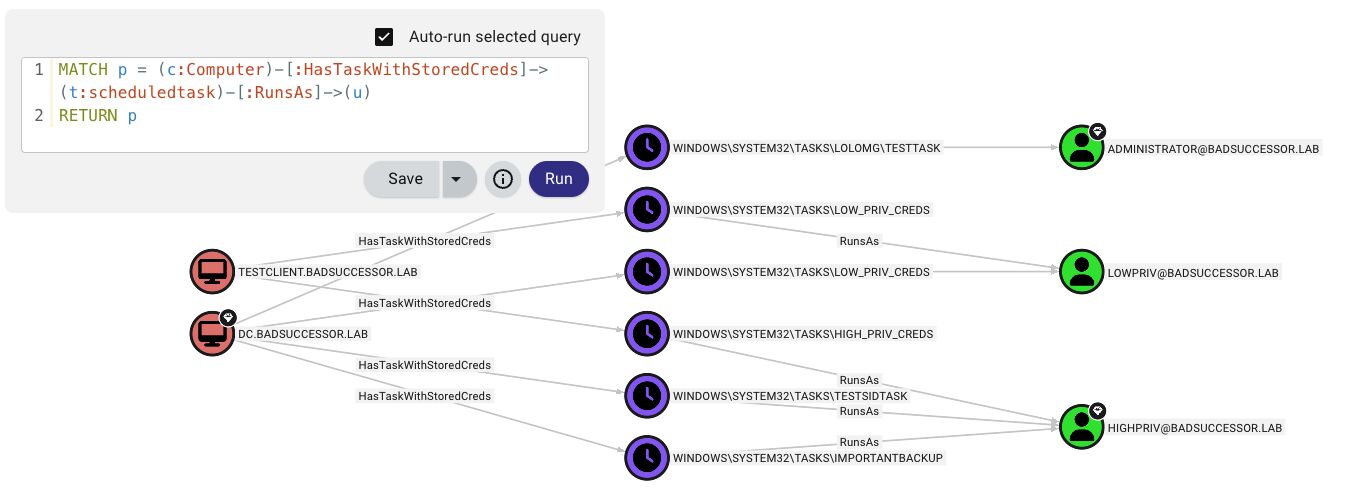
TaskHound preview

TaskHound

GitHub1r0bit/taskhound

Tool to enumerate privileged Scheduled Tasks on Remote Systems
information-gatheringlateral-movementpenetration-testing+4
3122 months ago
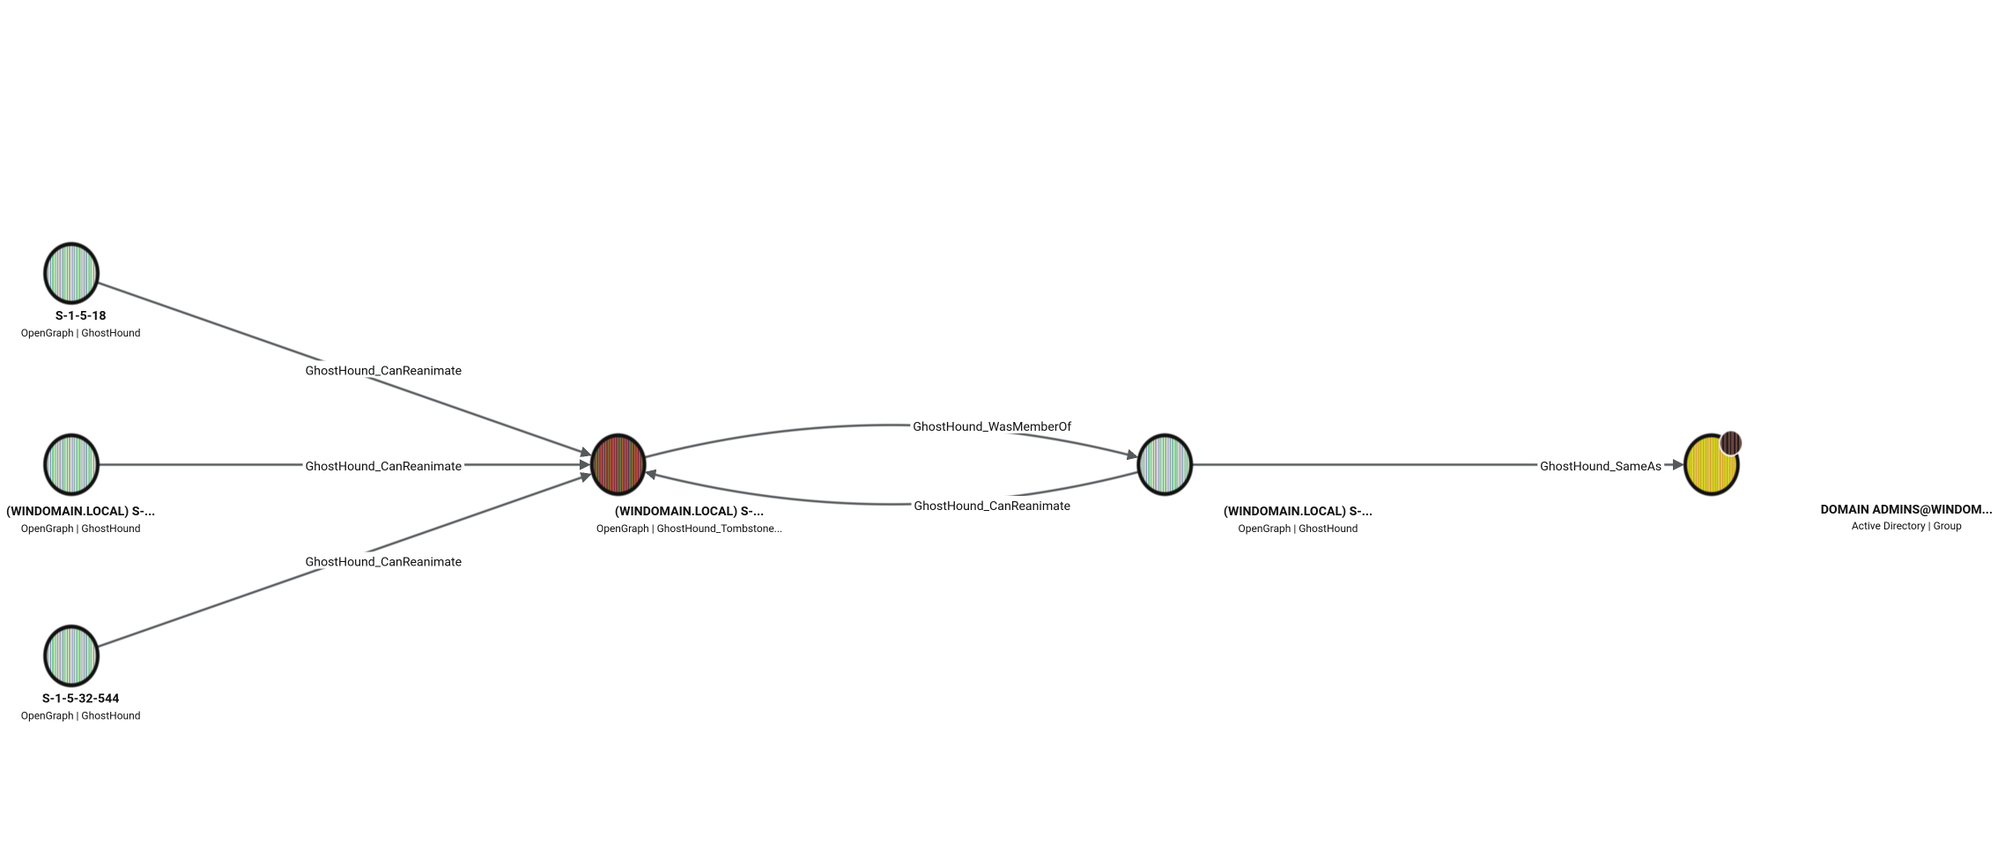
ghosthound preview

ghosthound

GitHubjvbotelho/ghosthound

GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
exploitationinformation-gatheringlateral-movement+5
422 months ago
AD-PathFinder preview

AD-PathFinder

GitHubnetspi/ad-pathfinder

Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
exploitationinformation-gatheringlateral-movement+7
952 months ago
cyanide preview

cyanide

GitHubhorizon3ai/cyanide

Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
exploitationinformation-gatheringlateral-movement+6
163 months ago
FUCKER preview

FUCKER

GitHubrazureink/fucker

Penetration testing framework with AI-driven decision engine
command-and-controlexploitationlateral-movement+7
3 months ago
CVE-2026-13768 preview

CVE-2026-13768

GitHubmichaeladamgroberman/cve-2026-13768

CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)

cloud-securityexploitationiot-security+5
4 months ago
Previous12345Next