

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…

anti-botcommand-and-controlids-ips-evasion+10
1.8k
1 day ago
Koi preview

Koi

GitHubb3rt1ng/koi

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
371 day ago
File-Tunnel preview

File-Tunnel

GitHubfiddyschmitt/file-tunnel

Tunnel TCP connections through a file

ids-ips-evasionlateral-movementnetwork-mapping+3
1.1k2 days ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
command-and-controlcryptographyids-ips-evasion+9
3413 days ago
RustyWater-ShellCode-Dropper preview

RustyWater-ShellCode-Dropper

GitHubs3n4t0r-0x0/rustywater-shellcode-dropper

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
binary-exploitationcommand-and-controlexploitation+9
1053 months ago
PortForwarder preview

PortForwarder

GitHublsecqt/portforwarder

TCP Port Forwarding Utility on C
general-purpose-utilitiesids-ips-evasionlateral-movement+4
424 months ago
cve-2026-0828 preview

cve-2026-0828

GitHubmein-0/cve-2026-0828

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
binary-exploitationexploitationids-ips-evasion+6
15 months ago
EDR-Redir preview

EDR-Redir

GitHubtwosevenonet/edr-redir

Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
anti-botdefensive-toolsids-ips-evasion+5
2475 months ago
hunting-rules preview

hunting-rules

GitHubtravisbgreen/hunting-rules

Suricata rules for network anomaly detection
anomaly-detectiondefensive-toolsintrusion-detection+3
1845 months ago
RelayKing-Depth preview

RelayKing-Depth

GitHubdepthsecurity/relayking-depth

Dominate the domain. Relay to royalty.
exploitationids-ips-evasioninformation-gathering+7
3577 months ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

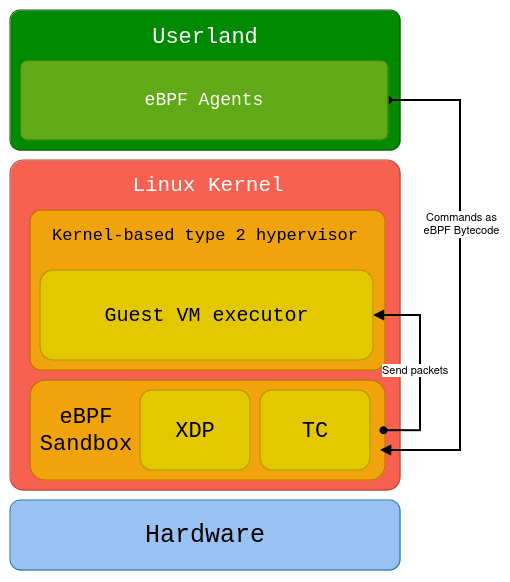
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
3408 months ago
360WFP_Exploit preview

360WFP_Exploit

GitHubkyxiaxiang/360wfp_exploit

BYOVD: Use 360 ​​WFP driver to block EDR/XDR network connection.
binary-analysisexploitationids-ips-evasion+6
1328 months ago
chisel-ng preview

chisel-ng

GitHubnullsection/chisel-ng

Chisel new generation, written in rust. SSH under WSS with some customization.
command-and-controlids-ips-evasionlateral-movement+5
1389 months ago
AV-EDR-Killer preview

AV-EDR-Killer

GitHubxm0kht4r/av-edr-killer

AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
command-and-controlexploitationids-ips-evasion+5
3039 months ago
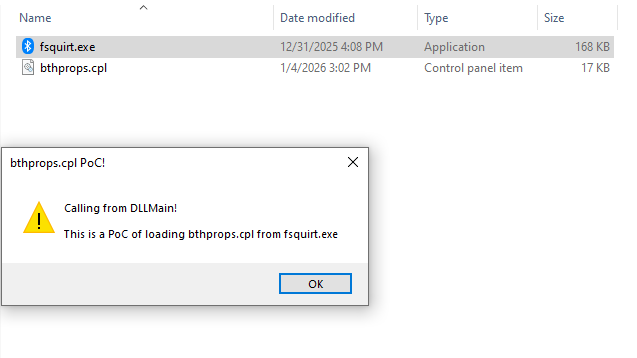
FsquirtCPLPoC preview

FsquirtCPLPoC

GitHubmhaskar/fsquirtcplpoc

PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
binary-exploitationcommand-and-controlexploitation+5
1229 months ago
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
command-and-controldefensive-toolsexploitation+7
4540 years ago
phantap preview

phantap

GitHubnccgroup/phantap

Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
ids-ips-evasionlateral-movementnetwork-mapping+4
6261 year ago
Dejavu preview

Dejavu

GitHubbhdresh/dejavu

DejaVU - Open Source Deception Framework

cloud-securitydefensive-toolsids-ips-evasion+7
4341 year ago
Previous12Next