

DLLHijackHunter
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
396
ghostvectoracademy/dllhijackhunterAutomated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
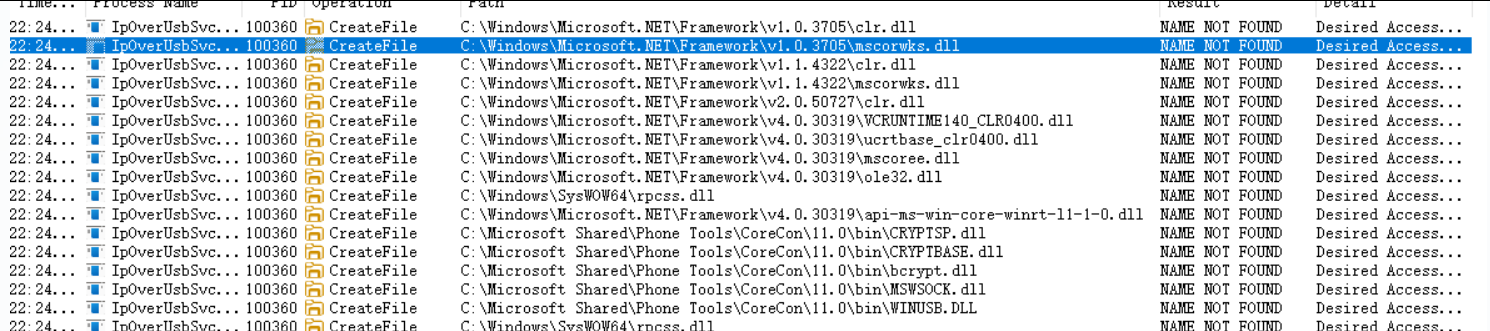 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
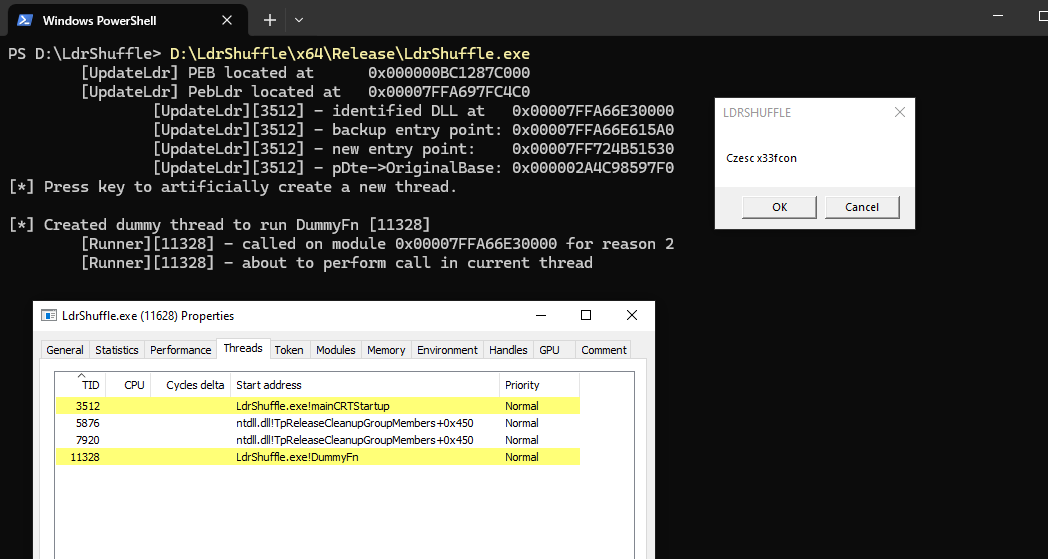 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
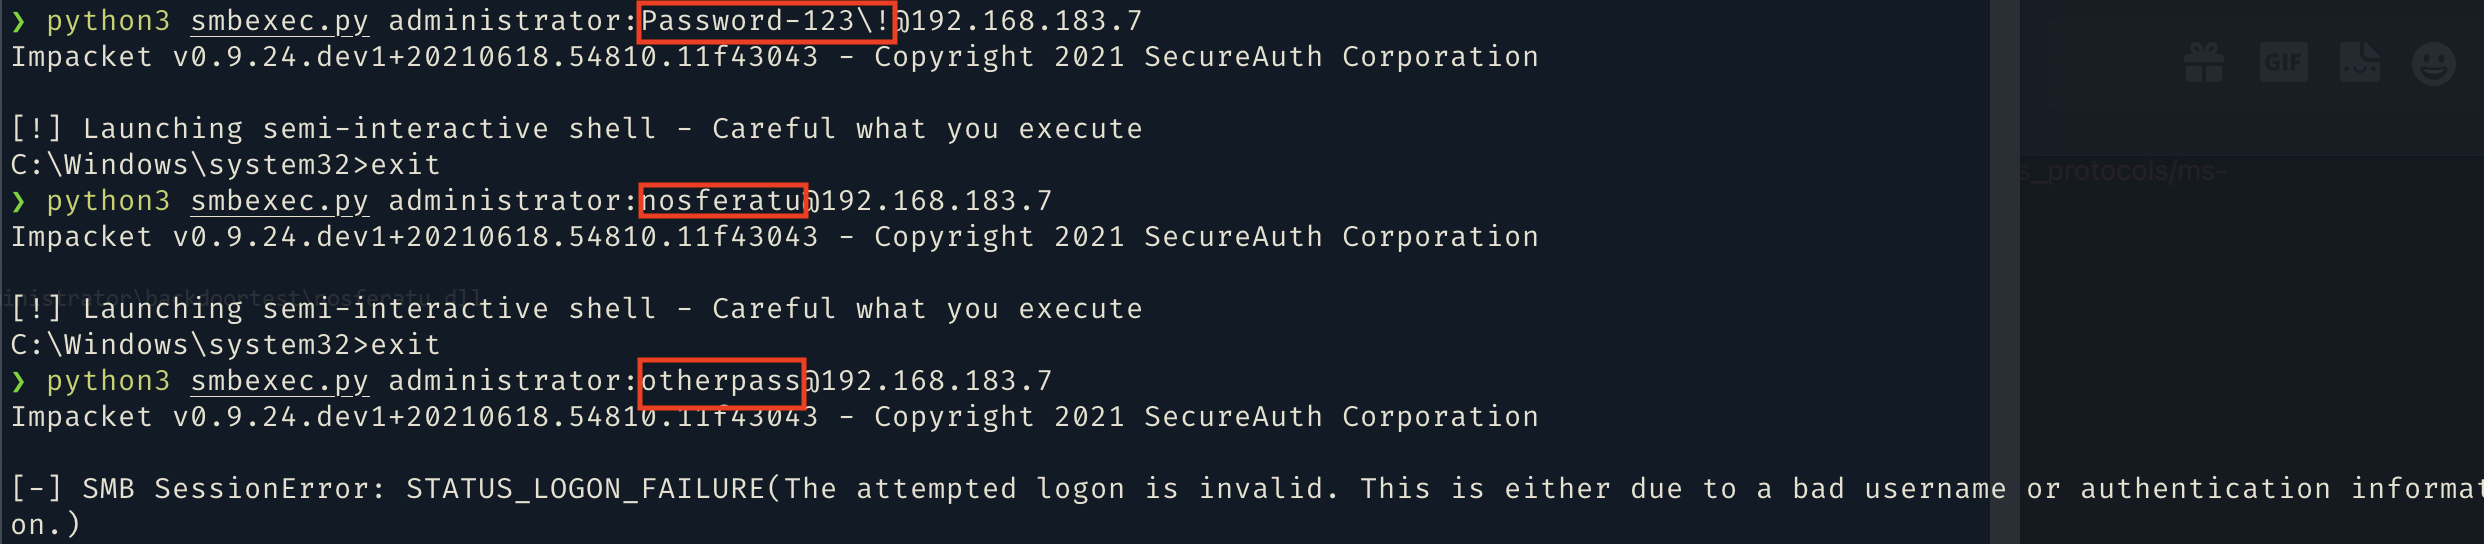 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 pamoutaf/cve-2024-34329
Proof-of-concept exploit for a local privilege escalation vulnerability in Datacard XPS Card Printer Driver via insecure file permissions and DLL…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 enkomio/alanframework
A C2 post-exploitation framework
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 trailer2/dll-planting-slack-4.33.73-cve-2023-38820
DLL Planting in the Slack 4.33.73 - CVE-2023-38820
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.