
brutus
 praetorian-inc/brutus
Fast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
authenticationexploitationinformation-gathering+7
327
praetorian-inc/brutusFast, zero-dependency credential testing tool in Go. Brute force SSH, MySQL, PostgreSQL, Redis, MongoDB, SMB, and 20+ protocols. Hydra alternative…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
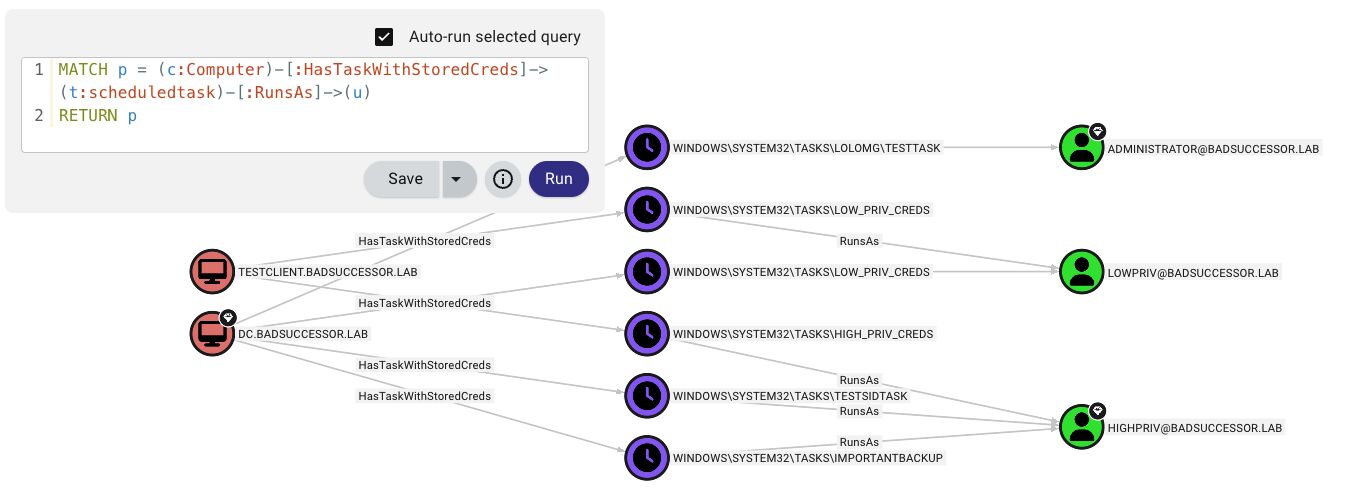 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
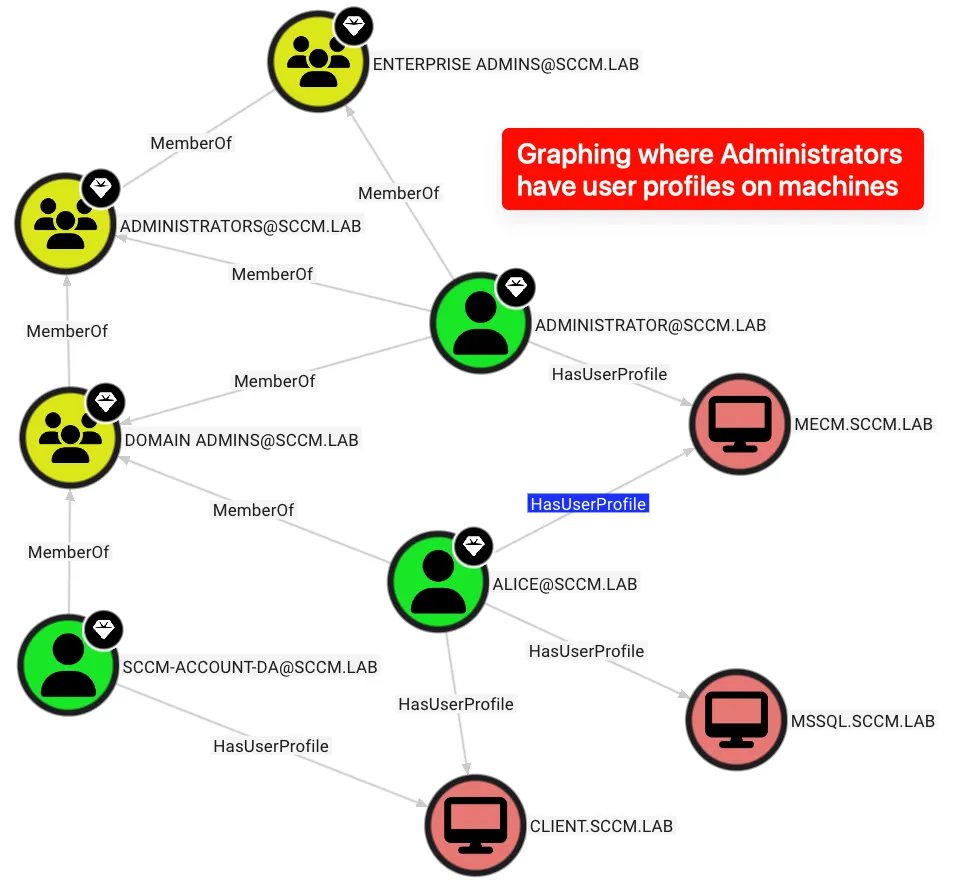 m4lwhere/profilehound
ProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…
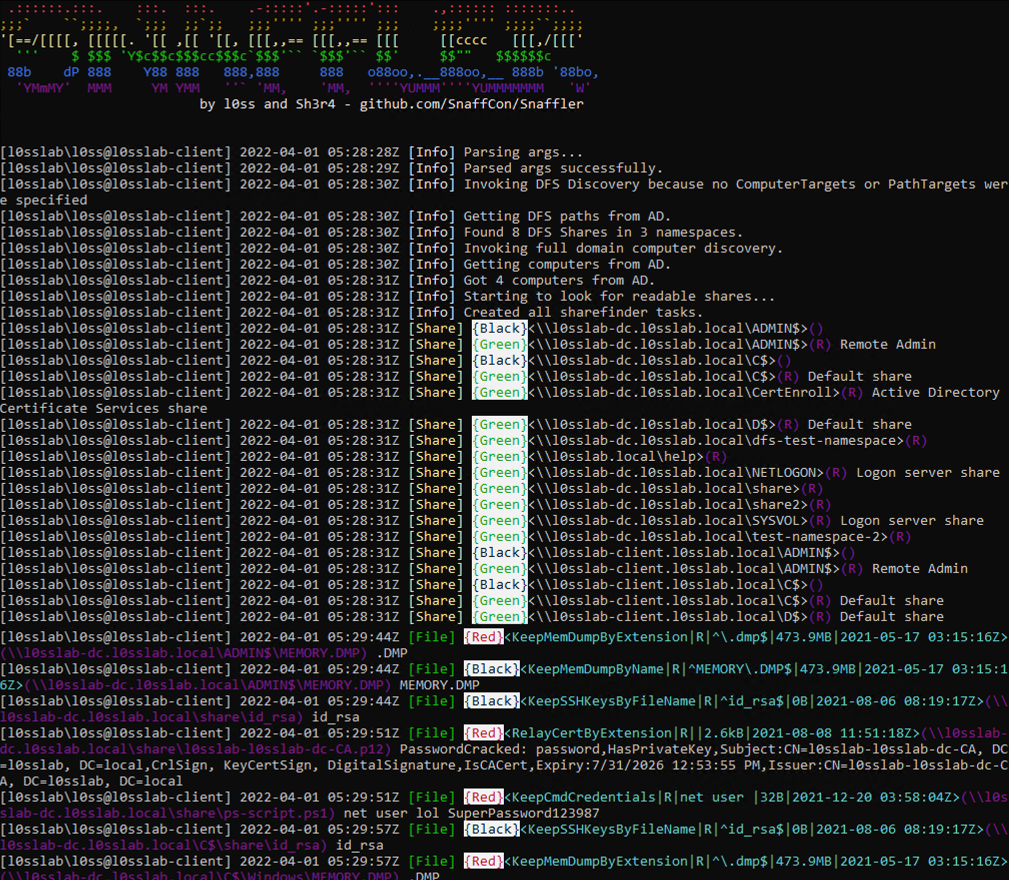 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing