
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
63 results
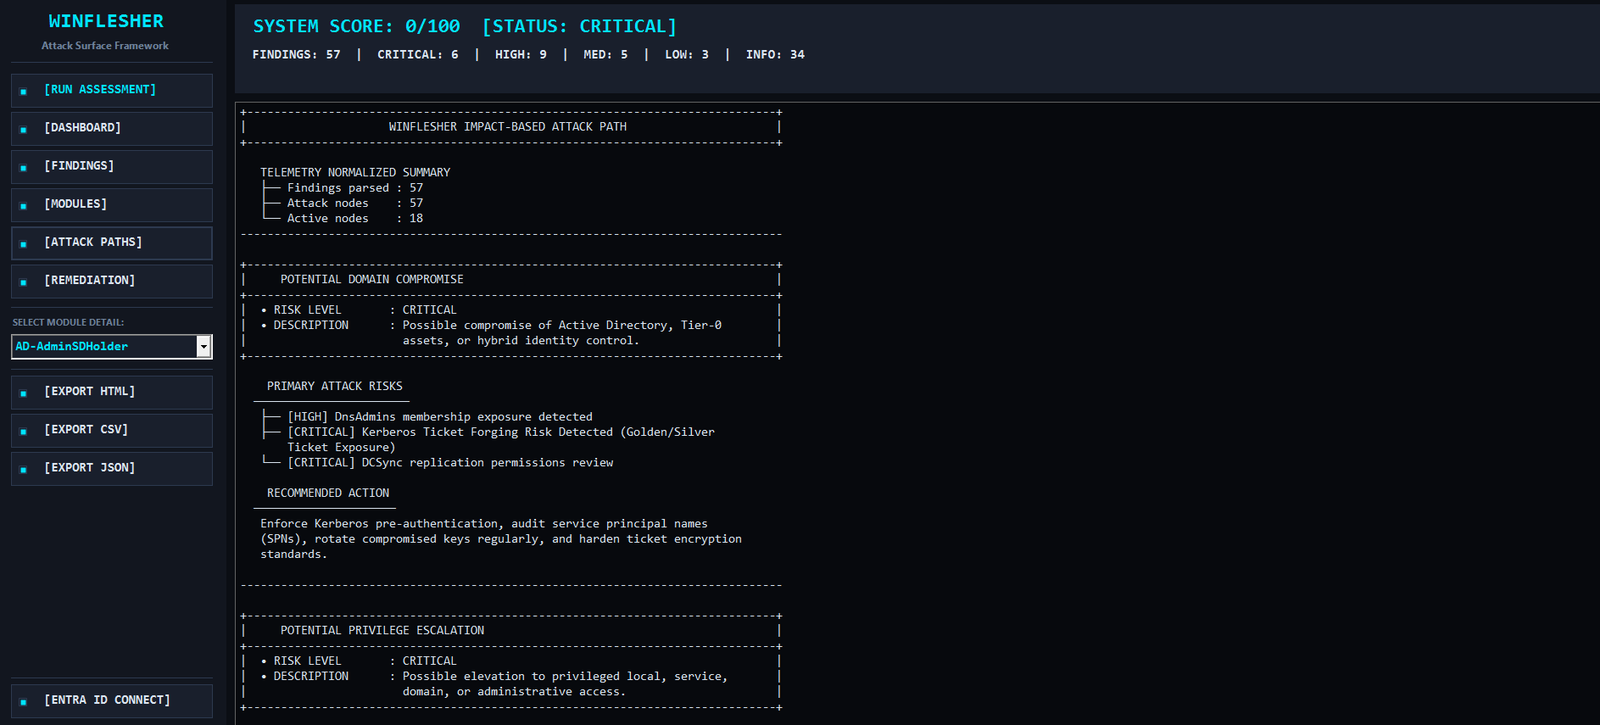
WinFlesher preview

WinFlesher

GitHubmindsflee/winflesher

Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
3 days ago
APTs-Adversary-Simulation preview

APTs-Adversary-Simulation

GitHubs3n4t0r-0x0/apts-adversary-simulation

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

adversarial-attackcommand-and-controleducation+9
1.1k3 days ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.9k4 days ago
DLLHijackHunter preview

DLLHijackHunter

GitHubghostvectoracademy/dllhijackhunter

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
4017 days ago
Misconfiguration-Manager preview

Misconfiguration-Manager

GitHubsubat0mik/misconfiguration-manager

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
configuration-auditingcurated-resourcesdefensive-tools+7
1.2k8 days ago
Thunderstorm preview

Thunderstorm

GitHubustayready/thunderstorm

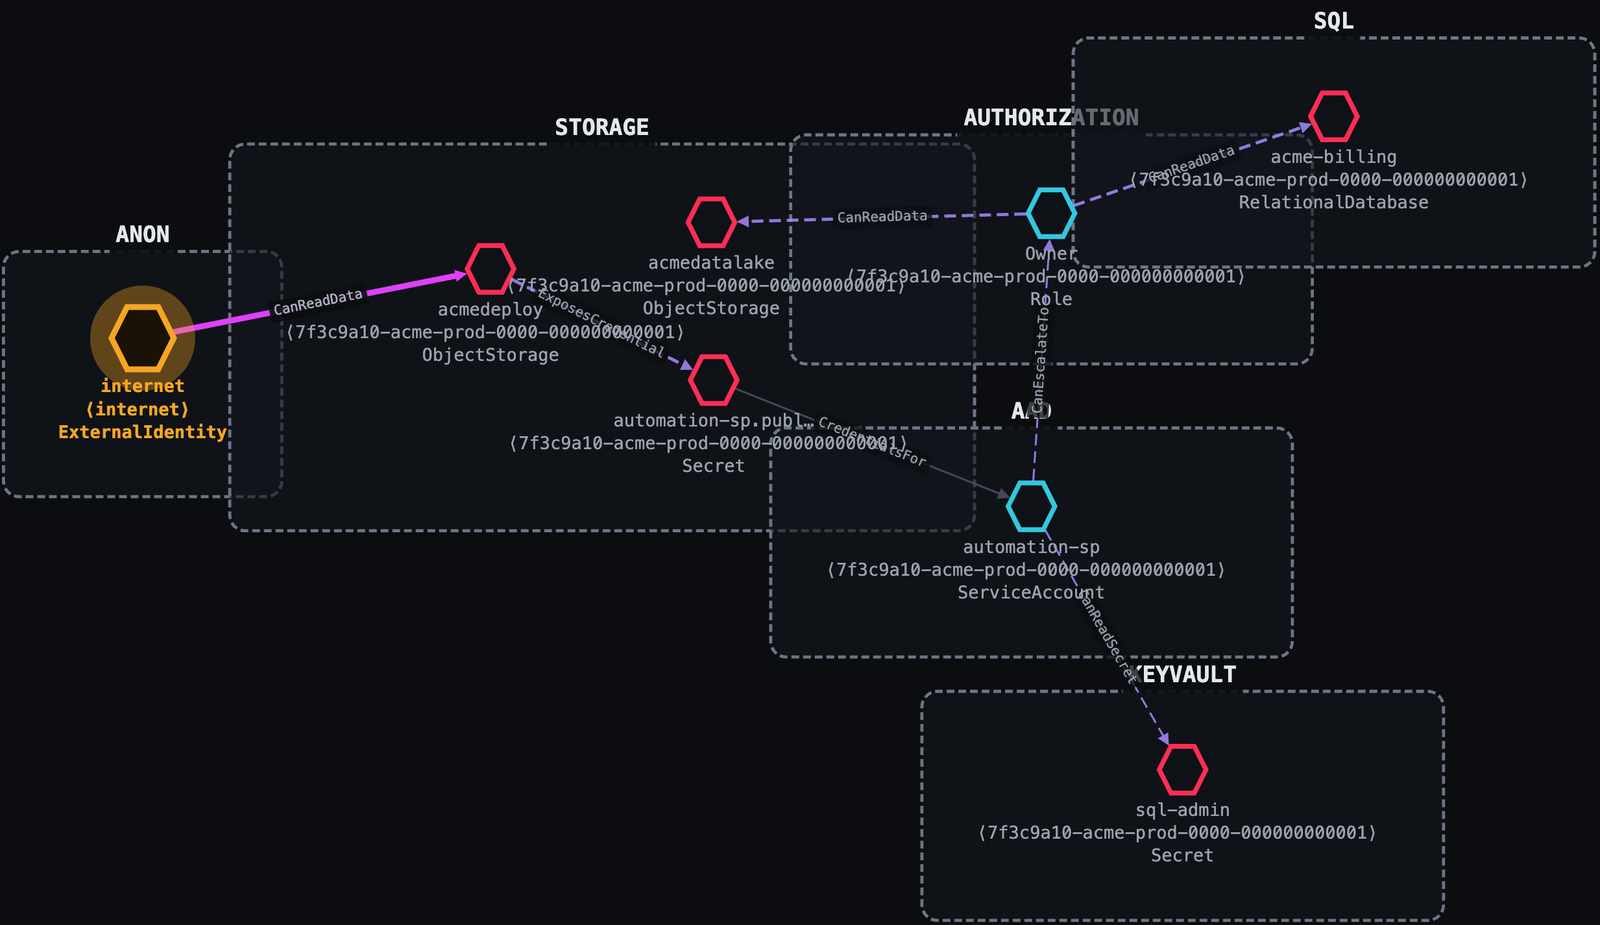
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
809 days ago
ad-autopwn preview

ad-autopwn

GitHubjonaslejon/ad-autopwn

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…

command-and-controlexploitationlateral-movement+7
20110 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k16 days ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubhkenzokimura/cve-2021-1675

Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…
educationexploitationlateral-movement+3
18 days ago
gpblib preview

gpblib

GitHubsynacktiv/gpblib

Common library for tools implementing GPO attack vectors
exploitationlateral-movementpenetration-testing+3
323 days ago
Adrenaline preview

Adrenaline

GitHubatomiczsec/adrenaline

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
command-and-controldefensive-toolsinformation-gathering+7
31824 days ago
AutoPtT preview

AutoPtT

GitHubricardojoserf/autoptt

Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
authenticationlateral-movementpost-exploitation+1
15524 days ago
NoiseHound preview

NoiseHound

GitHubwarpedatom/noisehound

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
adversarial-attackdefensive-toolslateral-movement+4
661 month ago
cloudfox preview

cloudfox

GitHubbishopfox/cloudfox

Automating situational awareness for cloud penetration tests.
cloud-infrastructure-securitycloud-securityexploitation+7
2.6k1 month ago
ghosthound preview

ghosthound

GitHubjvbotelho/ghosthound

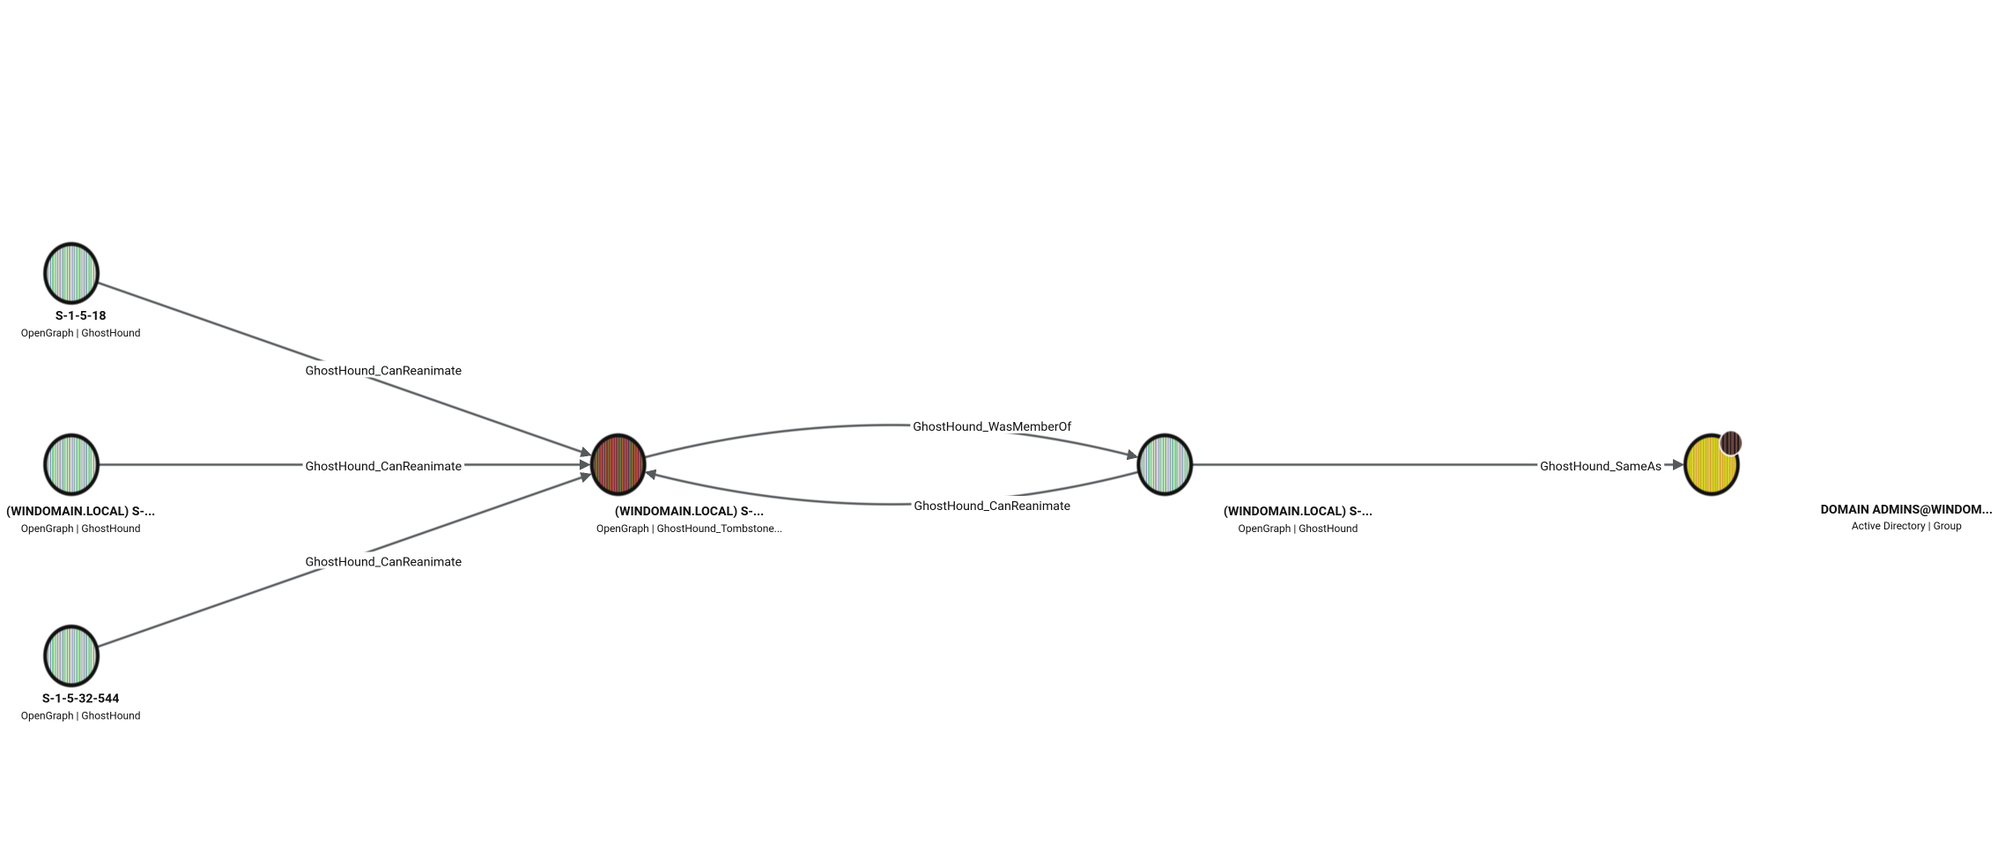
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
exploitationinformation-gatheringlateral-movement+5
441 month ago
AD-PathFinder preview

AD-PathFinder

GitHubnetspi/ad-pathfinder

Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
exploitationinformation-gatheringlateral-movement+7
2401 month ago
cyanide preview

cyanide

GitHubhorizon3ai/cyanide

Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
exploitationinformation-gatheringlateral-movement+6
161 month ago
CVE-2026-54121-CertiGhost preview

CVE-2026-54121-CertiGhost

GitHubmarcgoam/cve-2026-54121-certighost

CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.

adversarial-attackauthentication-authorizationexploitation+4
101 month ago
Previous1234Next