
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
WinFlesher preview

WinFlesher

GitHubmindsflee/winflesher

Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
3 days ago
SharpHound preview

SharpHound

GitHubspecterops/sharphound

Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…


information-gatheringlateral-movementpenetration-testing+4
1.4k3 days ago
offensive-one-liners preview

offensive-one-liners

GitLabwattocyber/offensive-one-liners

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
container-escapectfcurated-resources+9
1 month ago
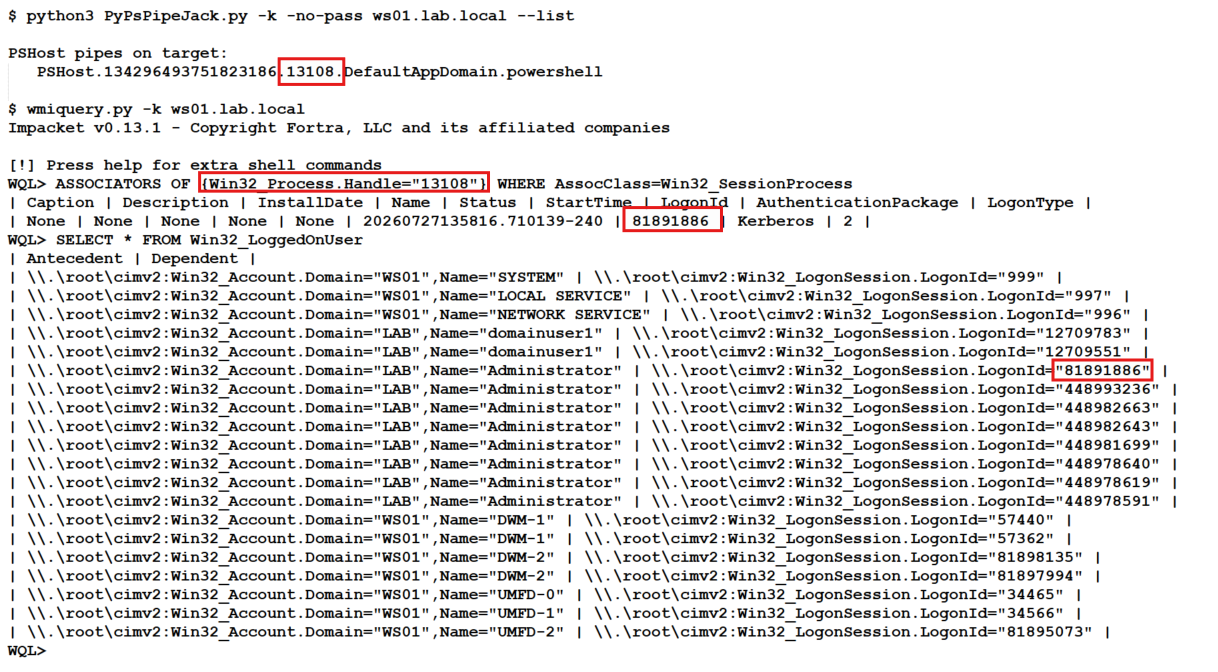
PyPsPipeJack preview

PyPsPipeJack

GitHube-fin/pypspipejack

Python implementation of OpenPsPipeJack

lateral-movementpenetration-testingpost-exploitation+3
231 month ago
peeko preview

peeko

GitHubb3rito/peeko

peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.

command-and-controldata-exfiltrationinformation-gathering+7
2331 year ago
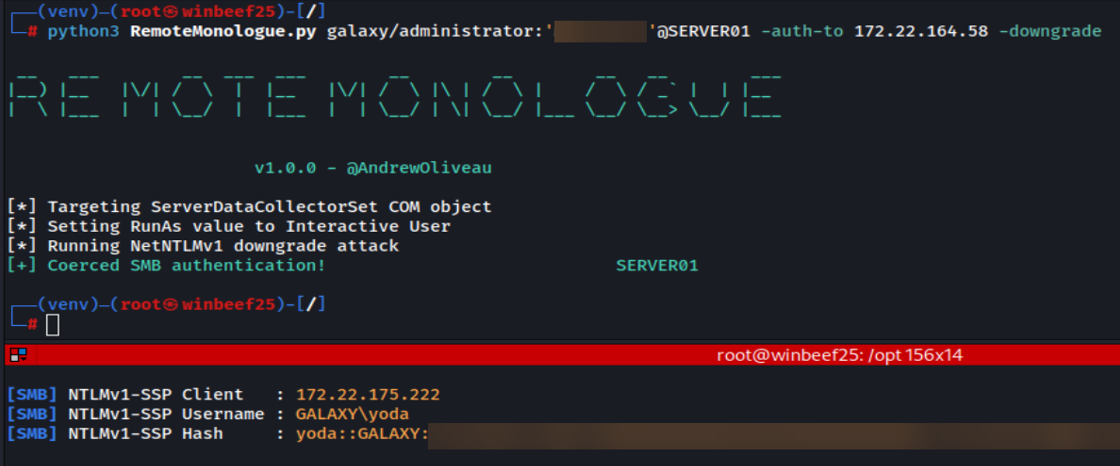
RemoteMonologue preview

RemoteMonologue

GitHubxforcered/remotemonologue

Weaponizing DCOM for NTLM Authentication Coercions
exploitationinformation-gatheringlateral-movement+3
2741 year ago
RemoteMonologue preview

RemoteMonologue

GitHub3lp4tr0n/remotemonologue

Weaponizing DCOM for NTLM Authentication Coercions
adversarial-attackauthenticationexploitation+6
21410 months ago
badsuccessor preview

badsuccessor

GitHubcybrly/badsuccessor

Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
adversarial-attackexploitationinformation-gathering+7
1211 year ago
SecretsStalker preview

SecretsStalker

GitHubrootsecdev/secretsstalker

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

authentication-authorizationcloud-infrastructure-securitycloud-security+7
201 month ago
sccmhound preview

sccmhound

GitHubcrowdstrike/sccmhound

A BloodHound collector for Microsoft Configuration Manager
information-gatheringlateral-movementpenetration-testing+1
4031 year ago
easyda preview

easyda

GitHubnccgroup/easyda

Easy Window domain access

lateral-movementpassword-attackspenetration-testing+1
5212 years ago
backup_dc_registry preview

backup_dc_registry

GitHubhorizon3ai/backup_dc_registry

A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY

exploitationlateral-movementmisconfiguration+3
964 years ago
Active-Directory-Exploitation-Cheat-Sheet preview

Active-Directory-Exploitation-Cheat-Sheet

GitHubintegration-it/active-directory-exploitation-cheat-sheet

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
curated-resourcesdata-exfiltrationeducation+6
2.8k5 years ago
OUned preview

OUned

GitHubsynacktiv/ouned

The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
authenticationexploitationlateral-movement+3
16627 days ago
FUCKER preview

FUCKER

GitHubrazureink/fucker

Penetration testing framework with AI-driven decision engine
command-and-controlexploitationlateral-movement+7
2 months ago
CVE-2026-54121-PoC-Exploit preview

CVE-2026-54121-PoC-Exploit

GitHubtc4dy/cve-2026-54121-poc-exploit

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
authentication-authorizationexploitationexploit-frameworks+5
2913 days ago
nimrm preview

nimrm

GitHubblue0x1/nimrm

Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
authenticationcommand-and-controlinformation-gathering+6
613 days ago
SessionGopher preview

SessionGopher

GitHubarvanaghi/sessiongopher

SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…

information-gatheringlateral-movementpenetration-testing+3
1.3k7 years ago
Previous12345Next