
CVE-2025-24071
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
exploitationinformation-gatheringlateral-movement+5
bardlaudian/cve-2025-24071Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 zhulin837/checkmk_cve-2024-0670
Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…
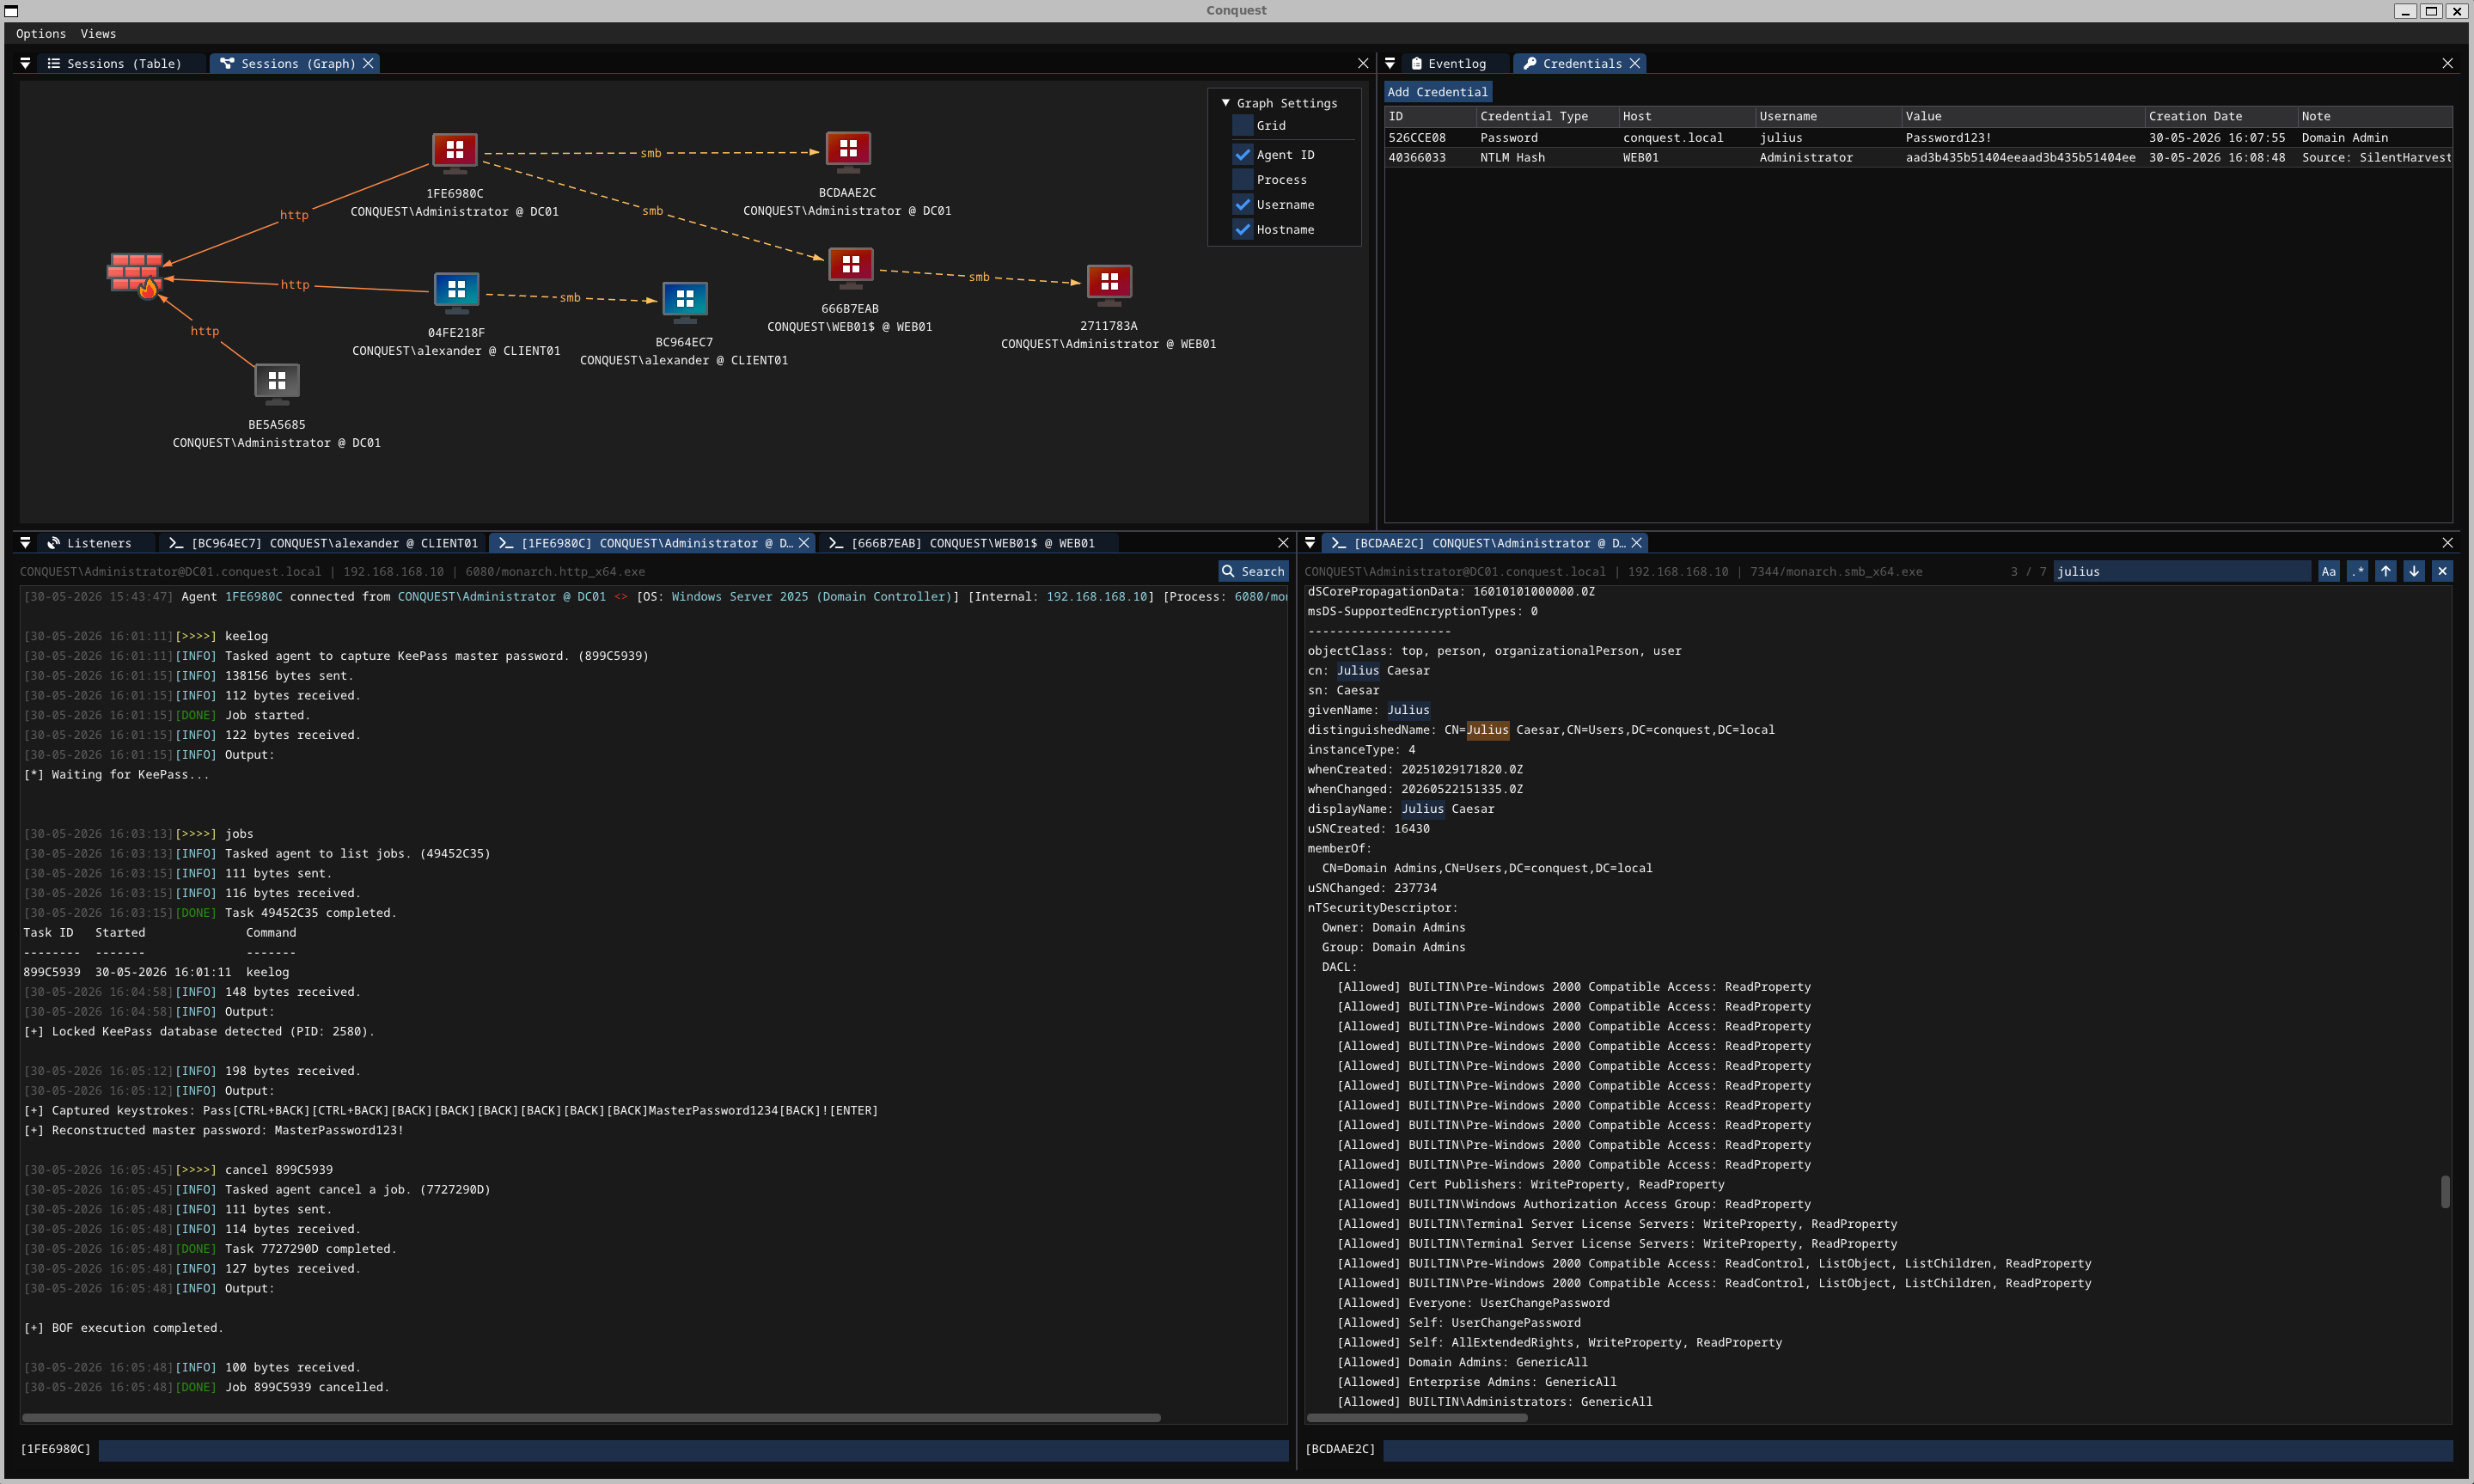 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
 galoget/printnightmare-cve-2021-1675-cve-2021-34527
CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
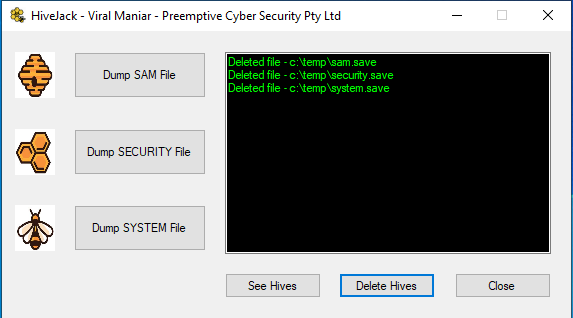 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
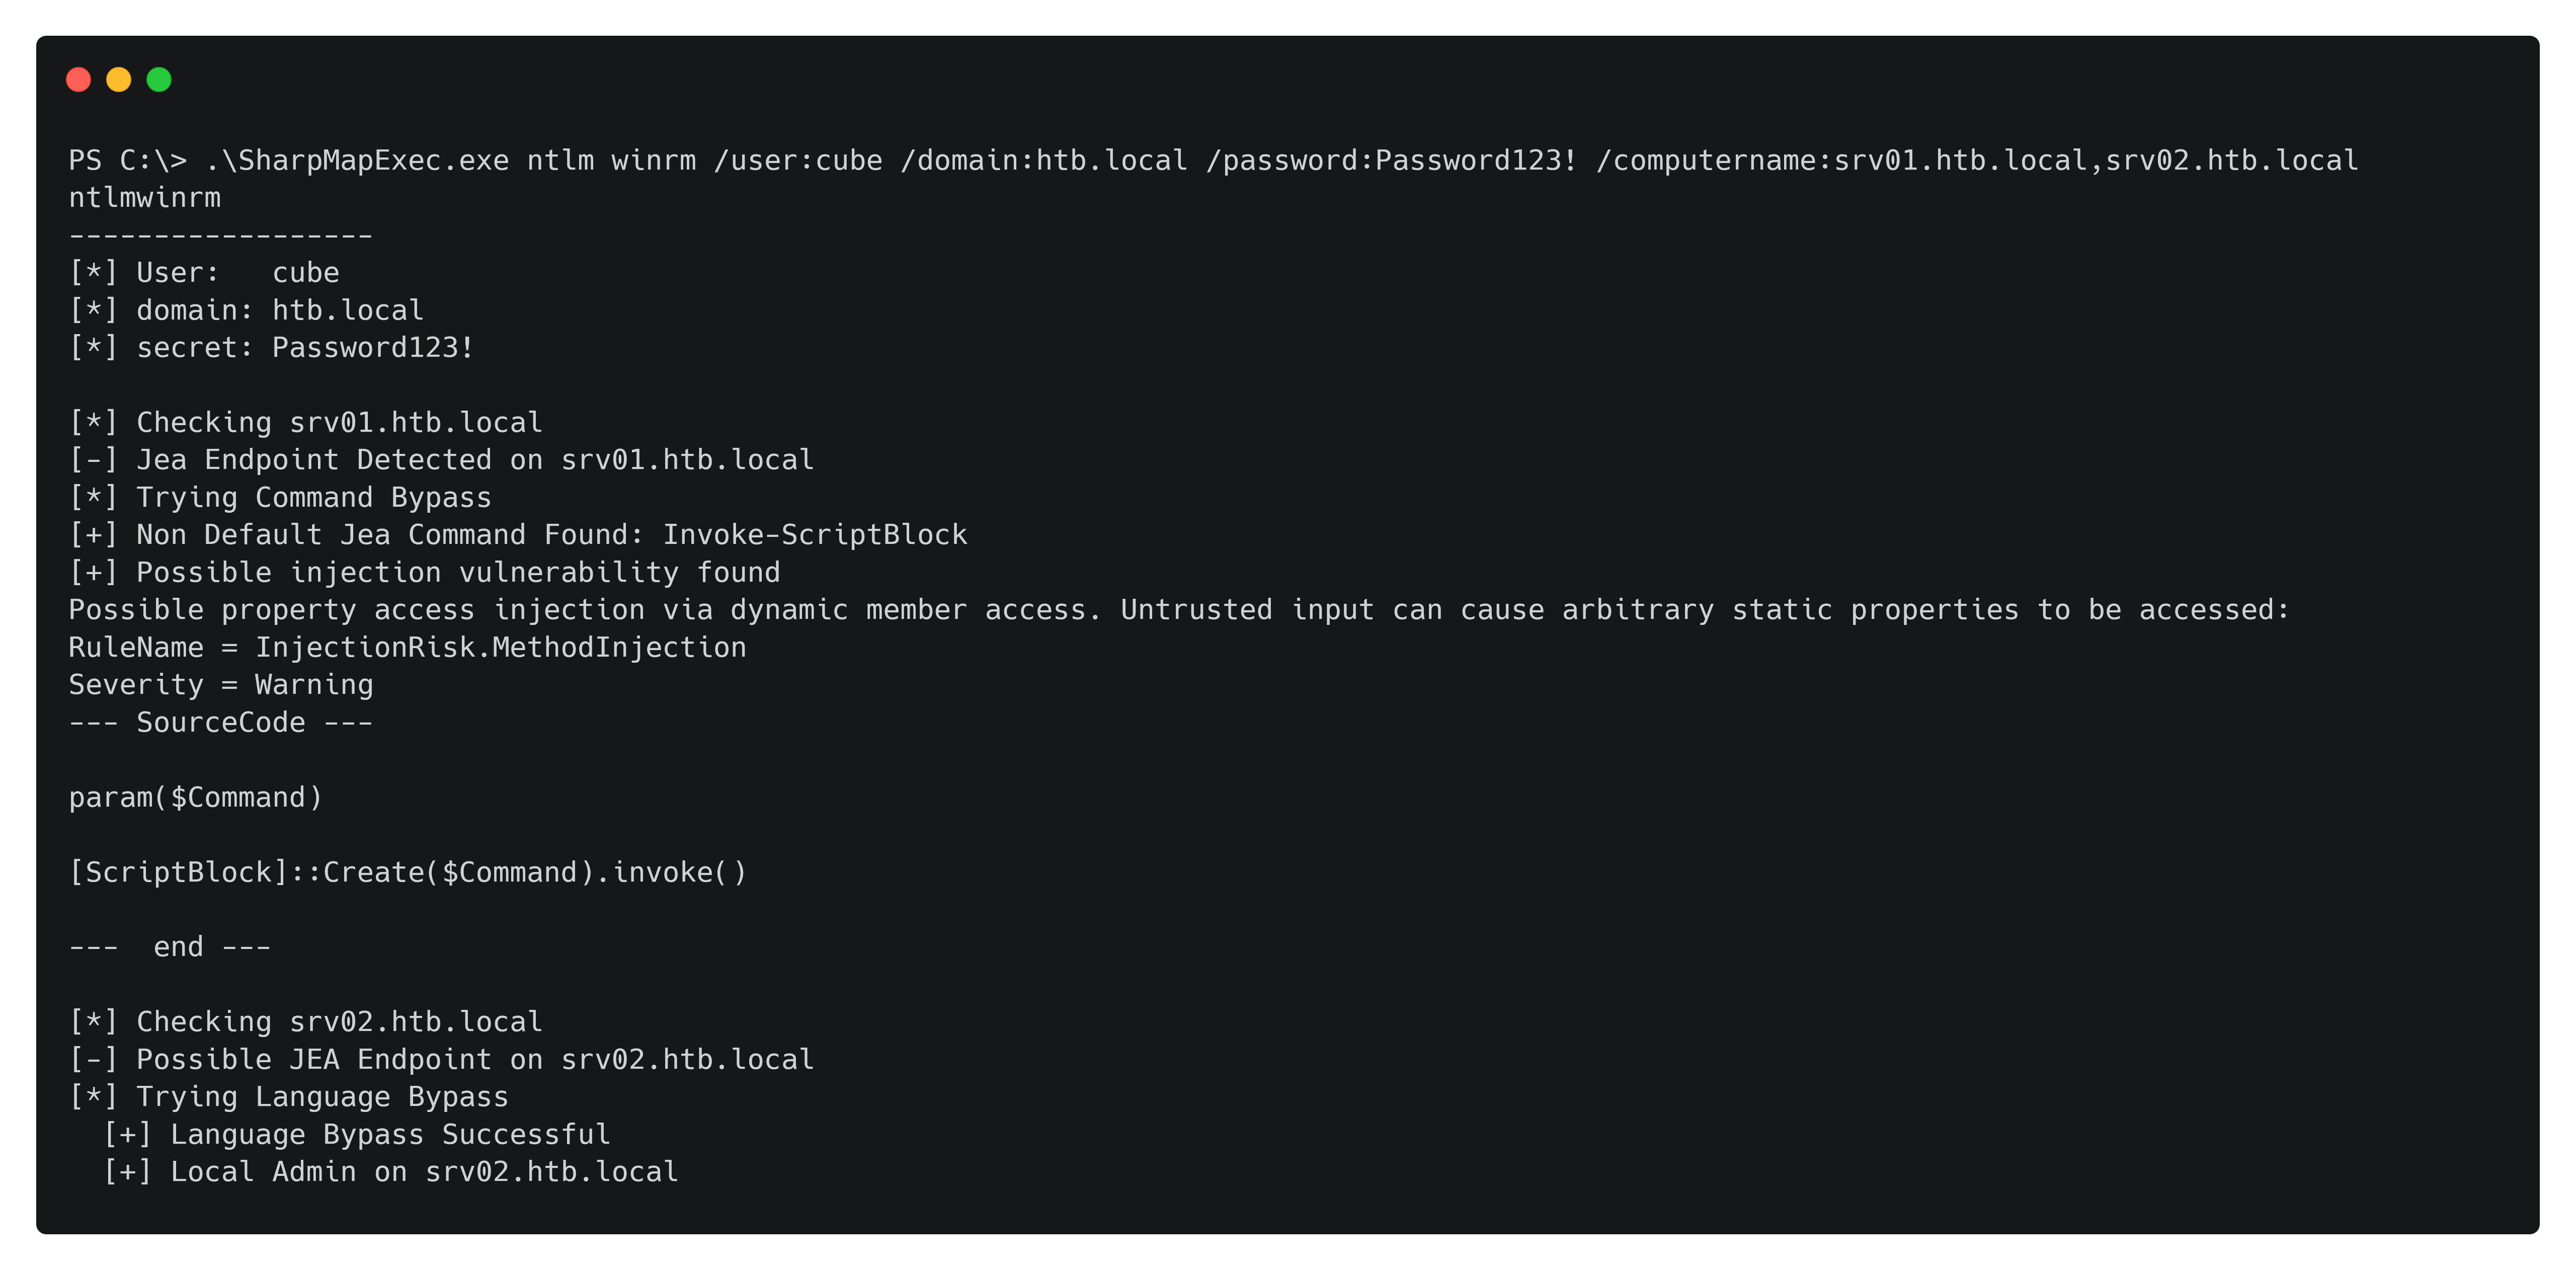 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
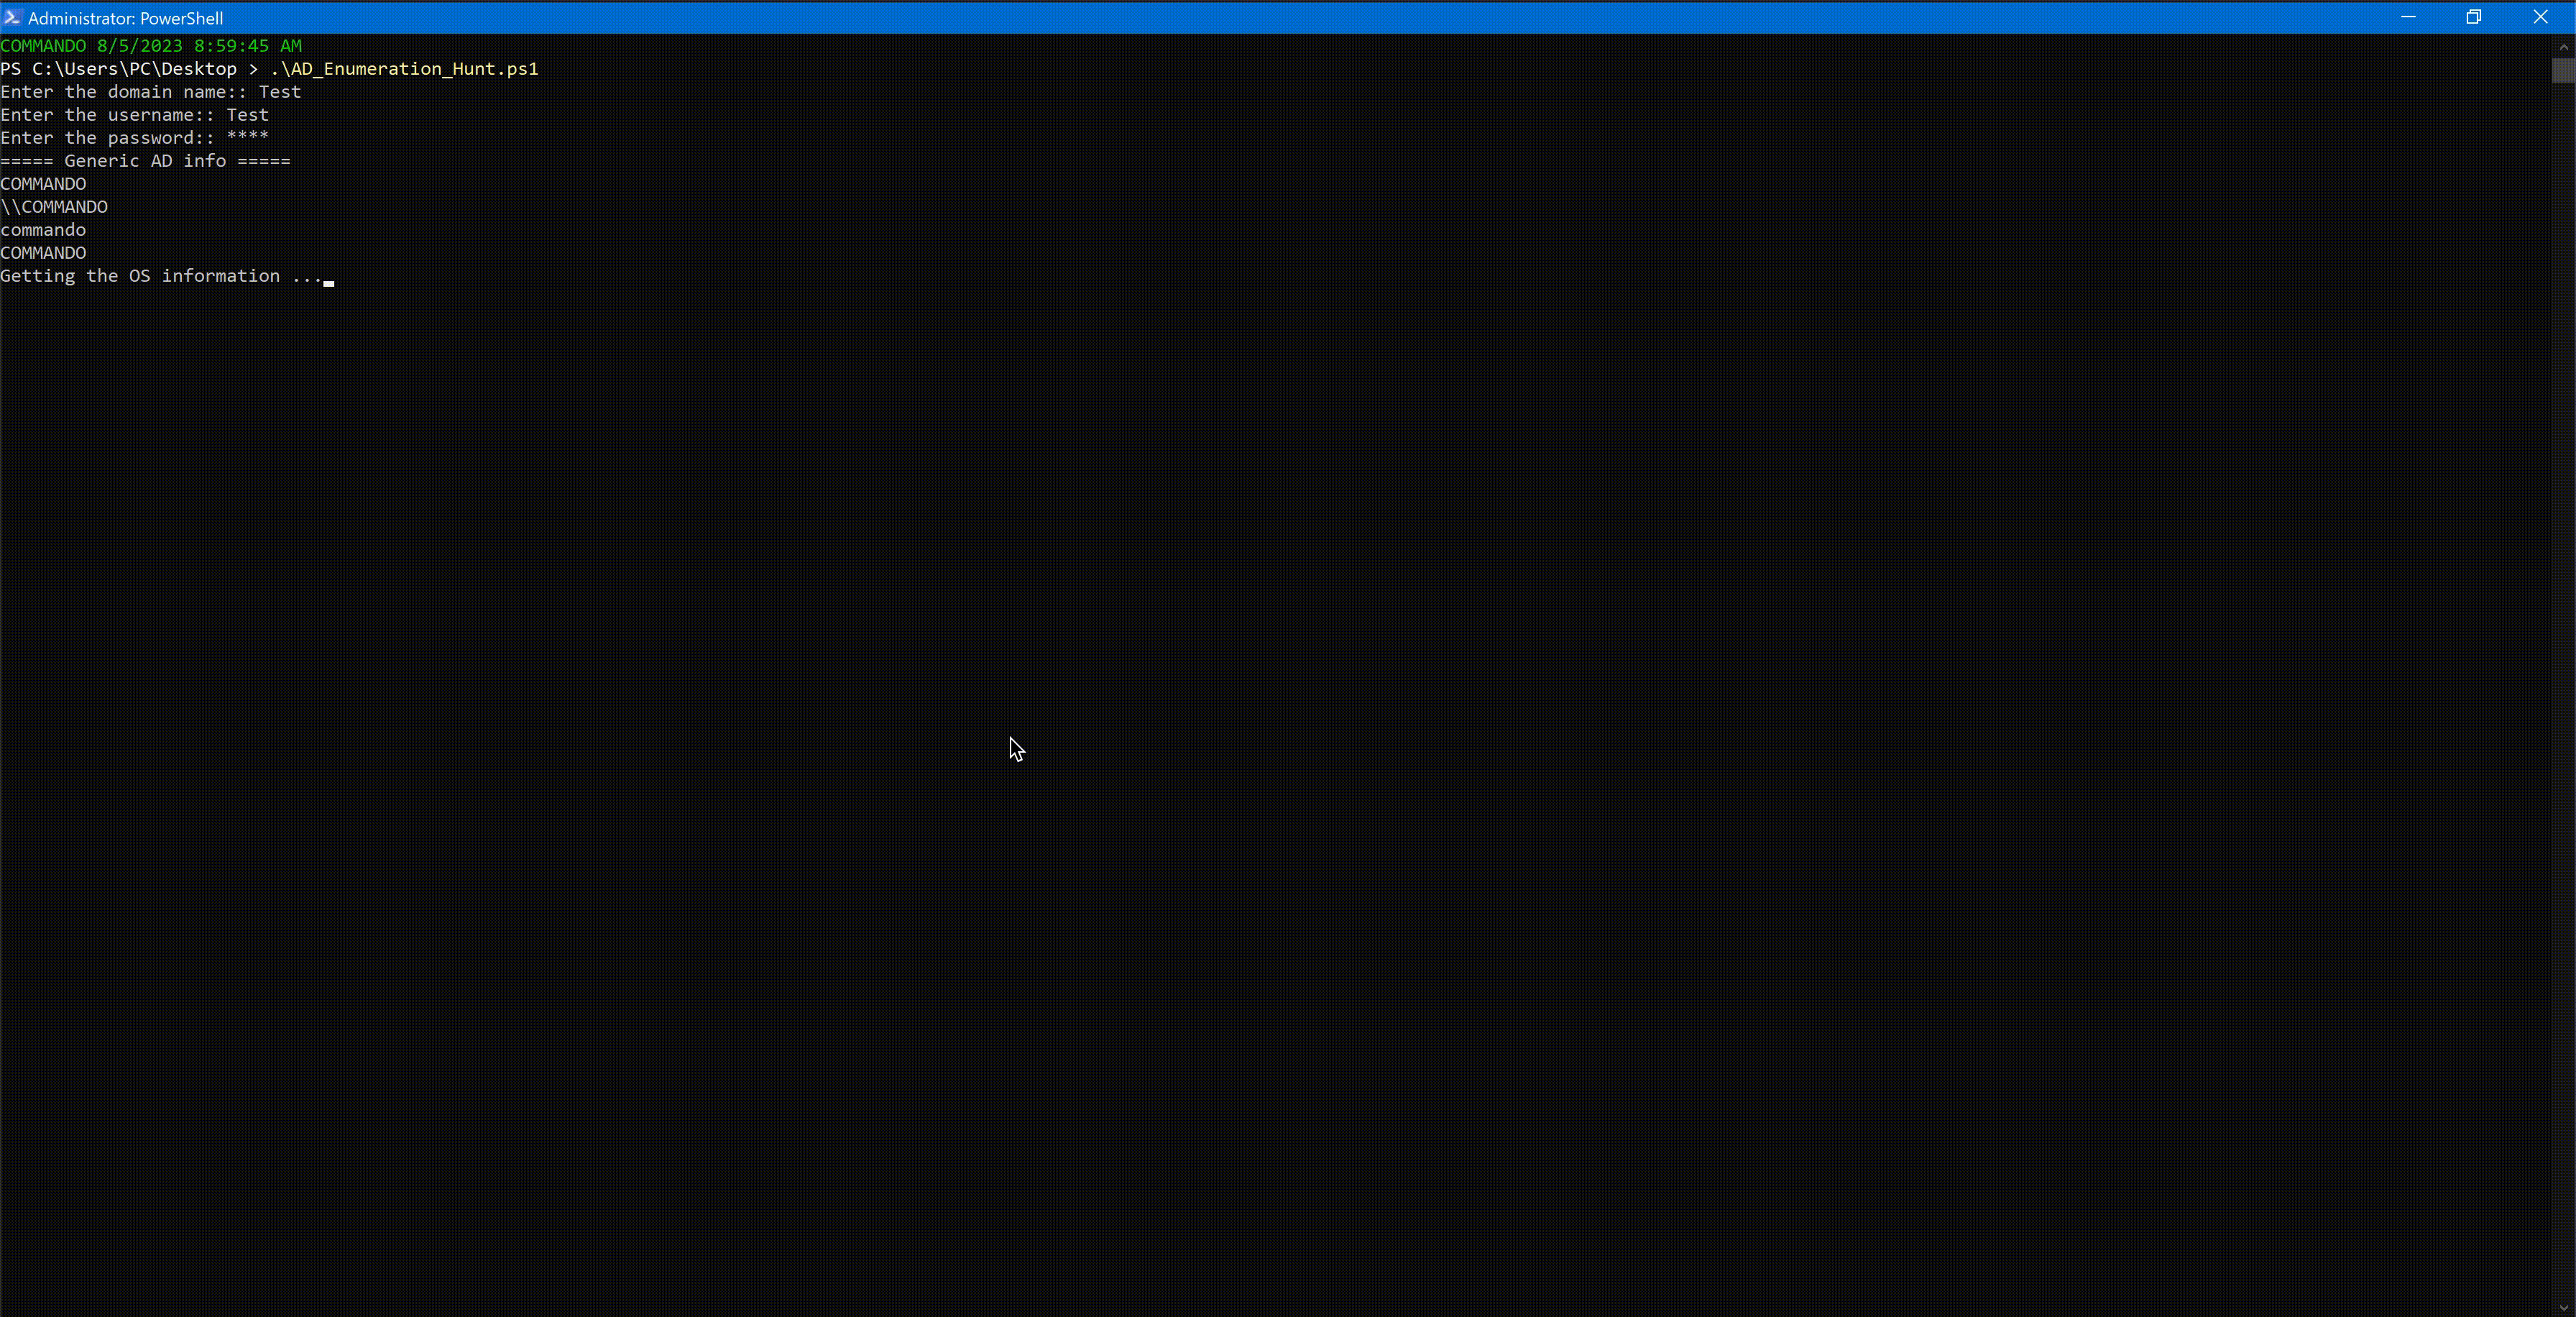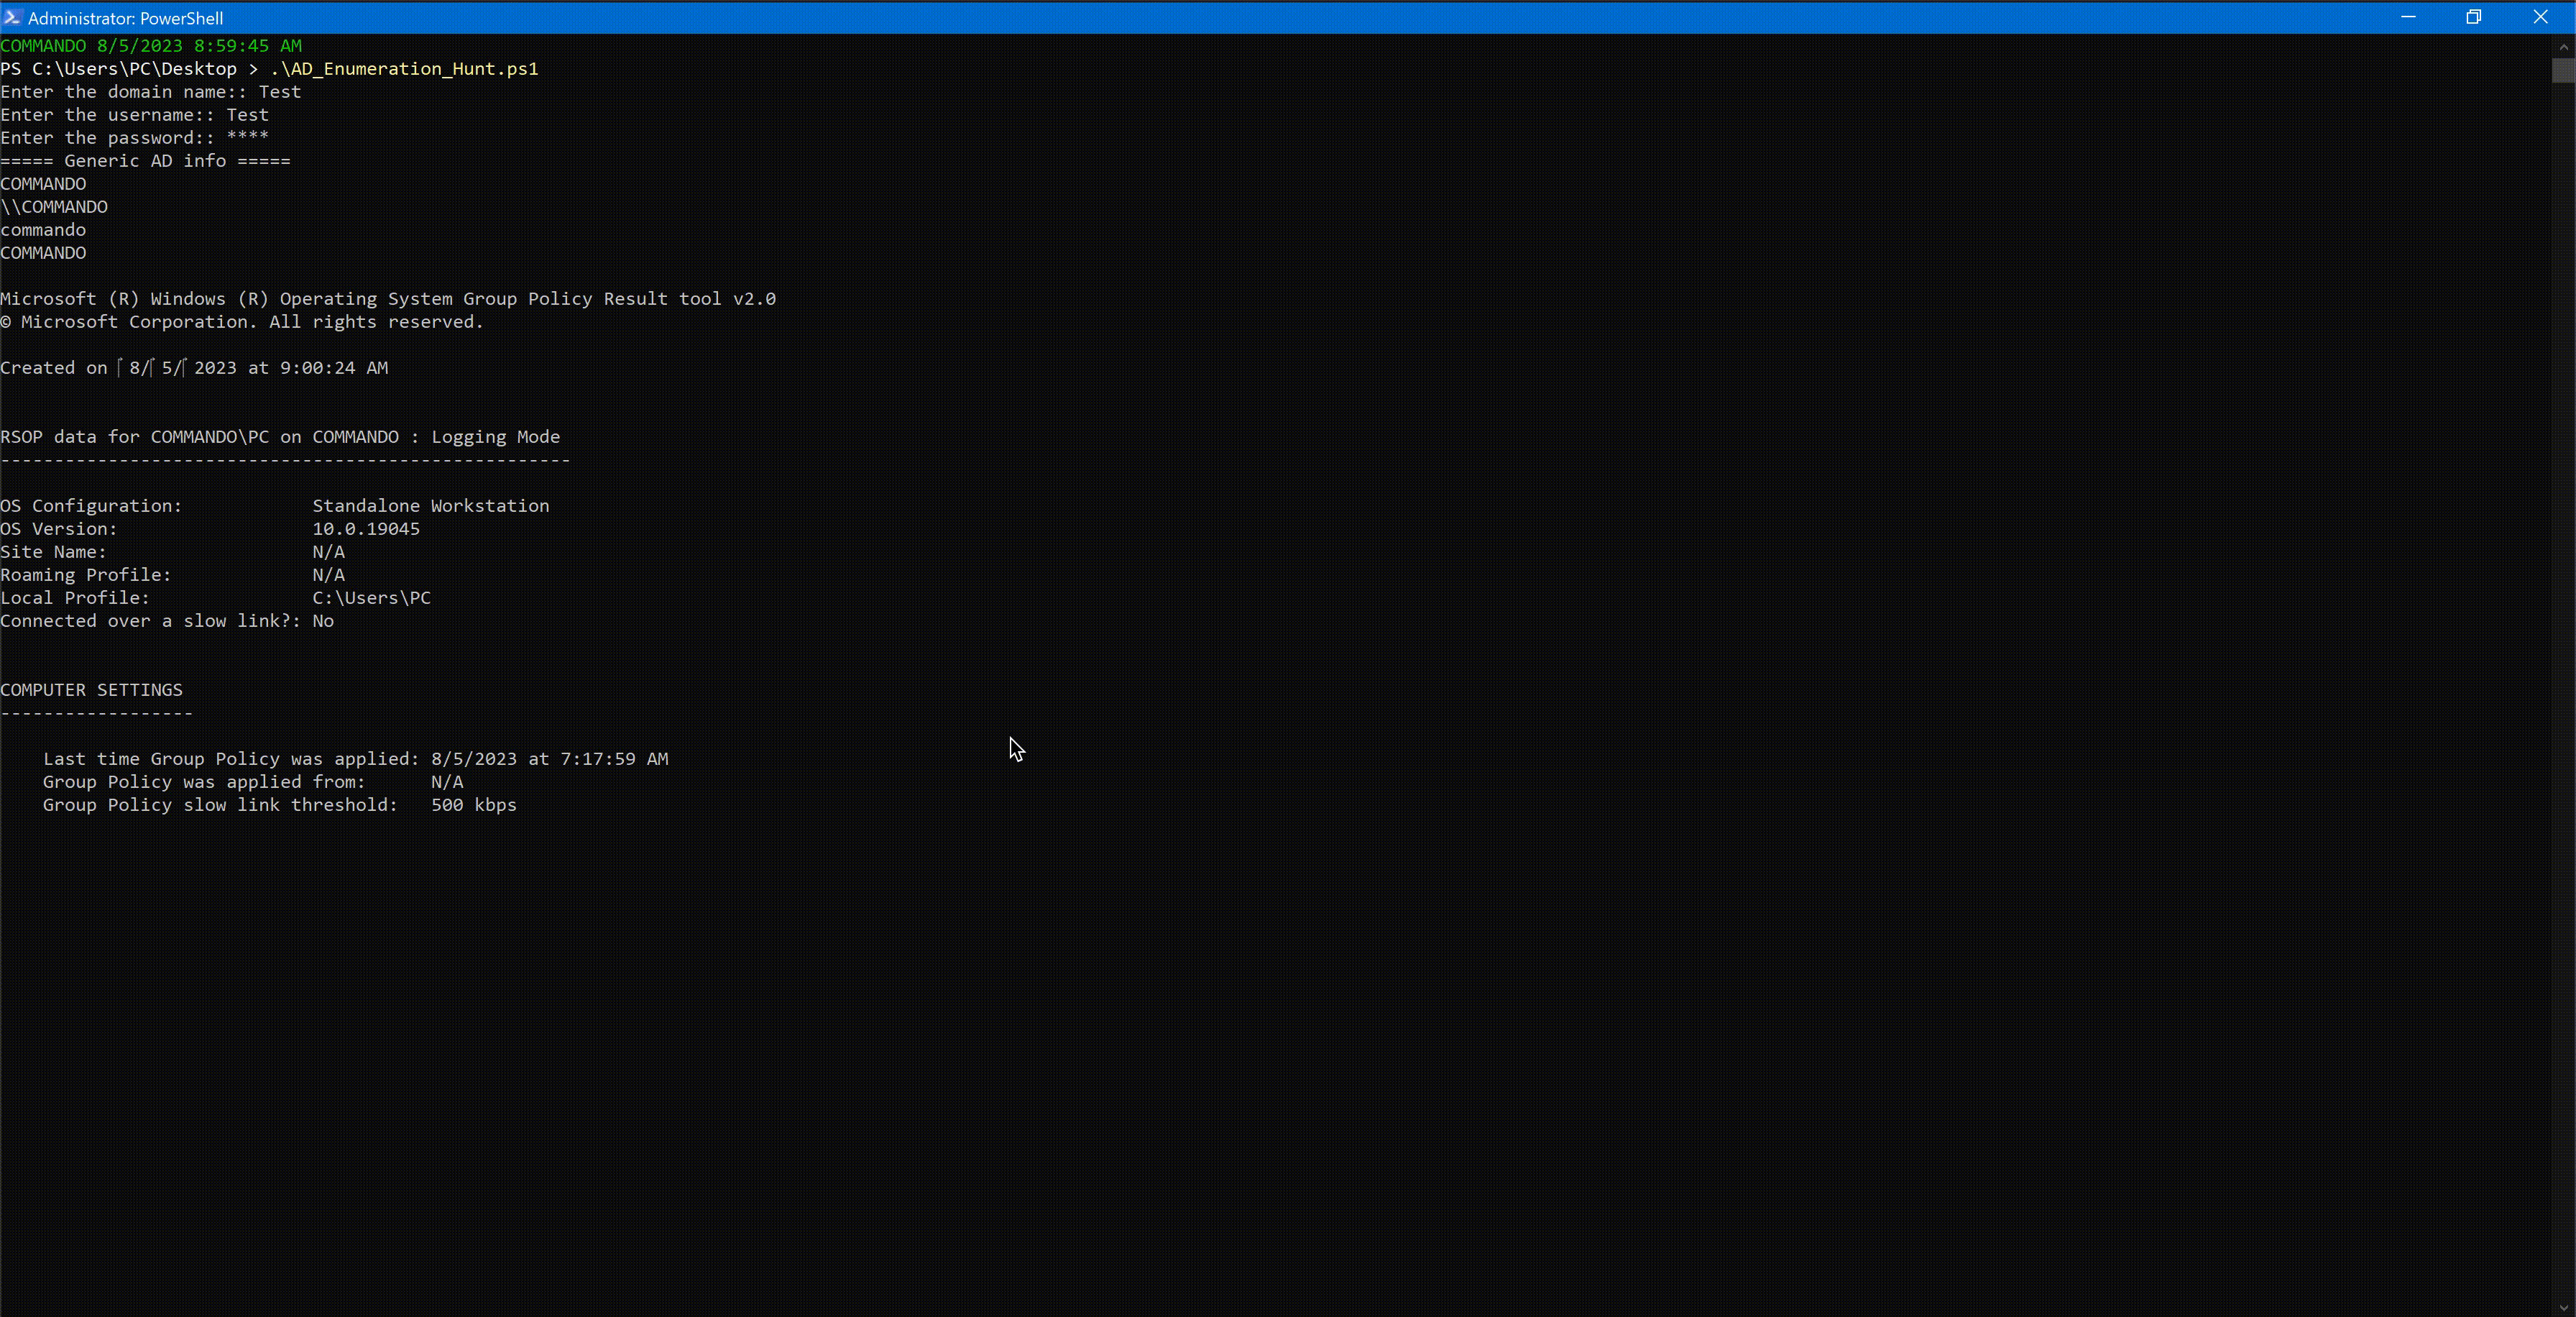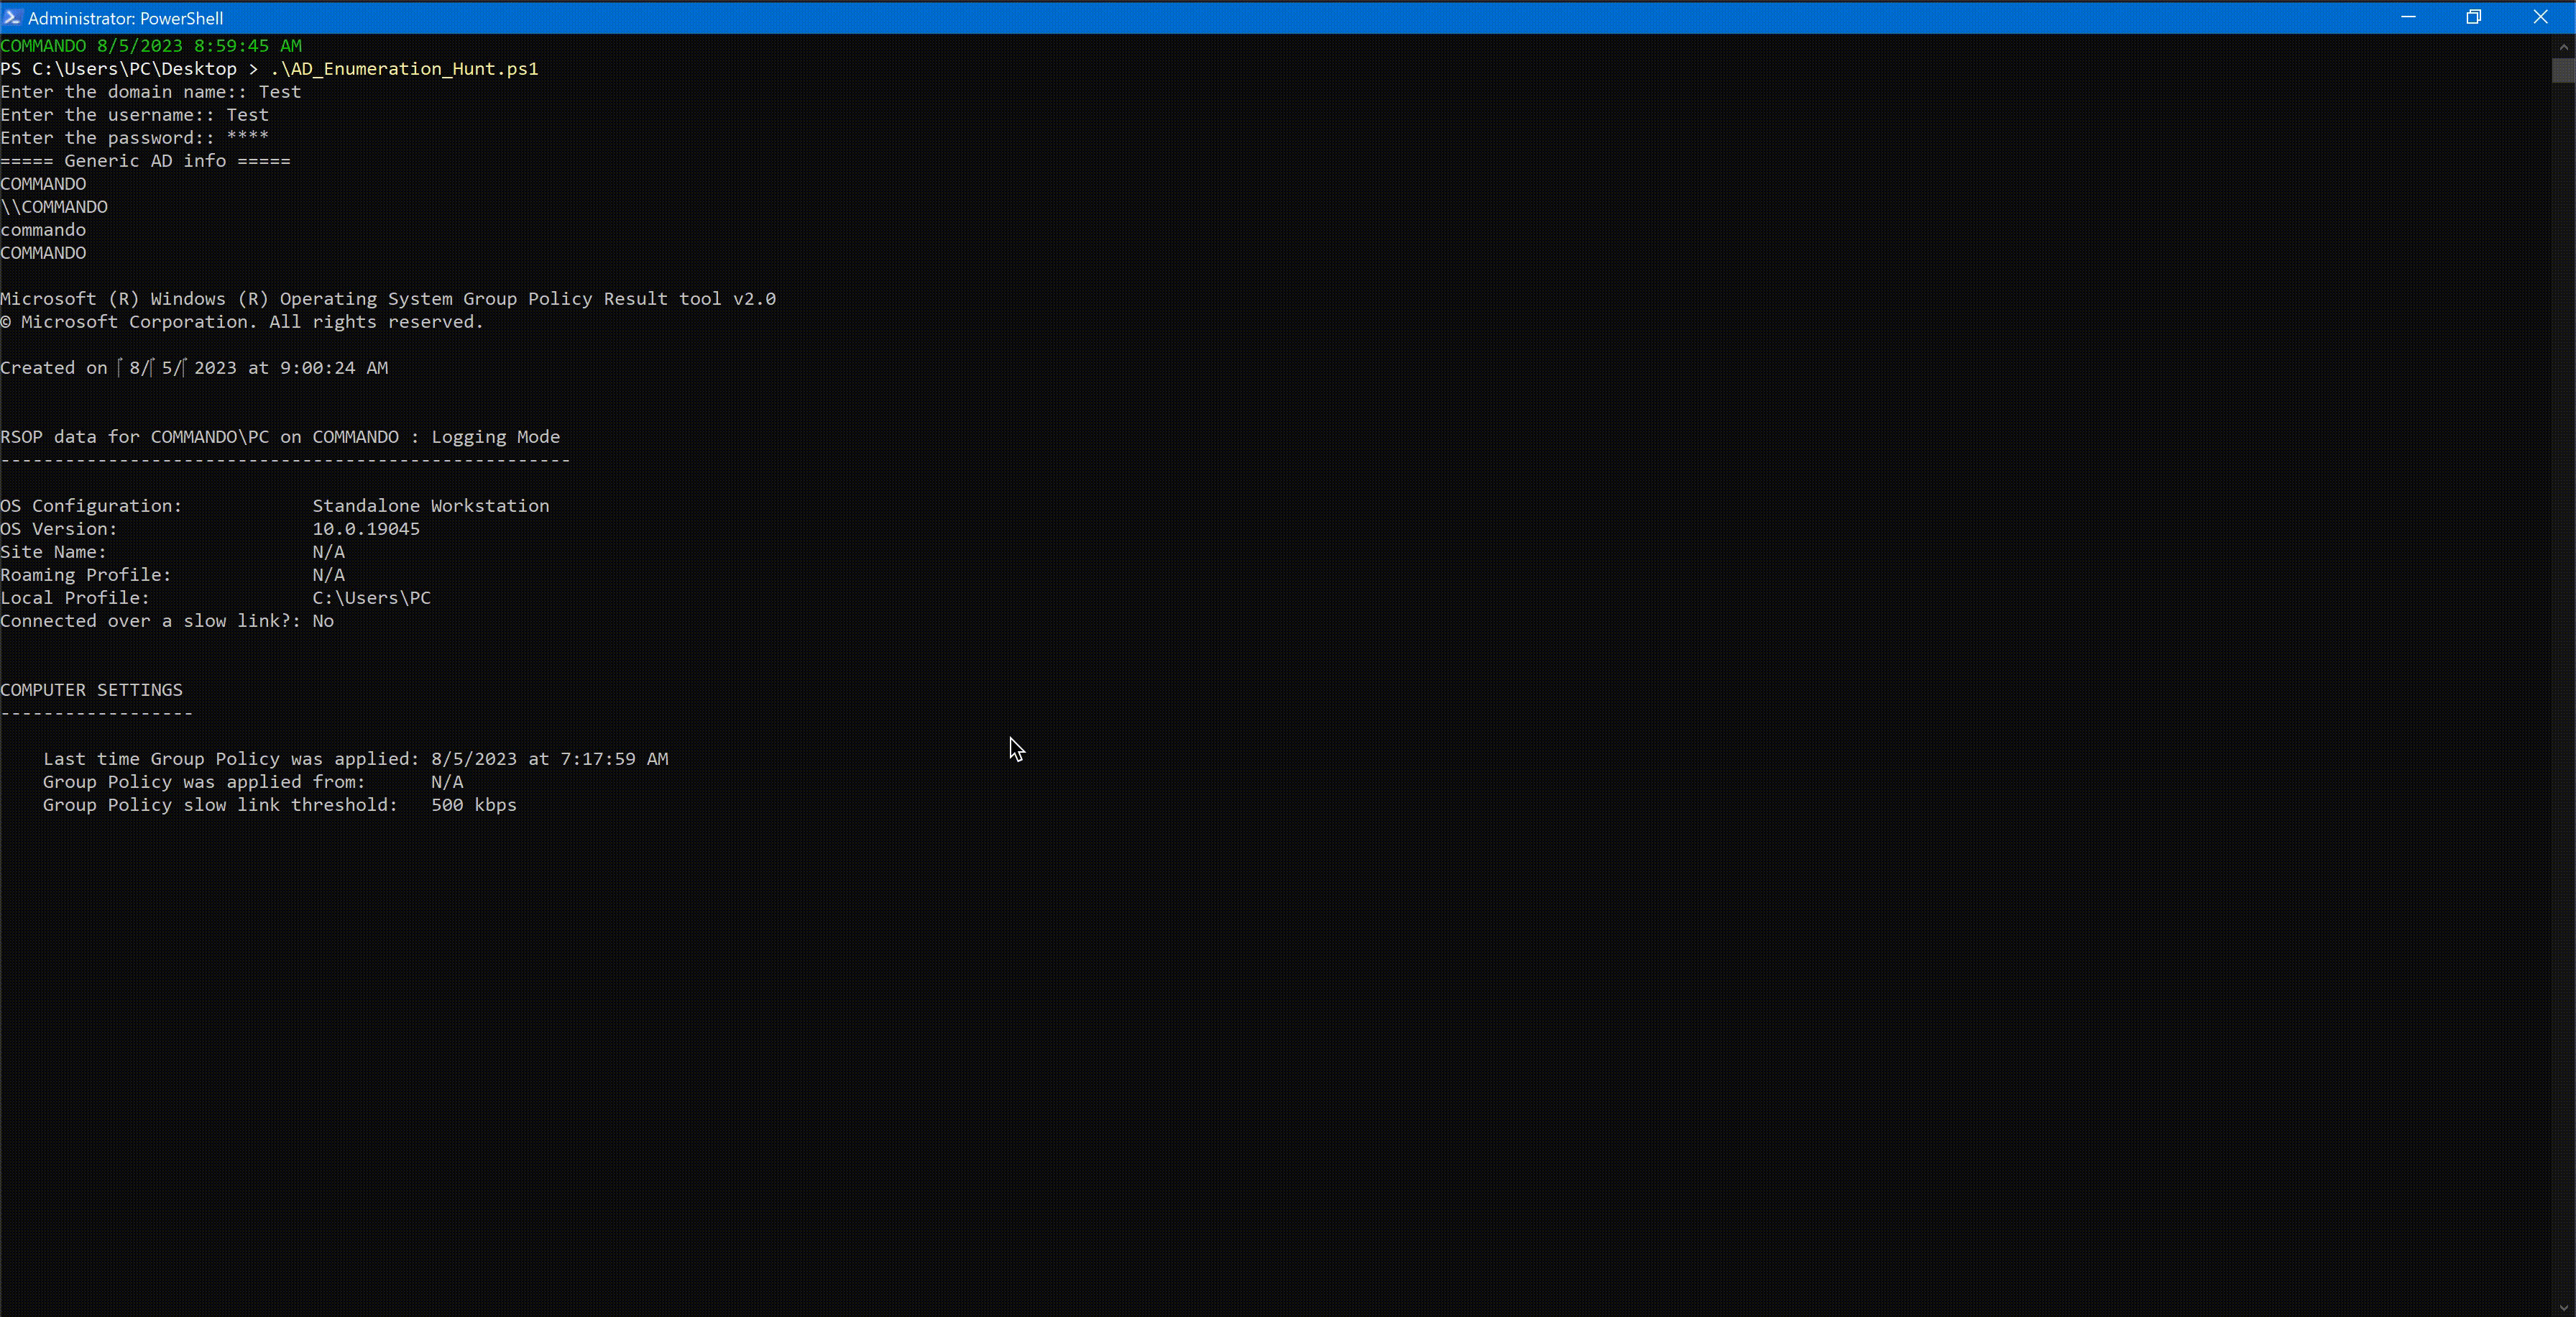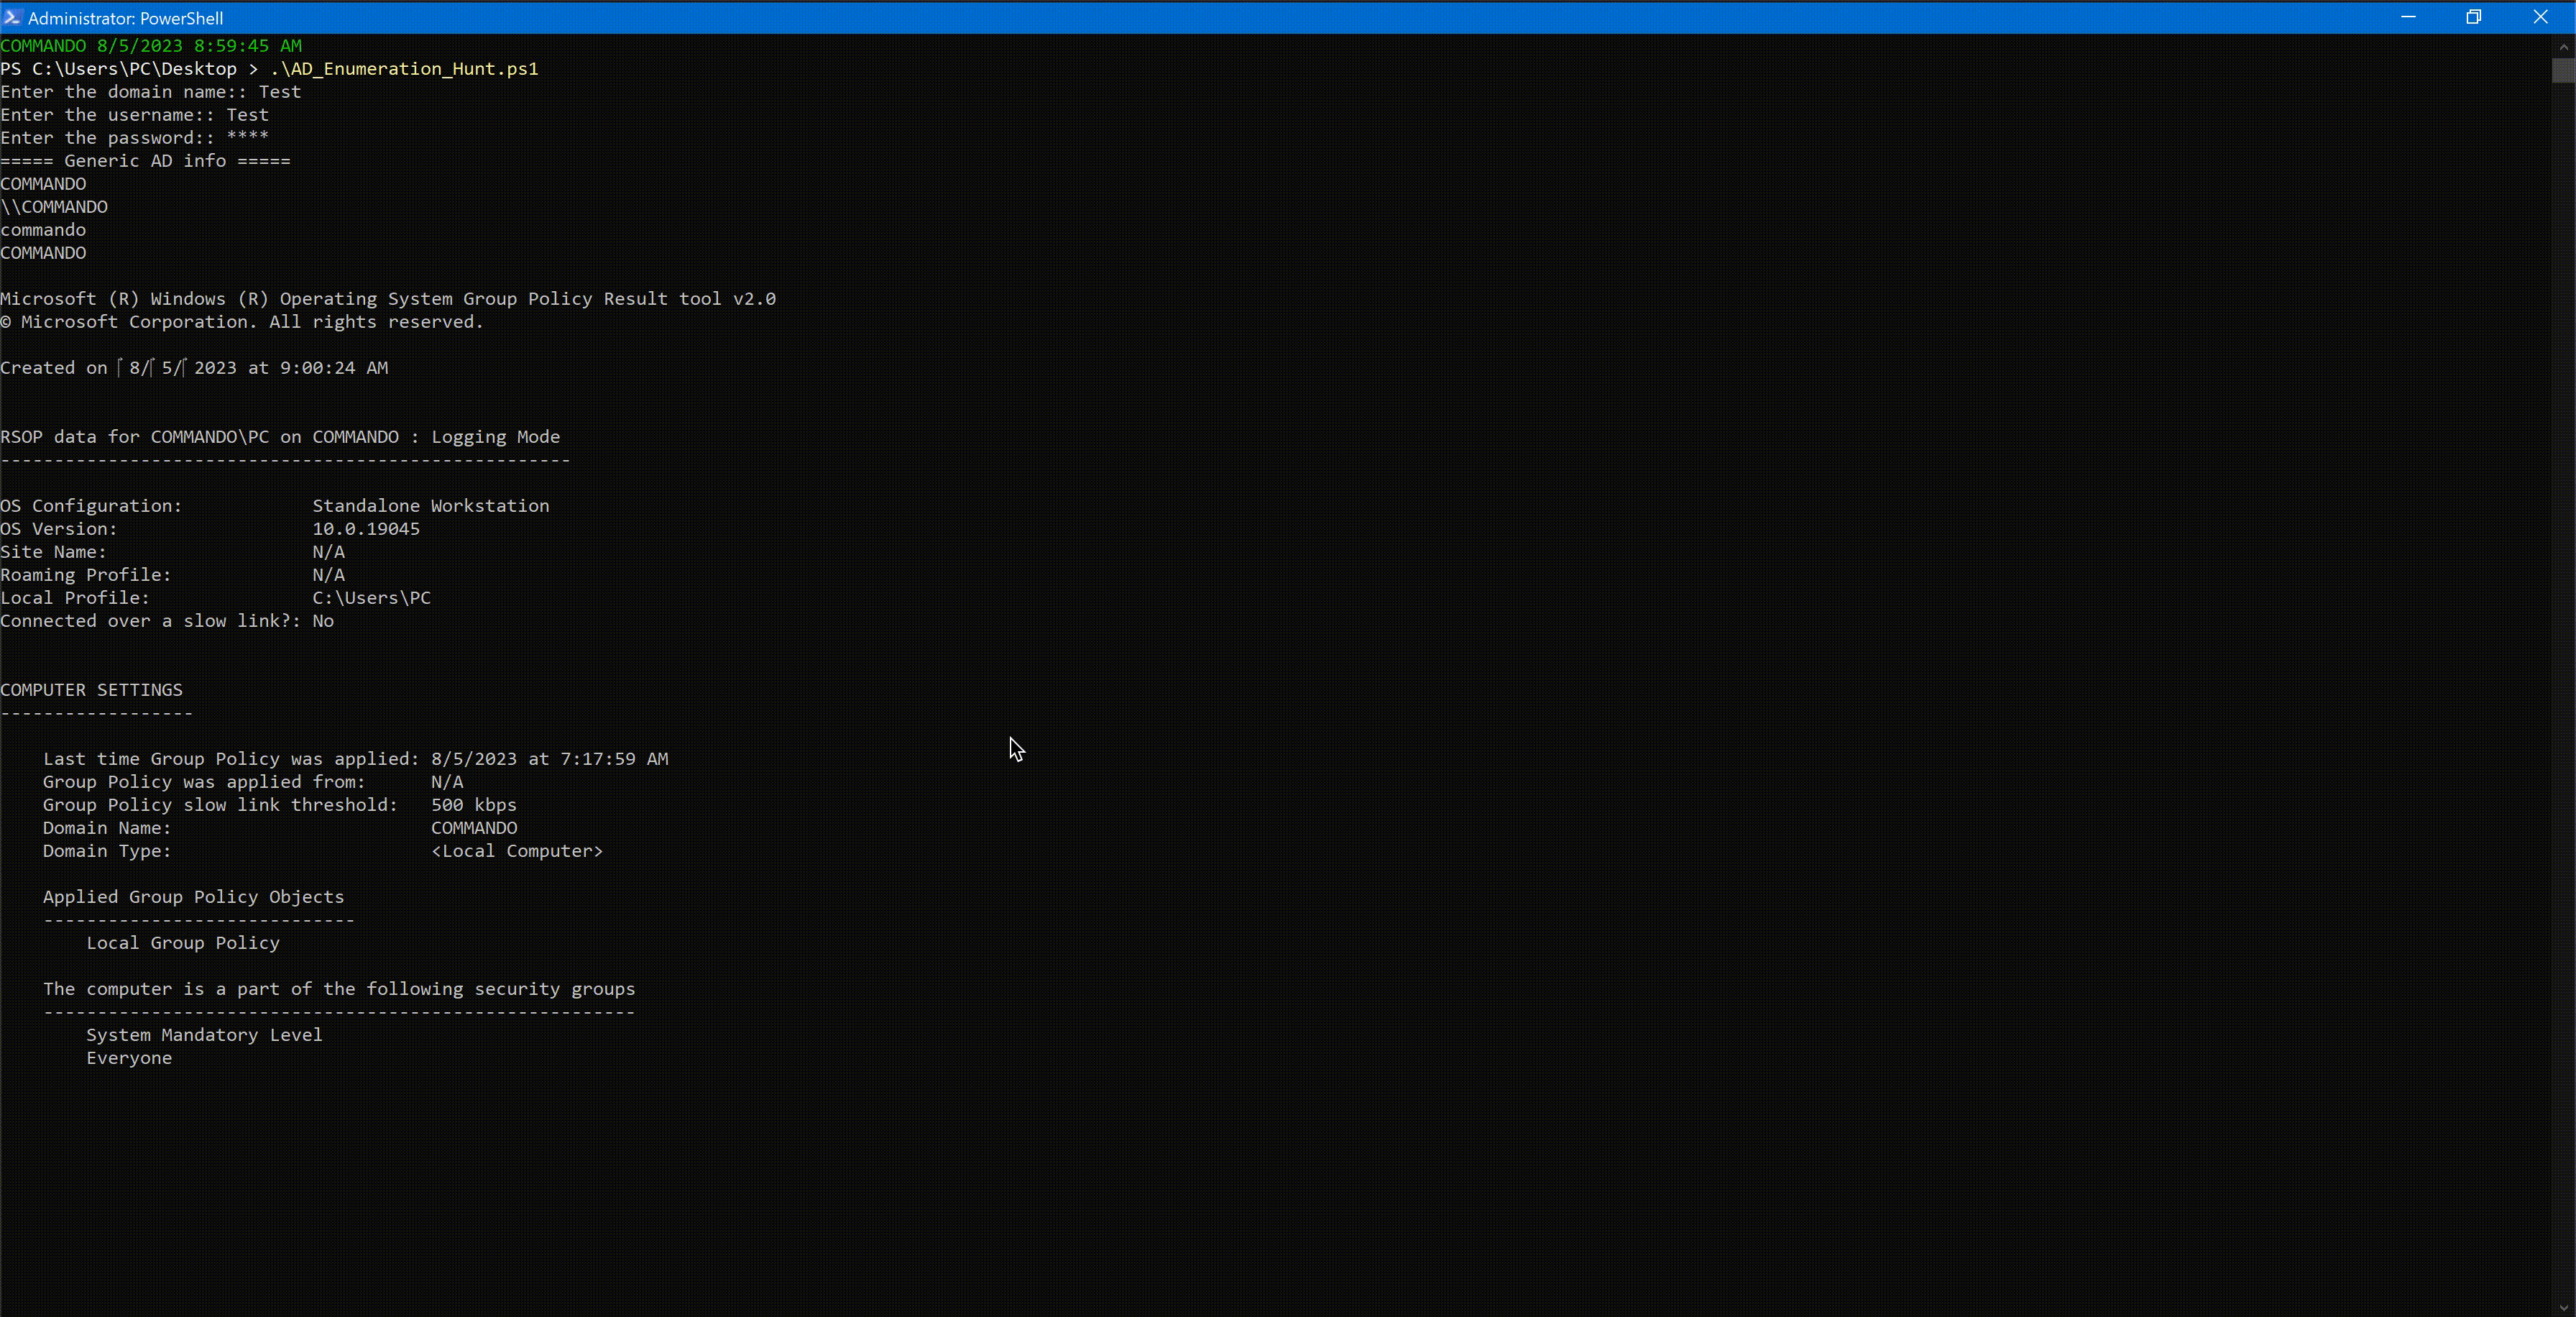 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
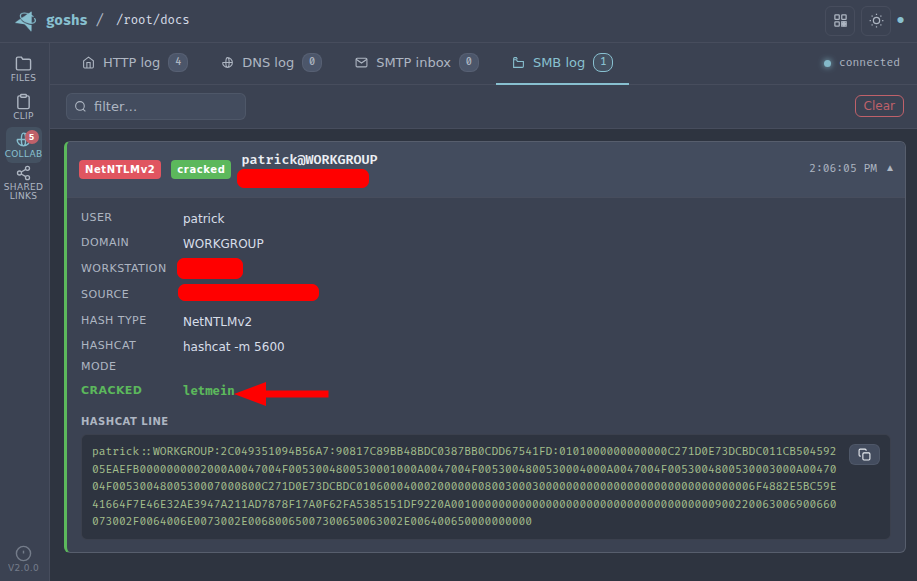 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing