
CVE-2025-50505
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
command-and-controldns-analysisexploitation+8
20
a0yami/cve-2025-50505Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 emptymonkey/revsh
A reverse shell with terminal support, data tunneling, and advanced pivoting capabilities.
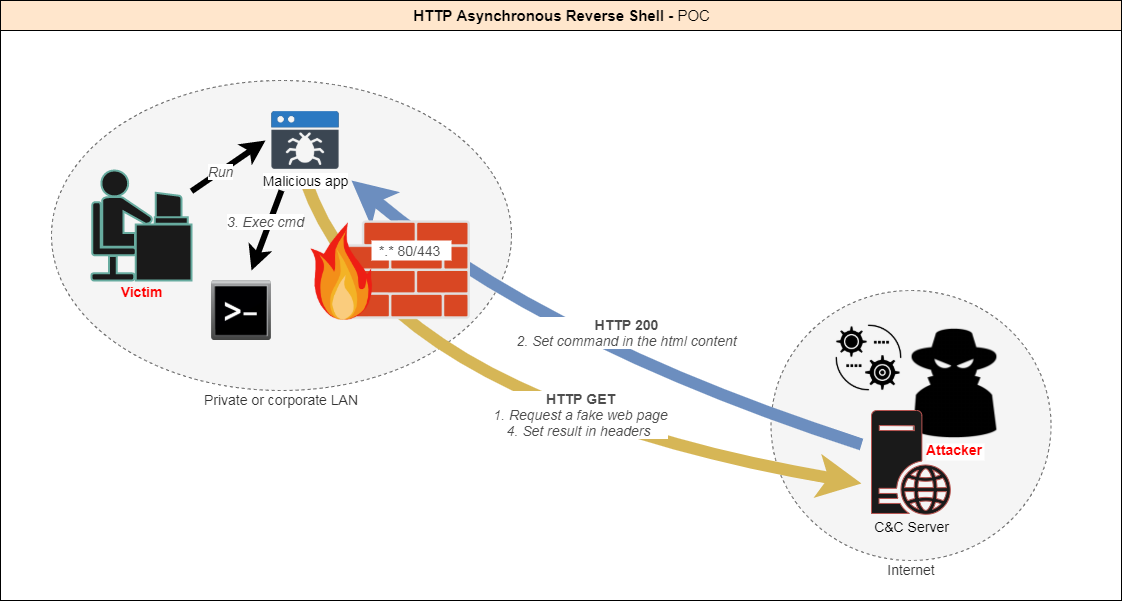 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 al1ex/cve-2020-11652
Exploit for SaltStack CVEs (CVE-2020-11651/11652) enabling remote command execution on master/minions, file read/upload, and reverse shell.
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 z50913/cve-2020-27955
Proof-of-concept exploit for CVE-2020-27955 in Git-LFS, demonstrating remote code execution via a crafted git clone operation to obtain a reverse…