
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
8 results
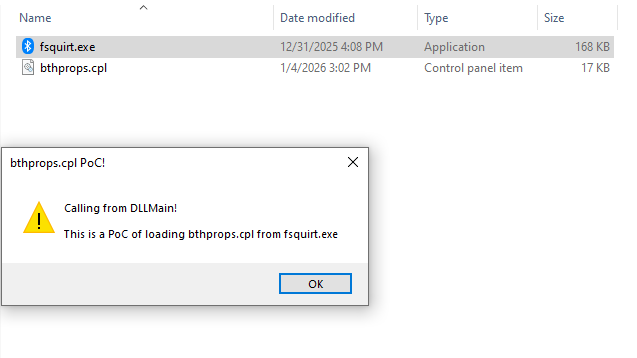
FsquirtCPLPoC preview

FsquirtCPLPoC

GitHubmhaskar/fsquirtcplpoc

PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
binary-exploitationcommand-and-controlexploitation+5
122
8 months ago
Rootsmart-v2.0 preview
Archived

Rootsmart-v2.0

GitHubnicchongwb/rootsmart-v2.0

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
android-securitycommand-and-controldata-exfiltration+8
14 years ago
CVE-2024-38472 preview

CVE-2024-38472

GitHubabdurahmon3236/cve-2024-38472

Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.

command-and-controlexploit-frameworkslateral-movement+6
42 years ago
smbtakeover preview

smbtakeover

GitHubzyn3rgy/smbtakeover

BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions

authentication-authorizationlateral-movementpenetration-testing+2
3621 year ago
scour preview

scour

GitHubgrines/scour

Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
cloud-securityexploitationlateral-movement+4
1272 years ago
BadSamba preview

BadSamba

GitHubstrozfriedberg/badsamba

This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
exploitationlateral-movementnetwork-security+3
226 years ago
AzureRT preview

AzureRT

GitHubmgeeky/azurert

AzureRT - A Powershell module implementing various Azure Red Team tactics
authenticationcloud-securityinformation-gathering+5
2334 years ago
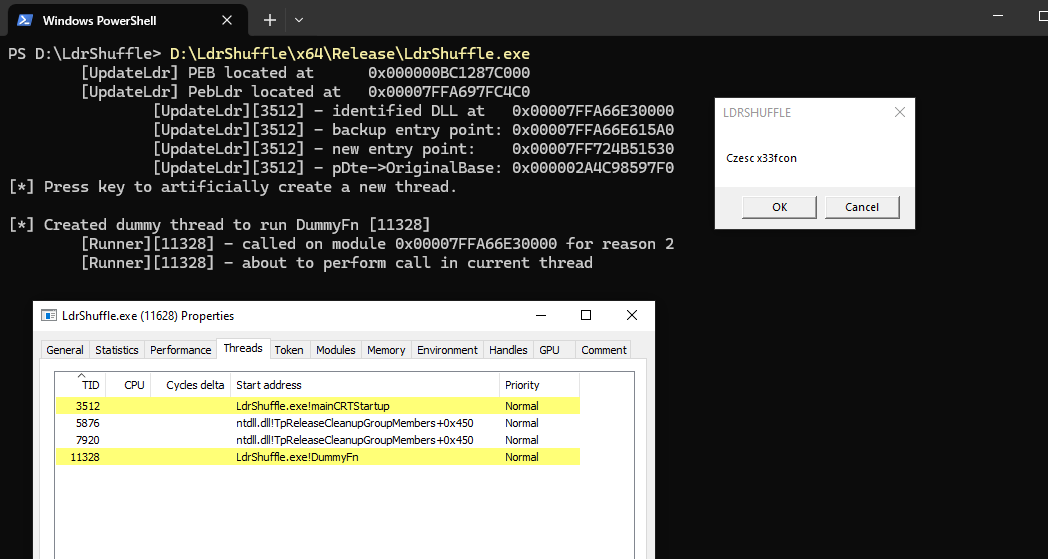
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation

binary-exploitationcode-analysisexploitation+6
2881 year ago