

sliver-gui
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
cloud-securitycommand-and-controllateral-movement+7
180
sliverarmory/sliver-guiCross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
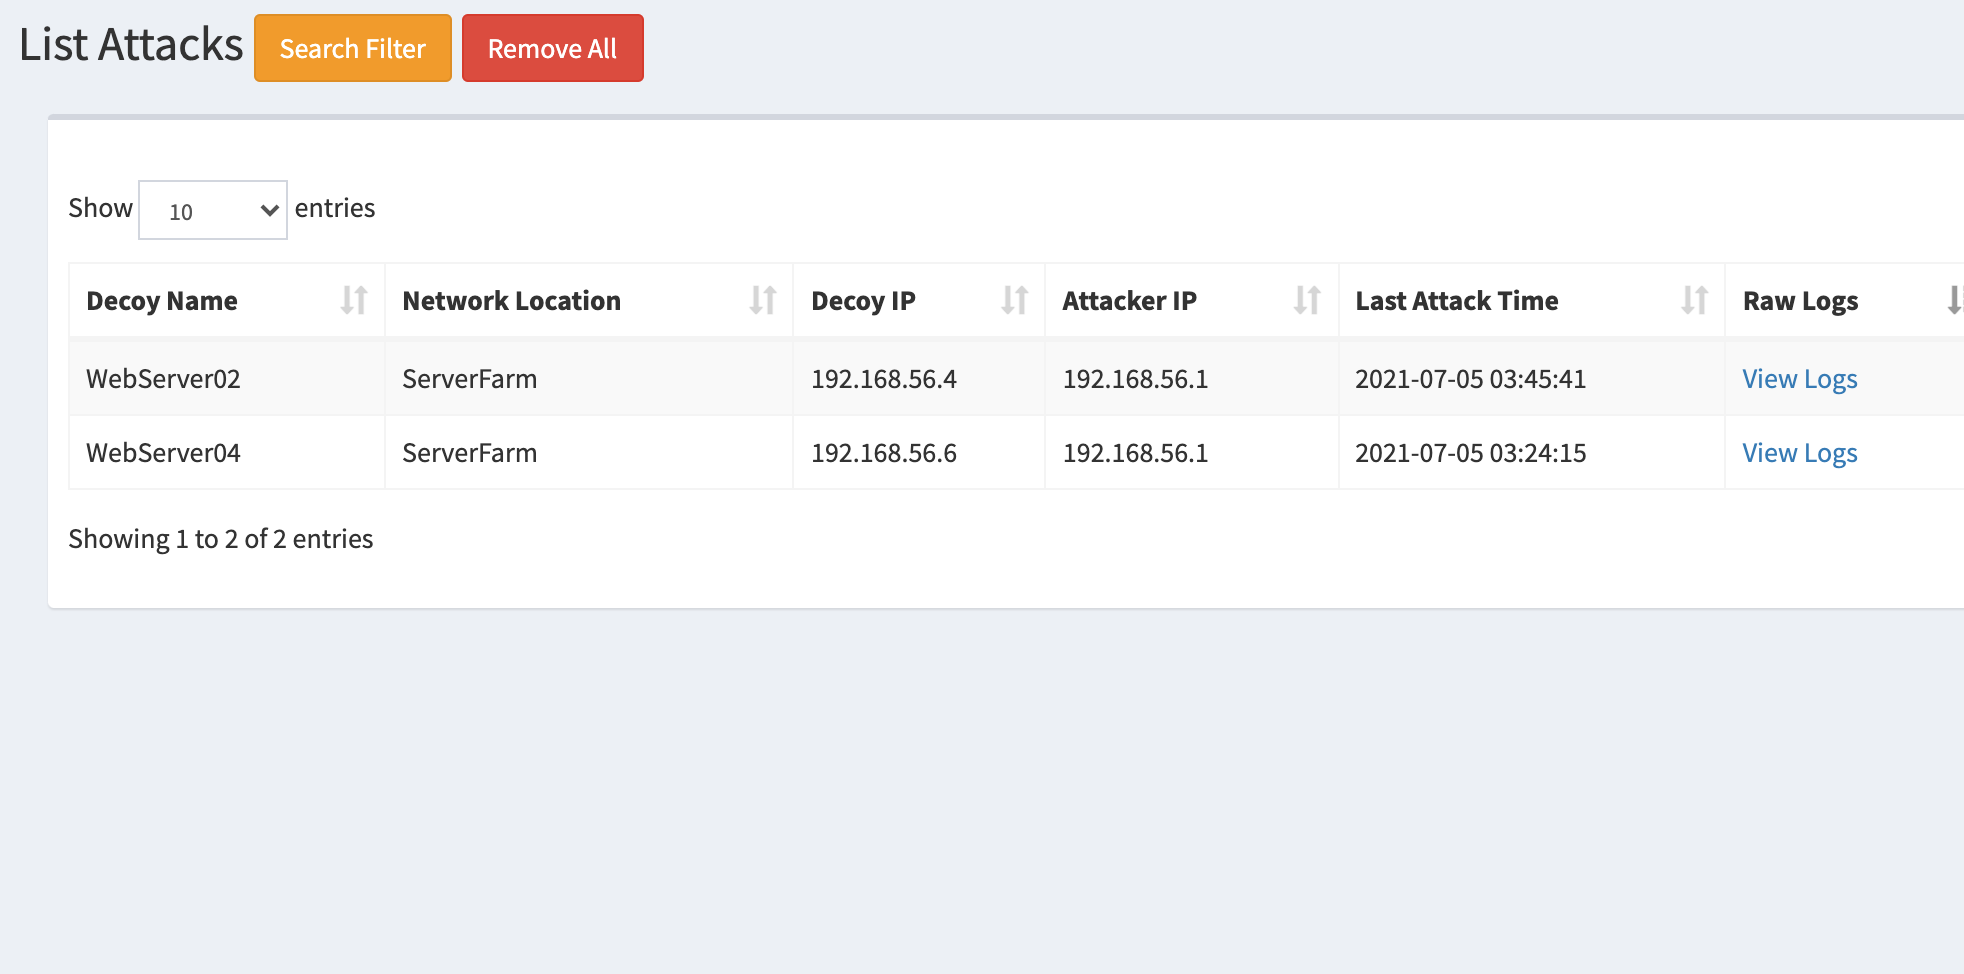 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
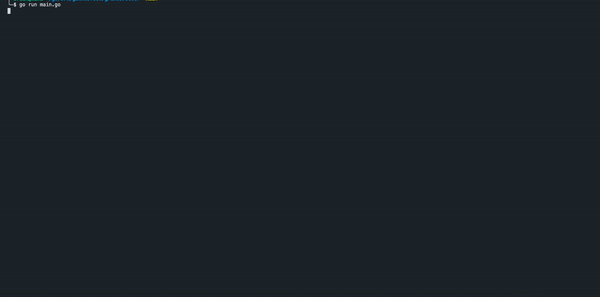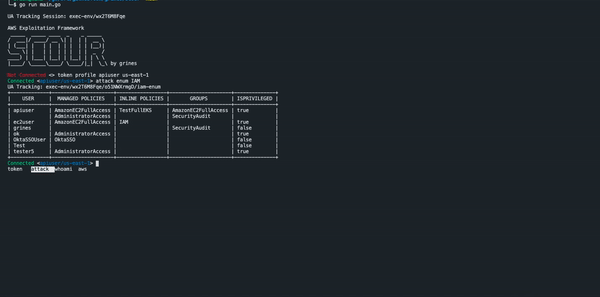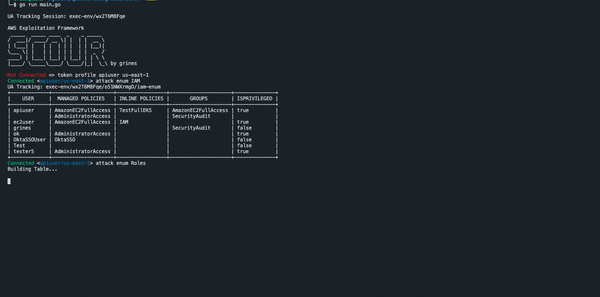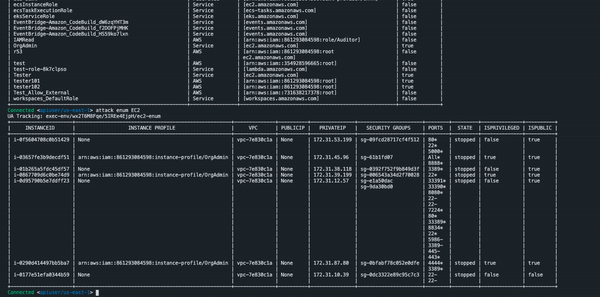 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
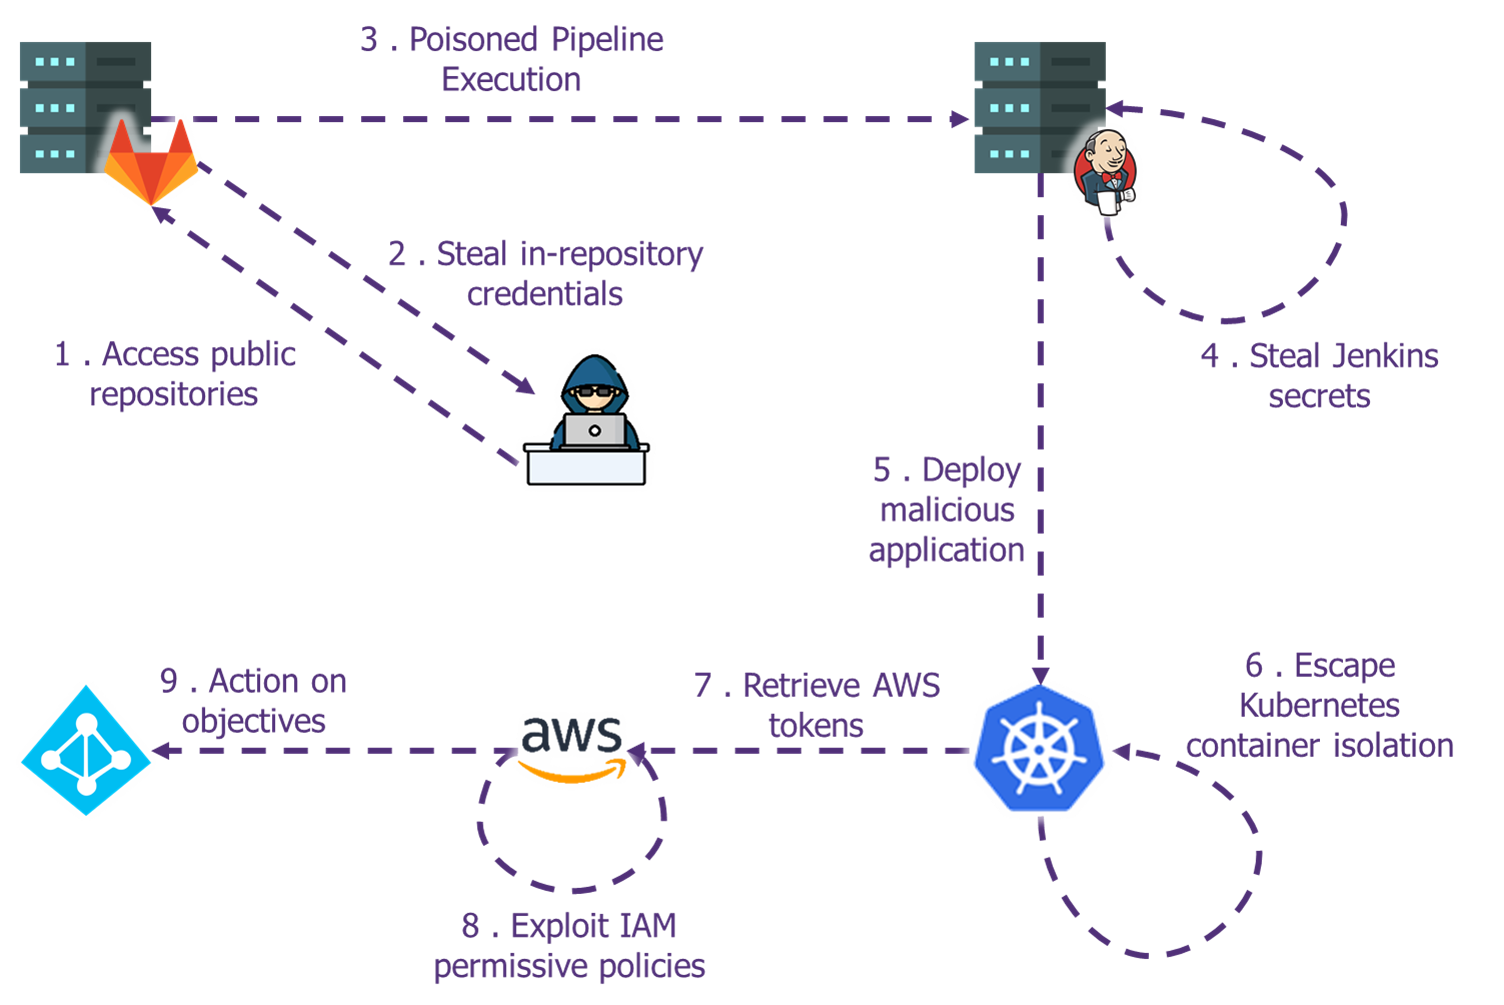 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…