
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
35 results
CVE-2022-30190 preview

CVE-2022-30190

GitHubdoocop/cve-2022-30190

Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…

educationexploitationlabs-practice+3
59
4 years ago
OWASPBugBounty preview

OWASPBugBounty

GitHubowasp/owaspbugbounty

This is a container of web applications that work with OWASP Bug Bounty for Projects
ctfeducationlabs-practice+3
341 year ago
cybersecurity-projects preview

cybersecurity-projects

GitHubosxninja/cybersecurity-projects

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
ai-securitycurated-resourcesdigital-forensics+7
2811 days ago
CVE-2025-7384 preview

CVE-2025-7384

GitHubdungsocool/cve-2025-7384

Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
educationexploitationlabs-practice+2
1 month ago
CVE-2026-75816 preview

CVE-2026-75816

GitHubabraxas/cve-2026-75816

Proof-of-concept and lab reproduction for CVE-2026-75816, an unauthenticated WordPress Frontend Admin account takeover via admin-ajax form submission.
authenticationexploitationlabs-practice+4
9 days ago
CVE-2018-7600 preview

CVE-2018-7600

GitHubdungsocool/cve-2018-7600

Step-by-step lab walkthrough for exploiting CVE-2018-7600 (Drupalgeddon2) RCE in Drupal 8.5.0, covering attack surface analysis, version…

educationexploitationlabs-practice+3
4 months ago
CVE-2024-5084-Red-Team preview

CVE-2024-5084-Red-Team

GitHubredteamblueteam/cve-2024-5084-red-team

Proof-of-concept exploit for CVE-2024-5084 (Hash Form WordPress plugin) demonstrating unauthenticated file upload to RCE. Designed for educational…
educationexploitationlabs-practice+4
17 months ago
cve-2025-55182 preview

cve-2025-55182

GitHubliamromanis101/cve-2025-55182

Python exploit for CVE-2025-55182, a server-side JavaScript injection in Next.js/React enabling remote code execution via malformed multipart form…
educationexploitationlabs-practice+3
9 months ago
lab-cve-2016-15042 preview

lab-cve-2016-15042

GitHubimbios/lab-cve-2016-15042

CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
ctfeducationlabs-practice+3
11 year ago
CVE-2025-64459 preview

CVE-2025-64459

GitHubz3yr0xx/cve-2025-64459

CTF challenge demonstrating Django ORM filter injection (CVE-2025-64459) with auth bypass and product filter bypass exploits, including deployment…
ctfeducationlabs-practice+3
9 months ago
LetsDefend-SOC173-Follina-0-Day-Detected preview

LetsDefend-SOC173-Follina-0-Day-Detected

GitHubarkha-corvus/letsdefend-soc173-follina-0-day-detected

We are presented with a security alert indicating the detection of the Follina (CVE-2022-30190) vulnerability. A malicious Word document triggered…
digital-forensicseducationincident-response+5
11 months ago
Log4Shell preview

Log4Shell

GitHubmgueye3/log4shell

This repository contains my work for a cybersecurity assignment where I exploited the real-world Log4Shell (CVE-2021-44228) vulnerability inside a…
ctfeducationexploitation+3
10 months ago
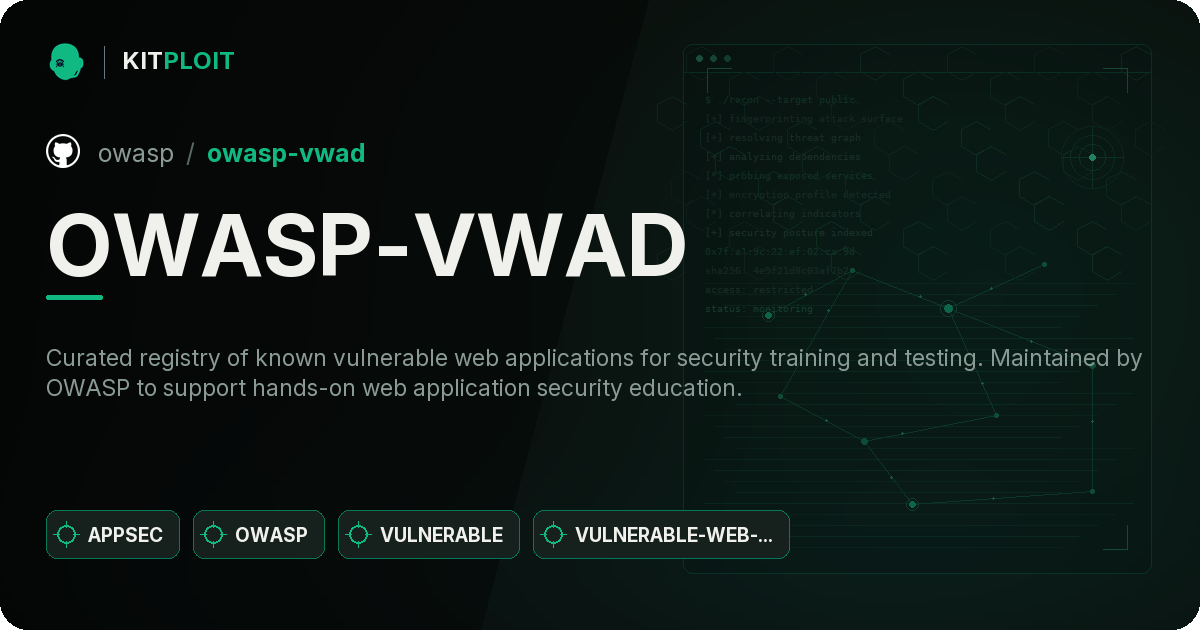
screenpipe preview

screenpipe

GitHubscreenpipe/screenpipe

YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
ctfcurated-resourceseducation+8
21.8k12h 32m ago
OWASP-VWAD preview

OWASP-VWAD

GitHubowasp/owasp-vwad

⚠️ This repo is no longer in use. Please refer to https://github.com/OWASP/www-project-vulnerable-web-applications-directory

curated-resourceseducationlabs-practice+3
8835 days ago
awesome-cybersec preview

awesome-cybersec

GitHubdhotrey/awesome-cybersec

A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
ctfcurated-resourceseducation+8
1952 months ago
0l4bs preview

0l4bs

GitHubtegal1337/0l4bs

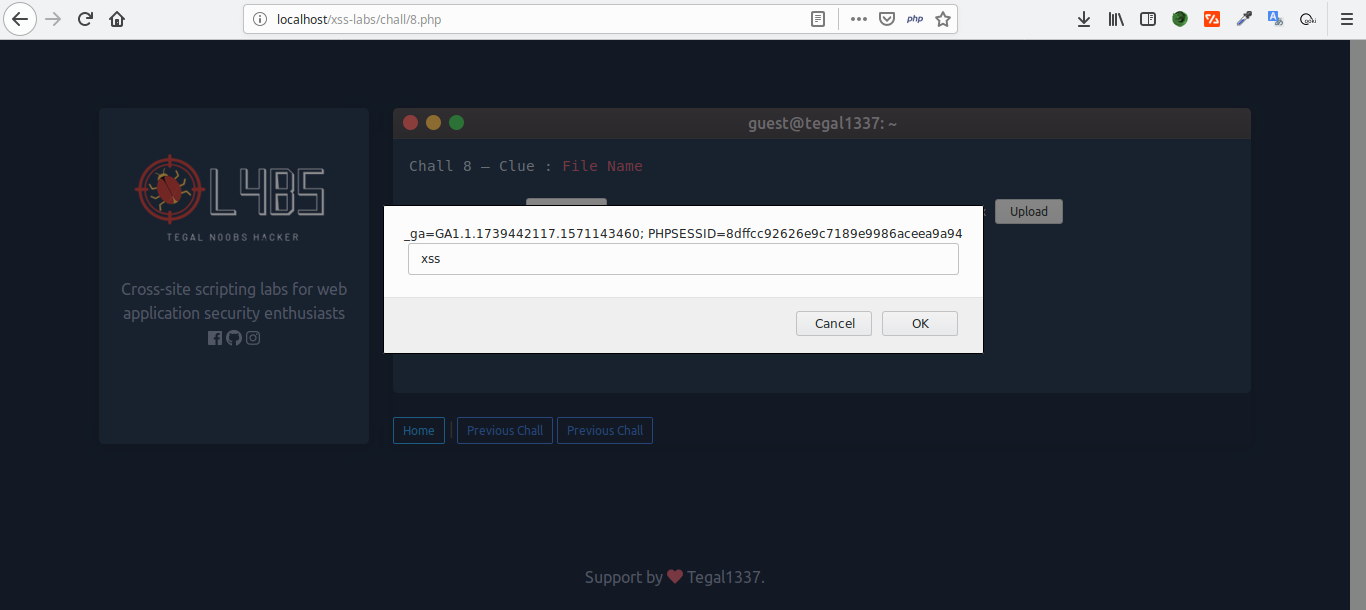
Cross-site scripting labs for web application security enthusiasts
ctfeducationlabs-practice+1
3485 years ago
Pentest-Bookmarkz preview

Pentest-Bookmarkz

GitHubsofianehamlaoui/pentest-bookmarkz

A collection of useful links for Pentesters
ctfcurated-resourceseducation+9
1801 year ago
ParsingPeas preview

ParsingPeas

GitHubyuvalmil/parsingpeas

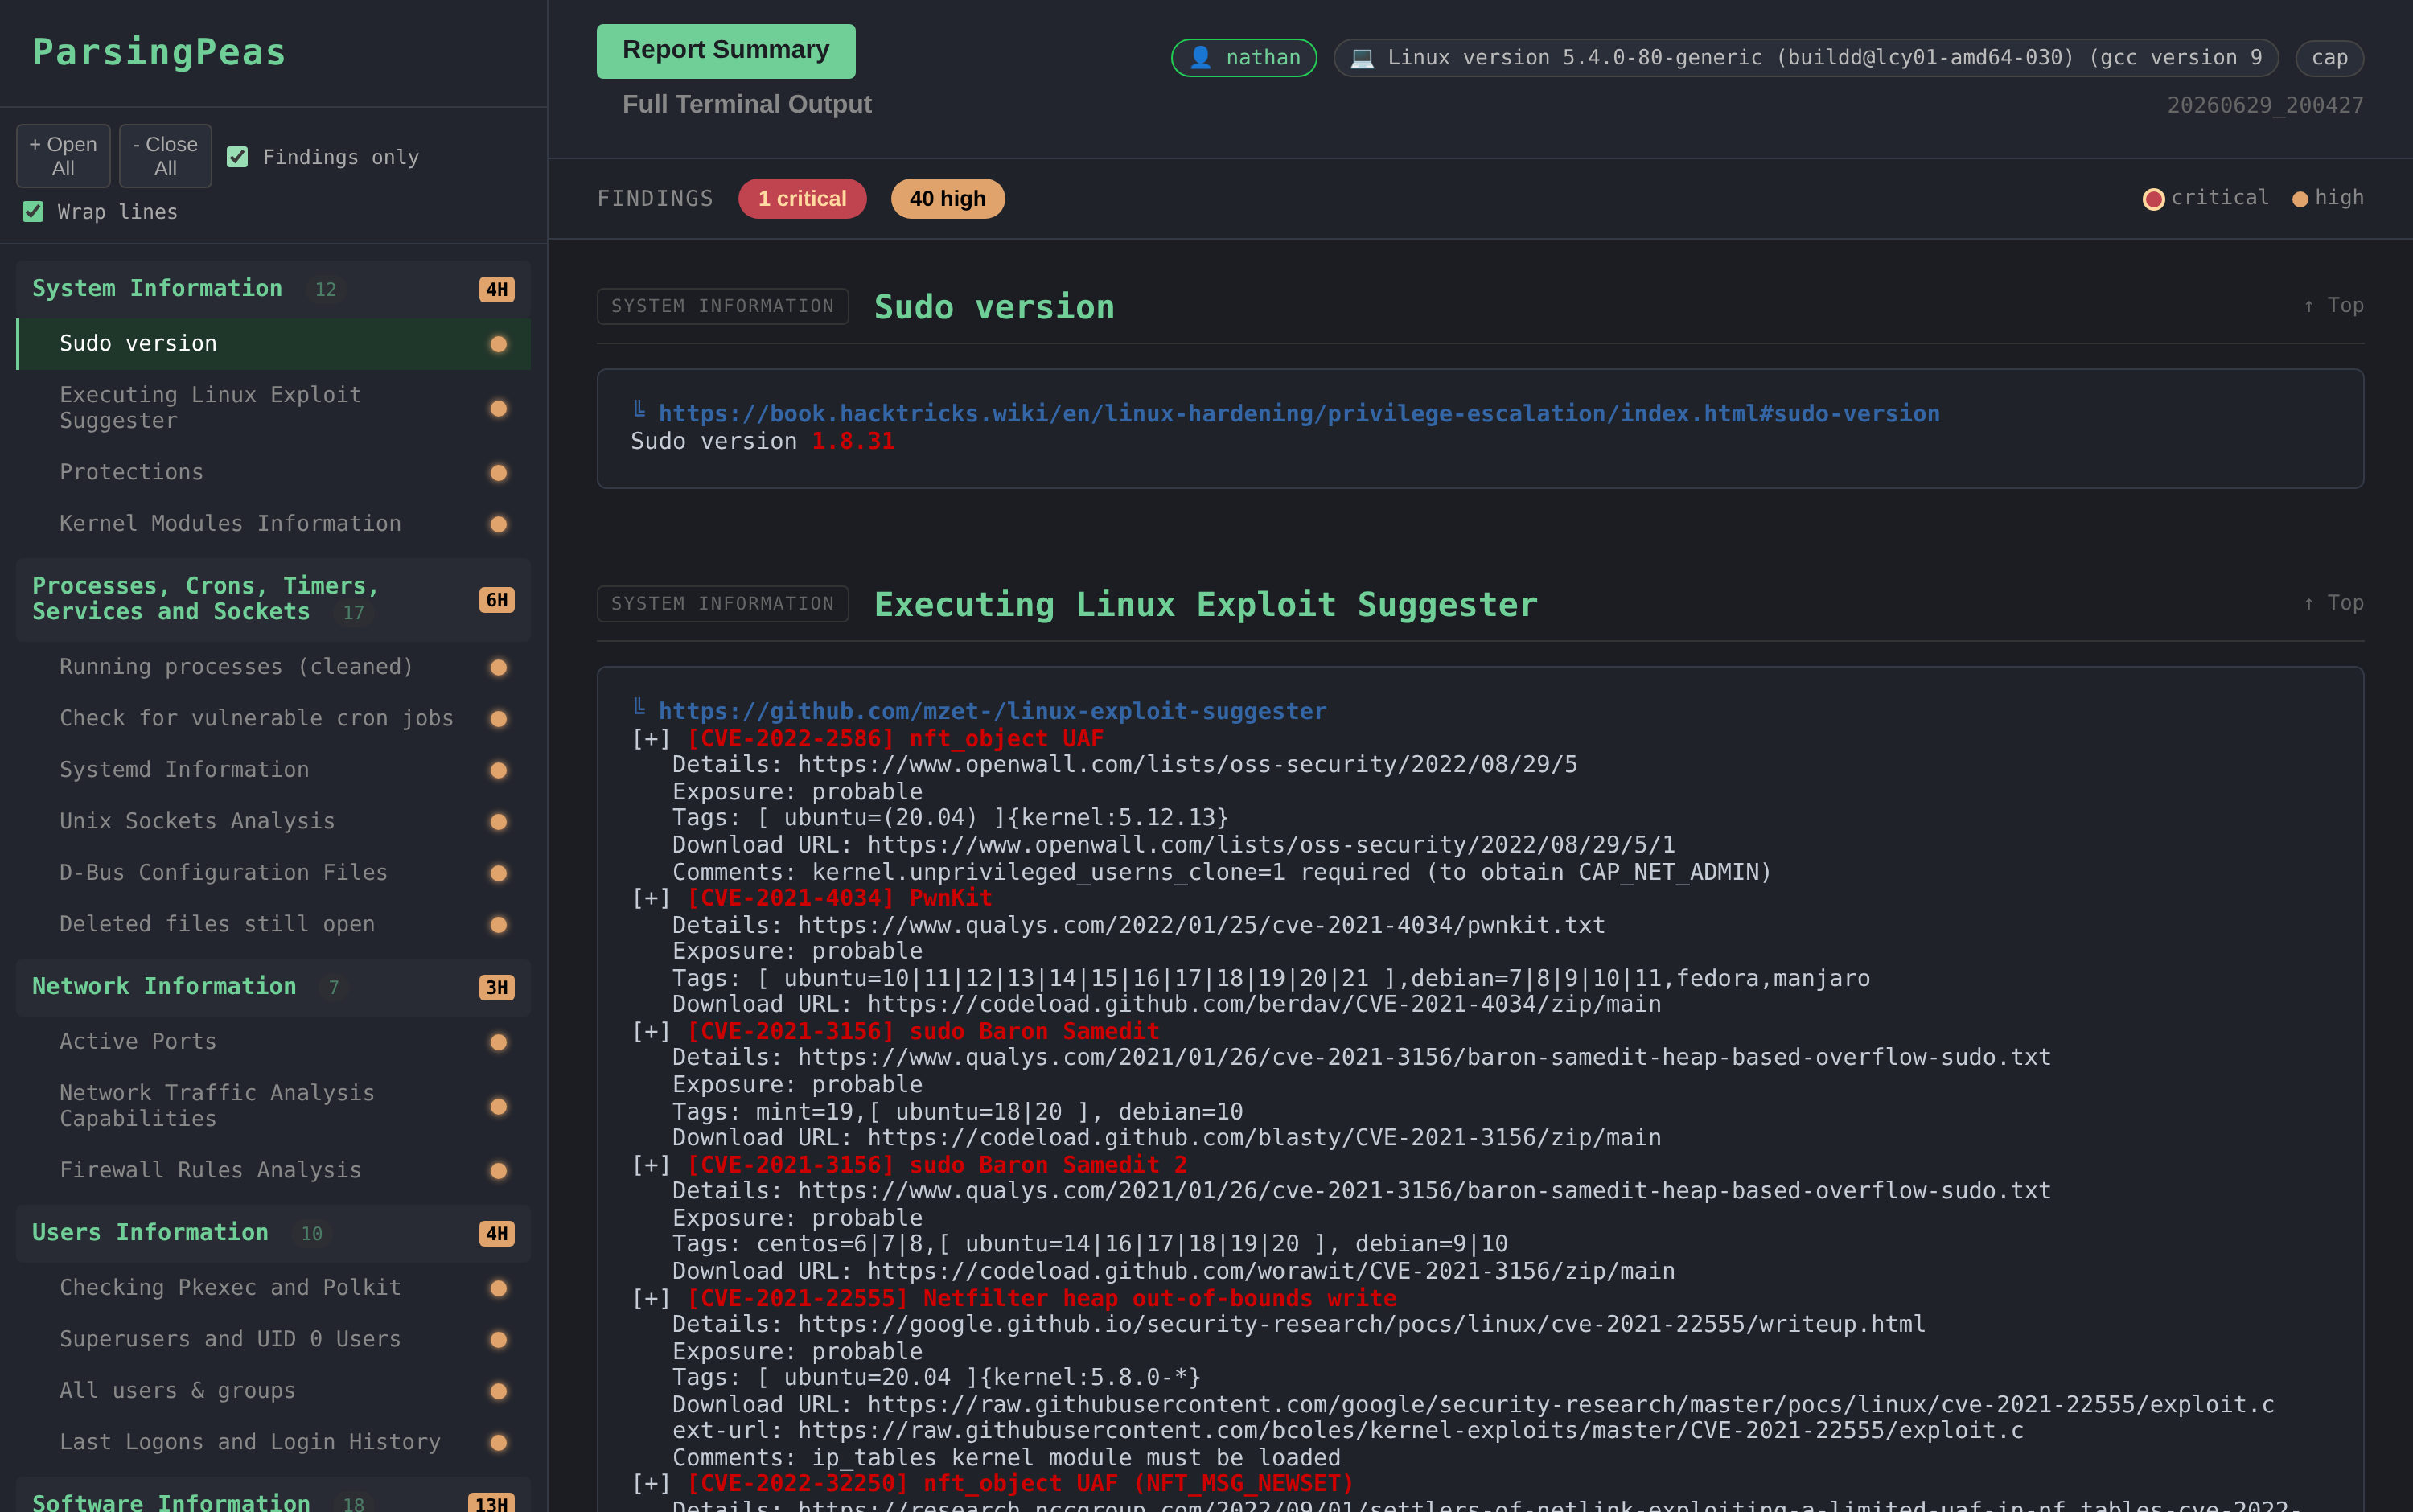
HTML parser for PEAS output with additional features

ctfeducationinformation-gathering+6
1633 months ago
Previous12Next